
#keplradvisessocialloginuserstotransferassets
keplradvisessocialloginuserstotransferassets
Hot
Latest
·
--
Article
KEPLR WALLET SECURITY ALERT: GOOGLE & APPLE LOGIN USERS URGED TO TRANSFER THEIR CRYPTO ASSETS NOWBREAKING CRYPTO SECURITY NEWS
November 8, 2026
🚨 KEPLR WALLET SECURITY BREACH: GOOGLE & APPLE LOGIN USERS URGED TO MOVE THEIR ASSETS
A major security incident has raised fresh concerns across the Cosmos ecosystem after Keplr Wallet warned users that some accounts created through Google and Apple social login may have exposed private keys.
According to Keplr, the incident is linked to a vulnerability in Web3Auth infrastructure, the third-party service supporting social-login wallet functionality.
Keplr is working with Web3Auth to protect affected assets. Users who created wallets using recovery phrases or hardware wallets are currently considered unaffected.
🔍 What Happened?
Some Google and Apple social-login wallets experienced private-key exposure and unauthorized transactions.Keplr has suspended the affected social-login functionality.Users are advised to stop depositing new funds into potentially affected accounts.Remaining transferable assets should be moved to wallets created with a recovery phrase or hardware wallet, following Keplr's official guidance.Staked and locked assets may require additional time to secure.Some affected accounts may already display reduced or zero balances due to ongoing protective measures.KuCoin+2💰 On-Chain Investigation Raises Concerns
An independent investigation by blockchain analytics firm Bitquery reported:
At least $6.01 million in assets held at two suspected attacker-controlled addresses.More than 44,000 wallets drained across multiple Cosmos ecosystem chains.Approximately 1.96 million staked ATOM moved during the incident.
These are independent investigation estimates, not a final loss figure confirmed by Keplr. Bitquery
⚠️ Important Warning for Users
If you created your Keplr wallet using Google or Apple:
Do not deposit additional funds into the potentially affected wallet.Follow verified instructions from Keplr before moving remaining assets.Use a properly secured recovery-phrase or hardware wallet.Never share your recovery phrase or private keys.Avoid unofficial recovery services, suspicious links and direct messages claiming they can recover stolen funds.
📊 My Market Perspective
This incident highlights a critical weakness in crypto wallet infrastructure: convenience does not automatically mean security.
Social login makes wallet creation easier for newcomers, but third-party authentication and key-management infrastructure can introduce additional security risks.
For the broader crypto industry, wallet security, private-key protection and user custody remain essential for long-term adoption.
The biggest question is whether Keplr and Web3Auth can fully secure affected assets and restore user confidence.
What do you think: Should crypto wallets prioritize social-login convenience or complete user control through private keys?
#Keplr #CryptoSecurity #Web3Auth #Cosmos #Blockchain #CryptoNews
Research references: Bitquery on-chain investigation · Keplr incident update · [Binance News coverage](https://www.binance.com/lo-LA/square/post/385911080190451?utm_source=chatgpt.com)
#keplradvisessocialloginuserstotransferassets $BNB
{spot}(BNBUSDT)
KEPLR WALLET SECURITY ALERT: GOOGLE & APPLE LOGIN USERS URGED TO TRANSFER THEIR CRYPTO ASSETS NOW
BREAKING CRYPTO SECURITY NEWS
November 8, 2026
🚨 KEPLR WALLET SECURITY BREACH: GOOGLE & APPLE LOGIN USERS URGED TO MOVE THEIR ASSETS
A major security incident has raised fresh concerns across the Cosmos ecosystem after Keplr Wallet warned users that some accounts created through Google and Apple social login may have exposed private keys.
According to Keplr, the incident is linked to a vulnerability in Web3Auth infrastructure, the third-party service supporting social-login wallet functionality.
Keplr is working with Web3Auth to protect affected assets. Users who created wallets using recovery phrases or hardware wallets are currently considered unaffected.
🔍 What Happened?
Some Google and Apple social-login wallets experienced private-key exposure and unauthorized transactions.Keplr has suspended the affected social-login functionality.Users are advised to stop depositing new funds into potentially affected accounts.Remaining transferable assets should be moved to wallets created with a recovery phrase or hardware wallet, following Keplr's official guidance.Staked and locked assets may require additional time to secure.Some affected accounts may already display reduced or zero balances due to ongoing protective measures.KuCoin+2💰 On-Chain Investigation Raises Concerns
An independent investigation by blockchain analytics firm Bitquery reported:
At least $6.01 million in assets held at two suspected attacker-controlled addresses.More than 44,000 wallets drained across multiple Cosmos ecosystem chains.Approximately 1.96 million staked ATOM moved during the incident.
These are independent investigation estimates, not a final loss figure confirmed by Keplr. Bitquery
⚠️ Important Warning for Users
If you created your Keplr wallet using Google or Apple:
Do not deposit additional funds into the potentially affected wallet.Follow verified instructions from Keplr before moving remaining assets.Use a properly secured recovery-phrase or hardware wallet.Never share your recovery phrase or private keys.Avoid unofficial recovery services, suspicious links and direct messages claiming they can recover stolen funds.
📊 My Market Perspective
This incident highlights a critical weakness in crypto wallet infrastructure: convenience does not automatically mean security.
Social login makes wallet creation easier for newcomers, but third-party authentication and key-management infrastructure can introduce additional security risks.
For the broader crypto industry, wallet security, private-key protection and user custody remain essential for long-term adoption.
The biggest question is whether Keplr and Web3Auth can fully secure affected assets and restore user confidence.
What do you think: Should crypto wallets prioritize social-login convenience or complete user control through private keys?
#Keplr #CryptoSecurity #Web3Auth #Cosmos #Blockchain #CryptoNews
Research references: Bitquery on-chain investigation · Keplr incident update · Binance News coverage
#keplradvisessocialloginuserstotransferassets $BNB
November 8, 2026
🚨 KEPLR WALLET SECURITY BREACH: GOOGLE & APPLE LOGIN USERS URGED TO MOVE THEIR ASSETS
A major security incident has raised fresh concerns across the Cosmos ecosystem after Keplr Wallet warned users that some accounts created through Google and Apple social login may have exposed private keys.
According to Keplr, the incident is linked to a vulnerability in Web3Auth infrastructure, the third-party service supporting social-login wallet functionality.
Keplr is working with Web3Auth to protect affected assets. Users who created wallets using recovery phrases or hardware wallets are currently considered unaffected.
🔍 What Happened?
Some Google and Apple social-login wallets experienced private-key exposure and unauthorized transactions.Keplr has suspended the affected social-login functionality.Users are advised to stop depositing new funds into potentially affected accounts.Remaining transferable assets should be moved to wallets created with a recovery phrase or hardware wallet, following Keplr's official guidance.Staked and locked assets may require additional time to secure.Some affected accounts may already display reduced or zero balances due to ongoing protective measures.KuCoin+2💰 On-Chain Investigation Raises Concerns
An independent investigation by blockchain analytics firm Bitquery reported:
At least $6.01 million in assets held at two suspected attacker-controlled addresses.More than 44,000 wallets drained across multiple Cosmos ecosystem chains.Approximately 1.96 million staked ATOM moved during the incident.
These are independent investigation estimates, not a final loss figure confirmed by Keplr. Bitquery
⚠️ Important Warning for Users
If you created your Keplr wallet using Google or Apple:
Do not deposit additional funds into the potentially affected wallet.Follow verified instructions from Keplr before moving remaining assets.Use a properly secured recovery-phrase or hardware wallet.Never share your recovery phrase or private keys.Avoid unofficial recovery services, suspicious links and direct messages claiming they can recover stolen funds.
📊 My Market Perspective
This incident highlights a critical weakness in crypto wallet infrastructure: convenience does not automatically mean security.
Social login makes wallet creation easier for newcomers, but third-party authentication and key-management infrastructure can introduce additional security risks.
For the broader crypto industry, wallet security, private-key protection and user custody remain essential for long-term adoption.
The biggest question is whether Keplr and Web3Auth can fully secure affected assets and restore user confidence.
What do you think: Should crypto wallets prioritize social-login convenience or complete user control through private keys?
#Keplr #CryptoSecurity #Web3Auth #Cosmos #Blockchain #CryptoNews
Research references: Bitquery on-chain investigation · Keplr incident update · Binance News coverage
#keplradvisessocialloginuserstotransferassets $BNB
3
2.9k
Article
Keplr Wallet Hack: Google and Apple Login Users Told to Move Funds After $6M Drain🔐 Keplr paused social logins after a Web3Auth breach, and investigators traced over $6M across Cosmos wallets. Here is what happened, who is at risk and what to do now.
🔐 One of the easiest ways to start in crypto just became the risky one for some Keplr users. Here is what the data shows, what is still unknown, and what to do now.
🚨 Logging in with Google or Apple felt safer than writing down a seed phrase. This week, Keplr paused both options after reports of unauthorized transactions. 🤔
📊 What Happened?
Keplr paused Google and Apple logins after users reported funds moving out of their wallets without approval. The wallet posted its statement on November 7 and said the affected accounts were those created through Google or Apple login.
🧩 Where the Problem Started
Keplr co-founder Josh Lee said this was not a hack of Keplr's own code and that the incident began at Web3Auth, the provider behind its social login. Web3Auth acknowledged a security incident on November 6 and paused its embedded wallet service. Keplr's support pages explain that social login keys are created through distributed key generation, which splits the work across several parties so no single one holds the full key.
📉 How Big Is It?
On-chain investigators at Bitquery traced about $6.01M in transfers involving more than 44,000 wallets across Cosmos networks. Lee gave an early estimate that about 20% of Google and Apple login accounts could be affected, though only a fraction have been exploited. At last check, neither Keplr nor Web3Auth had published an official total, so treat the $6M as an estimate.
🛟 What Keplr Advises
Keplr told social login users to stop adding funds and to move their remaining assets to an account created with a recovery phrase or a hardware wallet. My own addition: send a small test transfer first and double check the destination address before moving the rest.
👀 What You Might See
Web3Auth has begun a white-hat recovery effort for exposed accounts. Keplr warned that some Google and Apple login wallets may show reduced or empty balances because of those protection measures, so a low balance does not automatically mean funds are gone.
✅ What Reports Say Is Not Affected
Accounts created with a recovery phrase or a hardware wallet have been described as outside the affected group. Reports also say there have been no attacks on smart contracts or the underlying chain.
🛑 What We Still Don't Know
We don't yet know the exact number of affected accounts, the final loss, or when social login will return. At last check, Web3Auth's embedded wallet service was still paused. The bigger open question is whether other wallets built on the same login infrastructure are exposed, and Web3Auth's investigation will answer that.
🟢 The Bullish Case
The white-hat recovery returns funds, Web3Auth explains the root cause clearly, and social login comes back with stronger safeguards. That would limit the damage to the users already hit.
⚠️ The Risk Scenario
More accounts are drained, other wallets using the same infrastructure turn out to be affected, or the outage drags on. Users who have not moved their funds are the most exposed.
👀 Three Things to Watch Next
Does Web3Auth publish a root cause and an affected account count?Does the white-hat recovery return funds, and how much?Do other wallets that use the same login service report problems?
💡 The Takeaway
Keplr paused social logins after a Web3Auth breach, with about $6M traced and an early estimate of 20% of Google and Apple login accounts at risk.
Seed phrase and hardware accounts have been described as outside the affected group, but the full scope is not confirmed.
I would pay particular attention to Web3Auth's investigation, because it will tell us whether this stays a Keplr problem or reaches other wallets. ATOM holders should watch for updates from the Keplr team.
🎯 Do you use a social login wallet, or do you stick to a seed phrase or hardware wallet? And will this change how you store your crypto?
I'm interested in hearing how you decide. Share your view below. 👇
That is the part worth watching.
This post is for informational and educational purposes only and is not financial advice. Crypto markets are volatile. Always conduct your own research before making financial decisions.
#BinanceSquare #KeplrAdvisesSocialLoginUsersToTransferAssets #Cosmos #CryptoSecurity #CryptoNews
{spot}(ATOMUSDT)
Keplr Wallet Hack: Google and Apple Login Users Told to Move Funds After $6M Drain
🔐 Keplr paused social logins after a Web3Auth breach, and investigators traced over $6M across Cosmos wallets. Here is what happened, who is at risk and what to do now.
🔐 One of the easiest ways to start in crypto just became the risky one for some Keplr users. Here is what the data shows, what is still unknown, and what to do now.
🚨 Logging in with Google or Apple felt safer than writing down a seed phrase. This week, Keplr paused both options after reports of unauthorized transactions. 🤔
📊 What Happened?
Keplr paused Google and Apple logins after users reported funds moving out of their wallets without approval. The wallet posted its statement on November 7 and said the affected accounts were those created through Google or Apple login.
🧩 Where the Problem Started
Keplr co-founder Josh Lee said this was not a hack of Keplr's own code and that the incident began at Web3Auth, the provider behind its social login. Web3Auth acknowledged a security incident on November 6 and paused its embedded wallet service. Keplr's support pages explain that social login keys are created through distributed key generation, which splits the work across several parties so no single one holds the full key.
📉 How Big Is It?
On-chain investigators at Bitquery traced about $6.01M in transfers involving more than 44,000 wallets across Cosmos networks. Lee gave an early estimate that about 20% of Google and Apple login accounts could be affected, though only a fraction have been exploited. At last check, neither Keplr nor Web3Auth had published an official total, so treat the $6M as an estimate.
🛟 What Keplr Advises
Keplr told social login users to stop adding funds and to move their remaining assets to an account created with a recovery phrase or a hardware wallet. My own addition: send a small test transfer first and double check the destination address before moving the rest.
👀 What You Might See
Web3Auth has begun a white-hat recovery effort for exposed accounts. Keplr warned that some Google and Apple login wallets may show reduced or empty balances because of those protection measures, so a low balance does not automatically mean funds are gone.
✅ What Reports Say Is Not Affected
Accounts created with a recovery phrase or a hardware wallet have been described as outside the affected group. Reports also say there have been no attacks on smart contracts or the underlying chain.
🛑 What We Still Don't Know
We don't yet know the exact number of affected accounts, the final loss, or when social login will return. At last check, Web3Auth's embedded wallet service was still paused. The bigger open question is whether other wallets built on the same login infrastructure are exposed, and Web3Auth's investigation will answer that.
🟢 The Bullish Case
The white-hat recovery returns funds, Web3Auth explains the root cause clearly, and social login comes back with stronger safeguards. That would limit the damage to the users already hit.
⚠️ The Risk Scenario
More accounts are drained, other wallets using the same infrastructure turn out to be affected, or the outage drags on. Users who have not moved their funds are the most exposed.
👀 Three Things to Watch Next
Does Web3Auth publish a root cause and an affected account count?Does the white-hat recovery return funds, and how much?Do other wallets that use the same login service report problems?
💡 The Takeaway
Keplr paused social logins after a Web3Auth breach, with about $6M traced and an early estimate of 20% of Google and Apple login accounts at risk.
Seed phrase and hardware accounts have been described as outside the affected group, but the full scope is not confirmed.
I would pay particular attention to Web3Auth's investigation, because it will tell us whether this stays a Keplr problem or reaches other wallets. ATOM holders should watch for updates from the Keplr team.
🎯 Do you use a social login wallet, or do you stick to a seed phrase or hardware wallet? And will this change how you store your crypto?
I'm interested in hearing how you decide. Share your view below. 👇
That is the part worth watching.
This post is for informational and educational purposes only and is not financial advice. Crypto markets are volatile. Always conduct your own research before making financial decisions.
#BinanceSquare #KeplrAdvisesSocialLoginUsersToTransferAssets #Cosmos #CryptoSecurity #CryptoNews
🔐 One of the easiest ways to start in crypto just became the risky one for some Keplr users. Here is what the data shows, what is still unknown, and what to do now.
🚨 Logging in with Google or Apple felt safer than writing down a seed phrase. This week, Keplr paused both options after reports of unauthorized transactions. 🤔
📊 What Happened?
Keplr paused Google and Apple logins after users reported funds moving out of their wallets without approval. The wallet posted its statement on November 7 and said the affected accounts were those created through Google or Apple login.
🧩 Where the Problem Started
Keplr co-founder Josh Lee said this was not a hack of Keplr's own code and that the incident began at Web3Auth, the provider behind its social login. Web3Auth acknowledged a security incident on November 6 and paused its embedded wallet service. Keplr's support pages explain that social login keys are created through distributed key generation, which splits the work across several parties so no single one holds the full key.
📉 How Big Is It?
On-chain investigators at Bitquery traced about $6.01M in transfers involving more than 44,000 wallets across Cosmos networks. Lee gave an early estimate that about 20% of Google and Apple login accounts could be affected, though only a fraction have been exploited. At last check, neither Keplr nor Web3Auth had published an official total, so treat the $6M as an estimate.
🛟 What Keplr Advises
Keplr told social login users to stop adding funds and to move their remaining assets to an account created with a recovery phrase or a hardware wallet. My own addition: send a small test transfer first and double check the destination address before moving the rest.
👀 What You Might See
Web3Auth has begun a white-hat recovery effort for exposed accounts. Keplr warned that some Google and Apple login wallets may show reduced or empty balances because of those protection measures, so a low balance does not automatically mean funds are gone.
✅ What Reports Say Is Not Affected
Accounts created with a recovery phrase or a hardware wallet have been described as outside the affected group. Reports also say there have been no attacks on smart contracts or the underlying chain.
🛑 What We Still Don't Know
We don't yet know the exact number of affected accounts, the final loss, or when social login will return. At last check, Web3Auth's embedded wallet service was still paused. The bigger open question is whether other wallets built on the same login infrastructure are exposed, and Web3Auth's investigation will answer that.
🟢 The Bullish Case
The white-hat recovery returns funds, Web3Auth explains the root cause clearly, and social login comes back with stronger safeguards. That would limit the damage to the users already hit.
⚠️ The Risk Scenario
More accounts are drained, other wallets using the same infrastructure turn out to be affected, or the outage drags on. Users who have not moved their funds are the most exposed.
👀 Three Things to Watch Next
Does Web3Auth publish a root cause and an affected account count?Does the white-hat recovery return funds, and how much?Do other wallets that use the same login service report problems?
💡 The Takeaway
Keplr paused social logins after a Web3Auth breach, with about $6M traced and an early estimate of 20% of Google and Apple login accounts at risk.
Seed phrase and hardware accounts have been described as outside the affected group, but the full scope is not confirmed.
I would pay particular attention to Web3Auth's investigation, because it will tell us whether this stays a Keplr problem or reaches other wallets. ATOM holders should watch for updates from the Keplr team.
🎯 Do you use a social login wallet, or do you stick to a seed phrase or hardware wallet? And will this change how you store your crypto?
I'm interested in hearing how you decide. Share your view below. 👇
That is the part worth watching.
This post is for informational and educational purposes only and is not financial advice. Crypto markets are volatile. Always conduct your own research before making financial decisions.
#BinanceSquare #KeplrAdvisesSocialLoginUsersToTransferAssets #Cosmos #CryptoSecurity #CryptoNews
1
1
2k
🚨 KEPLR WALLET SECURITY ALERT!
Keplr urges users who created wallets through Google or Apple login to stop deposits and move remaining assets to wallets secured by a recovery phrase or hardware device.
#KeplrAdvisesSocialLoginUsersToTransferAssets
The issue is linked to a Web3Auth vulnerability that exposed private keys. Trackers identified around $6M in transfers involving 44,000+ wallets. However, this is NOT a confirmed loss figure: some movements were whitehat recovery operations.
Recovery-phrase and hardware-wallet accounts were not affected. Staked assets may take longer to secure.
Crypto convenience comes with risks. Follow official Keplr and Web3Auth updates only. Avoid fake recovery links and DMs. DYOR.
🚨 KEPLR WALLET SECURITY ALERT!
Keplr urges users who created wallets through Google or Apple login to stop deposits and move remaining assets to wallets secured by a recovery phrase or hardware device.
#KeplrAdvisesSocialLoginUsersToTransferAssets
The issue is linked to a Web3Auth vulnerability that exposed private keys. Trackers identified around $6M in transfers involving 44,000+ wallets. However, this is NOT a confirmed loss figure: some movements were whitehat recovery operations.
Recovery-phrase and hardware-wallet accounts were not affected. Staked assets may take longer to secure.
Crypto convenience comes with risks. Follow official Keplr and Web3Auth updates only. Avoid fake recovery links and DMs. DYOR.
Keplr urges users who created wallets through Google or Apple login to stop deposits and move remaining assets to wallets secured by a recovery phrase or hardware device.
#KeplrAdvisesSocialLoginUsersToTransferAssets
The issue is linked to a Web3Auth vulnerability that exposed private keys. Trackers identified around $6M in transfers involving 44,000+ wallets. However, this is NOT a confirmed loss figure: some movements were whitehat recovery operations.
Recovery-phrase and hardware-wallet accounts were not affected. Staked assets may take longer to secure.
Crypto convenience comes with risks. Follow official Keplr and Web3Auth updates only. Avoid fake recovery links and DMs. DYOR.
User-7f4bc:
thanks
4
34
1.3k
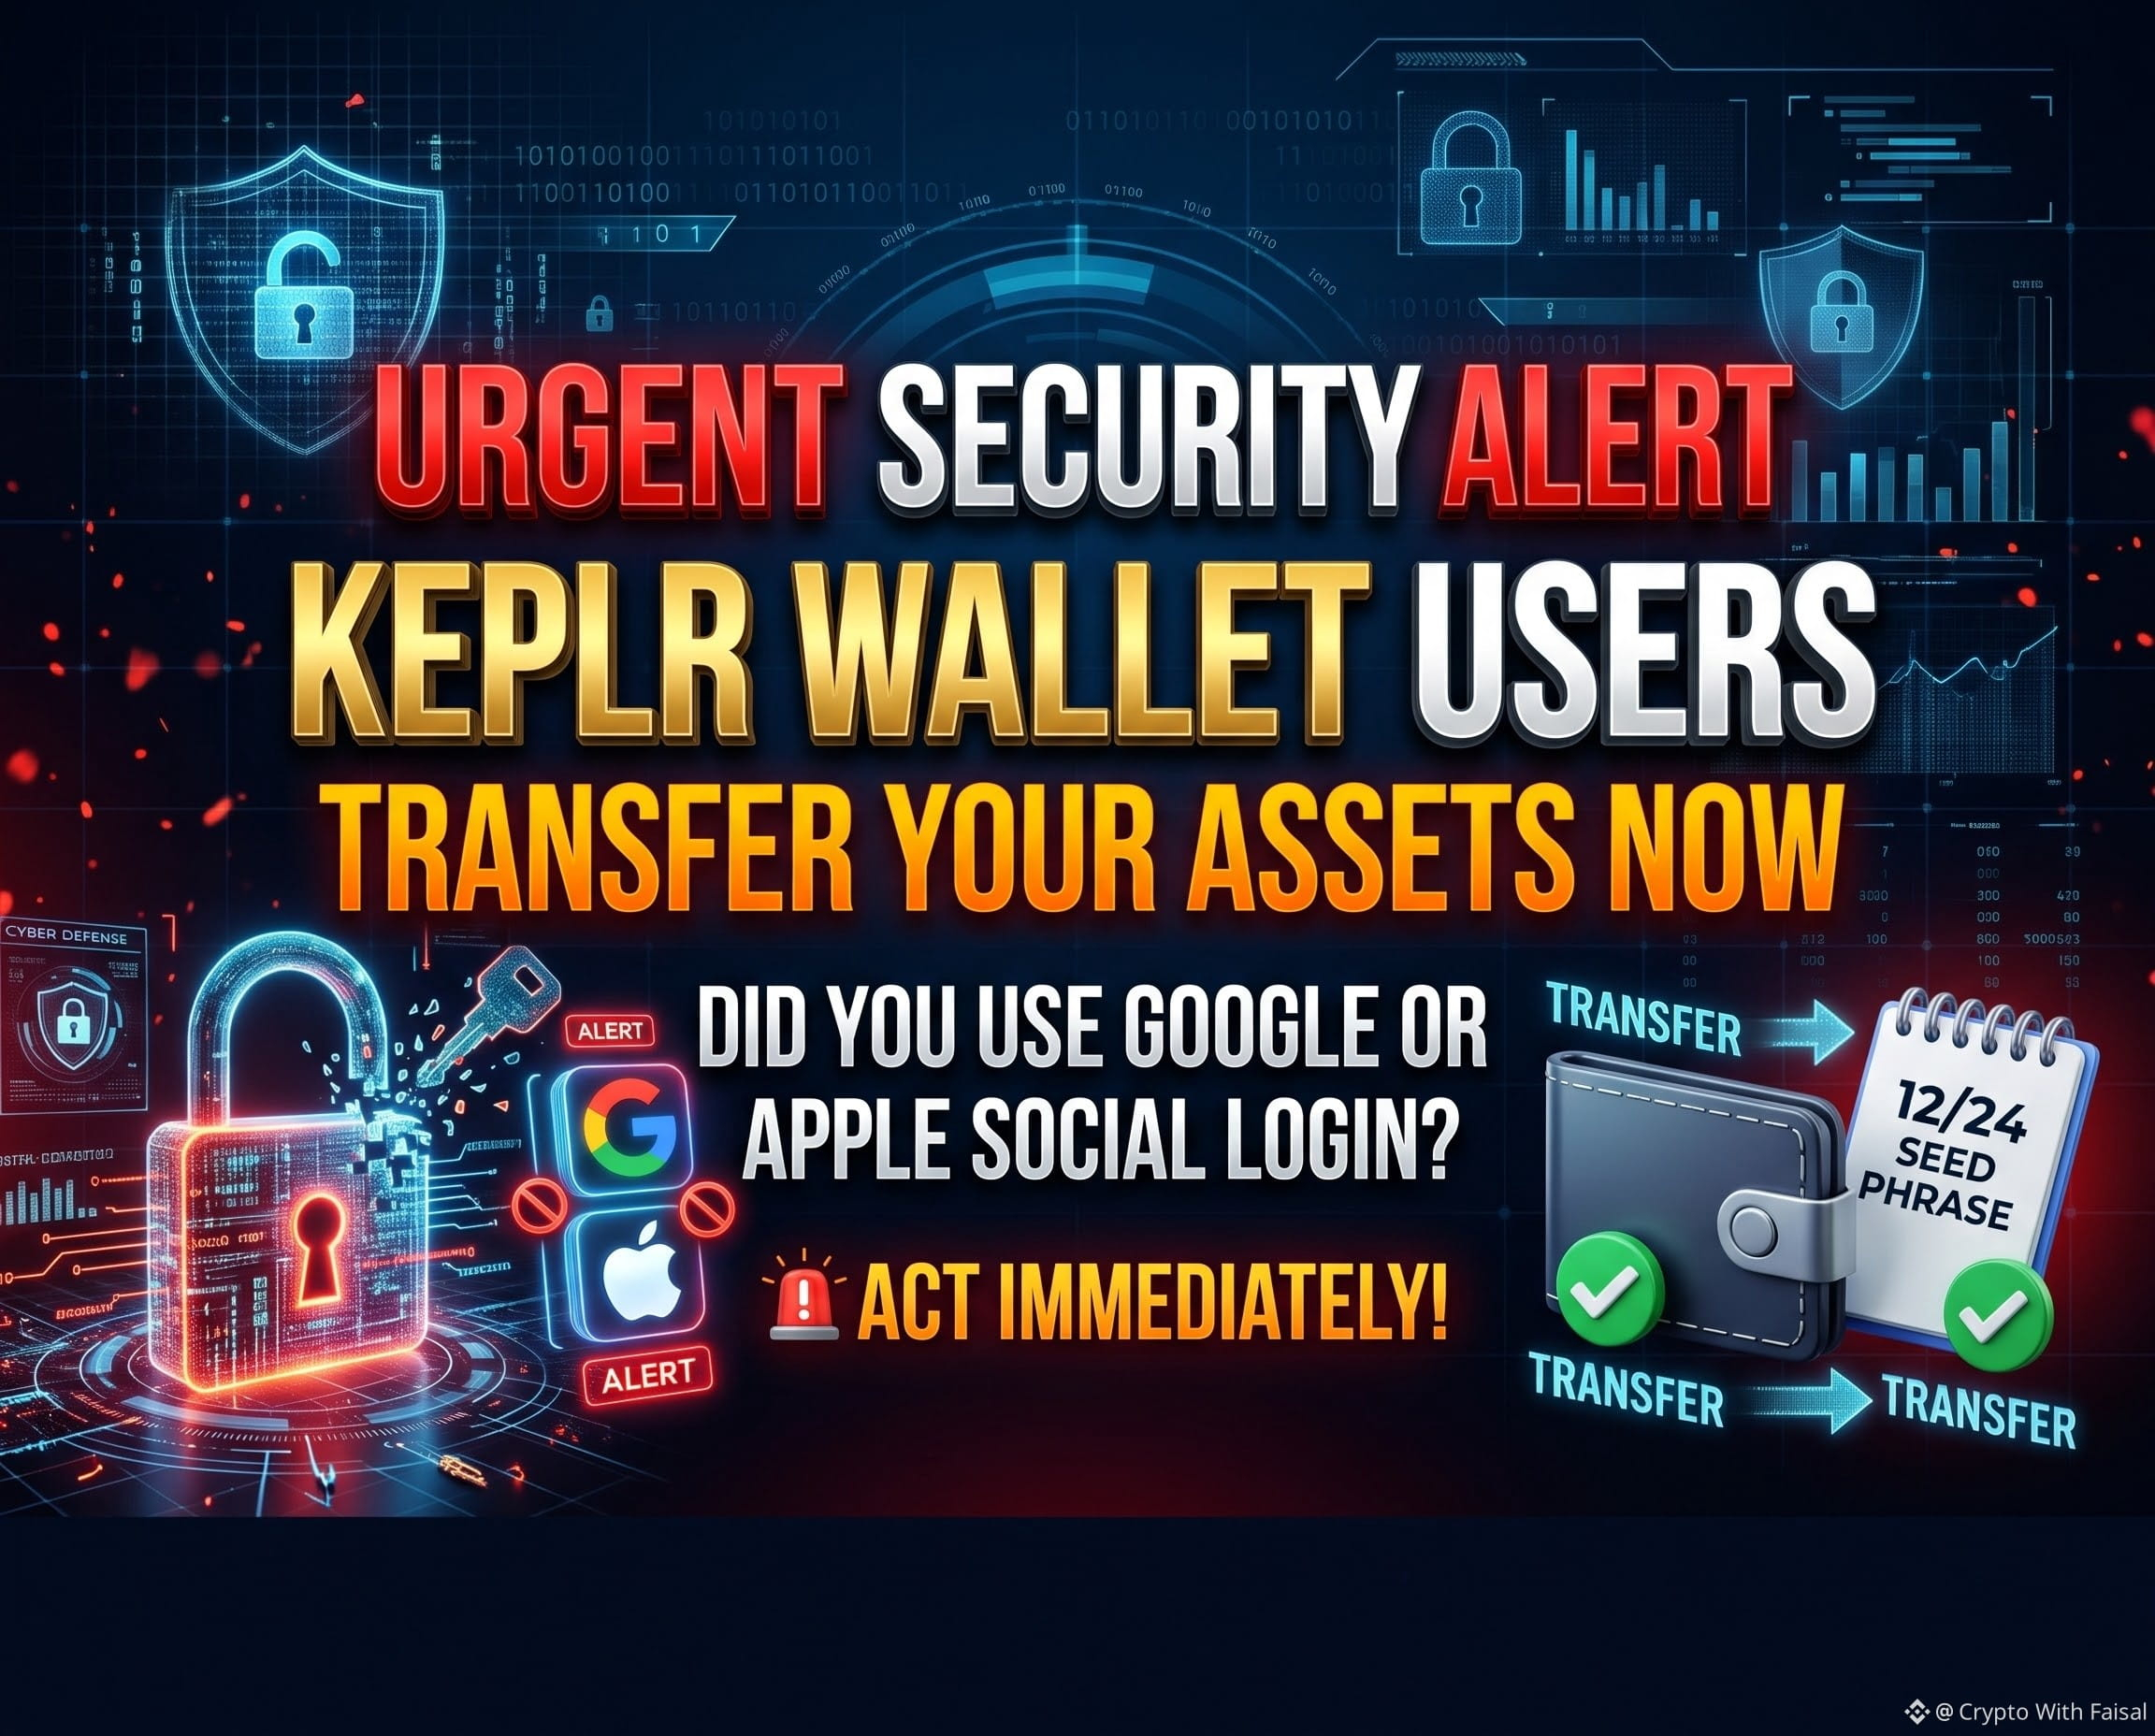
🚨 URGENT SECURITY ALERT: Keplr Wallet Users, Act Now! 🚨
Are you using Keplr Wallet with a Google or Apple social login? Pay close attention.
A critical vulnerability in the Web3Auth infrastructure has exposed private keys for users who created accounts via social logins. Over $6 million has already been drained across the Cosmos ecosystem.
As a trader, protecting your capital is rule number one. Here is your immediate action plan:
1️⃣ TRANSFER LIQUID FUNDS: Move any unstaked crypto from your social login account to a wallet secured by a traditional seed phrase or a hardware wallet immediately.
2️⃣ HALT DEPOSITS: Do NOT send any new funds to accounts created via Apple or Google.
3️⃣ STAKED ASSETS: If your funds are locked, Keplr is coordinating white-hat rescue efforts. Wait for official guidance.
4️⃣ AVOID SCAMS: Phishing accounts are DMing users with fake "asset recovery" links. Ignore them—only trust official Keplr channels.
Good news: If you created your Keplr wallet using a standard 12/24-word seed phrase or a hardware wallet, your assets are safe and unaffected.
Not your keys, not your coins. Upgrade your security today and stay safe!
$BTC
{future}(BTCUSDT)
$IDOL
{future}(IDOLUSDT)
$JCT
{future}(JCTUSDT)
#keplradvisessocialloginuserstotransferassets #CryptoSecurity #Cosmos #BinanceSquare
🚨 URGENT SECURITY ALERT: Keplr Wallet Users, Act Now! 🚨
Are you using Keplr Wallet with a Google or Apple social login? Pay close attention.
A critical vulnerability in the Web3Auth infrastructure has exposed private keys for users who created accounts via social logins. Over $6 million has already been drained across the Cosmos ecosystem.
As a trader, protecting your capital is rule number one. Here is your immediate action plan:
1️⃣ TRANSFER LIQUID FUNDS: Move any unstaked crypto from your social login account to a wallet secured by a traditional seed phrase or a hardware wallet immediately.
2️⃣ HALT DEPOSITS: Do NOT send any new funds to accounts created via Apple or Google.
3️⃣ STAKED ASSETS: If your funds are locked, Keplr is coordinating white-hat rescue efforts. Wait for official guidance.
4️⃣ AVOID SCAMS: Phishing accounts are DMing users with fake "asset recovery" links. Ignore them—only trust official Keplr channels.
Good news: If you created your Keplr wallet using a standard 12/24-word seed phrase or a hardware wallet, your assets are safe and unaffected.
Not your keys, not your coins. Upgrade your security today and stay safe!
$BTC
$IDOL
$JCT
#keplradvisessocialloginuserstotransferassets #CryptoSecurity #Cosmos #BinanceSquare
Are you using Keplr Wallet with a Google or Apple social login? Pay close attention.
A critical vulnerability in the Web3Auth infrastructure has exposed private keys for users who created accounts via social logins. Over $6 million has already been drained across the Cosmos ecosystem.
As a trader, protecting your capital is rule number one. Here is your immediate action plan:
1️⃣ TRANSFER LIQUID FUNDS: Move any unstaked crypto from your social login account to a wallet secured by a traditional seed phrase or a hardware wallet immediately.
2️⃣ HALT DEPOSITS: Do NOT send any new funds to accounts created via Apple or Google.
3️⃣ STAKED ASSETS: If your funds are locked, Keplr is coordinating white-hat rescue efforts. Wait for official guidance.
4️⃣ AVOID SCAMS: Phishing accounts are DMing users with fake "asset recovery" links. Ignore them—only trust official Keplr channels.
Good news: If you created your Keplr wallet using a standard 12/24-word seed phrase or a hardware wallet, your assets are safe and unaffected.
Not your keys, not your coins. Upgrade your security today and stay safe!
$BTC
$IDOL
$JCT
#keplradvisessocialloginuserstotransferassets #CryptoSecurity #Cosmos #BinanceSquare
1
1.9k

#KeplrAdvisesSocialLoginUsersToTransferAssets *🚨 URGENT: Keplr Users - READ THIS NOW! 🚨*
If you created your Keplr Wallet with *Google / Apple Social Login*, Keplr is advising you to *TRANSFER YOUR ASSETS IMMEDIATELY* to a new secure wallet.
Why? Your social login session could be at risk. Don't wait for a hack to happen.
*DO THIS NOW:*
1. Create a NEW Keplr Wallet with Seed Phrase (NOT social login)
2. Transfer ALL your $ATOM, $OSMO, $TIA & other Cosmos assets
3. Never share your seed phrase with ANYONE
4. Revoke old permissions
Your funds are YOUR responsibility. 1 minute of action today can save your entire portfolio.
Tag a friend who uses Keplr 👇 They need to see this!
#KeplrAdvisesSocialLoginUsersToTransferAssets #StaySafeCrypto #Binance #CryptoNews
#KeplrAdvisesSocialLoginUsersToTransferAssets *🚨 URGENT: Keplr Users - READ THIS NOW! 🚨*
If you created your Keplr Wallet with *Google / Apple Social Login*, Keplr is advising you to *TRANSFER YOUR ASSETS IMMEDIATELY* to a new secure wallet.
Why? Your social login session could be at risk. Don't wait for a hack to happen.
*DO THIS NOW:*
1. Create a NEW Keplr Wallet with Seed Phrase (NOT social login)
2. Transfer ALL your $ATOM, $OSMO, $TIA & other Cosmos assets
3. Never share your seed phrase with ANYONE
4. Revoke old permissions
Your funds are YOUR responsibility. 1 minute of action today can save your entire portfolio.
Tag a friend who uses Keplr 👇 They need to see this!
#KeplrAdvisesSocialLoginUsersToTransferAssets #StaySafeCrypto #Binance #CryptoNews
If you created your Keplr Wallet with *Google / Apple Social Login*, Keplr is advising you to *TRANSFER YOUR ASSETS IMMEDIATELY* to a new secure wallet.
Why? Your social login session could be at risk. Don't wait for a hack to happen.
*DO THIS NOW:*
1. Create a NEW Keplr Wallet with Seed Phrase (NOT social login)
2. Transfer ALL your $ATOM, $OSMO, $TIA & other Cosmos assets
3. Never share your seed phrase with ANYONE
4. Revoke old permissions
Your funds are YOUR responsibility. 1 minute of action today can save your entire portfolio.
Tag a friend who uses Keplr 👇 They need to see this!
#KeplrAdvisesSocialLoginUsersToTransferAssets #StaySafeCrypto #Binance #CryptoNews
waqar h 5:
💲
2
3
1.2k

·
--
Bearish
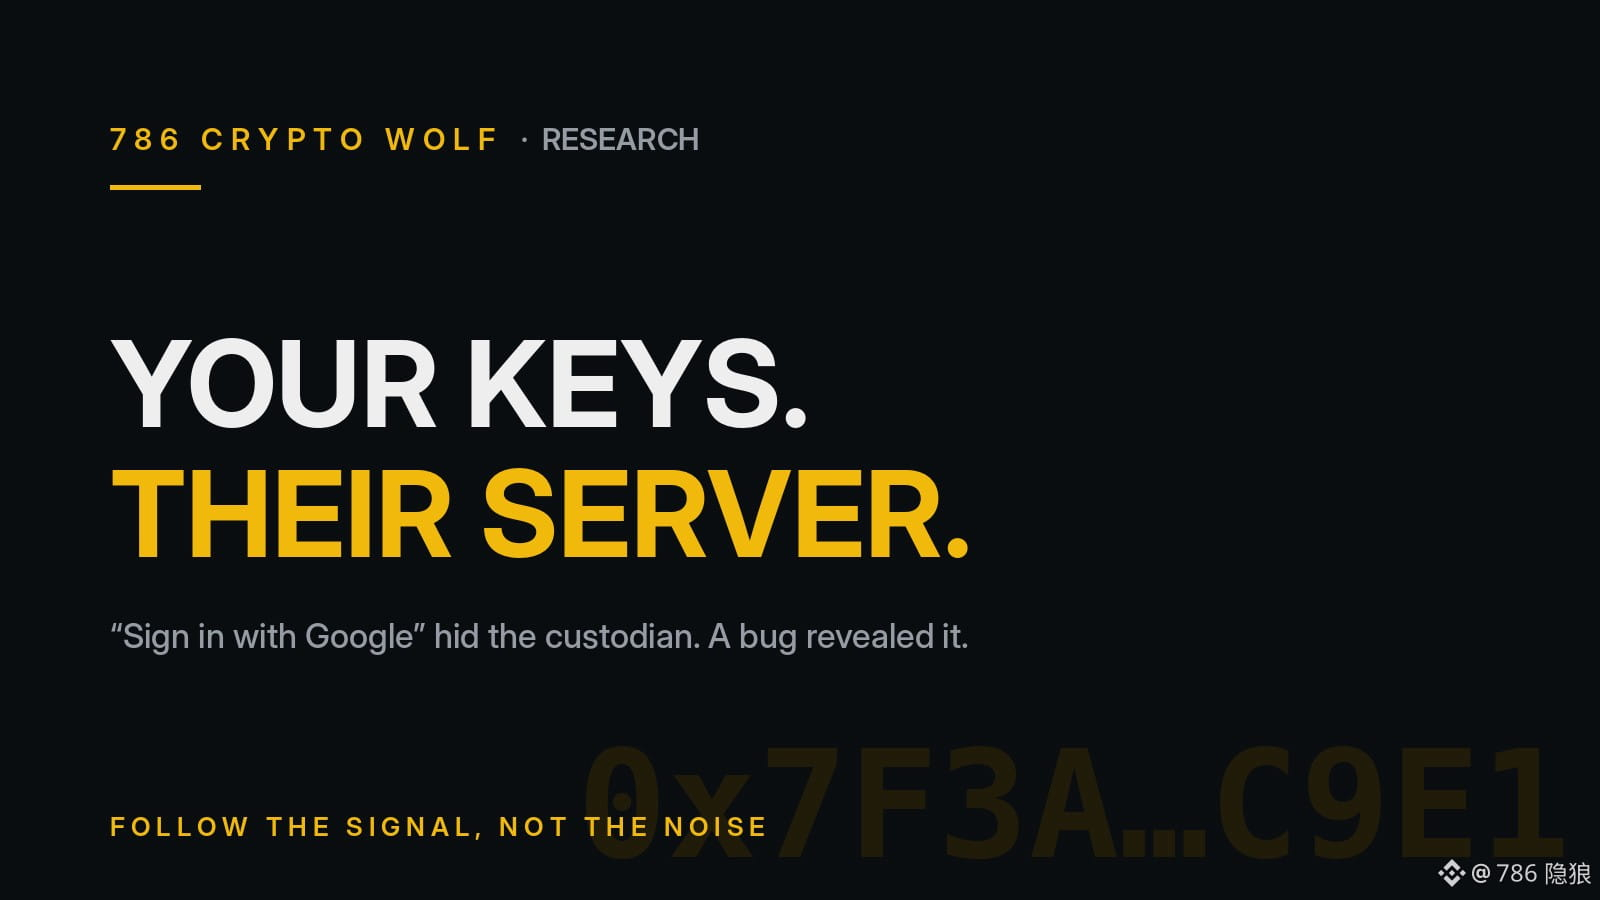
𝒀𝒐𝒖 𝒕𝒉𝒐𝒖𝒈𝒉𝒕 𝒚𝒐𝒖 𝒉𝒆𝒍𝒅 𝒚𝒐𝒖𝒓 𝒌𝒆𝒚𝒔. 𝑨 𝒃𝒖𝒈 𝒋𝒖𝒔𝒕 𝒑𝒓𝒐𝒗𝒆𝒅 𝒚𝒐𝒖 𝒅𝒊𝒅𝒏’𝒕.
This week, a flaw in Web3Auth exposed the private keys of users who signed into their wallets with a 𝐬𝐨𝐜𝐢𝐚𝐥 𝐥𝐨𝐠𝐢𝐧.Keplr told them to move their funds immediately.
No phishing. No leaked seed phrase. No careless click. Just a bug — in the “convenience” layer everyone told you was safe.
When a wallet lets you “sign in with Google,” it doesn’t remove the private key. 𝐈𝐭 𝐡𝐢𝐝𝐞𝐬 𝐢𝐭 —derived and managed through a company’s infrastructure you never audited.
You felt self-custodial. You were 𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐥 𝐰𝐢𝐭𝐡 𝐞𝐱𝐭𝐫𝐚 𝐬𝐭𝐞𝐩𝐬.
The seed phrase scared newcomers away, so the industry solved it by 𝐛𝐮𝐫𝐲𝐢𝐧𝐠 𝐭𝐡𝐞 𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐧, 𝐧𝐨𝐭 𝐫𝐞𝐦𝐨𝐯𝐢𝐧𝐠 𝐢𝐭.“Be your own bank” quietly became “trust our login.” And when their server has a bad week, the user who did everything right still has to race to save their own funds.
Self-custody protects your keys — 𝘰𝘯𝘭𝘺 𝘪𝘧 𝘵𝘩𝘦 𝘬𝘦𝘺𝘴 𝘸𝘦𝘳𝘦 𝘦𝘷𝘦𝘳 𝘢𝘤𝘵𝘶𝘢𝘭𝘭𝘺 𝘺𝘰𝘶𝘳𝘴.
𝐈𝐟 𝐚 𝐥𝐨𝐠𝐢𝐧 𝐛𝐮𝐠 𝐜𝐚𝐧 𝐥𝐞𝐚𝐤 𝐲𝐨𝐮𝐫 𝐩𝐫𝐢𝐯𝐚𝐭𝐞 𝐤𝐞𝐲, 𝐰𝐞𝐫𝐞 𝐲𝐨𝐮 𝐞𝐯𝐞𝐫 𝐬𝐞𝐥𝐟-𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐥 — 𝐨𝐫 𝐣𝐮𝐬𝐭 𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐥, 𝐰𝐢𝐭𝐡 𝐚 𝐧𝐢𝐜𝐞𝐫 𝐢𝐧𝐭𝐞𝐫𝐟𝐚𝐜𝐞?
🐺 𝟕𝟖𝟔 𝐂𝐑𝐘𝐏𝐓𝐎 𝐖𝐎𝐋𝐅 · 𝐑𝐄𝐒𝐄𝐀𝐑𝐂𝐇
Follow the signal, not the noise.
$BTC $ETH
#KeplrAdvisesSocialLoginUsersToTransferAssets
#SelfCustody #CryptoSecurity #Web3Auth #786CryptoWolf
𝒀𝒐𝒖 𝒕𝒉𝒐𝒖𝒈𝒉𝒕 𝒚𝒐𝒖 𝒉𝒆𝒍𝒅 𝒚𝒐𝒖𝒓 𝒌𝒆𝒚𝒔. 𝑨 𝒃𝒖𝒈 𝒋𝒖𝒔𝒕 𝒑𝒓𝒐𝒗𝒆𝒅 𝒚𝒐𝒖 𝒅𝒊𝒅𝒏’𝒕.
This week, a flaw in Web3Auth exposed the private keys of users who signed into their wallets with a 𝐬𝐨𝐜𝐢𝐚𝐥 𝐥𝐨𝐠𝐢𝐧.Keplr told them to move their funds immediately.
No phishing. No leaked seed phrase. No careless click. Just a bug — in the “convenience” layer everyone told you was safe.
When a wallet lets you “sign in with Google,” it doesn’t remove the private key. 𝐈𝐭 𝐡𝐢𝐝𝐞𝐬 𝐢𝐭 —derived and managed through a company’s infrastructure you never audited.
You felt self-custodial. You were 𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐥 𝐰𝐢𝐭𝐡 𝐞𝐱𝐭𝐫𝐚 𝐬𝐭𝐞𝐩𝐬.
The seed phrase scared newcomers away, so the industry solved it by 𝐛𝐮𝐫𝐲𝐢𝐧𝐠 𝐭𝐡𝐞 𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐧, 𝐧𝐨𝐭 𝐫𝐞𝐦𝐨𝐯𝐢𝐧𝐠 𝐢𝐭.“Be your own bank” quietly became “trust our login.” And when their server has a bad week, the user who did everything right still has to race to save their own funds.
Self-custody protects your keys — 𝘰𝘯𝘭𝘺 𝘪𝘧 𝘵𝘩𝘦 𝘬𝘦𝘺𝘴 𝘸𝘦𝘳𝘦 𝘦𝘷𝘦𝘳 𝘢𝘤𝘵𝘶𝘢𝘭𝘭𝘺 𝘺𝘰𝘶𝘳𝘴.
𝐈𝐟 𝐚 𝐥𝐨𝐠𝐢𝐧 𝐛𝐮𝐠 𝐜𝐚𝐧 𝐥𝐞𝐚𝐤 𝐲𝐨𝐮𝐫 𝐩𝐫𝐢𝐯𝐚𝐭𝐞 𝐤𝐞𝐲, 𝐰𝐞𝐫𝐞 𝐲𝐨𝐮 𝐞𝐯𝐞𝐫 𝐬𝐞𝐥𝐟-𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐥 — 𝐨𝐫 𝐣𝐮𝐬𝐭 𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐥, 𝐰𝐢𝐭𝐡 𝐚 𝐧𝐢𝐜𝐞𝐫 𝐢𝐧𝐭𝐞𝐫𝐟𝐚𝐜𝐞?
🐺 𝟕𝟖𝟔 𝐂𝐑𝐘𝐏𝐓𝐎 𝐖𝐎𝐋𝐅 · 𝐑𝐄𝐒𝐄𝐀𝐑𝐂𝐇
Follow the signal, not the noise.
$BTC $ETH
#KeplrAdvisesSocialLoginUsersToTransferAssets
#SelfCustody #CryptoSecurity #Web3Auth #786CryptoWolf
This week, a flaw in Web3Auth exposed the private keys of users who signed into their wallets with a 𝐬𝐨𝐜𝐢𝐚𝐥 𝐥𝐨𝐠𝐢𝐧.Keplr told them to move their funds immediately.
No phishing. No leaked seed phrase. No careless click. Just a bug — in the “convenience” layer everyone told you was safe.
When a wallet lets you “sign in with Google,” it doesn’t remove the private key. 𝐈𝐭 𝐡𝐢𝐝𝐞𝐬 𝐢𝐭 —derived and managed through a company’s infrastructure you never audited.
You felt self-custodial. You were 𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐥 𝐰𝐢𝐭𝐡 𝐞𝐱𝐭𝐫𝐚 𝐬𝐭𝐞𝐩𝐬.
The seed phrase scared newcomers away, so the industry solved it by 𝐛𝐮𝐫𝐲𝐢𝐧𝐠 𝐭𝐡𝐞 𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐧, 𝐧𝐨𝐭 𝐫𝐞𝐦𝐨𝐯𝐢𝐧𝐠 𝐢𝐭.“Be your own bank” quietly became “trust our login.” And when their server has a bad week, the user who did everything right still has to race to save their own funds.
Self-custody protects your keys — 𝘰𝘯𝘭𝘺 𝘪𝘧 𝘵𝘩𝘦 𝘬𝘦𝘺𝘴 𝘸𝘦𝘳𝘦 𝘦𝘷𝘦𝘳 𝘢𝘤𝘵𝘶𝘢𝘭𝘭𝘺 𝘺𝘰𝘶𝘳𝘴.
𝐈𝐟 𝐚 𝐥𝐨𝐠𝐢𝐧 𝐛𝐮𝐠 𝐜𝐚𝐧 𝐥𝐞𝐚𝐤 𝐲𝐨𝐮𝐫 𝐩𝐫𝐢𝐯𝐚𝐭𝐞 𝐤𝐞𝐲, 𝐰𝐞𝐫𝐞 𝐲𝐨𝐮 𝐞𝐯𝐞𝐫 𝐬𝐞𝐥𝐟-𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐥 — 𝐨𝐫 𝐣𝐮𝐬𝐭 𝐜𝐮𝐬𝐭𝐨𝐝𝐢𝐚𝐥, 𝐰𝐢𝐭𝐡 𝐚 𝐧𝐢𝐜𝐞𝐫 𝐢𝐧𝐭𝐞𝐫𝐟𝐚𝐜𝐞?
🐺 𝟕𝟖𝟔 𝐂𝐑𝐘𝐏𝐓𝐎 𝐖𝐎𝐋𝐅 · 𝐑𝐄𝐒𝐄𝐀𝐑𝐂𝐇
Follow the signal, not the noise.
$BTC $ETH
#KeplrAdvisesSocialLoginUsersToTransferAssets
#SelfCustody #CryptoSecurity #Web3Auth #786CryptoWolf
91
·
--
🚨 BREAKING: Keplr Advises Social Login Users To Transfer Assets
If you created your Keplr wallet with Google or Apple login, read this carefully. Your funds may be at risk right now.
Keplr has confirmed a vulnerability in Web3Auth's infrastructure exposed the private keys of some users who signed in through Google or Apple social login. Keplr has now suspended Google and Apple logins after reports of unauthorized transactions on Nov 6-7, with around $6M in unauthorized transfers traced and over 44,000 wallets reportedly affected.
Keplr is advising all social-login users to STOP depositing new funds into those wallets immediately, and to move any remaining transferable assets to a wallet created with a recovery phrase or a hardware wallet. Wallets created with a seed phrase or hardware wallet are NOT affected.
My analysis: Do not wait for an official recovery. Do not click any link in DM claiming to help you. Only use Keplr's official announcement. Create a new seed-phrase wallet, transfer in small test amount first, then move the rest.
Did you use Google / Apple login for Keplr? Comment YES or NO below.
#Keplr #KeplrWallet #CryptoSecurity #Web3Auth #BinanceSquare#keplradvisessocialloginuserstotransferassets
🚨 BREAKING: Keplr Advises Social Login Users To Transfer Assets
If you created your Keplr wallet with Google or Apple login, read this carefully. Your funds may be at risk right now.
Keplr has confirmed a vulnerability in Web3Auth's infrastructure exposed the private keys of some users who signed in through Google or Apple social login. Keplr has now suspended Google and Apple logins after reports of unauthorized transactions on Nov 6-7, with around $6M in unauthorized transfers traced and over 44,000 wallets reportedly affected.
Keplr is advising all social-login users to STOP depositing new funds into those wallets immediately, and to move any remaining transferable assets to a wallet created with a recovery phrase or a hardware wallet. Wallets created with a seed phrase or hardware wallet are NOT affected.
My analysis: Do not wait for an official recovery. Do not click any link in DM claiming to help you. Only use Keplr's official announcement. Create a new seed-phrase wallet, transfer in small test amount first, then move the rest.
Did you use Google / Apple login for Keplr? Comment YES or NO below.
#Keplr #KeplrWallet #CryptoSecurity #Web3Auth #BinanceSquare#keplradvisessocialloginuserstotransferassets
If you created your Keplr wallet with Google or Apple login, read this carefully. Your funds may be at risk right now.
Keplr has confirmed a vulnerability in Web3Auth's infrastructure exposed the private keys of some users who signed in through Google or Apple social login. Keplr has now suspended Google and Apple logins after reports of unauthorized transactions on Nov 6-7, with around $6M in unauthorized transfers traced and over 44,000 wallets reportedly affected.
Keplr is advising all social-login users to STOP depositing new funds into those wallets immediately, and to move any remaining transferable assets to a wallet created with a recovery phrase or a hardware wallet. Wallets created with a seed phrase or hardware wallet are NOT affected.
My analysis: Do not wait for an official recovery. Do not click any link in DM claiming to help you. Only use Keplr's official announcement. Create a new seed-phrase wallet, transfer in small test amount first, then move the rest.
Did you use Google / Apple login for Keplr? Comment YES or NO below.
#Keplr #KeplrWallet #CryptoSecurity #Web3Auth #BinanceSquare#keplradvisessocialloginuserstotransferassets
AAPL+0.63%
GOOGUS+1.25%
1
188
·
--
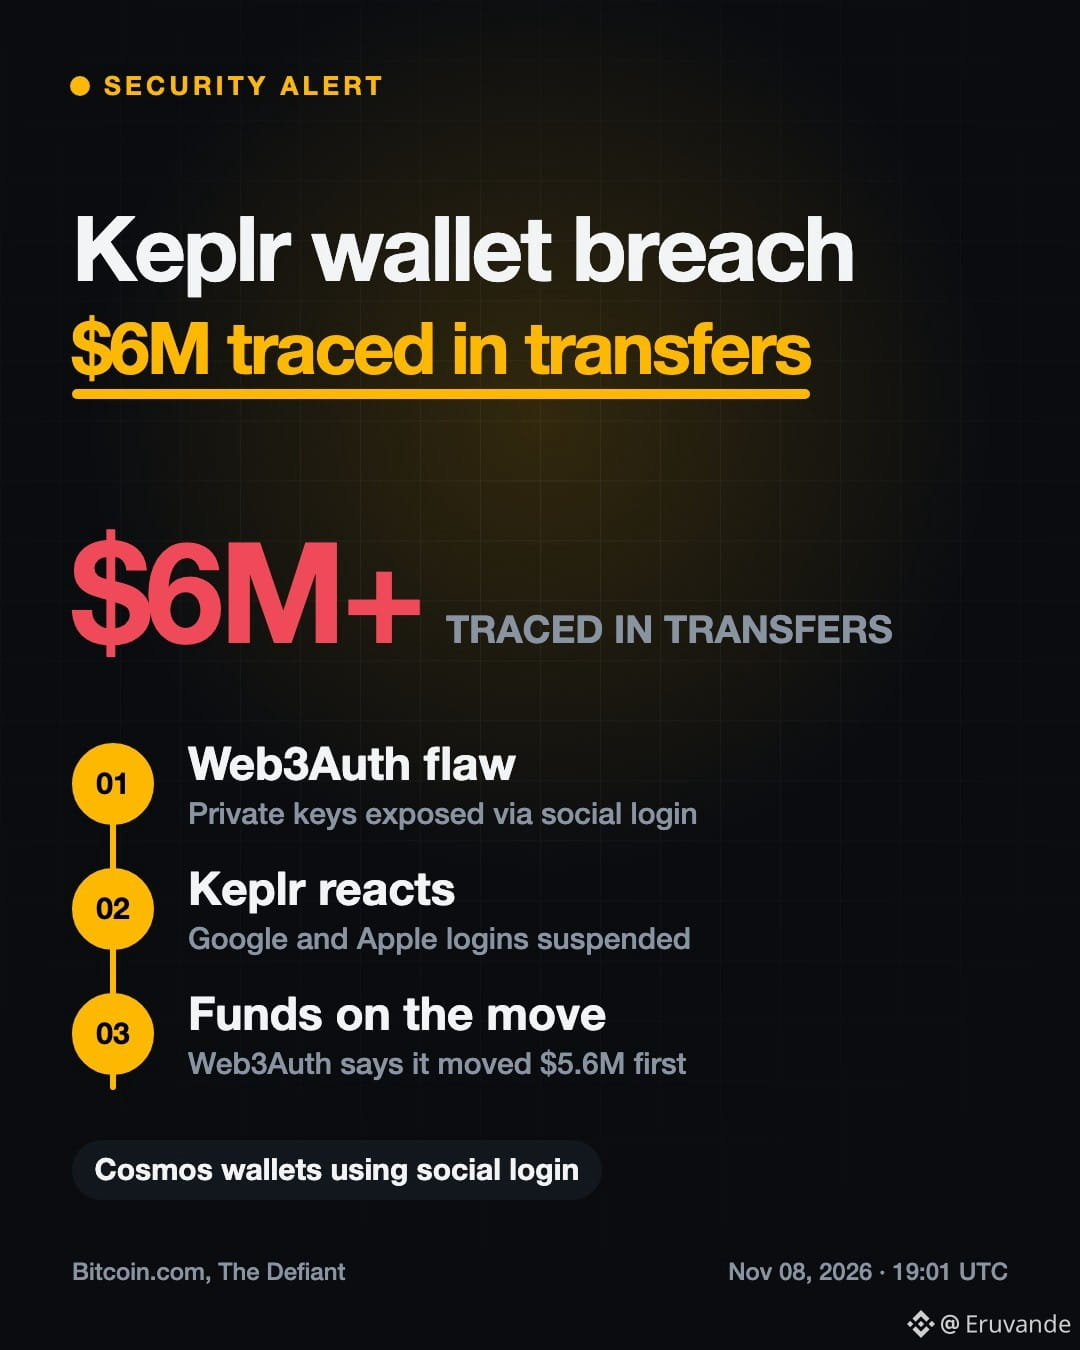
🚨 BREAKING: KEPLR SUSPENDS SOCIAL LOGINS AFTER WEB3AUTH BREACH
Private keys tied to Google and Apple logins were exposed. Investigators traced over $6M in transfers across Cosmos.
Web3Auth says it moved $5.6M out of exposed wallets first, but also mentioned an "original attacker."
$ATOM
If your Keplr wallet uses social login, would you move your funds tonight?
#KeplrAdvisesSocialLoginUsersToTransferAssets
🚨 BREAKING: KEPLR SUSPENDS SOCIAL LOGINS AFTER WEB3AUTH BREACH
Private keys tied to Google and Apple logins were exposed. Investigators traced over $6M in transfers across Cosmos.
Web3Auth says it moved $5.6M out of exposed wallets first, but also mentioned an "original attacker."
$ATOM
If your Keplr wallet uses social login, would you move your funds tonight?
#KeplrAdvisesSocialLoginUsersToTransferAssets
Private keys tied to Google and Apple logins were exposed. Investigators traced over $6M in transfers across Cosmos.
Web3Auth says it moved $5.6M out of exposed wallets first, but also mentioned an "original attacker."
$ATOM
If your Keplr wallet uses social login, would you move your funds tonight?
#KeplrAdvisesSocialLoginUsersToTransferAssets
15
·
--
Bullish
#KeplrAdvisesSocialLoginUsersToTransferAssets
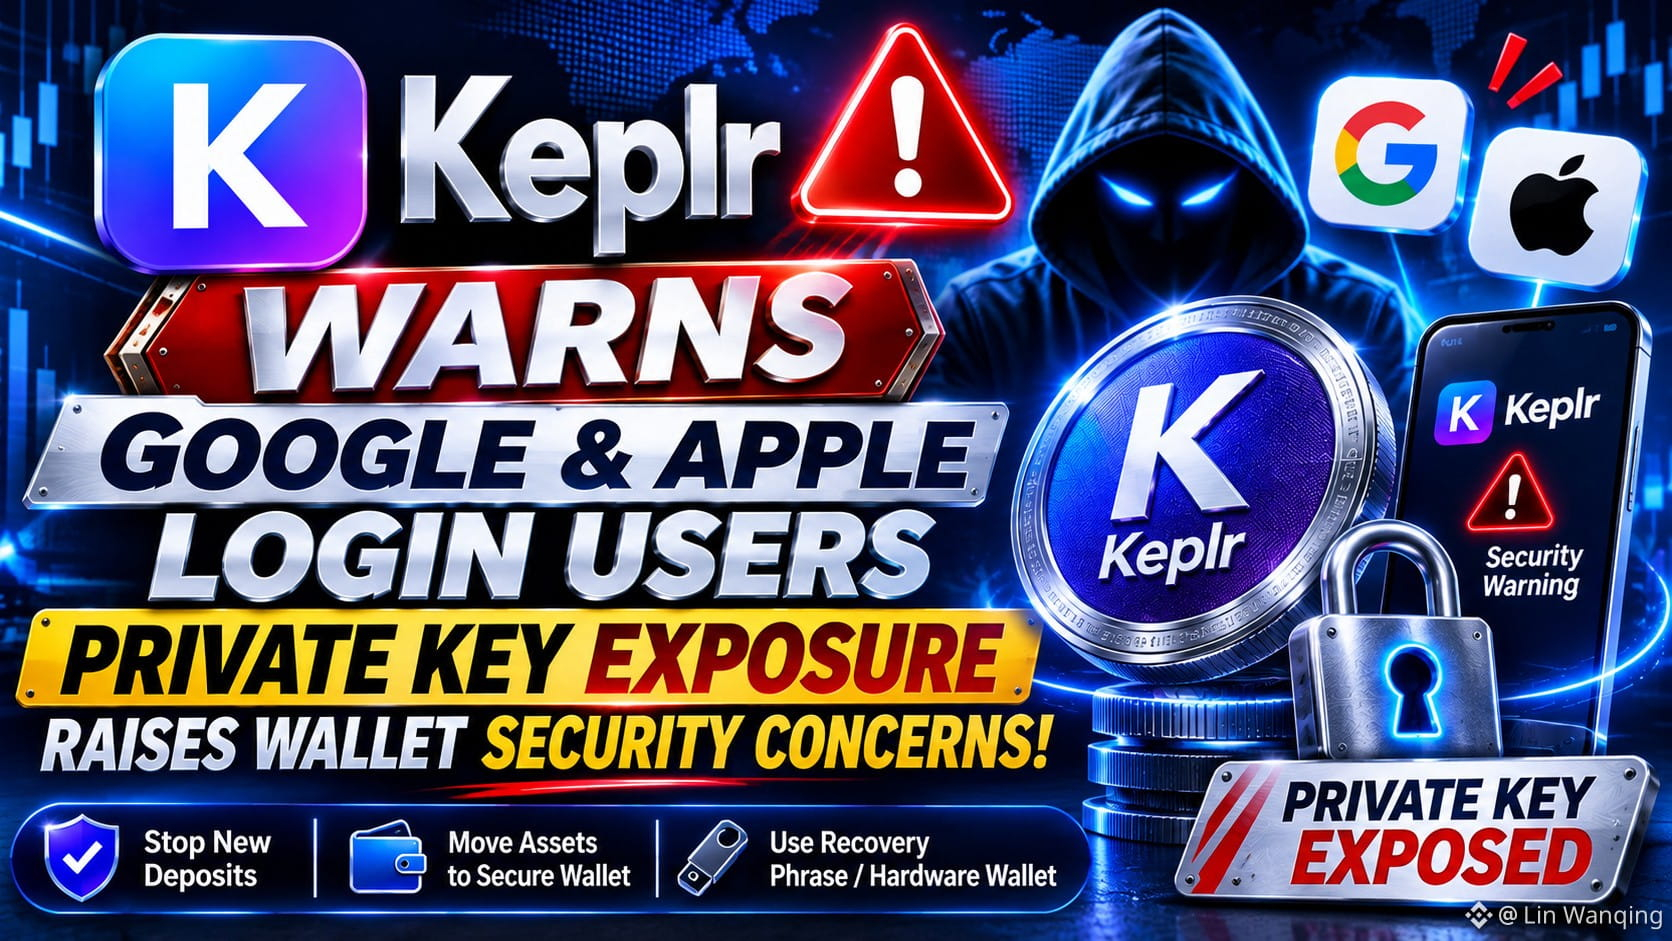
🚨 KEPLR WARNS SOCIAL LOGIN USERS — MOVE YOUR ASSETS!
Keplr Wallet has warned some users who created wallets through Google or Apple login after a Web3Auth vulnerability exposed private keys.
⚠️ What's Happening?
- Some social-login wallets may be affected.
- Users are advised to transfer assets to secure wallets.
- Recovery-phrase and hardware-wallet users are reportedly unaffected.
📊 Why It Matters:
This incident highlights the risks of third-party wallet infrastructure and the importance of secure self-custody.
💡 My Take:
Convenience should never come at the cost of security. Always understand how your wallet protects your private keys.
#Keplr #CryptoSecurity #Web3
$GOOGL $APR $UAI
{future}(UAIUSDT)
{future}(APRUSDT)
{future}(GOOGLUSDT)
#KeplrAdvisesSocialLoginUsersToTransferAssets
🚨 KEPLR WARNS SOCIAL LOGIN USERS — MOVE YOUR ASSETS!
Keplr Wallet has warned some users who created wallets through Google or Apple login after a Web3Auth vulnerability exposed private keys.
⚠️ What's Happening?
- Some social-login wallets may be affected.
- Users are advised to transfer assets to secure wallets.
- Recovery-phrase and hardware-wallet users are reportedly unaffected.
📊 Why It Matters:
This incident highlights the risks of third-party wallet infrastructure and the importance of secure self-custody.
💡 My Take:
Convenience should never come at the cost of security. Always understand how your wallet protects your private keys.
#Keplr #CryptoSecurity #Web3
$GOOGL $APR $UAI
🚨 KEPLR WARNS SOCIAL LOGIN USERS — MOVE YOUR ASSETS!
Keplr Wallet has warned some users who created wallets through Google or Apple login after a Web3Auth vulnerability exposed private keys.
⚠️ What's Happening?
- Some social-login wallets may be affected.
- Users are advised to transfer assets to secure wallets.
- Recovery-phrase and hardware-wallet users are reportedly unaffected.
📊 Why It Matters:
This incident highlights the risks of third-party wallet infrastructure and the importance of secure self-custody.
💡 My Take:
Convenience should never come at the cost of security. Always understand how your wallet protects your private keys.
#Keplr #CryptoSecurity #Web3
$GOOGL $APR $UAI
175
·
--
Bearish
#KeplrAdvisesSocialLoginUsersToTransferAssets
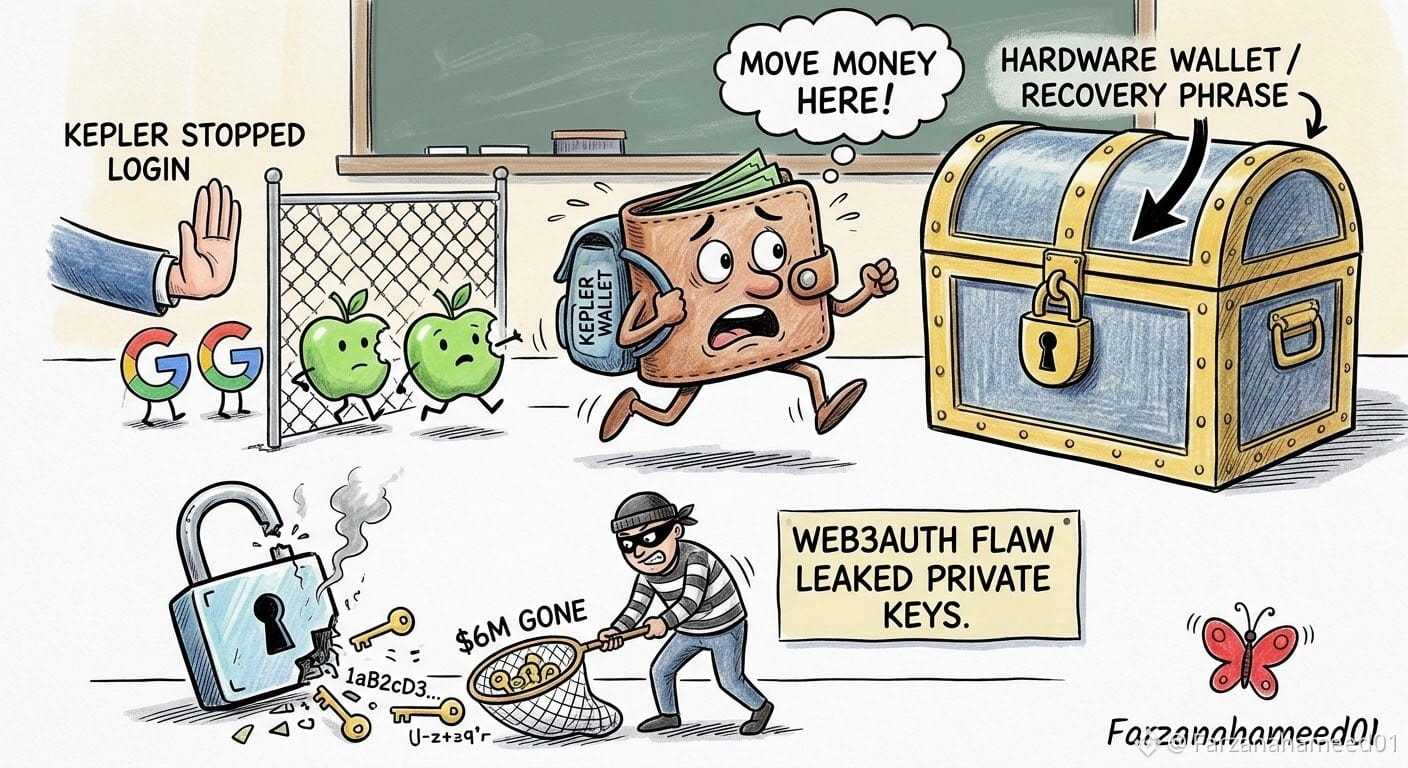
I THOUGHT GOOGLE LOGIN WAS SAFE. I WAS WRONG. 😱
I woke up and saw this!
Keplr Wallet stopped Google and Apple login! Because money went missing from some accounts!
There was a flaw in Web3Auth - it leaked the private keys of accounts made with Google and Apple!
Keplr is saying - do not send new money - move the remaining money to Recovery Phrase or Hardware Wallet!
ATOM- Keplr is a Cosmos wallet - its users are scared!
BTC - It is also watching this - because trust is broken!
What happened: $6M - Gone - 44,000 wallets!
Who is safe: Seed Phrase and Hardware - SAFE!
Who is not: Google and Apple Login - MAY BE AFFECTED!
So yeah, easy login is easy - but it is NOT safe. Your key is not in your hand.
Honestly, I thought Google login is the safest. But now I see - if you don't hold your key, someone else holds it.
Tell me honestly, do you use Google login or Seed Phrase for your wallet? 👇
$BTC $ATOM $ETH
#KeplrAdvisesSocialLoginUsersToTransferAssets #Wallets #Crypto
- 𝐅𝐚𝐫𝐳𝐚𝐧𝐚 𝐇𝐚𝐦𝐞𝐞𝐝 𝐎𝐟𝐟𝐢𝐜𝐢𝐚𝐥 • 🦋
#KeplrAdvisesSocialLoginUsersToTransferAssets
I THOUGHT GOOGLE LOGIN WAS SAFE. I WAS WRONG. 😱
I woke up and saw this!
Keplr Wallet stopped Google and Apple login! Because money went missing from some accounts!
There was a flaw in Web3Auth - it leaked the private keys of accounts made with Google and Apple!
Keplr is saying - do not send new money - move the remaining money to Recovery Phrase or Hardware Wallet!
ATOM- Keplr is a Cosmos wallet - its users are scared!
BTC - It is also watching this - because trust is broken!
What happened: $6M - Gone - 44,000 wallets!
Who is safe: Seed Phrase and Hardware - SAFE!
Who is not: Google and Apple Login - MAY BE AFFECTED!
So yeah, easy login is easy - but it is NOT safe. Your key is not in your hand.
Honestly, I thought Google login is the safest. But now I see - if you don't hold your key, someone else holds it.
Tell me honestly, do you use Google login or Seed Phrase for your wallet? 👇
$BTC $ATOM $ETH
#KeplrAdvisesSocialLoginUsersToTransferAssets #Wallets #Crypto
- 𝐅𝐚𝐫𝐳𝐚𝐧𝐚 𝐇𝐚𝐦𝐞𝐞𝐝 𝐎𝐟𝐟𝐢𝐜𝐢𝐚𝐥 • 🦋
I THOUGHT GOOGLE LOGIN WAS SAFE. I WAS WRONG. 😱
I woke up and saw this!
Keplr Wallet stopped Google and Apple login! Because money went missing from some accounts!
There was a flaw in Web3Auth - it leaked the private keys of accounts made with Google and Apple!
Keplr is saying - do not send new money - move the remaining money to Recovery Phrase or Hardware Wallet!
ATOM- Keplr is a Cosmos wallet - its users are scared!
BTC - It is also watching this - because trust is broken!
What happened: $6M - Gone - 44,000 wallets!
Who is safe: Seed Phrase and Hardware - SAFE!
Who is not: Google and Apple Login - MAY BE AFFECTED!
So yeah, easy login is easy - but it is NOT safe. Your key is not in your hand.
Honestly, I thought Google login is the safest. But now I see - if you don't hold your key, someone else holds it.
Tell me honestly, do you use Google login or Seed Phrase for your wallet? 👇
$BTC $ATOM $ETH
#KeplrAdvisesSocialLoginUsersToTransferAssets #Wallets #Crypto
- 𝐅𝐚𝐫𝐳𝐚𝐧𝐚 𝐇𝐚𝐦𝐞𝐞𝐝 𝐎𝐟𝐟𝐢𝐜𝐢𝐚𝐥 • 🦋
Vinhtocdo:
Cứ cụm từ hạt giống ghi ra giấy cho chắc 👍🌹$IDOL
3
8
293
#keplradvisessocialloginuserstotransferassets
🚨 Keplr Warns Social Login Users: Transfer Your Assets Before It's Too Late!
Keplr has issued an important warning to users who access their wallets through social login.
Users relying on social login should take action and transfer their assets to a securely backed-up wallet before they risk losing access.
🔍 What You Need to Know:
Social login users should review their wallet access immediately.
Make sure your recovery credentials and wallet backup are secure.
Transfer assets to a wallet where you control and safely store the recovery phrase.
Never share your seed phrase or private keys with anyone.
⚠️ Why It Matters:
Your crypto security depends on controlling access to your wallet. Losing access to a social login account could create serious problems if you haven't secured your wallet recovery options.
The message is simple: don't wait until you lose access to protect your funds.
#keplr #CryptoSecurity #WalletSafety
#keplradvisessocialloginuserstotransferassets
🚨 Keplr Warns Social Login Users: Transfer Your Assets Before It's Too Late!
Keplr has issued an important warning to users who access their wallets through social login.
Users relying on social login should take action and transfer their assets to a securely backed-up wallet before they risk losing access.
🔍 What You Need to Know:
Social login users should review their wallet access immediately.
Make sure your recovery credentials and wallet backup are secure.
Transfer assets to a wallet where you control and safely store the recovery phrase.
Never share your seed phrase or private keys with anyone.
⚠️ Why It Matters:
Your crypto security depends on controlling access to your wallet. Losing access to a social login account could create serious problems if you haven't secured your wallet recovery options.
The message is simple: don't wait until you lose access to protect your funds.
#keplr #CryptoSecurity #WalletSafety
🚨 Keplr Warns Social Login Users: Transfer Your Assets Before It's Too Late!
Keplr has issued an important warning to users who access their wallets through social login.
Users relying on social login should take action and transfer their assets to a securely backed-up wallet before they risk losing access.
🔍 What You Need to Know:
Social login users should review their wallet access immediately.
Make sure your recovery credentials and wallet backup are secure.
Transfer assets to a wallet where you control and safely store the recovery phrase.
Never share your seed phrase or private keys with anyone.
⚠️ Why It Matters:
Your crypto security depends on controlling access to your wallet. Losing access to a social login account could create serious problems if you haven't secured your wallet recovery options.
The message is simple: don't wait until you lose access to protect your funds.
#keplr #CryptoSecurity #WalletSafety
1
941
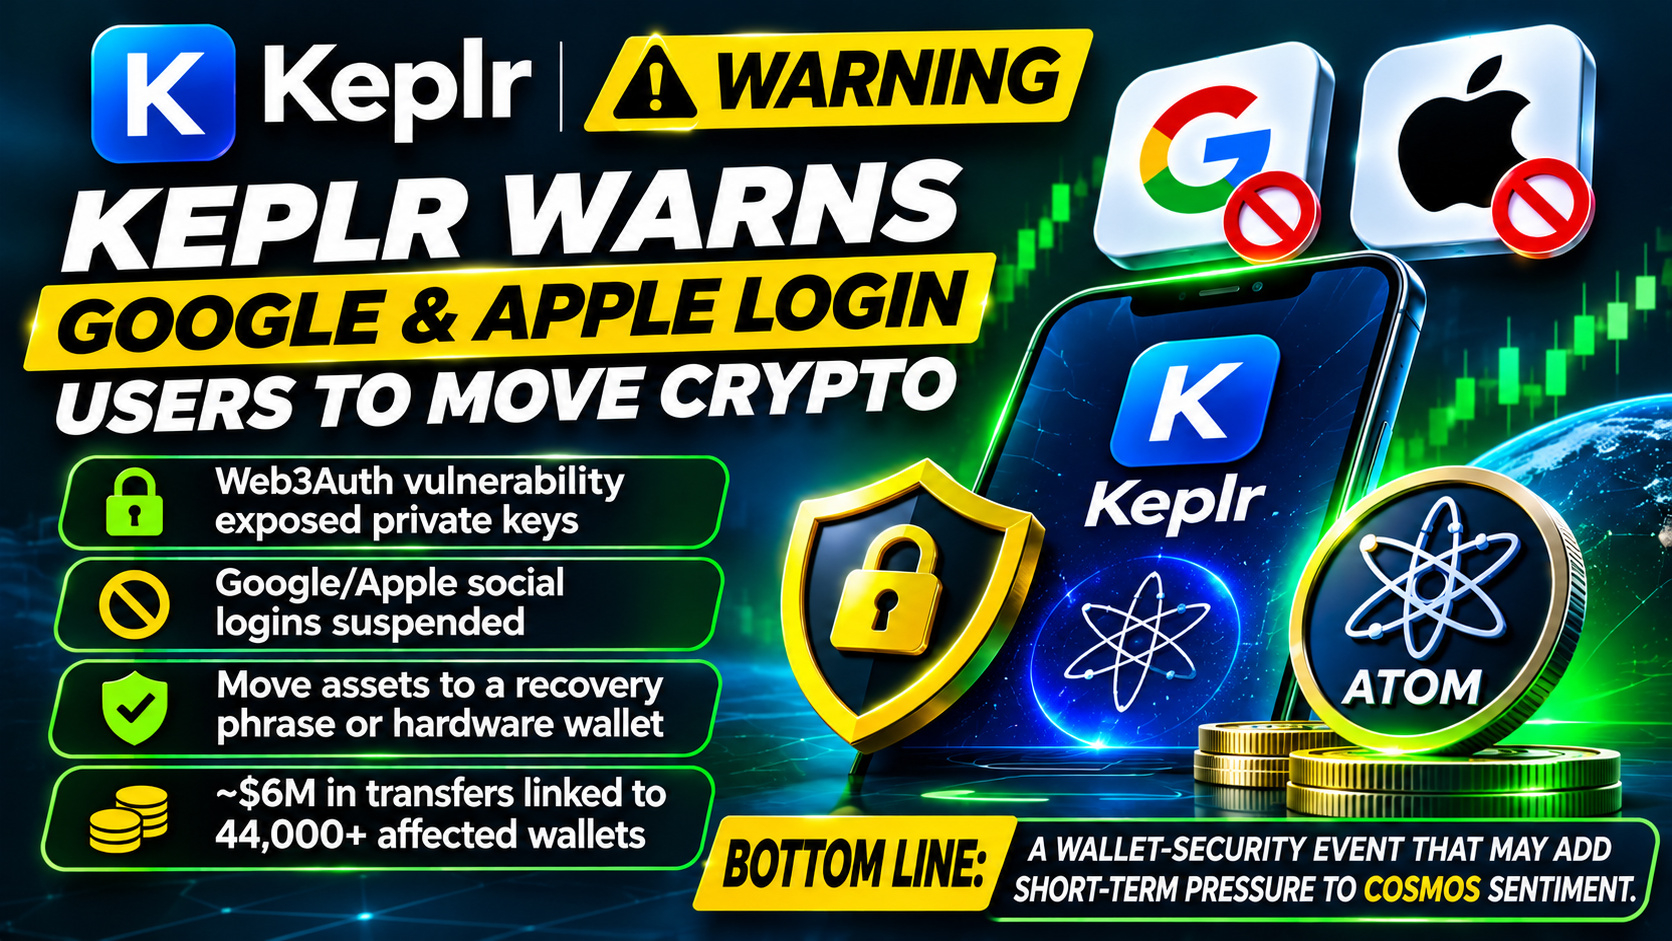
#KeplrAdvisesSocialLoginUsersToTransferAssets
🚨 Keplr Warns Google & Apple Login Users to Move Crypto Assets
Keplr Wallet has warned users who created wallets through Google or Apple social login after a vulnerability in Web3Auth infrastructure exposed private keys for some affected accounts. Keplr has suspended social logins and advised users not to deposit additional funds into potentially affected wallets.
🔐 Users with remaining liquid assets are being advised to move them to wallets secured by a recovery phrase or hardware wallet. Keplr says wallets created directly with mnemonic phrases or hardware wallets were not affected by this incident.
📊 On-chain analysis from Bitquery has linked at least $6 million in transfers to more than 44,000 affected wallets, although the final loss figure remains subject to clarification as some funds were moved as part of recovery efforts.
Bottom line: 🔴 This is primarily a wallet-security event, but it could increase caution around social-login wallets and add short-term pressure to sentiment across the Cosmos ecosystem.
#Keplr #Cosmos #ATOM #CryptoSecurity
$BEAT $EVAA $BEAT
{future}(UAIUSDT)
{future}(EVAAUSDT)
{future}(BEATUSDT)
#KeplrAdvisesSocialLoginUsersToTransferAssets
🚨 Keplr Warns Google & Apple Login Users to Move Crypto Assets
Keplr Wallet has warned users who created wallets through Google or Apple social login after a vulnerability in Web3Auth infrastructure exposed private keys for some affected accounts. Keplr has suspended social logins and advised users not to deposit additional funds into potentially affected wallets.
🔐 Users with remaining liquid assets are being advised to move them to wallets secured by a recovery phrase or hardware wallet. Keplr says wallets created directly with mnemonic phrases or hardware wallets were not affected by this incident.
📊 On-chain analysis from Bitquery has linked at least $6 million in transfers to more than 44,000 affected wallets, although the final loss figure remains subject to clarification as some funds were moved as part of recovery efforts.
Bottom line: 🔴 This is primarily a wallet-security event, but it could increase caution around social-login wallets and add short-term pressure to sentiment across the Cosmos ecosystem.
#Keplr #Cosmos #ATOM #CryptoSecurity
$BEAT $EVAA $BEAT
🚨 Keplr Warns Google & Apple Login Users to Move Crypto Assets
Keplr Wallet has warned users who created wallets through Google or Apple social login after a vulnerability in Web3Auth infrastructure exposed private keys for some affected accounts. Keplr has suspended social logins and advised users not to deposit additional funds into potentially affected wallets.
🔐 Users with remaining liquid assets are being advised to move them to wallets secured by a recovery phrase or hardware wallet. Keplr says wallets created directly with mnemonic phrases or hardware wallets were not affected by this incident.
📊 On-chain analysis from Bitquery has linked at least $6 million in transfers to more than 44,000 affected wallets, although the final loss figure remains subject to clarification as some funds were moved as part of recovery efforts.
Bottom line: 🔴 This is primarily a wallet-security event, but it could increase caution around social-login wallets and add short-term pressure to sentiment across the Cosmos ecosystem.
#Keplr #Cosmos #ATOM #CryptoSecurity
$BEAT $EVAA $BEAT
112
·
--
if your keplr wallet was made with a google or apple login, deal with that first today
keplr says a flaw at web3auth, the provider behind their social login, leaked keys for some of those accounts. social login is paused and users are told to move funds to a seed phrase or hardware wallet
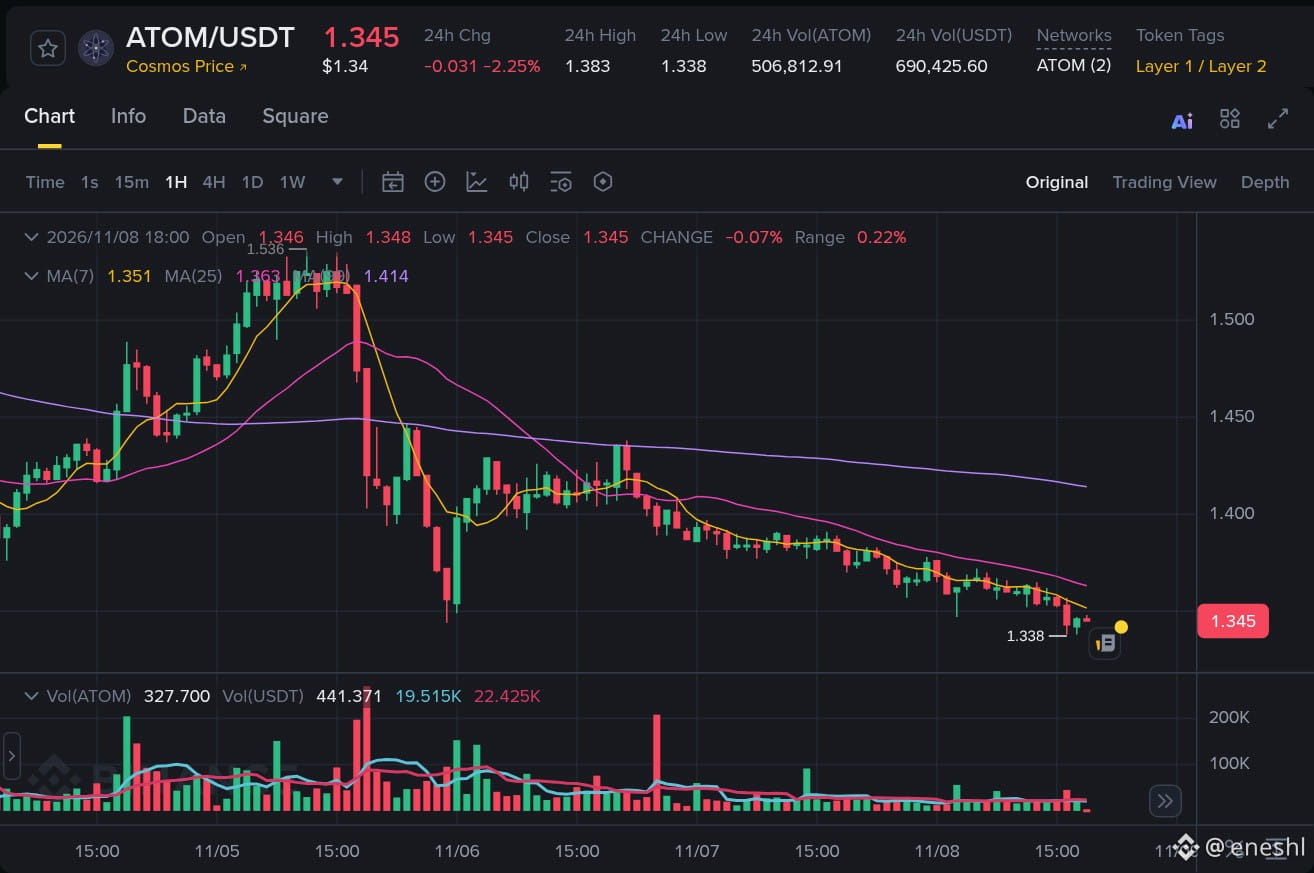
my read, this is less an $ATOM story and more a hit to easy onboarding. second order thing is staked funds, those take longer, so unbonding could drip supply out for weeks. flip side, it wasnt keplr's own code and if it stays contained it fades fast. $BTC didnt even blink
im watching atom's low from this afternoon, around 1.338
does that floor hold once unbonding starts landing, or get chipped away slowly ?
#KeplrAdvisesSocialLoginUsersToTransferAssets
if your keplr wallet was made with a google or apple login, deal with that first today
keplr says a flaw at web3auth, the provider behind their social login, leaked keys for some of those accounts. social login is paused and users are told to move funds to a seed phrase or hardware wallet
my read, this is less an $ATOM story and more a hit to easy onboarding. second order thing is staked funds, those take longer, so unbonding could drip supply out for weeks. flip side, it wasnt keplr's own code and if it stays contained it fades fast. $BTC didnt even blink
im watching atom's low from this afternoon, around 1.338
does that floor hold once unbonding starts landing, or get chipped away slowly ?
#KeplrAdvisesSocialLoginUsersToTransferAssets
keplr says a flaw at web3auth, the provider behind their social login, leaked keys for some of those accounts. social login is paused and users are told to move funds to a seed phrase or hardware wallet
my read, this is less an $ATOM story and more a hit to easy onboarding. second order thing is staked funds, those take longer, so unbonding could drip supply out for weeks. flip side, it wasnt keplr's own code and if it stays contained it fades fast. $BTC didnt even blink
im watching atom's low from this afternoon, around 1.338
does that floor hold once unbonding starts landing, or get chipped away slowly ?
#KeplrAdvisesSocialLoginUsersToTransferAssets
2
1.3k

·
--
Bullish
#keplradvisessocialloginuserstotransferassets
🚨 KEPLR & WEB3AUTH EXPLOIT: Over $6M Drained Across 44,000+ Social-Login Wallets! 🛡️⚡
Here is your short, trending market update covering the Keplr Security Breach, Web3Auth Infrastructure Vulnerability, On-Chain Metrics, & Custody Rules:
🔍 Incident Summary & On-Chain Impact
💥 Upstream Web3Auth Breach: Keplr suspended Google and Apple social-login functionality following a vulnerability in Web3Auth’s key-management infrastructure that exposed private keys.
📊 Bitquery Investigation Estimates: On-chain analytics indicate at least $6.01 million in assets drained across 44,000+ Cosmos ecosystem wallets, including over 1.96 million ATOM swept to attacker-controlled addresses.
🟢 Seed Phrase & Hardware Wallets Unaffected: Keplr confirmed that accounts created using traditional 12/24-word recovery phrases or Ledger/hardware devices remain completely secure and unaffected.
⚠️ Actionable Security Protocol for Affected Users
🚫 Halt All Deposits: Do not send fresh funds into any Keplr wallet originally generated via Google or Apple sign-in.
🔄 Transfer Liquid Assets: Safely move remaining funds to a newly created wallet backed by a physical seed phrase or hardware device following official Keplr guidance.
🛑 Beware of Scams: Ignore direct messages, unofficial "migration" links, or fake customer support teams claiming they can recover stolen assets.
💡 Market Takeaway: Convenience vs. True Self-Custody
⚖️ The Web3 Trade-Off: Multi-party computation (MPC) and social logins streamline user onboarding, but third-party key splitting exposes users to counterparty infrastructure risks.
$BNB
{future}(BNBUSDT)
🔐 Golden Custody Rule: For long-term holding, true self-custody via offline seed phrases or cold-storage hardware wallets remains the gold standard over convenience-first solutions! $ONE
{future}(ONEUSDT)
📊🛡️
$APP
{future}(APPUSDT)
#CPITestsDecemberRateOutlook #ARKPlans14ThematicETFsCoveringAIAndTokenizedMarkets #keplr #CryptoSecurity
#keplradvisessocialloginuserstotransferassets
🚨 KEPLR & WEB3AUTH EXPLOIT: Over $6M Drained Across 44,000+ Social-Login Wallets! 🛡️⚡
Here is your short, trending market update covering the Keplr Security Breach, Web3Auth Infrastructure Vulnerability, On-Chain Metrics, & Custody Rules:
🔍 Incident Summary & On-Chain Impact
💥 Upstream Web3Auth Breach: Keplr suspended Google and Apple social-login functionality following a vulnerability in Web3Auth’s key-management infrastructure that exposed private keys.
📊 Bitquery Investigation Estimates: On-chain analytics indicate at least $6.01 million in assets drained across 44,000+ Cosmos ecosystem wallets, including over 1.96 million ATOM swept to attacker-controlled addresses.
🟢 Seed Phrase & Hardware Wallets Unaffected: Keplr confirmed that accounts created using traditional 12/24-word recovery phrases or Ledger/hardware devices remain completely secure and unaffected.
⚠️ Actionable Security Protocol for Affected Users
🚫 Halt All Deposits: Do not send fresh funds into any Keplr wallet originally generated via Google or Apple sign-in.
🔄 Transfer Liquid Assets: Safely move remaining funds to a newly created wallet backed by a physical seed phrase or hardware device following official Keplr guidance.
🛑 Beware of Scams: Ignore direct messages, unofficial "migration" links, or fake customer support teams claiming they can recover stolen assets.
💡 Market Takeaway: Convenience vs. True Self-Custody
⚖️ The Web3 Trade-Off: Multi-party computation (MPC) and social logins streamline user onboarding, but third-party key splitting exposes users to counterparty infrastructure risks.
$BNB
🔐 Golden Custody Rule: For long-term holding, true self-custody via offline seed phrases or cold-storage hardware wallets remains the gold standard over convenience-first solutions! $ONE
📊🛡️
$APP
#CPITestsDecemberRateOutlook #ARKPlans14ThematicETFsCoveringAIAndTokenizedMarkets #keplr #CryptoSecurity
🚨 KEPLR & WEB3AUTH EXPLOIT: Over $6M Drained Across 44,000+ Social-Login Wallets! 🛡️⚡
Here is your short, trending market update covering the Keplr Security Breach, Web3Auth Infrastructure Vulnerability, On-Chain Metrics, & Custody Rules:
🔍 Incident Summary & On-Chain Impact
💥 Upstream Web3Auth Breach: Keplr suspended Google and Apple social-login functionality following a vulnerability in Web3Auth’s key-management infrastructure that exposed private keys.
📊 Bitquery Investigation Estimates: On-chain analytics indicate at least $6.01 million in assets drained across 44,000+ Cosmos ecosystem wallets, including over 1.96 million ATOM swept to attacker-controlled addresses.
🟢 Seed Phrase & Hardware Wallets Unaffected: Keplr confirmed that accounts created using traditional 12/24-word recovery phrases or Ledger/hardware devices remain completely secure and unaffected.
⚠️ Actionable Security Protocol for Affected Users
🚫 Halt All Deposits: Do not send fresh funds into any Keplr wallet originally generated via Google or Apple sign-in.
🔄 Transfer Liquid Assets: Safely move remaining funds to a newly created wallet backed by a physical seed phrase or hardware device following official Keplr guidance.
🛑 Beware of Scams: Ignore direct messages, unofficial "migration" links, or fake customer support teams claiming they can recover stolen assets.
💡 Market Takeaway: Convenience vs. True Self-Custody
⚖️ The Web3 Trade-Off: Multi-party computation (MPC) and social logins streamline user onboarding, but third-party key splitting exposes users to counterparty infrastructure risks.
$BNB
🔐 Golden Custody Rule: For long-term holding, true self-custody via offline seed phrases or cold-storage hardware wallets remains the gold standard over convenience-first solutions! $ONE
📊🛡️
$APP
#CPITestsDecemberRateOutlook #ARKPlans14ThematicETFsCoveringAIAndTokenizedMarkets #keplr #CryptoSecurity
2
1k
⚠️ Don't Ignore Your Wallet Security
Social login makes wallet access convenient, but users should understand how their assets are secured. Keplr's latest advisory is a reminder to review wallet arrangements and follow official migration instructions. $ATOM $BTC $ETH
#keplradvisessocialloginuserstotransferassets
⚠️ Don't Ignore Your Wallet Security
Social login makes wallet access convenient, but users should understand how their assets are secured. Keplr's latest advisory is a reminder to review wallet arrangements and follow official migration instructions. $ATOM $BTC $ETH
#keplradvisessocialloginuserstotransferassets
Social login makes wallet access convenient, but users should understand how their assets are secured. Keplr's latest advisory is a reminder to review wallet arrangements and follow official migration instructions. $ATOM $BTC $ETH
#keplradvisessocialloginuserstotransferassets
1
140
·
--
Article
Keplr Wallet Security Alert: $6 Million Crypto Drain Raises Questions — What Should $ONE and $AIN InMore than $6 million in crypto assets, tens of thousands of affected wallets, and a security failure involving private keys. The Keplr incident is a serious reminder that crypto investors can lose confidence in an ecosystem long before its token price reflects the damage.
On November 7–8, 2026, Keplr warned users who created wallets through Google or Apple social login to move their remaining liquid assets into wallets secured by recovery phrases or hardware devices.
The problem originated from a security vulnerability in Web3Auth, the infrastructure provider behind Keplr's social-login wallet functionality.
According to Bitquery's on-chain investigation, at least 44,041 wallets across seven Cosmos chains were drained, with another estimated 7,603 Injective wallets affected. The identified stolen assets were worth approximately $6.01 million at the time of its analysis.
One detail makes this incident particularly concerning: Bitquery reported that approximately 86% of the affected wallets on the seven chains were drained after Keplr had already issued its warning.
Keplr and Web3Auth also began recovery and asset-protection efforts. Some affected accounts may show reduced or zero balances as a result of these measures.
For investors, this raises an important question: could a security incident of this scale change how the market values smaller crypto projects?
First, Understand the Exposure
Before looking at individual tokens, there is an important distinction.
ONE (Harmony) and AIN (Infinity Ground) are not confirmed victims of the Keplr incident. Neither should be presented as directly compromised.
However, their prices can still be influenced by broader market sentiment, liquidity conditions and changes in speculative capital flows.
Let's examine their individual investment cases.
1. ONE (Harmony): A Sharp Rally, But Is It Sustainable?
<badge color="success">High-risk speculative setup</badge>
Harmony's native token ONE has attracted attention following a substantial price recovery.
According to the latest CoinMarketCap snapshot retrieved for November 8:
- Price: Approximately $0.001854
- Market capitalization: Approximately $30.46 million
- 24-hour trading volume: Approximately $146.83 million
- 24-hour range: $0.001791–$0.002443
The seven-day performance shown by CoinGecko was approximately +66.5%.
That is a strong move for a relatively small-cap asset. But I would be careful about interpreting it as the beginning of a long-term bull trend.
The reported trading volume is also unusually large relative to market capitalization. Traders should check whether that activity represents genuine spot demand or is heavily influenced by derivatives and exchange-specific turnover.
Technical levels to monitor:
- Near-term support: $0.00179–$0.00180
- Resistance: $0.00240–$0.00245
- Bullish confirmation: A sustained move above resistance with strong spot volume.
- Bearish warning: A breakdown below the recent trading range.
My strategy would be to wait for a breakout and retest rather than buying after an extended rally.
Harmony also needs stronger evidence of sustained ecosystem activity to support a longer-term investment thesis.
Investor outlook: ONE offers a speculative recovery opportunity, but volatility and weak fundamental confirmation make aggressive accumulation difficult to justify.
2. OPENAI: A Serious Verification Warning
<badge color="danger">Avoid unverified tokens</badge>
The OPENAI ticker requires a different approach.
OpenAI has not officially launched a cryptocurrency token. In September 2024, scammers compromised an OpenAI-associated X account and used it to promote a fake OPENAI token and phishing website.
There are also exchange-listed derivative products using the OPENAI ticker. These are not OpenAI-issued blockchain tokens and do not represent ownership in the company.
For investors, the distinction is critical.
Before considering anything marketed as OPENAI, verify:
- Whether it is an actual blockchain token or an exchange derivative.
- Its exact contract address, if applicable.
- The exchange and trading instrument.
- Liquidity and counterparty risks.
- Whether any claimed OpenAI association is officially documented.
Investor outlook: I would not issue a bullish price target for OPENAI without identifying the exact asset. A famous company name is not a substitute for legitimate fundamentals.
3. AIN (Infinity Ground): Can AI Demand Support Further Growth?
<badge color="success">Speculative AI exposure</badge>
Infinity Ground's AIN offers a different investment narrative.
The project operates in the AI and blockchain application development sector. Its token is associated with platform services, ecosystem participation and planned utility features.
The latest CoinMarketCap snapshot showed:
- Price: Approximately $0.1419
- Market capitalization: Approximately $45.27 million
- 24-hour trading volume: Approximately $12.74 million
- 24-hour change: +9.21%
- Maximum supply: 1 billion AIN
- 24-hour range: $0.1234–$0.1715
However, there is an important supply-related issue.
CoinGecko and CoinMarketCap currently show different circulating-supply figures. Therefore, I would not use a precise circulating percentage to make an investment decision until that discrepancy is resolved.
Another important signal is the recent price correction. CoinMarketCap's snapshot placed AIN approximately 55% below its November 5 all-time high of $0.3278.
This suggests that volatility remains substantial despite the renewed AI narrative.
What I would monitor:
- Whether buyers defend the $0.1234–$0.13 area.
- Whether price can reclaim the $0.17 region.
- Whether trading volume supports a sustained recovery.
- Token unlocks and future supply distribution.
- Real ecosystem adoption rather than social-media attention.
Investor outlook: AIN has exposure to an attractive AI-related market narrative, but the recent correction and supply-data discrepancy justify caution. I would prefer confirmation of a recovery before increasing exposure.
Which Asset Offers the Better Risk-to-Reward Setup?
These three symbols should not be treated as equivalent investments.
Asset| Investment case| Main concern
ONE| Speculative recovery| Volatility and ecosystem fundamentals
OPENAI| Requires asset verification| No official OpenAI token
AIN| AI-sector speculation| Supply transparency and price volatility
My preference would be to monitor $ONE and $AIN for technical confirmation while avoiding any unverified $OPENAI token.
I would also avoid using the Keplr incident itself as a reason to buy either ONE or AIN. Neither token has been established as a direct beneficiary of the security event.
My Trading Strategy: Protect Capital First
In this type of market, chasing momentum is usually more dangerous than missing an entry.
I would follow a few basic rules:
- Wait for volume-confirmed breakouts.
- Avoid buying after unusually large price candles.
- Keep position sizes small in low-cap assets.
- Check spot liquidity before entering.
- Monitor funding rates and open interest.
- Use predefined stop-loss levels.
- Avoid excessive leverage during uncertain market conditions.
The objective is not to catch every rally. It is to enter trades where the potential reward justifies the downside risk.
Final Investor Takeaway
The Keplr incident highlights how quickly security problems can damage confidence in crypto infrastructure.
For ONE, the focus should be on whether its recent rally can develop into a sustainable recovery.
For AIN, the AI narrative is worth watching, but token supply transparency and actual ecosystem demand remain important.
As for OPENAI, investors should first establish exactly what they are trading. There is no official OpenAI-issued cryptocurrency token.
My approach is simple: follow the liquidity, verify the fundamentals and never confuse market hype with genuine investment value.
Do you think ONE and AIN have enough momentum to sustain their current recovery, or will investors become more selective as security concerns grow across the crypto market?
Share your market outlook in the comments.
Disclaimer: This article is for educational and informational purposes only. It is not financial advice. Market prices and trading levels are snapshots, not guaranteed entry points. Always verify token contracts, supply data and liquidity before investing. DYOR. NFA.
{future}(AINUSDT)
{spot}(ONEUSDT)
{future}(OPENAIUSDT)
#KeplrAdvisesSocialLoginUsersToTransferAssets #CryptoAnalysis #CryptocurrencyWealth #Binance #cryptouniverseofficial
Keplr Wallet Security Alert: $6 Million Crypto Drain Raises Questions — What Should $ONE and $AIN In
More than $6 million in crypto assets, tens of thousands of affected wallets, and a security failure involving private keys. The Keplr incident is a serious reminder that crypto investors can lose confidence in an ecosystem long before its token price reflects the damage.
On November 7–8, 2026, Keplr warned users who created wallets through Google or Apple social login to move their remaining liquid assets into wallets secured by recovery phrases or hardware devices.
The problem originated from a security vulnerability in Web3Auth, the infrastructure provider behind Keplr's social-login wallet functionality.
According to Bitquery's on-chain investigation, at least 44,041 wallets across seven Cosmos chains were drained, with another estimated 7,603 Injective wallets affected. The identified stolen assets were worth approximately $6.01 million at the time of its analysis.
One detail makes this incident particularly concerning: Bitquery reported that approximately 86% of the affected wallets on the seven chains were drained after Keplr had already issued its warning.
Keplr and Web3Auth also began recovery and asset-protection efforts. Some affected accounts may show reduced or zero balances as a result of these measures.
For investors, this raises an important question: could a security incident of this scale change how the market values smaller crypto projects?
First, Understand the Exposure
Before looking at individual tokens, there is an important distinction.
ONE (Harmony) and AIN (Infinity Ground) are not confirmed victims of the Keplr incident. Neither should be presented as directly compromised.
However, their prices can still be influenced by broader market sentiment, liquidity conditions and changes in speculative capital flows.
Let's examine their individual investment cases.
1. ONE (Harmony): A Sharp Rally, But Is It Sustainable?
<badge color="success">High-risk speculative setup</badge>
Harmony's native token ONE has attracted attention following a substantial price recovery.
According to the latest CoinMarketCap snapshot retrieved for November 8:
- Price: Approximately $0.001854
- Market capitalization: Approximately $30.46 million
- 24-hour trading volume: Approximately $146.83 million
- 24-hour range: $0.001791–$0.002443
The seven-day performance shown by CoinGecko was approximately +66.5%.
That is a strong move for a relatively small-cap asset. But I would be careful about interpreting it as the beginning of a long-term bull trend.
The reported trading volume is also unusually large relative to market capitalization. Traders should check whether that activity represents genuine spot demand or is heavily influenced by derivatives and exchange-specific turnover.
Technical levels to monitor:
- Near-term support: $0.00179–$0.00180
- Resistance: $0.00240–$0.00245
- Bullish confirmation: A sustained move above resistance with strong spot volume.
- Bearish warning: A breakdown below the recent trading range.
My strategy would be to wait for a breakout and retest rather than buying after an extended rally.
Harmony also needs stronger evidence of sustained ecosystem activity to support a longer-term investment thesis.
Investor outlook: ONE offers a speculative recovery opportunity, but volatility and weak fundamental confirmation make aggressive accumulation difficult to justify.
2. OPENAI: A Serious Verification Warning
<badge color="danger">Avoid unverified tokens</badge>
The OPENAI ticker requires a different approach.
OpenAI has not officially launched a cryptocurrency token. In September 2024, scammers compromised an OpenAI-associated X account and used it to promote a fake OPENAI token and phishing website.
There are also exchange-listed derivative products using the OPENAI ticker. These are not OpenAI-issued blockchain tokens and do not represent ownership in the company.
For investors, the distinction is critical.
Before considering anything marketed as OPENAI, verify:
- Whether it is an actual blockchain token or an exchange derivative.
- Its exact contract address, if applicable.
- The exchange and trading instrument.
- Liquidity and counterparty risks.
- Whether any claimed OpenAI association is officially documented.
Investor outlook: I would not issue a bullish price target for OPENAI without identifying the exact asset. A famous company name is not a substitute for legitimate fundamentals.
3. AIN (Infinity Ground): Can AI Demand Support Further Growth?
<badge color="success">Speculative AI exposure</badge>
Infinity Ground's AIN offers a different investment narrative.
The project operates in the AI and blockchain application development sector. Its token is associated with platform services, ecosystem participation and planned utility features.
The latest CoinMarketCap snapshot showed:
- Price: Approximately $0.1419
- Market capitalization: Approximately $45.27 million
- 24-hour trading volume: Approximately $12.74 million
- 24-hour change: +9.21%
- Maximum supply: 1 billion AIN
- 24-hour range: $0.1234–$0.1715
However, there is an important supply-related issue.
CoinGecko and CoinMarketCap currently show different circulating-supply figures. Therefore, I would not use a precise circulating percentage to make an investment decision until that discrepancy is resolved.
Another important signal is the recent price correction. CoinMarketCap's snapshot placed AIN approximately 55% below its November 5 all-time high of $0.3278.
This suggests that volatility remains substantial despite the renewed AI narrative.
What I would monitor:
- Whether buyers defend the $0.1234–$0.13 area.
- Whether price can reclaim the $0.17 region.
- Whether trading volume supports a sustained recovery.
- Token unlocks and future supply distribution.
- Real ecosystem adoption rather than social-media attention.
Investor outlook: AIN has exposure to an attractive AI-related market narrative, but the recent correction and supply-data discrepancy justify caution. I would prefer confirmation of a recovery before increasing exposure.
Which Asset Offers the Better Risk-to-Reward Setup?
These three symbols should not be treated as equivalent investments.
Asset| Investment case| Main concern
ONE| Speculative recovery| Volatility and ecosystem fundamentals
OPENAI| Requires asset verification| No official OpenAI token
AIN| AI-sector speculation| Supply transparency and price volatility
My preference would be to monitor $ONE and $AIN for technical confirmation while avoiding any unverified $OPENAI token.
I would also avoid using the Keplr incident itself as a reason to buy either ONE or AIN. Neither token has been established as a direct beneficiary of the security event.
My Trading Strategy: Protect Capital First
In this type of market, chasing momentum is usually more dangerous than missing an entry.
I would follow a few basic rules:
- Wait for volume-confirmed breakouts.
- Avoid buying after unusually large price candles.
- Keep position sizes small in low-cap assets.
- Check spot liquidity before entering.
- Monitor funding rates and open interest.
- Use predefined stop-loss levels.
- Avoid excessive leverage during uncertain market conditions.
The objective is not to catch every rally. It is to enter trades where the potential reward justifies the downside risk.
Final Investor Takeaway
The Keplr incident highlights how quickly security problems can damage confidence in crypto infrastructure.
For ONE, the focus should be on whether its recent rally can develop into a sustainable recovery.
For AIN, the AI narrative is worth watching, but token supply transparency and actual ecosystem demand remain important.
As for OPENAI, investors should first establish exactly what they are trading. There is no official OpenAI-issued cryptocurrency token.
My approach is simple: follow the liquidity, verify the fundamentals and never confuse market hype with genuine investment value.
Do you think ONE and AIN have enough momentum to sustain their current recovery, or will investors become more selective as security concerns grow across the crypto market?
Share your market outlook in the comments.
Disclaimer: This article is for educational and informational purposes only. It is not financial advice. Market prices and trading levels are snapshots, not guaranteed entry points. Always verify token contracts, supply data and liquidity before investing. DYOR. NFA.
#KeplrAdvisesSocialLoginUsersToTransferAssets #CryptoAnalysis #CryptocurrencyWealth #Binance #cryptouniverseofficial
On November 7–8, 2026, Keplr warned users who created wallets through Google or Apple social login to move their remaining liquid assets into wallets secured by recovery phrases or hardware devices.
The problem originated from a security vulnerability in Web3Auth, the infrastructure provider behind Keplr's social-login wallet functionality.
According to Bitquery's on-chain investigation, at least 44,041 wallets across seven Cosmos chains were drained, with another estimated 7,603 Injective wallets affected. The identified stolen assets were worth approximately $6.01 million at the time of its analysis.
One detail makes this incident particularly concerning: Bitquery reported that approximately 86% of the affected wallets on the seven chains were drained after Keplr had already issued its warning.
Keplr and Web3Auth also began recovery and asset-protection efforts. Some affected accounts may show reduced or zero balances as a result of these measures.
For investors, this raises an important question: could a security incident of this scale change how the market values smaller crypto projects?
First, Understand the Exposure
Before looking at individual tokens, there is an important distinction.
ONE (Harmony) and AIN (Infinity Ground) are not confirmed victims of the Keplr incident. Neither should be presented as directly compromised.
However, their prices can still be influenced by broader market sentiment, liquidity conditions and changes in speculative capital flows.
Let's examine their individual investment cases.
1. ONE (Harmony): A Sharp Rally, But Is It Sustainable?
<badge color="success">High-risk speculative setup</badge>
Harmony's native token ONE has attracted attention following a substantial price recovery.
According to the latest CoinMarketCap snapshot retrieved for November 8:
- Price: Approximately $0.001854
- Market capitalization: Approximately $30.46 million
- 24-hour trading volume: Approximately $146.83 million
- 24-hour range: $0.001791–$0.002443
The seven-day performance shown by CoinGecko was approximately +66.5%.
That is a strong move for a relatively small-cap asset. But I would be careful about interpreting it as the beginning of a long-term bull trend.
The reported trading volume is also unusually large relative to market capitalization. Traders should check whether that activity represents genuine spot demand or is heavily influenced by derivatives and exchange-specific turnover.
Technical levels to monitor:
- Near-term support: $0.00179–$0.00180
- Resistance: $0.00240–$0.00245
- Bullish confirmation: A sustained move above resistance with strong spot volume.
- Bearish warning: A breakdown below the recent trading range.
My strategy would be to wait for a breakout and retest rather than buying after an extended rally.
Harmony also needs stronger evidence of sustained ecosystem activity to support a longer-term investment thesis.
Investor outlook: ONE offers a speculative recovery opportunity, but volatility and weak fundamental confirmation make aggressive accumulation difficult to justify.
2. OPENAI: A Serious Verification Warning
<badge color="danger">Avoid unverified tokens</badge>
The OPENAI ticker requires a different approach.
OpenAI has not officially launched a cryptocurrency token. In September 2024, scammers compromised an OpenAI-associated X account and used it to promote a fake OPENAI token and phishing website.
There are also exchange-listed derivative products using the OPENAI ticker. These are not OpenAI-issued blockchain tokens and do not represent ownership in the company.
For investors, the distinction is critical.
Before considering anything marketed as OPENAI, verify:
- Whether it is an actual blockchain token or an exchange derivative.
- Its exact contract address, if applicable.
- The exchange and trading instrument.
- Liquidity and counterparty risks.
- Whether any claimed OpenAI association is officially documented.
Investor outlook: I would not issue a bullish price target for OPENAI without identifying the exact asset. A famous company name is not a substitute for legitimate fundamentals.
3. AIN (Infinity Ground): Can AI Demand Support Further Growth?
<badge color="success">Speculative AI exposure</badge>
Infinity Ground's AIN offers a different investment narrative.
The project operates in the AI and blockchain application development sector. Its token is associated with platform services, ecosystem participation and planned utility features.
The latest CoinMarketCap snapshot showed:
- Price: Approximately $0.1419
- Market capitalization: Approximately $45.27 million
- 24-hour trading volume: Approximately $12.74 million
- 24-hour change: +9.21%
- Maximum supply: 1 billion AIN
- 24-hour range: $0.1234–$0.1715
However, there is an important supply-related issue.
CoinGecko and CoinMarketCap currently show different circulating-supply figures. Therefore, I would not use a precise circulating percentage to make an investment decision until that discrepancy is resolved.
Another important signal is the recent price correction. CoinMarketCap's snapshot placed AIN approximately 55% below its November 5 all-time high of $0.3278.
This suggests that volatility remains substantial despite the renewed AI narrative.
What I would monitor:
- Whether buyers defend the $0.1234–$0.13 area.
- Whether price can reclaim the $0.17 region.
- Whether trading volume supports a sustained recovery.
- Token unlocks and future supply distribution.
- Real ecosystem adoption rather than social-media attention.
Investor outlook: AIN has exposure to an attractive AI-related market narrative, but the recent correction and supply-data discrepancy justify caution. I would prefer confirmation of a recovery before increasing exposure.
Which Asset Offers the Better Risk-to-Reward Setup?
These three symbols should not be treated as equivalent investments.
Asset| Investment case| Main concern
ONE| Speculative recovery| Volatility and ecosystem fundamentals
OPENAI| Requires asset verification| No official OpenAI token
AIN| AI-sector speculation| Supply transparency and price volatility
My preference would be to monitor $ONE and $AIN for technical confirmation while avoiding any unverified $OPENAI token.
I would also avoid using the Keplr incident itself as a reason to buy either ONE or AIN. Neither token has been established as a direct beneficiary of the security event.
My Trading Strategy: Protect Capital First
In this type of market, chasing momentum is usually more dangerous than missing an entry.
I would follow a few basic rules:
- Wait for volume-confirmed breakouts.
- Avoid buying after unusually large price candles.
- Keep position sizes small in low-cap assets.
- Check spot liquidity before entering.
- Monitor funding rates and open interest.
- Use predefined stop-loss levels.
- Avoid excessive leverage during uncertain market conditions.
The objective is not to catch every rally. It is to enter trades where the potential reward justifies the downside risk.
Final Investor Takeaway
The Keplr incident highlights how quickly security problems can damage confidence in crypto infrastructure.
For ONE, the focus should be on whether its recent rally can develop into a sustainable recovery.
For AIN, the AI narrative is worth watching, but token supply transparency and actual ecosystem demand remain important.
As for OPENAI, investors should first establish exactly what they are trading. There is no official OpenAI-issued cryptocurrency token.
My approach is simple: follow the liquidity, verify the fundamentals and never confuse market hype with genuine investment value.
Do you think ONE and AIN have enough momentum to sustain their current recovery, or will investors become more selective as security concerns grow across the crypto market?
Share your market outlook in the comments.
Disclaimer: This article is for educational and informational purposes only. It is not financial advice. Market prices and trading levels are snapshots, not guaranteed entry points. Always verify token contracts, supply data and liquidity before investing. DYOR. NFA.
#KeplrAdvisesSocialLoginUsersToTransferAssets #CryptoAnalysis #CryptocurrencyWealth #Binance #cryptouniverseofficial
1
2
3.2k
🔐 Keplr Warns Social Login Users
Keplr is advising users who signed up through social login to transfer their assets to a self-managed wallet. Protecting private keys and maintaining wallet access are essential in crypto. $ATOM $OSMO $TIA
#keplradvisessocialloginuserstotransferassets
🔐 Keplr Warns Social Login Users
Keplr is advising users who signed up through social login to transfer their assets to a self-managed wallet. Protecting private keys and maintaining wallet access are essential in crypto. $ATOM $OSMO $TIA
#keplradvisessocialloginuserstotransferassets
Keplr is advising users who signed up through social login to transfer their assets to a self-managed wallet. Protecting private keys and maintaining wallet access are essential in crypto. $ATOM $OSMO $TIA
#keplradvisessocialloginuserstotransferassets
37

·
--
#KeplrAdvisesSocialLoginUsersToTransferAssets
🔄 Keplr Changed Its Advice: Move What's Left Now
A Web3Auth flaw exposed some Google and Apple login keys, so Keplr now tells those users to move remaining assets.
📊 Early estimate: about 20% of social-login accounts were exposed
⚠️ Only a fraction of that 20% appears fully exploited
🏦 Seed-phrase and hardware-wallet accounts were not affected
📉 Some empty balances may be a white-hat rescue, not the theft
Zoom out: the breach sat at the login provider, not seed wallets.
Move funds by Friday, or wait 7+ days for a checker? 👇
$ATOM
#KeplrAdvisesSocialLoginUsersToTransferAssets #Keplr #Security
#KeplrAdvisesSocialLoginUsersToTransferAssets
🔄 Keplr Changed Its Advice: Move What's Left Now
A Web3Auth flaw exposed some Google and Apple login keys, so Keplr now tells those users to move remaining assets.
📊 Early estimate: about 20% of social-login accounts were exposed
⚠️ Only a fraction of that 20% appears fully exploited
🏦 Seed-phrase and hardware-wallet accounts were not affected
📉 Some empty balances may be a white-hat rescue, not the theft
Zoom out: the breach sat at the login provider, not seed wallets.
Move funds by Friday, or wait 7+ days for a checker? 👇
$ATOM
#KeplrAdvisesSocialLoginUsersToTransferAssets #Keplr #Security
🔄 Keplr Changed Its Advice: Move What's Left Now
A Web3Auth flaw exposed some Google and Apple login keys, so Keplr now tells those users to move remaining assets.
📊 Early estimate: about 20% of social-login accounts were exposed
⚠️ Only a fraction of that 20% appears fully exploited
🏦 Seed-phrase and hardware-wallet accounts were not affected
📉 Some empty balances may be a white-hat rescue, not the theft
Zoom out: the breach sat at the login provider, not seed wallets.
Move funds by Friday, or wait 7+ days for a checker? 👇
$ATOM
#KeplrAdvisesSocialLoginUsersToTransferAssets #Keplr #Security
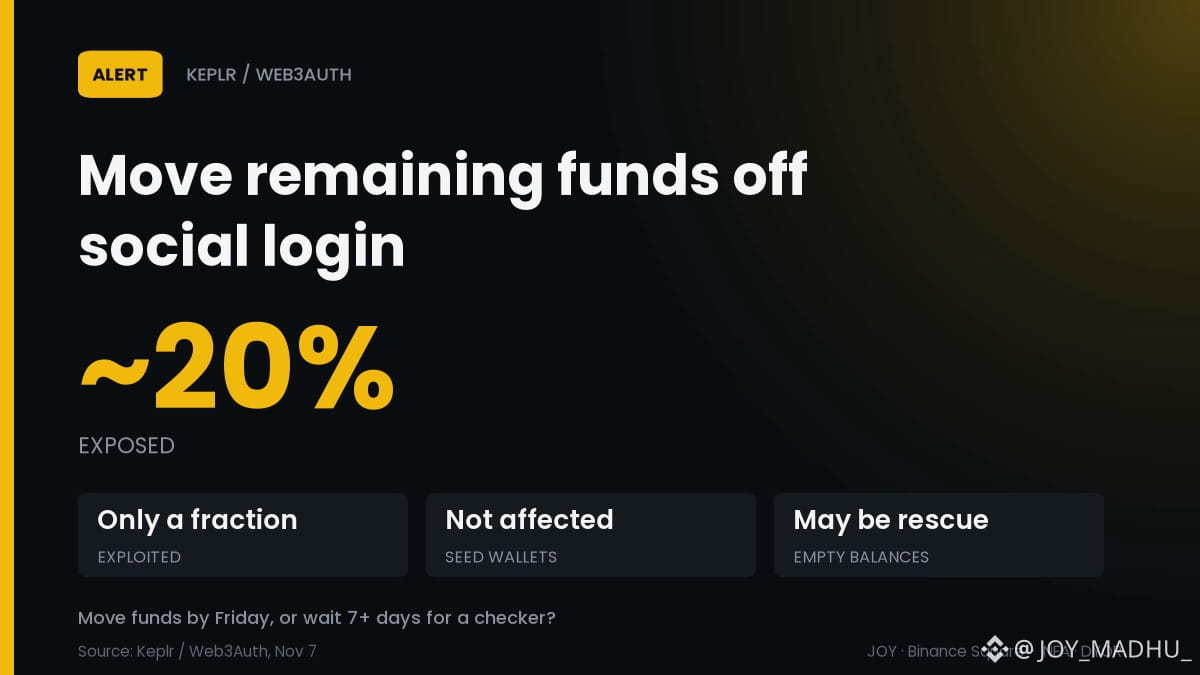
9
#KeplrAdvisesSocialLoginUsersToTransferAssets
🚨⚠️ SECURITY ALERT: YOUR CRYPTO ASSETS COULD BE AT RISK! DON'T IGNORE THIS WARNING!
The Keplr Wallet incident is raising serious concerns across the Web3 community.
Some users who created wallets through Google or Apple social login may be affected by a Web3Auth infrastructure vulnerability.
🔥 What should users know?
🔹 Potentially affected users should follow Keplr's official security instructions.
🔹 Avoid depositing additional funds into affected wallets.
🔹 Consider transferring eligible assets to a newly secured wallet.
🔹 Never share your seed phrase or private keys with anyone.
🔹 Beware of fake recovery links and impersonators.
🛡️ Remember: Convenience should NEVER come before crypto security!
💬 Let's discuss:
Would you trust Google or Apple login to protect your crypto assets again?
Or is a seed phrase / hardware wallet the only way to go?
👇 Share your thoughts. Your experience could help protect another investor!
#Keplr #CryptoSecurity #Web3
$BTC
{future}(BTCUSDT)
$HYPE
{future}(HYPEUSDT)
$ONE
{future}(ONEUSDT)
#KeplrAdvisesSocialLoginUsersToTransferAssets
🚨⚠️ SECURITY ALERT: YOUR CRYPTO ASSETS COULD BE AT RISK! DON'T IGNORE THIS WARNING!
The Keplr Wallet incident is raising serious concerns across the Web3 community.
Some users who created wallets through Google or Apple social login may be affected by a Web3Auth infrastructure vulnerability.
🔥 What should users know?
🔹 Potentially affected users should follow Keplr's official security instructions.
🔹 Avoid depositing additional funds into affected wallets.
🔹 Consider transferring eligible assets to a newly secured wallet.
🔹 Never share your seed phrase or private keys with anyone.
🔹 Beware of fake recovery links and impersonators.
🛡️ Remember: Convenience should NEVER come before crypto security!
💬 Let's discuss:
Would you trust Google or Apple login to protect your crypto assets again?
Or is a seed phrase / hardware wallet the only way to go?
👇 Share your thoughts. Your experience could help protect another investor!
#Keplr #CryptoSecurity #Web3
$BTC
$HYPE
$ONE
🚨⚠️ SECURITY ALERT: YOUR CRYPTO ASSETS COULD BE AT RISK! DON'T IGNORE THIS WARNING!
The Keplr Wallet incident is raising serious concerns across the Web3 community.
Some users who created wallets through Google or Apple social login may be affected by a Web3Auth infrastructure vulnerability.
🔥 What should users know?
🔹 Potentially affected users should follow Keplr's official security instructions.
🔹 Avoid depositing additional funds into affected wallets.
🔹 Consider transferring eligible assets to a newly secured wallet.
🔹 Never share your seed phrase or private keys with anyone.
🔹 Beware of fake recovery links and impersonators.
🛡️ Remember: Convenience should NEVER come before crypto security!
💬 Let's discuss:
Would you trust Google or Apple login to protect your crypto assets again?
Or is a seed phrase / hardware wallet the only way to go?
👇 Share your thoughts. Your experience could help protect another investor!
#Keplr #CryptoSecurity #Web3
$BTC
$HYPE
$ONE
547
Article
Security Incident Brief: Keplr Wallet & Web3Auth Infrastructure Vulnerability#keplradvisessocialloginuserstotransferassets
🚨 Security Incident Brief: Keplr Wallet & Web3Auth Infrastructure Vulnerability
📅 Issued: November 8, 2026 | ⚠️ Alert Level: High |
📌 Overview :- A critical upstream security vulnerability originating from Web3Auth—the third-party infrastructure provider powering social and embedded authentication—has impacted users utilizing Google and Apple ID logins on the Keplr ecosystem.
- 🔴 What Was Affected: Wallets generated through social/embedded sign-ins (Distributed Key Generation mechanism).
- 🟢 What Remained Safe: Traditional mnemonic seed-phrase wallets and hardware wallets (e.g., Ledger) are entirely unaffected. Keplr's core application code was not directly compromised.
📊 On-Chain Statistics & Impact Analysis
Comprehensive blockchain forensic data (via analytics providers such as Bitquery) highlights the scale of the exploit across the Cosmos ecosystem:
- 💰 Total Tracked Losses: ≥ $6.01 million in liquid assets across multiple Cosmos-based networks.
- 👛 Affected Scale: At least 44,041+ individual wallets suffered unauthorized balance sweeps.
- 🔒 Staked Asset Impact: Attackers extracted 1.96 million staked ATOM, bypassing traditional unbonding queues in certain vector sequences.
📉 Distribution of Losses:
- 88% of victims lost under $100, indicating a heavy impact on retail users.
- The median loss per wallet was low (~$1.34), meaning total losses are heavily concentrated within a few dozen higher-balance accounts (the single largest recorded individual drain reached $325K).
🌐 Multi-Chain Exposure: Because a single social login key manages cross-chain assets symmetrically, 46% of drained wallets were hit across two or more separate chains simultaneously.
⏱️ Behavioral Anomaly: Paradoxically, 86% of total funds were drained after initial public warnings went live, highlighting the propagation lag of security alerts among casual retail users.
🛡️ Important Note on "Disappearing" Balances
⚠️ Some affected wallets may show reduced or zero balances due to white-hat rescue transfers—assets proactively moved to safety by Keplr and Web3Auth—not theft.
- ✅ Check Web3Auth's verified rescue address list before concluding funds were stolen.
- ⏳ Staked and locked assets take longer to resolve due to processing complexity.
- 📌 The "86% drained after warnings" figure may be partially inflated by these rescue outflows.
✅ Immediate Action Items for Users
1. 🔍 Verify Your Login Type: If you access your assets strictly via seed phrase or hardware wallet, no action is required.
2. 💸 Move Remaining Assets: If you previously utilized Google/Apple sign-ins and still hold a liquid balance, urgently transfer remaining funds to a newly generated, self-custodied seed-phrase or hardware-backed wallet.
3. 🚫 Cease Deposits: Do not deposit any fresh liquidity into social-login associated accounts.
4. 🎣 Ignore Social Engineering: Beware of opportunistic threat actors circulating fake "recovery tools" or direct messages promising asset refunds. No legitimate entity will DM you first.
📡 What We're Monitoring
- Web3Auth's verified rescue address list publication
- Keplr's affected-account lookup tool launch
- Official corrections to total affected wallets and final loss figures
🔐 Stay safe, verify communication channels through official foundations, and prioritize cold storage hygiene. Self-custody with a seed phrase or hardware wallet remains the gold standard for high-value assets.
$GOOGLB $AAPLB $MSFTB
{spot}(MSFTBUSDT)
{spot}(AAPLBUSDT)
{spot}(GOOGLBUSDT)
#Binance #Google #Apple #BinanceSquareTalks
Security Incident Brief: Keplr Wallet & Web3Auth Infrastructure Vulnerability
#keplradvisessocialloginuserstotransferassets
🚨 Security Incident Brief: Keplr Wallet & Web3Auth Infrastructure Vulnerability
📅 Issued: November 8, 2026 | ⚠️ Alert Level: High |
📌 Overview :- A critical upstream security vulnerability originating from Web3Auth—the third-party infrastructure provider powering social and embedded authentication—has impacted users utilizing Google and Apple ID logins on the Keplr ecosystem.
- 🔴 What Was Affected: Wallets generated through social/embedded sign-ins (Distributed Key Generation mechanism).
- 🟢 What Remained Safe: Traditional mnemonic seed-phrase wallets and hardware wallets (e.g., Ledger) are entirely unaffected. Keplr's core application code was not directly compromised.
📊 On-Chain Statistics & Impact Analysis
Comprehensive blockchain forensic data (via analytics providers such as Bitquery) highlights the scale of the exploit across the Cosmos ecosystem:
- 💰 Total Tracked Losses: ≥ $6.01 million in liquid assets across multiple Cosmos-based networks.
- 👛 Affected Scale: At least 44,041+ individual wallets suffered unauthorized balance sweeps.
- 🔒 Staked Asset Impact: Attackers extracted 1.96 million staked ATOM, bypassing traditional unbonding queues in certain vector sequences.
📉 Distribution of Losses:
- 88% of victims lost under $100, indicating a heavy impact on retail users.
- The median loss per wallet was low (~$1.34), meaning total losses are heavily concentrated within a few dozen higher-balance accounts (the single largest recorded individual drain reached $325K).
🌐 Multi-Chain Exposure: Because a single social login key manages cross-chain assets symmetrically, 46% of drained wallets were hit across two or more separate chains simultaneously.
⏱️ Behavioral Anomaly: Paradoxically, 86% of total funds were drained after initial public warnings went live, highlighting the propagation lag of security alerts among casual retail users.
🛡️ Important Note on "Disappearing" Balances
⚠️ Some affected wallets may show reduced or zero balances due to white-hat rescue transfers—assets proactively moved to safety by Keplr and Web3Auth—not theft.
- ✅ Check Web3Auth's verified rescue address list before concluding funds were stolen.
- ⏳ Staked and locked assets take longer to resolve due to processing complexity.
- 📌 The "86% drained after warnings" figure may be partially inflated by these rescue outflows.
✅ Immediate Action Items for Users
1. 🔍 Verify Your Login Type: If you access your assets strictly via seed phrase or hardware wallet, no action is required.
2. 💸 Move Remaining Assets: If you previously utilized Google/Apple sign-ins and still hold a liquid balance, urgently transfer remaining funds to a newly generated, self-custodied seed-phrase or hardware-backed wallet.
3. 🚫 Cease Deposits: Do not deposit any fresh liquidity into social-login associated accounts.
4. 🎣 Ignore Social Engineering: Beware of opportunistic threat actors circulating fake "recovery tools" or direct messages promising asset refunds. No legitimate entity will DM you first.
📡 What We're Monitoring
- Web3Auth's verified rescue address list publication
- Keplr's affected-account lookup tool launch
- Official corrections to total affected wallets and final loss figures
🔐 Stay safe, verify communication channels through official foundations, and prioritize cold storage hygiene. Self-custody with a seed phrase or hardware wallet remains the gold standard for high-value assets.
$GOOGLB $AAPLB $MSFTB
#Binance #Google #Apple #BinanceSquareTalks
🚨 Security Incident Brief: Keplr Wallet & Web3Auth Infrastructure Vulnerability
📅 Issued: November 8, 2026 | ⚠️ Alert Level: High |
📌 Overview :- A critical upstream security vulnerability originating from Web3Auth—the third-party infrastructure provider powering social and embedded authentication—has impacted users utilizing Google and Apple ID logins on the Keplr ecosystem.
- 🔴 What Was Affected: Wallets generated through social/embedded sign-ins (Distributed Key Generation mechanism).
- 🟢 What Remained Safe: Traditional mnemonic seed-phrase wallets and hardware wallets (e.g., Ledger) are entirely unaffected. Keplr's core application code was not directly compromised.
📊 On-Chain Statistics & Impact Analysis
Comprehensive blockchain forensic data (via analytics providers such as Bitquery) highlights the scale of the exploit across the Cosmos ecosystem:
- 💰 Total Tracked Losses: ≥ $6.01 million in liquid assets across multiple Cosmos-based networks.
- 👛 Affected Scale: At least 44,041+ individual wallets suffered unauthorized balance sweeps.
- 🔒 Staked Asset Impact: Attackers extracted 1.96 million staked ATOM, bypassing traditional unbonding queues in certain vector sequences.
📉 Distribution of Losses:
- 88% of victims lost under $100, indicating a heavy impact on retail users.
- The median loss per wallet was low (~$1.34), meaning total losses are heavily concentrated within a few dozen higher-balance accounts (the single largest recorded individual drain reached $325K).
🌐 Multi-Chain Exposure: Because a single social login key manages cross-chain assets symmetrically, 46% of drained wallets were hit across two or more separate chains simultaneously.
⏱️ Behavioral Anomaly: Paradoxically, 86% of total funds were drained after initial public warnings went live, highlighting the propagation lag of security alerts among casual retail users.
🛡️ Important Note on "Disappearing" Balances
⚠️ Some affected wallets may show reduced or zero balances due to white-hat rescue transfers—assets proactively moved to safety by Keplr and Web3Auth—not theft.
- ✅ Check Web3Auth's verified rescue address list before concluding funds were stolen.
- ⏳ Staked and locked assets take longer to resolve due to processing complexity.
- 📌 The "86% drained after warnings" figure may be partially inflated by these rescue outflows.
✅ Immediate Action Items for Users
1. 🔍 Verify Your Login Type: If you access your assets strictly via seed phrase or hardware wallet, no action is required.
2. 💸 Move Remaining Assets: If you previously utilized Google/Apple sign-ins and still hold a liquid balance, urgently transfer remaining funds to a newly generated, self-custodied seed-phrase or hardware-backed wallet.
3. 🚫 Cease Deposits: Do not deposit any fresh liquidity into social-login associated accounts.
4. 🎣 Ignore Social Engineering: Beware of opportunistic threat actors circulating fake "recovery tools" or direct messages promising asset refunds. No legitimate entity will DM you first.
📡 What We're Monitoring
- Web3Auth's verified rescue address list publication
- Keplr's affected-account lookup tool launch
- Official corrections to total affected wallets and final loss figures
🔐 Stay safe, verify communication channels through official foundations, and prioritize cold storage hygiene. Self-custody with a seed phrase or hardware wallet remains the gold standard for high-value assets.
$GOOGLB $AAPLB $MSFTB
#Binance #Google #Apple #BinanceSquareTalks
1
2
107
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BitcoinFiveWeeklyLosses
16,273 views
462 Discussing
2
#AIChipSlumpNasdaq
8,629 views
264 Discussing
3
#NvidiaInvestigatesAfterHuang’sAffairApology
6,332 views
140 Discussing
4
#EthereumSpotETFsPost$365MWeeklyOutflow
16 views
4 Discussing
5
#SouthKoreaDraftLawTargets15To20%ShareholderCap
169,443 views
887 Discussing
6
#TradFiForBeginners
240,968 views
2,177 Discussing
7
#KeplrAdvisesSocialLoginUsersToTransferAssets
79,371 views
623 Discussing
8
#TetherPlans€28.8MForJuventusCapitalIncrease
57,396 views
460 Discussing
9
#JobsReportRaisesHikeOdds
994,870 views
4,625 Discussing
10
#CPITestsDecemberRateOutlook
458,355 views
2,033 Discussing