
#rseth
rseth
24,370 views
109 Discussing
Hot
Latest

·
--
The hacker stole $rsETH, but MEV bots got to it firstFirst, let’s say: it’s not that Safe itself isn’t secure—the custom module attached to the wallet left the backdoor too wide open.
At about 04:38 UTC on September 15, security firms including Blockaid traced an incident involving an Ethereum Safe where there was abuse of module authorization. The attacker used a public keeper multicall to route a custom Uniswap v4 liquidity module into an attacker-controlled hooked pool, splitting aEthrsETH into roughly 2,900 $rsETH valued at about $7.73 million (the media also reported a figure around $7.8 million). The security assessment classified it as module-authorization abuse, not a compromise of the Safe core or the owner key.
The hacker stole $rsETH, but MEV bots got to it first
First, let’s say: it’s not that Safe itself isn’t secure—the custom module attached to the wallet left the backdoor too wide open.
At about 04:38 UTC on September 15, security firms including Blockaid traced an incident involving an Ethereum Safe where there was abuse of module authorization. The attacker used a public keeper multicall to route a custom Uniswap v4 liquidity module into an attacker-controlled hooked pool, splitting aEthrsETH into roughly 2,900 $rsETH valued at about $7.73 million (the media also reported a figure around $7.8 million). The security assessment classified it as module-authorization abuse, not a compromise of the Safe core or the owner key.
At about 04:38 UTC on September 15, security firms including Blockaid traced an incident involving an Ethereum Safe where there was abuse of module authorization. The attacker used a public keeper multicall to route a custom Uniswap v4 liquidity module into an attacker-controlled hooked pool, splitting aEthrsETH into roughly 2,900 $rsETH valued at about $7.73 million (the media also reported a figure around $7.8 million). The security assessment classified it as module-authorization abuse, not a compromise of the Safe core or the owner key.
216
🚨 $RSETH UNDER ATTACK: $7.7M LIQUIDITY SWEEP UNLEASHED! 🦈
📊 Blockaid’s on‑chain radar flagged a Safe wallet hit on Ethereum, where the attacker hijacked the public Keeper Multicall to reroute a custom Uniswap V4 LP into a malicious Hook Pool. ⚡ The rogue Hook unwrapped aEth‑rsETH into rsETH, and Yoink MEV swooped in to extract the whole stack in a single block. 🔍 This play showcases how smart‑money operators weaponize contract hooks to drain liquidity in a flash, leaving the ecosystem scrambling for the next defensive patch.
💬 How will the rsETH community reinforce their vaults against this kind of hook‑driven raid? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #RSETH #SmartMoney #Hack #LiquiditySweep #Crypto
🦈 ⚡
🚨 $RSETH UNDER ATTACK: $7.7M LIQUIDITY SWEEP UNLEASHED! 🦈
📊 Blockaid’s on‑chain radar flagged a Safe wallet hit on Ethereum, where the attacker hijacked the public Keeper Multicall to reroute a custom Uniswap V4 LP into a malicious Hook Pool. ⚡ The rogue Hook unwrapped aEth‑rsETH into rsETH, and Yoink MEV swooped in to extract the whole stack in a single block. 🔍 This play showcases how smart‑money operators weaponize contract hooks to drain liquidity in a flash, leaving the ecosystem scrambling for the next defensive patch.
💬 How will the rsETH community reinforce their vaults against this kind of hook‑driven raid? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #RSETH #SmartMoney #Hack #LiquiditySweep #Crypto
🦈 ⚡
📊 Blockaid’s on‑chain radar flagged a Safe wallet hit on Ethereum, where the attacker hijacked the public Keeper Multicall to reroute a custom Uniswap V4 LP into a malicious Hook Pool. ⚡ The rogue Hook unwrapped aEth‑rsETH into rsETH, and Yoink MEV swooped in to extract the whole stack in a single block. 🔍 This play showcases how smart‑money operators weaponize contract hooks to drain liquidity in a flash, leaving the ecosystem scrambling for the next defensive patch.
💬 How will the rsETH community reinforce their vaults against this kind of hook‑driven raid? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #RSETH #SmartMoney #Hack #LiquiditySweep #Crypto
🦈 ⚡
9
·
--
#новости
#взлом #rseth
🪞 A hacker tried to steal $7.8m, but another bot intercepted the funds right during the attack.
The attacker found a vulnerability in a third-party module connected to an unknown user’s Safe wallet and attempted to withdraw ~2900 rsETH ($7.8m).
However, the MEV bot Yoink noticed the transaction, carried out the same attack earlier, and intercepted almost the entire amount.
The Kelp DAO protocol, which issues rsETH, temporarily froze the bot’s address. Kelp DAO and Safe themselves were not hacked.
The wallet owner’s funds have not been returned yet, and Yoink’s developer has not publicly said they plan to do so.
❗️Kelp DAO urged users to temporarily revoke permissions for their contracts. Funds of users who interacted with the protocol may be at risk.
#новости
#взлом #rseth
🪞 A hacker tried to steal $7.8m, but another bot intercepted the funds right during the attack.
The attacker found a vulnerability in a third-party module connected to an unknown user’s Safe wallet and attempted to withdraw ~2900 rsETH ($7.8m).
However, the MEV bot Yoink noticed the transaction, carried out the same attack earlier, and intercepted almost the entire amount.
The Kelp DAO protocol, which issues rsETH, temporarily froze the bot’s address. Kelp DAO and Safe themselves were not hacked.
The wallet owner’s funds have not been returned yet, and Yoink’s developer has not publicly said they plan to do so.
❗️Kelp DAO urged users to temporarily revoke permissions for their contracts. Funds of users who interacted with the protocol may be at risk.
#взлом #rseth
🪞 A hacker tried to steal $7.8m, but another bot intercepted the funds right during the attack.
The attacker found a vulnerability in a third-party module connected to an unknown user’s Safe wallet and attempted to withdraw ~2900 rsETH ($7.8m).
However, the MEV bot Yoink noticed the transaction, carried out the same attack earlier, and intercepted almost the entire amount.
The Kelp DAO protocol, which issues rsETH, temporarily froze the bot’s address. Kelp DAO and Safe themselves were not hacked.
The wallet owner’s funds have not been returned yet, and Yoink’s developer has not publicly said they plan to do so.
❗️Kelp DAO urged users to temporarily revoke permissions for their contracts. Funds of users who interacted with the protocol may be at risk.
1
134

·
--
Just saw this: An Ethereum user’s Safe multisig reportedly lost about $7.73 million in rsETH. The attacker used a public keeper multicall to pull a custom Uni V4 LP Safe module into a pool with a malicious hook, then unwrapped aEthrsETH into rsETH; in the same block, an MEV bot yoinked the funds and ran off with them. Blockaid is monitoring.
Kelp says the core contracts and collateral are normal, and it paused transfers for about 24 hours to the suspicious receiving address; minting/redemption proceeds as usual. The key issue is the authorization surface of the custom module—not that the Safe/Kelp core was compromised.
#DeFi #安全 #ETH #rsETH
Just saw this: An Ethereum user’s Safe multisig reportedly lost about $7.73 million in rsETH. The attacker used a public keeper multicall to pull a custom Uni V4 LP Safe module into a pool with a malicious hook, then unwrapped aEthrsETH into rsETH; in the same block, an MEV bot yoinked the funds and ran off with them. Blockaid is monitoring.
Kelp says the core contracts and collateral are normal, and it paused transfers for about 24 hours to the suspicious receiving address; minting/redemption proceeds as usual. The key issue is the authorization surface of the custom module—not that the Safe/Kelp core was compromised.
#DeFi #安全 #ETH #rsETH
Kelp says the core contracts and collateral are normal, and it paused transfers for about 24 hours to the suspicious receiving address; minting/redemption proceeds as usual. The key issue is the authorization surface of the custom module—not that the Safe/Kelp core was compromised.
#DeFi #安全 #ETH #rsETH
61
·
--
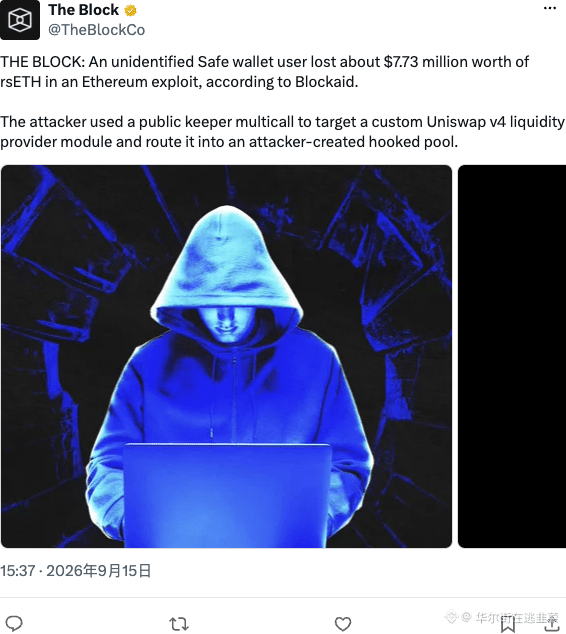
The anonymous Safe wallet was drained of $77.3M worth of rsETH. The hacker didn’t play games—he simply used a public keeper multicall to invoke a custom Uniswap v4 LP module, and routed everything directly into a hook contract he had created. Put plainly, it’s module-level authorization used as a backdoor: once a signature is approved, the money flies. Using Safe doesn’t equal safety—the plugin is the real weak point. Check your authorizations now.
$ETH #rsETH #Uniswap
The anonymous Safe wallet was drained of $77.3M worth of rsETH. The hacker didn’t play games—he simply used a public keeper multicall to invoke a custom Uniswap v4 LP module, and routed everything directly into a hook contract he had created. Put plainly, it’s module-level authorization used as a backdoor: once a signature is approved, the money flies. Using Safe doesn’t equal safety—the plugin is the real weak point. Check your authorizations now.
$ETH #rsETH #Uniswap
$ETH #rsETH #Uniswap
92
·
--
Verified
🔧 Kelp DAO confirms that rs$ETH has fully recovered after 5 weeks of damage control following the $293 million attack.
{future}(ETHUSDT)
According to the latest announcement, the final batch of 20,373.7 rsETH has been transferred to the cross-chain bridge system, officially completing the recovery plan. Currently, the mint, redeem, and reward distribution functions are all back to normal operation.
📊 The attack on April 18 not only impacted Kelp DAO but also created a domino effect across the entire DeFi ecosystem. The hackers used a large amount of rsETH as collateral to borrow WETH, causing the lending protocol to incur a bad debt of around $190 million.
👀 Although the recovery process has been completed, the total value locked (TVL) in the DeFi market has not yet returned to pre-incident levels, indicating that the effects of large-scale hacks still linger.
#DeFi #rsETH #KelpDAO #Crypto
🔧 Kelp DAO confirms that rs$ETH has fully recovered after 5 weeks of damage control following the $293 million attack.
According to the latest announcement, the final batch of 20,373.7 rsETH has been transferred to the cross-chain bridge system, officially completing the recovery plan. Currently, the mint, redeem, and reward distribution functions are all back to normal operation.
📊 The attack on April 18 not only impacted Kelp DAO but also created a domino effect across the entire DeFi ecosystem. The hackers used a large amount of rsETH as collateral to borrow WETH, causing the lending protocol to incur a bad debt of around $190 million.
👀 Although the recovery process has been completed, the total value locked (TVL) in the DeFi market has not yet returned to pre-incident levels, indicating that the effects of large-scale hacks still linger.
#DeFi #rsETH #KelpDAO #Crypto
According to the latest announcement, the final batch of 20,373.7 rsETH has been transferred to the cross-chain bridge system, officially completing the recovery plan. Currently, the mint, redeem, and reward distribution functions are all back to normal operation.
📊 The attack on April 18 not only impacted Kelp DAO but also created a domino effect across the entire DeFi ecosystem. The hackers used a large amount of rsETH as collateral to borrow WETH, causing the lending protocol to incur a bad debt of around $190 million.
👀 Although the recovery process has been completed, the total value locked (TVL) in the DeFi market has not yet returned to pre-incident levels, indicating that the effects of large-scale hacks still linger.
#DeFi #rsETH #KelpDAO #Crypto
2
2.1k
·
--
Kelp DAO Alert: Starting June 15th, cross-chain support for rsETH on multiple chains will be halted. Users holding or utilizing the rsETH cross-chain functionality are advised to check their asset networks, cross-chain pathways, and related DeFi positions in advance to avoid restricted operations down the line.
These types of calendar events may not directly impact prices, but they can affect liquidity migration, cross-chain experiences, and interactions with certain protocols. Users currently engaging with the Kelp ecosystem should keep an eye on official updates and migration plans. #KelpDAO #rsETH
Kelp DAO Alert: Starting June 15th, cross-chain support for rsETH on multiple chains will be halted. Users holding or utilizing the rsETH cross-chain functionality are advised to check their asset networks, cross-chain pathways, and related DeFi positions in advance to avoid restricted operations down the line.
These types of calendar events may not directly impact prices, but they can affect liquidity migration, cross-chain experiences, and interactions with certain protocols. Users currently engaging with the Kelp ecosystem should keep an eye on official updates and migration plans. #KelpDAO #rsETH
These types of calendar events may not directly impact prices, but they can affect liquidity migration, cross-chain experiences, and interactions with certain protocols. Users currently engaging with the Kelp ecosystem should keep an eye on official updates and migration plans. #KelpDAO #rsETH
96
Article
⚠️ AAVE: The Hidden Flaws of a Tranquil DeFi Giant$AAVE
Short Title: AAVE in Danger
📉 The rsETH Incident: Sharp Drop in TVL
On April 18, 2026, AAVE experienced a major shock following the rsETH security incident:
TVL dropped nearly 17% in just one day
Massive funds were urgently pulled out by investors
The impact continues to be felt on market confidence
🔴 AAVE's Fundamental Issues
1. Hidden Centralization
AAVE claims to be decentralized, but:
Token governance is concentrated among a few large holders
⚠️ AAVE: The Hidden Flaws of a Tranquil DeFi Giant
$AAVE
Short Title: AAVE in Danger
📉 The rsETH Incident: Sharp Drop in TVL
On April 18, 2026, AAVE experienced a major shock following the rsETH security incident:
TVL dropped nearly 17% in just one day
Massive funds were urgently pulled out by investors
The impact continues to be felt on market confidence
🔴 AAVE's Fundamental Issues
1. Hidden Centralization
AAVE claims to be decentralized, but:
Token governance is concentrated among a few large holders
Short Title: AAVE in Danger
📉 The rsETH Incident: Sharp Drop in TVL
On April 18, 2026, AAVE experienced a major shock following the rsETH security incident:
TVL dropped nearly 17% in just one day
Massive funds were urgently pulled out by investors
The impact continues to be felt on market confidence
🔴 AAVE's Fundamental Issues
1. Hidden Centralization
AAVE claims to be decentralized, but:
Token governance is concentrated among a few large holders
1.5k
·
--
The cross-chain bridge was hit by a spoofing attack, releasing 116,500 rsETH out of thin air. The attacker went straight to Aave and opened a position borrowing over 80,000 WETH—this isn’t a DeFi bug; it’s the trust assumptions of the infrastructure being breached.
The controversy lies here: Aave's review shifted the responsibility onto the "third-party cross-chain bridge infrastructure," but Aave V3 accepted that batch of rsETH as collateral. Where's the risk management? The protocol layer has no ability to verify the authenticity of cross-chain assets.
Some argue this proves Aave itself is fine; the process was completed, and the bad debt was eventually covered. I don't see it that way. The asset support recovery was due to LayerZero stepping in later, not because Aave was covering it themselves—what if LayerZero hadn’t stepped in?
Who bears the bad debt?
Now the rsETH market is "back to normal," but this repair path relies on third parties being willing to fill the gap, not on protocol design’s fault tolerance. Next time, if someone doesn’t want to cover, the outcome will be different.
I don’t have any DeFi-related positions in this matter. $BTC contract/spot ratio is still at 7.7x, BTC itself hasn't moved much today (+0.3%, around 74k), and the market isn't pricing this as systemic risk. I don't believe it is, but the collateral risk of cross-chain assets in lending protocols has always been underpriced.
That’s my judgment; it’s your money, you decide.
$BTC #Aave #DeFi #rsETH
The cross-chain bridge was hit by a spoofing attack, releasing 116,500 rsETH out of thin air. The attacker went straight to Aave and opened a position borrowing over 80,000 WETH—this isn’t a DeFi bug; it’s the trust assumptions of the infrastructure being breached.
The controversy lies here: Aave's review shifted the responsibility onto the "third-party cross-chain bridge infrastructure," but Aave V3 accepted that batch of rsETH as collateral. Where's the risk management? The protocol layer has no ability to verify the authenticity of cross-chain assets.
Some argue this proves Aave itself is fine; the process was completed, and the bad debt was eventually covered. I don't see it that way. The asset support recovery was due to LayerZero stepping in later, not because Aave was covering it themselves—what if LayerZero hadn’t stepped in?
Who bears the bad debt?
Now the rsETH market is "back to normal," but this repair path relies on third parties being willing to fill the gap, not on protocol design’s fault tolerance. Next time, if someone doesn’t want to cover, the outcome will be different.
I don’t have any DeFi-related positions in this matter. $BTC contract/spot ratio is still at 7.7x, BTC itself hasn't moved much today (+0.3%, around 74k), and the market isn't pricing this as systemic risk. I don't believe it is, but the collateral risk of cross-chain assets in lending protocols has always been underpriced.
That’s my judgment; it’s your money, you decide.
$BTC #Aave #DeFi #rsETH
The controversy lies here: Aave's review shifted the responsibility onto the "third-party cross-chain bridge infrastructure," but Aave V3 accepted that batch of rsETH as collateral. Where's the risk management? The protocol layer has no ability to verify the authenticity of cross-chain assets.
Some argue this proves Aave itself is fine; the process was completed, and the bad debt was eventually covered. I don't see it that way. The asset support recovery was due to LayerZero stepping in later, not because Aave was covering it themselves—what if LayerZero hadn’t stepped in?
Who bears the bad debt?
Now the rsETH market is "back to normal," but this repair path relies on third parties being willing to fill the gap, not on protocol design’s fault tolerance. Next time, if someone doesn’t want to cover, the outcome will be different.
I don’t have any DeFi-related positions in this matter. $BTC contract/spot ratio is still at 7.7x, BTC itself hasn't moved much today (+0.3%, around 74k), and the market isn't pricing this as systemic risk. I don't believe it is, but the collateral risk of cross-chain assets in lending protocols has always been underpriced.
That’s my judgment; it’s your money, you decide.
$BTC #Aave #DeFi #rsETH
159
·
--
In April, stolen rsETH was deposited into Aave to borrow $191M WETH. Pool utilization hit 100%. $8.45B TVL drained in two days.
Common lending tools have clear gaps:
Multi-collateral joint deviation — unsupported by Aave UI, ProfitLab, Hypernative. Only DeFi Saver partial.
Oracle deviation not deducted — missing in Aave UI, DeFi Saver, ProfitLab.
Actionable recommendations — none in Aave UI, Hypernative. ProfitLab manual only. DeFi Saver auto-executes.
Cross-protocol aggregation — no unified view for Aave + Compound.
Does your tool show the real risk?
#AAVE #defi #lending #rseth
In April, stolen rsETH was deposited into Aave to borrow $191M WETH. Pool utilization hit 100%. $8.45B TVL drained in two days.
Common lending tools have clear gaps:
Multi-collateral joint deviation — unsupported by Aave UI, ProfitLab, Hypernative. Only DeFi Saver partial.
Oracle deviation not deducted — missing in Aave UI, DeFi Saver, ProfitLab.
Actionable recommendations — none in Aave UI, Hypernative. ProfitLab manual only. DeFi Saver auto-executes.
Cross-protocol aggregation — no unified view for Aave + Compound.
Does your tool show the real risk?
#AAVE #defi #lending #rseth
Common lending tools have clear gaps:
Multi-collateral joint deviation — unsupported by Aave UI, ProfitLab, Hypernative. Only DeFi Saver partial.
Oracle deviation not deducted — missing in Aave UI, DeFi Saver, ProfitLab.
Actionable recommendations — none in Aave UI, Hypernative. ProfitLab manual only. DeFi Saver auto-executes.
Cross-protocol aggregation — no unified view for Aave + Compound.
Does your tool show the real risk?
#AAVE #defi #lending #rseth
167
$ETH RESTAKING ALERT: SUSPICIOUS $RSETH WALLET FLOW TRIGGERS LOCK 🚨
$ETH restaking just got a control-room test after $RSETH detected suspicious wallet flow and froze one address for 24 hours. 🚨 The team says contracts are secure, collateral is intact, minting, withdrawals, and integrations continue, and users need not act.
💡 For traders, this is not a protocol collapse signal yet, but a liquidity caution flag. A $7.73 million $RSETH loss tied to a compromised Safe wallet keeps sellers watching for panic bids. 👇 Will this short freeze become a buying opportunity, or another warning shot for restaking risk?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #RSETH #Restaking #Crypto #Security
⚡ 🦈
$ETH RESTAKING ALERT: SUSPICIOUS $RSETH WALLET FLOW TRIGGERS LOCK 🚨
$ETH restaking just got a control-room test after $RSETH detected suspicious wallet flow and froze one address for 24 hours. 🚨 The team says contracts are secure, collateral is intact, minting, withdrawals, and integrations continue, and users need not act.
💡 For traders, this is not a protocol collapse signal yet, but a liquidity caution flag. A $7.73 million $RSETH loss tied to a compromised Safe wallet keeps sellers watching for panic bids. 👇 Will this short freeze become a buying opportunity, or another warning shot for restaking risk?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #RSETH #Restaking #Crypto #Security
⚡ 🦈
$ETH restaking just got a control-room test after $RSETH detected suspicious wallet flow and froze one address for 24 hours. 🚨 The team says contracts are secure, collateral is intact, minting, withdrawals, and integrations continue, and users need not act.
💡 For traders, this is not a protocol collapse signal yet, but a liquidity caution flag. A $7.73 million $RSETH loss tied to a compromised Safe wallet keeps sellers watching for panic bids. 👇 Will this short freeze become a buying opportunity, or another warning shot for restaking risk?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #RSETH #Restaking #Crypto #Security
⚡ 🦈
12

Bot MEV Yoink grabs $7.7M when exploiting Safe module ETH fails, Kelp freezes the address
- Bot MEV Yoink front-runs the attacker who publicly exploited a custom Safe module
- Bot catches stolen rsETH worth $7.7M
- Kelp temporarily froze the receiving address
#BinanceSquare #CryptoNews #ETH #rsETH #MEV Kelp
$eth $rseth
vlikevn Titanbot
Source: CoinTelegraph
Bot MEV Yoink grabs $7.7M when exploiting Safe module ETH fails, Kelp freezes the address
- Bot MEV Yoink front-runs the attacker who publicly exploited a custom Safe module
- Bot catches stolen rsETH worth $7.7M
- Kelp temporarily froze the receiving address
#BinanceSquare #CryptoNews #ETH #rsETH #MEV Kelp
$eth $rseth
vlikevn Titanbot
Source: CoinTelegraph
- Bot MEV Yoink front-runs the attacker who publicly exploited a custom Safe module
- Bot catches stolen rsETH worth $7.7M
- Kelp temporarily froze the receiving address
#BinanceSquare #CryptoNews #ETH #rsETH #MEV Kelp
$eth $rseth
vlikevn Titanbot
Source: CoinTelegraph
67
·
--
🚨 Uniswap V4 Hook Maliciously Exploited, a Safe wallet user Lost About $7.73 million.
#ETH #rsETH
🚨 Uniswap V4 Hook Maliciously Exploited, a Safe wallet user Lost About $7.73 million.
#ETH #rsETH
#ETH #rsETH
75

Article
Alert in DeFi: Kelp DAO suffers massive hack of USD $292 million 🚨The ecosystem of Decentralized Finance (DeFi) faces a new earthquake after a million-dollar exploit against Kelp DAO, one of the most prominent liquid restaking protocols, was confirmed. The attack resulted in the loss of approximately USD $292 million, raising alarms about security in cross-chain bridges. 🛡️
The origin of the attack
According to reports from security firms, the attacker exploited a vulnerability in the rsETH bridge adapter contract. This allowed for the massive draining of funds, which were quickly converted to ETH and moved through mixers to attempt to erase the transaction trail. 💸
Alert in DeFi: Kelp DAO suffers massive hack of USD $292 million 🚨
The ecosystem of Decentralized Finance (DeFi) faces a new earthquake after a million-dollar exploit against Kelp DAO, one of the most prominent liquid restaking protocols, was confirmed. The attack resulted in the loss of approximately USD $292 million, raising alarms about security in cross-chain bridges. 🛡️
The origin of the attack
According to reports from security firms, the attacker exploited a vulnerability in the rsETH bridge adapter contract. This allowed for the massive draining of funds, which were quickly converted to ETH and moved through mixers to attempt to erase the transaction trail. 💸
The origin of the attack
According to reports from security firms, the attacker exploited a vulnerability in the rsETH bridge adapter contract. This allowed for the massive draining of funds, which were quickly converted to ETH and moved through mixers to attempt to erase the transaction trail. 💸
137

·
--
KelpDAO’s exploit lit the fuse, and DeFi felt the blast.
The attack drained about $293M in rsETH, but the real damage spread fast — Aave lost roughly $15B in supplied deposits as capital rushed for the exits. This was more than a hack. It was a stress test for trust, liquidity, and DeFi risk itself.
#AAVE #KelpDAO #DeFiCrisis #crypto #rsETH
KelpDAO’s exploit lit the fuse, and DeFi felt the blast.
The attack drained about $293M in rsETH, but the real damage spread fast — Aave lost roughly $15B in supplied deposits as capital rushed for the exits. This was more than a hack. It was a stress test for trust, liquidity, and DeFi risk itself.
#AAVE #KelpDAO #DeFiCrisis #crypto #rsETH
The attack drained about $293M in rsETH, but the real damage spread fast — Aave lost roughly $15B in supplied deposits as capital rushed for the exits. This was more than a hack. It was a stress test for trust, liquidity, and DeFi risk itself.
#AAVE #KelpDAO #DeFiCrisis #crypto #rsETH
1
235

Keep DAO got hit for $292M after a bridge bug let someone mint 116,500 fake rsETH and borrow against it on Aave. Is this a one-off or a flaw in how bridges are built?
One bad setting let fake tokens become $280M of "collateral" across major protocols. If bridges can print money out of thin air, what in DeFi do you still trust?
#DeFi #KelpDAOFacesAttac #CryptoSecurity #rseth #LayerZero
Keep DAO got hit for $292M after a bridge bug let someone mint 116,500 fake rsETH and borrow against it on Aave. Is this a one-off or a flaw in how bridges are built?
One bad setting let fake tokens become $280M of "collateral" across major protocols. If bridges can print money out of thin air, what in DeFi do you still trust?
#DeFi #KelpDAOFacesAttac #CryptoSecurity #rseth #LayerZero
One bad setting let fake tokens become $280M of "collateral" across major protocols. If bridges can print money out of thin air, what in DeFi do you still trust?
#DeFi #KelpDAOFacesAttac #CryptoSecurity #rseth #LayerZero
80
Big News
Big win for DeFi today. @aave stepping up to handle the @KelpDAO bad debt is the kind of maturity the market needs. 🛡️✨
Security > Hype. $BTC $ETH $AAVE
{spot}(AAVEUSDT)
#DEFİ #AaveProtocol #KelpDAO #CryptoUpdate #rseth
Big News
Big win for DeFi today. @aave stepping up to handle the @KelpDAO bad debt is the kind of maturity the market needs. 🛡️✨
Security > Hype. $BTC $ETH $AAVE
#DEFİ #AaveProtocol #KelpDAO #CryptoUpdate #rseth
Big win for DeFi today. @aave stepping up to handle the @KelpDAO bad debt is the kind of maturity the market needs. 🛡️✨
Security > Hype. $BTC $ETH $AAVE
#DEFİ #AaveProtocol #KelpDAO #CryptoUpdate #rseth
117
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#AIStocksWhatNext
51,620 views
292 Discussing
2
#MuseOvertakesChatGPTAsTopFreeIOSApp
179 views
0 Discussing
3
#TokenizedStockPlatformsCouldLaunchNextQuarter
1,028 views
2 Discussing
4
#StrategyAdds950Bitcoin
3,069 views
41 Discussing
5
#CardanoAddedToX402KitForADAPayments
8,542 views
241 Discussing
6
#XRPRises8%
19,356 views
575 Discussing
7
#AMDHits$1TrillionMarketCap
719 views
33 Discussing
8
#BitcoinSpotETFs$999MNetInflow
1,592 views
42 Discussing
9
#AppleGoogleSeekStablecoinTokenizedDepositTalent
11,009 views
409 Discussing
10
#NvidiaToBuyAnother$1.5BSBEnergySharesPreIPO
1,780 views
39 Discussing