
#hack
hack
1.3M views
1,342 Discussing
Hot
Latest

Trump Responds to Binance Hack Investigation
U.S. President Donald Trump is reportedly looking into the recent Binance hack, according to Bloomberg.
The development brings additional attention to the security incident and could raise questions about crypto exchange security, cybersecurity risks, and the protection of digital assets.
As the situation develops, the market will be watching closely for further details and any potential regulatory response.
Crypto security remains a major issue for the industry.
#Binance / #Hack / #TRUMP
Trump Responds to Binance Hack Investigation
U.S. President Donald Trump is reportedly looking into the recent Binance hack, according to Bloomberg.
The development brings additional attention to the security incident and could raise questions about crypto exchange security, cybersecurity risks, and the protection of digital assets.
As the situation develops, the market will be watching closely for further details and any potential regulatory response.
Crypto security remains a major issue for the industry.
#Binance / #Hack / #TRUMP
U.S. President Donald Trump is reportedly looking into the recent Binance hack, according to Bloomberg.
The development brings additional attention to the security incident and could raise questions about crypto exchange security, cybersecurity risks, and the protection of digital assets.
As the situation develops, the market will be watching closely for further details and any potential regulatory response.
Crypto security remains a major issue for the industry.
#Binance / #Hack / #TRUMP
1
442
Binance Security Incident Raises Serious Questions About AI and Wallet Protection
A reported security incident involving Binance has highlighted a new and concerning type of cybersecurity threat.
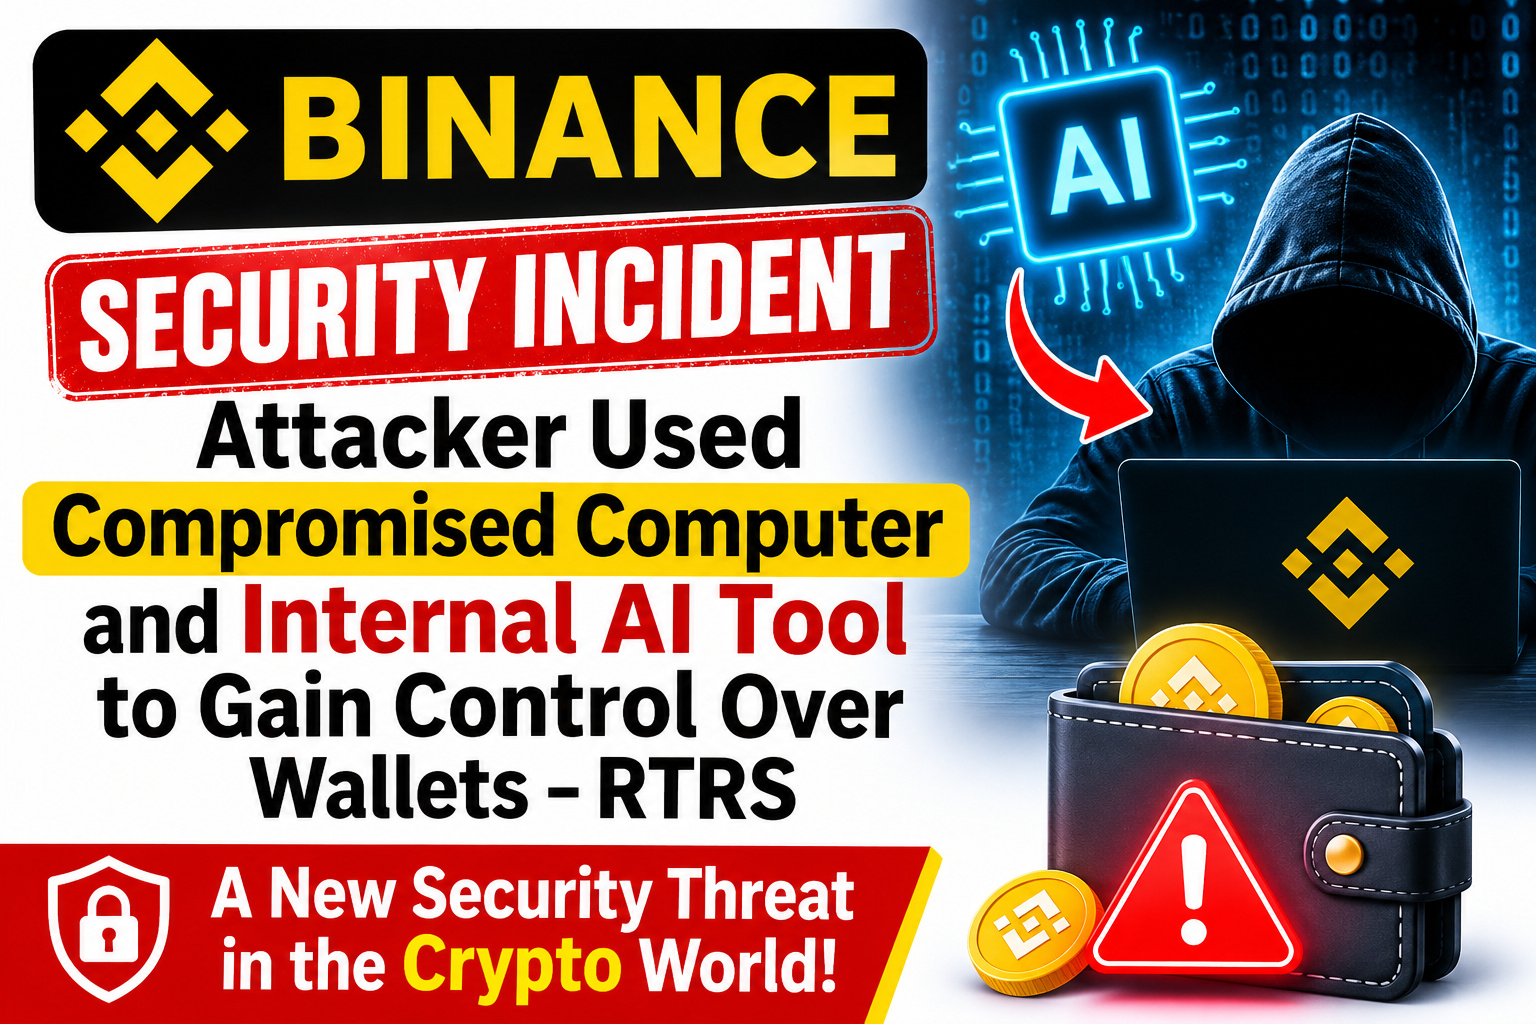
According to Reuters, the attacker allegedly exploited a compromised computer and used an internal AI tool to gain control over wallets.
What makes this incident particularly concerning is the reported combination of compromised devices, AI-assisted access, and wallet security vulnerabilities. It shows how attackers may use legitimate internal tools as part of sophisticated cyberattacks.
As AI becomes more deeply integrated into crypto infrastructure, protecting internal systems, access permissions, and sensitive wallet operations is becoming increasingly important.
The bigger takeaway is clear: Security risks in crypto are evolving, and even advanced platforms must continuously strengthen their defenses.
AI can improve efficiency, but it also introduces new security challenges that cannot be ignored.
#Binance / #Hack
Binance Security Incident Raises Serious Questions About AI and Wallet Protection
A reported security incident involving Binance has highlighted a new and concerning type of cybersecurity threat.
According to Reuters, the attacker allegedly exploited a compromised computer and used an internal AI tool to gain control over wallets.
What makes this incident particularly concerning is the reported combination of compromised devices, AI-assisted access, and wallet security vulnerabilities. It shows how attackers may use legitimate internal tools as part of sophisticated cyberattacks.
As AI becomes more deeply integrated into crypto infrastructure, protecting internal systems, access permissions, and sensitive wallet operations is becoming increasingly important.
The bigger takeaway is clear: Security risks in crypto are evolving, and even advanced platforms must continuously strengthen their defenses.
AI can improve efficiency, but it also introduces new security challenges that cannot be ignored.
#Binance / #Hack
A reported security incident involving Binance has highlighted a new and concerning type of cybersecurity threat.
According to Reuters, the attacker allegedly exploited a compromised computer and used an internal AI tool to gain control over wallets.
What makes this incident particularly concerning is the reported combination of compromised devices, AI-assisted access, and wallet security vulnerabilities. It shows how attackers may use legitimate internal tools as part of sophisticated cyberattacks.
As AI becomes more deeply integrated into crypto infrastructure, protecting internal systems, access permissions, and sensitive wallet operations is becoming increasingly important.
The bigger takeaway is clear: Security risks in crypto are evolving, and even advanced platforms must continuously strengthen their defenses.
AI can improve efficiency, but it also introduces new security challenges that cannot be ignored.
#Binance / #Hack
2
236

·
--
North Korea stole $7.61B in crypto this year, and not one big hit used a code exploit.
BitOK counts 38 incidents, Jan-Oct 2026:
• All six biggest attacks hijacked the people and systems that sign withdrawals
• $2.86B frozen or seized, $4.75B out of reach
• Binance accounts for $6.41B of the total
Every withdrawal carried valid signatures. Audits of contracts can't catch a compromised laptop or signing service. Stablecoins got frozen fast, so the thieves swapped into $ETH, which no issuer can freeze.
The takeaway: operational security matters more than code audits now. Watch how exchanges and multisig teams change signer controls.
Which matters more for your trust in a platform: code audits or signer security?
#CryptoSecurity #Hack #Binance $BNB
North Korea stole $7.61B in crypto this year, and not one big hit used a code exploit.
BitOK counts 38 incidents, Jan-Oct 2026:
• All six biggest attacks hijacked the people and systems that sign withdrawals
• $2.86B frozen or seized, $4.75B out of reach
• Binance accounts for $6.41B of the total
Every withdrawal carried valid signatures. Audits of contracts can't catch a compromised laptop or signing service. Stablecoins got frozen fast, so the thieves swapped into $ETH , which no issuer can freeze.
The takeaway: operational security matters more than code audits now. Watch how exchanges and multisig teams change signer controls.
Which matters more for your trust in a platform: code audits or signer security?
#CryptoSecurity #Hack #Binance $BNB
BitOK counts 38 incidents, Jan-Oct 2026:
• All six biggest attacks hijacked the people and systems that sign withdrawals
• $2.86B frozen or seized, $4.75B out of reach
• Binance accounts for $6.41B of the total
Every withdrawal carried valid signatures. Audits of contracts can't catch a compromised laptop or signing service. Stablecoins got frozen fast, so the thieves swapped into $ETH , which no issuer can freeze.
The takeaway: operational security matters more than code audits now. Watch how exchanges and multisig teams change signer controls.
Which matters more for your trust in a platform: code audits or signer security?
#CryptoSecurity #Hack #Binance $BNB
1
If you're an iPhone user, read this.
Hackers just stole $4.06 MILLION in crypto through cyberattacks that started with just one click.
The victim said they tapped an ad in Safari before wallet apps were emptied.
An iOS exploit kit such as DarkSword is suspected.
DarkSword
#Crypto #Hack
If you're an iPhone user, read this.
Hackers just stole $4.06 MILLION in crypto through cyberattacks that started with just one click.
The victim said they tapped an ad in Safari before wallet apps were emptied.
An iOS exploit kit such as DarkSword is suspected.
DarkSword
#Crypto #Hack
Hackers just stole $4.06 MILLION in crypto through cyberattacks that started with just one click.
The victim said they tapped an ad in Safari before wallet apps were emptied.
An iOS exploit kit such as DarkSword is suspected.
DarkSword
#Crypto #Hack
81
🚨 How Did Hackers Infiltrate Binance’s Wallet Infrastructure?
The reported attack highlights how dangerous social engineering can be, even for major crypto platforms.
According to the details, attackers first impersonated company recruiters and approached a Binance engineer through a fake hiring process. After two rounds of interviews, they sent the engineer a test assignment to download. Hidden inside the assignment was malicious code that went undetected by security systems.
Once the engineer’s computer was compromised, the attackers reportedly used an internal AI tool to move further into the company's environment, access other employees' devices, and steal login credentials.
The situation escalated on October 29, when the attackers deployed a malicious container and targeted the system responsible for signing cryptocurrency transactions.
The biggest takeaway? Security isn't just about protecting servers and wallets. One compromised employee device can potentially become the entry point to much larger systems.
In crypto, even the strongest infrastructure is only as secure as its weakest access point. 🔐
#Binance #Hack
🚨 How Did Hackers Infiltrate Binance’s Wallet Infrastructure?
The reported attack highlights how dangerous social engineering can be, even for major crypto platforms.
According to the details, attackers first impersonated company recruiters and approached a Binance engineer through a fake hiring process. After two rounds of interviews, they sent the engineer a test assignment to download. Hidden inside the assignment was malicious code that went undetected by security systems.
Once the engineer’s computer was compromised, the attackers reportedly used an internal AI tool to move further into the company's environment, access other employees' devices, and steal login credentials.
The situation escalated on October 29, when the attackers deployed a malicious container and targeted the system responsible for signing cryptocurrency transactions.
The biggest takeaway? Security isn't just about protecting servers and wallets. One compromised employee device can potentially become the entry point to much larger systems.
In crypto, even the strongest infrastructure is only as secure as its weakest access point. 🔐
#Binance #Hack
The reported attack highlights how dangerous social engineering can be, even for major crypto platforms.
According to the details, attackers first impersonated company recruiters and approached a Binance engineer through a fake hiring process. After two rounds of interviews, they sent the engineer a test assignment to download. Hidden inside the assignment was malicious code that went undetected by security systems.
Once the engineer’s computer was compromised, the attackers reportedly used an internal AI tool to move further into the company's environment, access other employees' devices, and steal login credentials.
The situation escalated on October 29, when the attackers deployed a malicious container and targeted the system responsible for signing cryptocurrency transactions.
The biggest takeaway? Security isn't just about protecting servers and wallets. One compromised employee device can potentially become the entry point to much larger systems.
In crypto, even the strongest infrastructure is only as secure as its weakest access point. 🔐
#Binance #Hack
416
·
--
70.5M $POL stolen in the Polymarket and Binance hacks could be pulled back with a hard fork.
What happened:
• A proposal posted Nov 4 would zero the balances of 5 frozen attacker wallets (23.86M POL from Polymarket, 46.63M from Binance) and credit verified recovery wallets
• Total POL supply stays the same. Block producers already blocked the wallets, but a block list can't return the funds
• It's only a proposal: needs governance approval, Amoy testnet testing and a client update. No activation date yet
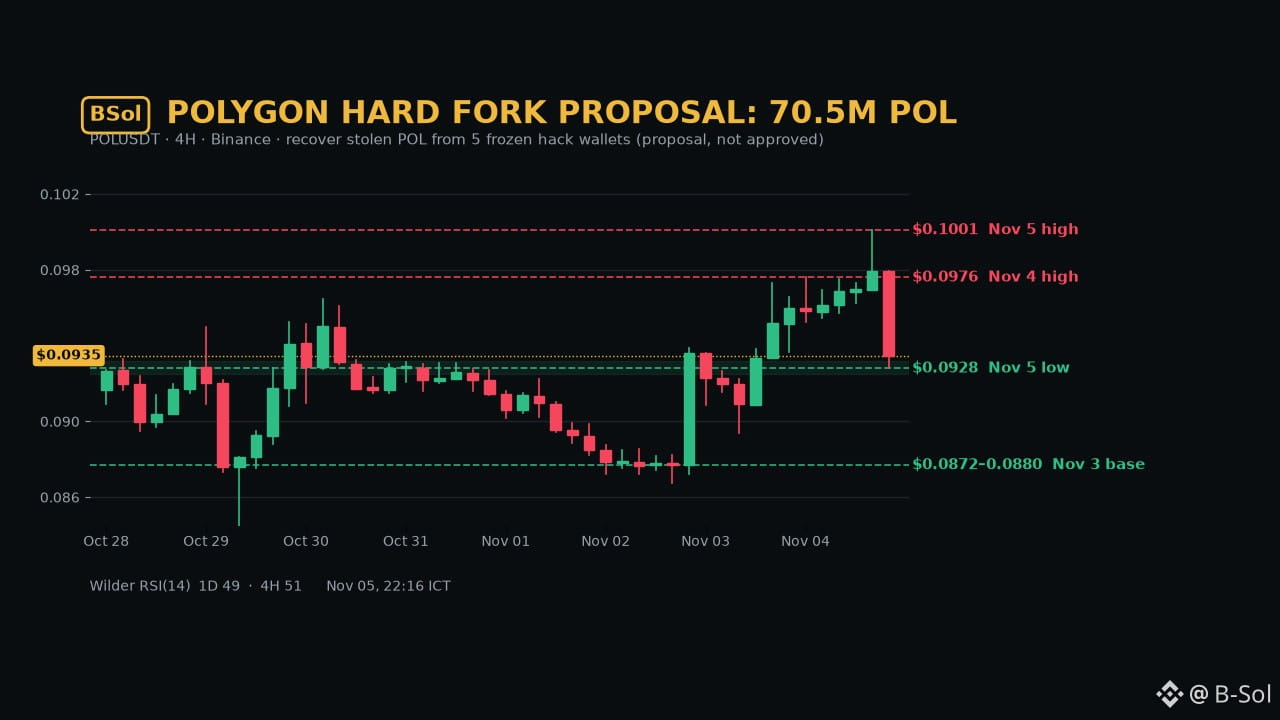
Chart: $POL $0.0935 on Binance, -1.9% 24h after a rejection at $0.1001. Support $0.0925-0.0932, then $0.0872-0.0880. Resistance $0.0976, then $0.1001. Wilder RSI 1D ~49 / 4H ~51.
Watch: a 4H close above $0.0976 or below $0.0872.
Rolling back balances on a major chain: justified exception or a bad precedent? Which side are you on?
#Polygon #POL #CryptoNews #Hack
70.5M $POL stolen in the Polymarket and Binance hacks could be pulled back with a hard fork.
What happened:
• A proposal posted Nov 4 would zero the balances of 5 frozen attacker wallets (23.86M POL from Polymarket, 46.63M from Binance) and credit verified recovery wallets
• Total POL supply stays the same. Block producers already blocked the wallets, but a block list can't return the funds
• It's only a proposal: needs governance approval, Amoy testnet testing and a client update. No activation date yet
Chart: $POL $0.0935 on Binance, -1.9% 24h after a rejection at $0.1001. Support $0.0925-0.0932, then $0.0872-0.0880. Resistance $0.0976, then $0.1001. Wilder RSI 1D ~49 / 4H ~51.
Watch: a 4H close above $0.0976 or below $0.0872.
Rolling back balances on a major chain: justified exception or a bad precedent? Which side are you on?
#Polygon #POL #CryptoNews #Hack
What happened:
• A proposal posted Nov 4 would zero the balances of 5 frozen attacker wallets (23.86M POL from Polymarket, 46.63M from Binance) and credit verified recovery wallets
• Total POL supply stays the same. Block producers already blocked the wallets, but a block list can't return the funds
• It's only a proposal: needs governance approval, Amoy testnet testing and a client update. No activation date yet
Chart: $POL $0.0935 on Binance, -1.9% 24h after a rejection at $0.1001. Support $0.0925-0.0932, then $0.0872-0.0880. Resistance $0.0976, then $0.1001. Wilder RSI 1D ~49 / 4H ~51.
Watch: a 4H close above $0.0976 or below $0.0872.
Rolling back balances on a major chain: justified exception or a bad precedent? Which side are you on?
#Polygon #POL #CryptoNews #Hack
26

·
--
Article
The Most Dangerous Hacker in Human History!The FBI Issues an International Arrest Warrant Against North Korea's Cyber Mastermind
Imagine being accused of helping orchestrate cyberattacks that shook Hollywood, robbed one of the world's financial institutions, and brought hospitals across the globe to a standstill.
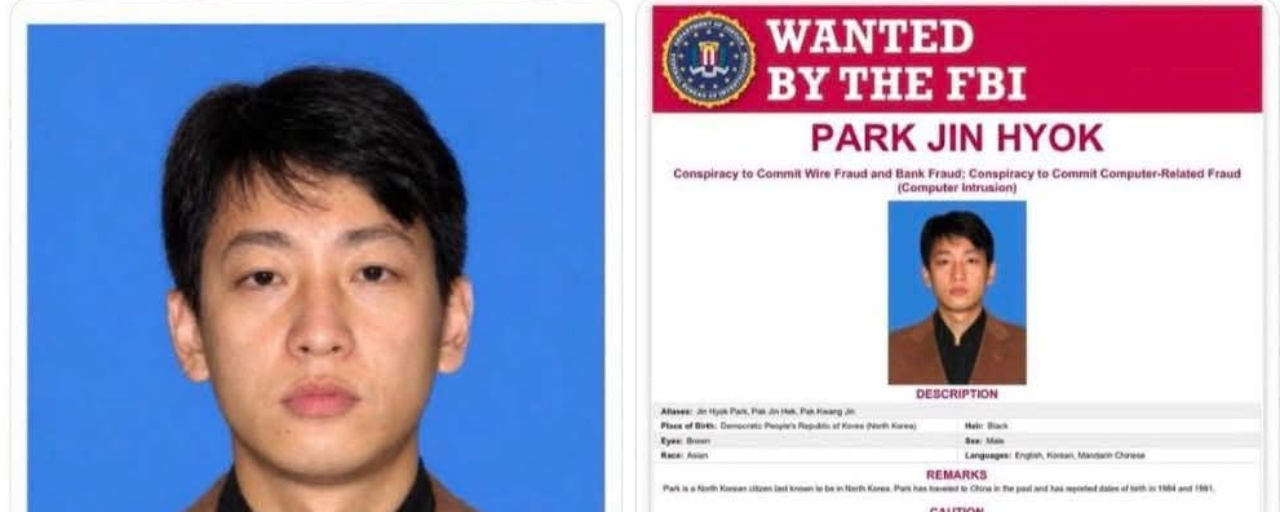
Meet Pak Jin-hyok — the North Korean computer programmer wanted by the FBI.
And here's what makes this story terrifying: U.S. authorities have linked him to a state-sponsored hacking conspiracy responsible for some of the most notorious cyber operations of the modern era.
THE CYBERATTACKS THAT PUT HIM ON THE FBI'S MOST-WANTED LIST:
1. SONY PICTURES HACK (2014)
A devastating attack that exposed confidential corporate emails, employee information, and unreleased Hollywood films. The breach sent shockwaves through the entertainment industry.
2. THE $81 MILLION BANGLADESH BANK HEIST (2016)
Hackers exploited the international banking system to steal approximately $81 million from Bangladesh's central bank. U.S. authorities linked Pak Jin-hyok to the conspiracy behind the attack.
3. WANNACRY RANSOMWARE (2017)
One of the most destructive cyberattacks ever recorded. WannaCry infected more than 300,000 computers across approximately 150 countries, crippling Britain's National Health Service and disrupting businesses worldwide.
4. A BILLION-DOLLAR CYBERCRIME CONSPIRACY
In 2021, the U.S. Department of Justice charged three North Korean hackers, including Pak Jin-hyok, in connection with an alleged conspiracy involving more than $1.3 BILLION in attempted and successful thefts and extortion.
Think about that number.
BUT THIS IS BIGGER THAN ONE HACKER...
U.S. authorities have repeatedly warned that North Korea uses sophisticated cybercrime operations to generate revenue for the regime.
That money can help support:
• Nuclear weapons and ballistic missile programs.
• Military development and modernization.
• The regime's broader strategic objectives.
AND HERE'S THE CATCH...
Pak Jin-hyok was publicly identified and charged by U.S. authorities, and the FBI issued a wanted notice for him.
But his last known location was North Korea — a country that does not cooperate with U.S. law enforcement in handing over its wanted citizens.
A hacker accused of participating in attacks spanning continents. A global cybercrime operation. And a suspect still beyond the FBI's reach.
$AIN #Hack $BTC #SouthKorea $ETH #FBI
The Most Dangerous Hacker in Human History!
The FBI Issues an International Arrest Warrant Against North Korea's Cyber Mastermind
Imagine being accused of helping orchestrate cyberattacks that shook Hollywood, robbed one of the world's financial institutions, and brought hospitals across the globe to a standstill.
Meet Pak Jin-hyok — the North Korean computer programmer wanted by the FBI.
And here's what makes this story terrifying: U.S. authorities have linked him to a state-sponsored hacking conspiracy responsible for some of the most notorious cyber operations of the modern era.
THE CYBERATTACKS THAT PUT HIM ON THE FBI'S MOST-WANTED LIST:
1. SONY PICTURES HACK (2014)
A devastating attack that exposed confidential corporate emails, employee information, and unreleased Hollywood films. The breach sent shockwaves through the entertainment industry.
2. THE $81 MILLION BANGLADESH BANK HEIST (2016)
Hackers exploited the international banking system to steal approximately $81 million from Bangladesh's central bank. U.S. authorities linked Pak Jin-hyok to the conspiracy behind the attack.
3. WANNACRY RANSOMWARE (2017)
One of the most destructive cyberattacks ever recorded. WannaCry infected more than 300,000 computers across approximately 150 countries, crippling Britain's National Health Service and disrupting businesses worldwide.
4. A BILLION-DOLLAR CYBERCRIME CONSPIRACY
In 2021, the U.S. Department of Justice charged three North Korean hackers, including Pak Jin-hyok, in connection with an alleged conspiracy involving more than $1.3 BILLION in attempted and successful thefts and extortion.
Think about that number.
BUT THIS IS BIGGER THAN ONE HACKER...
U.S. authorities have repeatedly warned that North Korea uses sophisticated cybercrime operations to generate revenue for the regime.
That money can help support:
• Nuclear weapons and ballistic missile programs.
• Military development and modernization.
• The regime's broader strategic objectives.
AND HERE'S THE CATCH...
Pak Jin-hyok was publicly identified and charged by U.S. authorities, and the FBI issued a wanted notice for him.
But his last known location was North Korea — a country that does not cooperate with U.S. law enforcement in handing over its wanted citizens.
A hacker accused of participating in attacks spanning continents. A global cybercrime operation. And a suspect still beyond the FBI's reach.
$AIN #Hack $BTC #SouthKorea $ETH #FBI
Imagine being accused of helping orchestrate cyberattacks that shook Hollywood, robbed one of the world's financial institutions, and brought hospitals across the globe to a standstill.
Meet Pak Jin-hyok — the North Korean computer programmer wanted by the FBI.
And here's what makes this story terrifying: U.S. authorities have linked him to a state-sponsored hacking conspiracy responsible for some of the most notorious cyber operations of the modern era.
THE CYBERATTACKS THAT PUT HIM ON THE FBI'S MOST-WANTED LIST:
1. SONY PICTURES HACK (2014)
A devastating attack that exposed confidential corporate emails, employee information, and unreleased Hollywood films. The breach sent shockwaves through the entertainment industry.
2. THE $81 MILLION BANGLADESH BANK HEIST (2016)
Hackers exploited the international banking system to steal approximately $81 million from Bangladesh's central bank. U.S. authorities linked Pak Jin-hyok to the conspiracy behind the attack.
3. WANNACRY RANSOMWARE (2017)
One of the most destructive cyberattacks ever recorded. WannaCry infected more than 300,000 computers across approximately 150 countries, crippling Britain's National Health Service and disrupting businesses worldwide.
4. A BILLION-DOLLAR CYBERCRIME CONSPIRACY
In 2021, the U.S. Department of Justice charged three North Korean hackers, including Pak Jin-hyok, in connection with an alleged conspiracy involving more than $1.3 BILLION in attempted and successful thefts and extortion.
Think about that number.
BUT THIS IS BIGGER THAN ONE HACKER...
U.S. authorities have repeatedly warned that North Korea uses sophisticated cybercrime operations to generate revenue for the regime.
That money can help support:
• Nuclear weapons and ballistic missile programs.
• Military development and modernization.
• The regime's broader strategic objectives.
AND HERE'S THE CATCH...
Pak Jin-hyok was publicly identified and charged by U.S. authorities, and the FBI issued a wanted notice for him.
But his last known location was North Korea — a country that does not cooperate with U.S. law enforcement in handing over its wanted citizens.
A hacker accused of participating in attacks spanning continents. A global cybercrime operation. And a suspect still beyond the FBI's reach.
$AIN #Hack $BTC #SouthKorea $ETH #FBI
1
140
·
--
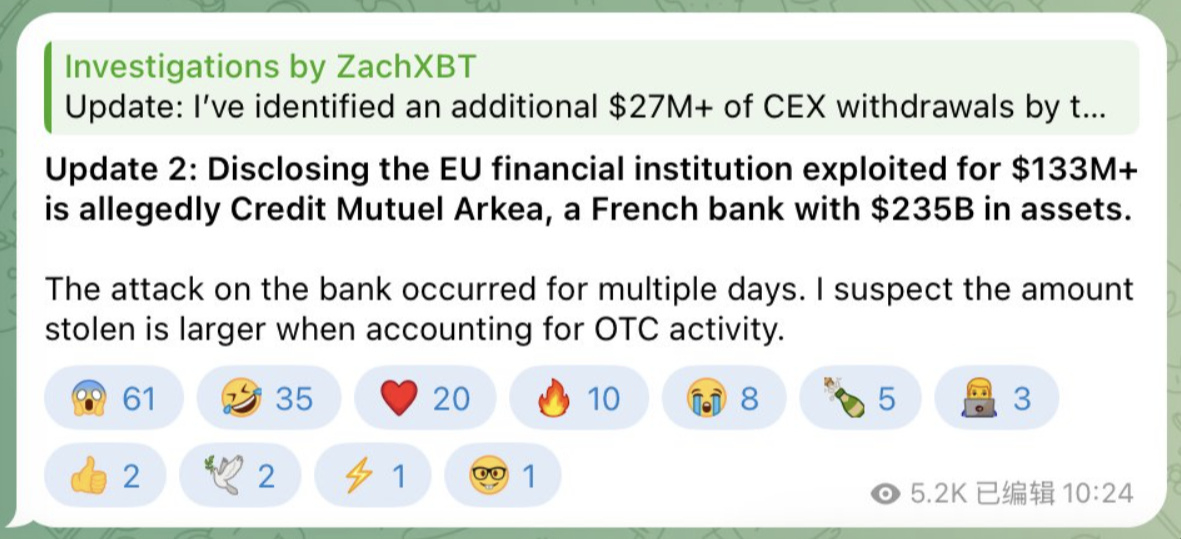
🏦 The $133M "EU entity" hack now has a name. And it's a bank.
ZachXBT says the victim is Crédit Mutuel Arkéa, a French banking group with about $235B in assets. The bank has not confirmed or denied anything.
What we know so far:
→ Withdrawals hit accounts at Kraken, Crypto.com and OKX starting Nov 1
→ About $62.98M in stablecoins was swapped into 27,553 $ETH in roughly four hours
→ Part went through instant exchanges, part into $XMR, part across bridges
→ ZachXBT is "highly confident" this is not North Korea's Lazarus Group
→ Kraken restricted linked accounts and says its own systems were not breached
Plot twist: remember the "whale" who bought 27,553 ETH at $2,286 on Nov 2 and got cheered as a dip buyer? Those are exactly the numbers Bitquery tied to this theft.
ZachXBT's biggest complaint is the silence. He says more than $30M got laundered that could have been frozen if the theft had been reported quickly.
Should any institution that loses crypto be forced to disclose it within 24 hours? Yes or no? 👇
#CryptoSecurity #ZachXBT #Hack #ETH
🏦 The $133M "EU entity" hack now has a name. And it's a bank.
ZachXBT says the victim is Crédit Mutuel Arkéa, a French banking group with about $235B in assets. The bank has not confirmed or denied anything.
What we know so far:
→ Withdrawals hit accounts at Kraken, Crypto.com and OKX starting Nov 1
→ About $62.98M in stablecoins was swapped into 27,553 $ETH in roughly four hours
→ Part went through instant exchanges, part into $XMR, part across bridges
→ ZachXBT is "highly confident" this is not North Korea's Lazarus Group
→ Kraken restricted linked accounts and says its own systems were not breached
Plot twist: remember the "whale" who bought 27,553 ETH at $2,286 on Nov 2 and got cheered as a dip buyer? Those are exactly the numbers Bitquery tied to this theft.
ZachXBT's biggest complaint is the silence. He says more than $30M got laundered that could have been frozen if the theft had been reported quickly.
Should any institution that loses crypto be forced to disclose it within 24 hours? Yes or no? 👇
#CryptoSecurity #ZachXBT #Hack #ETH
ZachXBT says the victim is Crédit Mutuel Arkéa, a French banking group with about $235B in assets. The bank has not confirmed or denied anything.
What we know so far:
→ Withdrawals hit accounts at Kraken, Crypto.com and OKX starting Nov 1
→ About $62.98M in stablecoins was swapped into 27,553 $ETH in roughly four hours
→ Part went through instant exchanges, part into $XMR, part across bridges
→ ZachXBT is "highly confident" this is not North Korea's Lazarus Group
→ Kraken restricted linked accounts and says its own systems were not breached
Plot twist: remember the "whale" who bought 27,553 ETH at $2,286 on Nov 2 and got cheered as a dip buyer? Those are exactly the numbers Bitquery tied to this theft.
ZachXBT's biggest complaint is the silence. He says more than $30M got laundered that could have been frozen if the theft had been reported quickly.
Should any institution that loses crypto be forced to disclose it within 24 hours? Yes or no? 👇
#CryptoSecurity #ZachXBT #Hack #ETH
1
280
OMG, this isn't just a crypto problem anymore. Hackers are using AI to go after the whole financial system🚨⚠️
Take the Binance hack. They got into one infected laptop, then used the company's own internal AI tools as a stepping stone and worked their way into the wallet-signing system.
And it's not only crypto!! Look at the banks this week:
🇫🇷 French banking group Crédit Mutuel Arkéa confirmed it got hit. Over $133M is involved, and the target was its online bank Fortuneo. Some transfers in the app still don't work.
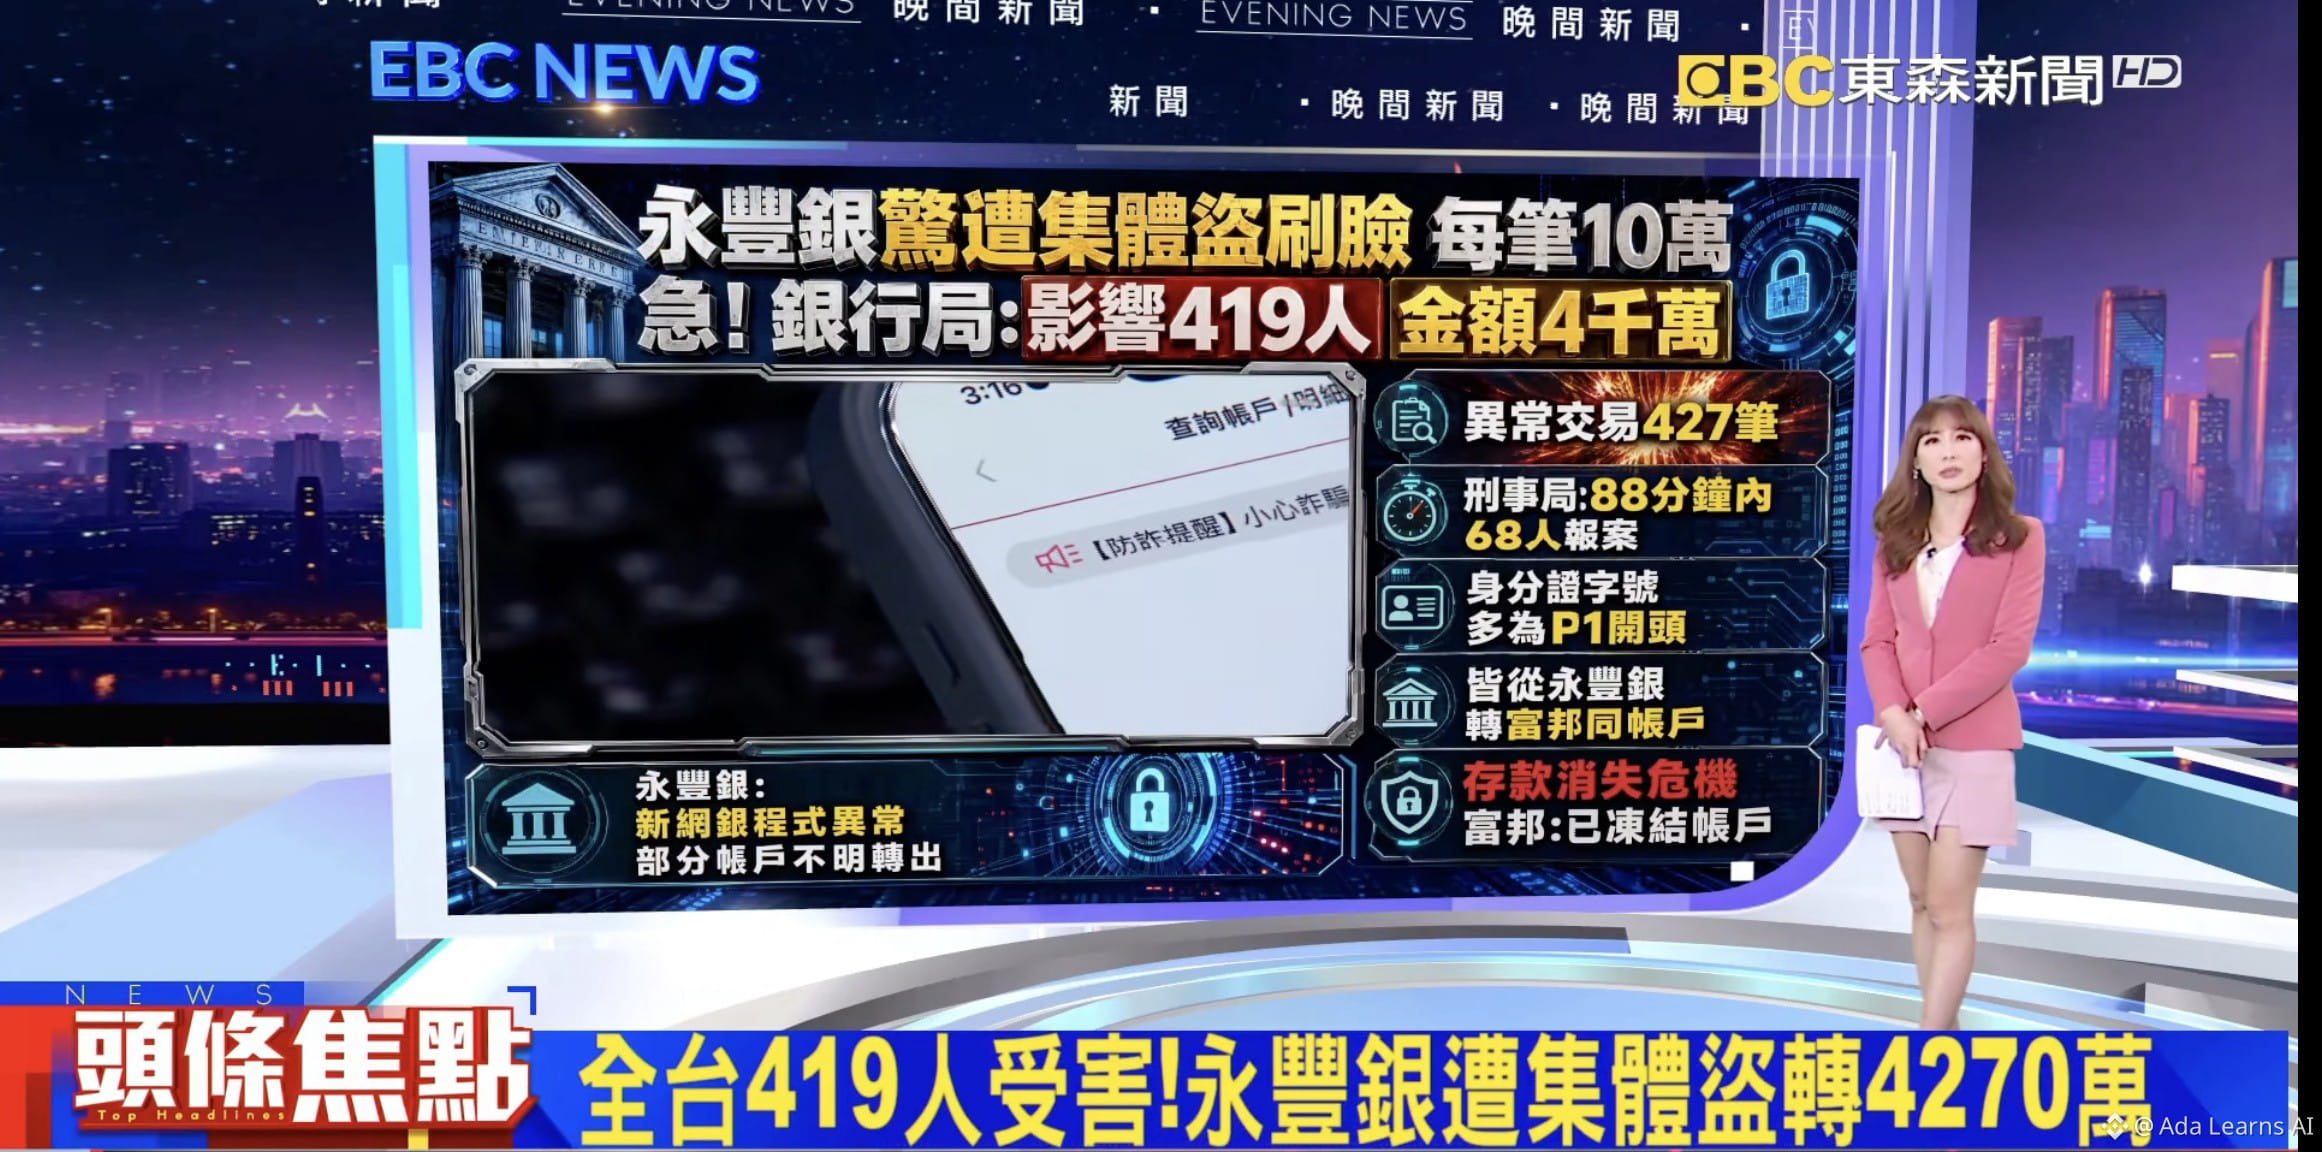
Taiwan's Bank SinoPac had a wave of unauthorized transfers: 418 customers, 427 transactions, about NT$41.76M (~$1.3M), all sent to the same account.
AI makes attacks fast and cheap, and hackers can hit lots of targets at once. They used to pick a few big names. Now they'll test every exchange, every online bank and every vendor, one by one. If the defense is one step slow anywhere, the money's gone #AI #crypto #Hack
OMG, this isn't just a crypto problem anymore. Hackers are using AI to go after the whole financial system🚨⚠️
Take the Binance hack. They got into one infected laptop, then used the company's own internal AI tools as a stepping stone and worked their way into the wallet-signing system.
And it's not only crypto!! Look at the banks this week:
🇫🇷 French banking group Crédit Mutuel Arkéa confirmed it got hit. Over $133M is involved, and the target was its online bank Fortuneo. Some transfers in the app still don't work.
Taiwan's Bank SinoPac had a wave of unauthorized transfers: 418 customers, 427 transactions, about NT$41.76M (~$1.3M), all sent to the same account.
AI makes attacks fast and cheap, and hackers can hit lots of targets at once. They used to pick a few big names. Now they'll test every exchange, every online bank and every vendor, one by one. If the defense is one step slow anywhere, the money's gone #AI #crypto #Hack
Take the Binance hack. They got into one infected laptop, then used the company's own internal AI tools as a stepping stone and worked their way into the wallet-signing system.
And it's not only crypto!! Look at the banks this week:
🇫🇷 French banking group Crédit Mutuel Arkéa confirmed it got hit. Over $133M is involved, and the target was its online bank Fortuneo. Some transfers in the app still don't work.
Taiwan's Bank SinoPac had a wave of unauthorized transfers: 418 customers, 427 transactions, about NT$41.76M (~$1.3M), all sent to the same account.
AI makes attacks fast and cheap, and hackers can hit lots of targets at once. They used to pick a few big names. Now they'll test every exchange, every online bank and every vendor, one by one. If the defense is one step slow anywhere, the money's gone #AI #crypto #Hack
1.7k
·
--
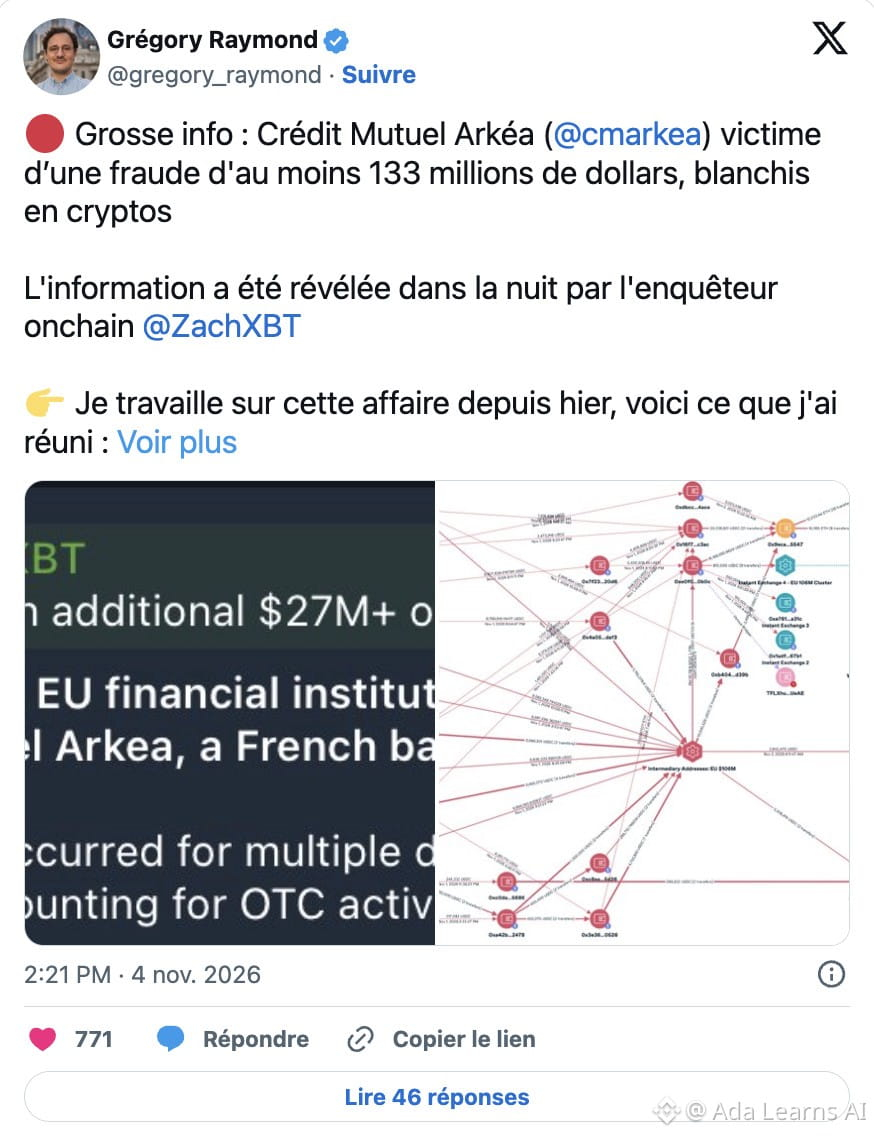
A French bank with $235B in assets may have just lost $133M+ in crypto.
ZachXBT named Crédit Mutuel Arkéa as the target of a multi-day theft.
The bank has issued no official statement as of Nov 4.
ZachXBT says the real total could be higher.
Second big institutional hit this week, after the Liquid Network exploit story. Attackers keep going after big custodians, not just DeFi protocols. Watch for bank confirmation and any stolen funds moving through mixers or $TRX rails.
Do traditional banks holding crypto worry you more than exchanges do? Yes or no?
#ZachXBT #CryptoSecurity #Hack $BTC
A French bank with $235B in assets may have just lost $133M+ in crypto.
ZachXBT named Crédit Mutuel Arkéa as the target of a multi-day theft.
The bank has issued no official statement as of Nov 4.
ZachXBT says the real total could be higher.
Second big institutional hit this week, after the Liquid Network exploit story. Attackers keep going after big custodians, not just DeFi protocols. Watch for bank confirmation and any stolen funds moving through mixers or $TRX rails.
Do traditional banks holding crypto worry you more than exchanges do? Yes or no?
#ZachXBT #CryptoSecurity #Hack $BTC
ZachXBT named Crédit Mutuel Arkéa as the target of a multi-day theft.
The bank has issued no official statement as of Nov 4.
ZachXBT says the real total could be higher.
Second big institutional hit this week, after the Liquid Network exploit story. Attackers keep going after big custodians, not just DeFi protocols. Watch for bank confirmation and any stolen funds moving through mixers or $TRX rails.
Do traditional banks holding crypto worry you more than exchanges do? Yes or no?
#ZachXBT #CryptoSecurity #Hack $BTC
5
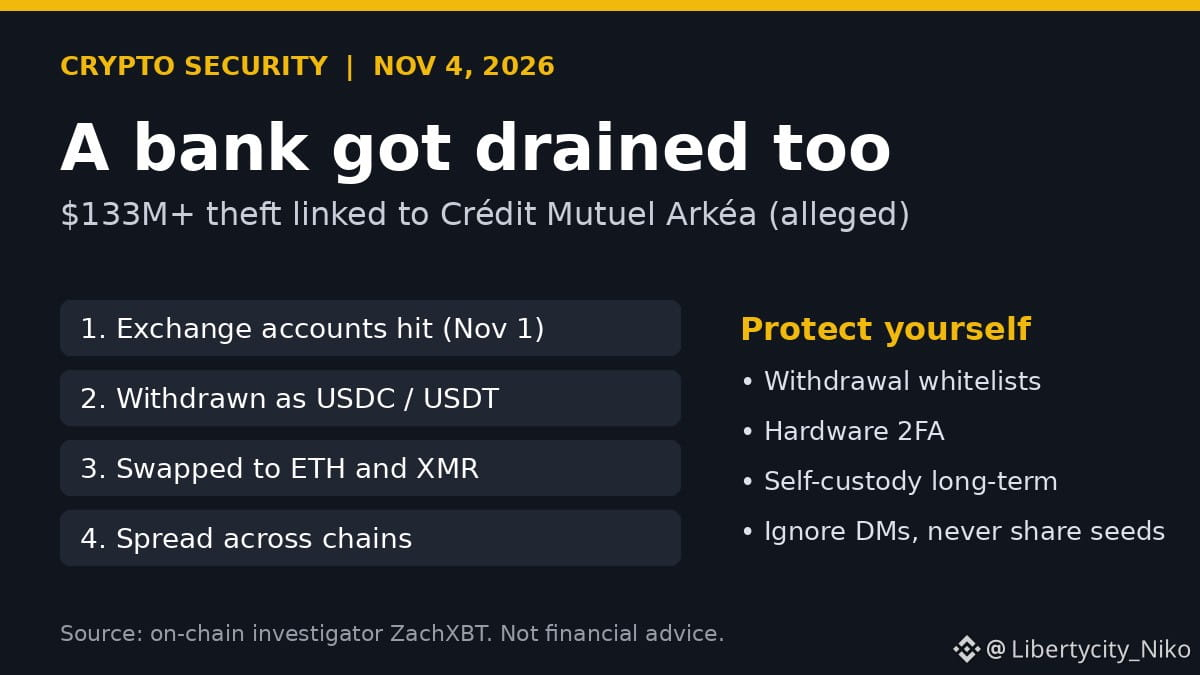
A French bank just showed up in a crypto theft story.
On-chain investigator ZachXBT says the institution behind a theft of more than $133 million is Crédit Mutuel Arkéa, a French banking group with roughly $235 billion in assets. It's still an allegation from on-chain work, so treat the name with care until the bank confirms.
What happened, per ZachXBT: funds were pulled from several exchange accounts on Nov 1, withdrawn as USDC and USDT, then swapped into $ETH and the privacy coin $XMR and spread across chains.
My take: as big institutions bring big balances into crypto, attackers follow the money. An exchange account is only as safe as the people and keys behind it. If you hold on an exchange, use withdrawal address whitelists and hardware 2FA, and keep long-term coins in self-custody. Never share seed phrases and ignore DMs.
#CryptoSecurity #CryptoNews #Hack
Not financial advice.
A French bank just showed up in a crypto theft story.
On-chain investigator ZachXBT says the institution behind a theft of more than $133 million is Crédit Mutuel Arkéa, a French banking group with roughly $235 billion in assets. It's still an allegation from on-chain work, so treat the name with care until the bank confirms.
What happened, per ZachXBT: funds were pulled from several exchange accounts on Nov 1, withdrawn as USDC and USDT, then swapped into $ETH and the privacy coin $XMR and spread across chains.
My take: as big institutions bring big balances into crypto, attackers follow the money. An exchange account is only as safe as the people and keys behind it. If you hold on an exchange, use withdrawal address whitelists and hardware 2FA, and keep long-term coins in self-custody. Never share seed phrases and ignore DMs.
#CryptoSecurity #CryptoNews #Hack
Not financial advice.
On-chain investigator ZachXBT says the institution behind a theft of more than $133 million is Crédit Mutuel Arkéa, a French banking group with roughly $235 billion in assets. It's still an allegation from on-chain work, so treat the name with care until the bank confirms.
What happened, per ZachXBT: funds were pulled from several exchange accounts on Nov 1, withdrawn as USDC and USDT, then swapped into $ETH and the privacy coin $XMR and spread across chains.
My take: as big institutions bring big balances into crypto, attackers follow the money. An exchange account is only as safe as the people and keys behind it. If you hold on an exchange, use withdrawal address whitelists and hardware 2FA, and keep long-term coins in self-custody. Never share seed phrases and ignore DMs.
#CryptoSecurity #CryptoNews #Hack
Not financial advice.
515

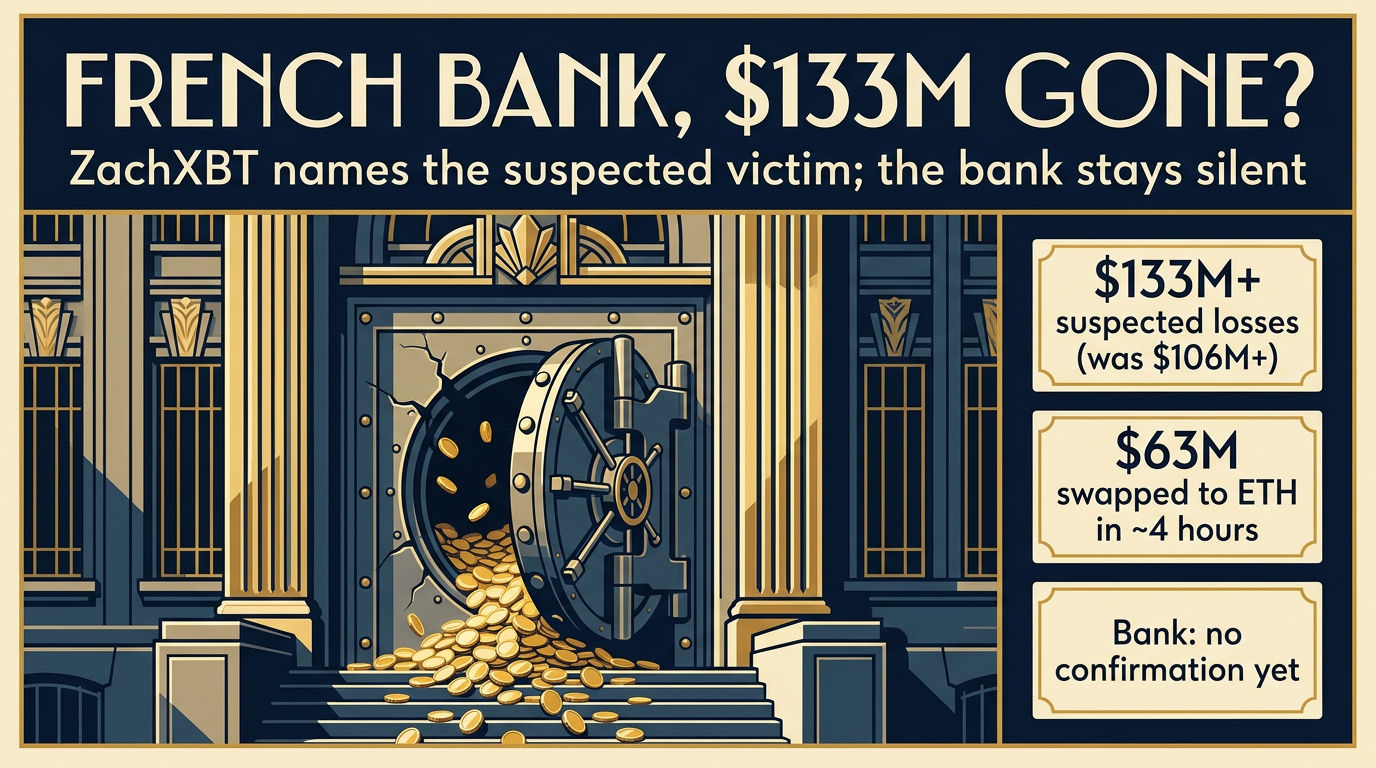
A French bank with $235B in assets may have just become the biggest institutional crypto-theft story of the week, and it isn't even the Binance one.
On-chain investigator ZachXBT now names Crédit Mutuel Arkéa as the suspected victim of a theft he puts at more than $133 million. Important: the bank has not confirmed anything and had issued no public statement as of Nov 4. This is the investigator's identification, not an official finding.
What's reported so far:
• First flagged Nov 2 at $106M+, then raised after another $27M+ in exchange withdrawals was traced, some after his first alert
• Funds left centralized exchange accounts as USDC and USDT, were swapped into ETH (about $63M within roughly four hours, per Bitquery), then routed through instant-swap services and bridges, with some moved into Monero
• Kraken says the incident did not originate on its platform and it restricted the accounts involved; Crypto.com moved to block related funds; OKX is reviewing
• ZachXBT says late disclosure let $30M+ get laundered that EU law enforcement could possibly have frozen, and suspects OTC activity means the real total is higher
Why it matters: this lands days after the largest exchange hack on record. Two very different victims, one lesson: custody and account-access security is now the main risk story, and speed of disclosure decides whether stolen funds can still be frozen.
Caution: figures may change, and attribution remains unverified until the bank speaks. Treat early numbers as estimates.
Should banks be required to disclose crypto-related breaches within hours, like exchanges are pressured to? Tell me what you think.
#CryptoSecurity #Hack #OnChain $ETH
Not financial advice.
A French bank with $235B in assets may have just become the biggest institutional crypto-theft story of the week, and it isn't even the Binance one.
On-chain investigator ZachXBT now names Crédit Mutuel Arkéa as the suspected victim of a theft he puts at more than $133 million. Important: the bank has not confirmed anything and had issued no public statement as of Nov 4. This is the investigator's identification, not an official finding.
What's reported so far:
• First flagged Nov 2 at $106M+, then raised after another $27M+ in exchange withdrawals was traced, some after his first alert
• Funds left centralized exchange accounts as USDC and USDT, were swapped into ETH (about $63M within roughly four hours, per Bitquery), then routed through instant-swap services and bridges, with some moved into Monero
• Kraken says the incident did not originate on its platform and it restricted the accounts involved; Crypto.com moved to block related funds; OKX is reviewing
• ZachXBT says late disclosure let $30M+ get laundered that EU law enforcement could possibly have frozen, and suspects OTC activity means the real total is higher
Why it matters: this lands days after the largest exchange hack on record. Two very different victims, one lesson: custody and account-access security is now the main risk story, and speed of disclosure decides whether stolen funds can still be frozen.
Caution: figures may change, and attribution remains unverified until the bank speaks. Treat early numbers as estimates.
Should banks be required to disclose crypto-related breaches within hours, like exchanges are pressured to? Tell me what you think.
#CryptoSecurity #Hack #OnChain $ETH
Not financial advice.
On-chain investigator ZachXBT now names Crédit Mutuel Arkéa as the suspected victim of a theft he puts at more than $133 million. Important: the bank has not confirmed anything and had issued no public statement as of Nov 4. This is the investigator's identification, not an official finding.
What's reported so far:
• First flagged Nov 2 at $106M+, then raised after another $27M+ in exchange withdrawals was traced, some after his first alert
• Funds left centralized exchange accounts as USDC and USDT, were swapped into ETH (about $63M within roughly four hours, per Bitquery), then routed through instant-swap services and bridges, with some moved into Monero
• Kraken says the incident did not originate on its platform and it restricted the accounts involved; Crypto.com moved to block related funds; OKX is reviewing
• ZachXBT says late disclosure let $30M+ get laundered that EU law enforcement could possibly have frozen, and suspects OTC activity means the real total is higher
Why it matters: this lands days after the largest exchange hack on record. Two very different victims, one lesson: custody and account-access security is now the main risk story, and speed of disclosure decides whether stolen funds can still be frozen.
Caution: figures may change, and attribution remains unverified until the bank speaks. Treat early numbers as estimates.
Should banks be required to disclose crypto-related breaches within hours, like exchanges are pressured to? Tell me what you think.
#CryptoSecurity #Hack #OnChain $ETH
Not financial advice.
132

🤔 How did hackers gain access to Binance's wallet infrastructure?
The hackers impersonated employers and, after two rounds of interviews, offered a Binance engineer a test assignment to download. This assignment contained malicious code that the security systems failed to detect.
Through the infected computer and an internal AI tool used by Binance, the attackers gained access to the devices of other employees and stole login credentials.
On October 29th, they deployed a malicious container and launched an attack on the system responsible for signing cryptocurrency transactions.
#Hack | #Binance
🤔 How did hackers gain access to Binance's wallet infrastructure?
The hackers impersonated employers and, after two rounds of interviews, offered a Binance engineer a test assignment to download. This assignment contained malicious code that the security systems failed to detect.
Through the infected computer and an internal AI tool used by Binance, the attackers gained access to the devices of other employees and stole login credentials.
On October 29th, they deployed a malicious container and launched an attack on the system responsible for signing cryptocurrency transactions.
#Hack | #Binance
The hackers impersonated employers and, after two rounds of interviews, offered a Binance engineer a test assignment to download. This assignment contained malicious code that the security systems failed to detect.
Through the infected computer and an internal AI tool used by Binance, the attackers gained access to the devices of other employees and stole login credentials.
On October 29th, they deployed a malicious container and launched an attack on the system responsible for signing cryptocurrency transactions.
#Hack | #Binance
hw10009:
@BiBi How much was the job offer for? If was more than employees current salary?
4
20
43.8k
·
--
Bullish
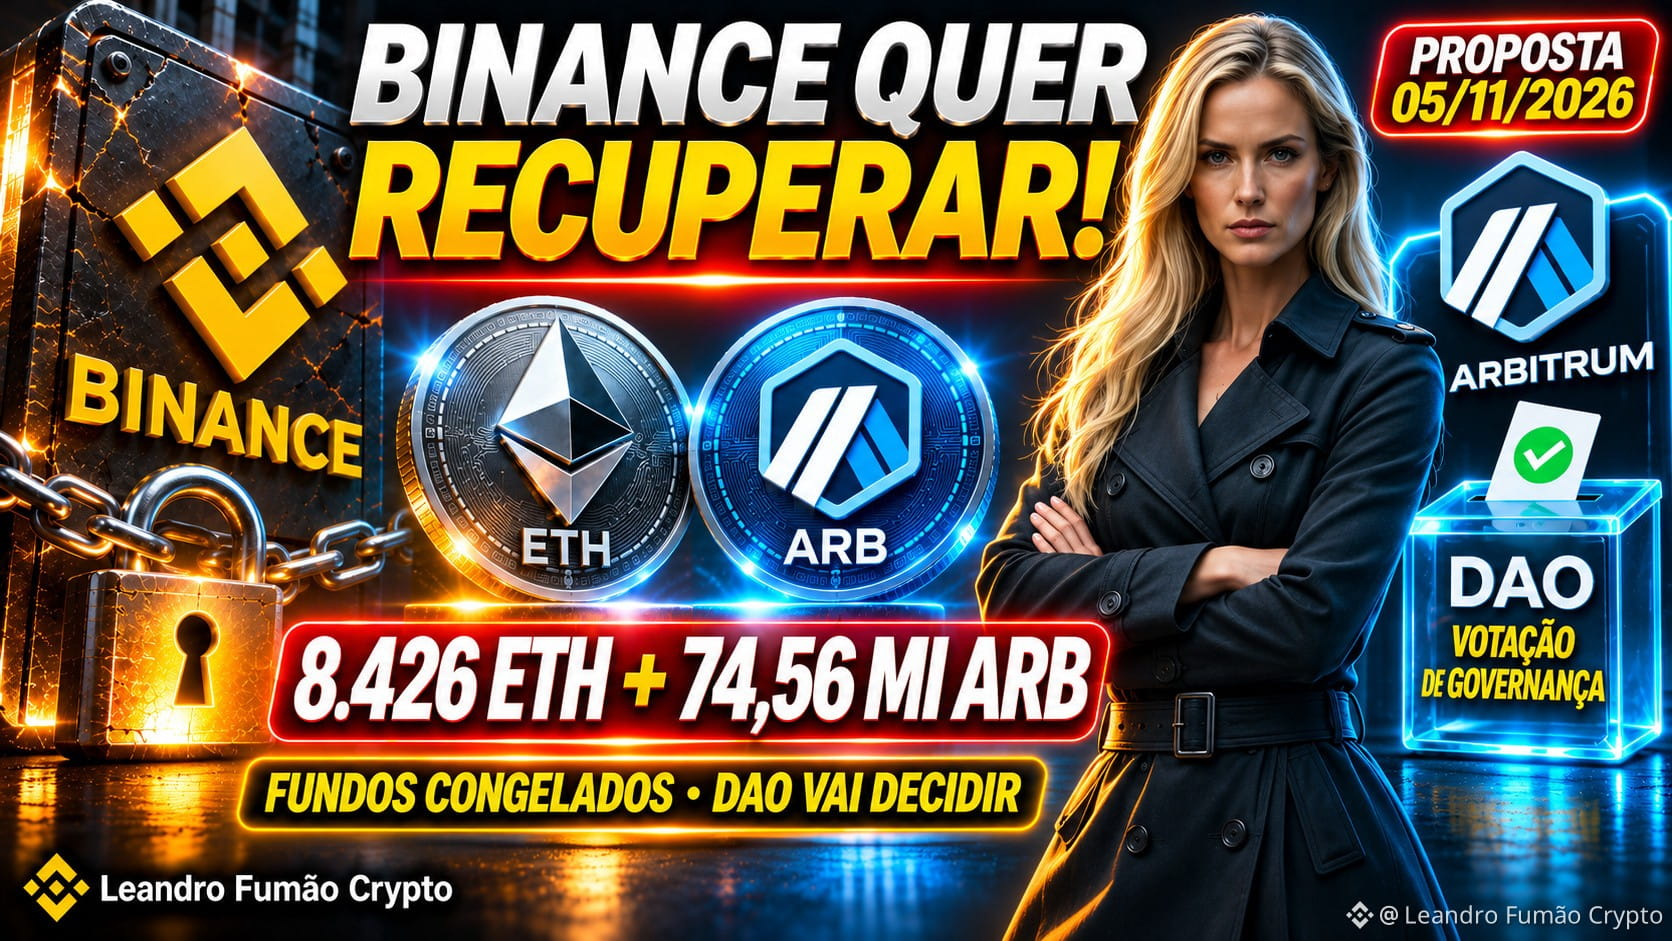
❖BINANCE SEEKS RETURN OF 8,426 ⟠ETH AND 74.56 MILLION 🔷ARB FROZEN ON ARBITRUM❗
Ξ The exchange submitted a formal proposal to the Arbitrum DAO to recover the assets frozen after the hot wallet exploit.
Binance $BNB submitted an official proposal to the Arbitrum DAO requesting the release of 8,425.997 ETH and 74.56 million ARB. The funds were frozen by the Arbitrum Security Council on October 30 in an emergency action following the attack on the exchange’s hot wallet.
The cryptocurrencies are currently held at an intermediate frozen address and can only be moved with DAO approval. Binance is not asking for new funds from the DAO treasury — only the return of assets that have already been frozen.
The governance process is expected to take about 7 weeks or more (forum discussion + temperature check + on-chain vote). The exchange said it will cover users’ losses with SAFU and its own funds.
Meanwhile, Binance is gradually resuming withdrawals and has removed all API keys linked to the SignalPlus platform following a security alert.
This is one of the largest requests to recover funds through DAO governance in 2026. The case tests Arbitrum’s ability to handle emergency freezes and returns transparently.
As Binance tries to recover the assets, market confidence in the security of exchanges and bridges remains under pressure. The decision by ARB holders will be closely watched by the entire community.
💬 Should Binance’s proposal to recover the frozen $ETH and $ARB be approved by the Arbitrum DAO?
#Binance #Arbitrum #Hack
❖BINANCE SEEKS RETURN OF 8,426 ⟠ETH AND 74.56 MILLION 🔷ARB FROZEN ON ARBITRUM❗
Ξ The exchange submitted a formal proposal to the Arbitrum DAO to recover the assets frozen after the hot wallet exploit.
Binance $BNB submitted an official proposal to the Arbitrum DAO requesting the release of 8,425.997 ETH and 74.56 million ARB. The funds were frozen by the Arbitrum Security Council on October 30 in an emergency action following the attack on the exchange’s hot wallet.
The cryptocurrencies are currently held at an intermediate frozen address and can only be moved with DAO approval. Binance is not asking for new funds from the DAO treasury — only the return of assets that have already been frozen.
The governance process is expected to take about 7 weeks or more (forum discussion + temperature check + on-chain vote). The exchange said it will cover users’ losses with SAFU and its own funds.
Meanwhile, Binance is gradually resuming withdrawals and has removed all API keys linked to the SignalPlus platform following a security alert.
This is one of the largest requests to recover funds through DAO governance in 2026. The case tests Arbitrum’s ability to handle emergency freezes and returns transparently.
As Binance tries to recover the assets, market confidence in the security of exchanges and bridges remains under pressure. The decision by ARB holders will be closely watched by the entire community.
💬 Should Binance’s proposal to recover the frozen $ETH and $ARB be approved by the Arbitrum DAO?
#Binance #Arbitrum #Hack
Ξ The exchange submitted a formal proposal to the Arbitrum DAO to recover the assets frozen after the hot wallet exploit.
Binance $BNB submitted an official proposal to the Arbitrum DAO requesting the release of 8,425.997 ETH and 74.56 million ARB. The funds were frozen by the Arbitrum Security Council on October 30 in an emergency action following the attack on the exchange’s hot wallet.
The cryptocurrencies are currently held at an intermediate frozen address and can only be moved with DAO approval. Binance is not asking for new funds from the DAO treasury — only the return of assets that have already been frozen.
The governance process is expected to take about 7 weeks or more (forum discussion + temperature check + on-chain vote). The exchange said it will cover users’ losses with SAFU and its own funds.
Meanwhile, Binance is gradually resuming withdrawals and has removed all API keys linked to the SignalPlus platform following a security alert.
This is one of the largest requests to recover funds through DAO governance in 2026. The case tests Arbitrum’s ability to handle emergency freezes and returns transparently.
As Binance tries to recover the assets, market confidence in the security of exchanges and bridges remains under pressure. The decision by ARB holders will be closely watched by the entire community.
💬 Should Binance’s proposal to recover the frozen $ETH and $ARB be approved by the Arbitrum DAO?
#Binance #Arbitrum #Hack
1.1k
·
--
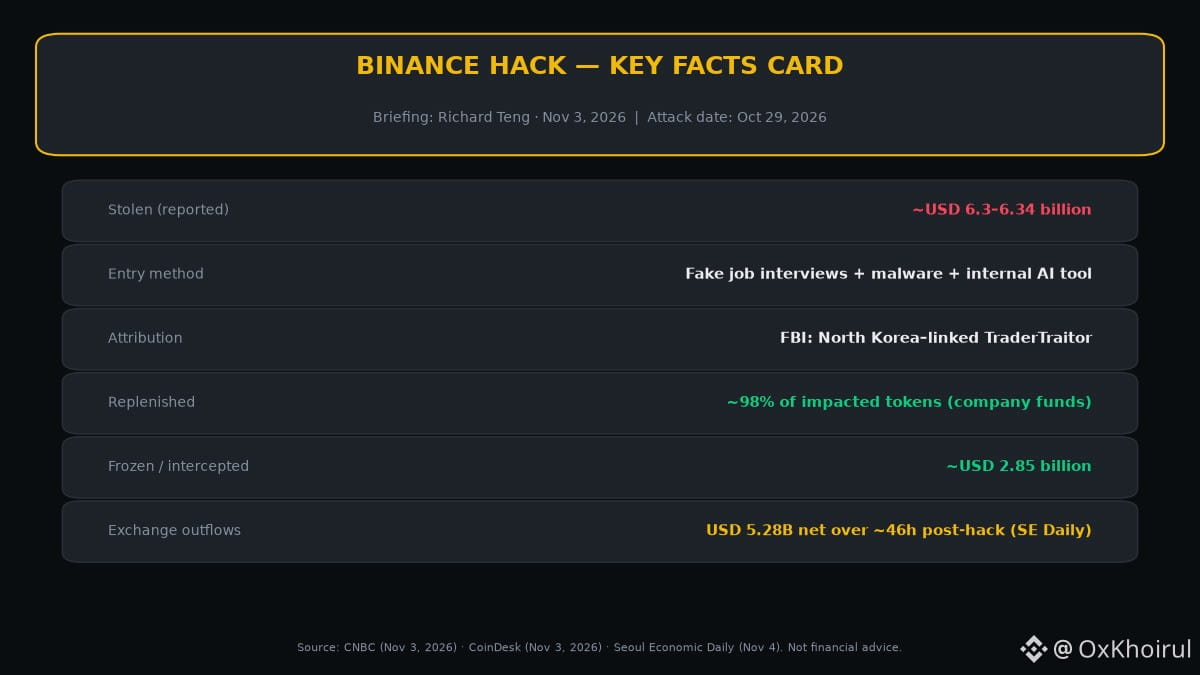
🚨 Biggest crypto hack ever — and the how is wilder than the headline.
Binance’s ~$6.3–6.34B breach (Oct 29) was a months-long campaign, not a one-click phish. Richard Teng (Nov 3): attackers used fake job interviews + malware, then moved through an internal AI tool. FBI links it to North Korea’s TraderTraitor.
What’s calming the room: Binance says ~98% of impacted tokens were replenished with company funds, and ~$2.85B was frozen/intercepted. Still, SE Daily reported $5.28B net exchange outflows over ~46 hours after the hack (flows later stabilizing).
Self-custody matters. So does not downloading “coding tests” from fake recruiters.
Do you trust big CEXs the same after this — yes or no? 👀
$BNB $BTC #Binance #CryptoSecurity #Hack #BinanceSquare
🚨 Biggest crypto hack ever — and the how is wilder than the headline.
Binance’s ~$6.3–6.34B breach (Oct 29) was a months-long campaign, not a one-click phish. Richard Teng (Nov 3): attackers used fake job interviews + malware, then moved through an internal AI tool. FBI links it to North Korea’s TraderTraitor.
What’s calming the room: Binance says ~98% of impacted tokens were replenished with company funds, and ~$2.85B was frozen/intercepted. Still, SE Daily reported $5.28B net exchange outflows over ~46 hours after the hack (flows later stabilizing).
Self-custody matters. So does not downloading “coding tests” from fake recruiters.
Do you trust big CEXs the same after this — yes or no? 👀
$BNB $BTC #Binance #CryptoSecurity #Hack #BinanceSquare
Binance’s ~$6.3–6.34B breach (Oct 29) was a months-long campaign, not a one-click phish. Richard Teng (Nov 3): attackers used fake job interviews + malware, then moved through an internal AI tool. FBI links it to North Korea’s TraderTraitor.
What’s calming the room: Binance says ~98% of impacted tokens were replenished with company funds, and ~$2.85B was frozen/intercepted. Still, SE Daily reported $5.28B net exchange outflows over ~46 hours after the hack (flows later stabilizing).
Self-custody matters. So does not downloading “coding tests” from fake recruiters.
Do you trust big CEXs the same after this — yes or no? 👀
$BNB $BTC #Binance #CryptoSecurity #Hack #BinanceSquare
389
·
--
🔥 Binance hack wipes out $6.3 billion in assets, a record breach! 🚨
It started when an employee installed a tampered Homebrew package in June.
A staged interview in September added a compromised code repo to the mix.
On Oct 29 the thieves moved $3 billion to frozen wallets, the rest still missing.
FBI points to North‑Korea‑linked TraderTraitor, sparking AI‑threat concerns.
What’s your take, is the crypto ecosystem ready for the next wave of AI attacks?
#security #Hack #AI
🔥 Binance hack wipes out $6.3 billion in assets, a record breach! 🚨
It started when an employee installed a tampered Homebrew package in June.
A staged interview in September added a compromised code repo to the mix.
On Oct 29 the thieves moved $3 billion to frozen wallets, the rest still missing.
FBI points to North‑Korea‑linked TraderTraitor, sparking AI‑threat concerns.
What’s your take, is the crypto ecosystem ready for the next wave of AI attacks?
#security #Hack #AI
It started when an employee installed a tampered Homebrew package in June.
A staged interview in September added a compromised code repo to the mix.
On Oct 29 the thieves moved $3 billion to frozen wallets, the rest still missing.
FBI points to North‑Korea‑linked TraderTraitor, sparking AI‑threat concerns.
What’s your take, is the crypto ecosystem ready for the next wave of AI attacks?
#security #Hack #AI
Red Zone 07:
Follow me 🙏
1
1
289

Understanding the Recent Binance Security Incident: What You Need to KnowOn October 29, 2026, the cryptocurrency industry witnessed one of its most significant security challenges to date. Binance experienced a major security breach involving unauthorized withdrawals from its hot wallet infrastructure, with total affected assets estimated at approximately $6.34 billion.
If you are an investor or user on the platform, here is a clear breakdown of how the incident unfolded, the immediate actions taken, and what it means for your funds.
How the Breach Occurred
Following an initial investigation, Binance disclosed that the breach was a sophisticated, multistage campaign. The attackers utilized social engineering tactics—including a fake job interview—targeting a DevOps engineer. By compromising the engineer's device and exploiting an internal AI tool, the malicious actors were able to access a service container and authorize unauthorized withdrawal transactions across multiple blockchain networks.
Importantly, Binance confirmed that there is no evidence of any wallet private keys being leaked. Blockchain intelligence firms, including TRM Labs and the FBI, have attributed the attack with high confidence to the North Korea-linked hacking group known as TraderTraitor.
Binance’s Immediate Response and Fund Security
The most critical takeaway for retail and institutional users is that user funds are safe. Binance has committed to covering all financial losses entirely through its Secure Asset Fund for Users (SAFU) and corporate treasury reserves.
To contain the fallout, Binance immediately:
Temporarily suspended withdrawals to conduct comprehensive security checks.
Partnered with blockchain intelligence firms and law enforcement to track and freeze stolen funds, successfully freezing roughly $3 billion on-chain so far.
Rebuilt affected systems, replaced compromised devices, and revoked the relevant credentials and tokens.
What Happens Next?
Binance is currently restoring withdrawal services in phased rollouts for various assets. The exchange has also pledged to publish a highly detailed technical post-mortem and an updated Proof of Reserves once the remediation process and independent cybersecurity reviews are complete. Moving forward, the company plans to heavily increase its investments in AI-enabled security infrastructure and industry-wide research initiatives to prevent future exploits.
While an incident of this scale is a stark reminder of the sophisticated cyber threats facing the digital asset space, Binance’s rapid containment, transparency, and full financial backing demonstrate the resilience required to protect user trust.
Stay tuned to official Binance announcements for the most accurate and up-to-date information regarding your specific assets.
$BNB
{future}(BNBUSDT)
#binanceincidentreport #Binance #Hack
Understanding the Recent Binance Security Incident: What You Need to Know
On October 29, 2026, the cryptocurrency industry witnessed one of its most significant security challenges to date. Binance experienced a major security breach involving unauthorized withdrawals from its hot wallet infrastructure, with total affected assets estimated at approximately $6.34 billion.
If you are an investor or user on the platform, here is a clear breakdown of how the incident unfolded, the immediate actions taken, and what it means for your funds.
How the Breach Occurred
Following an initial investigation, Binance disclosed that the breach was a sophisticated, multistage campaign. The attackers utilized social engineering tactics—including a fake job interview—targeting a DevOps engineer. By compromising the engineer's device and exploiting an internal AI tool, the malicious actors were able to access a service container and authorize unauthorized withdrawal transactions across multiple blockchain networks.
Importantly, Binance confirmed that there is no evidence of any wallet private keys being leaked. Blockchain intelligence firms, including TRM Labs and the FBI, have attributed the attack with high confidence to the North Korea-linked hacking group known as TraderTraitor.
Binance’s Immediate Response and Fund Security
The most critical takeaway for retail and institutional users is that user funds are safe. Binance has committed to covering all financial losses entirely through its Secure Asset Fund for Users (SAFU) and corporate treasury reserves.
To contain the fallout, Binance immediately:
Temporarily suspended withdrawals to conduct comprehensive security checks.
Partnered with blockchain intelligence firms and law enforcement to track and freeze stolen funds, successfully freezing roughly $3 billion on-chain so far.
Rebuilt affected systems, replaced compromised devices, and revoked the relevant credentials and tokens.
What Happens Next?
Binance is currently restoring withdrawal services in phased rollouts for various assets. The exchange has also pledged to publish a highly detailed technical post-mortem and an updated Proof of Reserves once the remediation process and independent cybersecurity reviews are complete. Moving forward, the company plans to heavily increase its investments in AI-enabled security infrastructure and industry-wide research initiatives to prevent future exploits.
While an incident of this scale is a stark reminder of the sophisticated cyber threats facing the digital asset space, Binance’s rapid containment, transparency, and full financial backing demonstrate the resilience required to protect user trust.
Stay tuned to official Binance announcements for the most accurate and up-to-date information regarding your specific assets.
$BNB
#binanceincidentreport #Binance #Hack
If you are an investor or user on the platform, here is a clear breakdown of how the incident unfolded, the immediate actions taken, and what it means for your funds.
How the Breach Occurred
Following an initial investigation, Binance disclosed that the breach was a sophisticated, multistage campaign. The attackers utilized social engineering tactics—including a fake job interview—targeting a DevOps engineer. By compromising the engineer's device and exploiting an internal AI tool, the malicious actors were able to access a service container and authorize unauthorized withdrawal transactions across multiple blockchain networks.
Importantly, Binance confirmed that there is no evidence of any wallet private keys being leaked. Blockchain intelligence firms, including TRM Labs and the FBI, have attributed the attack with high confidence to the North Korea-linked hacking group known as TraderTraitor.
Binance’s Immediate Response and Fund Security
The most critical takeaway for retail and institutional users is that user funds are safe. Binance has committed to covering all financial losses entirely through its Secure Asset Fund for Users (SAFU) and corporate treasury reserves.
To contain the fallout, Binance immediately:
Temporarily suspended withdrawals to conduct comprehensive security checks.
Partnered with blockchain intelligence firms and law enforcement to track and freeze stolen funds, successfully freezing roughly $3 billion on-chain so far.
Rebuilt affected systems, replaced compromised devices, and revoked the relevant credentials and tokens.
What Happens Next?
Binance is currently restoring withdrawal services in phased rollouts for various assets. The exchange has also pledged to publish a highly detailed technical post-mortem and an updated Proof of Reserves once the remediation process and independent cybersecurity reviews are complete. Moving forward, the company plans to heavily increase its investments in AI-enabled security infrastructure and industry-wide research initiatives to prevent future exploits.
While an incident of this scale is a stark reminder of the sophisticated cyber threats facing the digital asset space, Binance’s rapid containment, transparency, and full financial backing demonstrate the resilience required to protect user trust.
Stay tuned to official Binance announcements for the most accurate and up-to-date information regarding your specific assets.
$BNB
#binanceincidentreport #Binance #Hack
WonderBTC:
Tudo começa com engenharia social, do mesmo modo como agiram no hack do Banco de Bangladesh e na Bybit.
2
1
1.6k
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BitcoinRebounds$75KAsChipsLead
10,665 views
152 Discussing
2
#JobsReportRaisesHikeOdds
139,431 views
1,225 Discussing
3
#US Data Center Rules May Constrain AI Expansion
20,961 views
116 Discussing
4
#AnthropicStillPlansPreThanksgivingIPO
4,677 views
102 Discussing
5
#FinCENAndFedWithdraw$250CryptoTransferProposal
624 views
7 Discussing
6
#$2TWipedOutHedgeFundsFaceLiquidation
22,221 views
105 Discussing
7
#WillAnthropicListOnTime
29,736 views
414 Discussing
8
#USNovemberMichiganExpectationsIndexPrelimAt50.9
32,058 views
506 Discussing
9
#OilPlungesBelow$100
29,897 views
46 Discussing
10
#TradFiForBeginners
20,786 views
344 Discussing