

#revolutconfirmsfakegovemaildatabreach
revolutconfirmsfakegovemaildatabreach
168,802 views
1,615 Discussing
Hot
Latest

If you're still clicking links in official-looking verification emails without verifying sender signatures, stop now.
Phishing attacks have evolved far beyond poorly written spam, and having your identity credentials compromised can quietly expose your entire portfolio before you even spot unauthorized activity.
The latest incident involving spoofed government emails hitting Revolut is a stark reminder that centralized operational infrastructure remains the most vulnerable target in digital finance. We saw this exact playbook unfold during the Ledger customer data breach and past Mailchimp compromises, where attackers bypassed cryptographic security entirely to exploit human error and off-ramp communication channels.
When attackers get their hands on verified account records, simply parking your $USDT in cold storage only solves part of the equation. If social engineers can spoof compliance notices, even moving liquidity across $OP or decentralizing backups on $FIL won't shield you from targeted SIM-swaps and credential resets. At the end of the day, your operational security is only as tough as the easiest communication channel to spoof.
Do you think centralized fintech off-ramps will ever completely solve social engineering risks, or is full decentralized self-custody the only real long-term shield?
#RevolutConfirmsFakeGovEmailDataBreach #CryptoLiquidations
354

·
--
Most crypto breaches don't happen because someone cracked an on-chain smart contract, but because a spoofed email tricked an internal operator into handing over credentials.
Waking up to compromised accounts because a fintech bridge got breached is every trader's worst nightmare. You can park your dry powder safely in $USDT or deploy capital across $OP, but the moment off-ramp touchpoints slip up, personal records and linked wallet profiles land directly in the hands of malicious actors.
The recent confirmation regarding the Revolut data breach via fake government email domains shows how sophisticated targeted social engineering has become. Attackers did not brute force cryptographic infrastructure. Instead, they weaponized convincing regulatory correspondence to bypass operational defenses and extract sensitive user telemetry.
When attackers obtain internal verification files, secondary phishing escalates dramatically across the ecosystem. Anyone using integrated banking rails should expect hyper-personalized attack vectors, often disguised as mandatory compliance checks to siphon holdings like $DOGE or trigger rogue approvals.
How often do you audit your connected web3 authorizations and separate your off-ramp emails from your primary trading accounts?
#RevolutConfirmsFakeGovEmailDataBreach #CryptoLiquidations
Most crypto breaches don't happen because someone cracked an on-chain smart contract, but because a spoofed email tricked an internal operator into handing over credentials.
Waking up to compromised accounts because a fintech bridge got breached is every trader's worst nightmare. You can park your dry powder safely in $USDT or deploy capital across $OP , but the moment off-ramp touchpoints slip up, personal records and linked wallet profiles land directly in the hands of malicious actors.
The recent confirmation regarding the Revolut data breach via fake government email domains shows how sophisticated targeted social engineering has become. Attackers did not brute force cryptographic infrastructure. Instead, they weaponized convincing regulatory correspondence to bypass operational defenses and extract sensitive user telemetry.
When attackers obtain internal verification files, secondary phishing escalates dramatically across the ecosystem. Anyone using integrated banking rails should expect hyper-personalized attack vectors, often disguised as mandatory compliance checks to siphon holdings like $DOGE or trigger rogue approvals.
How often do you audit your connected web3 authorizations and separate your off-ramp emails from your primary trading accounts?
#RevolutConfirmsFakeGovEmailDataBreach #CryptoLiquidations
192

🚨 SECURITY SHOULD NEVER BE AN AFTERTHOUGHT
Revolut has confirmed a data breach linked to fraudulent government-style email requests.
For crypto users, this is another reminder:
Your biggest risk isn't always the blockchain.
Sometimes it's the person trying to trick you into giving access.
Never share your seed phrase.
Never approve a transaction you don't understand.
Always verify the sender and the official website.
📌 In crypto, security is part of trading.
One careless click can cost more than a bad trade.
$XLM $USDC $USDT
#RevolutConfirmsFakeGovEmailDataBreach
153
#revolutconfirmsfakegovemaildatabreach
🚨 THIS IS A SERIOUS WEB3 LESSON
Revolut confirmed that sensitive customer data was exposed after the company was deceived by fraudulent requests that appeared to come from a legitimate government email domain.
The scary part?
The attack didn't necessarily require breaking sophisticated blockchain technology.
It exploited TRUST.
This is a reminder for everyone in crypto and fintech:
Never assume an email is genuine just because it looks official.
Verify.
Double-check.
Use independent communication channels.
Security isn't just about wallets.
It's about people too.
$XLM $USDC $USDT
2
1
343
·
--
Bearish
#RevolutConfirmsFakeGovEmailDataBreach
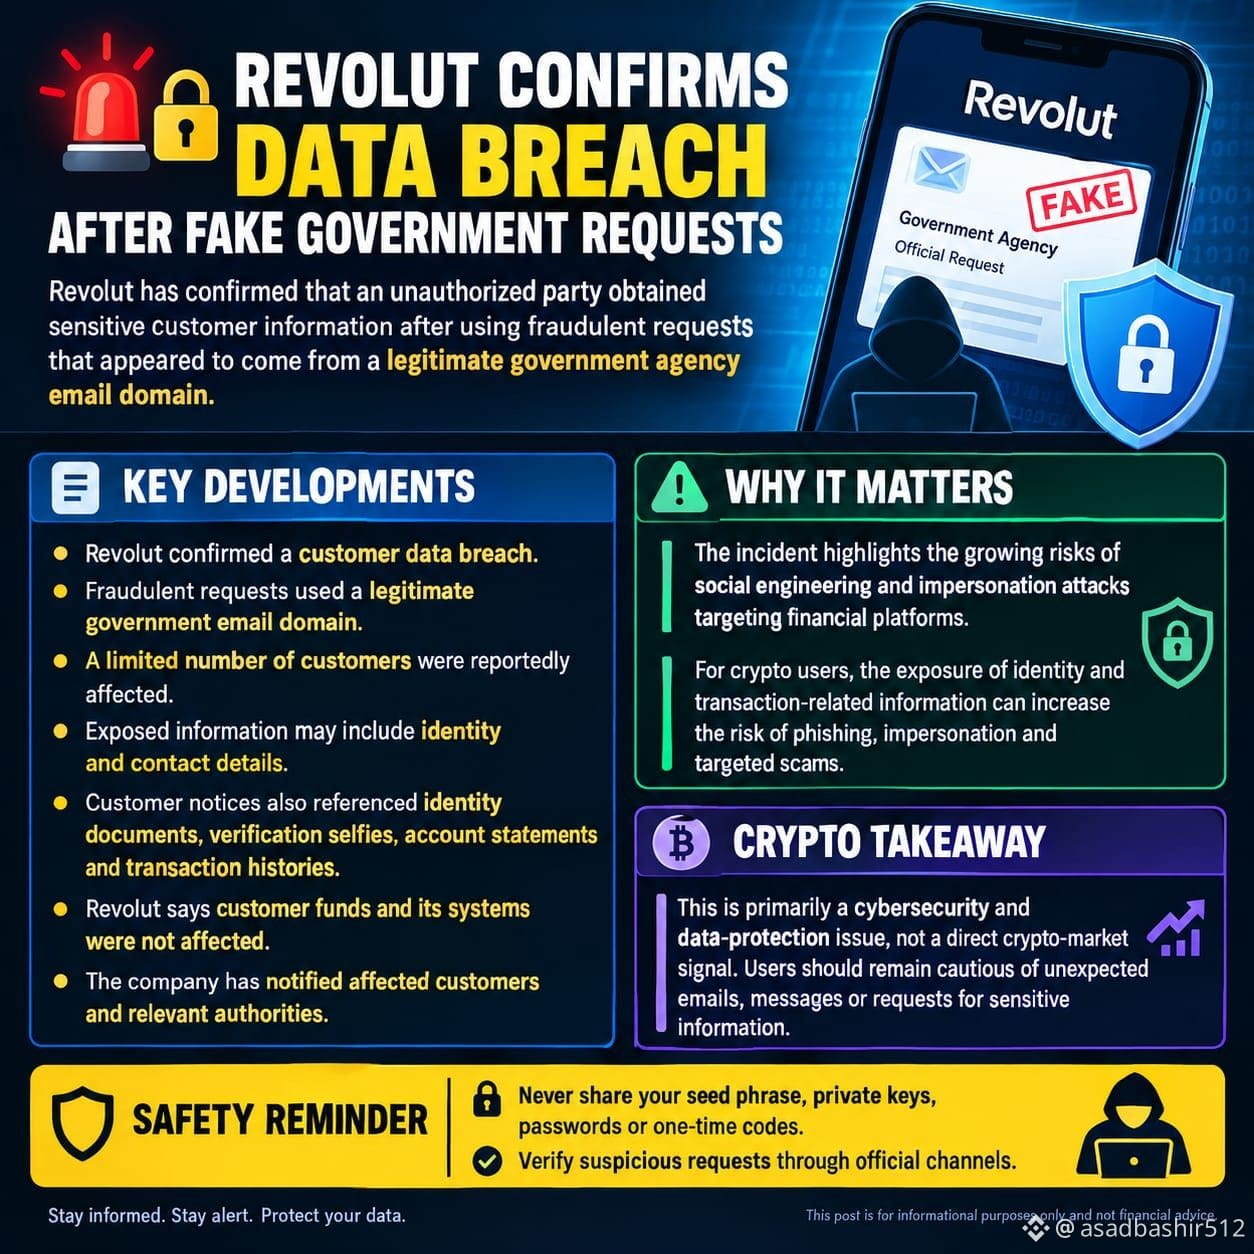
🚨🔐 REVOLUT CONFIRMS DATA BREACH AFTER FAKE GOVERNMENT REQUESTS
Revolut has confirmed that an unauthorized party obtained sensitive customer information after using fraudulent requests that appeared to come from a legitimate government agency email domain.
📊 KEY DEVELOPMENTS:
• Revolut confirmed a customer data breach
• Fraudulent requests used a legitimate government email domain
• A limited number of customers were reportedly affected
• Exposed information may include identity and contact details
• Customer notices also referenced identity documents, verification selfies, account statements and transaction histories
• Revolut says customer funds and its systems were not affected
• The company has notified affected customers and relevant authorities
⚠️ WHY IT MATTERS:
The incident highlights the growing risks of social engineering and impersonation attacks targeting financial platforms.
For crypto users, the exposure of identity and transaction-related information can increase the risk of phishing, impersonation and targeted scams.
📌 CRYPTO TAKEAWAY:
This is primarily a cybersecurity and data-protection issue, not a direct crypto-market signal. Users should remain cautious of unexpected emails, messages or requests for sensitive information.
🔒 SAFETY REMINDER:
Never share your seed phrase, private keys, passwords or one-time codes. Verify suspicious requests through official channels.
$ETHFI
{future}(ETHFIUSDT)
$MARSCOIN
{future}(MARSCOINUSDT)
$KAVA
{future}(KAVAUSDT)
#RevolutConfirmsFakeGovEmailDataBreach
🚨🔐 REVOLUT CONFIRMS DATA BREACH AFTER FAKE GOVERNMENT REQUESTS
Revolut has confirmed that an unauthorized party obtained sensitive customer information after using fraudulent requests that appeared to come from a legitimate government agency email domain.
📊 KEY DEVELOPMENTS:
• Revolut confirmed a customer data breach
• Fraudulent requests used a legitimate government email domain
• A limited number of customers were reportedly affected
• Exposed information may include identity and contact details
• Customer notices also referenced identity documents, verification selfies, account statements and transaction histories
• Revolut says customer funds and its systems were not affected
• The company has notified affected customers and relevant authorities
⚠️ WHY IT MATTERS:
The incident highlights the growing risks of social engineering and impersonation attacks targeting financial platforms.
For crypto users, the exposure of identity and transaction-related information can increase the risk of phishing, impersonation and targeted scams.
📌 CRYPTO TAKEAWAY:
This is primarily a cybersecurity and data-protection issue, not a direct crypto-market signal. Users should remain cautious of unexpected emails, messages or requests for sensitive information.
🔒 SAFETY REMINDER:
Never share your seed phrase, private keys, passwords or one-time codes. Verify suspicious requests through official channels.
$ETHFI
$MARSCOIN
$KAVA
82
·
--
#revolutconfirmsfakegovemaildatabreach Revolut disclosed a data breach where a fraudster used a spoofed government‑agency email to obtain customers’ personal and ID documents, affecting a limited but unspecified number of users.
Revolut identified a sophisticated external impersonation scam in which an unauthorized third party sent fraudulent information‑request emails from a legitimate government domain. The breach exposed identity data (birth date, addresses, phone numbers), copies of passports and driver’s licences, and potentially verification selfies, account statements, and transaction histories. Revolut blocked the offending address, notified affected customers, and alerted the implicated government agency, law enforcement, and regulators. The firm emphasized that its core systems and customer funds remain unaffected. With over 80 million global users and recent regulatory milestones—including a conditional U.S. bank licence—this incident raises concerns about data‑security practices as Revolut expands into new markets.$REZ $XRP $SUI
Revolut identified a sophisticated external impersonation scam in which an unauthorized third party sent fraudulent information‑request emails from a legitimate government domain. The breach exposed identity data (birth date, addresses, phone numbers), copies of passports and driver’s licences, and potentially verification selfies, account statements, and transaction histories. Revolut blocked the offending address, notified affected customers, and alerted the implicated government agency, law enforcement, and regulators. The firm emphasized that its core systems and customer funds remain unaffected. With over 80 million global users and recent regulatory milestones—including a conditional U.S. bank licence—this incident raises concerns about data‑security practices as Revolut expands into new markets.$REZ $XRP $SUI
1
2.7k
·
--
#revolutconfirmsfakegovemaildatabreach Revolut confirms it handed customer data to scammers posing as government agency
It’s not just ordinary people who fall for scams – major companies can be fooled, too. British fintech Revolut confirmed it disclosed sensitive customer information after receiving fraudulent data requests from what ppeared to be a legitimate government agency email account.
"Upon detection, we immediately blocked the address and alerted the relevant government agency as well as enforcement agencies, data protection, and financial regulators," a spokesperson told Reuters on Saturday.
The compromised data included customers' birth dates, postal and email addresses, occupation, and phone numbers, as well as copies of their identity documents, including passports and driver’s licenses, according to reports.
$STEEM $ARK $VTHO
1.1k
·
--
#revolutconfirmsfakegovemaildatabreach Revolut confirms sensitive customer data breach after fake government requests Sept 12 (Reuters) - British fintech Revolut confirmed on Saturday that sensitive customer information was disclosed to an unauthorized third party after it received fraudulent requests from a legitimate government agency email domain.
Jumpstart your morning with the latest legal news delivered straight to your inbox from The Daily Docket newsletter.
Revolut said in a statement that the breach affected a "very limited" number of customers, who had been notified by the company. It did not give further details.
"Revolut systems and customer funds are unaffected," a spokesperson for the company said, without disclosing the exact number of individuals affected by the breach.
"Upon detection, we immediately blocked the address and alerted the relevant government agency as well as enforcement agencies, data protection, and financial regulators," the spokesperson said.
The compromised data included customers' birth date, postal and email addresses, and phone numbers, as well as copies of their identity documents including passports and driver’s licenses, according to a TechCrunch report.
Revolut is planning for a potential public LISTING and aiming for a valuation of up to $200 billion.
It is one of the MOST SUCCSSEFUL European fintech companies, with no physical bank branches.$LSK $CVC $BTW
361

·
--
Bearish
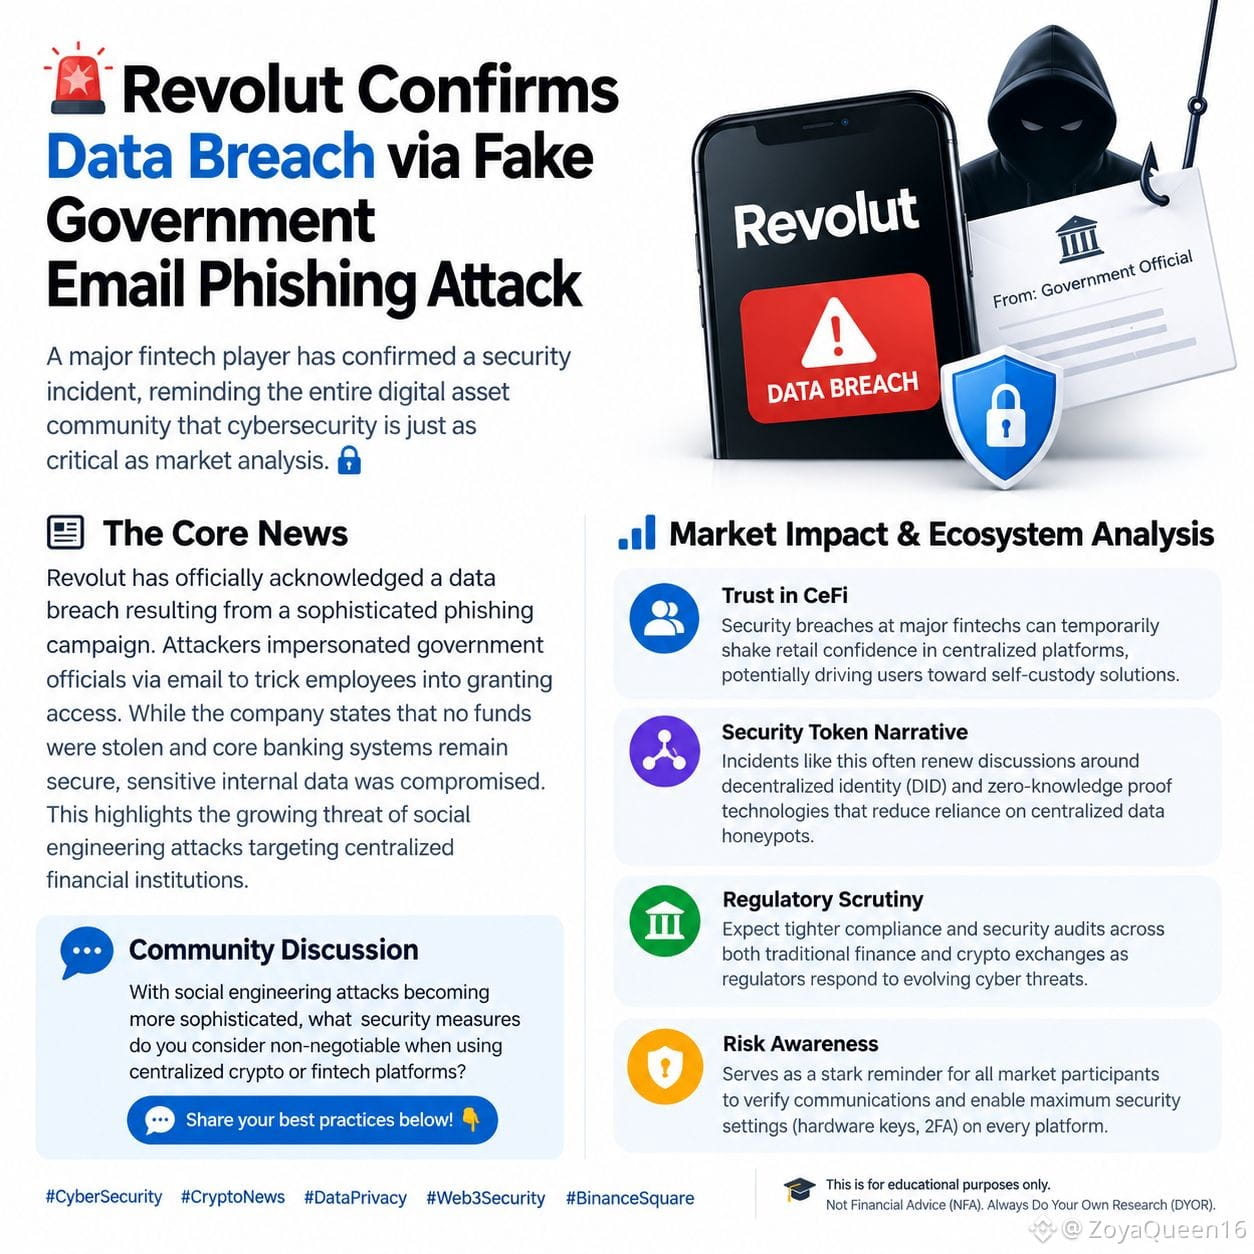
#revolutconfirmsfakegovemaildatabreach 🚨 Revolut Confirms Data Breach via Fake Government Email Phishing Attack
A major fintech player has confirmed a security incident, reminding the entire digital asset community that cybersecurity is just as critical as market analysis. 🔐
📰 The Core News
Revolut has officially acknowledged a data breach resulting from a sophisticated phishing campaign. Attackers impersonated government officials via email to trick employees into granting access. While the company states that no funds were stolen and core banking systems remain secure, sensitive internal data was compromised. This highlights the growing threat of social engineering attacks targeting centralized financial institutions.
📊 Market Impact & Ecosystem Analysis
Trust in CeFi Security breaches at major fintechs can temporarily shake retail confidence in centralized platforms, potentially driving users toward self-custody solutions.
* Security Token Narrative Incidents like this often renew discussions around decentralized identity (DID) and zero-knowledge proof technologies that reduce reliance on centralized data honeypots.
* Regulatory Scrutiny Expect tighter compliance and security audits across both traditional finance and crypto exchanges as regulators respond to evolving cyber threats.
* Risk Awareness Serves as a stark reminder for all market participants to verify communications and enable maximum security settings (hardware keys, 2FA) on every platform.
💬 Community Discussion
With social engineering attacks becoming more sophisticated, what security measures do you consider non-negotiable when using centralized crypto or fintech platforms? Share your best practices below! 👇
#CyberSecurity #CryptoNews #DataPrivacy #Web3Security #BinanceSquare
Disclaimer: This is for educational purposes only. Not Financial Advice (NFA). Always Do Your Own Research (DYOR).
$MUUB $MVLLB $SNXXB
{spot}(SNXXBUSDT)
{spot}(MUUBUSDT)
{spot}(MVLLBUSDT)
#revolutconfirmsfakegovemaildatabreach 🚨 Revolut Confirms Data Breach via Fake Government Email Phishing Attack
A major fintech player has confirmed a security incident, reminding the entire digital asset community that cybersecurity is just as critical as market analysis. 🔐
📰 The Core News
Revolut has officially acknowledged a data breach resulting from a sophisticated phishing campaign. Attackers impersonated government officials via email to trick employees into granting access. While the company states that no funds were stolen and core banking systems remain secure, sensitive internal data was compromised. This highlights the growing threat of social engineering attacks targeting centralized financial institutions.
📊 Market Impact & Ecosystem Analysis
Trust in CeFi Security breaches at major fintechs can temporarily shake retail confidence in centralized platforms, potentially driving users toward self-custody solutions.
* Security Token Narrative Incidents like this often renew discussions around decentralized identity (DID) and zero-knowledge proof technologies that reduce reliance on centralized data honeypots.
* Regulatory Scrutiny Expect tighter compliance and security audits across both traditional finance and crypto exchanges as regulators respond to evolving cyber threats.
* Risk Awareness Serves as a stark reminder for all market participants to verify communications and enable maximum security settings (hardware keys, 2FA) on every platform.
💬 Community Discussion
With social engineering attacks becoming more sophisticated, what security measures do you consider non-negotiable when using centralized crypto or fintech platforms? Share your best practices below! 👇
#CyberSecurity #CryptoNews #DataPrivacy #Web3Security #BinanceSquare
Disclaimer: This is for educational purposes only. Not Financial Advice (NFA). Always Do Your Own Research (DYOR).
$MUUB $MVLLB $SNXXB
33

💥 THE WEAK LINK CAN BE HUMAN TRUST
Revolut's confirmation of the incident puts social engineering back in focus.
Fake authority can make fraudulent emails look legitimate.
Never trust a message simply because it appears official.
🛡️ Crypto traders should verify links and notifications through official apps.
#revolutconfirmsfakegovemaildatabreach
1
39
·
--
#RevolutConfirmsFakeGovEmailDataBreach
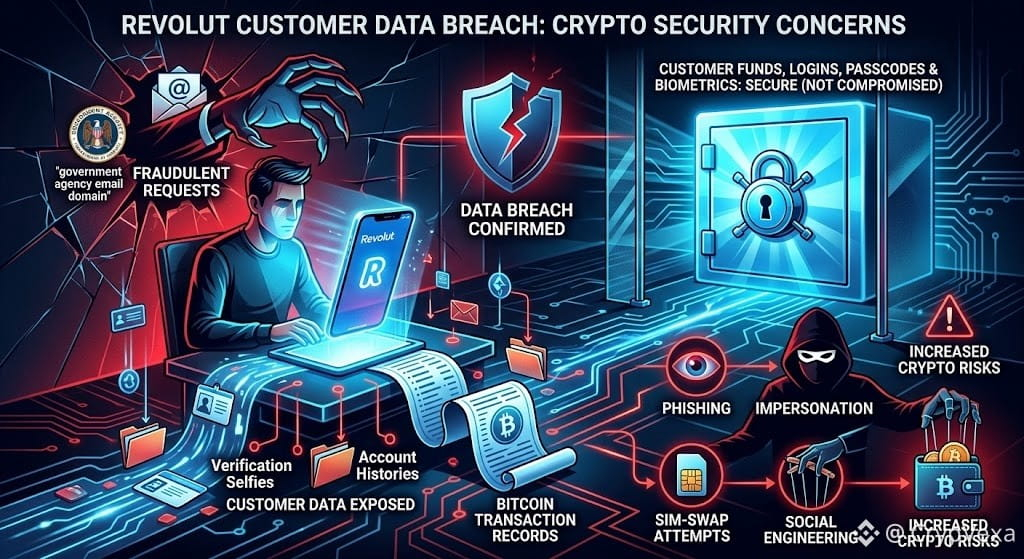
🚨 Revolut Customer Data Breach Raises Crypto Security Concerns
⚠️ Revolut confirmed a customer-data breach caused by fraudulent requests that appeared to come from a legitimate government agency email domain.
📂 Reports indicate limited customer records may have been exposed, including ID documents, verification selfies, and account or transaction histories. For some crypto users, this could include Bitcoin transaction records.
🔐 Revolut says customer funds, login credentials, passcodes, and biometric-login data were not compromised. The incident reportedly involved fake information requests rather than a direct breach of its core systems.
🛡️ For crypto users, exposed identity and transaction data could increase risks of phishing, impersonation, SIM-swap attempts, and social engineering.
👀 If you use Revolut, stay alert for suspicious calls, messages, or verification requests. Never share passcodes, verification codes, seed phrases, or private keys.
#Revolut #CryptoSecurity #DataBreach #Bitcoin
1
17
⚠️ PHISHING IS STILL A HUGE PROBLEM
A fake government-style email reportedly played a role in a Revolut security incident.
Attackers often target people rather than the technology itself.
One careless click can expose sensitive information.
🔒 $BTC and crypto users should apply the same security discipline to every account.
#revolutconfirmsfakegovemaildatabreach
1
182
🚨 A FAKE EMAIL JUST TRIGGERED A REAL SECURITY ISSUE
Revolut confirmed a data breach linked to a fraudulent government-themed email.
The incident highlights how convincing phishing attacks can exploit trust.
Digital finance users need to treat unexpected messages with extreme caution.
🔐 Security awareness matters as crypto adoption keeps growin
#revolutconfirmsfakegovemaildatabreach
13
😳 ONE FAKE EMAIL — SERIOUS CONSEQUENCES
Revolut has confirmed a breach involving a fake government email.
The incident shows that social engineering remains a major threat to financial platforms.
Trust can be exploited even when the technology behind the platform is strong.
👀 Crypto users should stay alert when receiving account-related messages.
#revolutconfirmsfakegovemaildatabreach
35
·
--
Article
Revolut Data Incident Raises New Crypto Security Concerns for Bitcoin and Ethereum Users#revolutconfirmsfakegovemaildatabreach
Revolut's confirmed data incident is putting a fresh spotlight on the importance of personal data security in crypto.
Crypto security is often associated with private keys, seed phrases and wallet protection. But sensitive information such as KYC details and transaction data can also become valuable targets for attackers.
For Bitcoin ($BTC) and Ethereum ($ETH) investors, protecting personal information is an important part of reducing exposure to targeted attacks, phishing attempts and other security risks.
The incident is also a reminder that security doesn't stop after a trade is completed. Keeping account information private, using strong authentication and staying cautious with unexpected messages can all help limit unnecessary exposure.
For traders, the takeaway is simple: focus on the market, but don't overlook the security of the information connected to your accounts.
#Revolut #CryptoSecurity #Bitcoin #Ethereum #CryptoNews
Disclaimer: This article is for educational and informational purposes only and is not financial advice.
Revolut Data Incident Raises New Crypto Security Concerns for Bitcoin and Ethereum Users
#revolutconfirmsfakegovemaildatabreach
Revolut's confirmed data incident is putting a fresh spotlight on the importance of personal data security in crypto.
Crypto security is often associated with private keys, seed phrases and wallet protection. But sensitive information such as KYC details and transaction data can also become valuable targets for attackers.
For Bitcoin ($BTC) and Ethereum ($ETH) investors, protecting personal information is an important part of reducing exposure to targeted attacks, phishing attempts and other security risks.
The incident is also a reminder that security doesn't stop after a trade is completed. Keeping account information private, using strong authentication and staying cautious with unexpected messages can all help limit unnecessary exposure.
For traders, the takeaway is simple: focus on the market, but don't overlook the security of the information connected to your accounts.
#Revolut #CryptoSecurity #Bitcoin #Ethereum #CryptoNews
Disclaimer: This article is for educational and informational purposes only and is not financial advice.
23
#RevolutConfirmsFakeGovEmailDataBreach
🚨 REVOLUT DATA BREACH: A SERIOUS WARNING
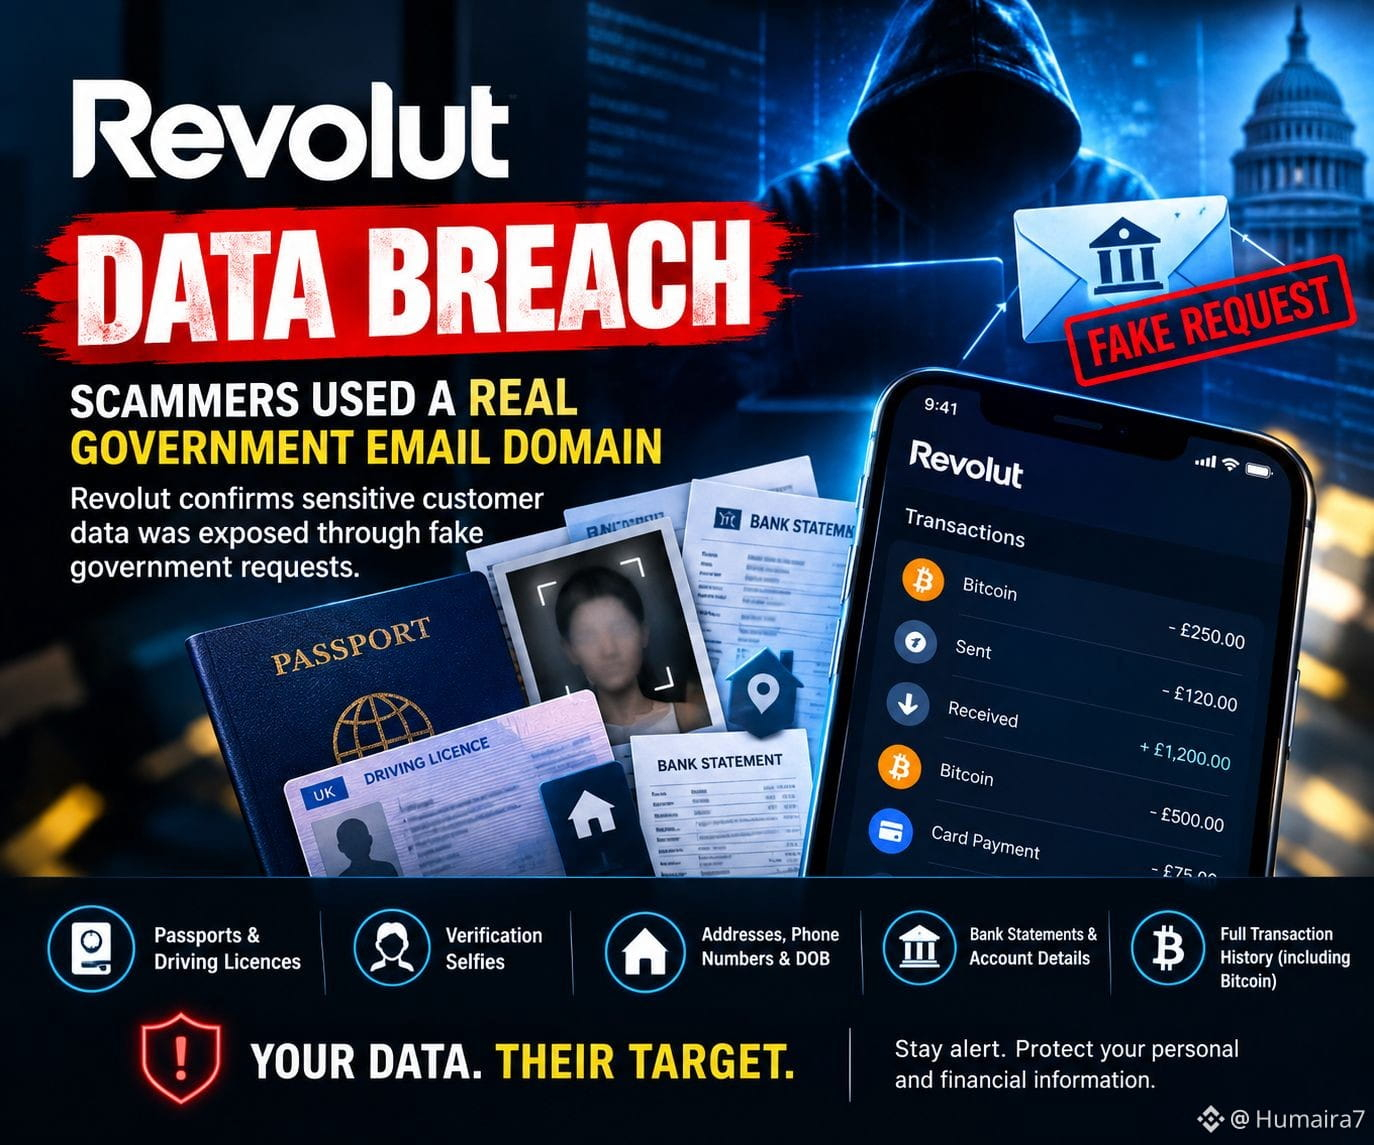
Revolut has confirmed that scammers used a legitimate government agency email domain to send fraudulent customer-data requests — and the company treated them as genuine.
Potentially exposed data included: • Passports & driving licences
• Verification selfies
• Addresses & phone numbers
• Bank statements & account details
• Full transaction history, including Bitcoin activity
Revolut says customer funds and its systems were not compromised, and only a limited number of customers were affected. The exact number and government agency have not been disclosed.
The biggest lesson? 🔐
Even when your own account is secure, your personal and financial data can still become a target through sophisticated social engineering.
For crypto users, leaked transaction history can make future phishing and scam attempts far more convincing.
Protect your data. Protect your crypto. Stay alert.
#Revolut #DataBreach #CyberSecurity #CryptoSecurity #Bitcoin #BTC #KYC #Privacy #CryptoNews
52
·
--
I NEED YOU TO ACTUALLY READ THIS ONE, NOT JUST SCROLL PAST IT.
Revolut, a fintech with over 80 million users, just admitted their own team got fooled into handing over customer data to attackers pretending to be a government agency.
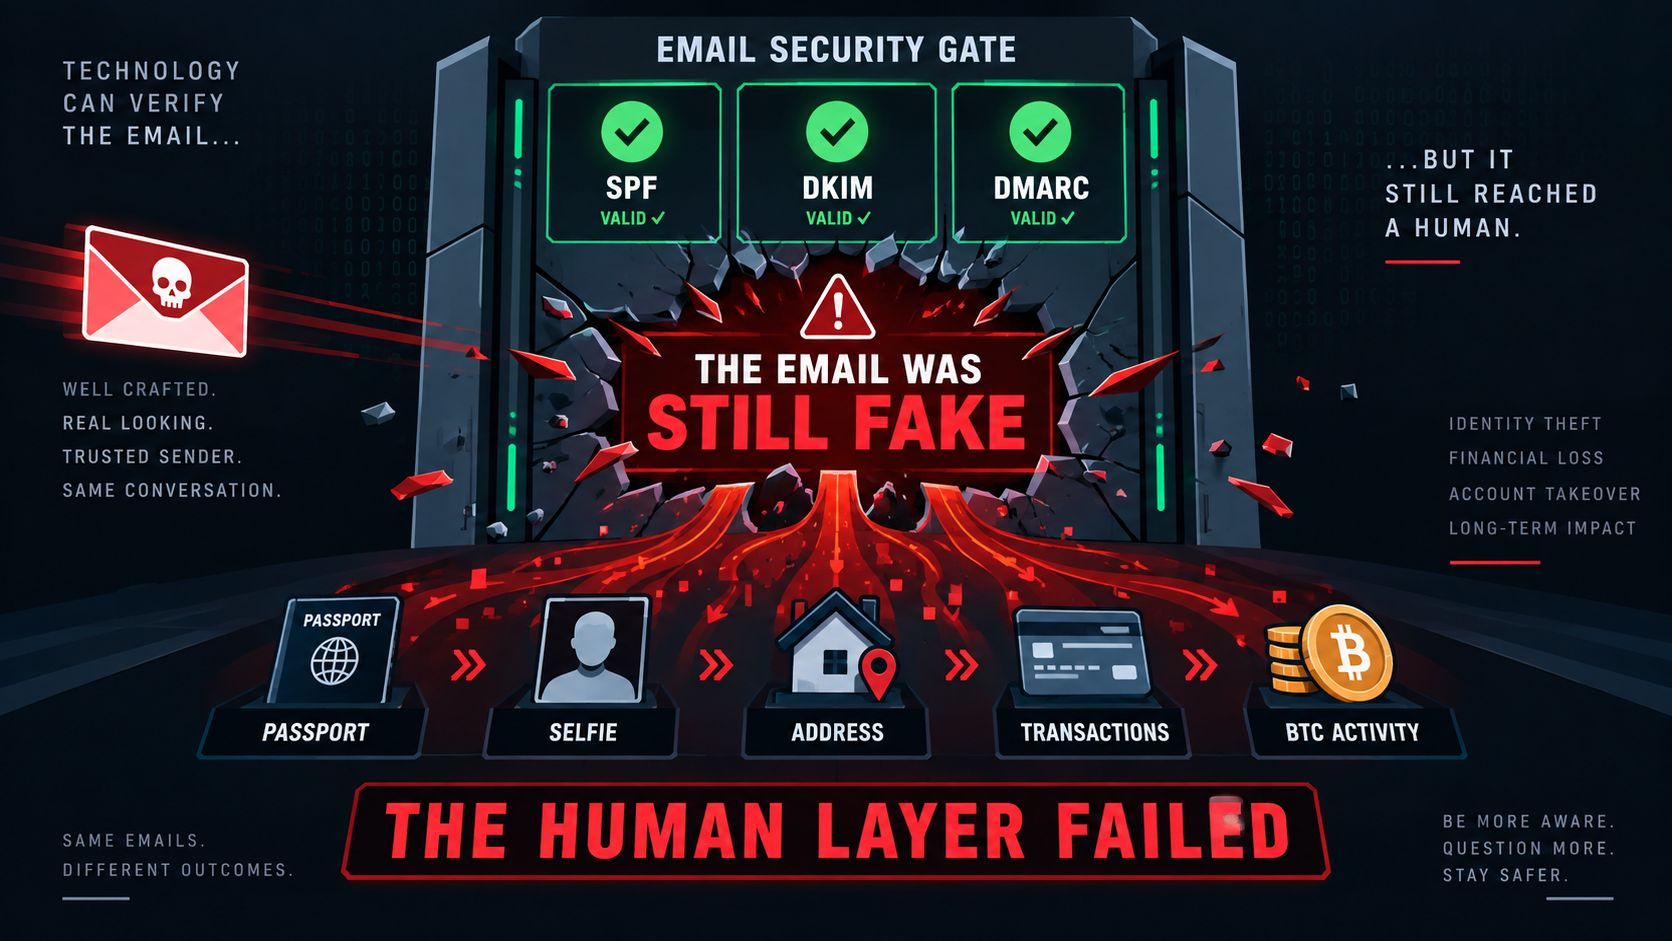
The email was so convincing it passed every authentication check email security is built on. Revolut's compliance staff processed the request like it was completely legitimate.
What actually left the building: passports, driver's licenses, verification selfies, home addresses, phone numbers, full account statements, and transaction history, Bitcoin included if you'd ever moved crypto through your account.
The part that actually scares me: a well-known crypto investigator says this looks like it specifically targeted wealthy accounts. Not a random scrape. A targeted operation.
Revolut's message is “Your money is safe,” and technically that's true. No passwords or card numbers were taken. But honestly, in 2026, your identity documents and financial history in the wrong hands can do just as much damage as a stolen card number, sometimes more.
If you use Revolut, especially if you've ever held crypto there, be extremely suspicious of any email about this breach right now. A second wave of phishing using this exact stolen data has already started.
#RevolutConfirmsFakeGovEmailDataBreach
2
132

·
--
#revolutconfirmsfakegovemaildatabreach
🛑 SECURITY WARNING: Revolut Data Breach Exposes User Emails—Protect Your Crypto!
📊 Security Alert & Breach Context
The Incident Details: Fintech and banking app Revolut confirmed a targeted data breach after compliance teams responded to a fraudulent record request sent from an email address using a legitimate government agency domain.
Exposed Customer Files: On-chain investigator ZachXBT revealed that the leak impacted high-net-worth users. Compromised files include full names, home addresses, phone numbers, passport/ID copies, verification selfies, account statements, and full transaction histories—including linked Bitcoin ($BTC) transfers.
System & Funds Status: Revolut confirmed that its core banking infrastructure, app passwords, card PINs, and private keys were not compromised, and user funds remain fully secure. However, exposed KYC data creates severe off-chain risks.
💡 How to Protect Yourself from Phishing Traps
Beware of Hyper-Targeted Phishing: Attackers with access to transaction records and home addresses can generate sophisticated phishing emails or SMS messages impersonating Revolut or crypto exchanges.
Never Share OTPs or Passwords: Revolut or exchange support agents will never ask for your 2FA codes, login credentials, or recovery phrases over the phone or via email.
Move Long-Term Holdings Off-App: Store high-value crypto assets in self-custody hardware wallets rather than centralized fintech platforms to minimize exposure to third-party data leaks.
💬 Community Poll: Does the exposure of KYC data by centralized platforms make you reconsider keeping crypto on fintech apps? Share your security tips below! 👇
#ClarityActFacesProceduralVoteSept15 #PhishingAlert #CYBER
1
174
·
--
Bearish
#revolutconfirmsfakegovemaildatabreach
🚨 Revolut Data Breach Exposes Customer Information
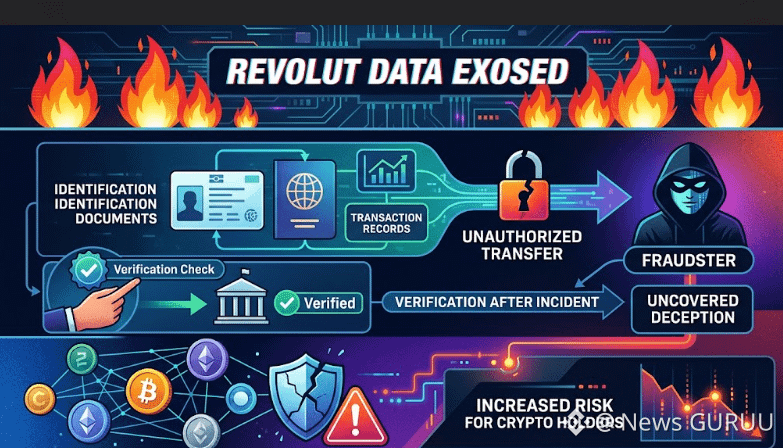
Revolut confirmed that fraudsters used a legitimate government-domain email to submit fake data requests, potentially exposing passports, addresses and Bitcoin transaction histories of a limited number of customers.
⚠️ Revolut says customer funds and systems were not affected, but the incident highlights serious privacy and security risks for crypto users.
Trading View: SELL 🔴
Question: Could this breach increase security concerns across crypto? "CLICK ON THE BELOW YELLOW COIN TAG TO GO TO DESIRED TRADING PAGE TO GET BENEFIT TRADE"$BNB $BTC
{spot}(BTCUSDT)
{spot}(BNBUSDT)
#revolut #CryptoSecurity
#revolutconfirmsfakegovemaildatabreach
🚨 Revolut Data Breach Exposes Customer Information
Revolut confirmed that fraudsters used a legitimate government-domain email to submit fake data requests, potentially exposing passports, addresses and Bitcoin transaction histories of a limited number of customers.
⚠️ Revolut says customer funds and systems were not affected, but the incident highlights serious privacy and security risks for crypto users.
Trading View: SELL 🔴
Question: Could this breach increase security concerns across crypto? "CLICK ON THE BELOW YELLOW COIN TAG TO GO TO DESIRED TRADING PAGE TO GET BENEFIT TRADE"$BNB $BTC
#revolut #CryptoSecurity
2
9
#revolutconfirmsfakegovemaildatabreach
The Revolut data breach is another reminder that crypto and fintech security cannot be ignored.
The incident reportedly involved fraudulent requests that appeared to come from a legitimate government email domain.
This shows how convincing social-engineering attacks can become.
For crypto users, never trust an email just because it looks official. Always verify the sender, links and requests for sensitive information.
$XMR $ZEC $DASH
2
1
1.1k
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BitcoinClears$85200
640 views
70 Discussing
2
#AltcoinSeasonIndexHoldsAbove60For5Days
7,016 views
445 Discussing
3
#USADPAdds90000JobsInSeptember
1,705 views
200 Discussing
4
#USCorePCEEasesTo3%InAugust
1,695 views
176 Discussing
5
#KospiPostsWorstQuarterSince2020
2,460 views
229 Discussing
6
#SECToClarifyOnChainFundraisingRules
8,439 views
394 Discussing
7
#UKFCAOpensCryptoFirmAuthorization
11,973 views
367 Discussing
8
#JapanMOFStudyGroupOnTokenizedGovtBonds
10,380 views
308 Discussing
9
#QNTRises287%
52,166 views
704 Discussing
10
#TrumpRejectsAIRulesForVoluntaryAudits
34,174 views
625 Discussing