
#cryptosecurity
cryptosecurity
9.3M views
15,086 Discussing
Hot
Latest
Article
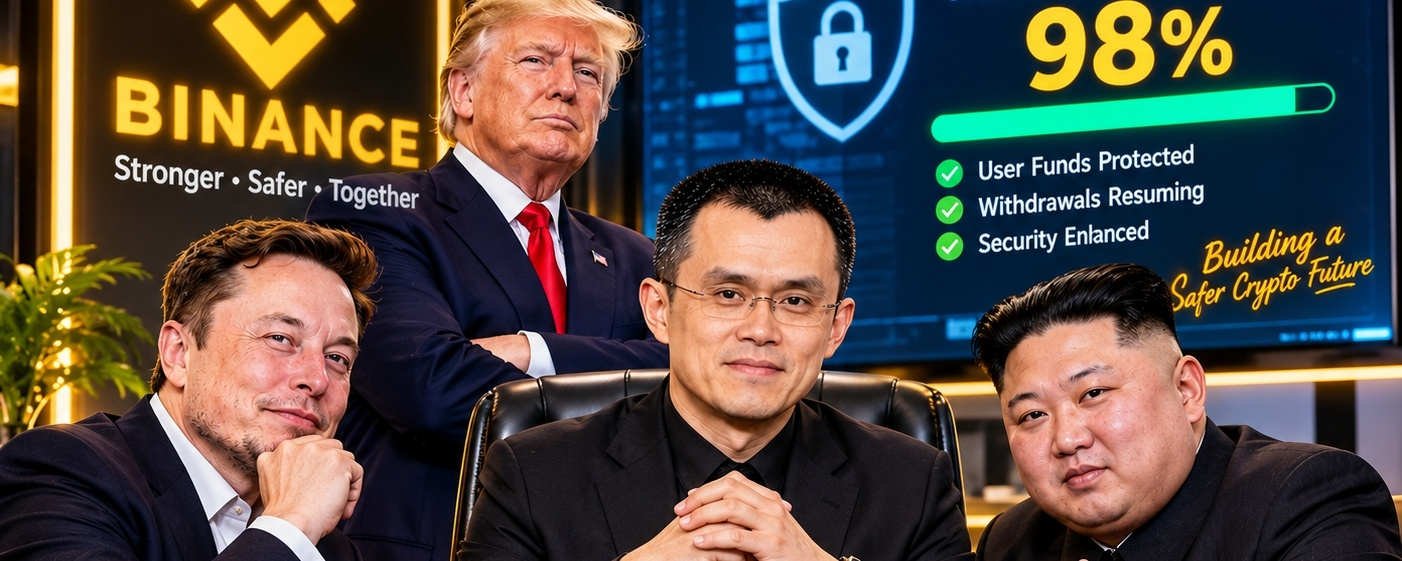
🚨 BINANCE SECURITY RECOVERY: CZ & THE CRYPTO WORLD UNITED FOR A SAFER FUTURE! 🔐🔥🚨 BINANCE HACK UPDATE: RECOVERY IS MOVING FORWARD! 🔐
The Binance security incident has become one of the biggest talking points in the crypto community.
On October 29, 2026, Binance experienced a serious security incident involving unauthorized transfers from its hot wallets, affecting approximately $6.34 billion in digital assets.
But what happened next is important!
🛡️ 1. Protecting User Funds
Binance says it will cover the financial impact of the stolen assets, not its users.
💰 2. 98% Recovery Progress
According to Binance's November 3 update, approximately 98% of the affected assets had been replenished.
🔓 3. Withdrawals Returning
Binance has been reopening withdrawals for additional assets in phases, including its November 6 Recovery Update #9.
🔐 4. Stronger Security
Affected systems have been rebuilt, access controls strengthened, and AI-based threat detection improved.
THE BIG QUESTION!
Can Binance fully restore user confidence after this major security incident?
Security, transparency, and trust are essential for the future of crypto.
👇 What do you think? Has Binance handled this crisis well?
#Binance #CryptoSecurity #BinanceUpdates
🚨 BINANCE SECURITY RECOVERY: CZ & THE CRYPTO WORLD UNITED FOR A SAFER FUTURE! 🔐🔥
🚨 BINANCE HACK UPDATE: RECOVERY IS MOVING FORWARD! 🔐
The Binance security incident has become one of the biggest talking points in the crypto community.
On October 29, 2026, Binance experienced a serious security incident involving unauthorized transfers from its hot wallets, affecting approximately $6.34 billion in digital assets.
But what happened next is important!
🛡️ 1. Protecting User Funds
Binance says it will cover the financial impact of the stolen assets, not its users.
💰 2. 98% Recovery Progress
According to Binance's November 3 update, approximately 98% of the affected assets had been replenished.
🔓 3. Withdrawals Returning
Binance has been reopening withdrawals for additional assets in phases, including its November 6 Recovery Update #9.
🔐 4. Stronger Security
Affected systems have been rebuilt, access controls strengthened, and AI-based threat detection improved.
THE BIG QUESTION!
Can Binance fully restore user confidence after this major security incident?
Security, transparency, and trust are essential for the future of crypto.
👇 What do you think? Has Binance handled this crisis well?
#Binance #CryptoSecurity #BinanceUpdates
The Binance security incident has become one of the biggest talking points in the crypto community.
On October 29, 2026, Binance experienced a serious security incident involving unauthorized transfers from its hot wallets, affecting approximately $6.34 billion in digital assets.
But what happened next is important!
🛡️ 1. Protecting User Funds
Binance says it will cover the financial impact of the stolen assets, not its users.
💰 2. 98% Recovery Progress
According to Binance's November 3 update, approximately 98% of the affected assets had been replenished.
🔓 3. Withdrawals Returning
Binance has been reopening withdrawals for additional assets in phases, including its November 6 Recovery Update #9.
🔐 4. Stronger Security
Affected systems have been rebuilt, access controls strengthened, and AI-based threat detection improved.
THE BIG QUESTION!
Can Binance fully restore user confidence after this major security incident?
Security, transparency, and trust are essential for the future of crypto.
👇 What do you think? Has Binance handled this crisis well?
#Binance #CryptoSecurity #BinanceUpdates
4
941
·
--
Bullish
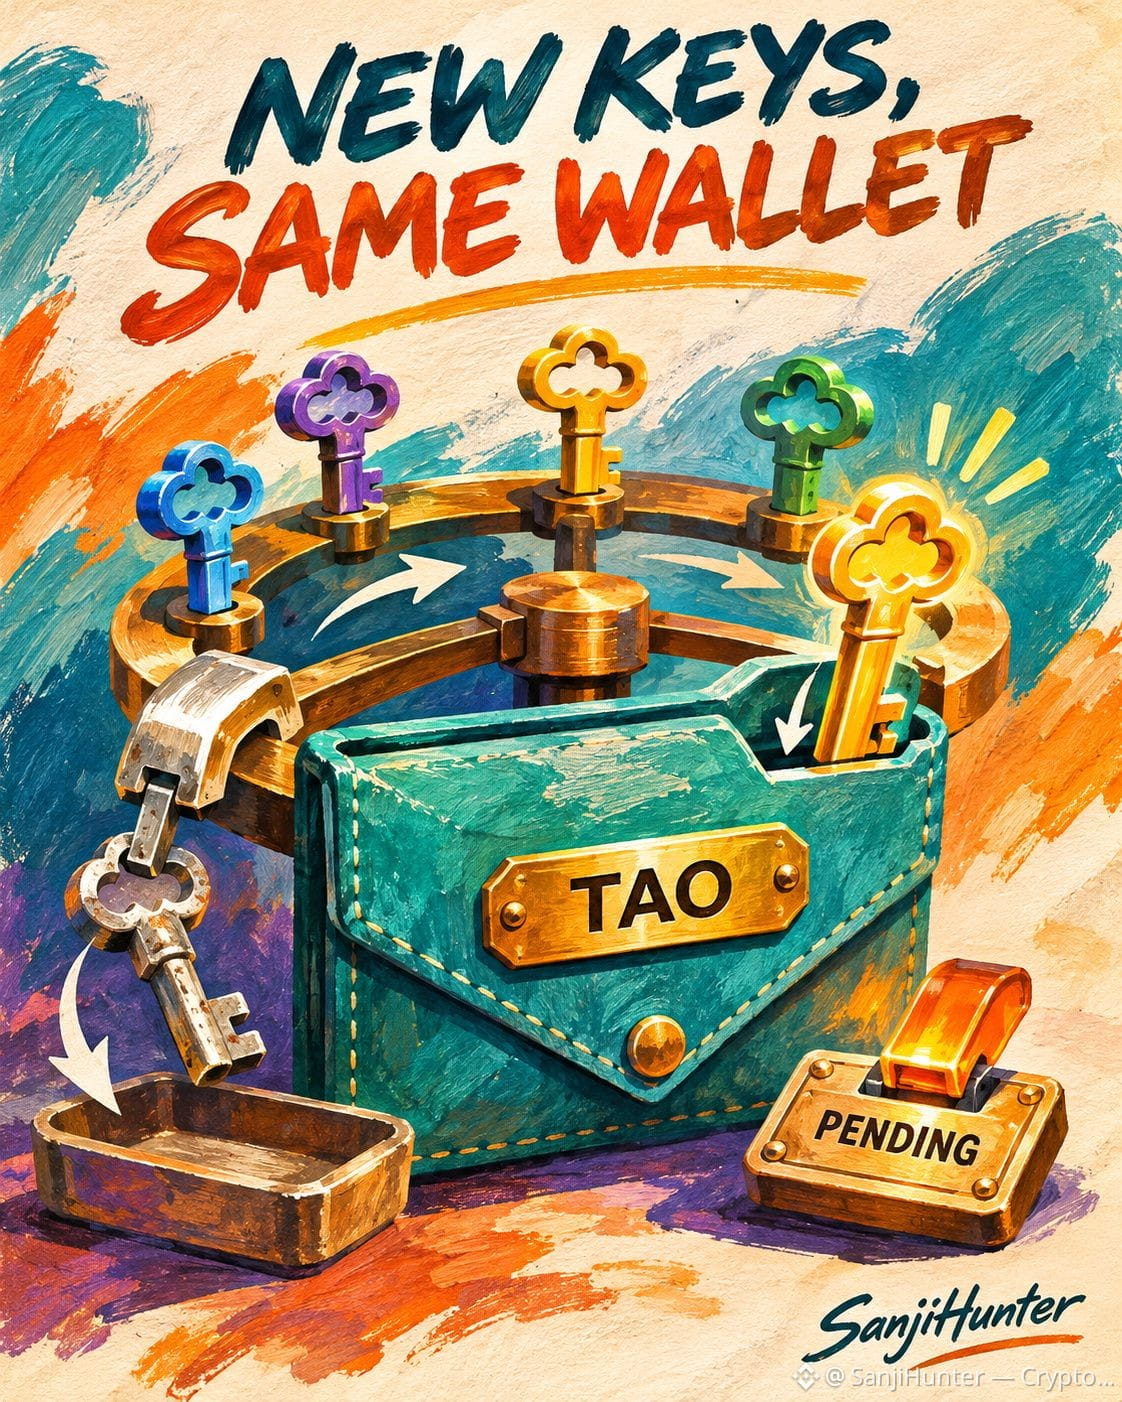
🔐 What if your crypto wallet could replace its signing key after every transaction — without changing its address?
Bittensor just unveiled quantum-resistant wallet technology for $TAO
Its new runtime supports ML-DSA-65 and Falcon signatures, with optional automatic key rotation
{future}(TAOUSDT)
Here's why that matters 👇
Your wallet address identifies your account
Your signing key proves you can authorize transactions
With key rotation, the address, balance and stake remain unchanged while the signing key is replaced after an onchain transaction
But there's an important distinction ⚠️
The technology has entered Bittensor's $TAO runtime, yet post-quantum authorization is disabled by default and requires activation
Wallet providers also need compatible software
Existing TAO wallets remain valid, with no forced migration
{spot}(TAOUSDT)
📌 The next milestone isn't another announcement
It's verified activation, compatible wallets and successful real transactions
Quantum security isn't just about stronger signatures
It's about making the entire wallet system ready to use
#TAO #bittensor #CryptoSecurity
🔐 What if your crypto wallet could replace its signing key after every transaction — without changing its address?
Bittensor just unveiled quantum-resistant wallet technology for $TAO
Its new runtime supports ML-DSA-65 and Falcon signatures, with optional automatic key rotation
Here's why that matters 👇
Your wallet address identifies your account
Your signing key proves you can authorize transactions
With key rotation, the address, balance and stake remain unchanged while the signing key is replaced after an onchain transaction
But there's an important distinction ⚠️
The technology has entered Bittensor's $TAO runtime, yet post-quantum authorization is disabled by default and requires activation
Wallet providers also need compatible software
Existing TAO wallets remain valid, with no forced migration
📌 The next milestone isn't another announcement
It's verified activation, compatible wallets and successful real transactions
Quantum security isn't just about stronger signatures
It's about making the entire wallet system ready to use
#TAO #bittensor #CryptoSecurity
Bittensor just unveiled quantum-resistant wallet technology for $TAO
Its new runtime supports ML-DSA-65 and Falcon signatures, with optional automatic key rotation
Here's why that matters 👇
Your wallet address identifies your account
Your signing key proves you can authorize transactions
With key rotation, the address, balance and stake remain unchanged while the signing key is replaced after an onchain transaction
But there's an important distinction ⚠️
The technology has entered Bittensor's $TAO runtime, yet post-quantum authorization is disabled by default and requires activation
Wallet providers also need compatible software
Existing TAO wallets remain valid, with no forced migration
📌 The next milestone isn't another announcement
It's verified activation, compatible wallets and successful real transactions
Quantum security isn't just about stronger signatures
It's about making the entire wallet system ready to use
#TAO #bittensor #CryptoSecurity
1
218
🚨 OPTIONS SECURITY | SIGNALPLUS: THE HIDDEN DANGER OF TRADING API KEYS
A third-party security incident has raised an important question for crypto derivatives traders:
Can your funds be at risk even when API withdrawals are disabled?
The answer is yes.
On November 5, Binance and Deribit revoked API keys associated with SignalPlus following a reported security incident involving the external trading platform.
Both exchanges stated that their own systems were not compromised.
🔍 WHY THIS MATTERS
Trading API permissions can allow third-party platforms to:
• Place and cancel orders
• Open or close leveraged positions
• Modify trading exposure
• Interact with derivatives markets
Even without withdrawal access, compromised trading permissions can potentially cause substantial losses through unauthorized transactions.
⚠️ FOUR ESSENTIAL SAFEGUARDS
Revoke unused or potentially exposed API keys.
Enable IP whitelisting wherever supported.
Apply minimum necessary permissions.
Review open orders, positions and trading history directly on the exchange.
For options traders, this is especially important. Complex positions can carry nonlinear risks, and unauthorized transactions may fundamentally change portfolio exposure.
🎯 OUR TAKE
Security is part of trading strategy, not a separate technical concern.
A sophisticated options model is worthless if external access controls fail.
The real question is not only whether an API can withdraw funds, but what damage it can cause through trading permissions alone.
BitChoice | Satya — Options Security
#CryptoSecurity #SignalPlus #CryptoOptions #APISecurity #RiskManagement $BTC
$ETH
{spot}(ETHUSDT)
🚨 OPTIONS SECURITY | SIGNALPLUS: THE HIDDEN DANGER OF TRADING API KEYS
A third-party security incident has raised an important question for crypto derivatives traders:
Can your funds be at risk even when API withdrawals are disabled?
The answer is yes.
On November 5, Binance and Deribit revoked API keys associated with SignalPlus following a reported security incident involving the external trading platform.
Both exchanges stated that their own systems were not compromised.
🔍 WHY THIS MATTERS
Trading API permissions can allow third-party platforms to:
• Place and cancel orders
• Open or close leveraged positions
• Modify trading exposure
• Interact with derivatives markets
Even without withdrawal access, compromised trading permissions can potentially cause substantial losses through unauthorized transactions.
⚠️ FOUR ESSENTIAL SAFEGUARDS
Revoke unused or potentially exposed API keys.
Enable IP whitelisting wherever supported.
Apply minimum necessary permissions.
Review open orders, positions and trading history directly on the exchange.
For options traders, this is especially important. Complex positions can carry nonlinear risks, and unauthorized transactions may fundamentally change portfolio exposure.
🎯 OUR TAKE
Security is part of trading strategy, not a separate technical concern.
A sophisticated options model is worthless if external access controls fail.
The real question is not only whether an API can withdraw funds, but what damage it can cause through trading permissions alone.
BitChoice | Satya — Options Security
#CryptoSecurity #SignalPlus #CryptoOptions #APISecurity #RiskManagement $BTC
$ETH
A third-party security incident has raised an important question for crypto derivatives traders:
Can your funds be at risk even when API withdrawals are disabled?
The answer is yes.
On November 5, Binance and Deribit revoked API keys associated with SignalPlus following a reported security incident involving the external trading platform.
Both exchanges stated that their own systems were not compromised.
🔍 WHY THIS MATTERS
Trading API permissions can allow third-party platforms to:
• Place and cancel orders
• Open or close leveraged positions
• Modify trading exposure
• Interact with derivatives markets
Even without withdrawal access, compromised trading permissions can potentially cause substantial losses through unauthorized transactions.
⚠️ FOUR ESSENTIAL SAFEGUARDS
Revoke unused or potentially exposed API keys.
Enable IP whitelisting wherever supported.
Apply minimum necessary permissions.
Review open orders, positions and trading history directly on the exchange.
For options traders, this is especially important. Complex positions can carry nonlinear risks, and unauthorized transactions may fundamentally change portfolio exposure.
🎯 OUR TAKE
Security is part of trading strategy, not a separate technical concern.
A sophisticated options model is worthless if external access controls fail.
The real question is not only whether an API can withdraw funds, but what damage it can cause through trading permissions alone.
BitChoice | Satya — Options Security
#CryptoSecurity #SignalPlus #CryptoOptions #APISecurity #RiskManagement $BTC
$ETH
126
·
--
🔐 Crypto Is Not Just About Profit — It's About Security!
The recent developments in the crypto industry remind us of one important lesson:
Your digital assets deserve protection, transparency, and security.
Before focusing on market gains, every crypto user should understand:
🔹 Security matters. 🔹 Transparency builds trust. 🔹 Knowledge is more valuable than hype. 🔹 Never ignore risk management.
💬 What matters most to you in a crypto exchange: Security, Transparency, or Trading Features?#Bitcoin #Binance #CryptoSecurity #Blockchain #CryptoEducation💡🚀
🔐 Crypto Is Not Just About Profit — It's About Security!
The recent developments in the crypto industry remind us of one important lesson:
Your digital assets deserve protection, transparency, and security.
Before focusing on market gains, every crypto user should understand:
🔹 Security matters. 🔹 Transparency builds trust. 🔹 Knowledge is more valuable than hype. 🔹 Never ignore risk management.
💬 What matters most to you in a crypto exchange: Security, Transparency, or Trading Features?#Bitcoin #Binance #CryptoSecurity #Blockchain #CryptoEducation💡🚀
The recent developments in the crypto industry remind us of one important lesson:
Your digital assets deserve protection, transparency, and security.
Before focusing on market gains, every crypto user should understand:
🔹 Security matters. 🔹 Transparency builds trust. 🔹 Knowledge is more valuable than hype. 🔹 Never ignore risk management.
💬 What matters most to you in a crypto exchange: Security, Transparency, or Trading Features?#Bitcoin #Binance #CryptoSecurity #Blockchain #CryptoEducation💡🚀
77
·
--
Bullish
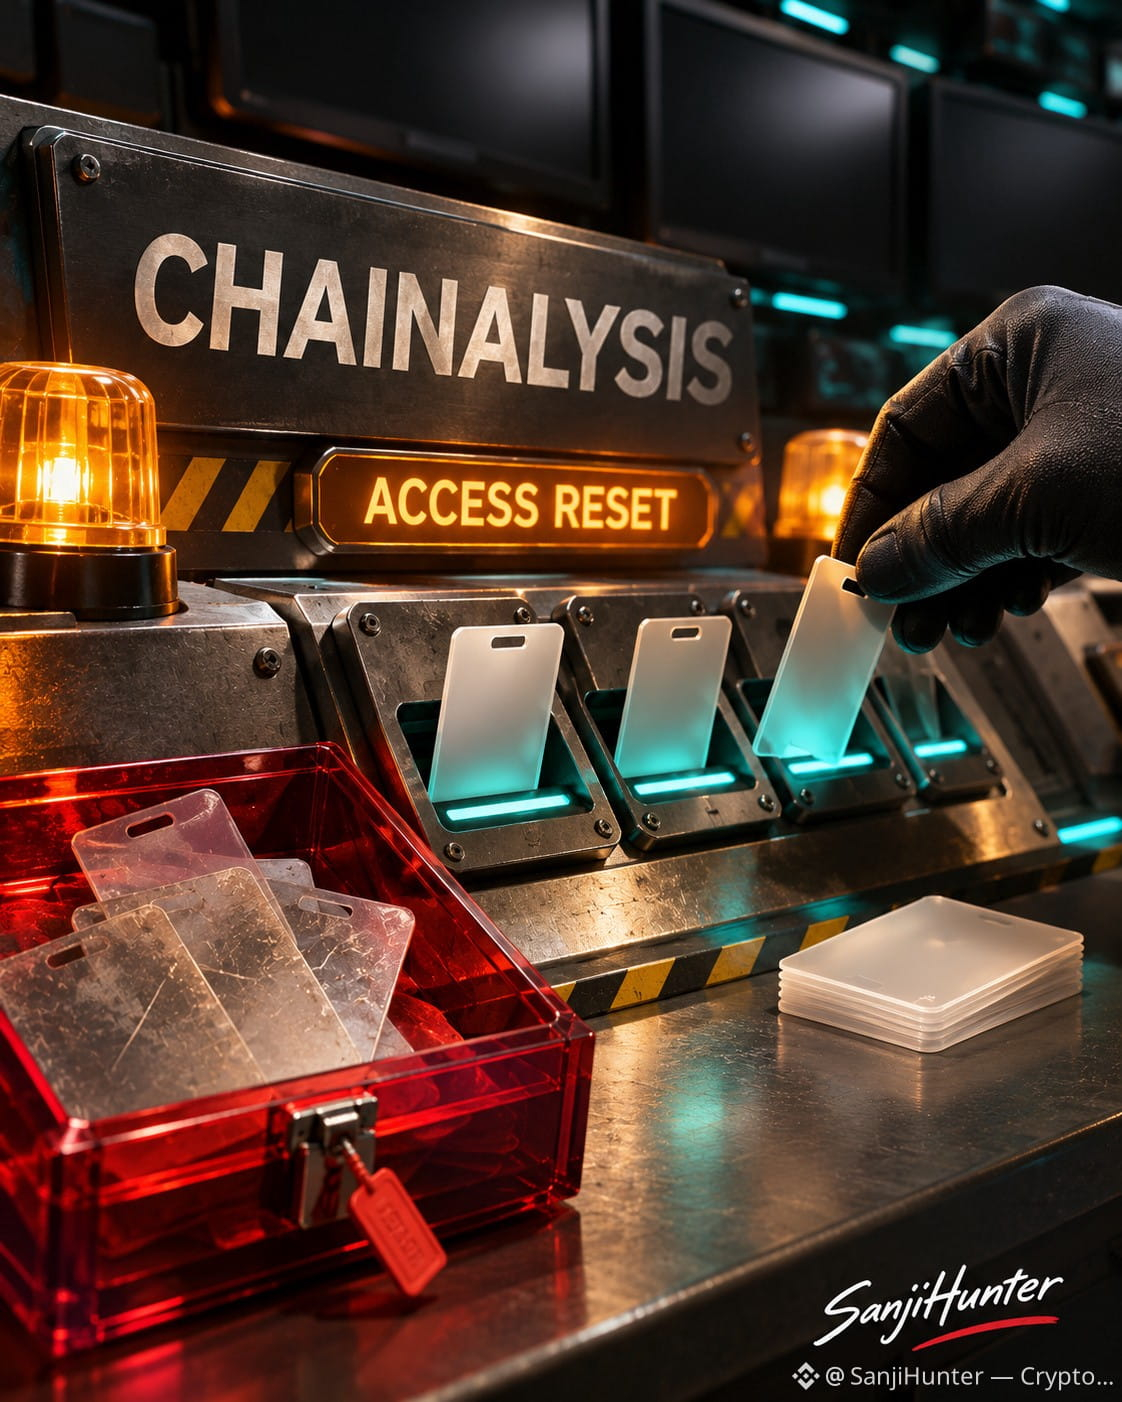
🚨 The company that helps investigate crypto crime just had to lock down its own security systems
Chainalysis initially reported no evidence that authentication credentials were accessed during its cyberattack
Then the findings changed
$LINK
{future}(LINKUSDT)
On November 4, the firm disclosed that customer information including password hashes and live tokens associated with all users had been exposed
It also took its KYT transaction-monitoring and address-screening services offline after detecting abnormal activity
By November 6, services were gradually coming back — but access came with new conditions 👇
$ZEC
{future}(ZECUSDT)
🔐 Trusted IP allowlisting
🔑 Mandatory password resets and API key rotation where applicable
Chainalysis says it still has no evidence that investigation data was accessed or blockchain attribution data manipulated
This incident is separate from the Binance theft
For compliance teams, the deeper risk isn't just stolen credentials
It's losing access to critical monitoring infrastructure during a security incident
📌 Watch service restoration, confirmed account misuse and backup screening procedures
Even the tools designed to detect threats need a fallback plan
$BNB
{future}(BNBUSDT)
#Chainalysis #CryptoSecurity
🚨 The company that helps investigate crypto crime just had to lock down its own security systems
Chainalysis initially reported no evidence that authentication credentials were accessed during its cyberattack
Then the findings changed
$LINK
On November 4, the firm disclosed that customer information including password hashes and live tokens associated with all users had been exposed
It also took its KYT transaction-monitoring and address-screening services offline after detecting abnormal activity
By November 6, services were gradually coming back — but access came with new conditions 👇
$ZEC
🔐 Trusted IP allowlisting
🔑 Mandatory password resets and API key rotation where applicable
Chainalysis says it still has no evidence that investigation data was accessed or blockchain attribution data manipulated
This incident is separate from the Binance theft
For compliance teams, the deeper risk isn't just stolen credentials
It's losing access to critical monitoring infrastructure during a security incident
📌 Watch service restoration, confirmed account misuse and backup screening procedures
Even the tools designed to detect threats need a fallback plan
$BNB
#Chainalysis #CryptoSecurity
Chainalysis initially reported no evidence that authentication credentials were accessed during its cyberattack
Then the findings changed
$LINK
On November 4, the firm disclosed that customer information including password hashes and live tokens associated with all users had been exposed
It also took its KYT transaction-monitoring and address-screening services offline after detecting abnormal activity
By November 6, services were gradually coming back — but access came with new conditions 👇
$ZEC
🔐 Trusted IP allowlisting
🔑 Mandatory password resets and API key rotation where applicable
Chainalysis says it still has no evidence that investigation data was accessed or blockchain attribution data manipulated
This incident is separate from the Binance theft
For compliance teams, the deeper risk isn't just stolen credentials
It's losing access to critical monitoring infrastructure during a security incident
📌 Watch service restoration, confirmed account misuse and backup screening procedures
Even the tools designed to detect threats need a fallback plan
$BNB
#Chainalysis #CryptoSecurity
312
·
--
Article
Title: The $6.3B Binance Hack Is Crypto’s Biggest Ever. So Why Did the Market Barely Flinch?The largest crypto hack in history just happened, and Bitcoin still climbed back above $80K within days. Here is what happened and what it means for you.
What happened
The FBI linked the theft of a record $6.3B from Binance to North Korea, and Binance said it replaced 90% of the stolen amount with company funds. Users are not absorbing the loss.
Binance said the attack began with a fake job interview and was a campaign built over many months, ending with an exploit of its hot-wallet signing infrastructure through Ethereum’s EIP-7702 mechanism. It also said it blocked 57 suspected North Korea-linked attempts this year and will bring in independent experts to review the incident.
Why the market stayed calm
Bitwise CIO Matt Hougan argued that the muted reaction to the hack reflects the industry’s growing maturity and improved security infrastructure.But it is not all smooth. BTC slipped under $75K after US jobs data beat forecasts and raised bets on a December interest-rate hike. US spot Bitcoin and Ether ETFs also shed a combined $530M in outflows on Thursday.
5 lessons for every user
Never run files or “test tasks” from recruiters or strangers. This whole attack started with a fake interview.Keep long-term holdings in a hardware wallet. Use exchanges for trading.Turn on passkeys or an authenticator app, the anti-phishing code, and withdrawal address whitelisting.Revoke old API keys and token approvals you no longer use.Don’t panic-sell on headlines. Check the facts first.
What to watch next
The Fed and December rate expectationsThe CLARITY Act, which faces a new test now that Democrats control Congress CointelegraphETF inflows and outflowsThe results of Binance’s independent security review
Your turn: Do you keep most of your crypto on an exchange or in self-custody? Tell me in the comments.
Not financial advice. Always DYOR.
$BTC $BNB $ETH #Binance #Bitcoin #CryptoSecurity #BinanceSquare #CryptoNews
Title: The $6.3B Binance Hack Is Crypto’s Biggest Ever. So Why Did the Market Barely Flinch?
The largest crypto hack in history just happened, and Bitcoin still climbed back above $80K within days. Here is what happened and what it means for you.
What happened
The FBI linked the theft of a record $6.3B from Binance to North Korea, and Binance said it replaced 90% of the stolen amount with company funds. Users are not absorbing the loss.
Binance said the attack began with a fake job interview and was a campaign built over many months, ending with an exploit of its hot-wallet signing infrastructure through Ethereum’s EIP-7702 mechanism. It also said it blocked 57 suspected North Korea-linked attempts this year and will bring in independent experts to review the incident.
Why the market stayed calm
Bitwise CIO Matt Hougan argued that the muted reaction to the hack reflects the industry’s growing maturity and improved security infrastructure.But it is not all smooth. BTC slipped under $75K after US jobs data beat forecasts and raised bets on a December interest-rate hike. US spot Bitcoin and Ether ETFs also shed a combined $530M in outflows on Thursday.
5 lessons for every user
Never run files or “test tasks” from recruiters or strangers. This whole attack started with a fake interview.Keep long-term holdings in a hardware wallet. Use exchanges for trading.Turn on passkeys or an authenticator app, the anti-phishing code, and withdrawal address whitelisting.Revoke old API keys and token approvals you no longer use.Don’t panic-sell on headlines. Check the facts first.
What to watch next
The Fed and December rate expectationsThe CLARITY Act, which faces a new test now that Democrats control Congress CointelegraphETF inflows and outflowsThe results of Binance’s independent security review
Your turn: Do you keep most of your crypto on an exchange or in self-custody? Tell me in the comments.
Not financial advice. Always DYOR.
$BTC $BNB $ETH #Binance #Bitcoin #CryptoSecurity #BinanceSquare #CryptoNews
What happened
The FBI linked the theft of a record $6.3B from Binance to North Korea, and Binance said it replaced 90% of the stolen amount with company funds. Users are not absorbing the loss.
Binance said the attack began with a fake job interview and was a campaign built over many months, ending with an exploit of its hot-wallet signing infrastructure through Ethereum’s EIP-7702 mechanism. It also said it blocked 57 suspected North Korea-linked attempts this year and will bring in independent experts to review the incident.
Why the market stayed calm
Bitwise CIO Matt Hougan argued that the muted reaction to the hack reflects the industry’s growing maturity and improved security infrastructure.But it is not all smooth. BTC slipped under $75K after US jobs data beat forecasts and raised bets on a December interest-rate hike. US spot Bitcoin and Ether ETFs also shed a combined $530M in outflows on Thursday.
5 lessons for every user
Never run files or “test tasks” from recruiters or strangers. This whole attack started with a fake interview.Keep long-term holdings in a hardware wallet. Use exchanges for trading.Turn on passkeys or an authenticator app, the anti-phishing code, and withdrawal address whitelisting.Revoke old API keys and token approvals you no longer use.Don’t panic-sell on headlines. Check the facts first.
What to watch next
The Fed and December rate expectationsThe CLARITY Act, which faces a new test now that Democrats control Congress CointelegraphETF inflows and outflowsThe results of Binance’s independent security review
Your turn: Do you keep most of your crypto on an exchange or in self-custody? Tell me in the comments.
Not financial advice. Always DYOR.
$BTC $BNB $ETH #Binance #Bitcoin #CryptoSecurity #BinanceSquare #CryptoNews
80
·
--
🟢 Bullish
🚨 Google Enters Crypto Custody Amid Binance Hack Aftermath!
Crypto exchange Binance has resumed withdrawals after a reported $6 billion hack. In related news, Google is expanding its crypto services with a new custody solution for institutions, designed to enhance security for digital assets.
📊 Market Impact: While the hack is a reminder of security risks, Google's move could bring more institutional confidence and adoption, potentially buffering future market shocks with more robust infrastructure.
#CryptoSecurity #Google
🟢 Bullish
🚨 Google Enters Crypto Custody Amid Binance Hack Aftermath!
Crypto exchange Binance has resumed withdrawals after a reported $6 billion hack. In related news, Google is expanding its crypto services with a new custody solution for institutions, designed to enhance security for digital assets.
📊 Market Impact: While the hack is a reminder of security risks, Google's move could bring more institutional confidence and adoption, potentially buffering future market shocks with more robust infrastructure.
#CryptoSecurity #Google
🚨 Google Enters Crypto Custody Amid Binance Hack Aftermath!
Crypto exchange Binance has resumed withdrawals after a reported $6 billion hack. In related news, Google is expanding its crypto services with a new custody solution for institutions, designed to enhance security for digital assets.
📊 Market Impact: While the hack is a reminder of security risks, Google's move could bring more institutional confidence and adoption, potentially buffering future market shocks with more robust infrastructure.
#CryptoSecurity #Google
16
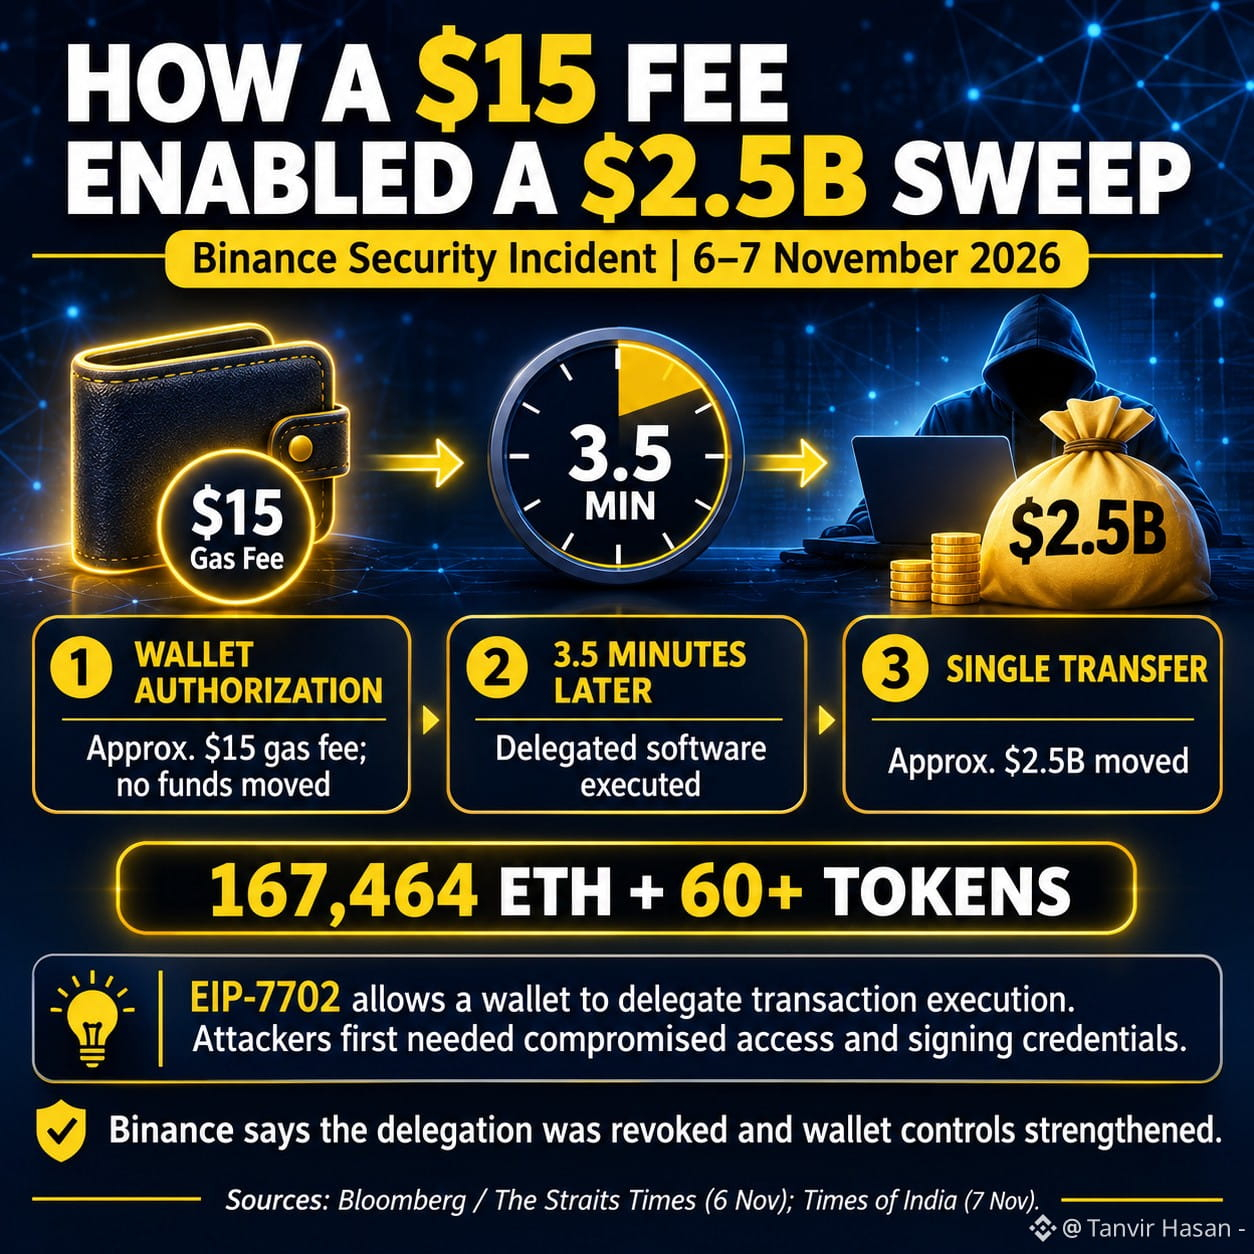
🚨 $15 Fee Behind Binance's $2.5B Crypto Heist!
A sophisticated EIP-7702 exploit enabled hackers to move approximately $2.5B in a single transaction.
A major lesson for crypto security: wallet permissions matter. 🔐
#Binance #Ethereum #CryptoSecurity #EIP7702 #Blockchain
🚨 $15 Fee Behind Binance's $2.5B Crypto Heist!
A sophisticated EIP-7702 exploit enabled hackers to move approximately $2.5B in a single transaction.
A major lesson for crypto security: wallet permissions matter. 🔐
#Binance #Ethereum #CryptoSecurity #EIP7702 #Blockchain
A sophisticated EIP-7702 exploit enabled hackers to move approximately $2.5B in a single transaction.
A major lesson for crypto security: wallet permissions matter. 🔐
#Binance #Ethereum #CryptoSecurity #EIP7702 #Blockchain
User-b50dad82:
পপিট কত
2
3
825


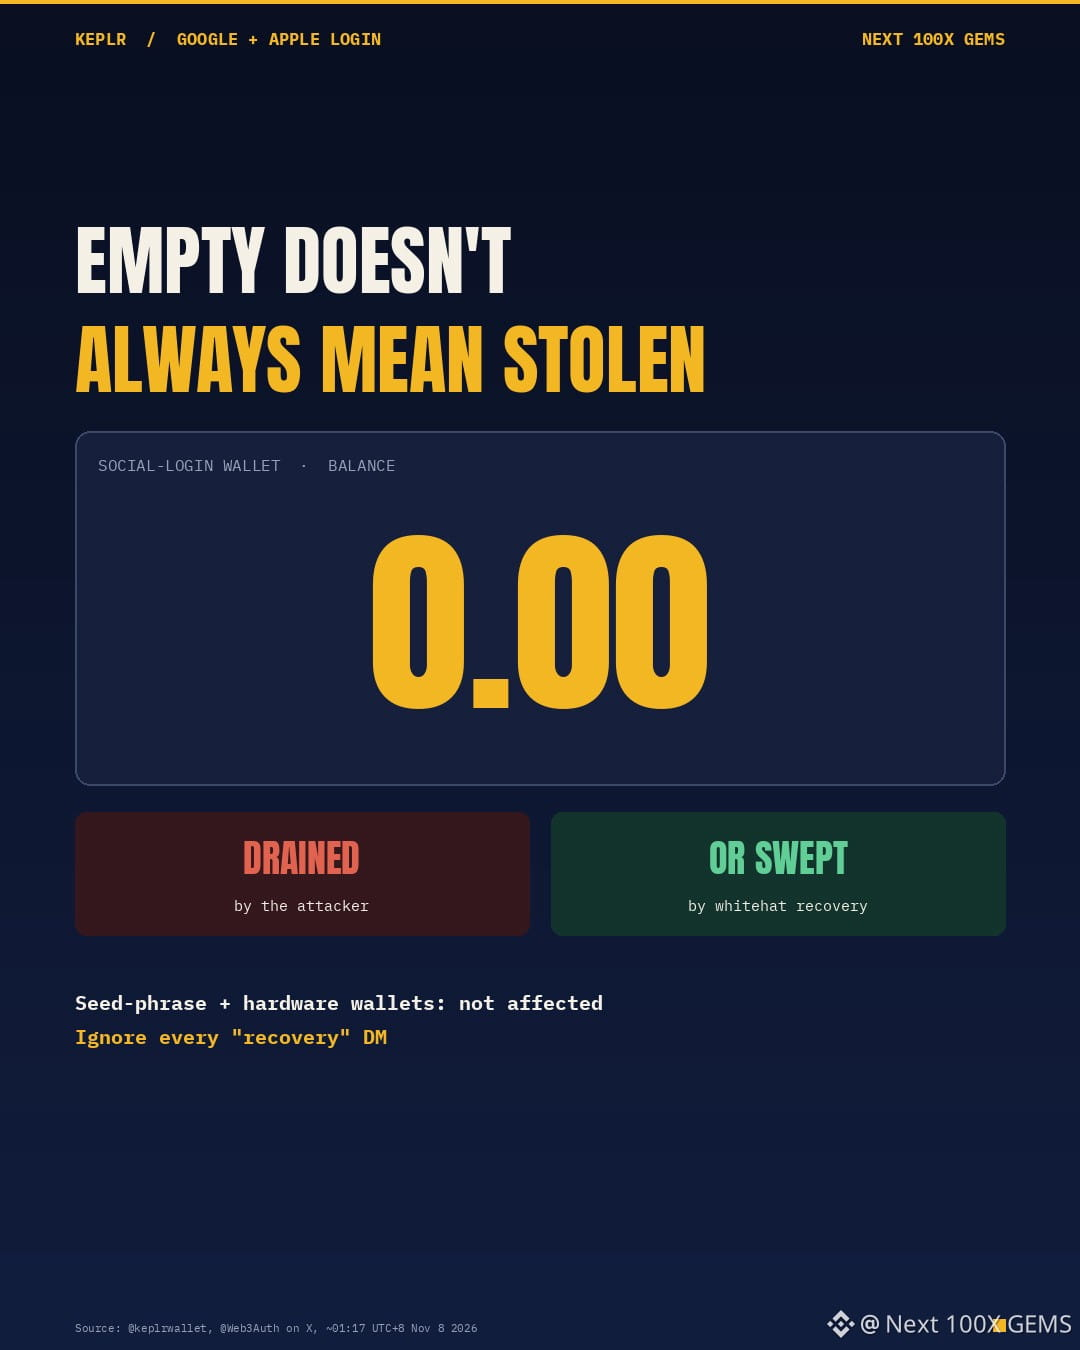
Some Keplr wallets hit zero this weekend, and Keplr is the default wallet for a lot of $ATOM holders.
Not all of those wallets were robbed.
Web3Auth, the provider behind Keplr's Google and Apple login, found a security issue in its infrastructure. Keplr calls it a private key breach. Keplr's co-founder put the early estimate at about 20% of social-login accounts affected, with only a fraction of those actually exploited so far.
Now the strange part. Web3Auth and partners started whitehat recovery on wallets that were vulnerable but not yet hit, using the same path the attacker used. So some Google/Apple-login accounts now show a reduced or empty balance because the funds were moved somewhere safe. Web3Auth says it's publishing a verified list of recovery addresses so people can tell rescue from theft.
What Keplr is telling users:
Recovery-phrase and hardware wallets are not affected.
Google/Apple-login accounts: send no new funds, and move any remaining liquid assets to a recovery-phrase or hardware wallet.
Staked and locked assets take longer to secure.
Trust only Keplr's and Web3Auth's official X accounts. Ignore every DM or link offering "recovery". That's where the second round of losses usually comes from.
An empty balance tonight is a reason to check official channels, not to panic-sign something.
#CryptoSecurity #Cosmos
NFA. DYOR.
Some Keplr wallets hit zero this weekend, and Keplr is the default wallet for a lot of $ATOM holders.
Not all of those wallets were robbed.
Web3Auth, the provider behind Keplr's Google and Apple login, found a security issue in its infrastructure. Keplr calls it a private key breach. Keplr's co-founder put the early estimate at about 20% of social-login accounts affected, with only a fraction of those actually exploited so far.
Now the strange part. Web3Auth and partners started whitehat recovery on wallets that were vulnerable but not yet hit, using the same path the attacker used. So some Google/Apple-login accounts now show a reduced or empty balance because the funds were moved somewhere safe. Web3Auth says it's publishing a verified list of recovery addresses so people can tell rescue from theft.
What Keplr is telling users:
Recovery-phrase and hardware wallets are not affected.
Google/Apple-login accounts: send no new funds, and move any remaining liquid assets to a recovery-phrase or hardware wallet.
Staked and locked assets take longer to secure.
Trust only Keplr's and Web3Auth's official X accounts. Ignore every DM or link offering "recovery". That's where the second round of losses usually comes from.
An empty balance tonight is a reason to check official channels, not to panic-sign something.
#CryptoSecurity #Cosmos
NFA. DYOR.
Not all of those wallets were robbed.
Web3Auth, the provider behind Keplr's Google and Apple login, found a security issue in its infrastructure. Keplr calls it a private key breach. Keplr's co-founder put the early estimate at about 20% of social-login accounts affected, with only a fraction of those actually exploited so far.
Now the strange part. Web3Auth and partners started whitehat recovery on wallets that were vulnerable but not yet hit, using the same path the attacker used. So some Google/Apple-login accounts now show a reduced or empty balance because the funds were moved somewhere safe. Web3Auth says it's publishing a verified list of recovery addresses so people can tell rescue from theft.
What Keplr is telling users:
Recovery-phrase and hardware wallets are not affected.
Google/Apple-login accounts: send no new funds, and move any remaining liquid assets to a recovery-phrase or hardware wallet.
Staked and locked assets take longer to secure.
Trust only Keplr's and Web3Auth's official X accounts. Ignore every DM or link offering "recovery". That's where the second round of losses usually comes from.
An empty balance tonight is a reason to check official channels, not to panic-sign something.
#CryptoSecurity #Cosmos
NFA. DYOR.
Carmelita Daniely fWzO:
这就是不建属于自己的网络钱包的短板只要合作伙伴的钱包出问题自己的持有者和用户的余额就会被波及,强烈提议cosmos创建独属于自己的生态网络钱包社绝此类风险
1
203

·
--
🚨 $SAND BLOWOUT: OVER 500 MILLION TOKENS ILLEGALLY MINTED IN CRITICAL EXPLOIT! 🩸
Smart contract exploit on Base allowed an attacker address to trigger an infinite mint, flooding supply with over 500M illegally created $SAND tokens. 🚨 Panic selling hit instantly, knocking price down by double digits as the market digested the massive dilution threat.
🔍 This vulnerability exposes severe risk vectors during multi-chain expansions when core minting rights are compromised. 💡 Smart money is stepping back to watch whether team response can contain the fallout or if contract permissions are permanently broken.
💬 Are you holding through the chaos or dumping your exposure until security audits confirm a fix? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAND #Exploit #CryptoSecurity #DeFi
🚨 📉
🚨 $SAND BLOWOUT: OVER 500 MILLION TOKENS ILLEGALLY MINTED IN CRITICAL EXPLOIT! 🩸
Smart contract exploit on Base allowed an attacker address to trigger an infinite mint, flooding supply with over 500M illegally created $SAND tokens. 🚨 Panic selling hit instantly, knocking price down by double digits as the market digested the massive dilution threat.
🔍 This vulnerability exposes severe risk vectors during multi-chain expansions when core minting rights are compromised. 💡 Smart money is stepping back to watch whether team response can contain the fallout or if contract permissions are permanently broken.
💬 Are you holding through the chaos or dumping your exposure until security audits confirm a fix? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAND #Exploit #CryptoSecurity #DeFi
🚨 📉
Smart contract exploit on Base allowed an attacker address to trigger an infinite mint, flooding supply with over 500M illegally created $SAND tokens. 🚨 Panic selling hit instantly, knocking price down by double digits as the market digested the massive dilution threat.
🔍 This vulnerability exposes severe risk vectors during multi-chain expansions when core minting rights are compromised. 💡 Smart money is stepping back to watch whether team response can contain the fallout or if contract permissions are permanently broken.
💬 Are you holding through the chaos or dumping your exposure until security audits confirm a fix? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAND #Exploit #CryptoSecurity #DeFi
🚨 📉
11
·
--
🛡️ BINANCE REPORTS 98% ASSET REPLENISHMENT
Following its October 29 security incident, Binance reported that approximately 98% of impacted token assets had been replenished.
The exchange also said it was working to restore remaining assets and that affected customers would not bear the losses.
The incident report highlighted compromised employee devices and stolen deployment credentials.
This case is a reminder that cybersecurity is critical for every major crypto platform.
How important is exchange security when choosing a platform?
#Binance #CryptoSecurity #BlockchainSecurity $BTC
🛡️ BINANCE REPORTS 98% ASSET REPLENISHMENT
Following its October 29 security incident, Binance reported that approximately 98% of impacted token assets had been replenished.
The exchange also said it was working to restore remaining assets and that affected customers would not bear the losses.
The incident report highlighted compromised employee devices and stolen deployment credentials.
This case is a reminder that cybersecurity is critical for every major crypto platform.
How important is exchange security when choosing a platform?
#Binance #CryptoSecurity #BlockchainSecurity $BTC
Following its October 29 security incident, Binance reported that approximately 98% of impacted token assets had been replenished.
The exchange also said it was working to restore remaining assets and that affected customers would not bear the losses.
The incident report highlighted compromised employee devices and stolen deployment credentials.
This case is a reminder that cybersecurity is critical for every major crypto platform.
How important is exchange security when choosing a platform?
#Binance #CryptoSecurity #BlockchainSecurity $BTC
65
·
--
Bullish
🔐 CRYPTO SECURITY IS MORE IMPORTANT THAN EVER!
Recent exchange security incidents have reminded the crypto community that protecting digital assets must remain a top priority.
Investors are paying closer attention to exchange security, proof of reserves and withdrawal transparency.
Remember: Protect your funds before chasing profits.
#CryptoSecurity #Binance #blockchain #CryptoNews $AAPLB $MSFTB $BTC
🔐 CRYPTO SECURITY IS MORE IMPORTANT THAN EVER!
Recent exchange security incidents have reminded the crypto community that protecting digital assets must remain a top priority.
Investors are paying closer attention to exchange security, proof of reserves and withdrawal transparency.
Remember: Protect your funds before chasing profits.
#CryptoSecurity #Binance #blockchain #CryptoNews $AAPLB $MSFTB $BTC
Recent exchange security incidents have reminded the crypto community that protecting digital assets must remain a top priority.
Investors are paying closer attention to exchange security, proof of reserves and withdrawal transparency.
Remember: Protect your funds before chasing profits.
#CryptoSecurity #Binance #blockchain #CryptoNews $AAPLB $MSFTB $BTC
60
·
--
$BTC $BNB $PLTRB 🔐 YOUR CRYPTO, YOUR RESPONSIBILITY!
In the world of cryptocurrency, security is just as important as profit.
Never share your Seed Phrase or Private Keys with anyone. Always enable 2FA and stay alert against suspicious links and fake websites.
Remember: Protecting your crypto is your responsibility! 🚀
💬 Question for the community:
What is your number one rule for keeping crypto safe?
👇 Share your thoughts!
#Binance #CryptoSecurity #bitcoin #blockchain #crypto
$BTC $BNB $PLTRB 🔐 YOUR CRYPTO, YOUR RESPONSIBILITY!
In the world of cryptocurrency, security is just as important as profit.
Never share your Seed Phrase or Private Keys with anyone. Always enable 2FA and stay alert against suspicious links and fake websites.
Remember: Protecting your crypto is your responsibility! 🚀
💬 Question for the community:
What is your number one rule for keeping crypto safe?
👇 Share your thoughts!
#Binance #CryptoSecurity #bitcoin #blockchain #crypto
In the world of cryptocurrency, security is just as important as profit.
Never share your Seed Phrase or Private Keys with anyone. Always enable 2FA and stay alert against suspicious links and fake websites.
Remember: Protecting your crypto is your responsibility! 🚀
💬 Question for the community:
What is your number one rule for keeping crypto safe?
👇 Share your thoughts!
#Binance #CryptoSecurity #bitcoin #blockchain #crypto
31
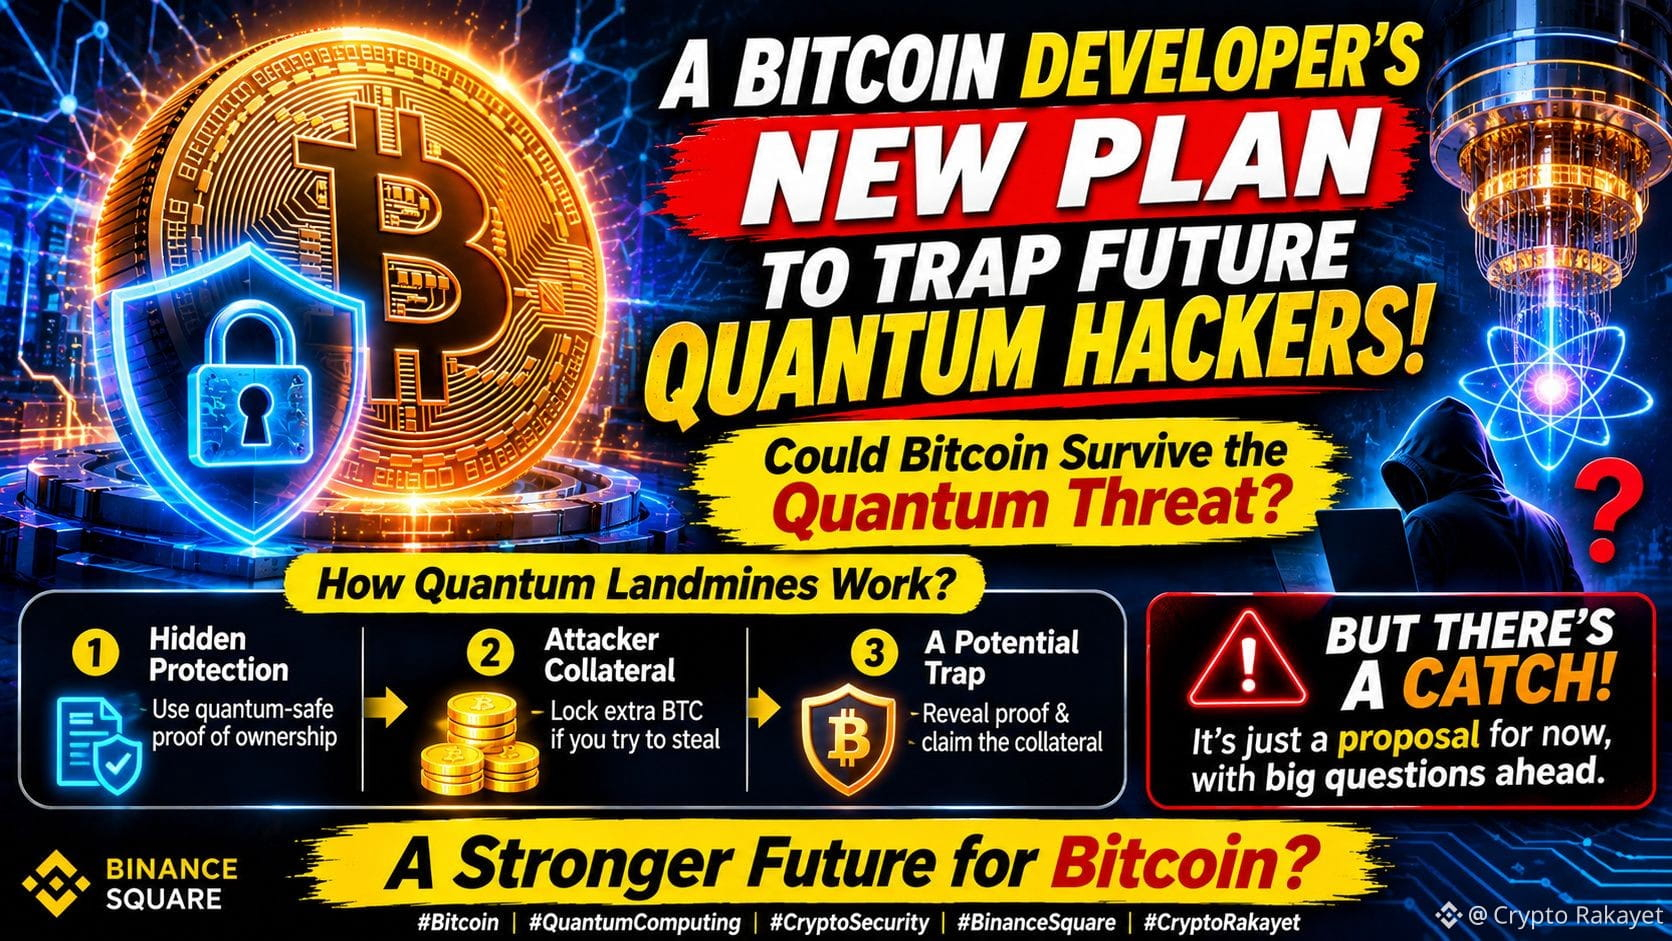
🚨 A BITCOIN DEVELOPER HAS A NEW PLAN TO TRAP FUTURE QUANTUM HACKERS!
Could Bitcoin turn a quantum attacker's biggest advantage into their biggest risk?
A Bitcoin Core developer named Cory Fields has proposed an unusual concept called “Quantum Landmines.”
🧠 How could it work?
🔐 1. Hidden Protection: Bitcoin owners could prepare secret proof of ownership using quantum-safe technology.
💰 2. Attacker Collateral: Anyone attempting to steal vulnerable BTC would have to lock up additional Bitcoin as collateral.
⚠️ 3. A Potential Trap: If the legitimate owner reveals their hidden proof during a waiting period, they could potentially recover their Bitcoin and claim the attacker's collateral.
But there's a catch!
This is only an early thought experiment, not an active Bitcoin upgrade.
It also raises difficult questions about legitimate owners, lost coins, and how such a system could be enforced.
💡 My perspective:
Quantum computing is not an immediate threat to Bitcoin today. But preparing for future cryptographic risks is important because major network upgrades can take years.
🔥 The big question:
Could Quantum Landmines become part of Bitcoin's future security strategy, or is this idea too complicated to implement?
💬 What do you think?
#Bitcoin #BTC #quantumcomputing #CryptoSecurity #BinanceSquare
🚨 A BITCOIN DEVELOPER HAS A NEW PLAN TO TRAP FUTURE QUANTUM HACKERS!
Could Bitcoin turn a quantum attacker's biggest advantage into their biggest risk?
A Bitcoin Core developer named Cory Fields has proposed an unusual concept called “Quantum Landmines.”
🧠 How could it work?
🔐 1. Hidden Protection: Bitcoin owners could prepare secret proof of ownership using quantum-safe technology.
💰 2. Attacker Collateral: Anyone attempting to steal vulnerable BTC would have to lock up additional Bitcoin as collateral.
⚠️ 3. A Potential Trap: If the legitimate owner reveals their hidden proof during a waiting period, they could potentially recover their Bitcoin and claim the attacker's collateral.
But there's a catch!
This is only an early thought experiment, not an active Bitcoin upgrade.
It also raises difficult questions about legitimate owners, lost coins, and how such a system could be enforced.
💡 My perspective:
Quantum computing is not an immediate threat to Bitcoin today. But preparing for future cryptographic risks is important because major network upgrades can take years.
🔥 The big question:
Could Quantum Landmines become part of Bitcoin's future security strategy, or is this idea too complicated to implement?
💬 What do you think?
#Bitcoin #BTC #quantumcomputing #CryptoSecurity #BinanceSquare
Could Bitcoin turn a quantum attacker's biggest advantage into their biggest risk?
A Bitcoin Core developer named Cory Fields has proposed an unusual concept called “Quantum Landmines.”
🧠 How could it work?
🔐 1. Hidden Protection: Bitcoin owners could prepare secret proof of ownership using quantum-safe technology.
💰 2. Attacker Collateral: Anyone attempting to steal vulnerable BTC would have to lock up additional Bitcoin as collateral.
⚠️ 3. A Potential Trap: If the legitimate owner reveals their hidden proof during a waiting period, they could potentially recover their Bitcoin and claim the attacker's collateral.
But there's a catch!
This is only an early thought experiment, not an active Bitcoin upgrade.
It also raises difficult questions about legitimate owners, lost coins, and how such a system could be enforced.
💡 My perspective:
Quantum computing is not an immediate threat to Bitcoin today. But preparing for future cryptographic risks is important because major network upgrades can take years.
🔥 The big question:
Could Quantum Landmines become part of Bitcoin's future security strategy, or is this idea too complicated to implement?
💬 What do you think?
#Bitcoin #BTC #quantumcomputing #CryptoSecurity #BinanceSquare
58
·
--
Bullish
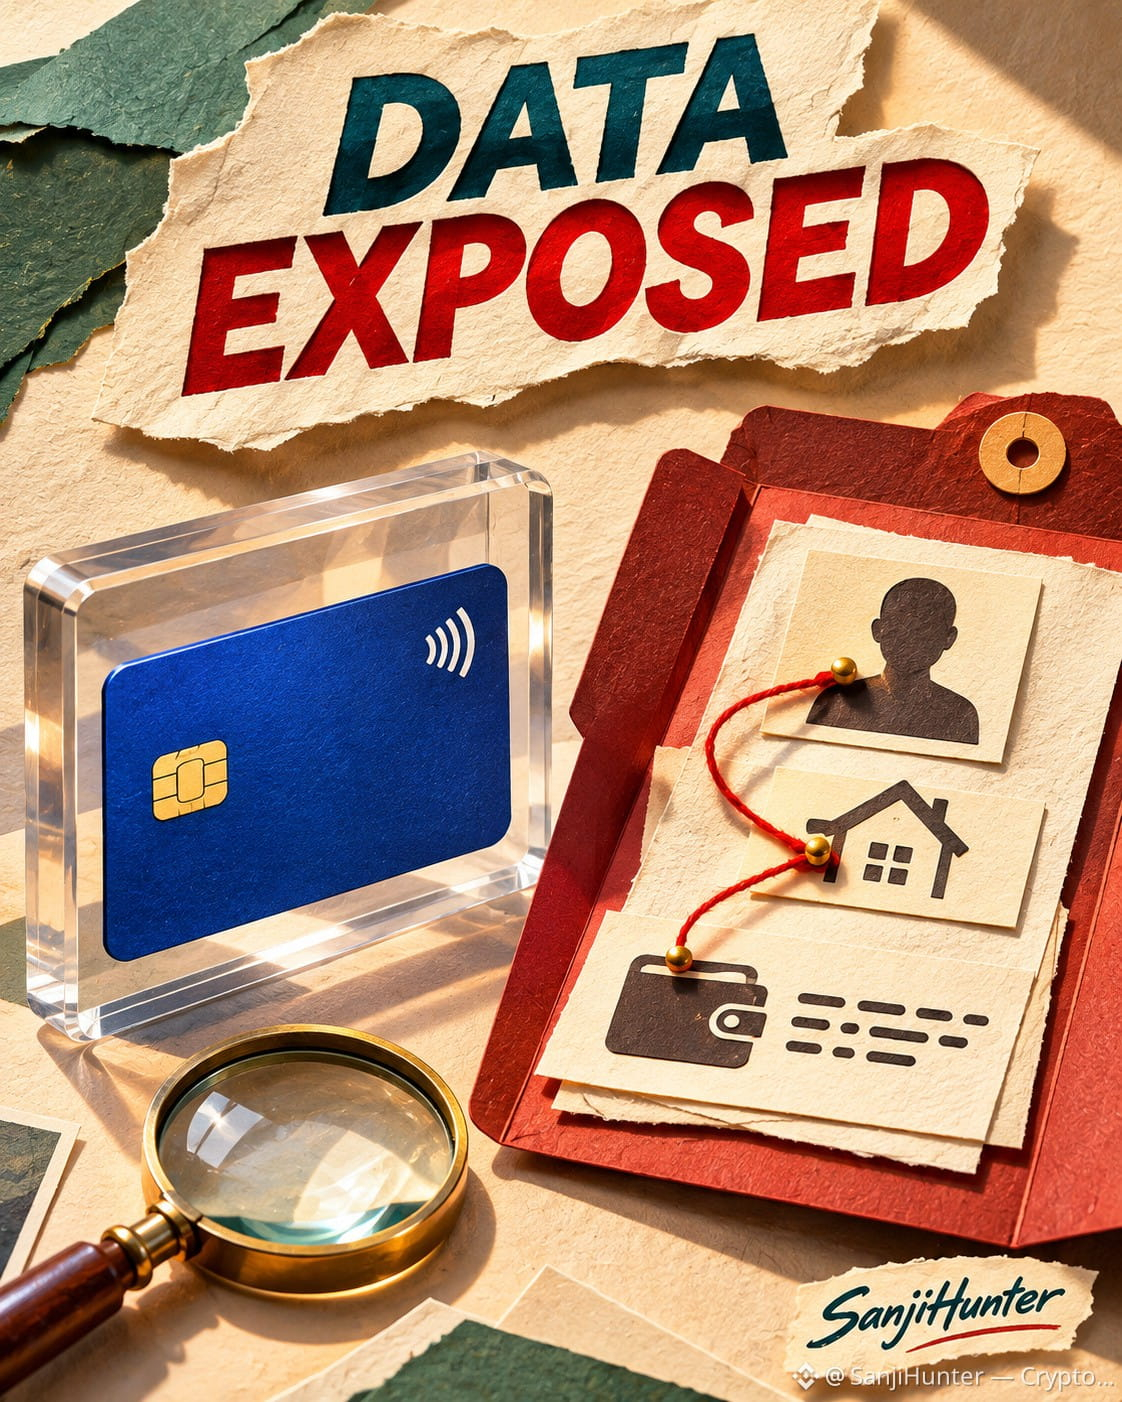
🚨 Your crypto can stay safe while your home address and wallet details are exposed
That's the disturbing lesson from Gnosis Pay's latest security breach
On November 3, attackers accessed the legacy system behind Gnosis Pay-branded cards
The company disclosed the incident on November 6, confirming that customer information was exposed
Customer funds were unaffected, according to Gnosis Pay
But some reported breach notifications included names, home addresses, card details and linked crypto wallet addresses
Think about what that means 👇
$GNO
{spot}(GNOUSDT)
💳 A compromised payment card can be replaced
🔗 A wallet address linked to your real identity may expose years of public blockchain activity
Gnosis Pay has tightened security and made 3D Secure mandatory for online payments
⚠️ If you receive a breach notice, check the affected details through official channels and review your card activity
Never follow unexpected links asking you to verify your identity or move crypto
The affected legacy card system is scheduled to close on December 20
But exposed personal information doesn't disappear when a system shuts down
$ETH
{future}(ETHUSDT)
#GnosisPay #CryptoSecurity
🚨 Your crypto can stay safe while your home address and wallet details are exposed
That's the disturbing lesson from Gnosis Pay's latest security breach
On November 3, attackers accessed the legacy system behind Gnosis Pay-branded cards
The company disclosed the incident on November 6, confirming that customer information was exposed
Customer funds were unaffected, according to Gnosis Pay
But some reported breach notifications included names, home addresses, card details and linked crypto wallet addresses
Think about what that means 👇
$GNO
💳 A compromised payment card can be replaced
🔗 A wallet address linked to your real identity may expose years of public blockchain activity
Gnosis Pay has tightened security and made 3D Secure mandatory for online payments
⚠️ If you receive a breach notice, check the affected details through official channels and review your card activity
Never follow unexpected links asking you to verify your identity or move crypto
The affected legacy card system is scheduled to close on December 20
But exposed personal information doesn't disappear when a system shuts down
$ETH
#GnosisPay #CryptoSecurity
That's the disturbing lesson from Gnosis Pay's latest security breach
On November 3, attackers accessed the legacy system behind Gnosis Pay-branded cards
The company disclosed the incident on November 6, confirming that customer information was exposed
Customer funds were unaffected, according to Gnosis Pay
But some reported breach notifications included names, home addresses, card details and linked crypto wallet addresses
Think about what that means 👇
$GNO
💳 A compromised payment card can be replaced
🔗 A wallet address linked to your real identity may expose years of public blockchain activity
Gnosis Pay has tightened security and made 3D Secure mandatory for online payments
⚠️ If you receive a breach notice, check the affected details through official channels and review your card activity
Never follow unexpected links asking you to verify your identity or move crypto
The affected legacy card system is scheduled to close on December 20
But exposed personal information doesn't disappear when a system shuts down
$ETH
#GnosisPay #CryptoSecurity
37
·
--
🚨 Security is everything in crypto!
Binance has reported progress in recovering assets following a major security incident, saying it has replenished 98% of affected token assets.
This is a reminder that even big platforms face serious security challenges.
Do you still trust centralized exchanges with your crypto?
#Binance #CryptoSecurity #BNB #CryptoNews
🚨 Security is everything in crypto!
Binance has reported progress in recovering assets following a major security incident, saying it has replenished 98% of affected token assets.
This is a reminder that even big platforms face serious security challenges.
Do you still trust centralized exchanges with your crypto?
#Binance #CryptoSecurity #BNB #CryptoNews
Binance has reported progress in recovering assets following a major security incident, saying it has replenished 98% of affected token assets.
This is a reminder that even big platforms face serious security challenges.
Do you still trust centralized exchanges with your crypto?
#Binance #CryptoSecurity #BNB #CryptoNews
Life is Race
·
--
$ONE Claim A Big Gift here 🎁🎁🎁🎁🎁🎁🧧🧧🧧🧧🧧✅✅✅✅✅✅
111
·
--
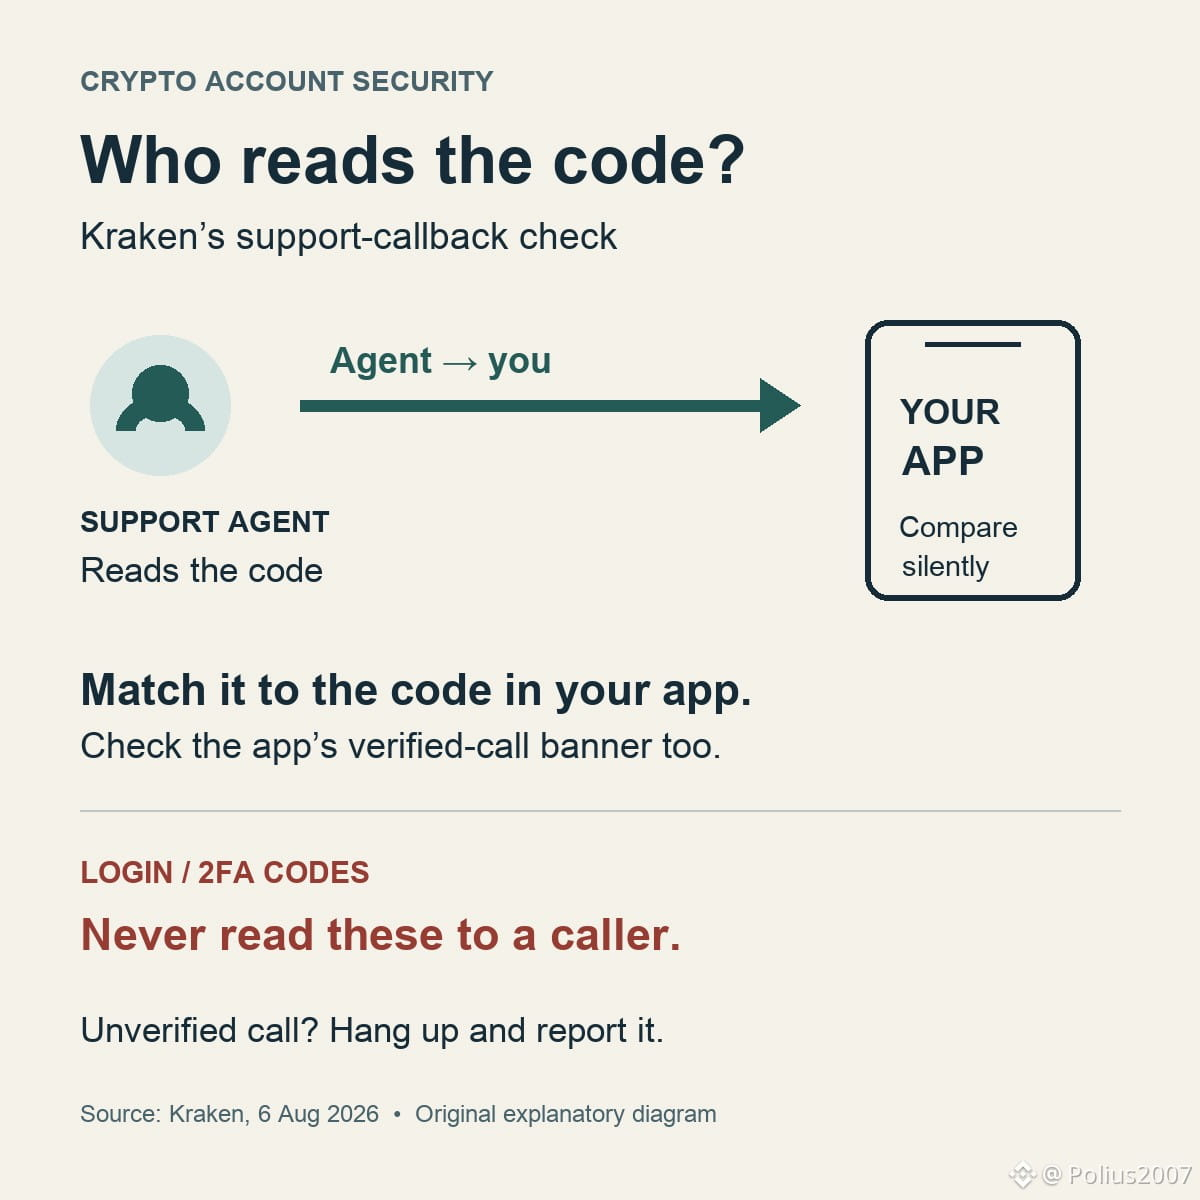
If someone calls claiming to be Kraken Support, ask them to read the verification code shown in your Kraken app. You compare it with your screen, rather than reading it out to the caller.
Kraken describes that check in its August 6 security update. During a support callback, the app displays a one-time code and a banner confirming the call. A matching code shows that the caller has legitimate access to your support case, according to Kraken. Caller ID alone cannot establish that: phone numbers can be spoofed.
This call-verification code is different from a login or two-factor authentication code. Kraken says support will never ask you to share your password or 2FA code, or move funds because of a phone request.
Kraken also says callbacks follow contact you initiated through its app, email or chat. If the app cannot verify the call, hang up and report it directly.
Source: Kraken's August 6, 2026 announcement, checked November 7. Existing features in Kraken, Kraken Pro and Krak, not a new launch today.
https://blog.kraken.com/product/security/how-to-verify-a-call-is-really-from-kraken-support
#CryptoSecurity
If someone calls claiming to be Kraken Support, ask them to read the verification code shown in your Kraken app. You compare it with your screen, rather than reading it out to the caller.
Kraken describes that check in its August 6 security update. During a support callback, the app displays a one-time code and a banner confirming the call. A matching code shows that the caller has legitimate access to your support case, according to Kraken. Caller ID alone cannot establish that: phone numbers can be spoofed.
This call-verification code is different from a login or two-factor authentication code. Kraken says support will never ask you to share your password or 2FA code, or move funds because of a phone request.
Kraken also says callbacks follow contact you initiated through its app, email or chat. If the app cannot verify the call, hang up and report it directly.
Source: Kraken's August 6, 2026 announcement, checked November 7. Existing features in Kraken, Kraken Pro and Krak, not a new launch today.
https://blog.kraken.com/product/security/how-to-verify-a-call-is-really-from-kraken-support
#CryptoSecurity
Kraken describes that check in its August 6 security update. During a support callback, the app displays a one-time code and a banner confirming the call. A matching code shows that the caller has legitimate access to your support case, according to Kraken. Caller ID alone cannot establish that: phone numbers can be spoofed.
This call-verification code is different from a login or two-factor authentication code. Kraken says support will never ask you to share your password or 2FA code, or move funds because of a phone request.
Kraken also says callbacks follow contact you initiated through its app, email or chat. If the app cannot verify the call, hang up and report it directly.
Source: Kraken's August 6, 2026 announcement, checked November 7. Existing features in Kraken, Kraken Pro and Krak, not a new launch today.
https://blog.kraken.com/product/security/how-to-verify-a-call-is-really-from-kraken-support
#CryptoSecurity
68
·
--
📰 Crypto News Update
Bloom bot hackers loot $953K faster than you can microwave popcorn
Why it matters: This security incident may affect users, platforms, fund safety, and market confidence.
Importance score: 7/10
Source: Cointelegraph
Read the original report: https://cointelegraph.com/news/bloom-bot-hackers-953k-faster-popcorn
#CryptoSecurity #CryptoNews #Cryptocurrency #Blockchain
📰 Crypto News Update
Bloom bot hackers loot $953K faster than you can microwave popcorn
Why it matters: This security incident may affect users, platforms, fund safety, and market confidence.
Importance score: 7/10
Source: Cointelegraph
Read the original report: https://cointelegraph.com/news/bloom-bot-hackers-953k-faster-popcorn
#CryptoSecurity #CryptoNews #Cryptocurrency #Blockchain
Bloom bot hackers loot $953K faster than you can microwave popcorn
Why it matters: This security incident may affect users, platforms, fund safety, and market confidence.
Importance score: 7/10
Source: Cointelegraph
Read the original report: https://cointelegraph.com/news/bloom-bot-hackers-953k-faster-popcorn
#CryptoSecurity #CryptoNews #Cryptocurrency #Blockchain
62
·
--
Never sign a blank or vague transaction. 📄
If the contract does not show what you are approving, reject it. Blind signing is how wallets get emptied. Know what you sign.
#KeepItLegit #ᴰʸᴼᴿ
#CryptoSecurity #DeFi #StaySAFU .
Never sign a blank or vague transaction. 📄
If the contract does not show what you are approving, reject it. Blind signing is how wallets get emptied. Know what you sign.
#KeepItLegit #ᴰʸᴼᴿ
#CryptoSecurity #DeFi #StaySAFU .
If the contract does not show what you are approving, reject it. Blind signing is how wallets get emptied. Know what you sign.
#KeepItLegit #ᴰʸᴼᴿ
#CryptoSecurity #DeFi #StaySAFU .
152
·
--
Protecting your trading bot from over-permissive API keys is crucial for success. 🔒
Securing your connection for platforms like WolfBot requires a precise, multi-layered approach.
1. Never grant withdrawal or transfer permissions. This is the most critical control setting. ⚠️
2. When setting up keys on exchanges like Binance, navigate to API Management. Enable Spot & Margin Trading, but specifically disable Withdrawals.
3. For WolfBot to work, ensure the API key has 'Trade' (Read-Write) and 'Read' (Read-Only) permissions enabled, while explicitly disabling all withdrawal or transfer capabilities. ✅
4. For maximum security, always bind your API keys to your machine's IP address. This prevents unauthorized use from different locations. 📍
5. If you suspect a key is compromised, immediately delete the key on the exchange, check for unauthorized activity, and generate a brand new, restricted key for WolfBot.
For a detailed walkthrough covering all these steps, review our guide here: https://community.wolfbot.io/brokers/api-key-guide
#APIKeys #CryptoSecurity #TradingBot #WolfBot
Protecting your trading bot from over-permissive API keys is crucial for success. 🔒
Securing your connection for platforms like WolfBot requires a precise, multi-layered approach.
1. Never grant withdrawal or transfer permissions. This is the most critical control setting. ⚠️
2. When setting up keys on exchanges like Binance, navigate to API Management. Enable Spot & Margin Trading, but specifically disable Withdrawals.
3. For WolfBot to work, ensure the API key has 'Trade' (Read-Write) and 'Read' (Read-Only) permissions enabled, while explicitly disabling all withdrawal or transfer capabilities. ✅
4. For maximum security, always bind your API keys to your machine's IP address. This prevents unauthorized use from different locations. 📍
5. If you suspect a key is compromised, immediately delete the key on the exchange, check for unauthorized activity, and generate a brand new, restricted key for WolfBot.
For a detailed walkthrough covering all these steps, review our guide here: https://community.wolfbot.io/brokers/api-key-guide
#APIKeys #CryptoSecurity #TradingBot #WolfBot
Securing your connection for platforms like WolfBot requires a precise, multi-layered approach.
1. Never grant withdrawal or transfer permissions. This is the most critical control setting. ⚠️
2. When setting up keys on exchanges like Binance, navigate to API Management. Enable Spot & Margin Trading, but specifically disable Withdrawals.
3. For WolfBot to work, ensure the API key has 'Trade' (Read-Write) and 'Read' (Read-Only) permissions enabled, while explicitly disabling all withdrawal or transfer capabilities. ✅
4. For maximum security, always bind your API keys to your machine's IP address. This prevents unauthorized use from different locations. 📍
5. If you suspect a key is compromised, immediately delete the key on the exchange, check for unauthorized activity, and generate a brand new, restricted key for WolfBot.
For a detailed walkthrough covering all these steps, review our guide here: https://community.wolfbot.io/brokers/api-key-guide
#APIKeys #CryptoSecurity #TradingBot #WolfBot
1
63
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#JobsReportRaisesHikeOdds
496,234 views
3,236 Discussing
2
#CPITestsDecemberRateOutlook
138,622 views
1,049 Discussing
3
#BitcoinRebounds$75KAsChipsLead
44,819 views
336 Discussing
4
#US Data Center Rules May Constrain AI Expansion
69,257 views
225 Discussing
5
#ARKPlans14ThematicETFsCoveringAIAndTokenizedMarkets
3,899 views
63 Discussing
6
#WillAnthropicListOnTime
146,677 views
1,301 Discussing
7
#WillUS-IranTensionsBoostSafe-HavenDemand?
63,385 views
460 Discussing
8
#BitcoinETFsSee$412MNetOutflows
14,190 views
71 Discussing
9
#HKSFCPlansToRestrictCryptoAndExchangeTerms
55,901 views
504 Discussing
10
#TradFiForBeginners
87,750 views
962 Discussing