

#security
security
1.8M views
4,768 Discussing
Hot
Latest
·
--
MetaMask flags security incident, begins validator exits to safeguard assets
MetaMask is investigating an undisclosed security incident affecting part of its infrastructure and says it has found no immediate threat to user wallets.
It is working with external security advisers and partners to contain and fix the issue.
As a precaution, MetaMask is exiting affected validators linked to its non‑custodial staking operations.
The company does not control withdrawal keys, so client assets remain under client control.
Lido confirmed the infrastructure compromise and is also exiting its Ethereum validators in the Lido protocol, expecting final exits (not full withdrawals) by October 7 2026, with potential foregone rewards and downtime penalties.
Around the same time, Lookonchain reported a transfer of 133,298 ETH (over $356 million) from a wallet tied to Ethereum co‑founder Joseph Lubin, though no link to the MetaMask incident has been established.
Opinions vary, with Andy Cavanaugh warning of possible worse outcomes and Taylor Monahan calling the response a standard precaution.
Given these steps, should users reconsider non‑custodial staking for their crypto holdings?
#Crypto #Ethereum #Security #FinTech #DeFi
64

·
--
🚨 MAJOR EXCHANGE RESTORES $300M PROTECTION FUND AFTER EXPLOIT WHILE $BTC HOLDS STRENGTH ⚡
📌 A top-tier exchange just front-ran its own timeline, restoring its protection fund above $300M in two days following a $388.8M hot wallet sweep. 🔍 Fresh Proof of Reserves snapshots confirm full 100%+ backing across all assets as phased withdrawals resume.
💡 With forensic heavyweights on the trail and exchange safety nets absorbing the hit, systemic contagion looks completely neutralized. 📊 Market sentiment is steadying as liquidity channels reopen across major trading hubs. 💬 Are you resuming full trading activity now or waiting for final forensic reports? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Crypto #MarketUpdate #Security #OnChain
🔥 🛡️
26
·
--
🚨 MetaMask Security Update MetaMask reports a security incident affecting part of its infrastructure, but says there is no immediate threat to wallets. As a precaution, affected staking validators are being exited. For now, this appears to be a containment measure rather than a confirmed user-funds breach. Market impact should remain limited unless the incident expands. #MetaMask #ETH #Crypto #security
🚨 MetaMask Security Update MetaMask reports a security incident affecting part of its infrastructure, but says there is no immediate threat to wallets. As a precaution, affected staking validators are being exited. For now, this appears to be a containment measure rather than a confirmed user-funds breach. Market impact should remain limited unless the incident expands. #MetaMask #ETH #Crypto #security
67
·
--
🛡️ TOP-TIER EXCHANGE BOOSTS USER PROTECTION FUND TO 3,705 $BTC WORTH OVER $300M! 🏦
Smart money moves aren't just executed on chart order books; back-end reserves tell the real story of institutional strength. 🏦 A top-tier exchange just topped up its user protection fund to over $300 million, locking in a massive vault of 3,705 $BTC for on-chain verifiable user security.
This public treasury mechanism has been running transparently since 2022, proving that liquidity depth and risk management go hand in hand. 📊 When heavy market volatility strikes, having fully traceable on-chain reserves acts as an unshakeable wall absorbing system stress. 💡
💬 Does seeing fully transparent on-chain reserves change where you park your capital during heavy market shifts? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Crypto #Security #MarketInsight
🛡️ 💎
12
·
--
$3 signs a crypto giveaway is a scam 🚩
1 . It asks you to send crypto first. Real giveaways never ask you to "verify" by sending funds.
2 . It asks for your seed phrase or login codes. No real company or project ever needs these.
3 . It pushes you to hurry. "Only 10 minutes left!" is meant to stop you from thinking.
Before you click any link, check that it's from the official Binance app or website. Stay safe out there!
#Crypto #Scam #security #EarningsSeason #scamriskwarning $GOOGL.US $NVDAB
NVDAB-0.63%
GOOGLUS-0.81%
1
102
·
--
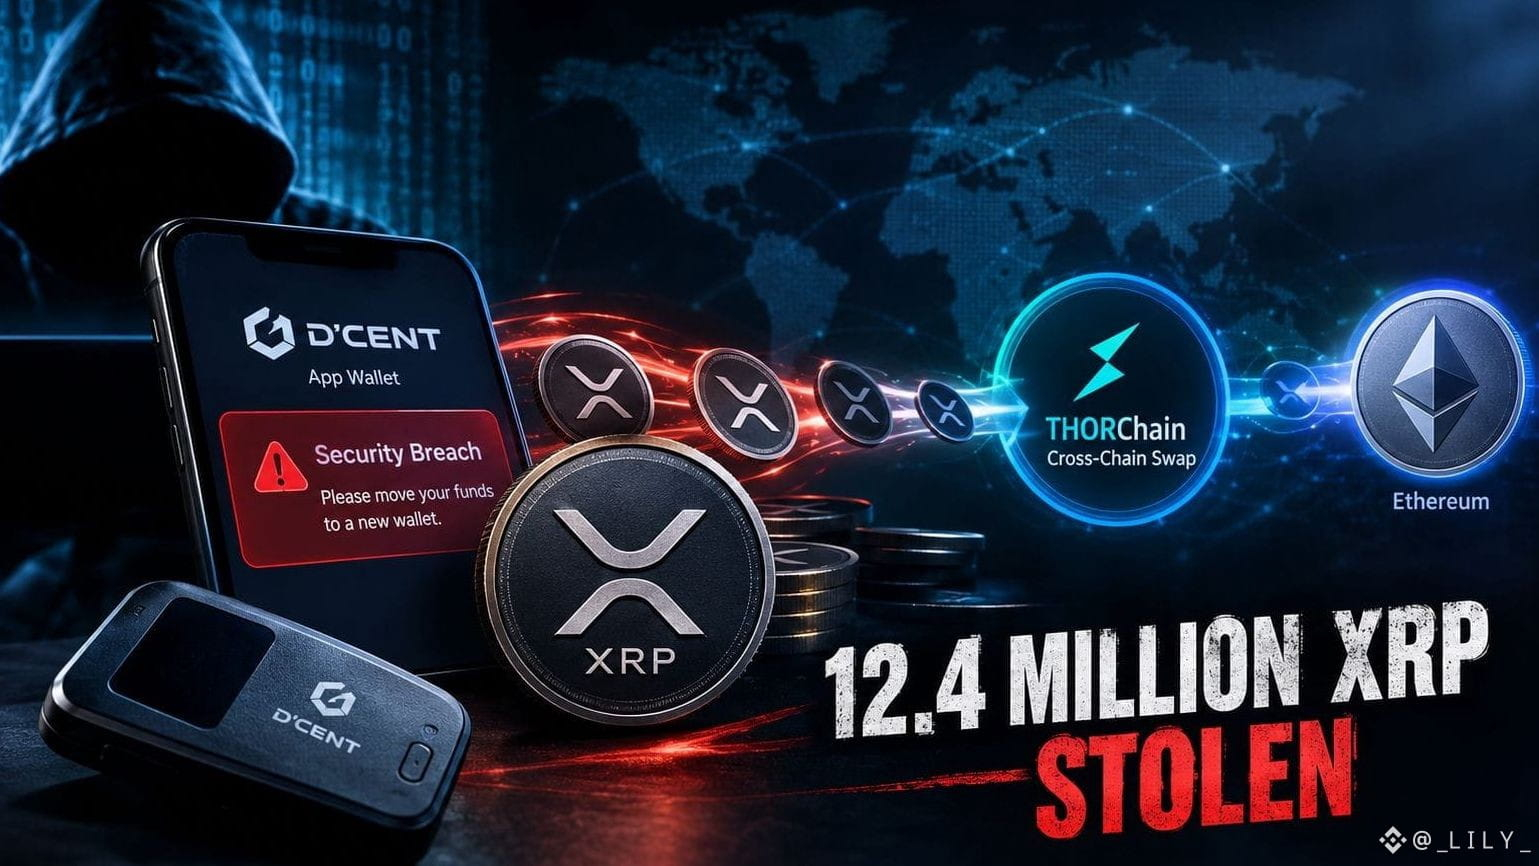
⚠️ 7,300+ D’CENT WALLETS HIT — 12.4M+ XRP DRAINED📝
🚨 A major security breach involving D’CENT App Wallets has reportedly resulted in more than 12.4 million $XRP being drained from over 7,300 wallets.
🔐 The XRP Ledger itself was not exploited — attackers used valid signatures from compromised private keys.
📉 Even after security warnings, additional XRP was reportedly stolen, pushing total losses to around $18–20M.
🌉 Some stolen funds have reportedly moved through THORChain into Ethereum, making recovery more difficult.
⚠️ D’CENT has urged affected users to generate new recovery phrases immediately.
$XRP $ETH
{future}(ETHUSDT)
#XRP #Crypto #Hack #Dcent #Security
⚠️ 7,300+ D’CENT WALLETS HIT — 12.4M+ XRP DRAINED📝
🚨 A major security breach involving D’CENT App Wallets has reportedly resulted in more than 12.4 million $XRP being drained from over 7,300 wallets.
🔐 The XRP Ledger itself was not exploited — attackers used valid signatures from compromised private keys.
📉 Even after security warnings, additional XRP was reportedly stolen, pushing total losses to around $18–20M.
🌉 Some stolen funds have reportedly moved through THORChain into Ethereum, making recovery more difficult.
⚠️ D’CENT has urged affected users to generate new recovery phrases immediately.
$XRP $ETH
#XRP #Crypto #Hack #Dcent #Security
96

·
--
🚨 $XRP SECURITY ALERT
Hackers have drained 12.4M+ $XRP from more than 7,000 D’CENT wallets in one of the biggest XRP thefts of 2026. 😳
The attack also affected assets on Bitcoin, Ethereum, Tron and Stellar.
D’CENT is urging affected users to create a new recovery phrase and migrate their assets immediately.
How safe are your crypto wallets right now? 👀
#crypto #bitcoin #Ethereum #security
#hackersdrainover12.4mxrpfromdcentwallets
2
106

·
--
🚨 CRITICAL SECURITY ALERT FOR ALL $BTC HOLDERS ON APPLE DEVICES BEFORE SYSTEM EXPLOITS 🚨
Institutional security vectors are being tested as SlowMist confirms black-hat entities actively exploiting zero-day vulnerabilities in pre-iOS 27 Apple operating systems to compromise wallet assets. 🔍 Smart money understands that operational security is the foundation of capital preservation when protecting your $BTC position. 🛡️
Attackers are executing targeted exploits via custom browser vectors and unauthorized application installs to bypass client-side encryption. 📥 Immediate system updates across all devices, alongside strict isolation of wallet interactions from Safari or unverified links, are non-negotiable protocol requirements. ⚡
Have you updated your mobile firmware today to lock down your self-custody cold storage? 💬
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #RiskManagement #Security
🛡️ 🔍
11
·
--
THORChain under fire for processing stolen Bitget assets.
Bitget confirmed on September 25 that $387.5 million reached attacker addresses, up from $351.6 million after Zcash and Tron assets were added.
CEO Gracy Chen asked THORChain on September 26 to refuse service to those addresses, saying “decentralization is a design principle, not a shield for facilitating known stolen funds.”
THORChain replied it is decentralized and permissionless like Bitcoin, Ethereum and BNB Chain, and asked what responsibility those networks would bear.
Bitget’s public tracker lists 2,377 attacker addresses holding $378 million, with 1,497 moving funds through THORChain for cross‑chain swaps.
Security researcher Taylor Monahan debated that screening transactions is equivalent to censorship; the discussion cited a May halt after a $10.7 million exploit that paused trading for five weeks.
Bitget offered 5 % bounties on frozen and recovered funds and announced phased withdrawals, with BTC restarting on September 28 at 08:00 UTC.
Should permissionless protocols intervene when known stolen assets flow through them?
#Crypto #DeFi #CrossChain #Security
1
552

#bitgetdetailssecurityincidenttimeline
#bitgetdetailssecurityincidenttimeline
Hey everyone! 👋 Let's talk about the latest updates regarding the [Bitget](https://www.binance.com/square/hashtag/Bitget) security incident timeline.
As many of you know, [Bitget](https://www.binance.com/square/hashtag/Bitget) recently faced unauthorized transfers from its hot and warm wallets, with the final affected amount revised to $387.5M.
Here is a quick look at how things unfolded:
Sept. 24: Unauthorized transfers detected and withdrawals temporarily suspended 🛑
Sept. 25: Attack path identified and vulnerability successfully fixed 🔍
Sept. 28: BTC withdrawals started returning in phases 📅
The great news is that cold wallets were completely unaffected, and the $464M+ User Protection Fund fully covers the losses, meaning user account balances remain safe and secure! 🛡️
What are your thoughts on how they handled this? Are you feeling confident about the phased withdrawal restart, or are you staying cautious? Let’s chat in the comments! 👇
$BTC, $ZEC
{spot}(ZECUSDT)
, $HBAR
{spot}(HBARUSDT)
#Bitget #crypto #security
#bitgetdetailssecurityincidenttimeline
#bitgetdetailssecurityincidenttimeline
Hey everyone! 👋 Let's talk about the latest updates regarding the Bitget security incident timeline.
As many of you know, Bitget recently faced unauthorized transfers from its hot and warm wallets, with the final affected amount revised to $387.5M.
Here is a quick look at how things unfolded:
Sept. 24: Unauthorized transfers detected and withdrawals temporarily suspended 🛑
Sept. 25: Attack path identified and vulnerability successfully fixed 🔍
Sept. 28: BTC withdrawals started returning in phases 📅
The great news is that cold wallets were completely unaffected, and the $464M+ User Protection Fund fully covers the losses, meaning user account balances remain safe and secure! 🛡️
What are your thoughts on how they handled this? Are you feeling confident about the phased withdrawal restart, or are you staying cautious? Let’s chat in the comments! 👇
$BTC, $ZEC
, $HBAR
#Bitget #crypto #security
#bitgetdetailssecurityincidenttimeline
Hey everyone! 👋 Let's talk about the latest updates regarding the Bitget security incident timeline.
As many of you know, Bitget recently faced unauthorized transfers from its hot and warm wallets, with the final affected amount revised to $387.5M.
Here is a quick look at how things unfolded:
Sept. 24: Unauthorized transfers detected and withdrawals temporarily suspended 🛑
Sept. 25: Attack path identified and vulnerability successfully fixed 🔍
Sept. 28: BTC withdrawals started returning in phases 📅
The great news is that cold wallets were completely unaffected, and the $464M+ User Protection Fund fully covers the losses, meaning user account balances remain safe and secure! 🛡️
What are your thoughts on how they handled this? Are you feeling confident about the phased withdrawal restart, or are you staying cautious? Let’s chat in the comments! 👇
$BTC, $ZEC
, $HBAR
#Bitget #crypto #security
1
3.6k

·
--
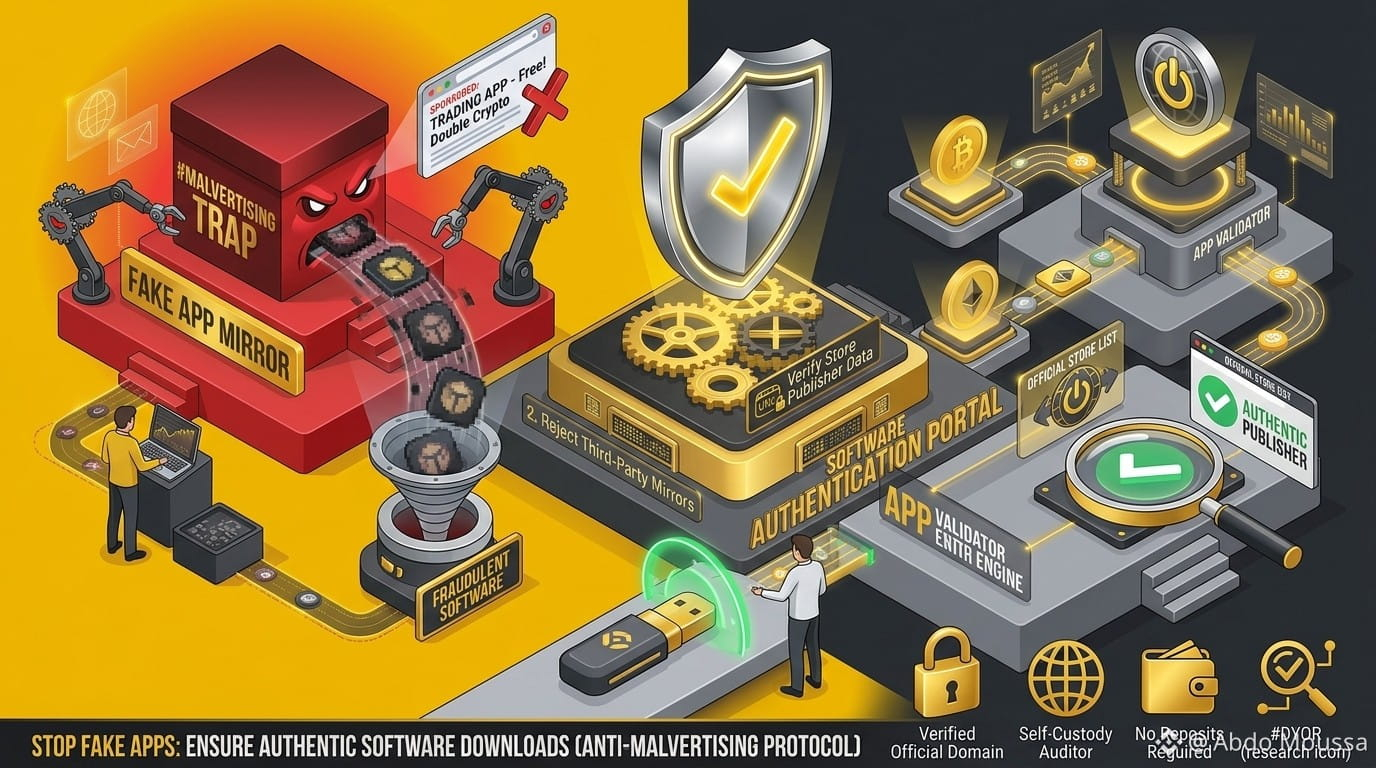
📥 Malvertising & Fake App Threats: Ensuring Authentic Software Downloads
Bad actors frequently leverage sponsored search engine ad slots—known as Malvertising—and malicious third-party mirrors to trick users into downloading counterfeit trading applications designed to harvest account credentials.
💡 Core Protocols for Software Authenticity
Avoid Sponsored Ad Links: When using search engines, bypass top "Sponsored" ad results and navigate directly to official verified web domains.
Verify Store Publisher Data: When installing applications from official stores (Google Play or Apple App Store), verify the publisher entity name and download metrics.
Reject External APK Installs: Avoid downloading third-party android package files (.apk) or software installers distributed via messaging platforms or unverified forums.
Cross-Check Developer Signatures: Ensure device security settings block side-loading of unknown applications.
⚠️ Security & Educational Disclaimer
Ensuring software integrity prevents remote keylogging and credential theft, This publication is prepared strictly for educational and security awareness purposes.
[https://www.binance.com/en/academy/glossary/malware](https://www.binance.com/en/academy/glossary/malware)
Verify your download origins, protect your endpoints, and always DYOR (Do Your Own Research) 💡
#Binance #security #AntiPhishingCode #CryptoSafety #dyor
📥 Malvertising & Fake App Threats: Ensuring Authentic Software Downloads
Bad actors frequently leverage sponsored search engine ad slots—known as Malvertising—and malicious third-party mirrors to trick users into downloading counterfeit trading applications designed to harvest account credentials.
💡 Core Protocols for Software Authenticity
Avoid Sponsored Ad Links: When using search engines, bypass top "Sponsored" ad results and navigate directly to official verified web domains.
Verify Store Publisher Data: When installing applications from official stores (Google Play or Apple App Store), verify the publisher entity name and download metrics.
Reject External APK Installs: Avoid downloading third-party android package files (.apk) or software installers distributed via messaging platforms or unverified forums.
Cross-Check Developer Signatures: Ensure device security settings block side-loading of unknown applications.
⚠️ Security & Educational Disclaimer
Ensuring software integrity prevents remote keylogging and credential theft, This publication is prepared strictly for educational and security awareness purposes.
https://www.binance.com/en/academy/glossary/malware
Verify your download origins, protect your endpoints, and always DYOR (Do Your Own Research) 💡
#Binance #security #AntiPhishingCode #CryptoSafety #dyor
6
68
·
--
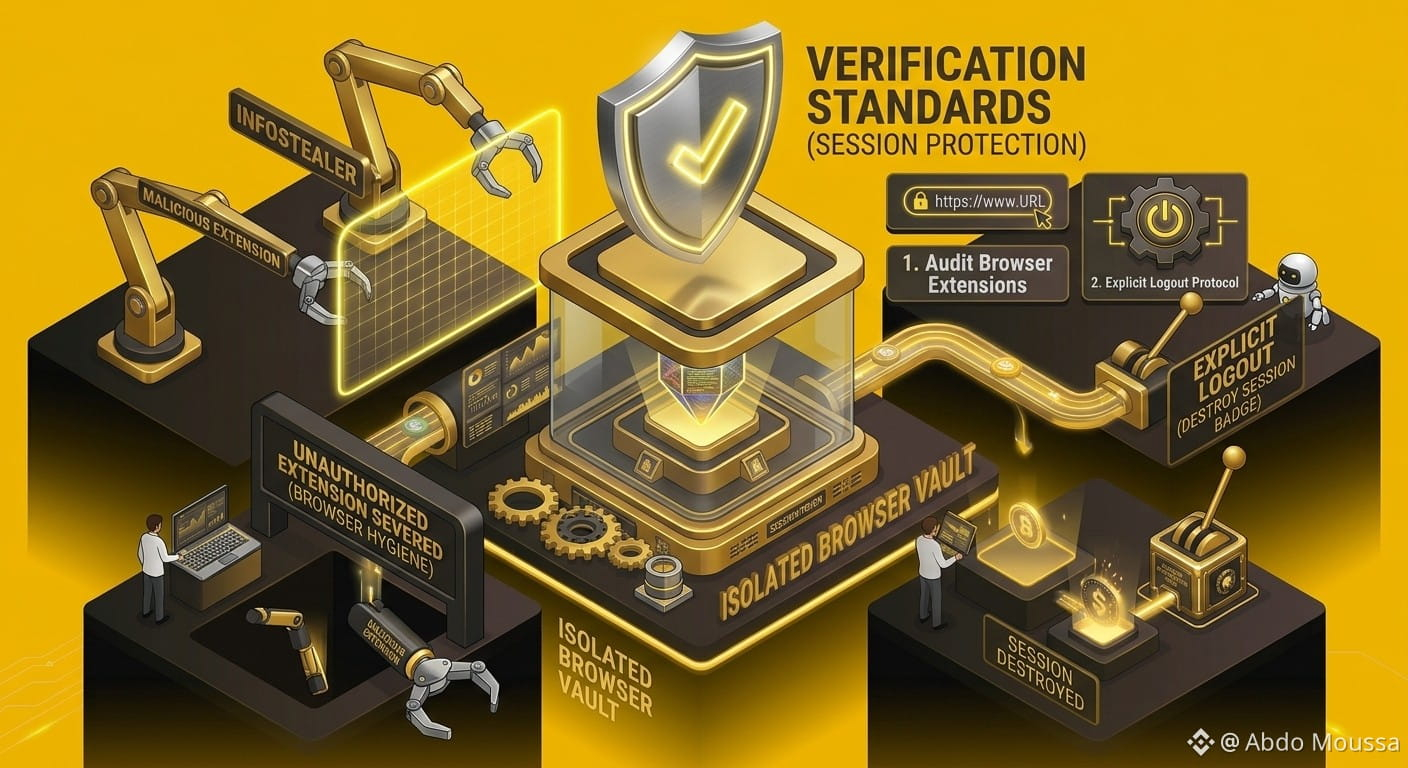
🍪 Browser Hygiene: Protecting Active Sessions from Cookie Theft
Relying solely on multi-factor authentication is insufficient if active browser sessions are left vulnerable to session-hijacking malware designed to steal access cookies and authorization tokens.
💡 Mitigating Session Hijacking & Token Theft
Understand Cookie Stealers: Specialized malware (InfoStealers) targets localized browser databases to export active session cookies, allowing attackers to clone an authenticated session on a remote machine.
Explicit Logouts: Always click the explicit Log Out button rather than simply closing the browser tab when concluding sensitive financial activities.
Audit Browser Extensions: Routinely inspect and remove unnecessary or unverified third-party browser extensions that possess broad web-reading permissions.
Isolate Trading Environments: Dedicate a clean, extension-free browser profile or isolated device exclusively for executing digital asset transactions.
⚠️ Security & Educational Disclaimer
Maintaining strict browser environment hygiene prevents unauthorized session cloning and credential harvesting, This publication is prepared strictly for educational and security awareness purposes.
[https://www.binance.com/en/academy/articles/what-are-cookies](https://www.binance.com/en/academy/articles/what-are-cookies)
Clean your browser cache, log out of sensitive sessions, and always DYOR (Do Your Own Research) 💡
#Binance #Security #AccountSecurity #dyor
🍪 Browser Hygiene: Protecting Active Sessions from Cookie Theft
Relying solely on multi-factor authentication is insufficient if active browser sessions are left vulnerable to session-hijacking malware designed to steal access cookies and authorization tokens.
💡 Mitigating Session Hijacking & Token Theft
Understand Cookie Stealers: Specialized malware (InfoStealers) targets localized browser databases to export active session cookies, allowing attackers to clone an authenticated session on a remote machine.
Explicit Logouts: Always click the explicit Log Out button rather than simply closing the browser tab when concluding sensitive financial activities.
Audit Browser Extensions: Routinely inspect and remove unnecessary or unverified third-party browser extensions that possess broad web-reading permissions.
Isolate Trading Environments: Dedicate a clean, extension-free browser profile or isolated device exclusively for executing digital asset transactions.
⚠️ Security & Educational Disclaimer
Maintaining strict browser environment hygiene prevents unauthorized session cloning and credential harvesting, This publication is prepared strictly for educational and security awareness purposes.
https://www.binance.com/en/academy/articles/what-are-cookies
Clean your browser cache, log out of sensitive sessions, and always DYOR (Do Your Own Research) 💡
#Binance #Security #AccountSecurity #dyor
7
67
·
--
Bullish
#bitgetdetailssecurityincidenttimeline
🚨 BITGET JUST REVEALED THE FULL SECURITY INCIDENT TIMELINE.
On September 24, Bitget detected unauthorized transfers from part of its hot and warm wallet infrastructure. The estimated affected amount was later revised from $351.6M to $387.5M after additional transactions were identified.
⏰ 18:31 UTC: Unauthorized transfers detected
🛑 Same day: Withdrawals temporarily suspended
🔍 Sept. 25: Attack path identified and vulnerability fixed
💰 $387.5M: Revised total affected amount
🛡️ Cold wallets: Not affected
🏦 Protection Fund: Over $464M
📅 Sept. 28: BTC withdrawals scheduled to begin returning in phases
Bitget says the incident is contained, user account balances remain unaffected, and Mandiant + SlowMist are assisting with the investigation.
🔥 Now the big question:
Will Bitget's phased withdrawal restart restore confidence — or will traders remain cautious? 👀
#Bitget #crypto #security
AngelOfCrypto_-:
nice
6
13
27.3k

If you're still keeping your entire bag on a centralized exchange, stop now.
The real damage is not just the hack. It is sitting through a withdrawal freeze while $BTC dumps or a setup you wanted evaporates, with no way to move.
Bitget has started phased withdrawals after a $388M exploit. Some people will call that a win because the exchange is covering users from reserves and reopening access in stages. Others will say a $388 million hole is exactly why you never treat a CEX as a vault.
I'm with the second group. Phased access still means you were locked when it mattered. Traders holding $ETH or sitting in $USDT cannot hedge, cannot exit, cannot rotate until someone else decides the queue is open.
Exchanges are for trading. They are not for storing the stack you cannot afford to lose. Keep what you need to trade and move the rest.
Are you still comfortable leaving the bulk of your funds on a CEX after this, or does $388M change the math for you?
#Crypto #Bitcoin #Security
34
·
--
Bullish
🚨 Alert | New developments in Ethereum staking
A security incident involving MetaMask has led the company to shut down the affected validators that are managed via Lido.
So far, this action does not indicate a breach of users’ wallets, but it highlights the importance of infrastructure security and its role in protecting staking operations.
👀 Under watch:
$ETH$ | LDO
Follow the developments and their potential impact on the staking market.
#Ethereum #ETH #Lido #LDO #MetaMask #Staking #Security
$ETH
{spot}(ETHUSDT)
$LDO
{spot}(LDOUSDT)
🚨 Alert | New developments in Ethereum staking
A security incident involving MetaMask has led the company to shut down the affected validators that are managed via Lido.
So far, this action does not indicate a breach of users’ wallets, but it highlights the importance of infrastructure security and its role in protecting staking operations.
👀 Under watch:
$ETH $ | LDO
Follow the developments and their potential impact on the staking market.
#Ethereum #ETH #Lido #LDO #MetaMask #Staking #Security
$ETH
$LDO
99

September saw crypto hack incidents worth $768 million, the worst in 2026
- In September 2026, a total of $768 million in cryptocurrency hacks were reported, making it the worst month of 2026 for cybersecurity.
- The breach of the Bitget system worth $388 million and the Liquid Network vulnerability valued at $320 million are the two main causes of the losses.
- Notably, over $270 million from the Liquid Network incident was repaid by relevant parties after the issue was discovered.
- The incident raises an important question about safeguarding assets and ensuring transaction security on blockchain platforms.
#BinanceSquare #CryptoNews #Blockchain #Security
$btc $eth
#vlikevn Titanbot
Source: CoinTelegraph
Losses from crypto hacks in September reach up to $768M, worst case in 2026
• Total losses from hacks and exploiting vulnerabilities in September reached $768 million, the worst month of 2026.
• A security breach at the Bitget exchange resulted in a loss of $388 million.
• The Liquid network was exploited for $320 million, of which more than $270 million was later reimbursed.
#BinanceSquare #CryptoNews #Security
$btc $eth
#vlikevn #Titanbot
Source: CoinTelegraph
265

🚨 $340K $USDT EXPLOIT CLAIMS FLARE UP AS API SECURITY RISKS HIT MAJOR EXCHANGE! 🚨
🔒 A high-profile trader reported a staggering $340,000 asset drain on a top-tier exchange, pointing directly at unrevoked API access during a security compromise. 🚨 The platform has launched a dedicated investigation team to handle the case one-on-one and address user protection concerns.
💡 Beyond the headline noise, this is a severe reminder that cold storage and strict API management are non-negotiable for real capital protection. 🛡️ Even the cleanest setups mean nothing if your key permissions leave the vault door wide open.
💬 How often do you audit and revoke stale API permissions across your exchange accounts? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #USDT #CryptoSecurity #RiskManagement #Security
🛡️ 👁️
9

🛡️ $BGB INFRASTRUCTURE RESTORES OPERATIONAL INTEGRITY AFTER THIRD-PARTY VULNERABILITY FIX 🔍
A top-tier exchange has fully contained an internal credential breach originating from a third-party vendor vulnerability. Affected servers were immediately isolated from the network, invalidating compromised access tokens and implementing mandatory multi-signature authorization for elevated operational protocols. 🔒
With patches finalized alongside security vendors, withdrawal architecture now enforces independent multi-chain verification prior to service resumption. System integrity remains intact, confirming zero ongoing unauthorized exposure across institutional wallet infrastructure. 🛡️
💬 How heavily do you weigh backend security protocols and withdrawal verification mechanisms when evaluating platform risk? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BGB #Security #RiskManagement #Crypto
🛡️ ⚖️
16

·
--
Bitget just got hacked for $388M and users reacted fast! Within 1 hour of withdrawals resuming, over 4000 BTC were withdrawn. This shows how quickly trust can disappear when security fails. exchanges really need to step up their security game!
Bitget刚被黑走3.88亿,用户反应真快!提款恢复才1小时,4000+个比特币就被提光了。这波操作,看得出来用户心里已经慌了,赶紧把币转走安心。交易所安全,真的太重要了!
#crypto #exchange #security #hack $BTC
Bitget刚被黑走3.88亿,用户反应真快!提款恢复才1小时,4000+个比特币就被提光了。这波操作,看得出来用户心里已经慌了,赶紧把币转走安心。交易所安全,真的太重要了!
#crypto #exchange #security #hack $BTC
99
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#EtherGains70.9%InQ3
1,521 views
117 Discussing
2
#US10YearYieldNears5.3%
32,395 views
354 Discussing
3
#DollarIndexHitsHighestSinceMay2025
786 views
74 Discussing
4
#USWeeklyJoblessClaimsFallTo197000
3,110 views
132 Discussing
5
#BitcoinETFsTake$6.34BillionInQ3
1,773 views
41 Discussing
6
#KoreaProposesTokenizingStocksAndBonds
30,633 views
492 Discussing
7
#MetaMaskExitsLidoValidatorsAfterSecurityIncident
106,673 views
1,217 Discussing
8
#MicronBeatsEarningsLiftsGuidance
59,931 views
912 Discussing
9
#CFTCSubmitsTwoEventContractRulesToWhiteHouse
41,843 views
716 Discussing
10
#BitcoinClears$85200
43,362 views
377 Discussing