
#optimjackattackinfectsatleast186websites
optimjackattackinfectsatleast186websites
33,115 views
239 Discussing
Hot
Latest
·
--
🚨 186+ WEBSITES EXPOSED TO CRYPTO-STEALING MALWARE — A MAJOR SECURITY WAKE-UP CALL!
A cyberattack dubbed OPTIMJACK has compromised third-party website scripts, exposing visitors to malicious code across major platforms, including CNN, BBC, Zoom, Salesforce and Ledger.
The malware reportedly carries three dangerous capabilities:
🔴 Crypto theft: Replaces copied cryptocurrency wallet addresses with attacker-controlled addresses.
🔴 Card theft: Attempts to capture payment-card details entered into website forms.
🔴 Device targeting: Deploys additional malicious code targeting iPhones and iPads.
Security researcher Scott Helme identified 188 infected script files across 178 organizations, while earlier reports cited at least 186 affected websites.
This incident highlights a serious weakness in digital security: even trusted websites can expose visitors through compromised third-party services.
Crypto users should always verify the complete wallet address before confirming a transaction.
#optimjackattackinfectsatleast186websites $BTC
{future}(BTCUSDT)
🚨 186+ WEBSITES EXPOSED TO CRYPTO-STEALING MALWARE — A MAJOR SECURITY WAKE-UP CALL!
A cyberattack dubbed OPTIMJACK has compromised third-party website scripts, exposing visitors to malicious code across major platforms, including CNN, BBC, Zoom, Salesforce and Ledger.
The malware reportedly carries three dangerous capabilities:
🔴 Crypto theft: Replaces copied cryptocurrency wallet addresses with attacker-controlled addresses.
🔴 Card theft: Attempts to capture payment-card details entered into website forms.
🔴 Device targeting: Deploys additional malicious code targeting iPhones and iPads.
Security researcher Scott Helme identified 188 infected script files across 178 organizations, while earlier reports cited at least 186 affected websites.
This incident highlights a serious weakness in digital security: even trusted websites can expose visitors through compromised third-party services.
Crypto users should always verify the complete wallet address before confirming a transaction.
#optimjackattackinfectsatleast186websites $BTC
A cyberattack dubbed OPTIMJACK has compromised third-party website scripts, exposing visitors to malicious code across major platforms, including CNN, BBC, Zoom, Salesforce and Ledger.
The malware reportedly carries three dangerous capabilities:
🔴 Crypto theft: Replaces copied cryptocurrency wallet addresses with attacker-controlled addresses.
🔴 Card theft: Attempts to capture payment-card details entered into website forms.
🔴 Device targeting: Deploys additional malicious code targeting iPhones and iPads.
Security researcher Scott Helme identified 188 infected script files across 178 organizations, while earlier reports cited at least 186 affected websites.
This incident highlights a serious weakness in digital security: even trusted websites can expose visitors through compromised third-party services.
Crypto users should always verify the complete wallet address before confirming a transaction.
#optimjackattackinfectsatleast186websites $BTC
1
1.9k
·
--
Bullish
🚨 OPTIMJACK Cyberattack: 186+ Websites Reportedly Affected!
A serious cybersecurity incident known as OPTIMJACK has raised concerns across the digital and crypto communities.
Security researchers discovered malicious JavaScript code affecting websites through compromised third-party scripts.
⚠️ What does the attack do?
🔹 Replaces copied cryptocurrency wallet addresses with attackers' addresses.
🔹 Attempts to steal credit card information.
🔹 Collects browser cookies and screenshots.
🔹 Delivers additional malicious code targeting certain iOS devices.
Major platforms, including CNN, BBC, Zoom and Salesforce, were among the reported affected websites.
🛡️ How to Stay Safe:
✅ Always verify wallet addresses before sending crypto.
✅ Double-check the first and last characters of an address.
✅ Keep your browser and devices updated.
✅ Avoid suspicious links and websites.
Important Reminder: Never trust a copied wallet address without verifying it. One small mistake can result in permanent loss of funds.
What do you think? Is third-party website security becoming a major concern for the crypto industry?
#OPTIMJACKAttackInfectsAtLeast186Websites #CryptoSecurity #CyberSecurity #BlockchainSecurity #Web3Safety
$BTC $ETH $SOL
🚨 OPTIMJACK Cyberattack: 186+ Websites Reportedly Affected!
A serious cybersecurity incident known as OPTIMJACK has raised concerns across the digital and crypto communities.
Security researchers discovered malicious JavaScript code affecting websites through compromised third-party scripts.
⚠️ What does the attack do?
🔹 Replaces copied cryptocurrency wallet addresses with attackers' addresses.
🔹 Attempts to steal credit card information.
🔹 Collects browser cookies and screenshots.
🔹 Delivers additional malicious code targeting certain iOS devices.
Major platforms, including CNN, BBC, Zoom and Salesforce, were among the reported affected websites.
🛡️ How to Stay Safe:
✅ Always verify wallet addresses before sending crypto.
✅ Double-check the first and last characters of an address.
✅ Keep your browser and devices updated.
✅ Avoid suspicious links and websites.
Important Reminder: Never trust a copied wallet address without verifying it. One small mistake can result in permanent loss of funds.
What do you think? Is third-party website security becoming a major concern for the crypto industry?
#OPTIMJACKAttackInfectsAtLeast186Websites #CryptoSecurity #CyberSecurity #BlockchainSecurity #Web3Safety
$BTC $ETH $SOL
A serious cybersecurity incident known as OPTIMJACK has raised concerns across the digital and crypto communities.
Security researchers discovered malicious JavaScript code affecting websites through compromised third-party scripts.
⚠️ What does the attack do?
🔹 Replaces copied cryptocurrency wallet addresses with attackers' addresses.
🔹 Attempts to steal credit card information.
🔹 Collects browser cookies and screenshots.
🔹 Delivers additional malicious code targeting certain iOS devices.
Major platforms, including CNN, BBC, Zoom and Salesforce, were among the reported affected websites.
🛡️ How to Stay Safe:
✅ Always verify wallet addresses before sending crypto.
✅ Double-check the first and last characters of an address.
✅ Keep your browser and devices updated.
✅ Avoid suspicious links and websites.
Important Reminder: Never trust a copied wallet address without verifying it. One small mistake can result in permanent loss of funds.
What do you think? Is third-party website security becoming a major concern for the crypto industry?
#OPTIMJACKAttackInfectsAtLeast186Websites #CryptoSecurity #CyberSecurity #BlockchainSecurity #Web3Safety
$BTC $ETH $SOL
1
80

🚨 TRADERS ALERT: A supply-chain attack just hit 186+ major websites—and it’s built to hijack your crypto clipboard.
Researchers uncovered OPTIMJACK, malicious JavaScript injected via Optimizely across 178 organizations—including Ledger, Coinpass, Zoom, CNN, and BBC.
What the malware does silently:
• Crypto Clipper: Swaps copied BTC, ETH, SOL, TRON, and TON addresses with the attacker’s wallet.
• Data Skimmer: Steals checkout card info, session cookies, and page screenshots.
• iOS Exploit: Targets unpatched iOS devices (18.6 and older).
Most infected scripts were scrubbed late Monday, but cached scripts still pose a risk.
Stay safe on-chain:
Check the first AND last 6 characters of every pasted address.
Verify destinations on your hardware wallet screen.
Update iOS and your browser now.
Do you double-check addresses before hitting send? Comment 👇
$BTC
{future}(BTCUSDT)
$ETH
{future}(ETHUSDT)
$HUMA
{future}(HUMAUSDT)
#optimjackattackinfectsatleast186websites
#CryptoSecurity #Web3Safety #TradingTips
🚨 TRADERS ALERT: A supply-chain attack just hit 186+ major websites—and it’s built to hijack your crypto clipboard.
Researchers uncovered OPTIMJACK, malicious JavaScript injected via Optimizely across 178 organizations—including Ledger, Coinpass, Zoom, CNN, and BBC.
What the malware does silently:
• Crypto Clipper: Swaps copied BTC, ETH, SOL, TRON, and TON addresses with the attacker’s wallet.
• Data Skimmer: Steals checkout card info, session cookies, and page screenshots.
• iOS Exploit: Targets unpatched iOS devices (18.6 and older).
Most infected scripts were scrubbed late Monday, but cached scripts still pose a risk.
Stay safe on-chain:
Check the first AND last 6 characters of every pasted address.
Verify destinations on your hardware wallet screen.
Update iOS and your browser now.
Do you double-check addresses before hitting send? Comment 👇
$BTC
$ETH
$HUMA
#optimjackattackinfectsatleast186websites
#CryptoSecurity #Web3Safety #TradingTips
Researchers uncovered OPTIMJACK, malicious JavaScript injected via Optimizely across 178 organizations—including Ledger, Coinpass, Zoom, CNN, and BBC.
What the malware does silently:
• Crypto Clipper: Swaps copied BTC, ETH, SOL, TRON, and TON addresses with the attacker’s wallet.
• Data Skimmer: Steals checkout card info, session cookies, and page screenshots.
• iOS Exploit: Targets unpatched iOS devices (18.6 and older).
Most infected scripts were scrubbed late Monday, but cached scripts still pose a risk.
Stay safe on-chain:
Check the first AND last 6 characters of every pasted address.
Verify destinations on your hardware wallet screen.
Update iOS and your browser now.
Do you double-check addresses before hitting send? Comment 👇
$BTC
$ETH
$HUMA
#optimjackattackinfectsatleast186websites
#CryptoSecurity #Web3Safety #TradingTips
Ahodakin:
Bonjour j'ai besoin d'aide
3
13
11.7k

·
--
#OPTIMJACKAttackInfectsAtLeast186Websites
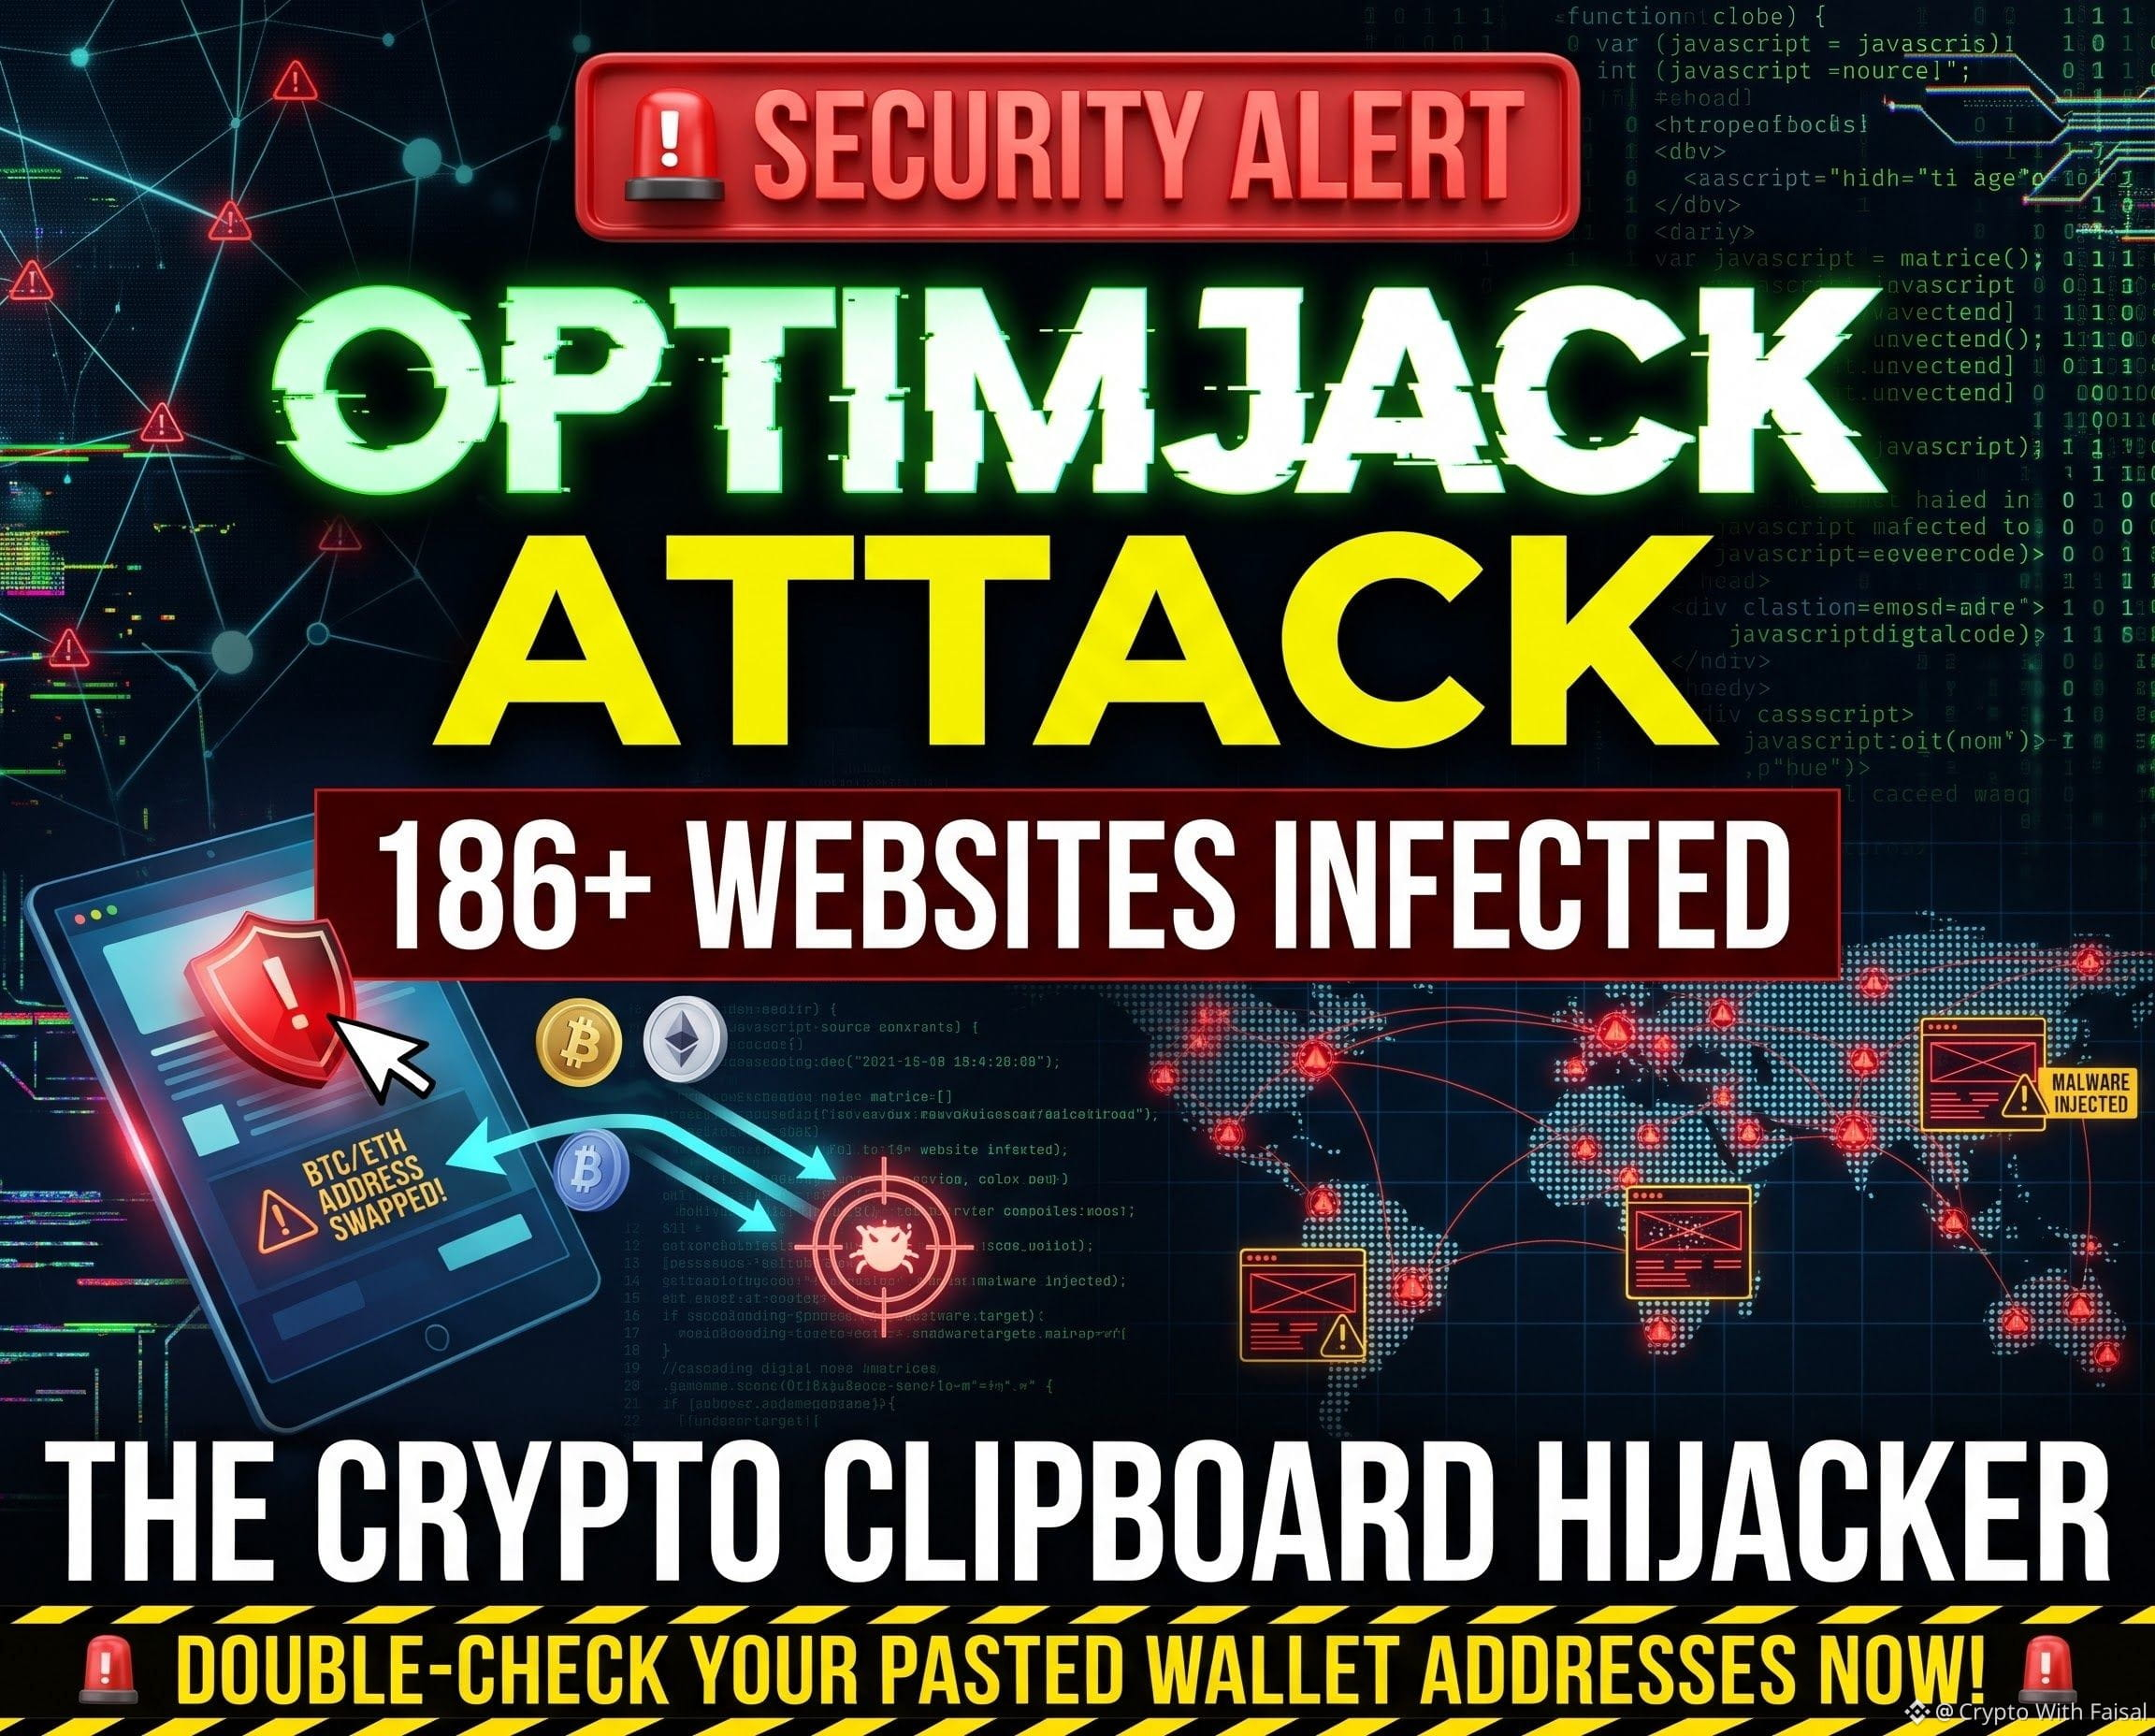
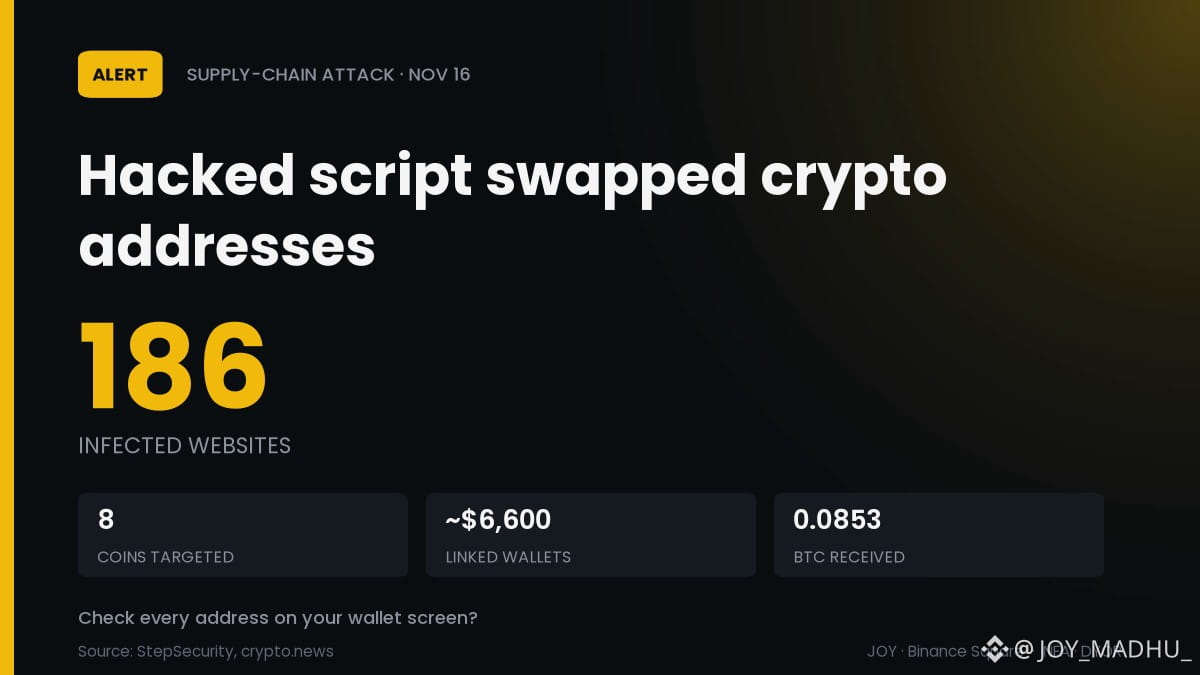
🕵️ 186 Sites Hijacked: Copied Wallet Addresses Got Swapped
A hacked Optimizely script served a crypto clipper on big-brand sites on Nov 16 (StepSecurity).
⚠️ 186 infected sites, incl. CNN, BBC, Zoom, Salesforce and Ledger
📊 Swapped addresses for 8 coins, incl. BTC, ETH, SOL and TRX
🏦 Linked wallets hold ~$6,600; the BTC one got 0.0853 BTC
📉 It also skimmed cards and targeted iPhones
My read: losses look small, but any trusted site can serve bad code.
Will you check every address on your wallet screen for 30 days: yes or no? 👇
$BTC
#OPTIMJACKAttackInfectsAtLeast186Websites #CryptoSecurity #Crypto
#OPTIMJACKAttackInfectsAtLeast186Websites
🕵️ 186 Sites Hijacked: Copied Wallet Addresses Got Swapped
A hacked Optimizely script served a crypto clipper on big-brand sites on Nov 16 (StepSecurity).
⚠️ 186 infected sites, incl. CNN, BBC, Zoom, Salesforce and Ledger
📊 Swapped addresses for 8 coins, incl. BTC, ETH, SOL and TRX
🏦 Linked wallets hold ~$6,600; the BTC one got 0.0853 BTC
📉 It also skimmed cards and targeted iPhones
My read: losses look small, but any trusted site can serve bad code.
Will you check every address on your wallet screen for 30 days: yes or no? 👇
$BTC
#OPTIMJACKAttackInfectsAtLeast186Websites #CryptoSecurity #Crypto
🕵️ 186 Sites Hijacked: Copied Wallet Addresses Got Swapped
A hacked Optimizely script served a crypto clipper on big-brand sites on Nov 16 (StepSecurity).
⚠️ 186 infected sites, incl. CNN, BBC, Zoom, Salesforce and Ledger
📊 Swapped addresses for 8 coins, incl. BTC, ETH, SOL and TRX
🏦 Linked wallets hold ~$6,600; the BTC one got 0.0853 BTC
📉 It also skimmed cards and targeted iPhones
My read: losses look small, but any trusted site can serve bad code.
Will you check every address on your wallet screen for 30 days: yes or no? 👇
$BTC
#OPTIMJACKAttackInfectsAtLeast186Websites #CryptoSecurity #Crypto
89
·
--
Bearish
🚨 Wallet address copy kiya, aur paisa kahin aur chala gaya!
#optimjackattackinfectsatleast186websites
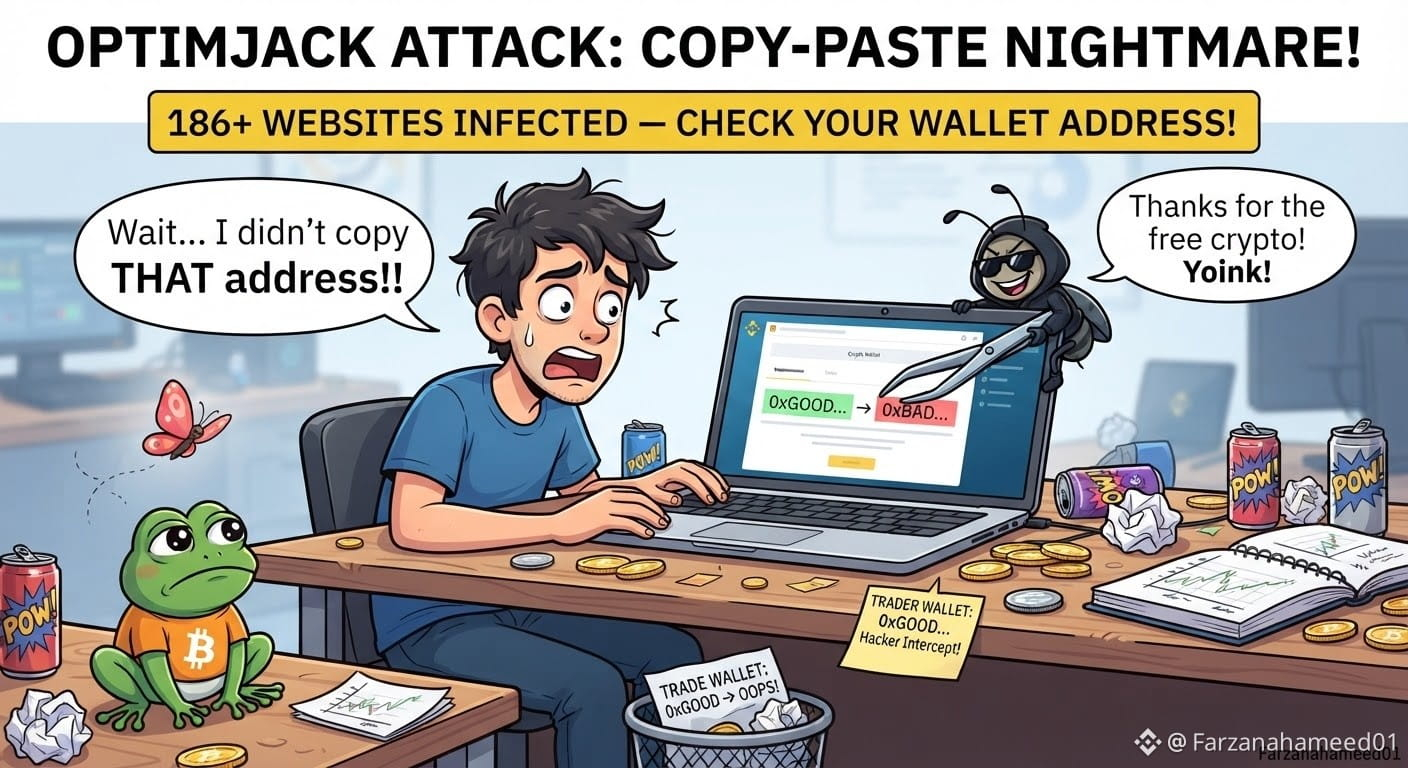
The OPTIMJACK supply chain attack is shaking up the internet after compromising Optimizely and infecting at least 186 major websites, including CNN, Zoom, and BBC!
Detailed analysis: Hackers inject malicious JavaScript code to secretly "swap out" the wallet address in your clipboard. One careless second without double-checking when you paste, and your crypto assets will "vanish" straight into a scammer's pocket!
Quick analysis:
◆ Significance: This is not just a hack, this is a clipboard attack. You copy the right address, but paste the wrong one. That is why even careful people can lose money.
◆ What learners should do: Always carefully check the first and last characters of a wallet address before sending money. Use a hardware wallet and limit transactions on unfamiliar browsers.
⚠️ This is not financial advice.✨
👇
$BTC - Watch for wallet security, strong.
$ETH - Watch for Web3 safety, strong.
$BLESS - Watch for long-term safety habits, strong.
✨𝐅𝐀𝐑𝐙𝐀𝐍𝐀 𝐇𝐀𝐌𝐄𝐄𝐃 𝐎𝐅𝐅𝐈𝐂𝐈𝐀𝐋 • 🦋 ✨
#CryptoSecurity #CyberAttack #Web3Safety #WalletSecurity #BinanceSquare
🚨 Wallet address copy kiya, aur paisa kahin aur chala gaya!
#optimjackattackinfectsatleast186websites
The OPTIMJACK supply chain attack is shaking up the internet after compromising Optimizely and infecting at least 186 major websites, including CNN, Zoom, and BBC!
Detailed analysis: Hackers inject malicious JavaScript code to secretly "swap out" the wallet address in your clipboard. One careless second without double-checking when you paste, and your crypto assets will "vanish" straight into a scammer's pocket!
Quick analysis:
◆ Significance: This is not just a hack, this is a clipboard attack. You copy the right address, but paste the wrong one. That is why even careful people can lose money.
◆ What learners should do: Always carefully check the first and last characters of a wallet address before sending money. Use a hardware wallet and limit transactions on unfamiliar browsers.
⚠️ This is not financial advice.✨
👇
$BTC - Watch for wallet security, strong.
$ETH - Watch for Web3 safety, strong.
$BLESS - Watch for long-term safety habits, strong.
✨𝐅𝐀𝐑𝐙𝐀𝐍𝐀 𝐇𝐀𝐌𝐄𝐄𝐃 𝐎𝐅𝐅𝐈𝐂𝐈𝐀𝐋 • 🦋 ✨
#CryptoSecurity #CyberAttack #Web3Safety #WalletSecurity #BinanceSquare
#optimjackattackinfectsatleast186websites
The OPTIMJACK supply chain attack is shaking up the internet after compromising Optimizely and infecting at least 186 major websites, including CNN, Zoom, and BBC!
Detailed analysis: Hackers inject malicious JavaScript code to secretly "swap out" the wallet address in your clipboard. One careless second without double-checking when you paste, and your crypto assets will "vanish" straight into a scammer's pocket!
Quick analysis:
◆ Significance: This is not just a hack, this is a clipboard attack. You copy the right address, but paste the wrong one. That is why even careful people can lose money.
◆ What learners should do: Always carefully check the first and last characters of a wallet address before sending money. Use a hardware wallet and limit transactions on unfamiliar browsers.
⚠️ This is not financial advice.✨
👇
$BTC - Watch for wallet security, strong.
$ETH - Watch for Web3 safety, strong.
$BLESS - Watch for long-term safety habits, strong.
✨𝐅𝐀𝐑𝐙𝐀𝐍𝐀 𝐇𝐀𝐌𝐄𝐄𝐃 𝐎𝐅𝐅𝐈𝐂𝐈𝐀𝐋 • 🦋 ✨
#CryptoSecurity #CyberAttack #Web3Safety #WalletSecurity #BinanceSquare
KYFKON:
JAZAK ALLAH 🌟
6
9
7.3k

·
--
🚨The websites didn't need to be hacked...
#optimjackattackinfectsatleast186websites
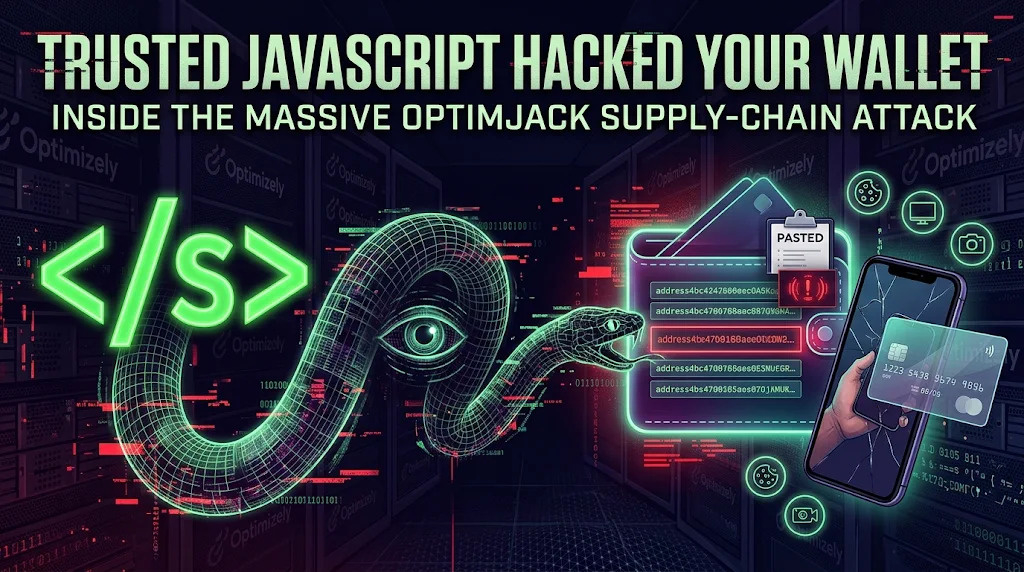
Their trusted JavaScript did the damage.
On November 16, malicious code was served through Optimizely Web snippets to visitors of 178 organisations. Security researcher Scott Helme found 188 infected customer snippets; one scan caught 186 of 1,611 checked. StepSecurity independently reported 186 affected sites on November 17.
The crucial correction: this was not CDN cache poisoning. Attackers inserted code into customers' optional projectJS fields. How they obtained write access across so many unrelated projects remains unexplained.
The payload replaced copied wallet addresses across BTC, ETH/EVM, TRON, Solana, TON and other chains. It also skimmed payment-card details from certain website forms and targeted cookies, screenshots and iOS devices.
Known cryptocurrency receipts were approximately $7,040 in Report URI's November 16 snapshot. StepSecurity's later estimate was around $6,600. These are different investigation snapshots, not amounts to add together.
The bigger damage may extend beyond visible blockchain transactions: stolen payment details, cookies and potential device compromises cannot be measured through on-chain balances.
The real lesson: a secure blockchain cannot protect a transaction when malware silently replaces the address before it reaches the wallet.
Not financial advice.
$BTC $ETH $BNB
{future}(BNBUSDT)
{future}(ETHUSDT)
{future}(BTCUSDT)
#OPTIMJACKAttackInfectsAtLeast186Websites #StablecoinMarketShrinksAtFastestPaceSinceTerraLuna #OptimJack #Web3Security #SupplyChainAttack #StrategySells2.09MMSTRSharesFor$244.7M
🚨The websites didn't need to be hacked...
#optimjackattackinfectsatleast186websites
Their trusted JavaScript did the damage.
On November 16, malicious code was served through Optimizely Web snippets to visitors of 178 organisations. Security researcher Scott Helme found 188 infected customer snippets; one scan caught 186 of 1,611 checked. StepSecurity independently reported 186 affected sites on November 17.
The crucial correction: this was not CDN cache poisoning. Attackers inserted code into customers' optional projectJS fields. How they obtained write access across so many unrelated projects remains unexplained.
The payload replaced copied wallet addresses across BTC, ETH/EVM, TRON, Solana, TON and other chains. It also skimmed payment-card details from certain website forms and targeted cookies, screenshots and iOS devices.
Known cryptocurrency receipts were approximately $7,040 in Report URI's November 16 snapshot. StepSecurity's later estimate was around $6,600. These are different investigation snapshots, not amounts to add together.
The bigger damage may extend beyond visible blockchain transactions: stolen payment details, cookies and potential device compromises cannot be measured through on-chain balances.
The real lesson: a secure blockchain cannot protect a transaction when malware silently replaces the address before it reaches the wallet.
Not financial advice.
$BTC $ETH $BNB
#OPTIMJACKAttackInfectsAtLeast186Websites #StablecoinMarketShrinksAtFastestPaceSinceTerraLuna #OptimJack #Web3Security #SupplyChainAttack #StrategySells2.09MMSTRSharesFor$244.7M
#optimjackattackinfectsatleast186websites
Their trusted JavaScript did the damage.
On November 16, malicious code was served through Optimizely Web snippets to visitors of 178 organisations. Security researcher Scott Helme found 188 infected customer snippets; one scan caught 186 of 1,611 checked. StepSecurity independently reported 186 affected sites on November 17.
The crucial correction: this was not CDN cache poisoning. Attackers inserted code into customers' optional projectJS fields. How they obtained write access across so many unrelated projects remains unexplained.
The payload replaced copied wallet addresses across BTC, ETH/EVM, TRON, Solana, TON and other chains. It also skimmed payment-card details from certain website forms and targeted cookies, screenshots and iOS devices.
Known cryptocurrency receipts were approximately $7,040 in Report URI's November 16 snapshot. StepSecurity's later estimate was around $6,600. These are different investigation snapshots, not amounts to add together.
The bigger damage may extend beyond visible blockchain transactions: stolen payment details, cookies and potential device compromises cannot be measured through on-chain balances.
The real lesson: a secure blockchain cannot protect a transaction when malware silently replaces the address before it reaches the wallet.
Not financial advice.
$BTC $ETH $BNB
#OPTIMJACKAttackInfectsAtLeast186Websites #StablecoinMarketShrinksAtFastestPaceSinceTerraLuna #OptimJack #Web3Security #SupplyChainAttack #StrategySells2.09MMSTRSharesFor$244.7M
2
1.3k
·
--
Article
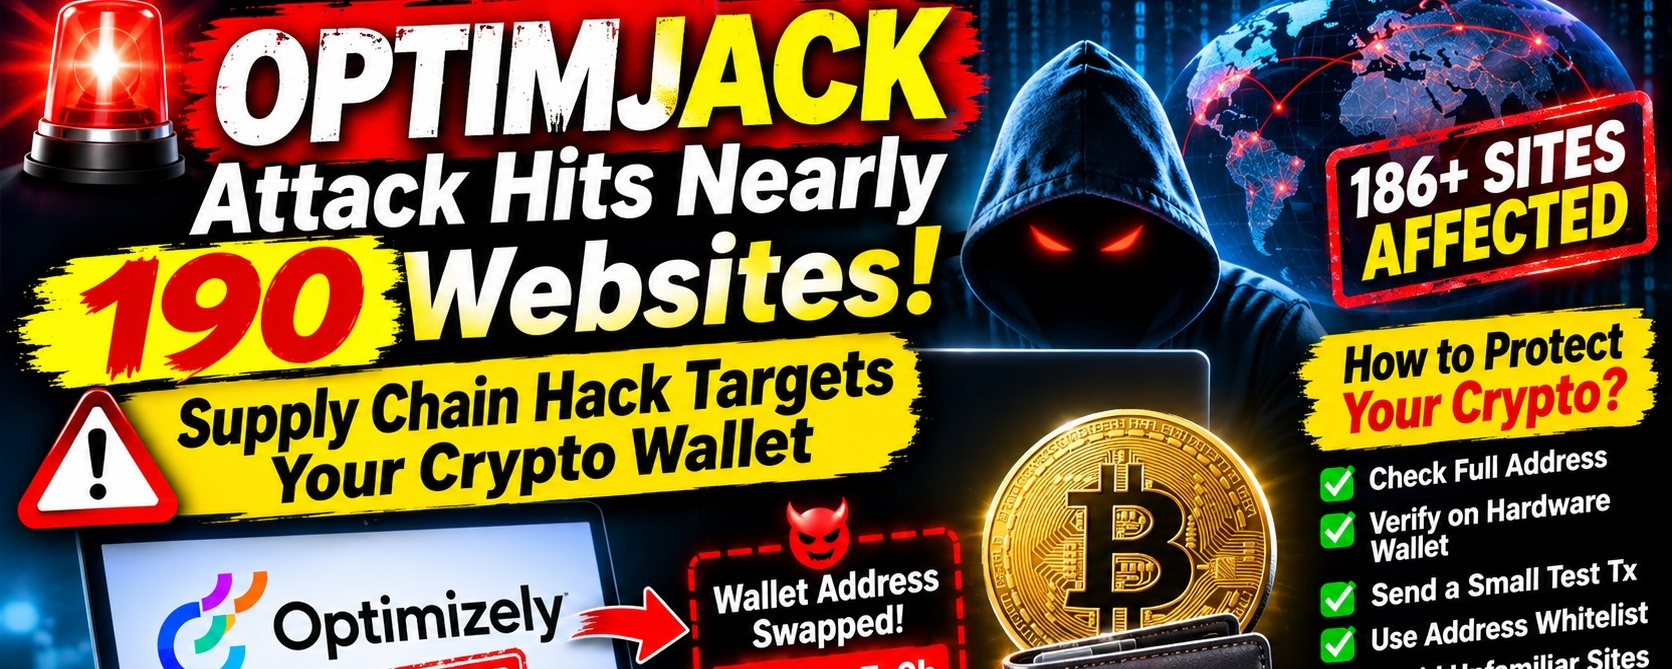
🚨🔓 OPTIMJACK Attack Hits Nearly 190 Websites: How a Supply Chain Hack Targets Your Crypto Wallet#OPTIMJACKAttackInfectsAtLeast186Websites
One of the biggest web security incidents of the year is still unfolding. 😱 A supply chain attack dubbed **OPTIMJACK** reportedly compromised **Optimizely**, an A/B testing platform used by many major websites. Attackers injected malicious JavaScript that can swap crypto wallet addresses and steal payment card data. 🧨 Here is what we know, what we don't, and how to protect yourself. 🛡️
## 🧩 What Happened?
According to reports, attackers injected malicious code into scripts served through Optimizely. 🌐 Security researcher Scott Helme reported **at least 186 infected websites** and warned the attack was still active. Other trackers cite slightly different counts, roughly **178 to 188 sites**, so treat the exact number as a moving target. 📊
- 🕓 The campaign reportedly began around **4:21 a.m. UTC on Monday, November 16, 2026**.
- 🏢 Affected sites reportedly include **CNN, Zoom, Fox News, BBC, Salesforce, GitLab, American Eagle and Hootsuite**. Finance and crypto-related sites such as Ledger, OANDA and IG were also named in some reports.
- 🕵️ The activity was named "OPTIMJACK" by independent researcher Amirul Iman.
## 💀 What Does the Malicious Code Do?
Researchers say the payload was built for theft. 🎯
1. 📋 **Crypto clipper:** When you copy a wallet address, the script can secretly replace it with the attacker's address. If you paste without checking, your funds go to a scammer. 💸
2. 💳 **Card skimming:** It can capture payment card details typed into website forms.
3. 🍪 **Data collection:** Some analysis mentions stolen screenshots and cookies.
4. 📱 **Mobile loaders:** One report says the code also included loaders aimed at Apple devices.
The code reportedly includes checks such as checksum and Luhn validation, which help it recognize real wallet addresses and card numbers. 🧠
## 🔎 How Could This Happen?
Many websites load scripts from third-party vendors for analytics, testing or ads. 🧱 Those scripts run with the same power as the site's own code. If a vendor's script is poisoned, every site that loads it may serve the malware to visitors. That is why it's called a **supply chain attack**. 🔗
Reports say the malicious JavaScript was inserted into Optimizely project files, and one report claims an unauthorized party exploited a weakness in the account signup flow. 🕳️ These details are still being investigated, so treat them as preliminary. 🔬
## 🧪 Why Many Sites Were Exposed
Security testing after the attack found that a strict **Content Security Policy (CSP)** can block this kind of payload. 🛑 But of 256 hosts tested, **68 had no CSP at all, 50 had one that still allowed the attack, and only 24 blocked it**. That shows how rarely this defense is set up correctly. ⚠️
## 🛡️ How to Protect Your Crypto
The viral post gives some good starting advice, but you can do more. 💪
1. 👀 **Check the whole address, not just the first and last characters.** Attackers often generate lookalike addresses that match the start and end. Compare every character, or use a copy of the address you saved safely beforehand.
2. 🔐 **Verify on your hardware wallet screen.** A hardware wallet protects you only if you confirm the destination address shown *on the device itself*, not on the website.
3. 🧪 **Send a small test transaction first** for large transfers. 💵
4. 📒 **Use an address book or whitelist** on exchanges and wallets for trusted addresses.
5. 🚫 **Avoid crypto transactions on unfamiliar sites** or browsers while the campaign is active.
6. 🌐 **Use a clean browser profile.** Disable unneeded extensions and consider a dedicated browser for crypto only.
7. 💳 **Watch your cards.** Review bank statements, and contact your bank if you entered card details on an affected site.
8. 🧹 **Clear cache and update your browser and operating system.**
## 🏢 Advice for Website Owners
- 🧱 Set up a **strict Content Security Policy** and test that it actually blocks unauthorized scripts.
- 🔏 Use **Subresource Integrity (SRI)** where possible.
- 📋 Audit every third-party script and remove ones you don't need.
- 🔑 Lock down vendor accounts with strong authentication and limit who can edit scripts.
- 🕵️ Monitor for unexpected changes in third-party code.
## 🌍 Why This Matters Beyond Crypto
OPTIMJACK is a reminder that **one compromised vendor can affect hundreds of trusted brands at once**. 🏗️ Even careful users can be exposed when a normal, well-known website serves a poisoned script. Crypto users are especially at risk, because blockchain transfers are **irreversible**. Once the money is sent to the wrong address, it is almost impossible to recover. ⛓️
## 🎯 Final Thoughts
The investigation is still ongoing, and numbers and technical details may change as researchers learn more. 🔄 Until the situation is clear, treat every copied wallet address with suspicion and verify it carefully before you send funds. A few extra seconds can save your entire balance. ⏱️💰 Stay alert, stay skeptical and keep your security habits sharp. 🧠🔐
*⚠️
**** #OPTIMJACK #CryptoSecurity #SupplyChainAttack #WalletSecurity #Web3Safety
#A Packed Week of Earnings and Data Tests Markets #AnthropicIPOTestsInvestorAppetiteForAI #NvidiaBoardNotConsideringHuang’sReturnasCEO #WhatInvestmentSignalsDo13FFilingsReveal?
🚨🔓 OPTIMJACK Attack Hits Nearly 190 Websites: How a Supply Chain Hack Targets Your Crypto Wallet
#OPTIMJACKAttackInfectsAtLeast186Websites
One of the biggest web security incidents of the year is still unfolding. 😱 A supply chain attack dubbed **OPTIMJACK** reportedly compromised **Optimizely**, an A/B testing platform used by many major websites. Attackers injected malicious JavaScript that can swap crypto wallet addresses and steal payment card data. 🧨 Here is what we know, what we don't, and how to protect yourself. 🛡️
## 🧩 What Happened?
According to reports, attackers injected malicious code into scripts served through Optimizely. 🌐 Security researcher Scott Helme reported **at least 186 infected websites** and warned the attack was still active. Other trackers cite slightly different counts, roughly **178 to 188 sites**, so treat the exact number as a moving target. 📊
- 🕓 The campaign reportedly began around **4:21 a.m. UTC on Monday, November 16, 2026**.
- 🏢 Affected sites reportedly include **CNN, Zoom, Fox News, BBC, Salesforce, GitLab, American Eagle and Hootsuite**. Finance and crypto-related sites such as Ledger, OANDA and IG were also named in some reports.
- 🕵️ The activity was named "OPTIMJACK" by independent researcher Amirul Iman.
## 💀 What Does the Malicious Code Do?
Researchers say the payload was built for theft. 🎯
1. 📋 **Crypto clipper:** When you copy a wallet address, the script can secretly replace it with the attacker's address. If you paste without checking, your funds go to a scammer. 💸
2. 💳 **Card skimming:** It can capture payment card details typed into website forms.
3. 🍪 **Data collection:** Some analysis mentions stolen screenshots and cookies.
4. 📱 **Mobile loaders:** One report says the code also included loaders aimed at Apple devices.
The code reportedly includes checks such as checksum and Luhn validation, which help it recognize real wallet addresses and card numbers. 🧠
## 🔎 How Could This Happen?
Many websites load scripts from third-party vendors for analytics, testing or ads. 🧱 Those scripts run with the same power as the site's own code. If a vendor's script is poisoned, every site that loads it may serve the malware to visitors. That is why it's called a **supply chain attack**. 🔗
Reports say the malicious JavaScript was inserted into Optimizely project files, and one report claims an unauthorized party exploited a weakness in the account signup flow. 🕳️ These details are still being investigated, so treat them as preliminary. 🔬
## 🧪 Why Many Sites Were Exposed
Security testing after the attack found that a strict **Content Security Policy (CSP)** can block this kind of payload. 🛑 But of 256 hosts tested, **68 had no CSP at all, 50 had one that still allowed the attack, and only 24 blocked it**. That shows how rarely this defense is set up correctly. ⚠️
## 🛡️ How to Protect Your Crypto
The viral post gives some good starting advice, but you can do more. 💪
1. 👀 **Check the whole address, not just the first and last characters.** Attackers often generate lookalike addresses that match the start and end. Compare every character, or use a copy of the address you saved safely beforehand.
2. 🔐 **Verify on your hardware wallet screen.** A hardware wallet protects you only if you confirm the destination address shown *on the device itself*, not on the website.
3. 🧪 **Send a small test transaction first** for large transfers. 💵
4. 📒 **Use an address book or whitelist** on exchanges and wallets for trusted addresses.
5. 🚫 **Avoid crypto transactions on unfamiliar sites** or browsers while the campaign is active.
6. 🌐 **Use a clean browser profile.** Disable unneeded extensions and consider a dedicated browser for crypto only.
7. 💳 **Watch your cards.** Review bank statements, and contact your bank if you entered card details on an affected site.
8. 🧹 **Clear cache and update your browser and operating system.**
## 🏢 Advice for Website Owners
- 🧱 Set up a **strict Content Security Policy** and test that it actually blocks unauthorized scripts.
- 🔏 Use **Subresource Integrity (SRI)** where possible.
- 📋 Audit every third-party script and remove ones you don't need.
- 🔑 Lock down vendor accounts with strong authentication and limit who can edit scripts.
- 🕵️ Monitor for unexpected changes in third-party code.
## 🌍 Why This Matters Beyond Crypto
OPTIMJACK is a reminder that **one compromised vendor can affect hundreds of trusted brands at once**. 🏗️ Even careful users can be exposed when a normal, well-known website serves a poisoned script. Crypto users are especially at risk, because blockchain transfers are **irreversible**. Once the money is sent to the wrong address, it is almost impossible to recover. ⛓️
## 🎯 Final Thoughts
The investigation is still ongoing, and numbers and technical details may change as researchers learn more. 🔄 Until the situation is clear, treat every copied wallet address with suspicion and verify it carefully before you send funds. A few extra seconds can save your entire balance. ⏱️💰 Stay alert, stay skeptical and keep your security habits sharp. 🧠🔐
*⚠️
**** #OPTIMJACK #CryptoSecurity #SupplyChainAttack #WalletSecurity #Web3Safety
#A Packed Week of Earnings and Data Tests Markets #AnthropicIPOTestsInvestorAppetiteForAI #NvidiaBoardNotConsideringHuang’sReturnasCEO #WhatInvestmentSignalsDo13FFilingsReveal?
One of the biggest web security incidents of the year is still unfolding. 😱 A supply chain attack dubbed **OPTIMJACK** reportedly compromised **Optimizely**, an A/B testing platform used by many major websites. Attackers injected malicious JavaScript that can swap crypto wallet addresses and steal payment card data. 🧨 Here is what we know, what we don't, and how to protect yourself. 🛡️
## 🧩 What Happened?
According to reports, attackers injected malicious code into scripts served through Optimizely. 🌐 Security researcher Scott Helme reported **at least 186 infected websites** and warned the attack was still active. Other trackers cite slightly different counts, roughly **178 to 188 sites**, so treat the exact number as a moving target. 📊
- 🕓 The campaign reportedly began around **4:21 a.m. UTC on Monday, November 16, 2026**.
- 🏢 Affected sites reportedly include **CNN, Zoom, Fox News, BBC, Salesforce, GitLab, American Eagle and Hootsuite**. Finance and crypto-related sites such as Ledger, OANDA and IG were also named in some reports.
- 🕵️ The activity was named "OPTIMJACK" by independent researcher Amirul Iman.
## 💀 What Does the Malicious Code Do?
Researchers say the payload was built for theft. 🎯
1. 📋 **Crypto clipper:** When you copy a wallet address, the script can secretly replace it with the attacker's address. If you paste without checking, your funds go to a scammer. 💸
2. 💳 **Card skimming:** It can capture payment card details typed into website forms.
3. 🍪 **Data collection:** Some analysis mentions stolen screenshots and cookies.
4. 📱 **Mobile loaders:** One report says the code also included loaders aimed at Apple devices.
The code reportedly includes checks such as checksum and Luhn validation, which help it recognize real wallet addresses and card numbers. 🧠
## 🔎 How Could This Happen?
Many websites load scripts from third-party vendors for analytics, testing or ads. 🧱 Those scripts run with the same power as the site's own code. If a vendor's script is poisoned, every site that loads it may serve the malware to visitors. That is why it's called a **supply chain attack**. 🔗
Reports say the malicious JavaScript was inserted into Optimizely project files, and one report claims an unauthorized party exploited a weakness in the account signup flow. 🕳️ These details are still being investigated, so treat them as preliminary. 🔬
## 🧪 Why Many Sites Were Exposed
Security testing after the attack found that a strict **Content Security Policy (CSP)** can block this kind of payload. 🛑 But of 256 hosts tested, **68 had no CSP at all, 50 had one that still allowed the attack, and only 24 blocked it**. That shows how rarely this defense is set up correctly. ⚠️
## 🛡️ How to Protect Your Crypto
The viral post gives some good starting advice, but you can do more. 💪
1. 👀 **Check the whole address, not just the first and last characters.** Attackers often generate lookalike addresses that match the start and end. Compare every character, or use a copy of the address you saved safely beforehand.
2. 🔐 **Verify on your hardware wallet screen.** A hardware wallet protects you only if you confirm the destination address shown *on the device itself*, not on the website.
3. 🧪 **Send a small test transaction first** for large transfers. 💵
4. 📒 **Use an address book or whitelist** on exchanges and wallets for trusted addresses.
5. 🚫 **Avoid crypto transactions on unfamiliar sites** or browsers while the campaign is active.
6. 🌐 **Use a clean browser profile.** Disable unneeded extensions and consider a dedicated browser for crypto only.
7. 💳 **Watch your cards.** Review bank statements, and contact your bank if you entered card details on an affected site.
8. 🧹 **Clear cache and update your browser and operating system.**
## 🏢 Advice for Website Owners
- 🧱 Set up a **strict Content Security Policy** and test that it actually blocks unauthorized scripts.
- 🔏 Use **Subresource Integrity (SRI)** where possible.
- 📋 Audit every third-party script and remove ones you don't need.
- 🔑 Lock down vendor accounts with strong authentication and limit who can edit scripts.
- 🕵️ Monitor for unexpected changes in third-party code.
## 🌍 Why This Matters Beyond Crypto
OPTIMJACK is a reminder that **one compromised vendor can affect hundreds of trusted brands at once**. 🏗️ Even careful users can be exposed when a normal, well-known website serves a poisoned script. Crypto users are especially at risk, because blockchain transfers are **irreversible**. Once the money is sent to the wrong address, it is almost impossible to recover. ⛓️
## 🎯 Final Thoughts
The investigation is still ongoing, and numbers and technical details may change as researchers learn more. 🔄 Until the situation is clear, treat every copied wallet address with suspicion and verify it carefully before you send funds. A few extra seconds can save your entire balance. ⏱️💰 Stay alert, stay skeptical and keep your security habits sharp. 🧠🔐
*⚠️
**** #OPTIMJACK #CryptoSecurity #SupplyChainAttack #WalletSecurity #Web3Safety
#A Packed Week of Earnings and Data Tests Markets #AnthropicIPOTestsInvestorAppetiteForAI #NvidiaBoardNotConsideringHuang’sReturnasCEO #WhatInvestmentSignalsDo13FFilingsReveal?
1
4
439

·
--
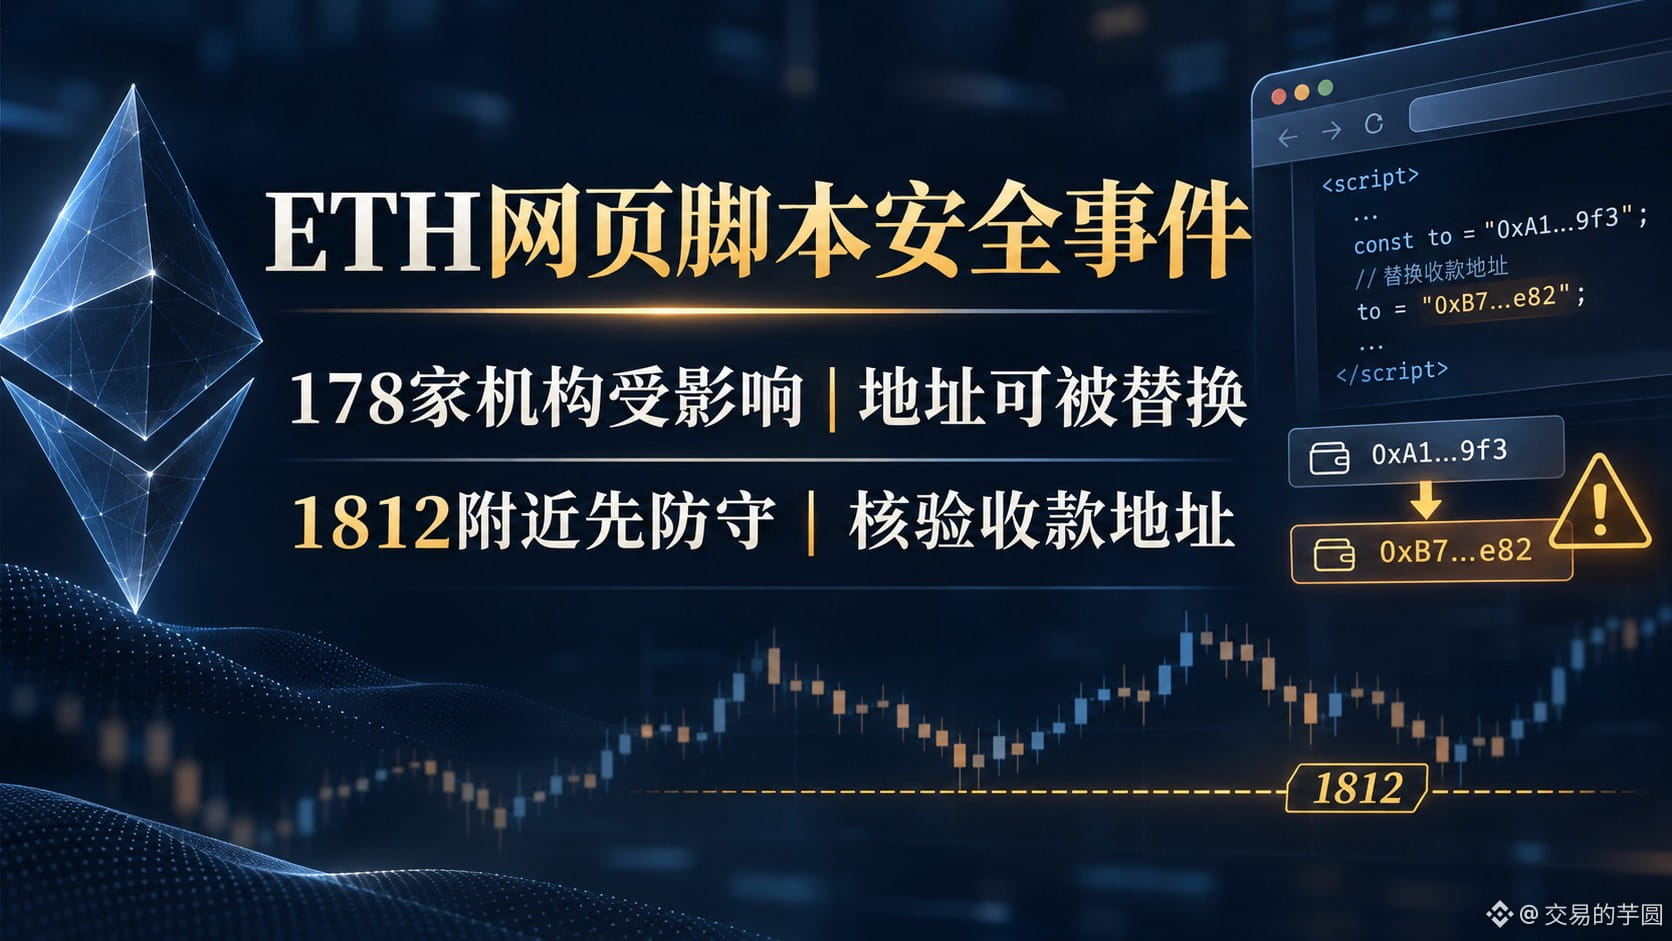
ETH security incident escalates|Third-party scripts can replace payment addresses|Defend first around 1812
My view: This news is primarily about risks in the transfer process, not evidence that the Ethereum blockchain itself has been breached. For now, I won't short ETH just because of security news, but I also won't treat an intraday rebound as proof that the risk has passed. Binance Square is discussing #OPTIMJACKAttackInfectsAtLeast186Websites, a topic title that uses an earlier tally. StepSecurity, a security research firm, updated its findings: on November 16, malicious code appeared in 188 Optimizely web experiment scripts used by 178 organizations. The two figures refer to organizations and scripts respectively; they should not be conflated as “188 websites.”
More importantly, Optimizely’s status page confirms that someone exploited a Web Experimentation vulnerability to add malicious JavaScript to some customer projects. The company says the vulnerability has been fixed, the injected code removed, and the affected accounts secured; the status is currently being monitored. StepSecurity’s independent analysis found that the code could replace valid payment addresses for ETH and other chains with attackers’ addresses while webpages were displayed, copied, or some forms submitted. It could also steal payment card information. StepSecurity listed Ledger and other affected organizations, but “visited these websites” does not mean every user lost funds; actual losses and the number of victims cannot be estimated from webpage exposure figures alone.
The incident affects the crypto market through trust and operational costs: even when copying an address from a seemingly legitimate website, users should verify it character by character on their wallet or hardware device’s confirmation screen. The entry point was the web supply chain, which does not justify inferring that the ETH protocol, mainnet, or all wallets have been compromised. If the relevant service providers disclose more victimized transactions in the short term, industry risk appetite may come under pressure; conversely, confirmation of the fix and no further evidence of victims would lessen the impact. Price-wise, ETH/USDT was around $1,812 at the time of observation, still up about 0.7% over the rolling 24 hours, with a range of 1,787 to 1,867. It has pulled back about $55 from the range high, but this entire move cannot be attributed to this incident. 1,787 is this swing’s low, and 1,800 is a psychological level; to the upside, watch 1,835 first, then 1,867.
If I were trading this myself: I’d stay out for now. The only direction I’d consider is a small spot long; I would absolutely not open a high-leverage short because of a security headline. I’d enter only if ETH regains 1,835 and then holds on a retest, with no further spread of the security incident. I’d use at most 3% of my total capital to open a position; the first target is 1,867, where I’d take half off, then watch whether the remaining position can hold above 1,870. I’d place a stop-loss below 1,815 after entry. If ETH breaks below 1,787 outright or an official update expands the reported scope of affected users, I’d cancel any unfilled order and immediately close any open position. If it merely rebounds to 1,835 and gets pushed back down, I’d remain on the sidelines. First verify the address, then think about position size.
#OPTIMJACKAttackInfectsAtLeast186Websites #ETH
The above is only my personal market observation and does not constitute investment advice.
ETH security incident escalates|Third-party scripts can replace payment addresses|Defend first around 1812
My view: This news is primarily about risks in the transfer process, not evidence that the Ethereum blockchain itself has been breached. For now, I won't short ETH just because of security news, but I also won't treat an intraday rebound as proof that the risk has passed. Binance Square is discussing #OPTIMJACKAttackInfectsAtLeast186Websites, a topic title that uses an earlier tally. StepSecurity, a security research firm, updated its findings: on November 16, malicious code appeared in 188 Optimizely web experiment scripts used by 178 organizations. The two figures refer to organizations and scripts respectively; they should not be conflated as “188 websites.”
More importantly, Optimizely’s status page confirms that someone exploited a Web Experimentation vulnerability to add malicious JavaScript to some customer projects. The company says the vulnerability has been fixed, the injected code removed, and the affected accounts secured; the status is currently being monitored. StepSecurity’s independent analysis found that the code could replace valid payment addresses for ETH and other chains with attackers’ addresses while webpages were displayed, copied, or some forms submitted. It could also steal payment card information. StepSecurity listed Ledger and other affected organizations, but “visited these websites” does not mean every user lost funds; actual losses and the number of victims cannot be estimated from webpage exposure figures alone.
The incident affects the crypto market through trust and operational costs: even when copying an address from a seemingly legitimate website, users should verify it character by character on their wallet or hardware device’s confirmation screen. The entry point was the web supply chain, which does not justify inferring that the ETH protocol, mainnet, or all wallets have been compromised. If the relevant service providers disclose more victimized transactions in the short term, industry risk appetite may come under pressure; conversely, confirmation of the fix and no further evidence of victims would lessen the impact. Price-wise, ETH/USDT was around $1,812 at the time of observation, still up about 0.7% over the rolling 24 hours, with a range of 1,787 to 1,867. It has pulled back about $55 from the range high, but this entire move cannot be attributed to this incident. 1,787 is this swing’s low, and 1,800 is a psychological level; to the upside, watch 1,835 first, then 1,867.
If I were trading this myself: I’d stay out for now. The only direction I’d consider is a small spot long; I would absolutely not open a high-leverage short because of a security headline. I’d enter only if ETH regains 1,835 and then holds on a retest, with no further spread of the security incident. I’d use at most 3% of my total capital to open a position; the first target is 1,867, where I’d take half off, then watch whether the remaining position can hold above 1,870. I’d place a stop-loss below 1,815 after entry. If ETH breaks below 1,787 outright or an official update expands the reported scope of affected users, I’d cancel any unfilled order and immediately close any open position. If it merely rebounds to 1,835 and gets pushed back down, I’d remain on the sidelines. First verify the address, then think about position size.
#OPTIMJACKAttackInfectsAtLeast186Websites #ETH
The above is only my personal market observation and does not constitute investment advice.
My view: This news is primarily about risks in the transfer process, not evidence that the Ethereum blockchain itself has been breached. For now, I won't short ETH just because of security news, but I also won't treat an intraday rebound as proof that the risk has passed. Binance Square is discussing #OPTIMJACKAttackInfectsAtLeast186Websites, a topic title that uses an earlier tally. StepSecurity, a security research firm, updated its findings: on November 16, malicious code appeared in 188 Optimizely web experiment scripts used by 178 organizations. The two figures refer to organizations and scripts respectively; they should not be conflated as “188 websites.”
More importantly, Optimizely’s status page confirms that someone exploited a Web Experimentation vulnerability to add malicious JavaScript to some customer projects. The company says the vulnerability has been fixed, the injected code removed, and the affected accounts secured; the status is currently being monitored. StepSecurity’s independent analysis found that the code could replace valid payment addresses for ETH and other chains with attackers’ addresses while webpages were displayed, copied, or some forms submitted. It could also steal payment card information. StepSecurity listed Ledger and other affected organizations, but “visited these websites” does not mean every user lost funds; actual losses and the number of victims cannot be estimated from webpage exposure figures alone.
The incident affects the crypto market through trust and operational costs: even when copying an address from a seemingly legitimate website, users should verify it character by character on their wallet or hardware device’s confirmation screen. The entry point was the web supply chain, which does not justify inferring that the ETH protocol, mainnet, or all wallets have been compromised. If the relevant service providers disclose more victimized transactions in the short term, industry risk appetite may come under pressure; conversely, confirmation of the fix and no further evidence of victims would lessen the impact. Price-wise, ETH/USDT was around $1,812 at the time of observation, still up about 0.7% over the rolling 24 hours, with a range of 1,787 to 1,867. It has pulled back about $55 from the range high, but this entire move cannot be attributed to this incident. 1,787 is this swing’s low, and 1,800 is a psychological level; to the upside, watch 1,835 first, then 1,867.
If I were trading this myself: I’d stay out for now. The only direction I’d consider is a small spot long; I would absolutely not open a high-leverage short because of a security headline. I’d enter only if ETH regains 1,835 and then holds on a retest, with no further spread of the security incident. I’d use at most 3% of my total capital to open a position; the first target is 1,867, where I’d take half off, then watch whether the remaining position can hold above 1,870. I’d place a stop-loss below 1,815 after entry. If ETH breaks below 1,787 outright or an official update expands the reported scope of affected users, I’d cancel any unfilled order and immediately close any open position. If it merely rebounds to 1,835 and gets pushed back down, I’d remain on the sidelines. First verify the address, then think about position size.
#OPTIMJACKAttackInfectsAtLeast186Websites #ETH
The above is only my personal market observation and does not constitute investment advice.
16

·
--
Bearish
🚨 COPIED YOUR WALLET ADDRESS AND PASTED THE WRONG ONE? 🚨
The #OPTIMJACKAttackInfectsAtLeast186Websites supply chain attack is shaking up the internet after compromising Optimizely and infecting at least 186 major websites, including CNN, Zoom, and BBC!
Detailed analysis: Hackers inject malicious JavaScript code to secretly "swap out" the wallet address in your clipboard. One careless second without double-checking when you paste, and your crypto assets will "vanish" straight into a scammer's pocket!
What should traders do? Always carefully check the first and last characters of a wallet address before sending money. Use a hardware wallet and limit transactions on unfamiliar browsers.
⚠️ This is not financial advice.
👇 Click below to trade and support me:
$BTC
{spot}(BTCUSDT)
$ETH
{spot}(ETHUSDT)
$BLESS
{future}(BLESSUSDT)
#CryptoSecurity #CyberAttack #Web3Safety #WalletSecurity #BinanceSquare #VINHTOCDO
🚨 COPIED YOUR WALLET ADDRESS AND PASTED THE WRONG ONE? 🚨
The #OPTIMJACKAttackInfectsAtLeast186Websites supply chain attack is shaking up the internet after compromising Optimizely and infecting at least 186 major websites, including CNN, Zoom, and BBC!
Detailed analysis: Hackers inject malicious JavaScript code to secretly "swap out" the wallet address in your clipboard. One careless second without double-checking when you paste, and your crypto assets will "vanish" straight into a scammer's pocket!
What should traders do? Always carefully check the first and last characters of a wallet address before sending money. Use a hardware wallet and limit transactions on unfamiliar browsers.
⚠️ This is not financial advice.
👇 Click below to trade and support me:
$BTC
$ETH
$BLESS
#CryptoSecurity #CyberAttack #Web3Safety #WalletSecurity #BinanceSquare #VINHTOCDO
The #OPTIMJACKAttackInfectsAtLeast186Websites supply chain attack is shaking up the internet after compromising Optimizely and infecting at least 186 major websites, including CNN, Zoom, and BBC!
Detailed analysis: Hackers inject malicious JavaScript code to secretly "swap out" the wallet address in your clipboard. One careless second without double-checking when you paste, and your crypto assets will "vanish" straight into a scammer's pocket!
What should traders do? Always carefully check the first and last characters of a wallet address before sending money. Use a hardware wallet and limit transactions on unfamiliar browsers.
⚠️ This is not financial advice.
👇 Click below to trade and support me:
$BTC
$ETH
$BLESS
#CryptoSecurity #CyberAttack #Web3Safety #WalletSecurity #BinanceSquare #VINHTOCDO
Trong_Hatachi:
Vụ mã độc tráo địa chỉ ví qua clipboard nghe đáng sợ thật—kiểm tra kỹ địa chỉ trước khi gửi là thói quen rất đáng giữ. Theo dõi mình nhé, mình cũng follow lại!
5
7
1.4k
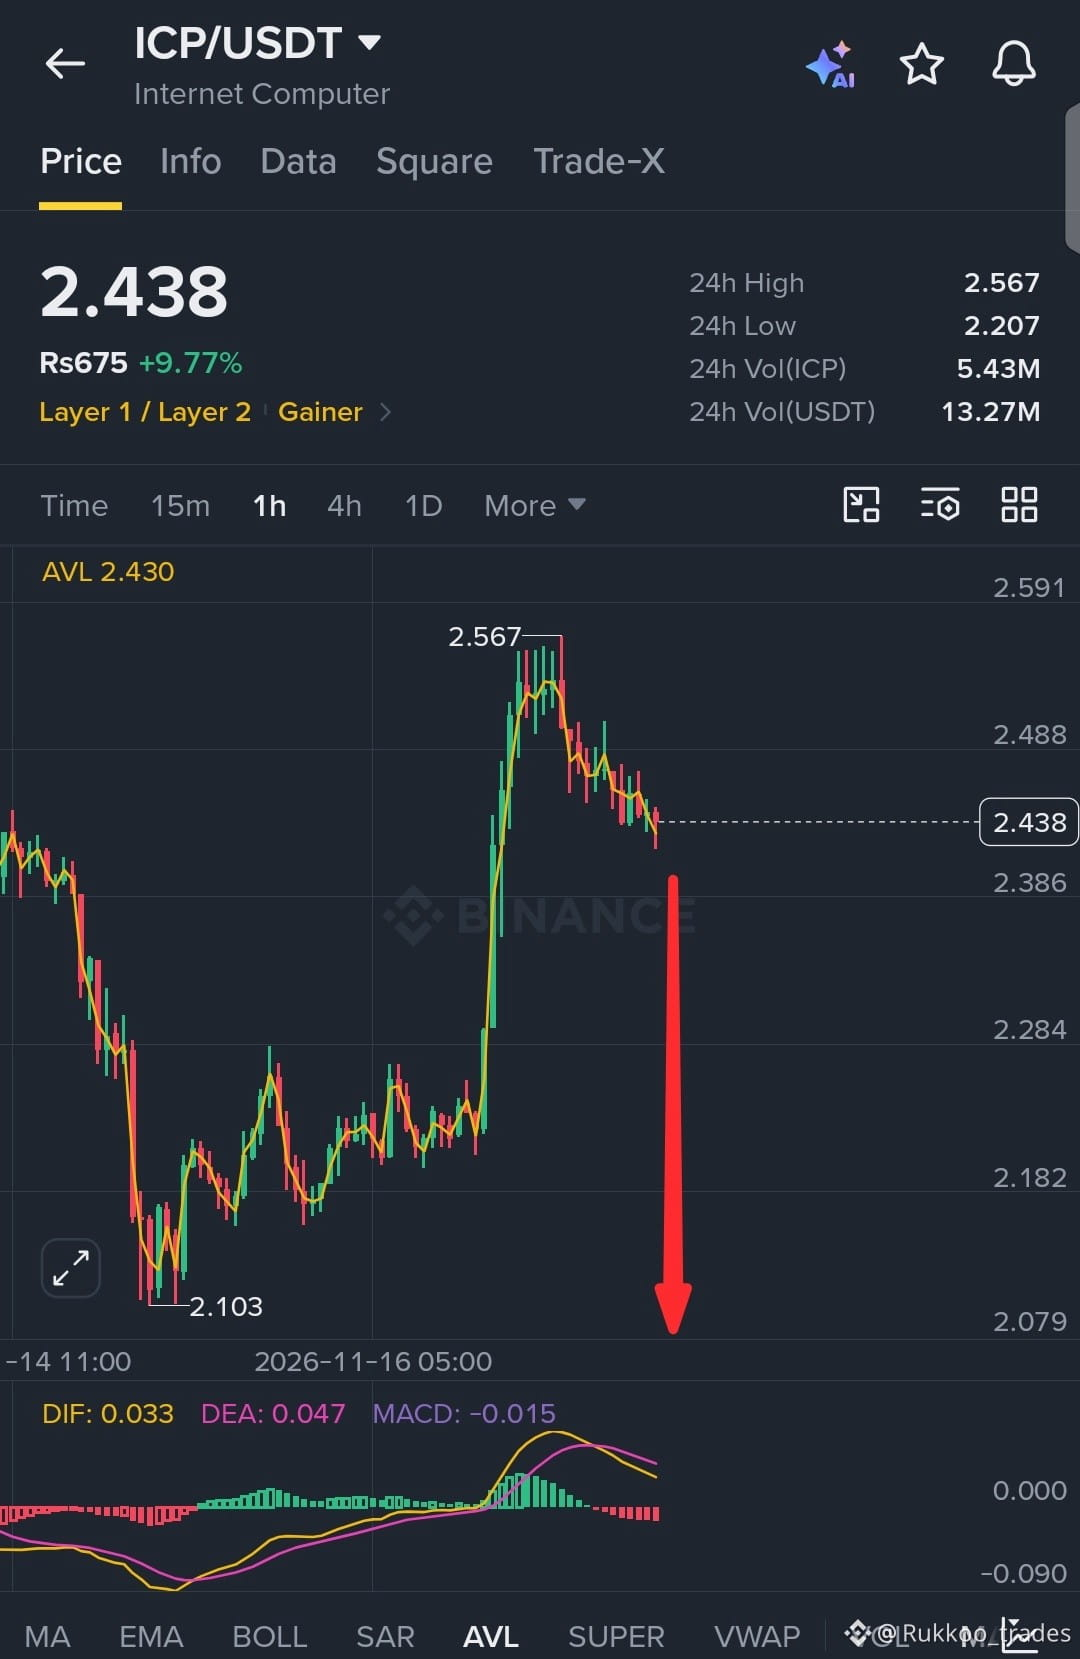
$ICP short setup‼️
I'm taking short on ICP as it is sitting at supply and can dump from here
Entry: 2.433 to 2.436
Targets
2.322
2.255
2.166
2.088
{future}(ICPUSDT)
#AnthropicIPOTestsInvestorAppetiteForAI #NvidiaBoardNotConsideringHuang’sReturnasCEO #InvescoStablecoinReservesFundLaunchesOnEthereum #OPTIMJACKAttackInfectsAtLeast186Websites
$ICP short setup‼️
I'm taking short on ICP as it is sitting at supply and can dump from here
Entry: 2.433 to 2.436
Targets
2.322
2.255
2.166
2.088
#AnthropicIPOTestsInvestorAppetiteForAI #NvidiaBoardNotConsideringHuang’sReturnasCEO #InvescoStablecoinReservesFundLaunchesOnEthereum #OPTIMJACKAttackInfectsAtLeast186Websites
I'm taking short on ICP as it is sitting at supply and can dump from here
Entry: 2.433 to 2.436
Targets
2.322
2.255
2.166
2.088
#AnthropicIPOTestsInvestorAppetiteForAI #NvidiaBoardNotConsideringHuang’sReturnasCEO #InvescoStablecoinReservesFundLaunchesOnEthereum #OPTIMJACKAttackInfectsAtLeast186Websites
Tharindu_Damayantha:
It will pump moree
4
1
790
·
--
Bullish
$SOL , how could you do this to me? Give me my money back, give it back!
#OPTIMJACKAttackInfectsAtLeast186Websites
$SOL , how could you do this to me? Give me my money back, give it back!
#OPTIMJACKAttackInfectsAtLeast186Websites
#OPTIMJACKAttackInfectsAtLeast186Websites
Aakash92:
why everyone was doing entry price from 90
2
329

🚀 $LAB – BIG CHALLENGE
{future}(LABUSDT)
If $LAB doesn't touch $0.10 today, you can unfollow me! 😎
But if it hits $0.10, I want all my followers to help me reach 5K followers! 🔥
And who knows… could $LAB eventually reach $1? 👀🚀
What's your prediction — $0.10 today or not?
⚠️ This is a community challenge, not a guaranteed price prediction. DYOR and manage your risk.#A Packed Week of Earnings and Data Tests Markets #AnthropicIPOTestsInvestorAppetiteForAI #NvidiaBoardNotConsideringHuang’sReturnasCEO #OPTIMJACKAttackInfectsAtLeast186Websites
🚀 $LAB – BIG CHALLENGE
If $LAB doesn't touch $0.10 today, you can unfollow me! 😎
But if it hits $0.10, I want all my followers to help me reach 5K followers! 🔥
And who knows… could $LAB eventually reach $1? 👀🚀
What's your prediction — $0.10 today or not?
⚠️ This is a community challenge, not a guaranteed price prediction. DYOR and manage your risk.#A Packed Week of Earnings and Data Tests Markets #AnthropicIPOTestsInvestorAppetiteForAI #NvidiaBoardNotConsideringHuang’sReturnasCEO #OPTIMJACKAttackInfectsAtLeast186Websites
If $LAB doesn't touch $0.10 today, you can unfollow me! 😎
But if it hits $0.10, I want all my followers to help me reach 5K followers! 🔥
And who knows… could $LAB eventually reach $1? 👀🚀
What's your prediction — $0.10 today or not?
⚠️ This is a community challenge, not a guaranteed price prediction. DYOR and manage your risk.#A Packed Week of Earnings and Data Tests Markets #AnthropicIPOTestsInvestorAppetiteForAI #NvidiaBoardNotConsideringHuang’sReturnasCEO #OPTIMJACKAttackInfectsAtLeast186Websites
4
589
·
--
$EVAA is leading this snapshot with a sharp 43.30% gain at Rs1,027.40. Watch Rs1,000 as near support and Rs1,070–1,100 as resistance. A sustained hold above resistance may extend momentum; losing support risks a cooling pullback. Volume confirmation remains essential.
$SPACE trades at Rs1.08528, up 30.77%, showing strong momentum. The Rs1.05–1.08 area is the first support watch; Rs1.12–1.16 is the next resistance zone. A clean breakout could invite continuation, provided broader market conditions stay supportive.
CROSS is up 22.56% at Rs41.44, with momentum still constructive. Track Rs40 as near support and Rs43–45 as resistance. Acceptance above Rs45 could open a higher leg; failure to defend Rs40 would favour a deeper retest if buyers sustain volume.
$ON has gained 18.42% to Rs29.66, keeping buyers in control for now. Rs28.50–29.00 is the support watch, while Rs31–32 forms near resistance. A decisive close above Rs32 may strengthen the trend; rejection raises pullback risk if breakout volume confirms strength.
#OPTIMJACKAttackInfectsAtLeast186Websites #WhatInvestmentSignalsDo13FFilingsReveal? #AnthropicIPOTestsInvestorAppetiteForA I #StablecoinMarketShrinksAtFastestPaceSinceTerraLuna
{future}(ONUSDT)
{future}(SPACEUSDT)
{future}(EVAAUSDT)
$EVAA is leading this snapshot with a sharp 43.30% gain at Rs1,027.40. Watch Rs1,000 as near support and Rs1,070–1,100 as resistance. A sustained hold above resistance may extend momentum; losing support risks a cooling pullback. Volume confirmation remains essential.
$SPACE trades at Rs1.08528, up 30.77%, showing strong momentum. The Rs1.05–1.08 area is the first support watch; Rs1.12–1.16 is the next resistance zone. A clean breakout could invite continuation, provided broader market conditions stay supportive.
CROSS is up 22.56% at Rs41.44, with momentum still constructive. Track Rs40 as near support and Rs43–45 as resistance. Acceptance above Rs45 could open a higher leg; failure to defend Rs40 would favour a deeper retest if buyers sustain volume.
$ON has gained 18.42% to Rs29.66, keeping buyers in control for now. Rs28.50–29.00 is the support watch, while Rs31–32 forms near resistance. A decisive close above Rs32 may strengthen the trend; rejection raises pullback risk if breakout volume confirms strength.
#OPTIMJACKAttackInfectsAtLeast186Websites #WhatInvestmentSignalsDo13FFilingsReveal? #AnthropicIPOTestsInvestorAppetiteForA I #StablecoinMarketShrinksAtFastestPaceSinceTerraLuna
$SPACE trades at Rs1.08528, up 30.77%, showing strong momentum. The Rs1.05–1.08 area is the first support watch; Rs1.12–1.16 is the next resistance zone. A clean breakout could invite continuation, provided broader market conditions stay supportive.
CROSS is up 22.56% at Rs41.44, with momentum still constructive. Track Rs40 as near support and Rs43–45 as resistance. Acceptance above Rs45 could open a higher leg; failure to defend Rs40 would favour a deeper retest if buyers sustain volume.
$ON has gained 18.42% to Rs29.66, keeping buyers in control for now. Rs28.50–29.00 is the support watch, while Rs31–32 forms near resistance. A decisive close above Rs32 may strengthen the trend; rejection raises pullback risk if breakout volume confirms strength.
#OPTIMJACKAttackInfectsAtLeast186Websites #WhatInvestmentSignalsDo13FFilingsReveal? #AnthropicIPOTestsInvestorAppetiteForA I #StablecoinMarketShrinksAtFastestPaceSinceTerraLuna
$EVAA
57%
$ON
24%
$SPACE
19%
59 votes • Voting closed
5.2k
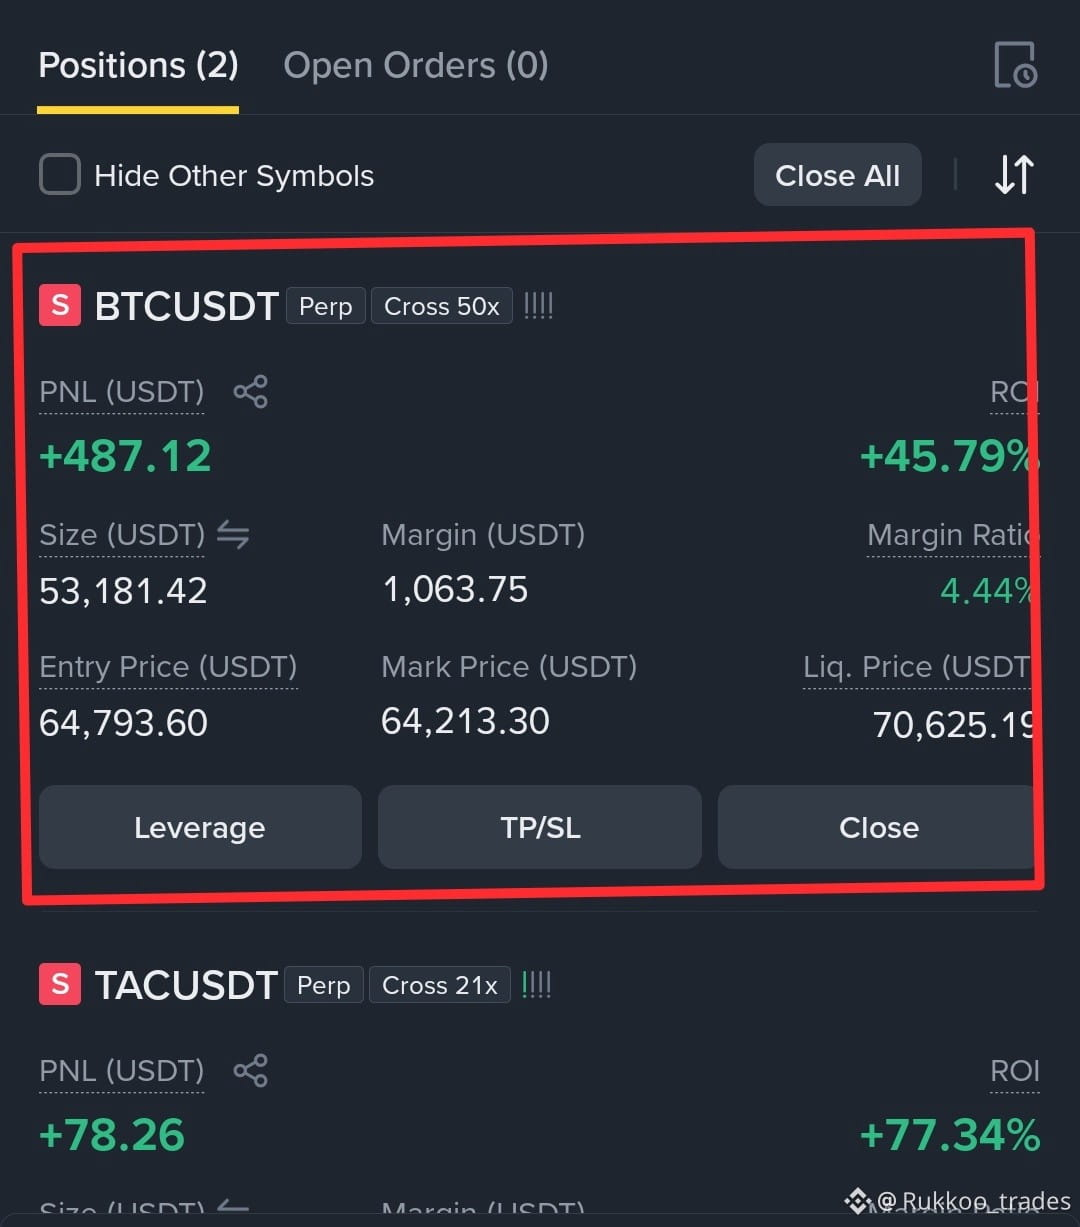
Booooooooooooooom🔥🔥🔥🔥🔥🔥
$BTC dumping exactly as I predicted💥💥💥
Just yesterday told you that BTC will dump and I opened a short position. It was in loss back then and now it's in 500$ profit🔥🔥🔥🔥
Congratulations to those who took this trade ✨✨
{future}(BTCUSDT)
#NvidiaEarningsTonight:AIStocks’NextMove? #AnthropicIPOTestsInvestorAppetiteForAI #WhatInvestmentSignalsDo13FFilingsReveal? #InvescoStablecoinReservesFundLaunchesOnEthereum #OPTIMJACKAttackInfectsAtLeast186Websites
Booooooooooooooom🔥🔥🔥🔥🔥🔥
$BTC dumping exactly as I predicted💥💥💥
Just yesterday told you that BTC will dump and I opened a short position. It was in loss back then and now it's in 500$ profit🔥🔥🔥🔥
Congratulations to those who took this trade ✨✨
#NvidiaEarningsTonight:AIStocks’NextMove? #AnthropicIPOTestsInvestorAppetiteForAI #WhatInvestmentSignalsDo13FFilingsReveal? #InvescoStablecoinReservesFundLaunchesOnEthereum #OPTIMJACKAttackInfectsAtLeast186Websites
$BTC dumping exactly as I predicted💥💥💥
Just yesterday told you that BTC will dump and I opened a short position. It was in loss back then and now it's in 500$ profit🔥🔥🔥🔥
Congratulations to those who took this trade ✨✨
#NvidiaEarningsTonight:AIStocks’NextMove? #AnthropicIPOTestsInvestorAppetiteForAI #WhatInvestmentSignalsDo13FFilingsReveal? #InvescoStablecoinReservesFundLaunchesOnEthereum #OPTIMJACKAttackInfectsAtLeast186Websites
453
·
--
$SIREN
{alpha}(560x997a58129890bbda032231a52ed1ddc845fc18e1)
Social Media Post (X / Binance Square / Telegram)
🚨 $SIREN Market Update & Next Price Targets 🚨
$SIREN is currently consolidating around $0.026 – $0.027 after heavy volatility. While the broader crypto market sits in Extreme Fear, traders are watching key technical levels for the next breakout or breakdown. [1, 2, 3, 4]
📊 Key Levels to Watch:
🟢 Immediate Resistance (Upside Targets): $0.0278 – $0.0285
A clean break and hold above the 50-day moving average opens the door toward $0.0350. [1, 2]
🔴 Key Support (Downside Risk): $0.0241 – $0.0247
Losing this zone could drag price back toward the $0.0208 – $0.0226 range. [1, 2]
⚠️ Keep in Mind:
• AI + Meme Narrative: Upcoming AI trading agent tools remain "coming soon"—actual product launches will be the real catalyst.
• High Concentration: Over 50% of the circulating supply sits in a single custody wallet, meaning whale moves can trigger sharp swings. [1, 2, 3]
#StablecoinMarketShrinksAtFastestPaceSinceTerraLuna #OPTIMJACKAttackInfectsAtLeast186Websites
$SIREN
Social Media Post (X / Binance Square / Telegram)
🚨 $SIREN Market Update & Next Price Targets 🚨
$SIREN is currently consolidating around $0.026 – $0.027 after heavy volatility. While the broader crypto market sits in Extreme Fear, traders are watching key technical levels for the next breakout or breakdown. [1, 2, 3, 4]
📊 Key Levels to Watch:
🟢 Immediate Resistance (Upside Targets): $0.0278 – $0.0285
A clean break and hold above the 50-day moving average opens the door toward $0.0350. [1, 2]
🔴 Key Support (Downside Risk): $0.0241 – $0.0247
Losing this zone could drag price back toward the $0.0208 – $0.0226 range. [1, 2]
⚠️ Keep in Mind:
• AI + Meme Narrative: Upcoming AI trading agent tools remain "coming soon"—actual product launches will be the real catalyst.
• High Concentration: Over 50% of the circulating supply sits in a single custody wallet, meaning whale moves can trigger sharp swings. [1, 2, 3]
#StablecoinMarketShrinksAtFastestPaceSinceTerraLuna #OPTIMJACKAttackInfectsAtLeast186Websites
Social Media Post (X / Binance Square / Telegram)
🚨 $SIREN Market Update & Next Price Targets 🚨
$SIREN is currently consolidating around $0.026 – $0.027 after heavy volatility. While the broader crypto market sits in Extreme Fear, traders are watching key technical levels for the next breakout or breakdown. [1, 2, 3, 4]
📊 Key Levels to Watch:
🟢 Immediate Resistance (Upside Targets): $0.0278 – $0.0285
A clean break and hold above the 50-day moving average opens the door toward $0.0350. [1, 2]
🔴 Key Support (Downside Risk): $0.0241 – $0.0247
Losing this zone could drag price back toward the $0.0208 – $0.0226 range. [1, 2]
⚠️ Keep in Mind:
• AI + Meme Narrative: Upcoming AI trading agent tools remain "coming soon"—actual product launches will be the real catalyst.
• High Concentration: Over 50% of the circulating supply sits in a single custody wallet, meaning whale moves can trigger sharp swings. [1, 2, 3]
#StablecoinMarketShrinksAtFastestPaceSinceTerraLuna #OPTIMJACKAttackInfectsAtLeast186Websites
1
1.2k

·
--
Bearish
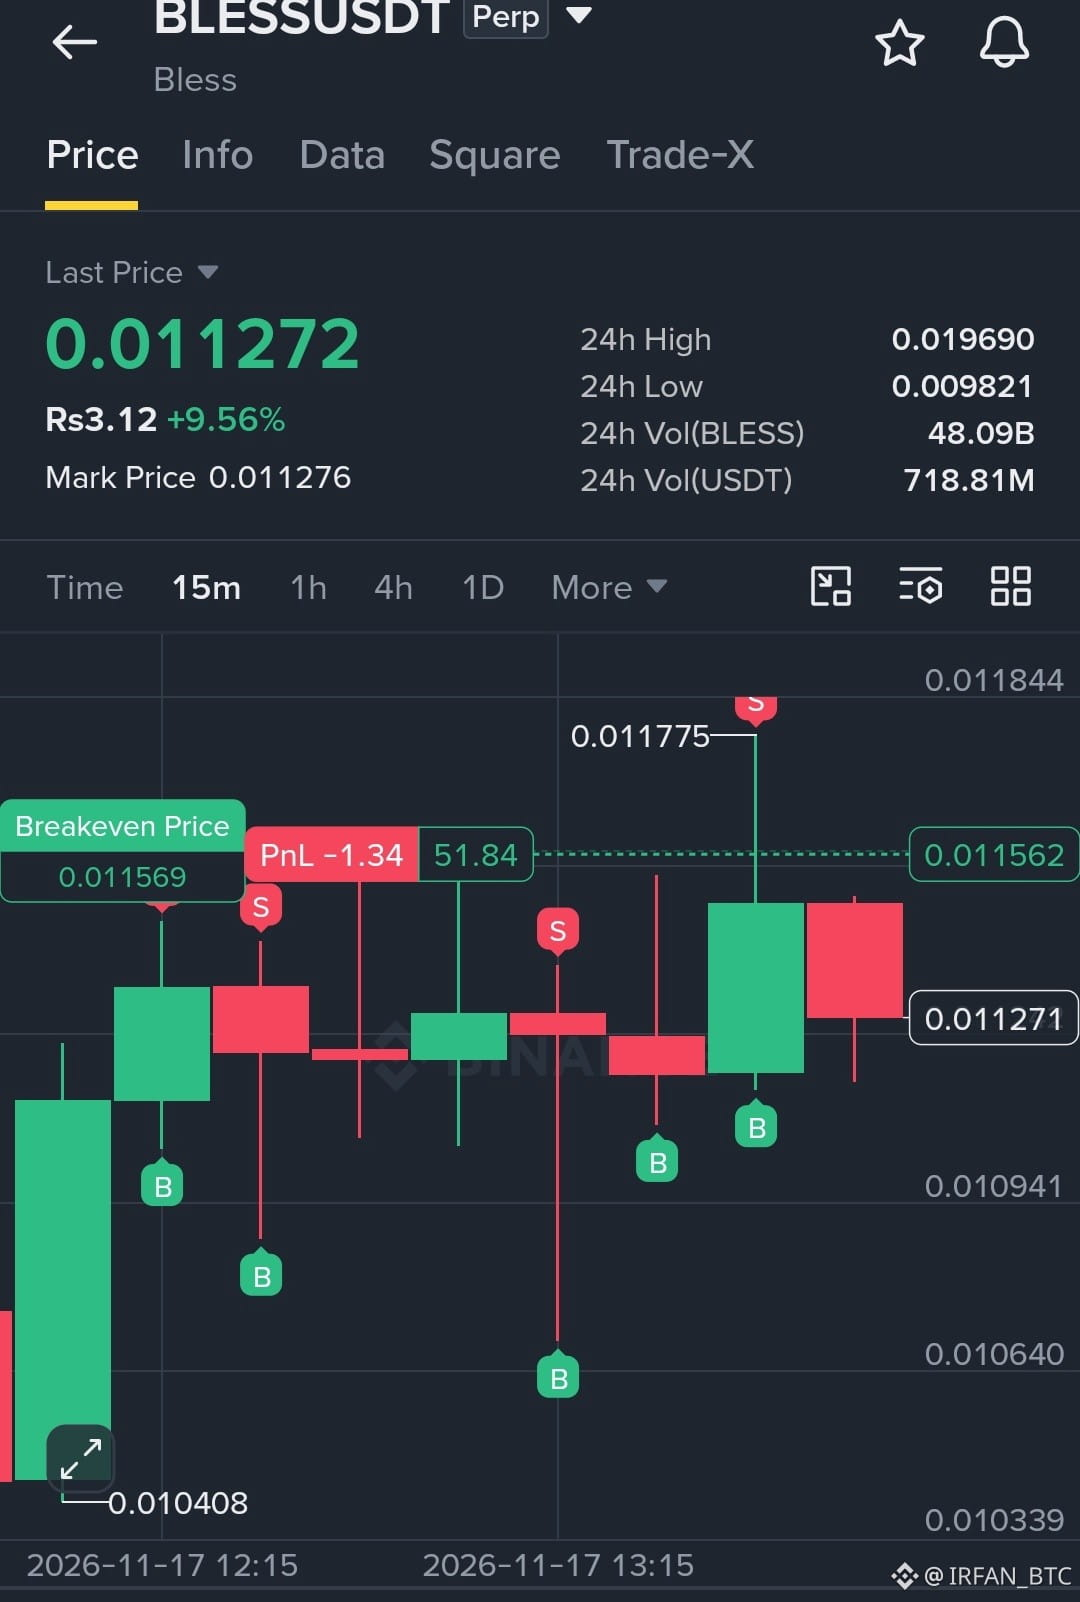
$BLESS is gaining strong bullish momentum, trading at 0.011272 USDT with a 9.56% surge! 24-hour volume has reached 48.09B BLESS, worth 718.81M USDT, while price recently touched 0.019690. Bulls are fighting for control, but volatility remains high. Is BLESS preparing for its next major breakout? DYOR. NFA.
#AnthropicIPOTestsInvestorAppetiteForAI #OPTIMJACKAttackInfectsAtLeast186Websites
$BLESS is gaining strong bullish momentum, trading at 0.011272 USDT with a 9.56% surge! 24-hour volume has reached 48.09B BLESS, worth 718.81M USDT, while price recently touched 0.019690. Bulls are fighting for control, but volatility remains high. Is BLESS preparing for its next major breakout? DYOR. NFA.
#AnthropicIPOTestsInvestorAppetiteForAI #OPTIMJACKAttackInfectsAtLeast186Websites
#AnthropicIPOTestsInvestorAppetiteForAI #OPTIMJACKAttackInfectsAtLeast186Websites
242
·
--
Bullish
$NEAR — Buyers Are Back, But One Important Resistance Stands in Their Way
NEAR is starting to look interesting again. Price has climbed to around $3.254, gaining 1.97%, and the latest move shows buyers coming back with much stronger momentum.
What I like about this setup is the recovery from the lower price levels. NEAR spent quite some time moving sideways before sellers pushed it down toward the $3.12–$3.15 area. Instead of continuing lower, buyers stepped in and gradually took control. The latest candles show a much stronger push toward the $3.286 high.
For me, the next important level is $3.286. This is where I want to see how buyers react. A clean break above it, followed by a successful retest, would make the bullish picture more convincing. If that happens, NEAR could have room to continue its recovery.
I'm also keeping an eye on the downside. The $3.240 area is the first level to watch, while $3.194 is another important support. If price falls back below these areas, the current momentum could start losing strength.
I haven't confirmed any personal entry, so I'm watching this opportunity rather than claiming an active position. I also want to see the 4H and daily charts, along with EMA and MACD confirmation, before making a stronger prediction about the bigger trend.
Overall, I like the way NEAR is recovering, but I don't want to get carried away by a few strong green candles. The real test is whether buyers can break $3.286 and hold above it. That's what I'll be watching next. A confirmed breakout could make things much more interesting for NEAR.
#AnthropicIPOTestsInvestorAppetiteForAI
#WhatInvestmentSignalsDo13FFilingsReveal?
#OPTIMJACKAttackInfectsAtLeast186Websites
#BitcoinExtendsLosingStreakToSixWeeks
$NEAR — Buyers Are Back, But One Important Resistance Stands in Their Way
NEAR is starting to look interesting again. Price has climbed to around $3.254, gaining 1.97%, and the latest move shows buyers coming back with much stronger momentum.
What I like about this setup is the recovery from the lower price levels. NEAR spent quite some time moving sideways before sellers pushed it down toward the $3.12–$3.15 area. Instead of continuing lower, buyers stepped in and gradually took control. The latest candles show a much stronger push toward the $3.286 high.
For me, the next important level is $3.286. This is where I want to see how buyers react. A clean break above it, followed by a successful retest, would make the bullish picture more convincing. If that happens, NEAR could have room to continue its recovery.
I'm also keeping an eye on the downside. The $3.240 area is the first level to watch, while $3.194 is another important support. If price falls back below these areas, the current momentum could start losing strength.
I haven't confirmed any personal entry, so I'm watching this opportunity rather than claiming an active position. I also want to see the 4H and daily charts, along with EMA and MACD confirmation, before making a stronger prediction about the bigger trend.
Overall, I like the way NEAR is recovering, but I don't want to get carried away by a few strong green candles. The real test is whether buyers can break $3.286 and hold above it. That's what I'll be watching next. A confirmed breakout could make things much more interesting for NEAR.
#AnthropicIPOTestsInvestorAppetiteForAI
#WhatInvestmentSignalsDo13FFilingsReveal?
#OPTIMJACKAttackInfectsAtLeast186Websites
#BitcoinExtendsLosingStreakToSixWeeks
NEAR is starting to look interesting again. Price has climbed to around $3.254, gaining 1.97%, and the latest move shows buyers coming back with much stronger momentum.
What I like about this setup is the recovery from the lower price levels. NEAR spent quite some time moving sideways before sellers pushed it down toward the $3.12–$3.15 area. Instead of continuing lower, buyers stepped in and gradually took control. The latest candles show a much stronger push toward the $3.286 high.
For me, the next important level is $3.286. This is where I want to see how buyers react. A clean break above it, followed by a successful retest, would make the bullish picture more convincing. If that happens, NEAR could have room to continue its recovery.
I'm also keeping an eye on the downside. The $3.240 area is the first level to watch, while $3.194 is another important support. If price falls back below these areas, the current momentum could start losing strength.
I haven't confirmed any personal entry, so I'm watching this opportunity rather than claiming an active position. I also want to see the 4H and daily charts, along with EMA and MACD confirmation, before making a stronger prediction about the bigger trend.
Overall, I like the way NEAR is recovering, but I don't want to get carried away by a few strong green candles. The real test is whether buyers can break $3.286 and hold above it. That's what I'll be watching next. A confirmed breakout could make things much more interesting for NEAR.
#AnthropicIPOTestsInvestorAppetiteForAI
#WhatInvestmentSignalsDo13FFilingsReveal?
#OPTIMJACKAttackInfectsAtLeast186Websites
#BitcoinExtendsLosingStreakToSixWeeks
1
488
·
--
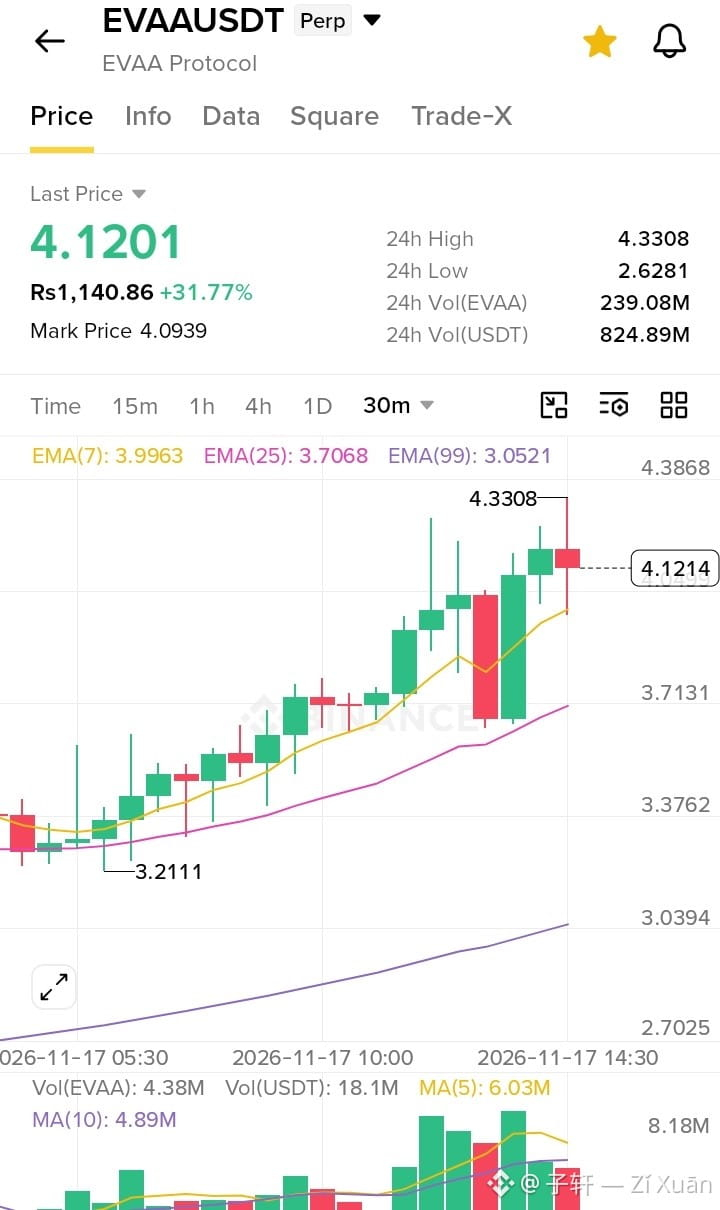
🔥 $EVAA USDT: Bulls Are Pushing Higher!
EVAA is trading at $4.1201, up 31.77%, showing strong buying pressure. Price is above EMA 7 ($3.9963), EMA 25 ($3.7068), and EMA 99 ($3.0521), keeping the short-term trend bullish.
📍 Buy Zone: $3.90–$4.02
🎯 Target 1: $4.20
🎯 Target 2: $4.33
🎯 Target 3: $4.50
🛑 Stop Loss: $3.78
What Next? Watch for a confirmed breakout above $4.33 or a healthy pullback into the buy zone. Avoid chasing sudden green candles. Strong volume is important for continuation. Keep leverage low and manage risk carefully.#OPTIMJACKAttackInfectsAtLeast186Websites #WhatInvestmentSignalsDo13FFilingsReveal? #AnthropicIPOTestsInvestorAppetiteForAI #NvidiaEarningsTonight:AIStocks’NextMove? $EVAA
{future}(EVAAUSDT)
🔥 $EVAA USDT: Bulls Are Pushing Higher!
EVAA is trading at $4.1201, up 31.77%, showing strong buying pressure. Price is above EMA 7 ($3.9963), EMA 25 ($3.7068), and EMA 99 ($3.0521), keeping the short-term trend bullish.
📍 Buy Zone: $3.90–$4.02
🎯 Target 1: $4.20
🎯 Target 2: $4.33
🎯 Target 3: $4.50
🛑 Stop Loss: $3.78
What Next? Watch for a confirmed breakout above $4.33 or a healthy pullback into the buy zone. Avoid chasing sudden green candles. Strong volume is important for continuation. Keep leverage low and manage risk carefully.#OPTIMJACKAttackInfectsAtLeast186Websites #WhatInvestmentSignalsDo13FFilingsReveal? #AnthropicIPOTestsInvestorAppetiteForAI #NvidiaEarningsTonight:AIStocks’NextMove? $EVAA
EVAA is trading at $4.1201, up 31.77%, showing strong buying pressure. Price is above EMA 7 ($3.9963), EMA 25 ($3.7068), and EMA 99 ($3.0521), keeping the short-term trend bullish.
📍 Buy Zone: $3.90–$4.02
🎯 Target 1: $4.20
🎯 Target 2: $4.33
🎯 Target 3: $4.50
🛑 Stop Loss: $3.78
What Next? Watch for a confirmed breakout above $4.33 or a healthy pullback into the buy zone. Avoid chasing sudden green candles. Strong volume is important for continuation. Keep leverage low and manage risk carefully.#OPTIMJACKAttackInfectsAtLeast186Websites #WhatInvestmentSignalsDo13FFilingsReveal? #AnthropicIPOTestsInvestorAppetiteForAI #NvidiaEarningsTonight:AIStocks’NextMove? $EVAA
3
153
Holding $BTC 0.1 USDT
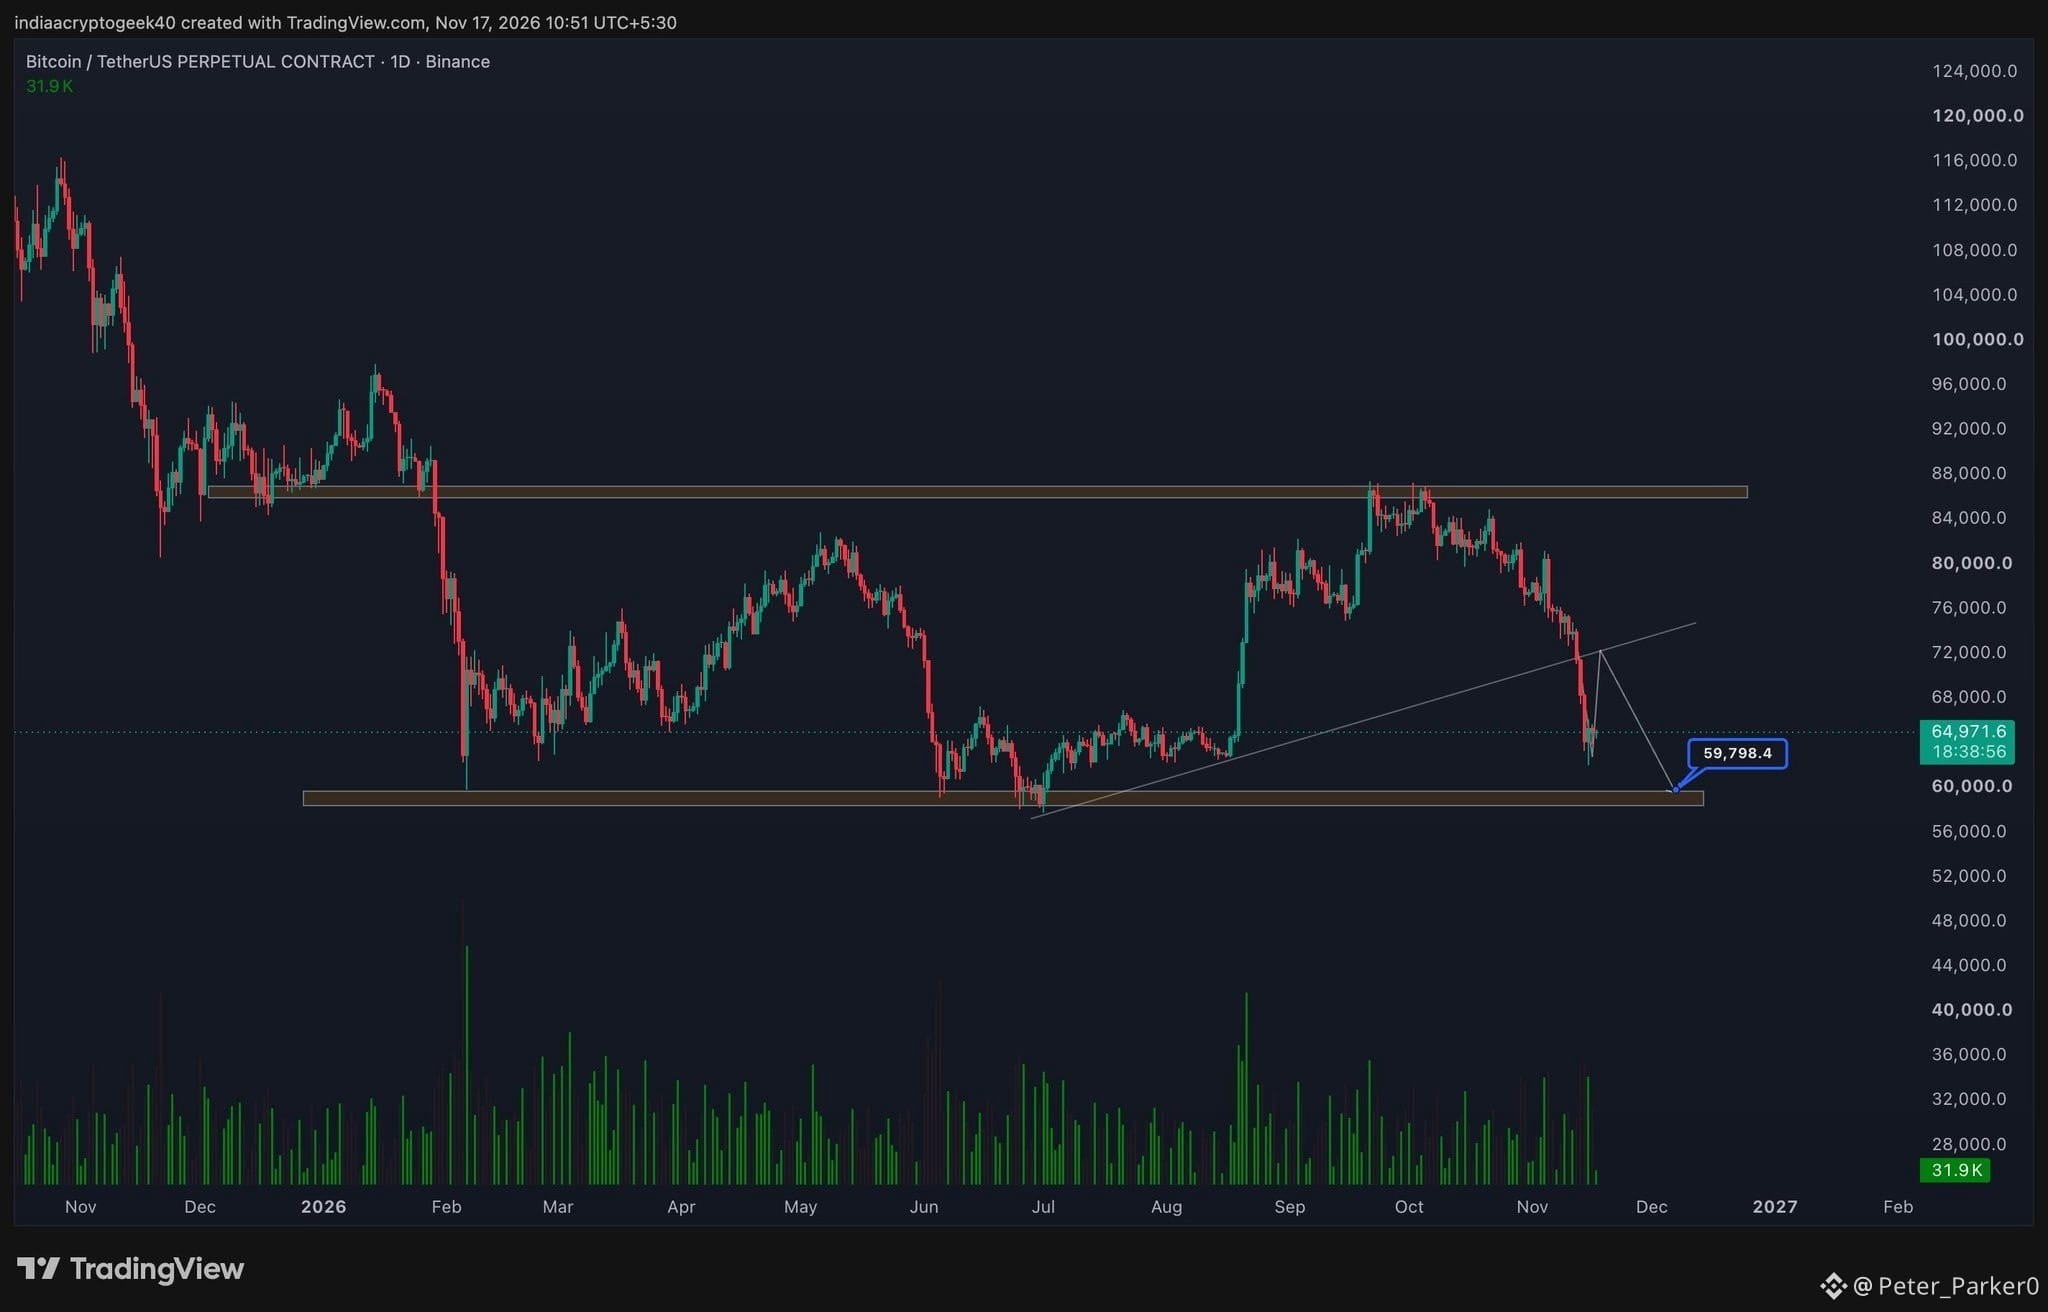
The $60K Magnet: Are We Ready for the Final Shakeout? 🩸📉
The chart doesn't lie, and right now, it’s screaming one word: PATIENCE.
Look at this setup on the Daily. We’ve had a brutal rejection from the $88K supply zone, and the structure is shifting. We broke the ascending trendline (the white diagonal), and the momentum is undeniably heavy.
But here is where it gets interesting for the thrill-seekers. 👇
The Setup:
1. The Liquidity Grab: See that blue arrow? The chart is pointing to a magnet at $59,798. This isn't just a random number; it’s the major support floor (the brown box) that has held us multiple times since early 2026.
2. The Trap: Retail is panicking right now at $64.9K. But the "smart money" play is often a swift wick down to sweep the lows, grab the liquidity sitting under that $60K support, and then reverse.
3. The Volume: Look at the bottom. Volume is starting to spike as we drift lower. That's the fuel.
The Thrill:
This is the moment where weak hands get shaken out and diamond hands get filled. If we hit that $59.8K target and bounce, that is the entry of a lifetime for the next leg up.
The Plan:
· Don't FOMO here. We are mid-air.
· Watch the $60K zone like a hawk. If we wick down to the blue box and immediately buy back up, that’s your confirmation.
· Invalidation: A daily close below $58K and we are looking into the abyss.
Who else is setting their buy orders in the $59K-$60K range? Or are you waiting for the bounce confirmation? 👇💬
$BTC
#NvidiaEarningsTonight:AIStocks’NextMove? #AnthropicIPOTestsInvestorAppetiteForAI #NvidiaBoardNotConsideringHuang’sReturnasCEO #WhatInvestmentSignalsDo13FFilingsReveal? #OPTIMJACKAttackInfectsAtLeast186Websites
The $60K Magnet: Are We Ready for the Final Shakeout? 🩸📉
The chart doesn't lie, and right now, it’s screaming one word: PATIENCE.
Look at this setup on the Daily. We’ve had a brutal rejection from the $88K supply zone, and the structure is shifting. We broke the ascending trendline (the white diagonal), and the momentum is undeniably heavy.
But here is where it gets interesting for the thrill-seekers. 👇
The Setup:
1. The Liquidity Grab: See that blue arrow? The chart is pointing to a magnet at $59,798. This isn't just a random number; it’s the major support floor (the brown box) that has held us multiple times since early 2026.
2. The Trap: Retail is panicking right now at $64.9K. But the "smart money" play is often a swift wick down to sweep the lows, grab the liquidity sitting under that $60K support, and then reverse.
3. The Volume: Look at the bottom. Volume is starting to spike as we drift lower. That's the fuel.
The Thrill:
This is the moment where weak hands get shaken out and diamond hands get filled. If we hit that $59.8K target and bounce, that is the entry of a lifetime for the next leg up.
The Plan:
· Don't FOMO here. We are mid-air.
· Watch the $60K zone like a hawk. If we wick down to the blue box and immediately buy back up, that’s your confirmation.
· Invalidation: A daily close below $58K and we are looking into the abyss.
Who else is setting their buy orders in the $59K-$60K range? Or are you waiting for the bounce confirmation? 👇💬
$BTC
#NvidiaEarningsTonight:AIStocks’NextMove? #AnthropicIPOTestsInvestorAppetiteForAI #NvidiaBoardNotConsideringHuang’sReturnasCEO #WhatInvestmentSignalsDo13FFilingsReveal? #OPTIMJACKAttackInfectsAtLeast186Websites
The chart doesn't lie, and right now, it’s screaming one word: PATIENCE.
Look at this setup on the Daily. We’ve had a brutal rejection from the $88K supply zone, and the structure is shifting. We broke the ascending trendline (the white diagonal), and the momentum is undeniably heavy.
But here is where it gets interesting for the thrill-seekers. 👇
The Setup:
1. The Liquidity Grab: See that blue arrow? The chart is pointing to a magnet at $59,798. This isn't just a random number; it’s the major support floor (the brown box) that has held us multiple times since early 2026.
2. The Trap: Retail is panicking right now at $64.9K. But the "smart money" play is often a swift wick down to sweep the lows, grab the liquidity sitting under that $60K support, and then reverse.
3. The Volume: Look at the bottom. Volume is starting to spike as we drift lower. That's the fuel.
The Thrill:
This is the moment where weak hands get shaken out and diamond hands get filled. If we hit that $59.8K target and bounce, that is the entry of a lifetime for the next leg up.
The Plan:
· Don't FOMO here. We are mid-air.
· Watch the $60K zone like a hawk. If we wick down to the blue box and immediately buy back up, that’s your confirmation.
· Invalidation: A daily close below $58K and we are looking into the abyss.
Who else is setting their buy orders in the $59K-$60K range? Or are you waiting for the bounce confirmation? 👇💬
$BTC
#NvidiaEarningsTonight:AIStocks’NextMove? #AnthropicIPOTestsInvestorAppetiteForAI #NvidiaBoardNotConsideringHuang’sReturnasCEO #WhatInvestmentSignalsDo13FFilingsReveal? #OPTIMJACKAttackInfectsAtLeast186Websites
2
239
·
--
Been watching $EVAA , and one thing caught my attention: the price is moving fast, but there's more to the story than a few green candles.
$EVAA is up 41.11% in the chart, and the short-term moving averages are looking positive. That's definitely interesting to see. But I'm also curious about what comes next.
The project has been working toward expanding its DeFi ecosystem, with plans involving crypto cards, vaults, cross-chain features and AI-powered financial tools.
What I personally want to see is how these developments translate into real usage. More people using the product, more activity and stronger liquidity would mean much more than a temporary price spike.
For now, I'm keeping $EVAA on my radar and watching how things unfold. No need to get carried away by one good chart.
A rising price gets attention, but real users and lasting utility are what give a project something worth believing in.
#EVAA #NvidiaBoardNotConsideringHuang’sReturnasCEO #OPTIMJACKAttackInfectsAtLeast186Websites #WhatInvestmentSignalsDo13FFilingsReveal? #AnthropicIPOTestsInvestorAppetiteForAI #StablecoinMarketShrinksAtFastestPaceSinceTerraLuna
.
{future}(EVAAUSDT)
Been watching $EVAA , and one thing caught my attention: the price is moving fast, but there's more to the story than a few green candles.
$EVAA is up 41.11% in the chart, and the short-term moving averages are looking positive. That's definitely interesting to see. But I'm also curious about what comes next.
The project has been working toward expanding its DeFi ecosystem, with plans involving crypto cards, vaults, cross-chain features and AI-powered financial tools.
What I personally want to see is how these developments translate into real usage. More people using the product, more activity and stronger liquidity would mean much more than a temporary price spike.
For now, I'm keeping $EVAA on my radar and watching how things unfold. No need to get carried away by one good chart.
A rising price gets attention, but real users and lasting utility are what give a project something worth believing in.
#EVAA #NvidiaBoardNotConsideringHuang’sReturnasCEO #OPTIMJACKAttackInfectsAtLeast186Websites #WhatInvestmentSignalsDo13FFilingsReveal? #AnthropicIPOTestsInvestorAppetiteForAI #StablecoinMarketShrinksAtFastestPaceSinceTerraLuna
.
$EVAA is up 41.11% in the chart, and the short-term moving averages are looking positive. That's definitely interesting to see. But I'm also curious about what comes next.
The project has been working toward expanding its DeFi ecosystem, with plans involving crypto cards, vaults, cross-chain features and AI-powered financial tools.
What I personally want to see is how these developments translate into real usage. More people using the product, more activity and stronger liquidity would mean much more than a temporary price spike.
For now, I'm keeping $EVAA on my radar and watching how things unfold. No need to get carried away by one good chart.
A rising price gets attention, but real users and lasting utility are what give a project something worth believing in.
#EVAA #NvidiaBoardNotConsideringHuang’sReturnasCEO #OPTIMJACKAttackInfectsAtLeast186Websites #WhatInvestmentSignalsDo13FFilingsReveal? #AnthropicIPOTestsInvestorAppetiteForAI #StablecoinMarketShrinksAtFastestPaceSinceTerraLuna
.
LONG ♥️.
34%
SHORT 💚.
66%
103 votes • Voting closed
1
3.2k
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#NvidiaBeatsEstimatesWith$130BQ4Outlook
45,637 views
265 Discussing
2
#AnthropicIPOPriceCouldExceed$80
49,331 views
228 Discussing
3
#RussiaCentralBankAddsAlfaBankToCryptoExchangeRegister
2,321 views
38 Discussing
4
#RussianCentralBankPlansToAllowFundsToHoldCryptoIn2027
1,530 views
26 Discussing
5
#VisaPlansStablecoinPrefundingForAPACCrossBorderPayments
2,638 views
31 Discussing
6
#CanNvidia’sDataCenterGrowthContinue?
125,935 views
1,337 Discussing
7
#CanadaAndUSLaunchOperationNiagaraAgainstApprovalPhishing
27,036 views
53 Discussing
8
#BankOfEnglandUnveilsClearingHousePathwayCoveringDLTFirms
3,839 views
64 Discussing
9
#DBSAndCirclePartnerToExpandAsianInstitutionsUSDCAccess
5,011 views
66 Discussing
10
#LedgerHardwareImplantReportsExtendToDubai
71,932 views
739 Discussing