
#blockchainsecurity
blockchainsecurity
644,607 views
1,628 Discussing
Hot
Latest

Here's what happened when a once-promising layer-1 network finally threw in the towel after getting exploited one too many times.
There is nothing worse for an investor than holding bags while watching a chain's underlying infrastructure completely collapse. You back a project believing in its technology, only to realize that persistent security flaws can wipe out years of adoption in a single afternoon.
The downfall of Harmony $ONE is a sobering case study in how cumulative security failures destroy user trust. It started with the 2022 Horizon bridge exploit that drained $100 million, followed by a minting bug in 2023. The final blow came when attackers illegally minted roughly 2.4 trillion unauthorized $ONE tokens, forcing the core team to admit that defending the network was no longer financially sustainable. Rather than fighting an uphill battle, they announced plans to shut down the chain entirely and migrate remaining users to $ETH via a snapshot airdrop.
When you compare this trajectory to resilient networks like $SOL that weathered massive outages and market crashes to rebuild their ecosystem, it highlights how crucial battle-tested code really is. We saw similar bridge-related collapses during the last cycle, but seeing an established layer-1 give up its sovereign chain to become an Ethereum token proves that not every network is built to survive the long game.
Do you think we will see more struggling layer-1 chains abandon their native networks to pivot into Ethereum tokens?
#CryptoAnalysis #Harmony #BlockchainSecurity
Here's what happened when a once-promising layer-1 network finally threw in the towel after getting exploited one too many times.
There is nothing worse for an investor than holding bags while watching a chain's underlying infrastructure completely collapse. You back a project believing in its technology, only to realize that persistent security flaws can wipe out years of adoption in a single afternoon.
The downfall of Harmony $ONE is a sobering case study in how cumulative security failures destroy user trust. It started with the 2022 Horizon bridge exploit that drained $100 million, followed by a minting bug in 2023. The final blow came when attackers illegally minted roughly 2.4 trillion unauthorized $ONE tokens, forcing the core team to admit that defending the network was no longer financially sustainable. Rather than fighting an uphill battle, they announced plans to shut down the chain entirely and migrate remaining users to $ETH via a snapshot airdrop.
When you compare this trajectory to resilient networks like $SOL that weathered massive outages and market crashes to rebuild their ecosystem, it highlights how crucial battle-tested code really is. We saw similar bridge-related collapses during the last cycle, but seeing an established layer-1 give up its sovereign chain to become an Ethereum token proves that not every network is built to survive the long game.
Do you think we will see more struggling layer-1 chains abandon their native networks to pivot into Ethereum tokens?
#CryptoAnalysis #Harmony #BlockchainSecurity
There is nothing worse for an investor than holding bags while watching a chain's underlying infrastructure completely collapse. You back a project believing in its technology, only to realize that persistent security flaws can wipe out years of adoption in a single afternoon.
The downfall of Harmony $ONE is a sobering case study in how cumulative security failures destroy user trust. It started with the 2022 Horizon bridge exploit that drained $100 million, followed by a minting bug in 2023. The final blow came when attackers illegally minted roughly 2.4 trillion unauthorized $ONE tokens, forcing the core team to admit that defending the network was no longer financially sustainable. Rather than fighting an uphill battle, they announced plans to shut down the chain entirely and migrate remaining users to $ETH via a snapshot airdrop.
When you compare this trajectory to resilient networks like $SOL that weathered massive outages and market crashes to rebuild their ecosystem, it highlights how crucial battle-tested code really is. We saw similar bridge-related collapses during the last cycle, but seeing an established layer-1 give up its sovereign chain to become an Ethereum token proves that not every network is built to survive the long game.
Do you think we will see more struggling layer-1 chains abandon their native networks to pivot into Ethereum tokens?
#CryptoAnalysis #Harmony #BlockchainSecurity
347

North Korea drives a surge in on-chain malware; CoinEx shuts down: Asia Express
- A news report says North Korea-linked activities are driving a spike in on-chain malware.
- CoinEx has been reported to be shut down, but the current RSS does not provide the reason, timing, scope, or subsequent arrangements.
- The update touches on on-chain security, exchange operations, and geopolitical risk, which could have potential effects on the crypto market.
- The RSS does not specify the malware types involved, affected assets, the scale of losses, or market reaction.
#BinanceSquare #CryptoNews #BlockchainSecurity
$btc $eth
#vlikevn #Titanbot
Source: CoinTelegraph
North Korea drives a surge in on-chain malware; CoinEx shuts down: Asia Express
- A news report says North Korea-linked activities are driving a spike in on-chain malware.
- CoinEx has been reported to be shut down, but the current RSS does not provide the reason, timing, scope, or subsequent arrangements.
- The update touches on on-chain security, exchange operations, and geopolitical risk, which could have potential effects on the crypto market.
- The RSS does not specify the malware types involved, affected assets, the scale of losses, or market reaction.
#BinanceSquare #CryptoNews #BlockchainSecurity
$btc $eth
#vlikevn #Titanbot
Source: CoinTelegraph
- A news report says North Korea-linked activities are driving a spike in on-chain malware.
- CoinEx has been reported to be shut down, but the current RSS does not provide the reason, timing, scope, or subsequent arrangements.
- The update touches on on-chain security, exchange operations, and geopolitical risk, which could have potential effects on the crypto market.
- The RSS does not specify the malware types involved, affected assets, the scale of losses, or market reaction.
#BinanceSquare #CryptoNews #BlockchainSecurity
$btc $eth
#vlikevn #Titanbot
Source: CoinTelegraph
104
·
--
🚨 $ETC DODGES NETWORK SPLIT AFTER UNAUTHORIZED CLIENT SECURITY BREACH! ⚠️
🚨 Social engineering attacked the $ETC infrastructure through an unreviewed Core-Geth update. Mining pool nodes briefly adopted the unauthorized client before swiftly rolling back to the long-maintained version. 📊
🔍 While block production, fund safety, and chain continuity remained completely intact, the compromised code targeted critical node discovery and consensus mechanics. 💡 Structural risk was neutralized quickly, but client governance remains under the institutional microscope. 💬 Do you view this swift rollback as proof of network resilience or structural vulnerability? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETC #EthereumClassic #Crypto #BlockchainSecurity
🛡️ 🔍
🚨 $ETC DODGES NETWORK SPLIT AFTER UNAUTHORIZED CLIENT SECURITY BREACH! ⚠️
🚨 Social engineering attacked the $ETC infrastructure through an unreviewed Core-Geth update. Mining pool nodes briefly adopted the unauthorized client before swiftly rolling back to the long-maintained version. 📊
🔍 While block production, fund safety, and chain continuity remained completely intact, the compromised code targeted critical node discovery and consensus mechanics. 💡 Structural risk was neutralized quickly, but client governance remains under the institutional microscope. 💬 Do you view this swift rollback as proof of network resilience or structural vulnerability? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETC #EthereumClassic #Crypto #BlockchainSecurity
🛡️ 🔍
🚨 Social engineering attacked the $ETC infrastructure through an unreviewed Core-Geth update. Mining pool nodes briefly adopted the unauthorized client before swiftly rolling back to the long-maintained version. 📊
🔍 While block production, fund safety, and chain continuity remained completely intact, the compromised code targeted critical node discovery and consensus mechanics. 💡 Structural risk was neutralized quickly, but client governance remains under the institutional microscope. 💬 Do you view this swift rollback as proof of network resilience or structural vulnerability? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETC #EthereumClassic #Crypto #BlockchainSecurity
🛡️ 🔍
15
·
--
Article
The Achilles’ Heel of PoS Networks and How Bitcoin Comes to Fix It 🛡️
Hello DeFi & RWA community! 🚀
If we analyze the growth of Proof-of-Stake (PoS) networks and modular application chains, we will come across a recurring technical challenge that is rarely discussed in depth: the cold-start problem of economic security.
Today we’re going to break down why new blockchains struggle to protect themselves at the beginning, and how the world’s largest cryptocurrency is changing the rules of the game.
🧩 1. What is "Cold Start" in Proof-of-Stake Networks?
The Achilles’ Heel of PoS Networks and How Bitcoin Comes to Fix It 🛡️
Hello DeFi & RWA community! 🚀
If we analyze the growth of Proof-of-Stake (PoS) networks and modular application chains, we will come across a recurring technical challenge that is rarely discussed in depth: the cold-start problem of economic security.
Today we’re going to break down why new blockchains struggle to protect themselves at the beginning, and how the world’s largest cryptocurrency is changing the rules of the game.
🧩 1. What is "Cold Start" in Proof-of-Stake Networks?
Hello DeFi & RWA community! 🚀
If we analyze the growth of Proof-of-Stake (PoS) networks and modular application chains, we will come across a recurring technical challenge that is rarely discussed in depth: the cold-start problem of economic security.
Today we’re going to break down why new blockchains struggle to protect themselves at the beginning, and how the world’s largest cryptocurrency is changing the rules of the game.
🧩 1. What is "Cold Start" in Proof-of-Stake Networks?
1
3
109

·
--
Have you noticed how many investors treat blockchain immutability as an absolute guarantee of bug-free perfection?
Most traders panic over temporary price dips or exchange outages, completely ignoring that underlying code vulnerabilities can wipe out an entire ecosystem overnight. We trust ledger finality until a single math error threatens the entire monetary supply.
Back in 2010, the market almost broke before it ever really started. When only about 3.8 million $BTC were in circulation, a single transaction exploited an integer overflow flaw and generated 184.4 billion coins. That was nearly 8,800 times the hard cap that will ever exist.
Satoshi and early developers had to coordinate an emergency fork within hours to roll back the chain and patch the overflow. If an exploit of that scale hit modern giants like $ETH or $BNB today, the panic would liquidate billions across liquidity pools before developers could even push a fix.
Where do you think the market would be today if that bug had gone unnoticed for a week?
#CryptoHistory #Bitcoin #BlockchainSecurity
Have you noticed how many investors treat blockchain immutability as an absolute guarantee of bug-free perfection?
Most traders panic over temporary price dips or exchange outages, completely ignoring that underlying code vulnerabilities can wipe out an entire ecosystem overnight. We trust ledger finality until a single math error threatens the entire monetary supply.
Back in 2010, the market almost broke before it ever really started. When only about 3.8 million $BTC were in circulation, a single transaction exploited an integer overflow flaw and generated 184.4 billion coins. That was nearly 8,800 times the hard cap that will ever exist.
Satoshi and early developers had to coordinate an emergency fork within hours to roll back the chain and patch the overflow. If an exploit of that scale hit modern giants like $ETH or $BNB today, the panic would liquidate billions across liquidity pools before developers could even push a fix.
Where do you think the market would be today if that bug had gone unnoticed for a week?
#CryptoHistory #Bitcoin #BlockchainSecurity
Most traders panic over temporary price dips or exchange outages, completely ignoring that underlying code vulnerabilities can wipe out an entire ecosystem overnight. We trust ledger finality until a single math error threatens the entire monetary supply.
Back in 2010, the market almost broke before it ever really started. When only about 3.8 million $BTC were in circulation, a single transaction exploited an integer overflow flaw and generated 184.4 billion coins. That was nearly 8,800 times the hard cap that will ever exist.
Satoshi and early developers had to coordinate an emergency fork within hours to roll back the chain and patch the overflow. If an exploit of that scale hit modern giants like $ETH or $BNB today, the panic would liquidate billions across liquidity pools before developers could even push a fix.
Where do you think the market would be today if that bug had gone unnoticed for a week?
#CryptoHistory #Bitcoin #BlockchainSecurity
18
·
--
Picture this: back in August 2010, block 74638 slipped onto the ledger, almost breaking the entire promise of hard money before most people even knew what digital assets were.
Most investors worry about bad trades or sudden market crashes, but few stop to consider what happens when the underlying math itself glitches and threatens to render your holdings worthless overnight.
Inside that single transaction, an integer overflow exploit created 184,467,440,737 $BTC out of thin air, completely shattering the strict 21 million supply limit. Satoshi Nakamoto and early developers had to coordinate a quick soft fork within hours, rolling back the chain to overwrite the bad block. If you look at newer ecosystems like $ETH or networks running $SOL, modern smart contract exploits often drain millions permanently, whereas Bitcoin’s core crisis was fixed before the market could even panic.
Where do you think the market would be today if that bug had gone unnoticed for a few days?
#Bitcoin #CryptoHistory #BlockchainSecurity
Picture this: back in August 2010, block 74638 slipped onto the ledger, almost breaking the entire promise of hard money before most people even knew what digital assets were.
Most investors worry about bad trades or sudden market crashes, but few stop to consider what happens when the underlying math itself glitches and threatens to render your holdings worthless overnight.
Inside that single transaction, an integer overflow exploit created 184,467,440,737 $BTC out of thin air, completely shattering the strict 21 million supply limit. Satoshi Nakamoto and early developers had to coordinate a quick soft fork within hours, rolling back the chain to overwrite the bad block. If you look at newer ecosystems like $ETH or networks running $SOL , modern smart contract exploits often drain millions permanently, whereas Bitcoin’s core crisis was fixed before the market could even panic.
Where do you think the market would be today if that bug had gone unnoticed for a few days?
#Bitcoin #CryptoHistory #BlockchainSecurity
Most investors worry about bad trades or sudden market crashes, but few stop to consider what happens when the underlying math itself glitches and threatens to render your holdings worthless overnight.
Inside that single transaction, an integer overflow exploit created 184,467,440,737 $BTC out of thin air, completely shattering the strict 21 million supply limit. Satoshi Nakamoto and early developers had to coordinate a quick soft fork within hours, rolling back the chain to overwrite the bad block. If you look at newer ecosystems like $ETH or networks running $SOL , modern smart contract exploits often drain millions permanently, whereas Bitcoin’s core crisis was fixed before the market could even panic.
Where do you think the market would be today if that bug had gone unnoticed for a few days?
#Bitcoin #CryptoHistory #BlockchainSecurity
17
#bitcointhirdsingleblockreorginfourweeks
ON-CHAIN ALARM BELLS: Bitcoin Suffers A Third Block Reorganization! 🔍
While retail is blindly celebrating the recent breakout, on-chain analysts and node operators are quietly raising serious technical questions tonight.
Data confirms that $BTC has just experienced its third single-block reorganization (reorg) in the last four weeks alone.
Here is the breakdown you need to know:
What is a Reorg? It occurs when two separate miners solve blocks nearly simultaneously, forcing the network to drop one valid block to keep consensus uniform.
The Real Concern: While a single-block reorg is typically a harmless network latency anomaly, witnessing three of them in a tiny 30-day window points directly to mining pool structural shifts or significant block propagation lag.
Your spot portfolio is perfectly safe, but this is a critical structural anomaly that smart money is monitoring with extreme precision.
👇 Do you see this as a minor network latency issue, or an underlying mining pool problem? 👇
#BitcoinNetwork #BlockchainSecurity #OnChainData
#bitcointhirdsingleblockreorginfourweeks
ON-CHAIN ALARM BELLS: Bitcoin Suffers A Third Block Reorganization! 🔍
While retail is blindly celebrating the recent breakout, on-chain analysts and node operators are quietly raising serious technical questions tonight.
Data confirms that $BTC has just experienced its third single-block reorganization (reorg) in the last four weeks alone.
Here is the breakdown you need to know:
What is a Reorg? It occurs when two separate miners solve blocks nearly simultaneously, forcing the network to drop one valid block to keep consensus uniform.
The Real Concern: While a single-block reorg is typically a harmless network latency anomaly, witnessing three of them in a tiny 30-day window points directly to mining pool structural shifts or significant block propagation lag.
Your spot portfolio is perfectly safe, but this is a critical structural anomaly that smart money is monitoring with extreme precision.
👇 Do you see this as a minor network latency issue, or an underlying mining pool problem? 👇
#BitcoinNetwork #BlockchainSecurity #OnChainData
ON-CHAIN ALARM BELLS: Bitcoin Suffers A Third Block Reorganization! 🔍
While retail is blindly celebrating the recent breakout, on-chain analysts and node operators are quietly raising serious technical questions tonight.
Data confirms that $BTC has just experienced its third single-block reorganization (reorg) in the last four weeks alone.
Here is the breakdown you need to know:
What is a Reorg? It occurs when two separate miners solve blocks nearly simultaneously, forcing the network to drop one valid block to keep consensus uniform.
The Real Concern: While a single-block reorg is typically a harmless network latency anomaly, witnessing three of them in a tiny 30-day window points directly to mining pool structural shifts or significant block propagation lag.
Your spot portfolio is perfectly safe, but this is a critical structural anomaly that smart money is monitoring with extreme precision.
👇 Do you see this as a minor network latency issue, or an underlying mining pool problem? 👇
#BitcoinNetwork #BlockchainSecurity #OnChainData
77

·
--
Picture this: you wake up to a screenshot floating around Telegram claiming your personal financial records are being auctioned off until a major fintech app pays up.
For anyone holding crypto, that sinking feeling is all too familiar. A single leaked database can expose user identities, turning your assets into prime targets for targeted phishing and account takeovers.
We saw this dynamic during past hardware wallet breaches, where leaked customer records led to relentless phishing waves aimed at draining $BTC and $ETH holdings. Now, attackers are allegedly threatening to release daily tranches of customer information unless an extortion fee is settled. But before panic sets in, there is a fundamental difference between an unverified hacker claim and a confirmed security compromise.
In crypto risk management, treating attacker claims with healthy skepticism is just as critical as securing your private keys. When similar extortion attempts targeted fiat gateways and platforms trading $BNB in the past, threat actors routinely inflated breach claims to create panic and force quick payouts. Until independent forensic investigations or law enforcement confirm the scope, reacting to unverified ransom claims usually creates unnecessary panic.
How do you separate credible security reports from extortion bluffing when breaking headlines hit your feed?
#CryptoSecurity #DataPrivacy #BlockchainSecurity
Picture this: you wake up to a screenshot floating around Telegram claiming your personal financial records are being auctioned off until a major fintech app pays up.
For anyone holding crypto, that sinking feeling is all too familiar. A single leaked database can expose user identities, turning your assets into prime targets for targeted phishing and account takeovers.
We saw this dynamic during past hardware wallet breaches, where leaked customer records led to relentless phishing waves aimed at draining $BTC and $ETH holdings. Now, attackers are allegedly threatening to release daily tranches of customer information unless an extortion fee is settled. But before panic sets in, there is a fundamental difference between an unverified hacker claim and a confirmed security compromise.
In crypto risk management, treating attacker claims with healthy skepticism is just as critical as securing your private keys. When similar extortion attempts targeted fiat gateways and platforms trading $BNB in the past, threat actors routinely inflated breach claims to create panic and force quick payouts. Until independent forensic investigations or law enforcement confirm the scope, reacting to unverified ransom claims usually creates unnecessary panic.
How do you separate credible security reports from extortion bluffing when breaking headlines hit your feed?
#CryptoSecurity #DataPrivacy #BlockchainSecurity
For anyone holding crypto, that sinking feeling is all too familiar. A single leaked database can expose user identities, turning your assets into prime targets for targeted phishing and account takeovers.
We saw this dynamic during past hardware wallet breaches, where leaked customer records led to relentless phishing waves aimed at draining $BTC and $ETH holdings. Now, attackers are allegedly threatening to release daily tranches of customer information unless an extortion fee is settled. But before panic sets in, there is a fundamental difference between an unverified hacker claim and a confirmed security compromise.
In crypto risk management, treating attacker claims with healthy skepticism is just as critical as securing your private keys. When similar extortion attempts targeted fiat gateways and platforms trading $BNB in the past, threat actors routinely inflated breach claims to create panic and force quick payouts. Until independent forensic investigations or law enforcement confirm the scope, reacting to unverified ransom claims usually creates unnecessary panic.
How do you separate credible security reports from extortion bluffing when breaking headlines hit your feed?
#CryptoSecurity #DataPrivacy #BlockchainSecurity
19
·
--
Shock! Cronos confirms that during the Tectonic vulnerability incident, $9.2 million had already been successfully transferred by hackers before the rollback! Total impacted amount is $120.4 million, with over 7% of funds flowing out. $CRO and $TETIC holders should be alert to short-term downside price risk!#DeFi #BlockchainSecurity
Shock! Cronos confirms that during the Tectonic vulnerability incident, $9.2 million had already been successfully transferred by hackers before the rollback! Total impacted amount is $120.4 million, with over 7% of funds flowing out. $CRO and $TETIC holders should be alert to short-term downside price risk!#DeFi #BlockchainSecurity
5

Crypto researchers cut Bitcoin and Ethereum quantum attack estimate by 50%
A paper shared with CoinDesk shows humans and AI agents beating Google’s March result on a core calculation used by Shor’s algorithm, adding another variable to crypto’s quantum clock.
#BTC $NVDAB
#ETH #CPIWatch
#CryptoNews
#BlockchainSecurity
Crypto researchers cut Bitcoin and Ethereum quantum attack estimate by 50%
A paper shared with CoinDesk shows humans and AI agents beating Google’s March result on a core calculation used by Shor’s algorithm, adding another variable to crypto’s quantum clock.
#BTC $NVDAB
#ETH #CPIWatch
#CryptoNews
#BlockchainSecurity
A paper shared with CoinDesk shows humans and AI agents beating Google’s March result on a core calculation used by Shor’s algorithm, adding another variable to crypto’s quantum clock.
#BTC $NVDAB
#ETH #CPIWatch
#CryptoNews
#BlockchainSecurity

83
·
--
What on earth is quantum computing? This quantum special-issue article explains, in a straightforward way, the difference between quantum computing and traditional computing—along with the potential impact on the cryptocurrency industry. In theory, quantum computers could break the encryption algorithms used by today’s blockchains, posing a potential threat to the security of crypto assets like Bitcoin. But don’t panic— the industry is already developing quantum-resistant solutions! In the long run, projects that are first to achieve quantum resistance could see a significant value revaluation.
$BTC #量子计算 #区块链安全
Quantum computing explained in simple terms! This article breaks down how quantum computing differs from traditional computing and the potential impact on crypto. In theory, quantum computers could crack current blockchain encryption, posing a threat to assets like Bitcoin's security. But don't panic—the industry is already developing quantum-resistant solutions! Projects that first achieve quantum resistance could see significant value revaluation in the long run.
$BTC #QuantumComputing #BlockchainSecurity
What on earth is quantum computing? This quantum special-issue article explains, in a straightforward way, the difference between quantum computing and traditional computing—along with the potential impact on the cryptocurrency industry. In theory, quantum computers could break the encryption algorithms used by today’s blockchains, posing a potential threat to the security of crypto assets like Bitcoin. But don’t panic— the industry is already developing quantum-resistant solutions! In the long run, projects that are first to achieve quantum resistance could see a significant value revaluation.
$BTC #量子计算 #区块链安全
Quantum computing explained in simple terms! This article breaks down how quantum computing differs from traditional computing and the potential impact on crypto. In theory, quantum computers could crack current blockchain encryption, posing a threat to assets like Bitcoin's security. But don't panic—the industry is already developing quantum-resistant solutions! Projects that first achieve quantum resistance could see significant value revaluation in the long run.
$BTC #QuantumComputing #BlockchainSecurity
$BTC #量子计算 #区块链安全
Quantum computing explained in simple terms! This article breaks down how quantum computing differs from traditional computing and the potential impact on crypto. In theory, quantum computers could crack current blockchain encryption, posing a threat to assets like Bitcoin's security. But don't panic—the industry is already developing quantum-resistant solutions! Projects that first achieve quantum resistance could see significant value revaluation in the long run.
$BTC #QuantumComputing #BlockchainSecurity
110


🚨 Spanish Crypto Exchange Bit2Me Takes On Illegal Crypto Activity with Specialized Law Enforcement Unit!
Spanish crypto exchange Bit2Me has officially established a dedicated unit designed specifically to assist global law enforcement agencies in tracking and recovering illicit digital assets.
🔹 Building on Success: Formalizes previous operations that already processed over 1.5 million euros in seized assets in 2025.
🛡️ High-Profile Partners: Working directly alongside major international agencies including Interpol and Europol.
✅ Compliance Focus: Demonstrates growing institutional focus on compliance, transparency, and regulation in European crypto markets.
As regulatory oversight tightens globally, proactive compliance moves by exchanges are setting new security standards across the industry.
$BTC #CryptoNews #BlockchainSecurity #Compliance #Write2Earn
🚨 Spanish Crypto Exchange Bit2Me Takes On Illegal Crypto Activity with Specialized Law Enforcement Unit!
Spanish crypto exchange Bit2Me has officially established a dedicated unit designed specifically to assist global law enforcement agencies in tracking and recovering illicit digital assets.
🔹 Building on Success: Formalizes previous operations that already processed over 1.5 million euros in seized assets in 2025.
🛡️ High-Profile Partners: Working directly alongside major international agencies including Interpol and Europol.
✅ Compliance Focus: Demonstrates growing institutional focus on compliance, transparency, and regulation in European crypto markets.
As regulatory oversight tightens globally, proactive compliance moves by exchanges are setting new security standards across the industry.
$BTC #CryptoNews #BlockchainSecurity #Compliance #Write2Earn
Spanish crypto exchange Bit2Me has officially established a dedicated unit designed specifically to assist global law enforcement agencies in tracking and recovering illicit digital assets.
🔹 Building on Success: Formalizes previous operations that already processed over 1.5 million euros in seized assets in 2025.
🛡️ High-Profile Partners: Working directly alongside major international agencies including Interpol and Europol.
✅ Compliance Focus: Demonstrates growing institutional focus on compliance, transparency, and regulation in European crypto markets.
As regulatory oversight tightens globally, proactive compliance moves by exchanges are setting new security standards across the industry.
$BTC #CryptoNews #BlockchainSecurity #Compliance #Write2Earn
32
🛡️ Ethereum sets sight on quantum-safe future by 2029!
The Ethereum Foundation is accelerating its technical roadmap to prepare the leading smart contract network for the upcoming era of quantum computing.
Key takeaways from the announcement:
🔹 Post-Quantum Security: Core developers are targeting full post-quantum cryptographic protection on Layer-1 by 2029.
🔹 Hegotá Upgrade: The transition kicks off with the Hegotá upgrade, introducing foundational technical updates.
🔹 Core Focus: Initial implementations will prioritize robust account abstraction and enhanced censorship resistance.
🔹 Long-Term Vision: Preparing Ethereum infrastructure well before quantum threats become viable to safeguard user assets.
This proactive roadmap shows Ethereum's commitment to maintaining uncompromised blockchain security for decades to come.
$ETH #Ethereum #QuantumComputing #BlockchainSecurity #Write2Earn
🛡️ Ethereum sets sight on quantum-safe future by 2029!
The Ethereum Foundation is accelerating its technical roadmap to prepare the leading smart contract network for the upcoming era of quantum computing.
Key takeaways from the announcement:
🔹 Post-Quantum Security: Core developers are targeting full post-quantum cryptographic protection on Layer-1 by 2029.
🔹 Hegotá Upgrade: The transition kicks off with the Hegotá upgrade, introducing foundational technical updates.
🔹 Core Focus: Initial implementations will prioritize robust account abstraction and enhanced censorship resistance.
🔹 Long-Term Vision: Preparing Ethereum infrastructure well before quantum threats become viable to safeguard user assets.
This proactive roadmap shows Ethereum's commitment to maintaining uncompromised blockchain security for decades to come.
$ETH #Ethereum #QuantumComputing #BlockchainSecurity #Write2Earn
The Ethereum Foundation is accelerating its technical roadmap to prepare the leading smart contract network for the upcoming era of quantum computing.
Key takeaways from the announcement:
🔹 Post-Quantum Security: Core developers are targeting full post-quantum cryptographic protection on Layer-1 by 2029.
🔹 Hegotá Upgrade: The transition kicks off with the Hegotá upgrade, introducing foundational technical updates.
🔹 Core Focus: Initial implementations will prioritize robust account abstraction and enhanced censorship resistance.
🔹 Long-Term Vision: Preparing Ethereum infrastructure well before quantum threats become viable to safeguard user assets.
This proactive roadmap shows Ethereum's commitment to maintaining uncompromised blockchain security for decades to come.
$ETH #Ethereum #QuantumComputing #BlockchainSecurity #Write2Earn
85
·
--
What should you do if you get hacked? Unplug the network cable—quickly. But unplugging the cable doesn’t mean you get the money back. Just look at these three cases:
After Cronos was hacked, it promptly rolled back, hard-reverting the chain to the state before the hack. The assets literally “came back to life”—a pretty ruthless move.
Ontology acted even faster: before the hacker could even confirm the funds were received, it paused the chain to prevent things from getting worse.
The worst was ICON: by the time it remembered to unplug the line, the coins had already been transferred to the exchange, and the money was already gone after laundering.
In plain terms, “pausing the chain” has never been a magic cure—the key is how far along the hacker got. This also exposes a painful question: what did you actually buy—blockchain technology, or a database that an administrator can pause at any time? Centralized intervention can save you temporarily, but trust will take a hit.
In the short term, security incidents like this tend to weigh negatively on small-cap chains such as $CRO and $ICX. Capital may flow more toward safer havens like BTC. But from another angle, teams that can respond in seconds are better than projects that just go silent after something happens. The project team’s post-incident execution is actually a plus.
For decentralized ideals and security backstops—where do you stand? Let’s discuss in the comments below 👇
$CRO $ICX #BlockchainSecurity #Crypto
What should you do if you get hacked? Unplug the network cable—quickly. But unplugging the cable doesn’t mean you get the money back. Just look at these three cases:
After Cronos was hacked, it promptly rolled back, hard-reverting the chain to the state before the hack. The assets literally “came back to life”—a pretty ruthless move.
Ontology acted even faster: before the hacker could even confirm the funds were received, it paused the chain to prevent things from getting worse.
The worst was ICON: by the time it remembered to unplug the line, the coins had already been transferred to the exchange, and the money was already gone after laundering.
In plain terms, “pausing the chain” has never been a magic cure—the key is how far along the hacker got. This also exposes a painful question: what did you actually buy—blockchain technology, or a database that an administrator can pause at any time? Centralized intervention can save you temporarily, but trust will take a hit.
In the short term, security incidents like this tend to weigh negatively on small-cap chains such as $CRO and $ICX. Capital may flow more toward safer havens like BTC. But from another angle, teams that can respond in seconds are better than projects that just go silent after something happens. The project team’s post-incident execution is actually a plus.
For decentralized ideals and security backstops—where do you stand? Let’s discuss in the comments below 👇
$CRO $ICX #BlockchainSecurity #Crypto
After Cronos was hacked, it promptly rolled back, hard-reverting the chain to the state before the hack. The assets literally “came back to life”—a pretty ruthless move.
Ontology acted even faster: before the hacker could even confirm the funds were received, it paused the chain to prevent things from getting worse.
The worst was ICON: by the time it remembered to unplug the line, the coins had already been transferred to the exchange, and the money was already gone after laundering.
In plain terms, “pausing the chain” has never been a magic cure—the key is how far along the hacker got. This also exposes a painful question: what did you actually buy—blockchain technology, or a database that an administrator can pause at any time? Centralized intervention can save you temporarily, but trust will take a hit.
In the short term, security incidents like this tend to weigh negatively on small-cap chains such as $CRO and $ICX. Capital may flow more toward safer havens like BTC. But from another angle, teams that can respond in seconds are better than projects that just go silent after something happens. The project team’s post-incident execution is actually a plus.
For decentralized ideals and security backstops—where do you stand? Let’s discuss in the comments below 👇
$CRO $ICX #BlockchainSecurity #Crypto
66
When Blockchain Security Gets Tested 🔐⛓️A blockchain isn’t truly secure just because transactions are recorded permanently.
Real security comes from decentralization, strong consensus, network participation, and resistance to attacks.
When a blockchain faces a major network issue, it raises an important question:
How resilient is the chain when consensus is under pressure?
Blockchain technology is powerful—but understanding its risks is just as important as understanding its potential.
Read more about what makes a blockchain truly secure. 🚀
#Blockchain #Crypto #Binance #Web3 #Bitcoin #Cryptocurrency #DeFi #BlockchainSecurity
When Blockchain Security Gets Tested 🔐⛓️
A blockchain isn’t truly secure just because transactions are recorded permanently.
Real security comes from decentralization, strong consensus, network participation, and resistance to attacks.
When a blockchain faces a major network issue, it raises an important question:
How resilient is the chain when consensus is under pressure?
Blockchain technology is powerful—but understanding its risks is just as important as understanding its potential.
Read more about what makes a blockchain truly secure. 🚀
#Blockchain #Crypto #Binance #Web3 #Bitcoin #Cryptocurrency #DeFi #BlockchainSecurity
Real security comes from decentralization, strong consensus, network participation, and resistance to attacks.
When a blockchain faces a major network issue, it raises an important question:
How resilient is the chain when consensus is under pressure?
Blockchain technology is powerful—but understanding its risks is just as important as understanding its potential.
Read more about what makes a blockchain truly secure. 🚀
#Blockchain #Crypto #Binance #Web3 #Bitcoin #Cryptocurrency #DeFi #BlockchainSecurity
83
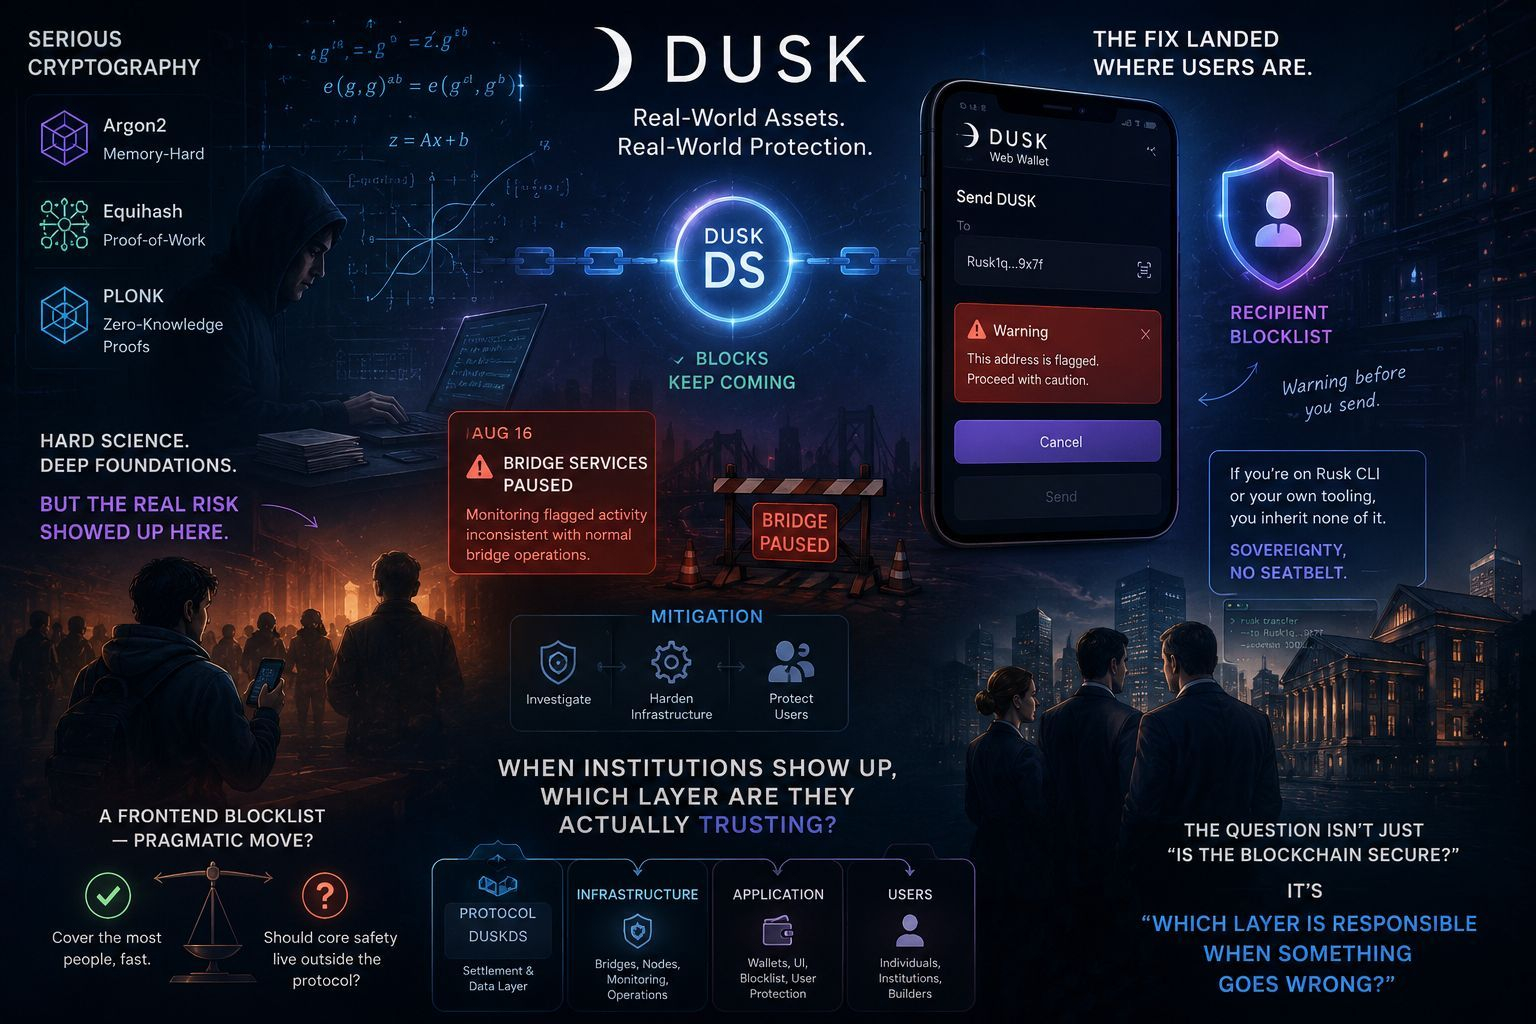
🛡️ $DUSK DEMONSTRATES INSTITUTIONAL MATURITY IN REAL-WORLD SECURITY BATTLES! 💥
While everyone hypes ZK proofs and heavy math, $DUSK just proved what institutions actually care about during real market stress. 🔍 When suspicious activity hit their bridge, the core chain kept humming while rapid defense layers locked down the Web Wallet.
Smart money knows that institutional capital demands clear accountability across protocol, infrastructure, and wallet layers when real size moves on-chain. 🛡️ Crisp operational execution matters far more to big allocators than theoretical code.
🤔 Should security be baked strictly into the protocol level, or is this multi-layer defense the real blueprint for institutional adoption? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #DUSK #Crypto #RWA #BlockchainSecurity
💎 ⚡
🛡️ $DUSK DEMONSTRATES INSTITUTIONAL MATURITY IN REAL-WORLD SECURITY BATTLES! 💥
While everyone hypes ZK proofs and heavy math, $DUSK just proved what institutions actually care about during real market stress. 🔍 When suspicious activity hit their bridge, the core chain kept humming while rapid defense layers locked down the Web Wallet.
Smart money knows that institutional capital demands clear accountability across protocol, infrastructure, and wallet layers when real size moves on-chain. 🛡️ Crisp operational execution matters far more to big allocators than theoretical code.
🤔 Should security be baked strictly into the protocol level, or is this multi-layer defense the real blueprint for institutional adoption? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #DUSK #Crypto #RWA #BlockchainSecurity
💎 ⚡
While everyone hypes ZK proofs and heavy math, $DUSK just proved what institutions actually care about during real market stress. 🔍 When suspicious activity hit their bridge, the core chain kept humming while rapid defense layers locked down the Web Wallet.
Smart money knows that institutional capital demands clear accountability across protocol, infrastructure, and wallet layers when real size moves on-chain. 🛡️ Crisp operational execution matters far more to big allocators than theoretical code.
🤔 Should security be baked strictly into the protocol level, or is this multi-layer defense the real blueprint for institutional adoption? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #DUSK #Crypto #RWA #BlockchainSecurity
💎 ⚡
15
·
--
$ADA FOUNDER DEMANDING ACCOUNTABILITY AFTER MAJOR SECURITY BREACH 🛡️
The ecosystem is watching closely as Charles Hoskinson pushes for full transparency regarding the SecondFi hack. He is insisting on an independent third-party audit to verify the vulnerabilities and restore user trust.
This level of oversight is a double-edged sword for the project. While the pressure for accountability is necessary, any failure to comply could damage the reputation of the broader ecosystem. Investors are waiting to see if the team steps up or remains silent.
Do you think SecondFi will meet this demand or continue to evade responsibility?
Not financial advice. Always manage your risk.
#ADA #Cardano #CryptoNews #BlockchainSecurity
🎯
$ADA FOUNDER DEMANDING ACCOUNTABILITY AFTER MAJOR SECURITY BREACH 🛡️
The ecosystem is watching closely as Charles Hoskinson pushes for full transparency regarding the SecondFi hack. He is insisting on an independent third-party audit to verify the vulnerabilities and restore user trust.
This level of oversight is a double-edged sword for the project. While the pressure for accountability is necessary, any failure to comply could damage the reputation of the broader ecosystem. Investors are waiting to see if the team steps up or remains silent.
Do you think SecondFi will meet this demand or continue to evade responsibility?
Not financial advice. Always manage your risk.
#ADA #Cardano #CryptoNews #BlockchainSecurity
🎯
The ecosystem is watching closely as Charles Hoskinson pushes for full transparency regarding the SecondFi hack. He is insisting on an independent third-party audit to verify the vulnerabilities and restore user trust.
This level of oversight is a double-edged sword for the project. While the pressure for accountability is necessary, any failure to comply could damage the reputation of the broader ecosystem. Investors are waiting to see if the team steps up or remains silent.
Do you think SecondFi will meet this demand or continue to evade responsibility?
Not financial advice. Always manage your risk.
#ADA #Cardano #CryptoNews #BlockchainSecurity
🎯
69
·
--
$ALPHA BRIDGE HIT IN 7-MINUTE DRAIN 🚨
Alephium’s TokenBridge lost roughly $815K after attackers forced forged messages through an off-chain backend flaw across $ETH and BNB Chain. The team says guardian keys were not stolen, the bridge is halted, and affected users are set for a recovery path.
Fast drain. Fake wrapped supply. Bridge risk just got louder.
Attackers minted 13.76M unbacked wrapped $ALPH, exceeding the prior wrapped supply. Funds were reported unmoved at disclosure, with a full postmortem expected this week.
Not financial advice. Manage your risk.
#Crypto #DeFi #BlockchainSecurity #Altcoins #web
⚡
{future}(ETHUSDT)
$ALPHA BRIDGE HIT IN 7-MINUTE DRAIN 🚨
Alephium’s TokenBridge lost roughly $815K after attackers forced forged messages through an off-chain backend flaw across $ETH and BNB Chain. The team says guardian keys were not stolen, the bridge is halted, and affected users are set for a recovery path.
Fast drain. Fake wrapped supply. Bridge risk just got louder.
Attackers minted 13.76M unbacked wrapped $ALPH, exceeding the prior wrapped supply. Funds were reported unmoved at disclosure, with a full postmortem expected this week.
Not financial advice. Manage your risk.
#Crypto #DeFi #BlockchainSecurity #Altcoins #web
⚡
Alephium’s TokenBridge lost roughly $815K after attackers forced forged messages through an off-chain backend flaw across $ETH and BNB Chain. The team says guardian keys were not stolen, the bridge is halted, and affected users are set for a recovery path.
Fast drain. Fake wrapped supply. Bridge risk just got louder.
Attackers minted 13.76M unbacked wrapped $ALPH, exceeding the prior wrapped supply. Funds were reported unmoved at disclosure, with a full postmortem expected this week.
Not financial advice. Manage your risk.
#Crypto #DeFi #BlockchainSecurity #Altcoins #web
⚡
31
🚨 BREAKING !!!
SUI BLOCKCHAIN GOES DOWN 3 TIMES IN A ROW DUE TO ISSUES IN UPGRADE V1.72 🔴
Three mainnet outages occurred on Thursday and Friday, stemming from two separate bugs introduced in upgrade v1.72 ⚠️
The first two outages were due to gas fee calculation errors related to the "address balances" feature; an emergency fix was rolled out but it itself carried a low probability of causing another network halt, leading to the third outage 🛠
The third outage happened when validators restarted and encountered latent issues in the network's random setup preservation mechanism 📊
Sui Foundation confirms: the bugs have been patched, no user funds were at risk, and no transactions were rolled back. The network has also implemented a mechanism to force-close stalled epochs to prevent future occurrences.
#Sui #BlockchainSecurity
$SUI $ETH $PORTAL
🚨 BREAKING !!!
SUI BLOCKCHAIN GOES DOWN 3 TIMES IN A ROW DUE TO ISSUES IN UPGRADE V1.72 🔴
Three mainnet outages occurred on Thursday and Friday, stemming from two separate bugs introduced in upgrade v1.72 ⚠️
The first two outages were due to gas fee calculation errors related to the "address balances" feature; an emergency fix was rolled out but it itself carried a low probability of causing another network halt, leading to the third outage 🛠
The third outage happened when validators restarted and encountered latent issues in the network's random setup preservation mechanism 📊
Sui Foundation confirms: the bugs have been patched, no user funds were at risk, and no transactions were rolled back. The network has also implemented a mechanism to force-close stalled epochs to prevent future occurrences.
#Sui #BlockchainSecurity
$SUI $ETH $PORTAL
SUI BLOCKCHAIN GOES DOWN 3 TIMES IN A ROW DUE TO ISSUES IN UPGRADE V1.72 🔴
Three mainnet outages occurred on Thursday and Friday, stemming from two separate bugs introduced in upgrade v1.72 ⚠️
The first two outages were due to gas fee calculation errors related to the "address balances" feature; an emergency fix was rolled out but it itself carried a low probability of causing another network halt, leading to the third outage 🛠
The third outage happened when validators restarted and encountered latent issues in the network's random setup preservation mechanism 📊
Sui Foundation confirms: the bugs have been patched, no user funds were at risk, and no transactions were rolled back. The network has also implemented a mechanism to force-close stalled epochs to prevent future occurrences.
#Sui #BlockchainSecurity
$SUI $ETH $PORTAL
430
·
--
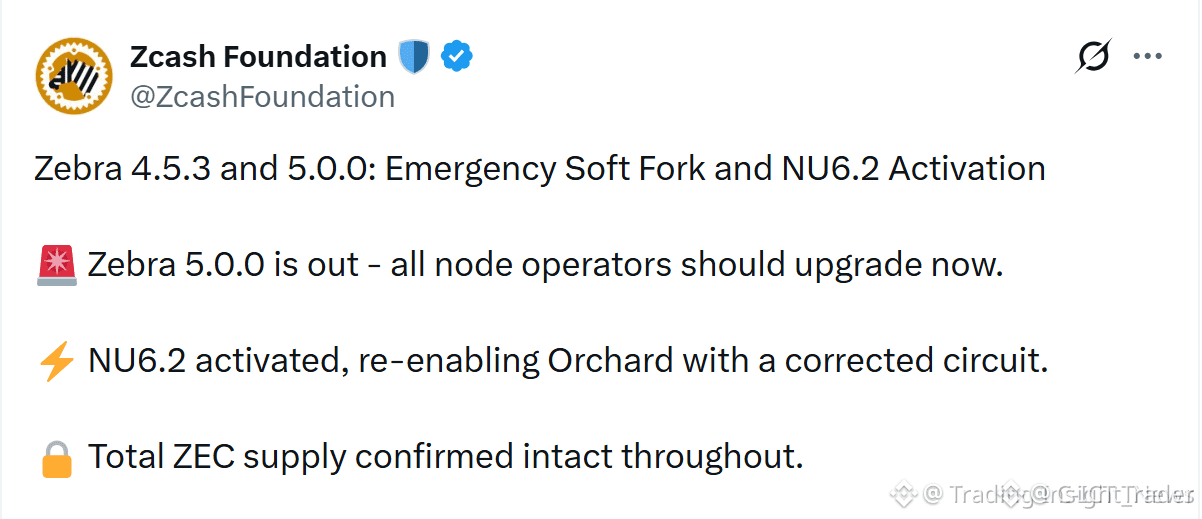
$ZEC ORCHARD FLAW PATCHED BEFORE EXPLOIT ⚠️
Zcash Foundation released emergency Zebra updates to address a critical Orchard Action circuit soundness vulnerability. The fix temporarily disables Orchard actions, then restores functionality through NU6.2 with the patched circuit, with no evidence of unauthorized value creation.
The key market takeaway is operational risk containment. Privacy was reported unaffected, while Sapling and transparent transactions continued functioning normally. Zebra operators are required to upgrade to version 5.0.0, making node compliance the near-term focus for network stability.
Not financial advice. Manage your risk.
#CryptoNews #Zcash #BlockchainSecurity #Altcoins
🔎
{future}(ZECUSDT)
$ZEC ORCHARD FLAW PATCHED BEFORE EXPLOIT ⚠️
Zcash Foundation released emergency Zebra updates to address a critical Orchard Action circuit soundness vulnerability. The fix temporarily disables Orchard actions, then restores functionality through NU6.2 with the patched circuit, with no evidence of unauthorized value creation.
The key market takeaway is operational risk containment. Privacy was reported unaffected, while Sapling and transparent transactions continued functioning normally. Zebra operators are required to upgrade to version 5.0.0, making node compliance the near-term focus for network stability.
Not financial advice. Manage your risk.
#CryptoNews #Zcash #BlockchainSecurity #Altcoins
🔎
Zcash Foundation released emergency Zebra updates to address a critical Orchard Action circuit soundness vulnerability. The fix temporarily disables Orchard actions, then restores functionality through NU6.2 with the patched circuit, with no evidence of unauthorized value creation.
The key market takeaway is operational risk containment. Privacy was reported unaffected, while Sapling and transparent transactions continued functioning normally. Zebra operators are required to upgrade to version 5.0.0, making node compliance the near-term focus for network stability.
Not financial advice. Manage your risk.
#CryptoNews #Zcash #BlockchainSecurity #Altcoins
🔎
249
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#AIStocksWhatNext
469,663 views
3,487 Discussing
2
#BitcoinTops$87KAtEightMonthHigh
335 views
18 Discussing
3
#ZECBreaksAbove$1600AtRecordHigh
64 views
5 Discussing
4
#BitwiseNEARStakingETPAssetsTop$100M
7,862 views
48 Discussing
5
#BitcoinBreaksAboveMayHighNears$86K
21,920 views
228 Discussing
6
#DogecoinRises15%
69,743 views
1,219 Discussing
7
#$14BBitcoinOptionsExpireFriday
6,184 views
104 Discussing
8
#BNBMarketCapPassesBNYMellon
43,035 views
892 Discussing
9
#CryptoMarketCapReclaims$3Trillion
8,944 views
87 Discussing
10
#MuseOvertakesChatGPTAsTopFreeIOSApp
24,769 views
651 Discussing