
#wallethack
wallethack
11,553 views
23 Discussing
Hot
Latest

·
--
Bearish
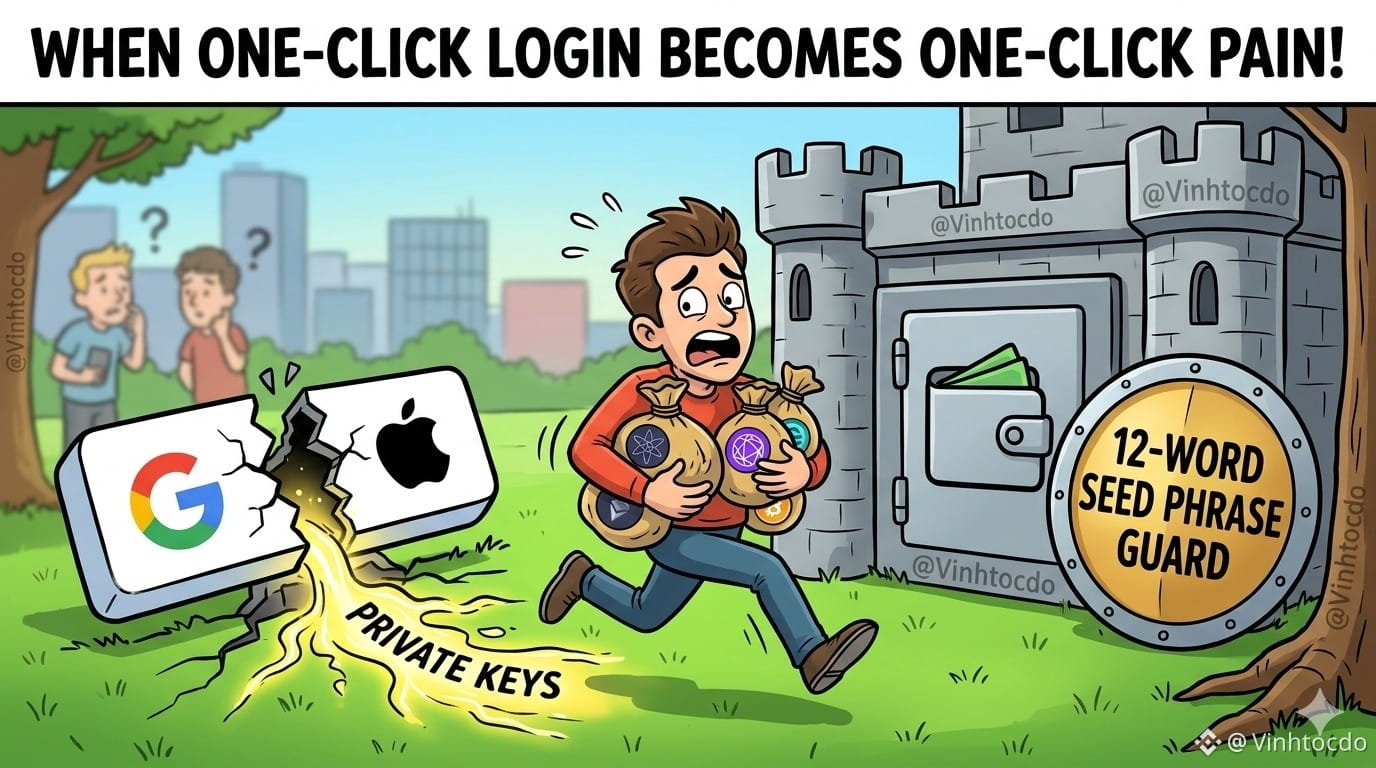
Keplr Wallet warning: When “one-tap login” hits where it hurts! 🤦♂️
Keplr Wallet has just issued an emergency alert: If you used Google or Apple ID to log in to your wallet, you should move your assets out immediately! The reason is a bug in Web3Auth’s infrastructure that exposed users’ private keys. Turns out “convenient, sure—but your money nearly vanished too”! The worst part is that some users’ balances suddenly show as zero or their staking is locked. Now they can only sit there “chanting” and wait for Keplr to coordinate a rescue.
What should traders and users do?
1. Stop depositing: Do not send any more funds to wallets created using social media accounts.
2. Evacuate immediately: Transfer your assets to a newly created wallet using a traditional Recovery Phrase (12/24 words) or to a hardware wallet to be safe.
3. Watch out for scams: At a time like this, there are few honest helpers and plenty of scammers impersonating “asset recovery support.” Don’t click on anything suspicious!
⚠️ This is not financial advice!
#KeplrAdvisesSocialLoginUsersToTransferAssets #KeplrWallet #Web3Auth #CryptoSecurity #WalletHack #Web3 #VINHTOCDO
Click below to trade and support me:
$ATOM
{spot}(ATOMUSDT)
$TIA
{spot}(TIAUSDT)
$ONE
{future}(ONEUSDT)
Keplr Wallet warning: When “one-tap login” hits where it hurts! 🤦♂️
Keplr Wallet has just issued an emergency alert: If you used Google or Apple ID to log in to your wallet, you should move your assets out immediately! The reason is a bug in Web3Auth’s infrastructure that exposed users’ private keys. Turns out “convenient, sure—but your money nearly vanished too”! The worst part is that some users’ balances suddenly show as zero or their staking is locked. Now they can only sit there “chanting” and wait for Keplr to coordinate a rescue.
What should traders and users do?
1. Stop depositing: Do not send any more funds to wallets created using social media accounts.
2. Evacuate immediately: Transfer your assets to a newly created wallet using a traditional Recovery Phrase (12/24 words) or to a hardware wallet to be safe.
3. Watch out for scams: At a time like this, there are few honest helpers and plenty of scammers impersonating “asset recovery support.” Don’t click on anything suspicious!
⚠️ This is not financial advice!
#KeplrAdvisesSocialLoginUsersToTransferAssets #KeplrWallet #Web3Auth #CryptoSecurity #WalletHack #Web3 #VINHTOCDO
Click below to trade and support me:
$ATOM
$TIA
$ONE
Keplr Wallet has just issued an emergency alert: If you used Google or Apple ID to log in to your wallet, you should move your assets out immediately! The reason is a bug in Web3Auth’s infrastructure that exposed users’ private keys. Turns out “convenient, sure—but your money nearly vanished too”! The worst part is that some users’ balances suddenly show as zero or their staking is locked. Now they can only sit there “chanting” and wait for Keplr to coordinate a rescue.
What should traders and users do?
1. Stop depositing: Do not send any more funds to wallets created using social media accounts.
2. Evacuate immediately: Transfer your assets to a newly created wallet using a traditional Recovery Phrase (12/24 words) or to a hardware wallet to be safe.
3. Watch out for scams: At a time like this, there are few honest helpers and plenty of scammers impersonating “asset recovery support.” Don’t click on anything suspicious!
⚠️ This is not financial advice!
#KeplrAdvisesSocialLoginUsersToTransferAssets #KeplrWallet #Web3Auth #CryptoSecurity #WalletHack #Web3 #VINHTOCDO
Click below to trade and support me:
$ATOM
$TIA
$ONE
User-6279aa89:
Follow me and I’ll follow you back; let’s grow together on Binance Square. newbies
4
8
1.5k

$2.3M crypto heist as wallet keys were compromised.
private keys linked to two wallets were leaked, enabling attackers to steal around $2.3 million in USDT. The incident highlights persistent security risks in crypto and the critical need for stronger key protection.
#CryptoNews #WalletHack #cryptofirst21 #Write2Earn #crypto
$2.3M crypto heist as wallet keys were compromised.
private keys linked to two wallets were leaked, enabling attackers to steal around $2.3 million in USDT. The incident highlights persistent security risks in crypto and the critical need for stronger key protection.
#CryptoNews #WalletHack #cryptofirst21 #Write2Earn #crypto
private keys linked to two wallets were leaked, enabling attackers to steal around $2.3 million in USDT. The incident highlights persistent security risks in crypto and the critical need for stronger key protection.
#CryptoNews #WalletHack #cryptofirst21 #Write2Earn #crypto
16
840
·
--
Bullish
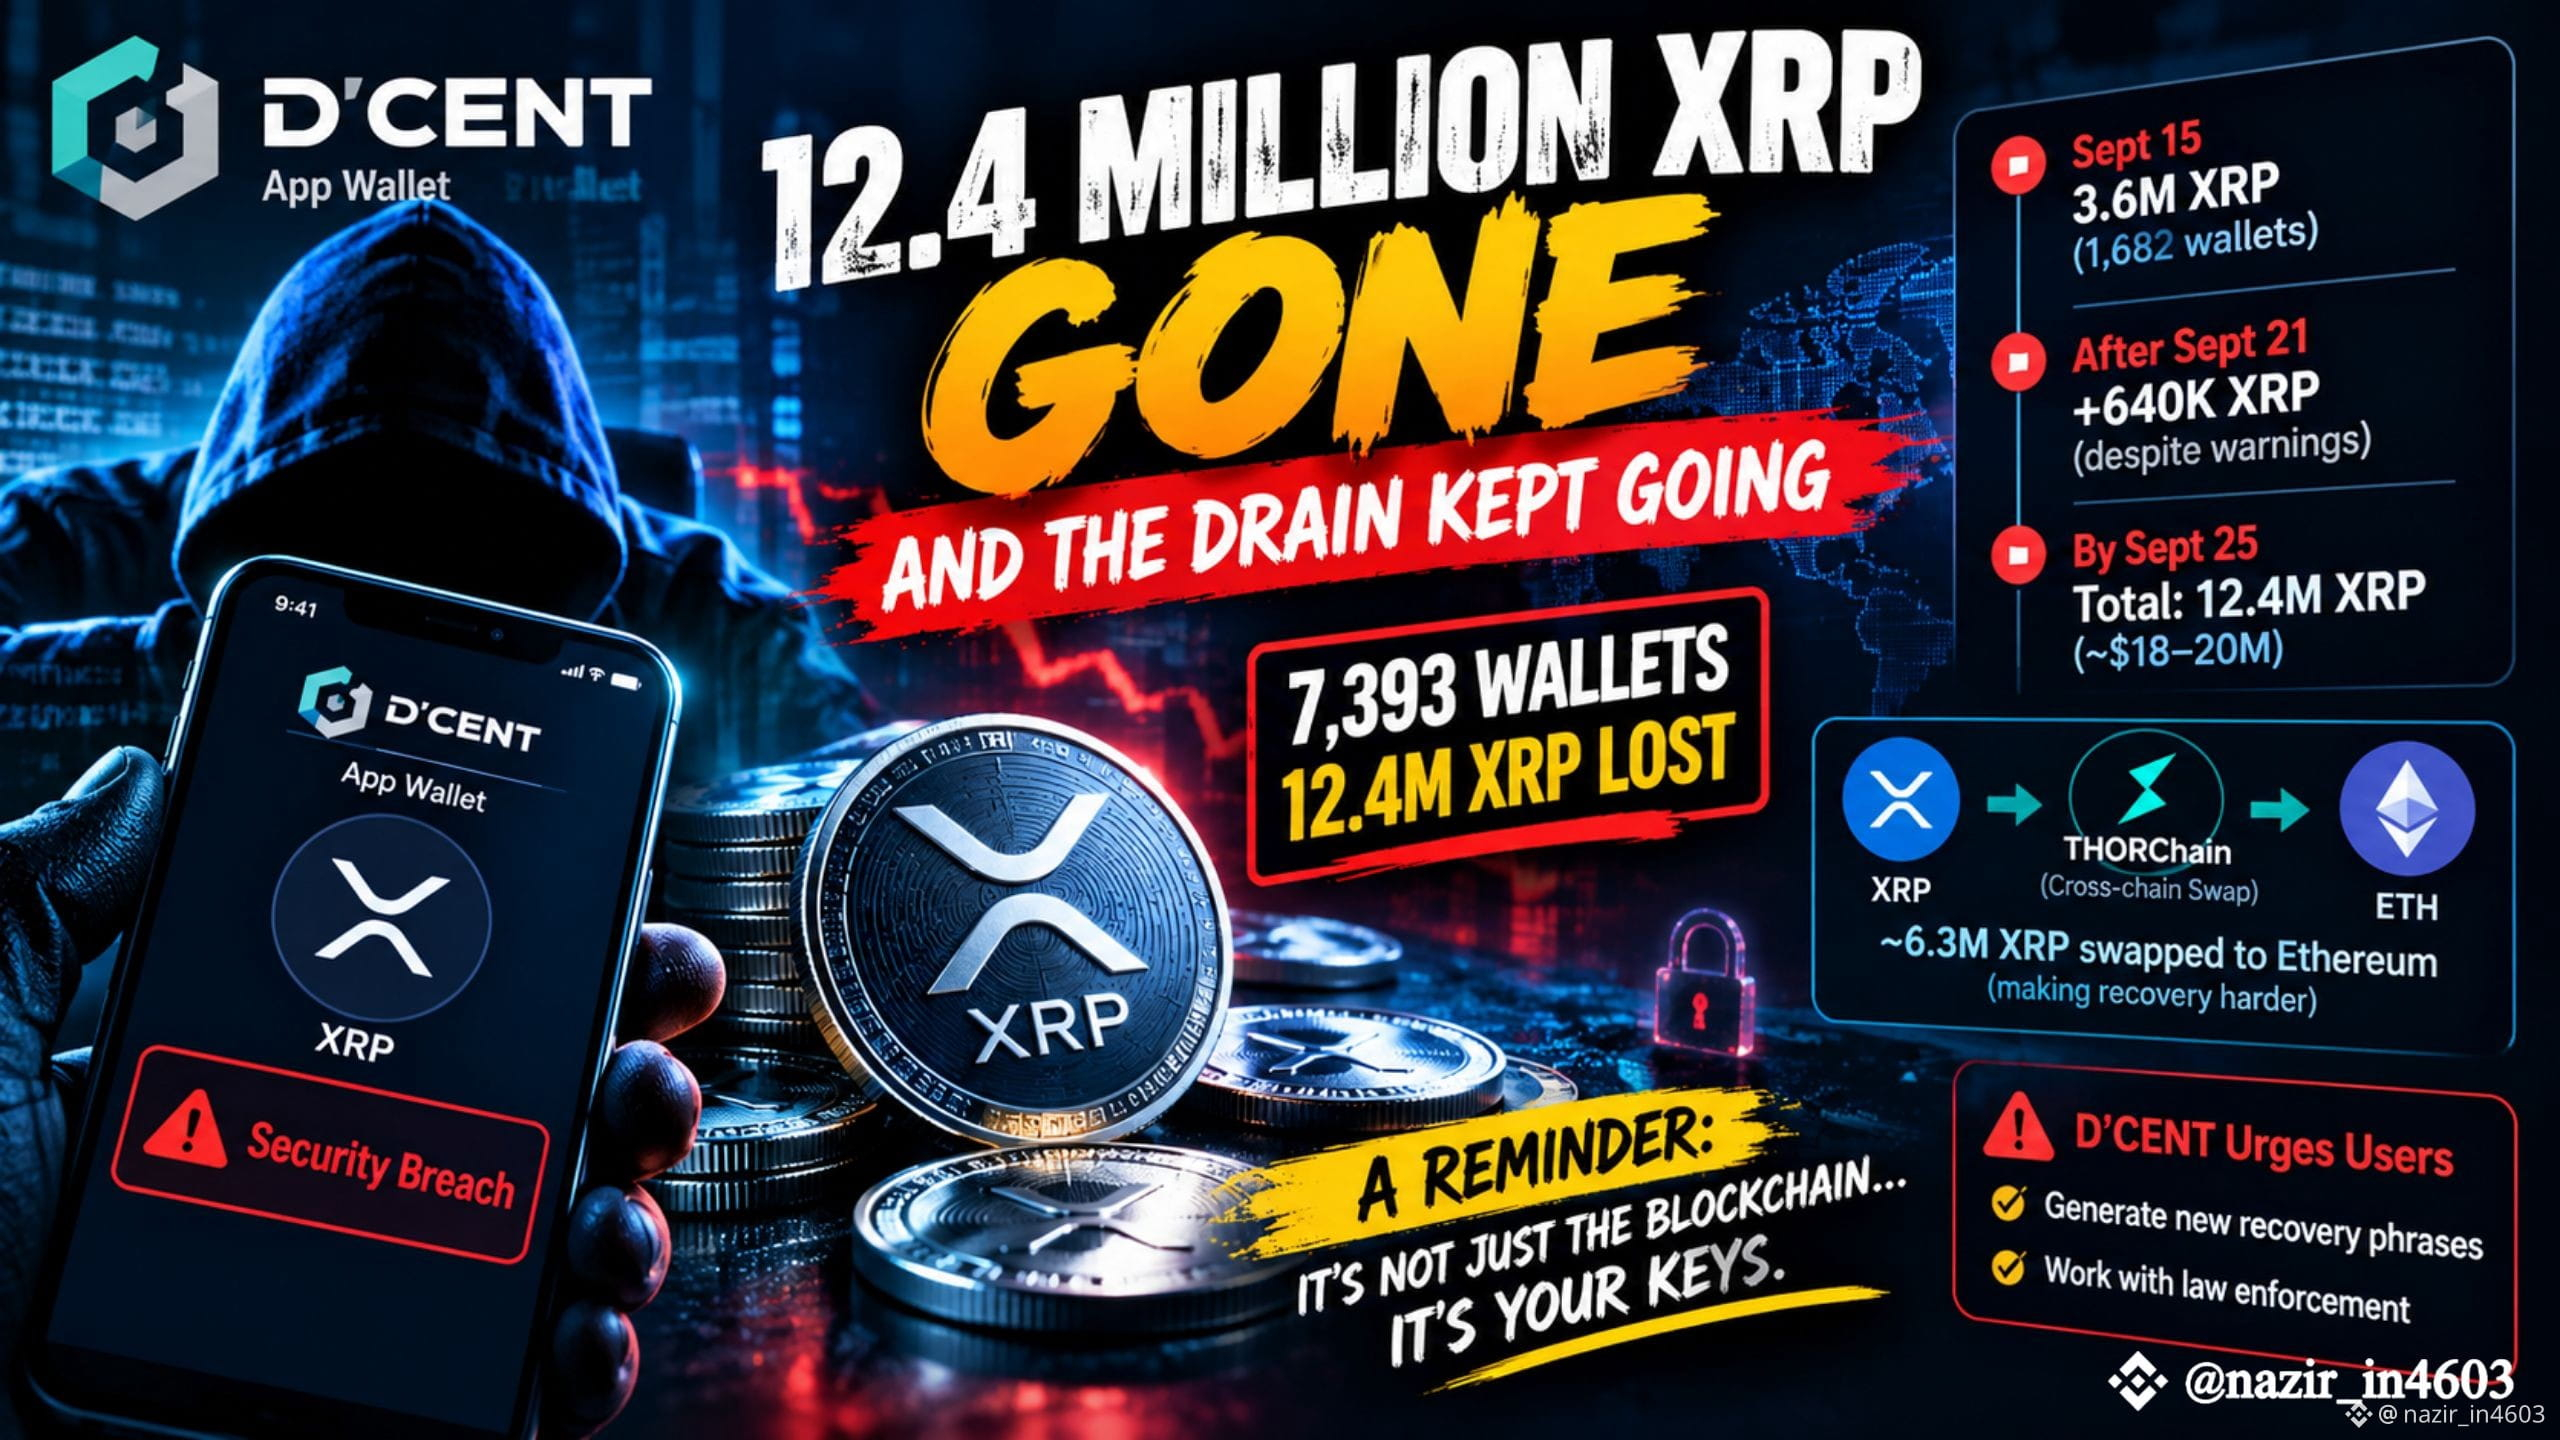
🚨 12.4 MILLION $XRP GONE — AND THE DRAIN KEPT GOING
This is the kind of crypto security story that makes you stop and look twice.
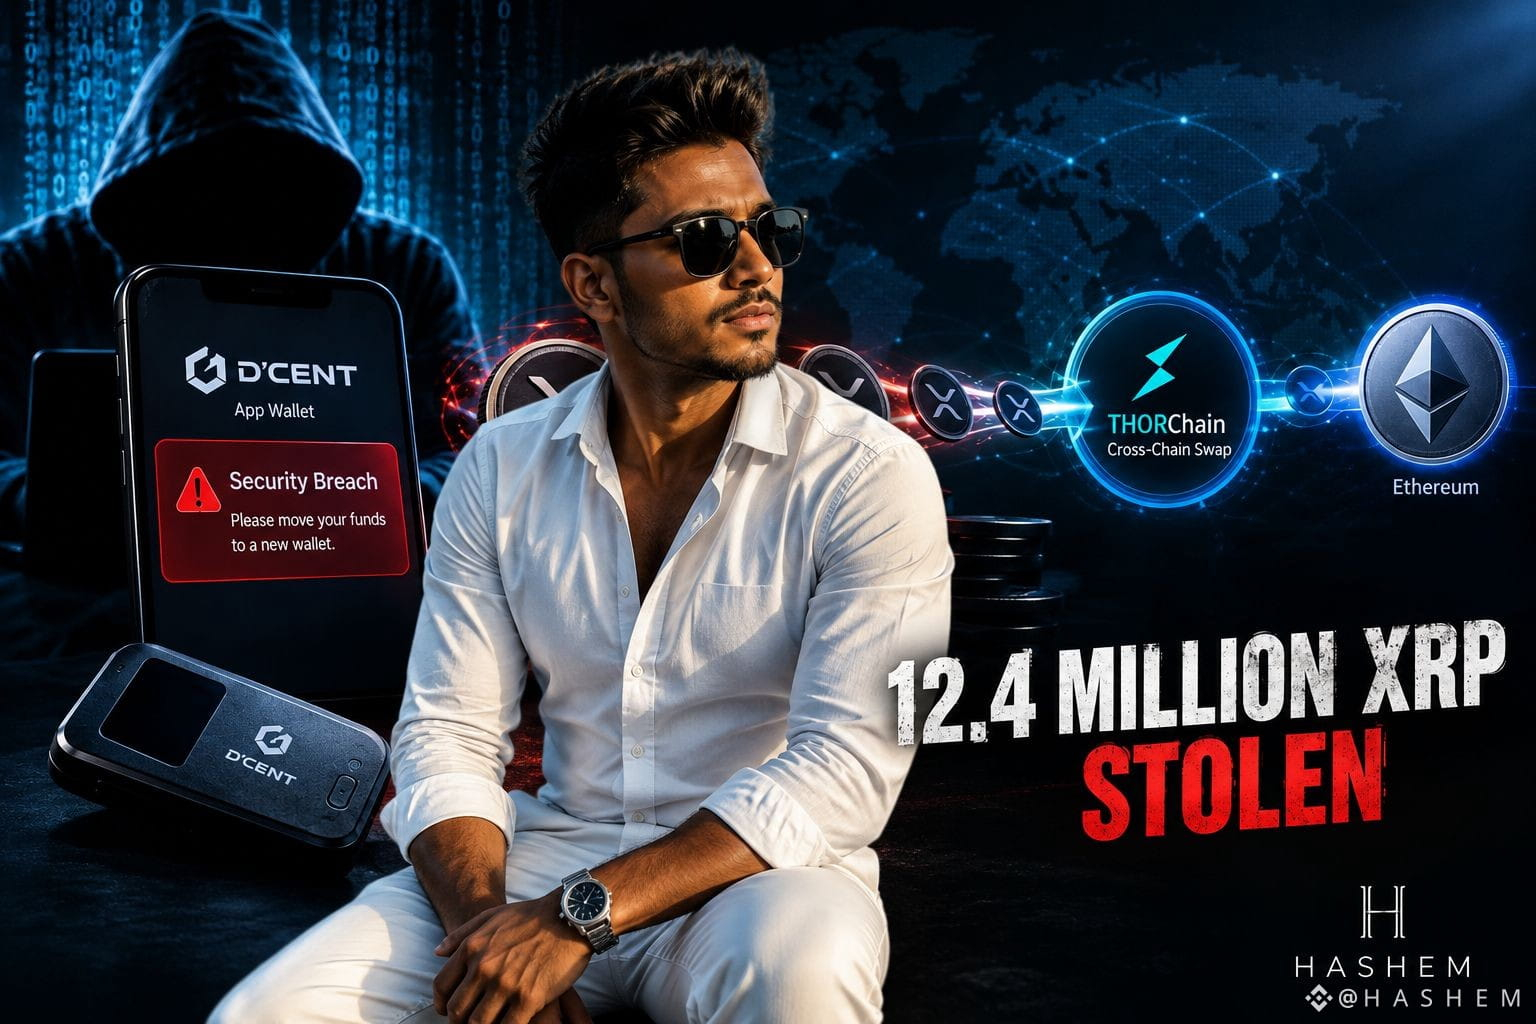
The D’CENT App Wallet incident has now been linked to roughly 12.4 million XRP drained from 7,393 wallets. But the most disturbing part isn’t just the amount.
It’s what happened after the warnings started going out.
The first major wave hit on September 15, when around 3.6 million XRP was drained from 1,682 wallets in just a few hours. The attackers weren’t breaking the XRP Ledger itself — the transfers were signed using private keys that had already been compromised.
Then came the part that really raises questions.
Even after users were being warned to move their funds, the same compromised keys were still being used. More than 640,000 XRP was taken after September 21, pushing the overall losses to around 12.4 million XRP. Some wallets were even drained again after being refilled.
And the money started moving across chains. On-chain analysis indicates that roughly 6.3 million XRP was swapped toward Ethereum through THORChain, making recovery and tracking even more complicated.
That’s the real lesson here:
🔐 A blockchain can remain secure while the keys controlling individual wallets are compromised.
For crypto users, the phrase “not your keys, not your coins” suddenly feels a lot less like a slogan.
The big question now isn’t only how the keys were compromised.
It’s also this:
When a wallet breach is actively happening, how quickly can affected users actually be warned — and how much time do they have to react? 🤔
#XRP #CryptoSecurity #WalletHack #DCENT #XRPL #CryptoNews
{future}(XRPUSDT)
🚨 12.4 MILLION $XRP GONE — AND THE DRAIN KEPT GOING
This is the kind of crypto security story that makes you stop and look twice.
The D’CENT App Wallet incident has now been linked to roughly 12.4 million XRP drained from 7,393 wallets. But the most disturbing part isn’t just the amount.
It’s what happened after the warnings started going out.
The first major wave hit on September 15, when around 3.6 million XRP was drained from 1,682 wallets in just a few hours. The attackers weren’t breaking the XRP Ledger itself — the transfers were signed using private keys that had already been compromised.
Then came the part that really raises questions.
Even after users were being warned to move their funds, the same compromised keys were still being used. More than 640,000 XRP was taken after September 21, pushing the overall losses to around 12.4 million XRP. Some wallets were even drained again after being refilled.
And the money started moving across chains. On-chain analysis indicates that roughly 6.3 million XRP was swapped toward Ethereum through THORChain, making recovery and tracking even more complicated.
That’s the real lesson here:
🔐 A blockchain can remain secure while the keys controlling individual wallets are compromised.
For crypto users, the phrase “not your keys, not your coins” suddenly feels a lot less like a slogan.
The big question now isn’t only how the keys were compromised.
It’s also this:
When a wallet breach is actively happening, how quickly can affected users actually be warned — and how much time do they have to react? 🤔
#XRP #CryptoSecurity #WalletHack #DCENT #XRPL #CryptoNews
This is the kind of crypto security story that makes you stop and look twice.
The D’CENT App Wallet incident has now been linked to roughly 12.4 million XRP drained from 7,393 wallets. But the most disturbing part isn’t just the amount.
It’s what happened after the warnings started going out.
The first major wave hit on September 15, when around 3.6 million XRP was drained from 1,682 wallets in just a few hours. The attackers weren’t breaking the XRP Ledger itself — the transfers were signed using private keys that had already been compromised.
Then came the part that really raises questions.
Even after users were being warned to move their funds, the same compromised keys were still being used. More than 640,000 XRP was taken after September 21, pushing the overall losses to around 12.4 million XRP. Some wallets were even drained again after being refilled.
And the money started moving across chains. On-chain analysis indicates that roughly 6.3 million XRP was swapped toward Ethereum through THORChain, making recovery and tracking even more complicated.
That’s the real lesson here:
🔐 A blockchain can remain secure while the keys controlling individual wallets are compromised.
For crypto users, the phrase “not your keys, not your coins” suddenly feels a lot less like a slogan.
The big question now isn’t only how the keys were compromised.
It’s also this:
When a wallet breach is actively happening, how quickly can affected users actually be warned — and how much time do they have to react? 🤔
#XRP #CryptoSecurity #WalletHack #DCENT #XRPL #CryptoNews
129
🚨 Warning: Malicious software targets crypto wallets on macOS via Telegram!
SlowMist has uncovered new malware targeting macOS users, capable of stealing Telegram session credentials and compromising cryptocurrency wallets. It can also trick users into obtaining wallet recovery phrases through fake applications, posing a serious threat to digital assets.
Mac users must exercise extreme caution.
━━━━━━━━━━━━━━
📊 Impact: 🔥 Very High
🏷️ OTHER
#macOS #Malware #CryptoSecurity #Telegram #WalletHack
🔗 Source: https://cointelegraph.com/news/macos-malware-crypto-investors-slowmist
🚨 Warning: Malicious software targets crypto wallets on macOS via Telegram!
SlowMist has uncovered new malware targeting macOS users, capable of stealing Telegram session credentials and compromising cryptocurrency wallets. It can also trick users into obtaining wallet recovery phrases through fake applications, posing a serious threat to digital assets.
Mac users must exercise extreme caution.
━━━━━━━━━━━━━━
📊 Impact: 🔥 Very High
🏷️ OTHER
#macOS #Malware #CryptoSecurity #Telegram #WalletHack
🔗 Source: https://cointelegraph.com/news/macos-malware-crypto-investors-slowmist
SlowMist has uncovered new malware targeting macOS users, capable of stealing Telegram session credentials and compromising cryptocurrency wallets. It can also trick users into obtaining wallet recovery phrases through fake applications, posing a serious threat to digital assets.
Mac users must exercise extreme caution.
━━━━━━━━━━━━━━
📊 Impact: 🔥 Very High
🏷️ OTHER
#macOS #Malware #CryptoSecurity #Telegram #WalletHack
🔗 Source: https://cointelegraph.com/news/macos-malware-crypto-investors-slowmist
1
26
·
--
#hackersdrainover12.4mxrpfromdcentwallets
A Wallet Breach Kept Bleeding Even After the Warnings Went Out
Over 7,300 crypto wallets just lost more than 12.4 million XRP — and the strangest part is how long the theft continued even after users were told to move their funds.
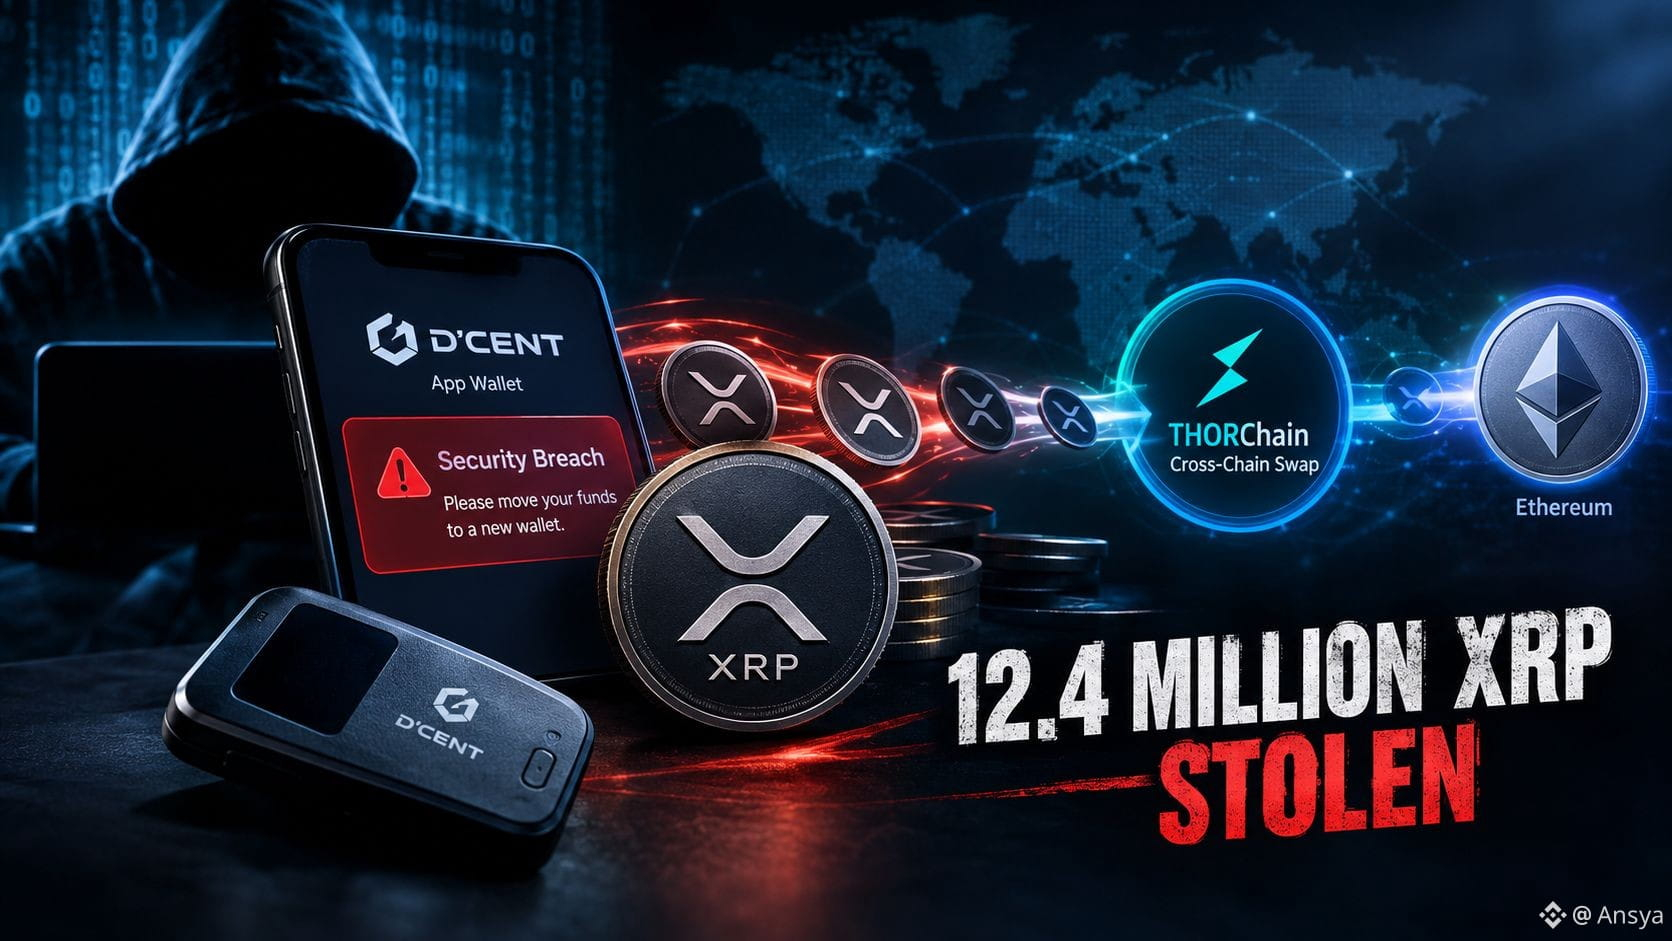
Here's the timeline: South Korean wallet provider D'CENT confirmed a security breach affecting its App Wallet on September 16, after attackers began exploiting compromised private keys the day before. The first wave was brutal — roughly 3.6 million XRP drained from 1,682 wallets in under three hours, mixing manual theft of large balances with automated scripts sweeping smaller ones. Despite public warnings, more than 640,000 additional XRP disappeared after September 21, and by September 25, total losses reached approximately 12.4 million XRP, worth roughly $18-20 million. No exploit hit the XRP Ledger itself — every transfer used valid signatures from already-compromised keys. Roughly half the stolen funds have since moved to Ethereum via THORChain, a cross-chain swap protocol that doesn't require identity verification, complicating recovery efforts. D'CENT says it's working with law enforcement and has urged all App Wallet users to generate new recovery phrases immediately.
Why does this matter? This wasn't a protocol-level flaw — it was compromised key material, a reminder that wallet security often hinges on implementation details users never see. The continued draining after public alerts also raises a real question about how effectively warnings reach affected users in time, and cross-chain laundering tools make recovery meaningfully harder once funds start moving.
Whether D'CENT fully identifies the breach's root cause, or whether affected users see any reimbursement, remains unresolved.
Does the industry need faster, more forceful ways to warn users mid-breach — or is user vigilance always the last line of defense? 🤔
#xrp #CryptoSecurity #WalletHack #DCENT
#hackersdrainover12.4mxrpfromdcentwallets
A Wallet Breach Kept Bleeding Even After the Warnings Went Out
Over 7,300 crypto wallets just lost more than 12.4 million XRP — and the strangest part is how long the theft continued even after users were told to move their funds.
Here's the timeline: South Korean wallet provider D'CENT confirmed a security breach affecting its App Wallet on September 16, after attackers began exploiting compromised private keys the day before. The first wave was brutal — roughly 3.6 million XRP drained from 1,682 wallets in under three hours, mixing manual theft of large balances with automated scripts sweeping smaller ones. Despite public warnings, more than 640,000 additional XRP disappeared after September 21, and by September 25, total losses reached approximately 12.4 million XRP, worth roughly $18-20 million. No exploit hit the XRP Ledger itself — every transfer used valid signatures from already-compromised keys. Roughly half the stolen funds have since moved to Ethereum via THORChain, a cross-chain swap protocol that doesn't require identity verification, complicating recovery efforts. D'CENT says it's working with law enforcement and has urged all App Wallet users to generate new recovery phrases immediately.
Why does this matter? This wasn't a protocol-level flaw — it was compromised key material, a reminder that wallet security often hinges on implementation details users never see. The continued draining after public alerts also raises a real question about how effectively warnings reach affected users in time, and cross-chain laundering tools make recovery meaningfully harder once funds start moving.
Whether D'CENT fully identifies the breach's root cause, or whether affected users see any reimbursement, remains unresolved.
Does the industry need faster, more forceful ways to warn users mid-breach — or is user vigilance always the last line of defense? 🤔
#xrp #CryptoSecurity #WalletHack #DCENT
A Wallet Breach Kept Bleeding Even After the Warnings Went Out
Over 7,300 crypto wallets just lost more than 12.4 million XRP — and the strangest part is how long the theft continued even after users were told to move their funds.
Here's the timeline: South Korean wallet provider D'CENT confirmed a security breach affecting its App Wallet on September 16, after attackers began exploiting compromised private keys the day before. The first wave was brutal — roughly 3.6 million XRP drained from 1,682 wallets in under three hours, mixing manual theft of large balances with automated scripts sweeping smaller ones. Despite public warnings, more than 640,000 additional XRP disappeared after September 21, and by September 25, total losses reached approximately 12.4 million XRP, worth roughly $18-20 million. No exploit hit the XRP Ledger itself — every transfer used valid signatures from already-compromised keys. Roughly half the stolen funds have since moved to Ethereum via THORChain, a cross-chain swap protocol that doesn't require identity verification, complicating recovery efforts. D'CENT says it's working with law enforcement and has urged all App Wallet users to generate new recovery phrases immediately.
Why does this matter? This wasn't a protocol-level flaw — it was compromised key material, a reminder that wallet security often hinges on implementation details users never see. The continued draining after public alerts also raises a real question about how effectively warnings reach affected users in time, and cross-chain laundering tools make recovery meaningfully harder once funds start moving.
Whether D'CENT fully identifies the breach's root cause, or whether affected users see any reimbursement, remains unresolved.
Does the industry need faster, more forceful ways to warn users mid-breach — or is user vigilance always the last line of defense? 🤔
#xrp #CryptoSecurity #WalletHack #DCENT
10
1
25
20.6k
·
--
Bullish
$ETH $XRP $BNB 🚨 7,300+ WALLETS DRAINED… OVER 12.4M XRP GONE! 😳🔓
A major wallet security incident involving D’CENT has turned into a massive XRP loss — and the most alarming part is that the draining reportedly continued even after warnings were issued.
📌 What Happened?
🔹 D’CENT confirmed a security breach affecting its App Wallet on September 16, after compromised private keys were reportedly exploited.
🔹 In the first wave, around 3.6M XRP was drained from approximately 1,682 wallets in less than three hours.
🔹 Attackers reportedly used both manual transfers for larger balances and automated scripts to sweep smaller holdings.
🔹 Even after public warnings, another 640K+ XRP was reportedly drained after September 21.
🔹 By September 25, total losses had reached roughly 12.4M XRP, estimated at around $18–20M.
⚠️ The XRP Ledger itself wasn’t hacked.
The transactions were reportedly signed using valid credentials linked to compromised private keys — making this a wallet/key-security incident rather than a protocol-level exploit.
🌉 Then came the bigger problem…
A significant portion of the stolen XRP reportedly moved across chains through THORChain, making fund tracing and potential recovery more complicated.
🛡️ D’CENT has said it is working with law enforcement and has urged affected App Wallet users to generate new recovery phrases immediately.
💡 The Bigger Lesson
Crypto security isn't only about the blockchain.
Sometimes, the biggest vulnerability sits one layer above it — in wallet software, private-key handling, or how quickly users can be warned during an active breach.
And once stolen assets begin moving across multiple chains, recovery can become significantly harder.
🤔 What do you think?
Should wallet providers have stronger emergency systems to instantly alert affected users during an active breach — or does self-custody ultimately mean users must remain the final line of defense?
#XRP #CryptoSecurity #WalletHack #DCENT #CryptoNews
{spot}(XRPUSDT)
{spot}(BTCUSDT)
{spot}(BNBUSDT)
$ETH $XRP $BNB 🚨 7,300+ WALLETS DRAINED… OVER 12.4M XRP GONE! 😳🔓
A major wallet security incident involving D’CENT has turned into a massive XRP loss — and the most alarming part is that the draining reportedly continued even after warnings were issued.
📌 What Happened?
🔹 D’CENT confirmed a security breach affecting its App Wallet on September 16, after compromised private keys were reportedly exploited.
🔹 In the first wave, around 3.6M XRP was drained from approximately 1,682 wallets in less than three hours.
🔹 Attackers reportedly used both manual transfers for larger balances and automated scripts to sweep smaller holdings.
🔹 Even after public warnings, another 640K+ XRP was reportedly drained after September 21.
🔹 By September 25, total losses had reached roughly 12.4M XRP, estimated at around $18–20M.
⚠️ The XRP Ledger itself wasn’t hacked.
The transactions were reportedly signed using valid credentials linked to compromised private keys — making this a wallet/key-security incident rather than a protocol-level exploit.
🌉 Then came the bigger problem…
A significant portion of the stolen XRP reportedly moved across chains through THORChain, making fund tracing and potential recovery more complicated.
🛡️ D’CENT has said it is working with law enforcement and has urged affected App Wallet users to generate new recovery phrases immediately.
💡 The Bigger Lesson
Crypto security isn't only about the blockchain.
Sometimes, the biggest vulnerability sits one layer above it — in wallet software, private-key handling, or how quickly users can be warned during an active breach.
And once stolen assets begin moving across multiple chains, recovery can become significantly harder.
🤔 What do you think?
Should wallet providers have stronger emergency systems to instantly alert affected users during an active breach — or does self-custody ultimately mean users must remain the final line of defense?
#XRP #CryptoSecurity #WalletHack #DCENT #CryptoNews
A major wallet security incident involving D’CENT has turned into a massive XRP loss — and the most alarming part is that the draining reportedly continued even after warnings were issued.
📌 What Happened?
🔹 D’CENT confirmed a security breach affecting its App Wallet on September 16, after compromised private keys were reportedly exploited.
🔹 In the first wave, around 3.6M XRP was drained from approximately 1,682 wallets in less than three hours.
🔹 Attackers reportedly used both manual transfers for larger balances and automated scripts to sweep smaller holdings.
🔹 Even after public warnings, another 640K+ XRP was reportedly drained after September 21.
🔹 By September 25, total losses had reached roughly 12.4M XRP, estimated at around $18–20M.
⚠️ The XRP Ledger itself wasn’t hacked.
The transactions were reportedly signed using valid credentials linked to compromised private keys — making this a wallet/key-security incident rather than a protocol-level exploit.
🌉 Then came the bigger problem…
A significant portion of the stolen XRP reportedly moved across chains through THORChain, making fund tracing and potential recovery more complicated.
🛡️ D’CENT has said it is working with law enforcement and has urged affected App Wallet users to generate new recovery phrases immediately.
💡 The Bigger Lesson
Crypto security isn't only about the blockchain.
Sometimes, the biggest vulnerability sits one layer above it — in wallet software, private-key handling, or how quickly users can be warned during an active breach.
And once stolen assets begin moving across multiple chains, recovery can become significantly harder.
🤔 What do you think?
Should wallet providers have stronger emergency systems to instantly alert affected users during an active breach — or does self-custody ultimately mean users must remain the final line of defense?
#XRP #CryptoSecurity #WalletHack #DCENT #CryptoNews
135
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#USPPIMissMayEaseBTCPressure
4,084 views
213 Discussing
2
#BitcoinCoreDisclosesTorTrafficVulnerability
1 views
15 Discussing
3
#WhatWillDriveCryptoandStocks’NextRebound?
92,569 views
1,216 Discussing
4
#BitcoinBreaksBelow200WeekMovingAverage
14,401 views
255 Discussing
5
#SpaceXTeslaMergerTalksWouldCombine30220BTC
5,269 views
124 Discussing
6
#Anthropic’s6xIPODemandSignalsPotentialRecordRaise
30,238 views
570 Discussing
7
#USCryptoETFsLose$1.48BInFiveDays
1,141 views
29 Discussing
8
#KoreaDigitalAssetBasicActFinalDraftExpectedEarlyJanuary
2,726 views
15 Discussing
9
#RippleRLUSDMarketCapSurpassesPayPalPYUSD
2,437 views
80 Discussing
10
#JaneStreetNearlyOctuplesFidelityBitcoinETFHoldings
10,711 views
183 Discussing