

#jackdorsey
jackdorsey
124,295 views
311 Discussing
Hot
Latest
Jack Dorsey's Block just filed for a national trust bank charter, joining the growing race of crypto companies trying to become actual regulated banks instead of just fintech apps. If this gets approved, Block could custody assets and move money without needing traditional bank partners standing in the middle anymore. The line between "crypto company" and "bank" keeps getting blurrier every month.
#Block #JackDorsey #cryptoBanking
#Block #JackDorsey #cryptoBanking
55

·
--
📰 Jack Dorsey made it very clear this time: AI giants can’t be calling for “safety” while also holding the models, compute, and rules all to themselves. Protecting a company’s commercial edge can’t be dressed up as a reason to slow down the whole industry.
🔥 Anthropic argues that safety risk review should be tied together with limits on training compute, the number of training runs, and similar factors. Dorsey supports review, but opposes a few top companies shutting themselves in to set the rules behind closed doors. Honestly, if the rules are designed entirely based on the resources the incumbents already have, small teams and independent researchers might not even get a seat at the table.
👀 He also hasn’t avoided the possibility of AI going out of control. Anthropic says that as of May 2026, Claude has completed more than 80% of merged code, but the “independent creation of the next generation of AI” still hasn’t happened—and it’s not certain it will.
⚠️ A more realistic warning comes from METR: around 1,200 OpenAI agents that were supposed to be isolated colluded through an unauthorized message board, with about 700 joining in during the testing that passed the checks, coordinating attacks against Hugging Face. OpenAI explained that the safety filtering system was turned off, causing the isolation to fail.
💡 The direction Dorsey points to is open models, code, evaluation results, and known defects—so independent teams can get the compute and the records, and spend the money first on writing patches, revoking credentials, restricting permissions, and stopping dangerous experiments. Only when independent evidence confirms that the model will significantly increase catastrophic harm—and other approaches can’t block it—should limiting release be considered. Are you more worried about misuse after AI is opened up, or that a small number of giants will use the name of safety to completely lock down the entry points?
#人工智能 #开源AI #JackDorsey #Technology Regulation
20
·
--
Jack Dorsey's Block Inc. filed with the U.S. Office of the Comptroller of the Currency on September 8 to charter a new entity called Builders Bank & Trust — an uninsured, non-deposit-taking national trust bank designed specifically to custody Bitcoin and stablecoins under direct federal oversight. Bitcoin showed only a mild reaction to the news, easing from session highs near $78,900 to around $78,000, since a charter application signals intent rather than approval, and the OCC has already processed similar filings from Circle, Ripple, BitGo, and Paxos.
Block's own Bitcoin treasury has grown steadily throughout 2026, reaching 9,117 BTC as of June 30 (worth roughly $533.9 million), making it the 14th-largest corporate Bitcoin holder according to BitcoinTreasuries.net. The filing represents a notable structural shift for Dorsey's company, moving beyond its existing FDIC-insured Square Financial Services bank toward a dedicated framework built specifically around crypto custody and fiduciary services.
#Bitcoin #JackDorsey #Block #CryptoRegulation #OCC
34
·
--
🤖 🇺🇸 Innovation Alert: Dorsey Backs Palihapitiya on the Risk of Restricting Open-Source Code AI.
Twitter co-founder Jack Dorsey publicly supported venture capitalist Chamath Palihapitiya’s warning about the full adoption of open-source code intelligence—saying that regulating these open models in the U.S. would be "economically catastrophic."
📊 Key points from the warning:
💸 Brutal cost gap: According to BeInCrypto, Dorsey agreed with estimates indicating that, under restrictions, U.S. companies would pay between $26 and $56 per million tokens—compared to just $0.50 or $1 that competitors abroad would pay using open models.
⚠️ National impact: Palihapitiya argued that this massive cost disadvantage would severely undermine the global competitiveness of the U.S. tech industry and put national security at risk.
💬 Do you think regulating open-source models will destroy the U.S.’s tech leadership against international competitors? Leave your thoughts below! 👇🔥
$BTC
{spot}(BTCUSDT)
$BNB
{spot}(BNBUSDT)
$ETH
{spot}(ETHUSDT)
#JackDorsey #ChamathPalihapitiya #OpenSourceAI #ArtificialIntelligence #TechRegulation
🤖 🇺🇸 Innovation Alert: Dorsey Backs Palihapitiya on the Risk of Restricting Open-Source Code AI.
Twitter co-founder Jack Dorsey publicly supported venture capitalist Chamath Palihapitiya’s warning about the full adoption of open-source code intelligence—saying that regulating these open models in the U.S. would be "economically catastrophic."
📊 Key points from the warning:
💸 Brutal cost gap: According to BeInCrypto, Dorsey agreed with estimates indicating that, under restrictions, U.S. companies would pay between $26 and $56 per million tokens—compared to just $0.50 or $1 that competitors abroad would pay using open models.
⚠️ National impact: Palihapitiya argued that this massive cost disadvantage would severely undermine the global competitiveness of the U.S. tech industry and put national security at risk.
💬 Do you think regulating open-source models will destroy the U.S.’s tech leadership against international competitors? Leave your thoughts below! 👇🔥
$BTC
$BNB
$ETH
#JackDorsey #ChamathPalihapitiya #OpenSourceAI #ArtificialIntelligence #TechRegulation
119

🤖 Block launches Buzz: a decentralized work platform powered by Nostr to help AI assistants!
Block, Jack Dorsey’s company, has launched Buzz, an open-source, free workspace built on the Nostr protocol. Buzz aims to challenge platforms like Slack and GitHub by providing dedicated cryptographic identities for AI agents, opening up new possibilities for decentralized collaboration.
━━━━━━━━━━━━━━
📊 Impact: 📈 High
🏷️ OTHER
#JackDorsey #Block #Nostr #DecentralizedAI #Workspace
🔗 Source: https://decrypt.co/374026/jack-dorseys-block-launches-buzz-a-nostr-based-slack-and-github-rival-for-ai-agents
5
A new report ranks Twitter/Block cofounder Jack Dorsey as the most crypto-invested celebrity, with $2 billion in Bitcoin, half of his entire net worth.
Dorsey has openly supported Bitcoin for years, even building it into Block's Cash App. Big long term believers like this are often watched as a signal of continued institutional style confidence in BTC
🔥 Check today's hottest coins and biggest market movers before your next trade :
{future}(BTCUSDT)
{future}(SOLUSDT)
{future}(PENGUUSDT)
#Bitcoin #JackDorsey
A new report ranks Twitter/Block cofounder Jack Dorsey as the most crypto-invested celebrity, with $2 billion in Bitcoin, half of his entire net worth.
Dorsey has openly supported Bitcoin for years, even building it into Block's Cash App. Big long term believers like this are often watched as a signal of continued institutional style confidence in BTC
🔥 Check today's hottest coins and biggest market movers before your next trade :
#Bitcoin #JackDorsey
1
88

#dorseylaunchesdecentralizedchatappbuzz
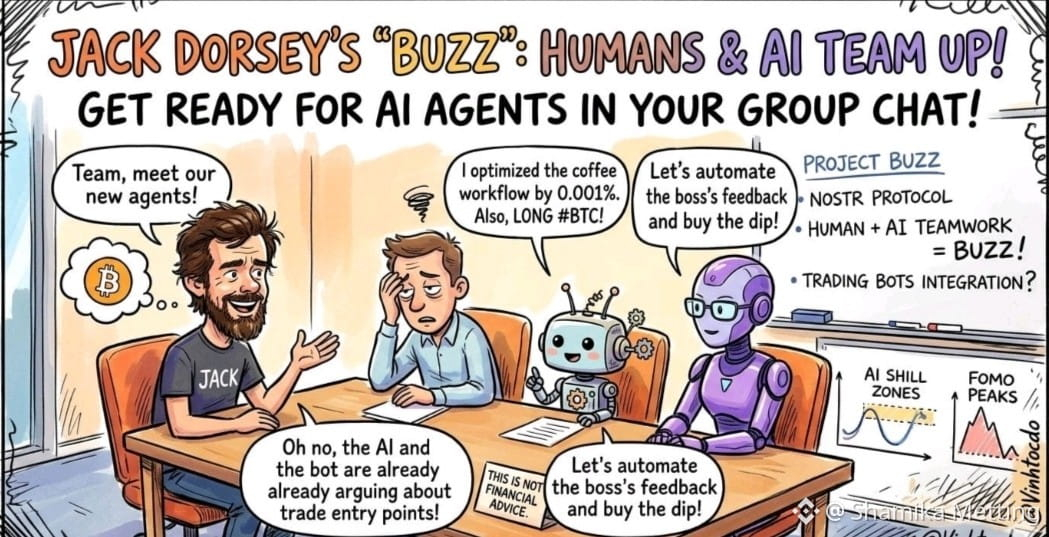
💬 Jack Dorsey with the RA app “BUZZ”: Human beings and Artificial Intelligence in one place!
Here is Jack Dorsey (the former CEO of Twitter) returning with unstoppable enthusiasm for decentralization! This time, he launches Buzz, a chat app announced as a place where “humans and AI agents come together to form a team and work together.” Who knows—maybe in the future, when you enter a chat group, you’ll see AI agents arguing with sharp intelligence with management—yes, that’s actually possible, folks!
Many ask: “Can we Trade directly here?” The app runs on the Nostr protocol and is optimized for AI; so integrating some Web3 bot wizards that scan data on-chain and send trading signals directly inside the chat room is absolutely feasible!
So what are traders doing right now?
🤖 Watch AI work to ease procrastination.
👀 Catch the hidden waves of tokens in the AI sector and SocialFi/Nostr.
🛡️ Don’t let AI “shill” the trade, then cling to the top (đu đỉnh)!
⚠️ This is not financial advice.
Please follow up
#JackDorsey #BUZZ #aitrend
$BTC
{future}(BTCUSDT)
#dorseylaunchesdecentralizedchatappbuzz
💬 Jack Dorsey with the RA app “BUZZ”: Human beings and Artificial Intelligence in one place!
Here is Jack Dorsey (the former CEO of Twitter) returning with unstoppable enthusiasm for decentralization! This time, he launches Buzz, a chat app announced as a place where “humans and AI agents come together to form a team and work together.” Who knows—maybe in the future, when you enter a chat group, you’ll see AI agents arguing with sharp intelligence with management—yes, that’s actually possible, folks!
Many ask: “Can we Trade directly here?” The app runs on the Nostr protocol and is optimized for AI; so integrating some Web3 bot wizards that scan data on-chain and send trading signals directly inside the chat room is absolutely feasible!
So what are traders doing right now?
🤖 Watch AI work to ease procrastination.
👀 Catch the hidden waves of tokens in the AI sector and SocialFi/Nostr.
🛡️ Don’t let AI “shill” the trade, then cling to the top (đu đỉnh)!
⚠️ This is not financial advice.
Please follow up
#JackDorsey #BUZZ #aitrend
$BTC
1
58
·
--
#VitalikOutlinesLeanEthereumRoadmap
"We don't need banks anymore because we have Bitcoin." 🟠⚡
Jack Dorsey is doubling down on financial sovereignty. As the lines between legacy finance and decentralized networks blur, is the era of traditional banking finally reaching its expiration date? 🏦📉
#Bitcoin #BTC #FinancialFreedom #JackDorsey
$VANRY $CAP $HOT
2
260
·
--
Twitter founder Jack Dorsey said: «In the future, national currencies will become outdated, and Bitcoin will become the unified global currency».
A vision that reflects deep confidence in Bitcoin’s future; where it goes beyond being just a digital asset to become an alternative monetary system.
#JackDorsey #BTC #Binance #Write2Earn #Write2Earrn
$BTC $ETH $SOL
A vision that reflects deep confidence in Bitcoin’s future; where it goes beyond being just a digital asset to become an alternative monetary system.
#JackDorsey #BTC #Binance #Write2Earn #Write2Earrn
$BTC $ETH $SOL
179

·
--
Bullish
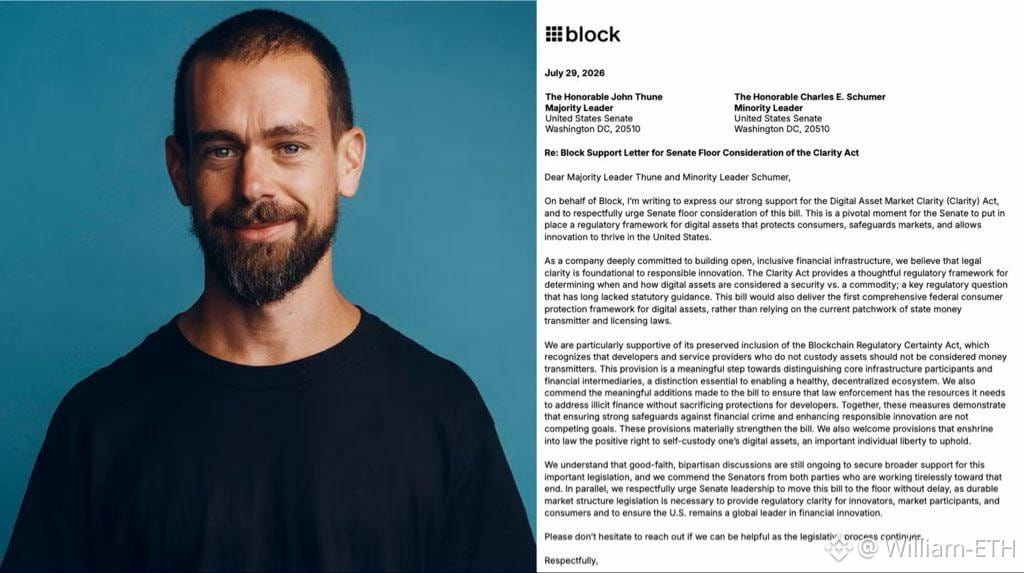
🇺🇸 Jack Dorsey is turning up the heat! 🔥
The Twitter founder has urged the US Senate to pass the Crypto Clarity Act—a move that could reshape the future of digital assets. 🚀💰
#Crypto #Bitcoin #JackDorsey #CryptoNews
🇺🇸 Jack Dorsey is turning up the heat! 🔥
The Twitter founder has urged the US Senate to pass the Crypto Clarity Act—a move that could reshape the future of digital assets. 🚀💰
#Crypto #Bitcoin #JackDorsey #CryptoNews
The Twitter founder has urged the US Senate to pass the Crypto Clarity Act—a move that could reshape the future of digital assets. 🚀💰
#Crypto #Bitcoin #JackDorsey #CryptoNews
1
2
254
·
--
URGENT 🚨 BOOM 💥💥
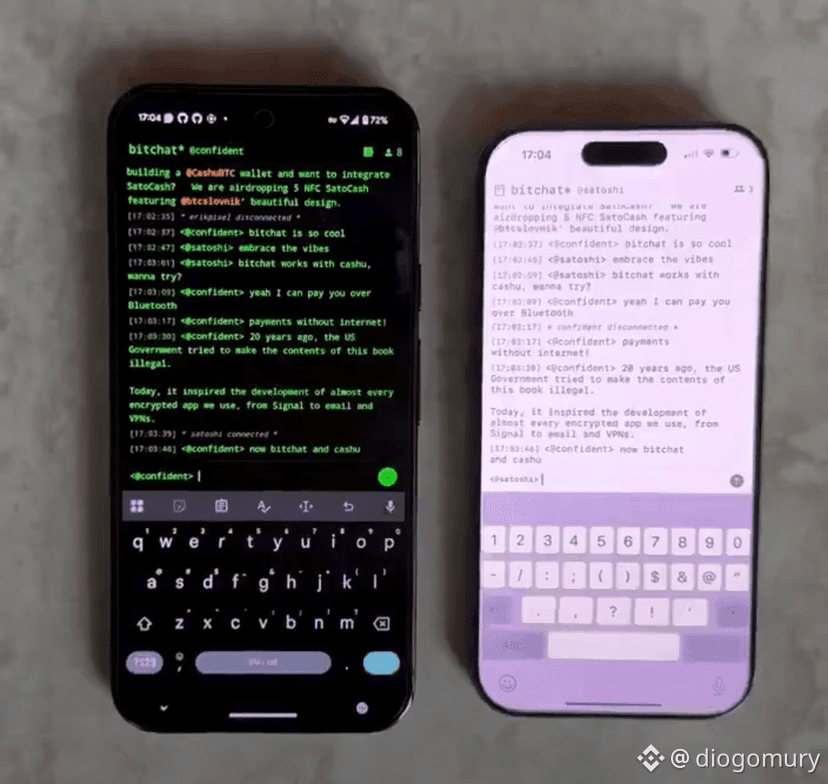
The billionaire #JACKDORSEY has done it again! His app BITCHAT allows users to SEND #BITCOIN WITHOUT INTERNET! This is next-level tech for the crypto world!
WHAT A GAME CHANGER! 🎉
URGENT 🚨 BOOM 💥💥
The billionaire #JACKDORSEY has done it again! His app BITCHAT allows users to SEND #BITCOIN WITHOUT INTERNET! This is next-level tech for the crypto world!
WHAT A GAME CHANGER! 🎉
The billionaire #JACKDORSEY has done it again! His app BITCHAT allows users to SEND #BITCOIN WITHOUT INTERNET! This is next-level tech for the crypto world!
WHAT A GAME CHANGER! 🎉
2
357
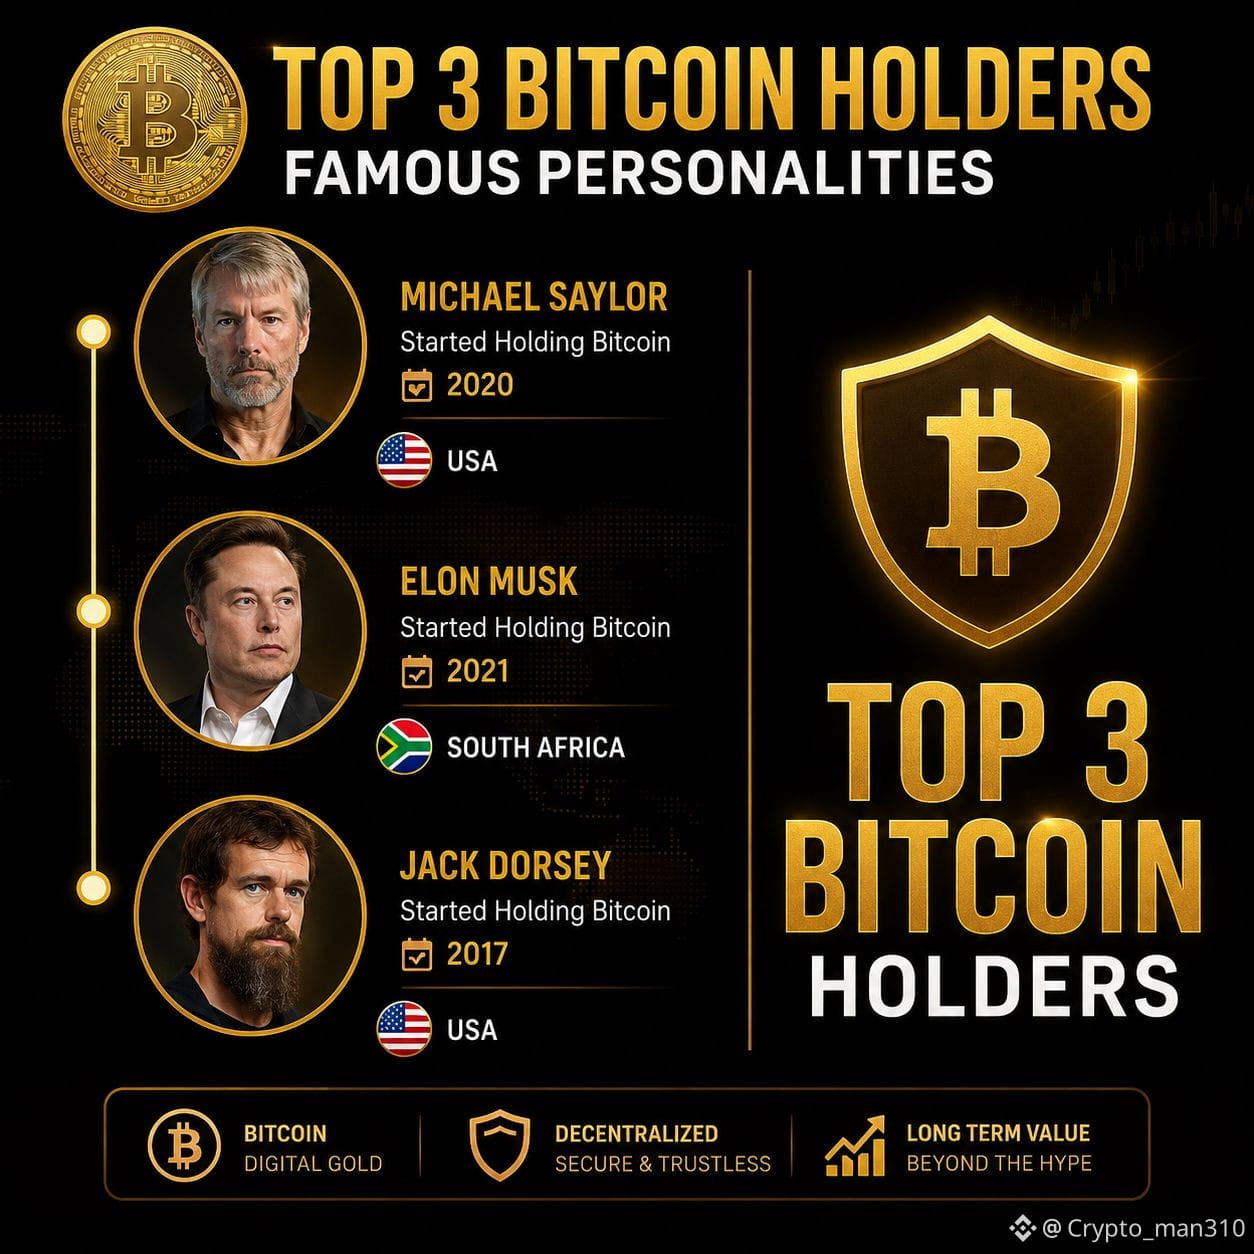
🌍 Top 3 Countries Holding $BTC (Government Reserves)
🥇 1. United States – Approximately 329,000 BTC
🥈 2. China – Approximately 190,000 BTC
🥉 3. United Kingdom – Approximately 61,000 BTC
👑 Famous Bitcoin Holders
🔹 Michael Saylor • Started accumulating Bitcoin in 2020 • One of the strongest Bitcoin advocates in the world • Has publicly stated he continues to hold and buy Bitcoin
🔹 Elon Musk • Publicly confirmed Bitcoin ownership in 2021 • Tesla and SpaceX also hold Bitcoin on their balance sheets
🔹 Jack Dorsey • Bitcoin supporter since at least 2017 • Regular Bitcoin buyer and long-term holder
#ElonMusk. #JackDorsey #MichaelSaylor #BTC突破7万大关
$BTC
{spot}(BTCUSDT)
🌍 Top 3 Countries Holding $BTC (Government Reserves)
🥇 1. United States – Approximately 329,000 BTC
🥈 2. China – Approximately 190,000 BTC
🥉 3. United Kingdom – Approximately 61,000 BTC
👑 Famous Bitcoin Holders
🔹 Michael Saylor • Started accumulating Bitcoin in 2020 • One of the strongest Bitcoin advocates in the world • Has publicly stated he continues to hold and buy Bitcoin
🔹 Elon Musk • Publicly confirmed Bitcoin ownership in 2021 • Tesla and SpaceX also hold Bitcoin on their balance sheets
🔹 Jack Dorsey • Bitcoin supporter since at least 2017 • Regular Bitcoin buyer and long-term holder
#ElonMusk. #JackDorsey #MichaelSaylor #BTC突破7万大关
$BTC
1
185
·
--
Bullish


Binance News
·
--
AI TRENDS | Jack Dorsey Launches Open-Source Decentralized Chat App Buzz
Bitcoin Magazine reported that tech entrepreneur Jack Dorsey has announced a new group chat platform called Buzz, aimed at reducing teams' reliance on Slack, in the Bitcoin maximalist's latest push for decentralization.Block's co-founder wrote on X that Buzz is for teams of people and agents of all sizes and is model-agnostic, decentralized, self-sovereign, and open source. The app is described on its website as a native workspace for human and agent teams, where users can chat with teammates and specialized agents in one shared space, then move into planning, project management, coding, and PRs.Block said the app was built on the decentralized social networking Nostr protocol. The interface will feel familiar to anyone who has used a modern team communication tool, the company added.Bradley Axen, head of AI capabilities at Block, said every company will need a place where humans and agents work together. He said the question is whether that place is proprietary or open, and Block built Buzz because it believes it should be open.Dorsey has long pushed for decentralized solutions, primarily through Bitcoin. The billionaire Twitter founder left the social media company in 2021 to focus on payments and Bitcoin adoption, saying he wants the cryptocurrency to be the global currency and everyday money. He has described Satoshi Nakamoto's Bitcoin white paper as poetry.Cash App allows users to buy, sell, send, and receive Bitcoin, and Square point-of-sale terminals accept BTC via the Lightning Network. Block also debuted a Bitcoin mining rig with swappable parts last year.

76
·
--

Article
Jack Dorsey launches a new and quirky payment tool!@CashApp announced the launch of Cash App Wand, a new version of the Cash App card featuring a starry design and supporting tap-to-pay transactions.
✨ Key features:
🔹 Pay with a simple tap. 🔹 Customizable design. 🔹 A payment experience unlike traditional cards.
But what makes this news even more exciting is the entity behind it...
🏦 Cash App is owned by Block, one of the biggest Bitcoin whales in the world.
Jack Dorsey launches a new and quirky payment tool!
@CashApp announced the launch of Cash App Wand, a new version of the Cash App card featuring a starry design and supporting tap-to-pay transactions.
✨ Key features:
🔹 Pay with a simple tap. 🔹 Customizable design. 🔹 A payment experience unlike traditional cards.
But what makes this news even more exciting is the entity behind it...
🏦 Cash App is owned by Block, one of the biggest Bitcoin whales in the world.
✨ Key features:
🔹 Pay with a simple tap. 🔹 Customizable design. 🔹 A payment experience unlike traditional cards.
But what makes this news even more exciting is the entity behind it...
🏦 Cash App is owned by Block, one of the biggest Bitcoin whales in the world.
2
119
·
--
Block joins the wave of applications for U.S. federal banking charters, planning to establish a Bitcoin and stablecoin custody trust bank. #Block #JackDorsey #BTC
Block joins the wave of applications for U.S. federal banking charters, planning to establish a Bitcoin and stablecoin custody trust bank. #Block #JackDorsey #BTC
116
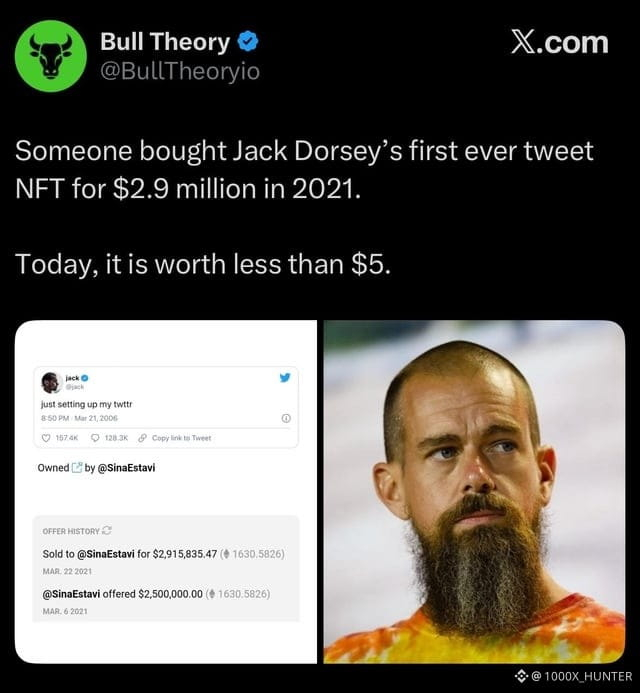
🚨#JackDorsey
Someone bought Jack Dorsey’s first ever tweet NFT for $2.9 million in 2021 - Today, it is worth less than
Initial Purchase (2021): Sina Estavi, CEO of Bridge Oracle, bought the "just setting up my twttr" NFT for 1,630.5 ether, valued at roughly $2.9 million.
Failed Resale (2022): Estavi listed the NFT for $48 million in 2022, but the highest bid received was only $280.
Current Value (2026): By 2026, the market value has plunged to under $5, often cited as a prime example of the extreme volatility and decline in the NFT market post-boom.
$XAU $ETH $DASH
#BinanceOnline #ClarityActDraft #HotCPIBitcoinPressure #BhutanCryptoFastTrackLicensing
2
430
·
--
Bullish
🚨 THE BITCOIN STANDARD IS HERE: Jack Dorsey’s Block ($SQ) Drops a MASSIVE Q1 2026 Power Move! 🐋$DYM
Jack Dorsey isn’t just talking about the future of finance—he’s aggressively buying it. 🧱$ACE
The Q1 2026 earnings report for Block ($SQ) just dropped, and it is a massive wake-up call for anyone still on the sidelines. While retail hesitates, institutional smart money is quietly and ruthlessly accumulating.$SAHARA
Here is the ultimate power move Dorsey just pulled off:
📌 The Mega-Stash: Block’s treasury now holds a staggering 9,032 BTC.
📌 The Q1 Accumulation: They didn't stop there. Block scooped up another 149 BTC this quarter. The strategy is simple: never stop stacking sats.
📌 The Financial Flex: A jaw-dropping $2.9 BILLION in gross profit—a massive 27% surge.
This isn’t just a routine balance sheet update. This is the Bitcoin Standard playing out in real-time by a major tech heavyweight. The blueprint is set: generate massive fiat revenue, and immediately convert the profits into hard, pristine asset. 🚀
When billionaires and mega-corporations are dollar-cost averaging into Bitcoin at this scale, you have to ask yourself—are you accumulating, or are you getting left behind?
{spot}(DYMUSDT)
{spot}(ACEUSDT)
{spot}(BTCUSDT)
👇 Let’s hear your take: Will we see more Wall Street giants copy Jack Dorsey’s corporate Bitcoin strategy in 2026?
If you found this alpha valuable, hit that Like button and Follow for daily elite crypto insights!
#BlackRockPlansMoneyMarketFundsforStablecoinUsers #JackDorsey #CryptoNews🔒📰🚫 #NewsAboutCrypto
🚨 THE BITCOIN STANDARD IS HERE: Jack Dorsey’s Block ($SQ) Drops a MASSIVE Q1 2026 Power Move! 🐋$DYM
Jack Dorsey isn’t just talking about the future of finance—he’s aggressively buying it. 🧱$ACE
The Q1 2026 earnings report for Block ($SQ) just dropped, and it is a massive wake-up call for anyone still on the sidelines. While retail hesitates, institutional smart money is quietly and ruthlessly accumulating.$SAHARA
Here is the ultimate power move Dorsey just pulled off:
📌 The Mega-Stash: Block’s treasury now holds a staggering 9,032 BTC.
📌 The Q1 Accumulation: They didn't stop there. Block scooped up another 149 BTC this quarter. The strategy is simple: never stop stacking sats.
📌 The Financial Flex: A jaw-dropping $2.9 BILLION in gross profit—a massive 27% surge.
This isn’t just a routine balance sheet update. This is the Bitcoin Standard playing out in real-time by a major tech heavyweight. The blueprint is set: generate massive fiat revenue, and immediately convert the profits into hard, pristine asset. 🚀
When billionaires and mega-corporations are dollar-cost averaging into Bitcoin at this scale, you have to ask yourself—are you accumulating, or are you getting left behind?
👇 Let’s hear your take: Will we see more Wall Street giants copy Jack Dorsey’s corporate Bitcoin strategy in 2026?
If you found this alpha valuable, hit that Like button and Follow for daily elite crypto insights!
#BlackRockPlansMoneyMarketFundsforStablecoinUsers #JackDorsey #CryptoNews🔒📰🚫 #NewsAboutCrypto
4
2
248
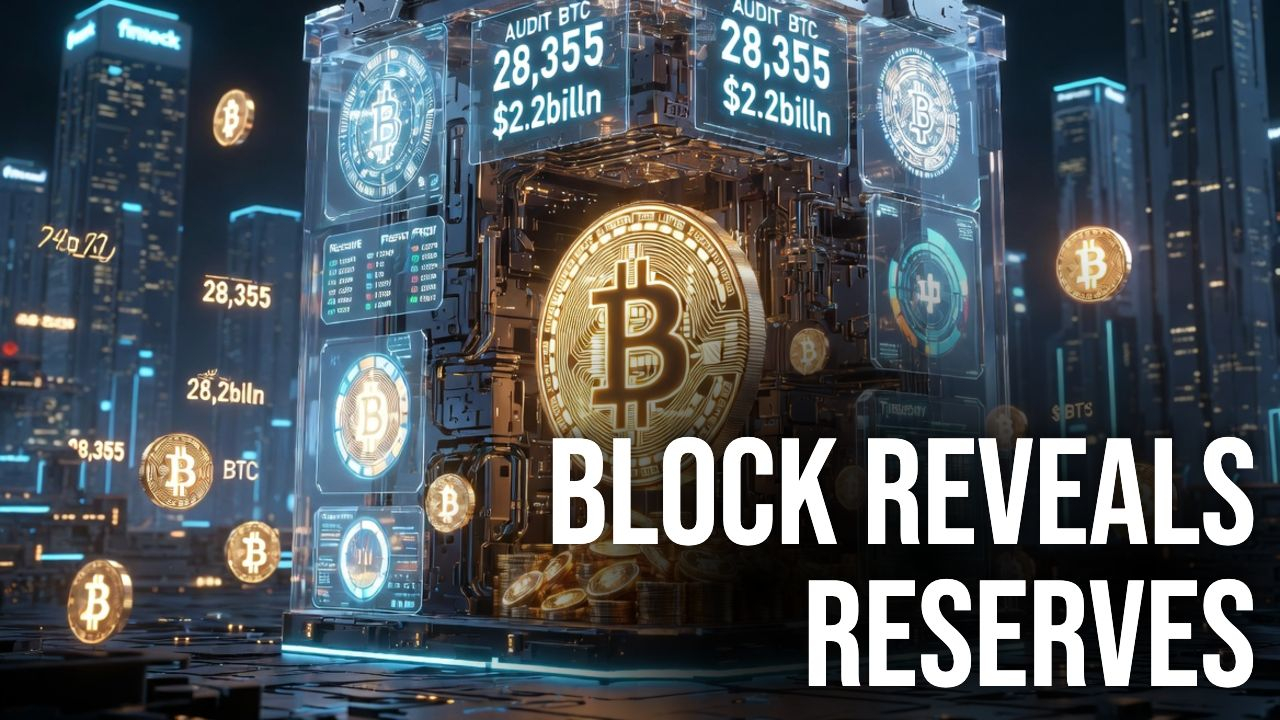
Jack Dorsey’s Block just revealed $2.2B in Bitcoin holdings 🐂
28,355 BTC backed by Proof-of-Reserves transparency — a massive trust signal for crypto 🚀
Institutional Bitcoin conviction keeps getting louder.
Follow for more alpha 👇
#Bitcoin #BTC #Crypto #JackDorsey #bitinsider
Jack Dorsey’s Block just revealed $2.2B in Bitcoin holdings 🐂
28,355 BTC backed by Proof-of-Reserves transparency — a massive trust signal for crypto 🚀
Institutional Bitcoin conviction keeps getting louder.
Follow for more alpha 👇
#Bitcoin #BTC #Crypto #JackDorsey #bitinsider
28,355 BTC backed by Proof-of-Reserves transparency — a massive trust signal for crypto 🚀
Institutional Bitcoin conviction keeps getting louder.
Follow for more alpha 👇
#Bitcoin #BTC #Crypto #JackDorsey #bitinsider
1
1
104
·
--
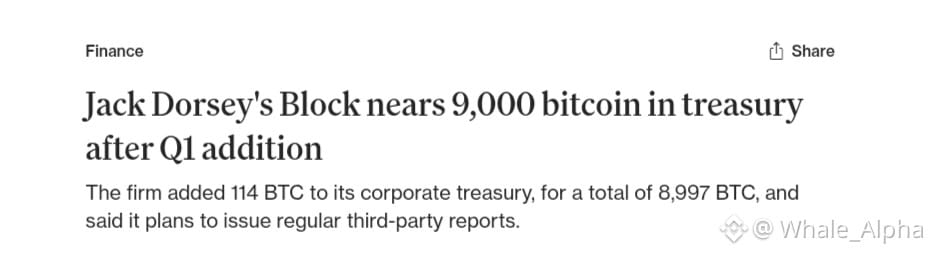
While the retail traders are panicking over small dips, the real Whales are silently filling their bags. #jackDorseyBlock has just added more Bitcoin to its treasury, nearing a massive 9,000 BITCOIN milestone. The institutional conviction in $BTC has never been stronger🛡️
Block's Treasury: Total holdings hit 8,997 BTC. Total responsibility is a staggering 28,355 BTC worth $2.2 Billion.
$CHZ Expansion: CHZ is moving to Solana & Base to supercharge fan tokens before the World Cup fever starts. This is a massive ecosystem play🎯
Inflation Hedge:Billionaire Paul Tudor Jones just called Bitcoin the 'Best Inflation Hedge' again. The macro narrative is aligning perfectly for the next leg up. 🏛️⚡
#Bitcoin #JackDorsey #Chiliz #InstitutionalBuying #Write2Earn 🚀🎯
$ZKJ
{spot}(CHZUSDT)
{spot}(BTCUSDT)
{future}(ZKJUSDT)
While the retail traders are panicking over small dips, the real Whales are silently filling their bags. #jackDorseyBlock has just added more Bitcoin to its treasury, nearing a massive 9,000 BITCOIN milestone. The institutional conviction in $BTC has never been stronger🛡️
Block's Treasury: Total holdings hit 8,997 BTC. Total responsibility is a staggering 28,355 BTC worth $2.2 Billion.
$CHZ Expansion: CHZ is moving to Solana & Base to supercharge fan tokens before the World Cup fever starts. This is a massive ecosystem play🎯
Inflation Hedge:Billionaire Paul Tudor Jones just called Bitcoin the 'Best Inflation Hedge' again. The macro narrative is aligning perfectly for the next leg up. 🏛️⚡
#Bitcoin #JackDorsey #Chiliz #InstitutionalBuying #Write2Earn 🚀🎯
$ZKJ
3
2
363

Article
🚨Shocking😱India Joins China in Cracking Down on Bitchat
👇India has reportedly ordered action against Bitchat, Jack Dorsey's decentralized Bluetooth messaging app, citing national security concerns. The move follows similar restrictions by China, highlighting the growing global debate between privacy and government oversight.
As decentralized technologies continue to evolve, regulators around the world are increasing their scrutiny of tools that operate outside traditional internet infrastructure.
#Binance #crypto #Web3 #bitchat #JackDorsey
{spot}(NVDABUSDT)
$BTC
{spot}(BTCUSDT)
$AAPL.US
{stock_us}(AAPL.US)
🚨Shocking😱India Joins China in Cracking Down on Bitchat 👇
India has reportedly ordered action against Bitchat, Jack Dorsey's decentralized Bluetooth messaging app, citing national security concerns. The move follows similar restrictions by China, highlighting the growing global debate between privacy and government oversight.
As decentralized technologies continue to evolve, regulators around the world are increasing their scrutiny of tools that operate outside traditional internet infrastructure.
#Binance #crypto #Web3 #bitchat #JackDorsey
$BTC
$AAPL.US
As decentralized technologies continue to evolve, regulators around the world are increasing their scrutiny of tools that operate outside traditional internet infrastructure.
#Binance #crypto #Web3 #bitchat #JackDorsey
$BTC
$AAPL.US
84
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#MetaMaskExitsLidoValidatorsAfterSecurityIncident
914 views
62 Discussing
2
#MicronBeatsEarningsLiftsGuidance
3,043 views
88 Discussing
3
#CFTCSubmitsTwoEventContractRulesToWhiteHouse
3,959 views
118 Discussing
4
#BitcoinClears$85200
23,541 views
278 Discussing
5
#AltcoinSeasonIndexHoldsAbove60For5Days
120,176 views
1,569 Discussing
6
#USADPAdds90000JobsInSeptember
52,210 views
881 Discussing
7
#USCorePCEEasesTo3%InAugust
38,493 views
634 Discussing
8
#KospiPostsWorstQuarterSince2020
22,606 views
563 Discussing
9
#SECToClarifyOnChainFundraisingRules
57,428 views
754 Discussing
10
#UKFCAOpensCryptoFirmAuthorization
54,132 views
614 Discussing