
#hack
hack
1.4M views
1,385 Discussing
Hot
Latest
·
--
$891 million in stolen funds transferredAccording to monitoring by Onchain Lens, the Binance hacker has transferred or laundered nearly $900 million in stolen funds. Of the total estimated stolen funds of $6.34 billion: $891.37 million has likely been transferred or laundered; $2.85 billion remains under the hacker’s control; and $2.6 billion has been frozen. Over the past 2 to 3 days, the hacker has been actively moving funds via THORChain and Chainflip.#Binance #Hack $BNB $BTC
$891 million in stolen funds transferred
According to monitoring by Onchain Lens, the Binance hacker has transferred or laundered nearly $900 million in stolen funds. Of the total estimated stolen funds of $6.34 billion: $891.37 million has likely been transferred or laundered; $2.85 billion remains under the hacker’s control; and $2.6 billion has been frozen. Over the past 2 to 3 days, the hacker has been actively moving funds via THORChain and Chainflip.#Binance #Hack $BNB $BTC
516
🚨 ALERT: An ongoing exploit has drained ~$292K from Ankr’s Ethereum bridge, per Blockaid.
#Ethereum $ETH #Hack
🚨 ALERT: An ongoing exploit has drained ~$292K from Ankr’s Ethereum bridge, per Blockaid.
#Ethereum $ETH #Hack
#Ethereum $ETH #Hack
53
·
--
Feed-Creator-77f209622:
последний гвоздь в крышку гроба osmo and cosmos /atom/
1
1
455

·
--
The FBI just named who it blames for the record $6.34B Binance hack: North Korea's TraderTraitor group.
TRM Labs says DPRK-linked hackers have stolen $12.8B in digital assets since 2017.
That means roughly half of all their lifetime haul came from one incident. Security, not price, is the story driving exchange sentiment right now.
Watch for: proof-of-reserves updates, withdrawal behavior, and whether users shift more funds to self-custody.
Do you keep most of your crypto on an exchange or in self-custody? Why?
$BNB $BTC
#Binance #CryptoSecurity #Hack #Square
The FBI just named who it blames for the record $6.34B Binance hack: North Korea's TraderTraitor group.
TRM Labs says DPRK-linked hackers have stolen $12.8B in digital assets since 2017.
That means roughly half of all their lifetime haul came from one incident. Security, not price, is the story driving exchange sentiment right now.
Watch for: proof-of-reserves updates, withdrawal behavior, and whether users shift more funds to self-custody.
Do you keep most of your crypto on an exchange or in self-custody? Why?
$BNB $BTC
#Binance #CryptoSecurity #Hack #Square
TRM Labs says DPRK-linked hackers have stolen $12.8B in digital assets since 2017.
That means roughly half of all their lifetime haul came from one incident. Security, not price, is the story driving exchange sentiment right now.
Watch for: proof-of-reserves updates, withdrawal behavior, and whether users shift more funds to self-custody.
Do you keep most of your crypto on an exchange or in self-custody? Why?
$BNB $BTC
#Binance #CryptoSecurity #Hack #Square
17
Article
🚨 INITIA SUFFERS AN ATTACK AND LOSES US$ 3.27 MILLION!Initia confirmed a security breach following the compromise of cloud credentials. The attack enabled fraudulent transfers across five Rollups, while another US$ 2.16 million remained temporarily locked on the network.
The team promises to fully replenish the affected reserves and is already working to strengthen security, but there is still no timeline for recovery.
⚠️ Could this incident affect investor confidence in Initia?
I’d like to hear your thoughts!
🚨 INITIA SUFFERS AN ATTACK AND LOSES US$ 3.27 MILLION!
Initia confirmed a security breach following the compromise of cloud credentials. The attack enabled fraudulent transfers across five Rollups, while another US$ 2.16 million remained temporarily locked on the network.
The team promises to fully replenish the affected reserves and is already working to strengthen security, but there is still no timeline for recovery.
⚠️ Could this incident affect investor confidence in Initia?
I’d like to hear your thoughts!
The team promises to fully replenish the affected reserves and is already working to strengthen security, but there is still no timeline for recovery.
⚠️ Could this incident affect investor confidence in Initia?
I’d like to hear your thoughts!
1
430
·
--
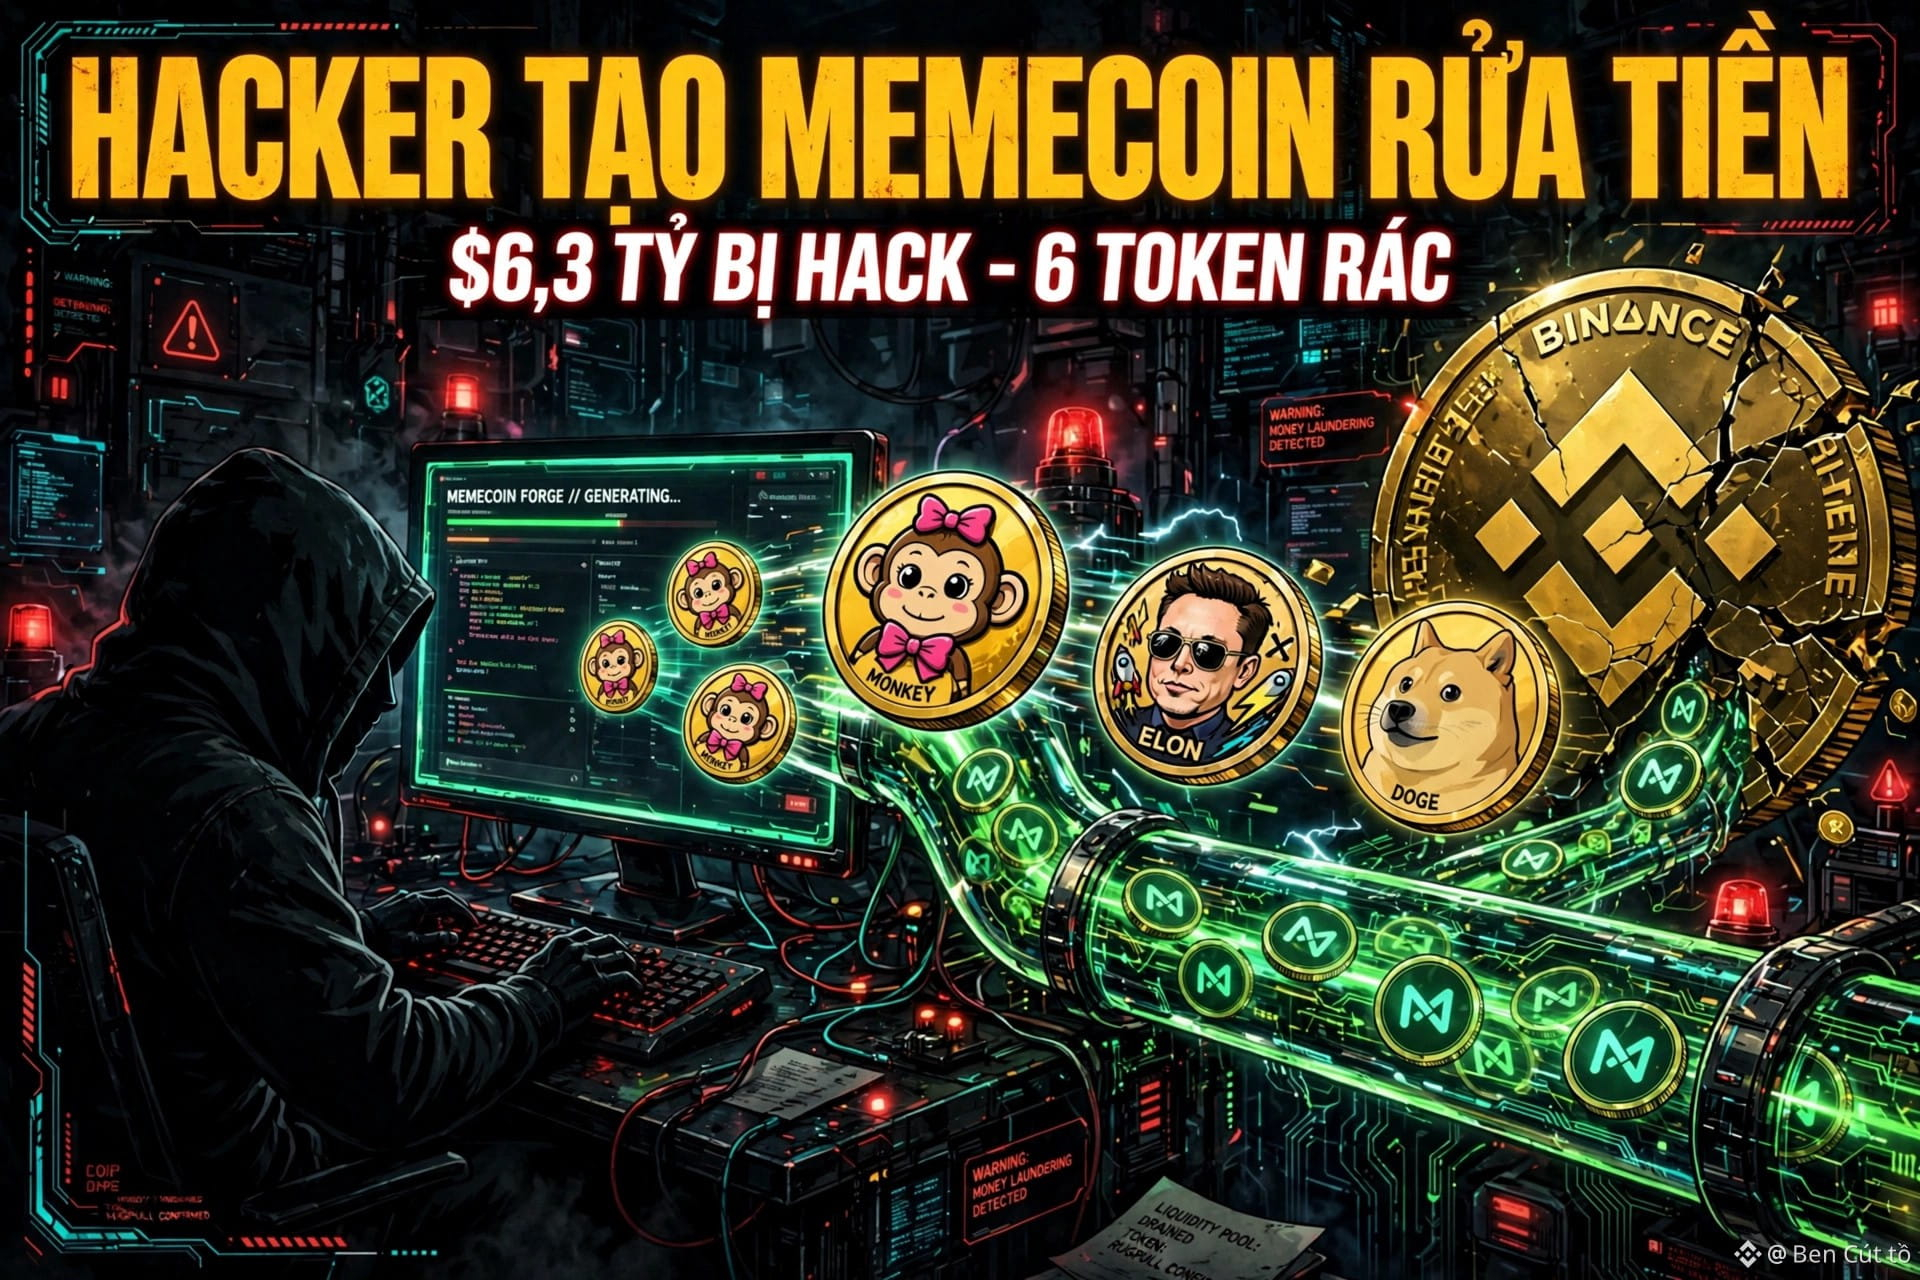
🚨 BREAKING NEWS: North Korean hackers created their own memecoins to launder money from the $6.3 billion Binance hack!
Elliptic has just exposed their latest scheme: from Nov. 5–7, the TraderTraitor group created 6 memecoins on $NEAR —FUK, MEILI, SINU... Each token cost only about $90 to create. Then they bought and sold them among themselves through liquidity pools to turn stolen funds into “trading profits.”
117,000 NEAR (about $430,000) passed through these 6 junk tokens. But this is still less than 0.01% of the total amount stolen — 11.8 million NEAR (about $43.7 million) remains untouched.
Binance $BNB said it has recovered about 98% of the losses. But this homemade memecoin laundering scheme shows that hackers are getting more creative — and more dangerous than ever.
Be careful with unfamiliar memecoins. Follow me — I post here first.
#Binance #Hack #NEAR
🚨 BREAKING NEWS: North Korean hackers created their own memecoins to launder money from the $6.3 billion Binance hack!
Elliptic has just exposed their latest scheme: from Nov. 5–7, the TraderTraitor group created 6 memecoins on $NEAR —FUK, MEILI, SINU... Each token cost only about $90 to create. Then they bought and sold them among themselves through liquidity pools to turn stolen funds into “trading profits.”
117,000 NEAR (about $430,000) passed through these 6 junk tokens. But this is still less than 0.01% of the total amount stolen — 11.8 million NEAR (about $43.7 million) remains untouched.
Binance $BNB said it has recovered about 98% of the losses. But this homemade memecoin laundering scheme shows that hackers are getting more creative — and more dangerous than ever.
Be careful with unfamiliar memecoins. Follow me — I post here first.
#Binance #Hack #NEAR
Elliptic has just exposed their latest scheme: from Nov. 5–7, the TraderTraitor group created 6 memecoins on $NEAR —FUK, MEILI, SINU... Each token cost only about $90 to create. Then they bought and sold them among themselves through liquidity pools to turn stolen funds into “trading profits.”
117,000 NEAR (about $430,000) passed through these 6 junk tokens. But this is still less than 0.01% of the total amount stolen — 11.8 million NEAR (about $43.7 million) remains untouched.
Binance $BNB said it has recovered about 98% of the losses. But this homemade memecoin laundering scheme shows that hackers are getting more creative — and more dangerous than ever.
Be careful with unfamiliar memecoins. Follow me — I post here first.
#Binance #Hack #NEAR
Tony Dong 2020:
Đây là đâu ben
1
3
5.8k
·
--
This sounds made up, but it actually happened😂😂
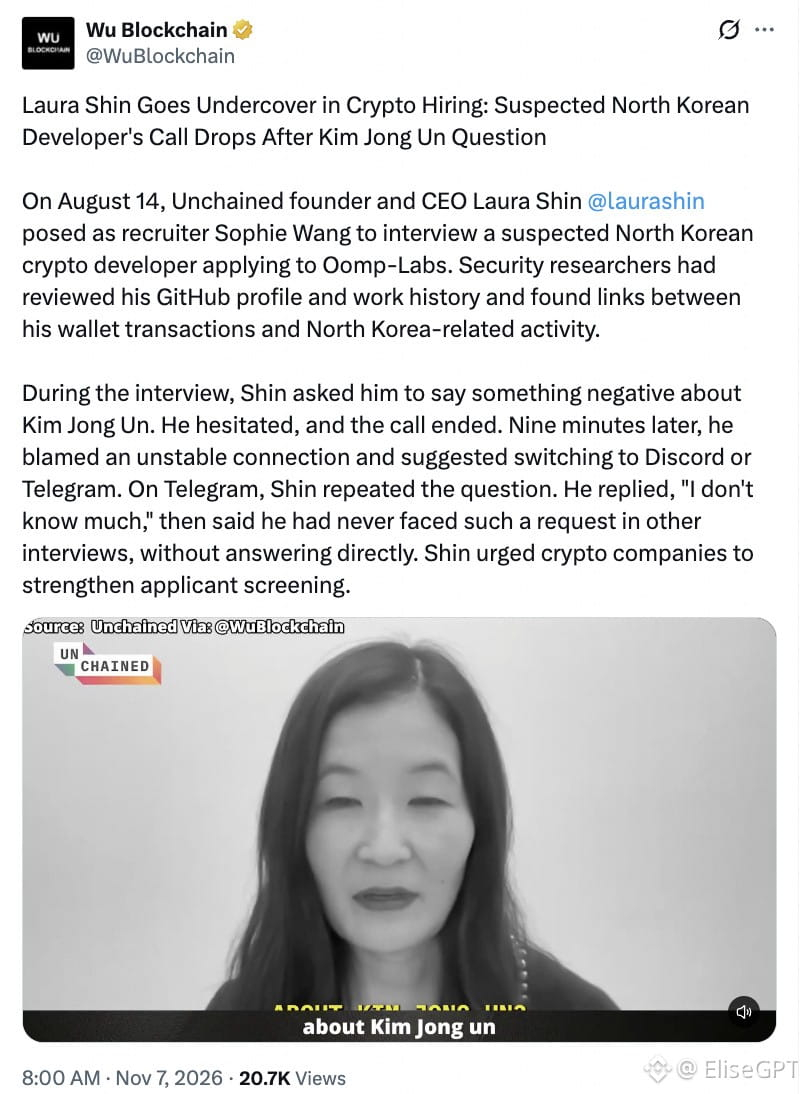
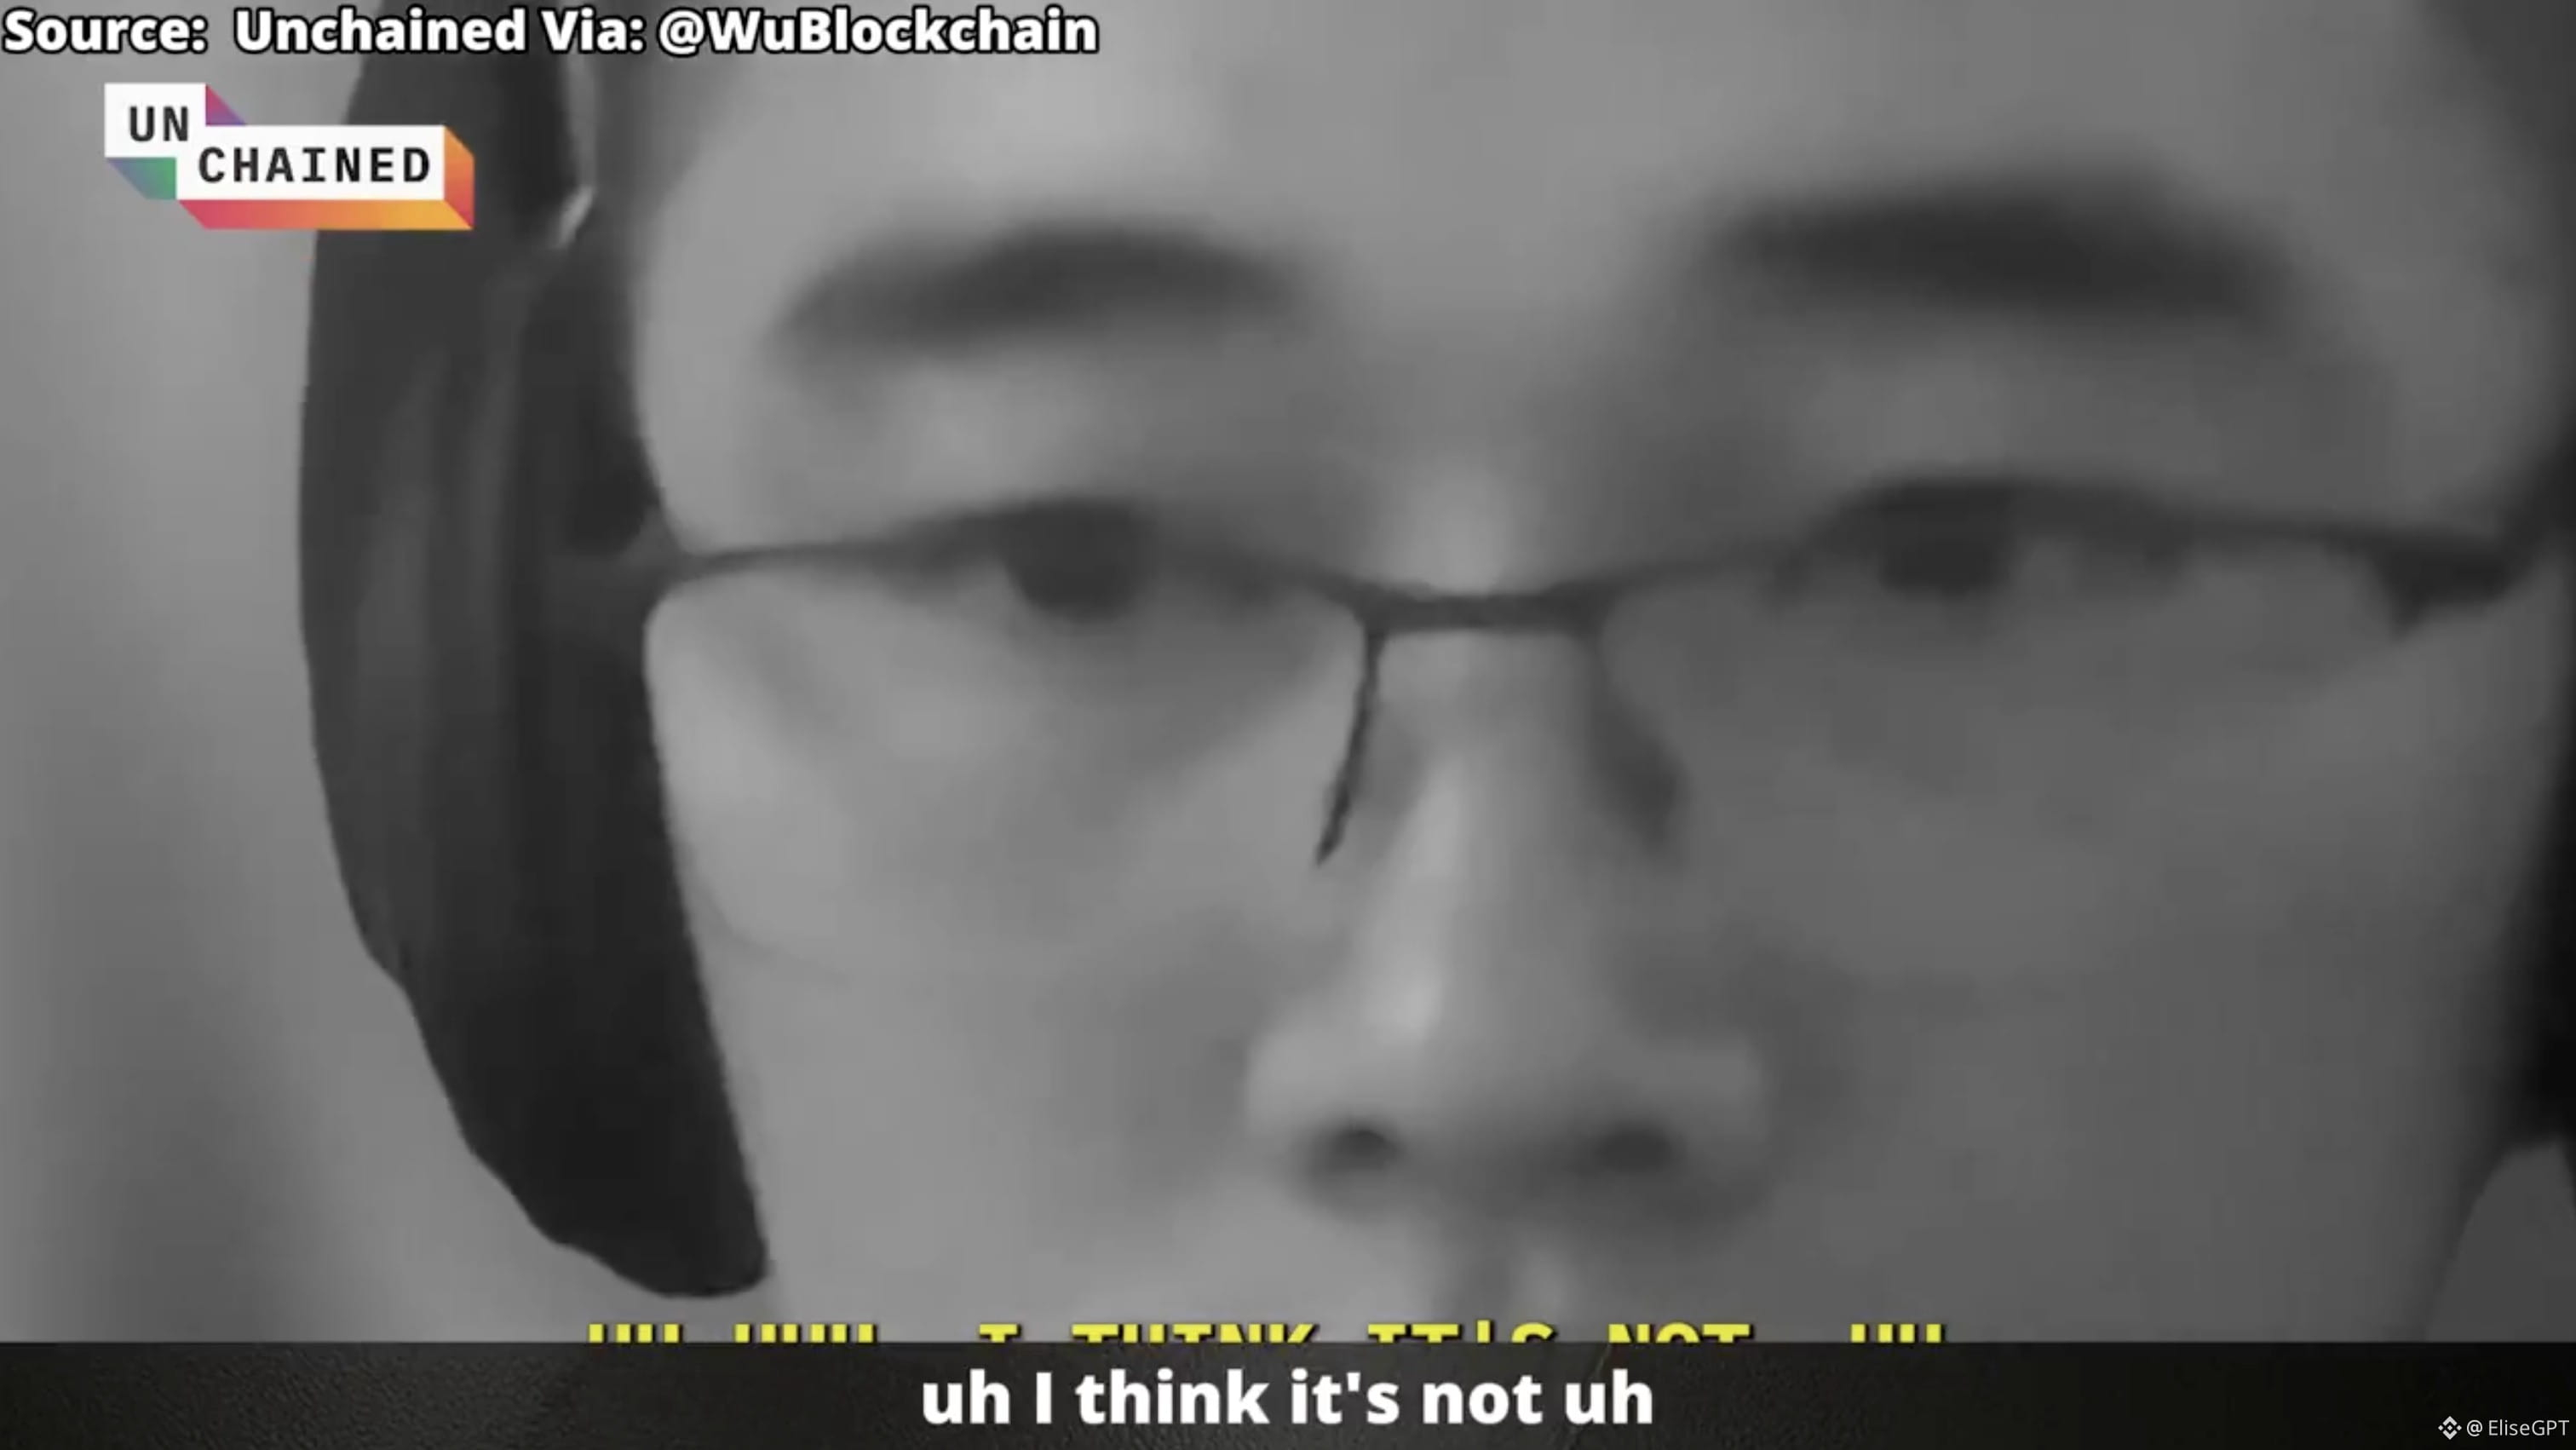
Back in August, Unchained founder Laura Shin posed as a recruiter to interview a suspected North Korean crypto developer.
During the interview, she asked him to say something negative about Kim Jong Un. He stumbled over his words, then the call cut out. Afterward, he kept coming up with excuses to avoid answering.
So is “say something bad about Kim Jong Un” about to become a standard question in remote job interviews? 🤣 The new screening test for North Korean hackers, lol #AI #Hack
This sounds made up, but it actually happened😂😂
Back in August, Unchained founder Laura Shin posed as a recruiter to interview a suspected North Korean crypto developer.
During the interview, she asked him to say something negative about Kim Jong Un. He stumbled over his words, then the call cut out. Afterward, he kept coming up with excuses to avoid answering.
So is “say something bad about Kim Jong Un” about to become a standard question in remote job interviews? 🤣 The new screening test for North Korean hackers, lol #AI #Hack
Back in August, Unchained founder Laura Shin posed as a recruiter to interview a suspected North Korean crypto developer.
During the interview, she asked him to say something negative about Kim Jong Un. He stumbled over his words, then the call cut out. Afterward, he kept coming up with excuses to avoid answering.
So is “say something bad about Kim Jong Un” about to become a standard question in remote job interviews? 🤣 The new screening test for North Korean hackers, lol #AI #Hack
User-6279aa89:
Follow me and I’ll follow you back; let’s grow together on Binance Square. newbies
8
51
46.2k
·
--
🚨 BREAKING: Brazil’s BIGGEST crypto exchange just had its hot wallets completely drained!
Mercado Bitcoin froze withdrawals starting Nov 2, after hackers drained 36,042 ETH deposit addresses in just 4.5 hours — with estimated losses of $40–46 million, spanning at least 10 blockchains.
Today, Nov 9, the exchange has reopened... but ONLY for viewing balances. Deposits, withdrawals, and trading are still completely locked, with no reopening date announced. Tether has already managed to freeze more than 4.5 million USDT.
The twist: $BTC barely moved — still hovering around $76,000, just above the 200-day moving average. Has the market become numb to hacks, or is the storm still waiting to break?
The exchange promises to compensate users out of its own pocket. Believe it if you want.
Save this — next time an exchange says “absolute security,” remember this story.
Follow me; I post here first. 🔥
#Bitcoin #Hack
🚨 BREAKING: Brazil’s BIGGEST crypto exchange just had its hot wallets completely drained!
Mercado Bitcoin froze withdrawals starting Nov 2, after hackers drained 36,042 ETH deposit addresses in just 4.5 hours — with estimated losses of $40–46 million, spanning at least 10 blockchains.
Today, Nov 9, the exchange has reopened... but ONLY for viewing balances. Deposits, withdrawals, and trading are still completely locked, with no reopening date announced. Tether has already managed to freeze more than 4.5 million USDT.
The twist: $BTC barely moved — still hovering around $76,000, just above the 200-day moving average. Has the market become numb to hacks, or is the storm still waiting to break?
The exchange promises to compensate users out of its own pocket. Believe it if you want.
Save this — next time an exchange says “absolute security,” remember this story.
Follow me; I post here first. 🔥
#Bitcoin #Hack
Mercado Bitcoin froze withdrawals starting Nov 2, after hackers drained 36,042 ETH deposit addresses in just 4.5 hours — with estimated losses of $40–46 million, spanning at least 10 blockchains.
Today, Nov 9, the exchange has reopened... but ONLY for viewing balances. Deposits, withdrawals, and trading are still completely locked, with no reopening date announced. Tether has already managed to freeze more than 4.5 million USDT.
The twist: $BTC barely moved — still hovering around $76,000, just above the 200-day moving average. Has the market become numb to hacks, or is the storm still waiting to break?
The exchange promises to compensate users out of its own pocket. Believe it if you want.
Save this — next time an exchange says “absolute security,” remember this story.
Follow me; I post here first. 🔥
#Bitcoin #Hack
3
3.5k
·
--
#Hack
In Cybersecurity and Computing
A hack is a technique, method, or procedure designed to modify the normal operation of a computer system, device, or program, often to achieve an objective that its creators did not originally or intentionally anticipate.
Hardware and Device Modifications
In the field of electronics and physical devices, a hack refers to adapting or modifying equipment (such as video game consoles, phones, development boards, or household appliances) to unlock hidden features, change the operating system (firmware), or repair components using alternative parts.
Everyday Use: “Lifehacks”
Outside of pure technology, the word became popular as “lifehack,” referring to household tricks, shortcuts, or clever methods that make everyday life more efficient and easier by using resources already on hand.
It is very important to separate myth from reality: the blockchain itself is extremely difficult to hack due to its decentralized and cryptographic structure. However, the crypto ecosystem is surrounded by applications, platforms, and users, and that is where attackers find vulnerabilities to exploit.
Attacks on Exchanges and Centralized Platforms
Although cryptocurrencies are decentralized, millions of users store their money on centralized exchange platforms (exchanges).
Exploitation of “Bridges” (Cross-Chain Bridges)
Bridges are protocols that allow cryptocurrencies to be transferred from one blockchain to another (for example, moving funds from Ethereum to BNB Chain).
Phishing and Theft of Users’ Private Keys
At the individual level, the vast majority of “hacks” do not happen by breaking the network’s security, but by deceiving people.
#Hack
In Cybersecurity and Computing
A hack is a technique, method, or procedure designed to modify the normal operation of a computer system, device, or program, often to achieve an objective that its creators did not originally or intentionally anticipate.
Hardware and Device Modifications
In the field of electronics and physical devices, a hack refers to adapting or modifying equipment (such as video game consoles, phones, development boards, or household appliances) to unlock hidden features, change the operating system (firmware), or repair components using alternative parts.
Everyday Use: “Lifehacks”
Outside of pure technology, the word became popular as “lifehack,” referring to household tricks, shortcuts, or clever methods that make everyday life more efficient and easier by using resources already on hand.
It is very important to separate myth from reality: the blockchain itself is extremely difficult to hack due to its decentralized and cryptographic structure. However, the crypto ecosystem is surrounded by applications, platforms, and users, and that is where attackers find vulnerabilities to exploit.
Attacks on Exchanges and Centralized Platforms
Although cryptocurrencies are decentralized, millions of users store their money on centralized exchange platforms (exchanges).
Exploitation of “Bridges” (Cross-Chain Bridges)
Bridges are protocols that allow cryptocurrencies to be transferred from one blockchain to another (for example, moving funds from Ethereum to BNB Chain).
Phishing and Theft of Users’ Private Keys
At the individual level, the vast majority of “hacks” do not happen by breaking the network’s security, but by deceiving people.
In Cybersecurity and Computing
A hack is a technique, method, or procedure designed to modify the normal operation of a computer system, device, or program, often to achieve an objective that its creators did not originally or intentionally anticipate.
Hardware and Device Modifications
In the field of electronics and physical devices, a hack refers to adapting or modifying equipment (such as video game consoles, phones, development boards, or household appliances) to unlock hidden features, change the operating system (firmware), or repair components using alternative parts.
Everyday Use: “Lifehacks”
Outside of pure technology, the word became popular as “lifehack,” referring to household tricks, shortcuts, or clever methods that make everyday life more efficient and easier by using resources already on hand.
It is very important to separate myth from reality: the blockchain itself is extremely difficult to hack due to its decentralized and cryptographic structure. However, the crypto ecosystem is surrounded by applications, platforms, and users, and that is where attackers find vulnerabilities to exploit.
Attacks on Exchanges and Centralized Platforms
Although cryptocurrencies are decentralized, millions of users store their money on centralized exchange platforms (exchanges).
Exploitation of “Bridges” (Cross-Chain Bridges)
Bridges are protocols that allow cryptocurrencies to be transferred from one blockchain to another (for example, moving funds from Ethereum to BNB Chain).
Phishing and Theft of Users’ Private Keys
At the individual level, the vast majority of “hacks” do not happen by breaking the network’s security, but by deceiving people.
97

Trump Responds to Binance Hack Investigation
U.S. President Donald Trump is reportedly looking into the recent Binance hack, according to Bloomberg.
The development brings additional attention to the security incident and could raise questions about crypto exchange security, cybersecurity risks, and the protection of digital assets.
As the situation develops, the market will be watching closely for further details and any potential regulatory response.
Crypto security remains a major issue for the industry.
#Binance / #Hack / #TRUMP
Trump Responds to Binance Hack Investigation
U.S. President Donald Trump is reportedly looking into the recent Binance hack, according to Bloomberg.
The development brings additional attention to the security incident and could raise questions about crypto exchange security, cybersecurity risks, and the protection of digital assets.
As the situation develops, the market will be watching closely for further details and any potential regulatory response.
Crypto security remains a major issue for the industry.
#Binance / #Hack / #TRUMP
U.S. President Donald Trump is reportedly looking into the recent Binance hack, according to Bloomberg.
The development brings additional attention to the security incident and could raise questions about crypto exchange security, cybersecurity risks, and the protection of digital assets.
As the situation develops, the market will be watching closely for further details and any potential regulatory response.
Crypto security remains a major issue for the industry.
#Binance / #Hack / #TRUMP
2
803
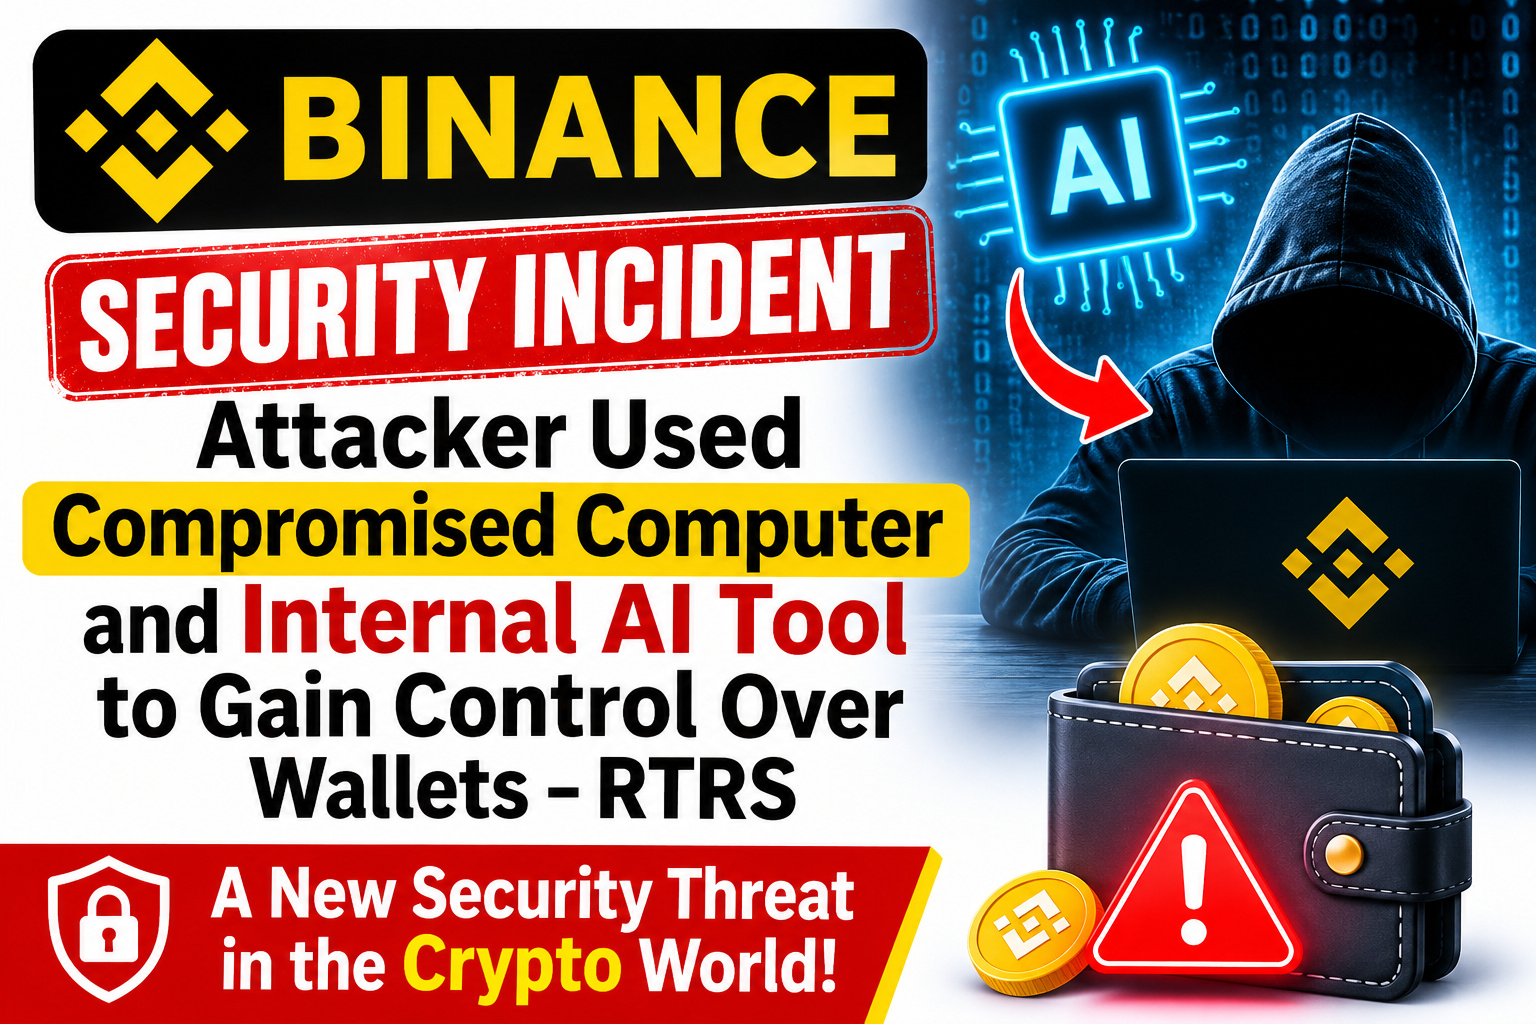
Binance Security Incident Raises Serious Questions About AI and Wallet Protection
A reported security incident involving Binance has highlighted a new and concerning type of cybersecurity threat.
According to Reuters, the attacker allegedly exploited a compromised computer and used an internal AI tool to gain control over wallets.
What makes this incident particularly concerning is the reported combination of compromised devices, AI-assisted access, and wallet security vulnerabilities. It shows how attackers may use legitimate internal tools as part of sophisticated cyberattacks.
As AI becomes more deeply integrated into crypto infrastructure, protecting internal systems, access permissions, and sensitive wallet operations is becoming increasingly important.
The bigger takeaway is clear: Security risks in crypto are evolving, and even advanced platforms must continuously strengthen their defenses.
AI can improve efficiency, but it also introduces new security challenges that cannot be ignored.
#Binance / #Hack
Binance Security Incident Raises Serious Questions About AI and Wallet Protection
A reported security incident involving Binance has highlighted a new and concerning type of cybersecurity threat.
According to Reuters, the attacker allegedly exploited a compromised computer and used an internal AI tool to gain control over wallets.
What makes this incident particularly concerning is the reported combination of compromised devices, AI-assisted access, and wallet security vulnerabilities. It shows how attackers may use legitimate internal tools as part of sophisticated cyberattacks.
As AI becomes more deeply integrated into crypto infrastructure, protecting internal systems, access permissions, and sensitive wallet operations is becoming increasingly important.
The bigger takeaway is clear: Security risks in crypto are evolving, and even advanced platforms must continuously strengthen their defenses.
AI can improve efficiency, but it also introduces new security challenges that cannot be ignored.
#Binance / #Hack
A reported security incident involving Binance has highlighted a new and concerning type of cybersecurity threat.
According to Reuters, the attacker allegedly exploited a compromised computer and used an internal AI tool to gain control over wallets.
What makes this incident particularly concerning is the reported combination of compromised devices, AI-assisted access, and wallet security vulnerabilities. It shows how attackers may use legitimate internal tools as part of sophisticated cyberattacks.
As AI becomes more deeply integrated into crypto infrastructure, protecting internal systems, access permissions, and sensitive wallet operations is becoming increasingly important.
The bigger takeaway is clear: Security risks in crypto are evolving, and even advanced platforms must continuously strengthen their defenses.
AI can improve efficiency, but it also introduces new security challenges that cannot be ignored.
#Binance / #Hack
2
374
·
--
North Korea stole $7.61B in crypto this year, and not one big hit used a code exploit.
BitOK counts 38 incidents, Jan-Oct 2026:
• All six biggest attacks hijacked the people and systems that sign withdrawals
• $2.86B frozen or seized, $4.75B out of reach
• Binance accounts for $6.41B of the total
Every withdrawal carried valid signatures. Audits of contracts can't catch a compromised laptop or signing service. Stablecoins got frozen fast, so the thieves swapped into $ETH, which no issuer can freeze.
The takeaway: operational security matters more than code audits now. Watch how exchanges and multisig teams change signer controls.
Which matters more for your trust in a platform: code audits or signer security?
#CryptoSecurity #Hack #Binance $BNB
North Korea stole $7.61B in crypto this year, and not one big hit used a code exploit.
BitOK counts 38 incidents, Jan-Oct 2026:
• All six biggest attacks hijacked the people and systems that sign withdrawals
• $2.86B frozen or seized, $4.75B out of reach
• Binance accounts for $6.41B of the total
Every withdrawal carried valid signatures. Audits of contracts can't catch a compromised laptop or signing service. Stablecoins got frozen fast, so the thieves swapped into $ETH , which no issuer can freeze.
The takeaway: operational security matters more than code audits now. Watch how exchanges and multisig teams change signer controls.
Which matters more for your trust in a platform: code audits or signer security?
#CryptoSecurity #Hack #Binance $BNB
BitOK counts 38 incidents, Jan-Oct 2026:
• All six biggest attacks hijacked the people and systems that sign withdrawals
• $2.86B frozen or seized, $4.75B out of reach
• Binance accounts for $6.41B of the total
Every withdrawal carried valid signatures. Audits of contracts can't catch a compromised laptop or signing service. Stablecoins got frozen fast, so the thieves swapped into $ETH , which no issuer can freeze.
The takeaway: operational security matters more than code audits now. Watch how exchanges and multisig teams change signer controls.
Which matters more for your trust in a platform: code audits or signer security?
#CryptoSecurity #Hack #Binance $BNB
3
If you're an iPhone user, read this.
Hackers just stole $4.06 MILLION in crypto through cyberattacks that started with just one click.
The victim said they tapped an ad in Safari before wallet apps were emptied.
An iOS exploit kit such as DarkSword is suspected.
DarkSword
#Crypto #Hack
If you're an iPhone user, read this.
Hackers just stole $4.06 MILLION in crypto through cyberattacks that started with just one click.
The victim said they tapped an ad in Safari before wallet apps were emptied.
An iOS exploit kit such as DarkSword is suspected.
DarkSword
#Crypto #Hack
Hackers just stole $4.06 MILLION in crypto through cyberattacks that started with just one click.
The victim said they tapped an ad in Safari before wallet apps were emptied.
An iOS exploit kit such as DarkSword is suspected.
DarkSword
#Crypto #Hack
99
🚨 How Did Hackers Infiltrate Binance’s Wallet Infrastructure?
The reported attack highlights how dangerous social engineering can be, even for major crypto platforms.
According to the details, attackers first impersonated company recruiters and approached a Binance engineer through a fake hiring process. After two rounds of interviews, they sent the engineer a test assignment to download. Hidden inside the assignment was malicious code that went undetected by security systems.
Once the engineer’s computer was compromised, the attackers reportedly used an internal AI tool to move further into the company's environment, access other employees' devices, and steal login credentials.
The situation escalated on October 29, when the attackers deployed a malicious container and targeted the system responsible for signing cryptocurrency transactions.
The biggest takeaway? Security isn't just about protecting servers and wallets. One compromised employee device can potentially become the entry point to much larger systems.
In crypto, even the strongest infrastructure is only as secure as its weakest access point. 🔐
#Binance #Hack
🚨 How Did Hackers Infiltrate Binance’s Wallet Infrastructure?
The reported attack highlights how dangerous social engineering can be, even for major crypto platforms.
According to the details, attackers first impersonated company recruiters and approached a Binance engineer through a fake hiring process. After two rounds of interviews, they sent the engineer a test assignment to download. Hidden inside the assignment was malicious code that went undetected by security systems.
Once the engineer’s computer was compromised, the attackers reportedly used an internal AI tool to move further into the company's environment, access other employees' devices, and steal login credentials.
The situation escalated on October 29, when the attackers deployed a malicious container and targeted the system responsible for signing cryptocurrency transactions.
The biggest takeaway? Security isn't just about protecting servers and wallets. One compromised employee device can potentially become the entry point to much larger systems.
In crypto, even the strongest infrastructure is only as secure as its weakest access point. 🔐
#Binance #Hack
The reported attack highlights how dangerous social engineering can be, even for major crypto platforms.
According to the details, attackers first impersonated company recruiters and approached a Binance engineer through a fake hiring process. After two rounds of interviews, they sent the engineer a test assignment to download. Hidden inside the assignment was malicious code that went undetected by security systems.
Once the engineer’s computer was compromised, the attackers reportedly used an internal AI tool to move further into the company's environment, access other employees' devices, and steal login credentials.
The situation escalated on October 29, when the attackers deployed a malicious container and targeted the system responsible for signing cryptocurrency transactions.
The biggest takeaway? Security isn't just about protecting servers and wallets. One compromised employee device can potentially become the entry point to much larger systems.
In crypto, even the strongest infrastructure is only as secure as its weakest access point. 🔐
#Binance #Hack
424
·
--
Bullish
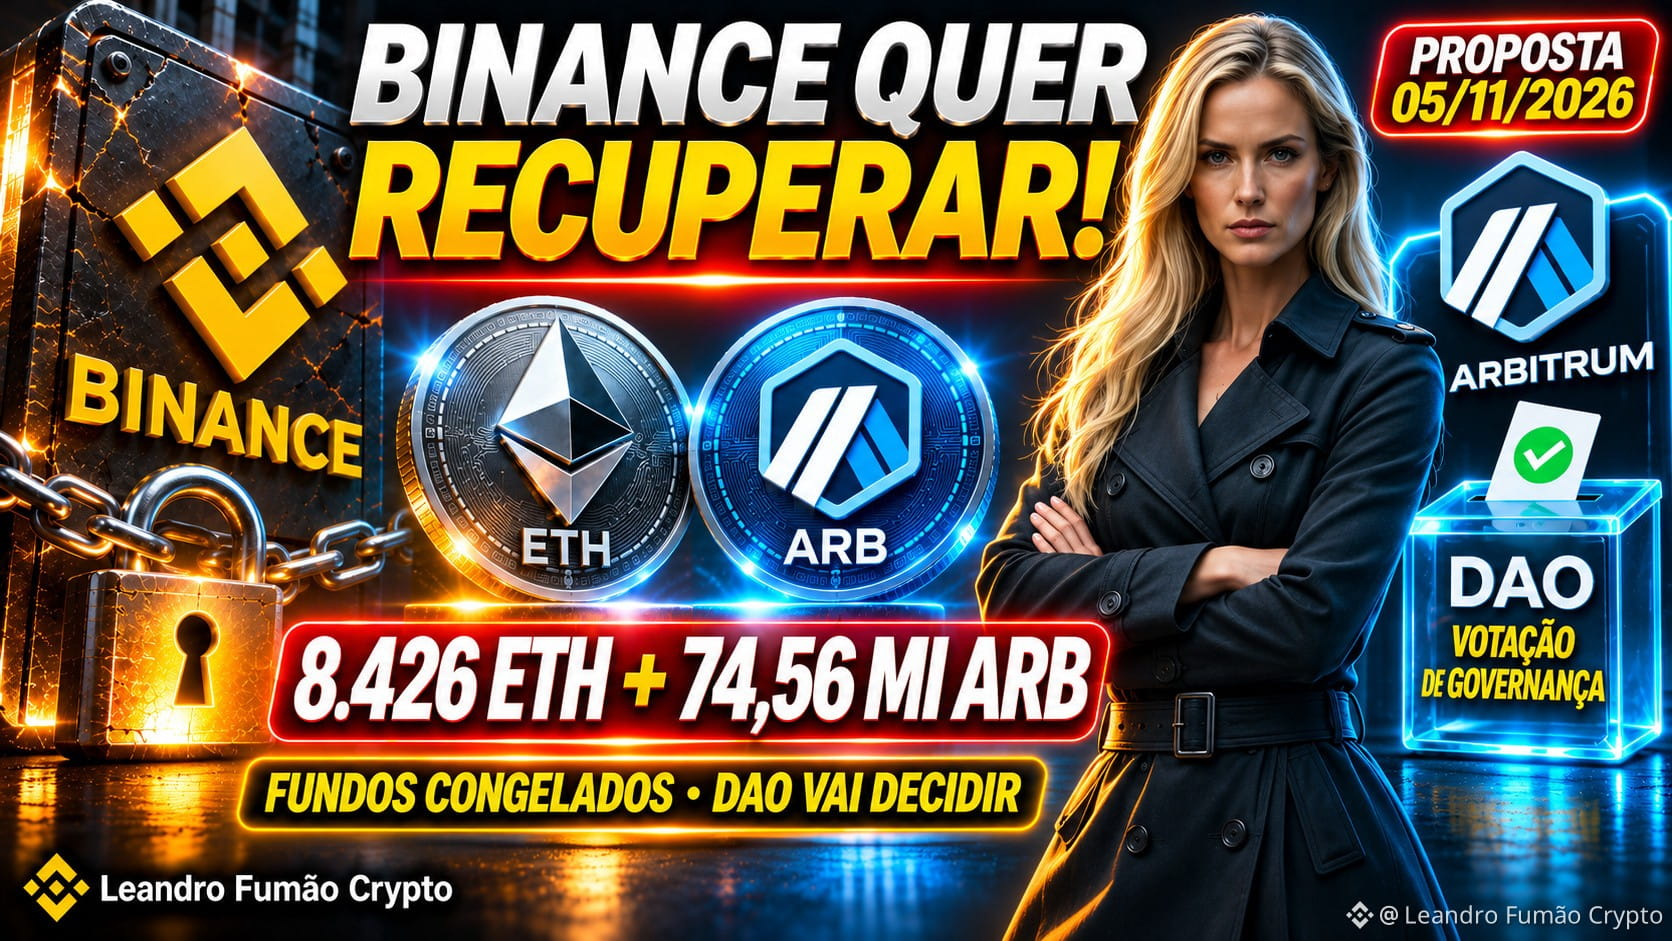
❖BINANCE SEEKS RETURN OF 8,426 ⟠ETH AND 74.56 MILLION 🔷ARB FROZEN ON ARBITRUM❗
Ξ The exchange submitted a formal proposal to the Arbitrum DAO to recover the assets frozen after the hot wallet exploit.
Binance $BNB submitted an official proposal to the Arbitrum DAO requesting the release of 8,425.997 ETH and 74.56 million ARB. The funds were frozen by the Arbitrum Security Council on October 30 in an emergency action following the attack on the exchange’s hot wallet.
The cryptocurrencies are currently held at an intermediate frozen address and can only be moved with DAO approval. Binance is not asking for new funds from the DAO treasury — only the return of assets that have already been frozen.
The governance process is expected to take about 7 weeks or more (forum discussion + temperature check + on-chain vote). The exchange said it will cover users’ losses with SAFU and its own funds.
Meanwhile, Binance is gradually resuming withdrawals and has removed all API keys linked to the SignalPlus platform following a security alert.
This is one of the largest requests to recover funds through DAO governance in 2026. The case tests Arbitrum’s ability to handle emergency freezes and returns transparently.
As Binance tries to recover the assets, market confidence in the security of exchanges and bridges remains under pressure. The decision by ARB holders will be closely watched by the entire community.
💬 Should Binance’s proposal to recover the frozen $ETH and $ARB be approved by the Arbitrum DAO?
#Binance #Arbitrum #Hack
❖BINANCE SEEKS RETURN OF 8,426 ⟠ETH AND 74.56 MILLION 🔷ARB FROZEN ON ARBITRUM❗
Ξ The exchange submitted a formal proposal to the Arbitrum DAO to recover the assets frozen after the hot wallet exploit.
Binance $BNB submitted an official proposal to the Arbitrum DAO requesting the release of 8,425.997 ETH and 74.56 million ARB. The funds were frozen by the Arbitrum Security Council on October 30 in an emergency action following the attack on the exchange’s hot wallet.
The cryptocurrencies are currently held at an intermediate frozen address and can only be moved with DAO approval. Binance is not asking for new funds from the DAO treasury — only the return of assets that have already been frozen.
The governance process is expected to take about 7 weeks or more (forum discussion + temperature check + on-chain vote). The exchange said it will cover users’ losses with SAFU and its own funds.
Meanwhile, Binance is gradually resuming withdrawals and has removed all API keys linked to the SignalPlus platform following a security alert.
This is one of the largest requests to recover funds through DAO governance in 2026. The case tests Arbitrum’s ability to handle emergency freezes and returns transparently.
As Binance tries to recover the assets, market confidence in the security of exchanges and bridges remains under pressure. The decision by ARB holders will be closely watched by the entire community.
💬 Should Binance’s proposal to recover the frozen $ETH and $ARB be approved by the Arbitrum DAO?
#Binance #Arbitrum #Hack
Ξ The exchange submitted a formal proposal to the Arbitrum DAO to recover the assets frozen after the hot wallet exploit.
Binance $BNB submitted an official proposal to the Arbitrum DAO requesting the release of 8,425.997 ETH and 74.56 million ARB. The funds were frozen by the Arbitrum Security Council on October 30 in an emergency action following the attack on the exchange’s hot wallet.
The cryptocurrencies are currently held at an intermediate frozen address and can only be moved with DAO approval. Binance is not asking for new funds from the DAO treasury — only the return of assets that have already been frozen.
The governance process is expected to take about 7 weeks or more (forum discussion + temperature check + on-chain vote). The exchange said it will cover users’ losses with SAFU and its own funds.
Meanwhile, Binance is gradually resuming withdrawals and has removed all API keys linked to the SignalPlus platform following a security alert.
This is one of the largest requests to recover funds through DAO governance in 2026. The case tests Arbitrum’s ability to handle emergency freezes and returns transparently.
As Binance tries to recover the assets, market confidence in the security of exchanges and bridges remains under pressure. The decision by ARB holders will be closely watched by the entire community.
💬 Should Binance’s proposal to recover the frozen $ETH and $ARB be approved by the Arbitrum DAO?
#Binance #Arbitrum #Hack
1
1.2k
·
--
70.5M $POL stolen in the Polymarket and Binance hacks could be pulled back with a hard fork.
What happened:
• A proposal posted Nov 4 would zero the balances of 5 frozen attacker wallets (23.86M POL from Polymarket, 46.63M from Binance) and credit verified recovery wallets
• Total POL supply stays the same. Block producers already blocked the wallets, but a block list can't return the funds
• It's only a proposal: needs governance approval, Amoy testnet testing and a client update. No activation date yet
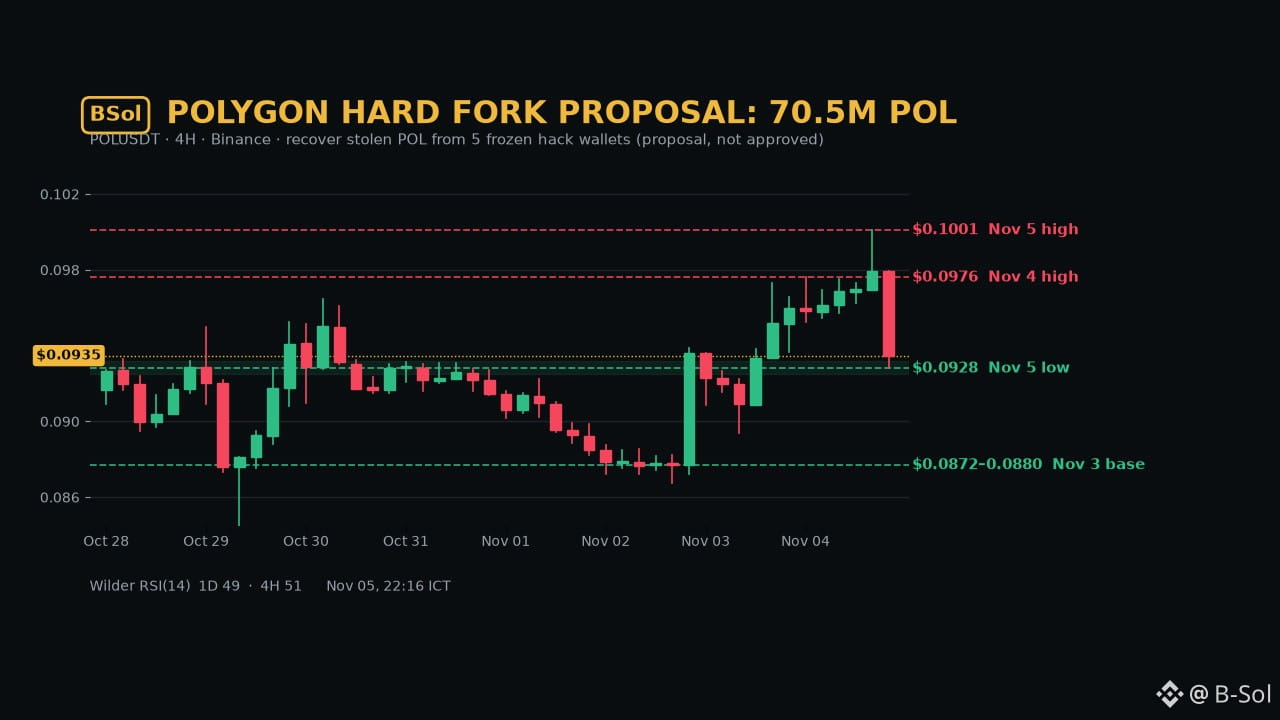
Chart: $POL $0.0935 on Binance, -1.9% 24h after a rejection at $0.1001. Support $0.0925-0.0932, then $0.0872-0.0880. Resistance $0.0976, then $0.1001. Wilder RSI 1D ~49 / 4H ~51.
Watch: a 4H close above $0.0976 or below $0.0872.
Rolling back balances on a major chain: justified exception or a bad precedent? Which side are you on?
#Polygon #POL #CryptoNews #Hack
70.5M $POL stolen in the Polymarket and Binance hacks could be pulled back with a hard fork.
What happened:
• A proposal posted Nov 4 would zero the balances of 5 frozen attacker wallets (23.86M POL from Polymarket, 46.63M from Binance) and credit verified recovery wallets
• Total POL supply stays the same. Block producers already blocked the wallets, but a block list can't return the funds
• It's only a proposal: needs governance approval, Amoy testnet testing and a client update. No activation date yet
Chart: $POL $0.0935 on Binance, -1.9% 24h after a rejection at $0.1001. Support $0.0925-0.0932, then $0.0872-0.0880. Resistance $0.0976, then $0.1001. Wilder RSI 1D ~49 / 4H ~51.
Watch: a 4H close above $0.0976 or below $0.0872.
Rolling back balances on a major chain: justified exception or a bad precedent? Which side are you on?
#Polygon #POL #CryptoNews #Hack
What happened:
• A proposal posted Nov 4 would zero the balances of 5 frozen attacker wallets (23.86M POL from Polymarket, 46.63M from Binance) and credit verified recovery wallets
• Total POL supply stays the same. Block producers already blocked the wallets, but a block list can't return the funds
• It's only a proposal: needs governance approval, Amoy testnet testing and a client update. No activation date yet
Chart: $POL $0.0935 on Binance, -1.9% 24h after a rejection at $0.1001. Support $0.0925-0.0932, then $0.0872-0.0880. Resistance $0.0976, then $0.1001. Wilder RSI 1D ~49 / 4H ~51.
Watch: a 4H close above $0.0976 or below $0.0872.
Rolling back balances on a major chain: justified exception or a bad precedent? Which side are you on?
#Polygon #POL #CryptoNews #Hack
28

·
--
Article
The Most Dangerous Hacker in Human History!The FBI Issues an International Arrest Warrant Against North Korea's Cyber Mastermind
Imagine being accused of helping orchestrate cyberattacks that shook Hollywood, robbed one of the world's financial institutions, and brought hospitals across the globe to a standstill.
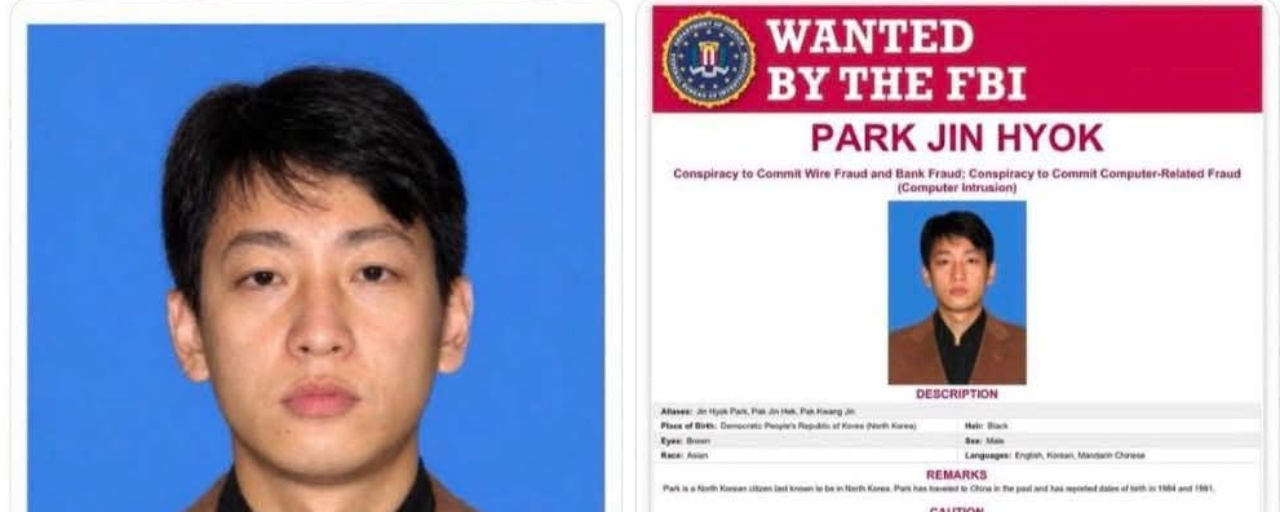
Meet Pak Jin-hyok — the North Korean computer programmer wanted by the FBI.
And here's what makes this story terrifying: U.S. authorities have linked him to a state-sponsored hacking conspiracy responsible for some of the most notorious cyber operations of the modern era.
THE CYBERATTACKS THAT PUT HIM ON THE FBI'S MOST-WANTED LIST:
1. SONY PICTURES HACK (2014)
A devastating attack that exposed confidential corporate emails, employee information, and unreleased Hollywood films. The breach sent shockwaves through the entertainment industry.
2. THE $81 MILLION BANGLADESH BANK HEIST (2016)
Hackers exploited the international banking system to steal approximately $81 million from Bangladesh's central bank. U.S. authorities linked Pak Jin-hyok to the conspiracy behind the attack.
3. WANNACRY RANSOMWARE (2017)
One of the most destructive cyberattacks ever recorded. WannaCry infected more than 300,000 computers across approximately 150 countries, crippling Britain's National Health Service and disrupting businesses worldwide.
4. A BILLION-DOLLAR CYBERCRIME CONSPIRACY
In 2021, the U.S. Department of Justice charged three North Korean hackers, including Pak Jin-hyok, in connection with an alleged conspiracy involving more than $1.3 BILLION in attempted and successful thefts and extortion.
Think about that number.
BUT THIS IS BIGGER THAN ONE HACKER...
U.S. authorities have repeatedly warned that North Korea uses sophisticated cybercrime operations to generate revenue for the regime.
That money can help support:
• Nuclear weapons and ballistic missile programs.
• Military development and modernization.
• The regime's broader strategic objectives.
AND HERE'S THE CATCH...
Pak Jin-hyok was publicly identified and charged by U.S. authorities, and the FBI issued a wanted notice for him.
But his last known location was North Korea — a country that does not cooperate with U.S. law enforcement in handing over its wanted citizens.
A hacker accused of participating in attacks spanning continents. A global cybercrime operation. And a suspect still beyond the FBI's reach.
$AIN #Hack $BTC #SouthKorea $ETH #FBI
The Most Dangerous Hacker in Human History!
The FBI Issues an International Arrest Warrant Against North Korea's Cyber Mastermind
Imagine being accused of helping orchestrate cyberattacks that shook Hollywood, robbed one of the world's financial institutions, and brought hospitals across the globe to a standstill.
Meet Pak Jin-hyok — the North Korean computer programmer wanted by the FBI.
And here's what makes this story terrifying: U.S. authorities have linked him to a state-sponsored hacking conspiracy responsible for some of the most notorious cyber operations of the modern era.
THE CYBERATTACKS THAT PUT HIM ON THE FBI'S MOST-WANTED LIST:
1. SONY PICTURES HACK (2014)
A devastating attack that exposed confidential corporate emails, employee information, and unreleased Hollywood films. The breach sent shockwaves through the entertainment industry.
2. THE $81 MILLION BANGLADESH BANK HEIST (2016)
Hackers exploited the international banking system to steal approximately $81 million from Bangladesh's central bank. U.S. authorities linked Pak Jin-hyok to the conspiracy behind the attack.
3. WANNACRY RANSOMWARE (2017)
One of the most destructive cyberattacks ever recorded. WannaCry infected more than 300,000 computers across approximately 150 countries, crippling Britain's National Health Service and disrupting businesses worldwide.
4. A BILLION-DOLLAR CYBERCRIME CONSPIRACY
In 2021, the U.S. Department of Justice charged three North Korean hackers, including Pak Jin-hyok, in connection with an alleged conspiracy involving more than $1.3 BILLION in attempted and successful thefts and extortion.
Think about that number.
BUT THIS IS BIGGER THAN ONE HACKER...
U.S. authorities have repeatedly warned that North Korea uses sophisticated cybercrime operations to generate revenue for the regime.
That money can help support:
• Nuclear weapons and ballistic missile programs.
• Military development and modernization.
• The regime's broader strategic objectives.
AND HERE'S THE CATCH...
Pak Jin-hyok was publicly identified and charged by U.S. authorities, and the FBI issued a wanted notice for him.
But his last known location was North Korea — a country that does not cooperate with U.S. law enforcement in handing over its wanted citizens.
A hacker accused of participating in attacks spanning continents. A global cybercrime operation. And a suspect still beyond the FBI's reach.
$AIN #Hack $BTC #SouthKorea $ETH #FBI
Imagine being accused of helping orchestrate cyberattacks that shook Hollywood, robbed one of the world's financial institutions, and brought hospitals across the globe to a standstill.
Meet Pak Jin-hyok — the North Korean computer programmer wanted by the FBI.
And here's what makes this story terrifying: U.S. authorities have linked him to a state-sponsored hacking conspiracy responsible for some of the most notorious cyber operations of the modern era.
THE CYBERATTACKS THAT PUT HIM ON THE FBI'S MOST-WANTED LIST:
1. SONY PICTURES HACK (2014)
A devastating attack that exposed confidential corporate emails, employee information, and unreleased Hollywood films. The breach sent shockwaves through the entertainment industry.
2. THE $81 MILLION BANGLADESH BANK HEIST (2016)
Hackers exploited the international banking system to steal approximately $81 million from Bangladesh's central bank. U.S. authorities linked Pak Jin-hyok to the conspiracy behind the attack.
3. WANNACRY RANSOMWARE (2017)
One of the most destructive cyberattacks ever recorded. WannaCry infected more than 300,000 computers across approximately 150 countries, crippling Britain's National Health Service and disrupting businesses worldwide.
4. A BILLION-DOLLAR CYBERCRIME CONSPIRACY
In 2021, the U.S. Department of Justice charged three North Korean hackers, including Pak Jin-hyok, in connection with an alleged conspiracy involving more than $1.3 BILLION in attempted and successful thefts and extortion.
Think about that number.
BUT THIS IS BIGGER THAN ONE HACKER...
U.S. authorities have repeatedly warned that North Korea uses sophisticated cybercrime operations to generate revenue for the regime.
That money can help support:
• Nuclear weapons and ballistic missile programs.
• Military development and modernization.
• The regime's broader strategic objectives.
AND HERE'S THE CATCH...
Pak Jin-hyok was publicly identified and charged by U.S. authorities, and the FBI issued a wanted notice for him.
But his last known location was North Korea — a country that does not cooperate with U.S. law enforcement in handing over its wanted citizens.
A hacker accused of participating in attacks spanning continents. A global cybercrime operation. And a suspect still beyond the FBI's reach.
$AIN #Hack $BTC #SouthKorea $ETH #FBI
1
146
·
--
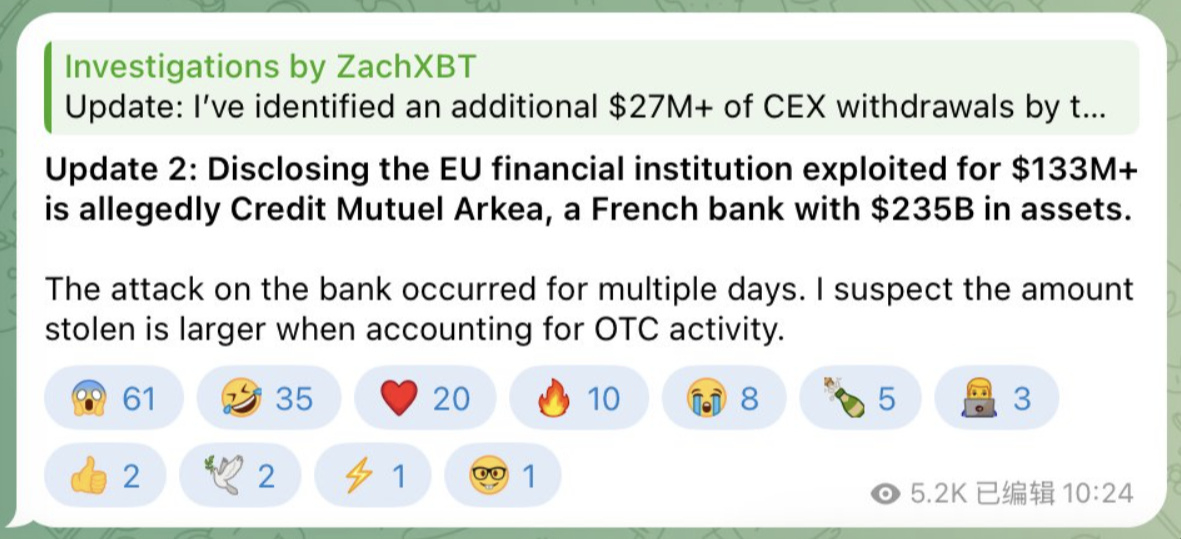
🏦 The $133M "EU entity" hack now has a name. And it's a bank.
ZachXBT says the victim is Crédit Mutuel Arkéa, a French banking group with about $235B in assets. The bank has not confirmed or denied anything.
What we know so far:
→ Withdrawals hit accounts at Kraken, Crypto.com and OKX starting Nov 1
→ About $62.98M in stablecoins was swapped into 27,553 $ETH in roughly four hours
→ Part went through instant exchanges, part into $XMR, part across bridges
→ ZachXBT is "highly confident" this is not North Korea's Lazarus Group
→ Kraken restricted linked accounts and says its own systems were not breached
Plot twist: remember the "whale" who bought 27,553 ETH at $2,286 on Nov 2 and got cheered as a dip buyer? Those are exactly the numbers Bitquery tied to this theft.
ZachXBT's biggest complaint is the silence. He says more than $30M got laundered that could have been frozen if the theft had been reported quickly.
Should any institution that loses crypto be forced to disclose it within 24 hours? Yes or no? 👇
#CryptoSecurity #ZachXBT #Hack #ETH
🏦 The $133M "EU entity" hack now has a name. And it's a bank.
ZachXBT says the victim is Crédit Mutuel Arkéa, a French banking group with about $235B in assets. The bank has not confirmed or denied anything.
What we know so far:
→ Withdrawals hit accounts at Kraken, Crypto.com and OKX starting Nov 1
→ About $62.98M in stablecoins was swapped into 27,553 $ETH in roughly four hours
→ Part went through instant exchanges, part into $XMR, part across bridges
→ ZachXBT is "highly confident" this is not North Korea's Lazarus Group
→ Kraken restricted linked accounts and says its own systems were not breached
Plot twist: remember the "whale" who bought 27,553 ETH at $2,286 on Nov 2 and got cheered as a dip buyer? Those are exactly the numbers Bitquery tied to this theft.
ZachXBT's biggest complaint is the silence. He says more than $30M got laundered that could have been frozen if the theft had been reported quickly.
Should any institution that loses crypto be forced to disclose it within 24 hours? Yes or no? 👇
#CryptoSecurity #ZachXBT #Hack #ETH
ZachXBT says the victim is Crédit Mutuel Arkéa, a French banking group with about $235B in assets. The bank has not confirmed or denied anything.
What we know so far:
→ Withdrawals hit accounts at Kraken, Crypto.com and OKX starting Nov 1
→ About $62.98M in stablecoins was swapped into 27,553 $ETH in roughly four hours
→ Part went through instant exchanges, part into $XMR, part across bridges
→ ZachXBT is "highly confident" this is not North Korea's Lazarus Group
→ Kraken restricted linked accounts and says its own systems were not breached
Plot twist: remember the "whale" who bought 27,553 ETH at $2,286 on Nov 2 and got cheered as a dip buyer? Those are exactly the numbers Bitquery tied to this theft.
ZachXBT's biggest complaint is the silence. He says more than $30M got laundered that could have been frozen if the theft had been reported quickly.
Should any institution that loses crypto be forced to disclose it within 24 hours? Yes or no? 👇
#CryptoSecurity #ZachXBT #Hack #ETH
1
293
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#HotCPIDecemberHikePriced
103,925 views
1,219 Discussing
2
#AnthropicRejectsIPODelayValuationinQuestion
227,612 views
1,903 Discussing
3
#CanNvidiaEarningsEaseMarketConcerns?
38,629 views
560 Discussing
4
#BitcoinFiveWeeklyLosses
559,209 views
3,439 Discussing
5
#TrumpMediaAdds1510BTCInQ3
8,761 views
129 Discussing
6
#TradFiForBeginners
436,263 views
2,840 Discussing
7
#NvidiaInvestigatesAfterHuang’sAffairApology
524,560 views
3,244 Discussing
8
#ADPWeeklyEstimateShowsUSPrivatePayrollsUp19750
18,711 views
301 Discussing
9
#BitcoinSpotETFsPost$201MNetOutflowForThirdStraightDay
2,921 views
39 Discussing
10
#CryptoLiquidationsReach$1.16BIn24Hours
80,187 views
88 Discussing