

#securityalert
securityalert
533,335 views
1,320 Discussing
Hot
Latest

·
--
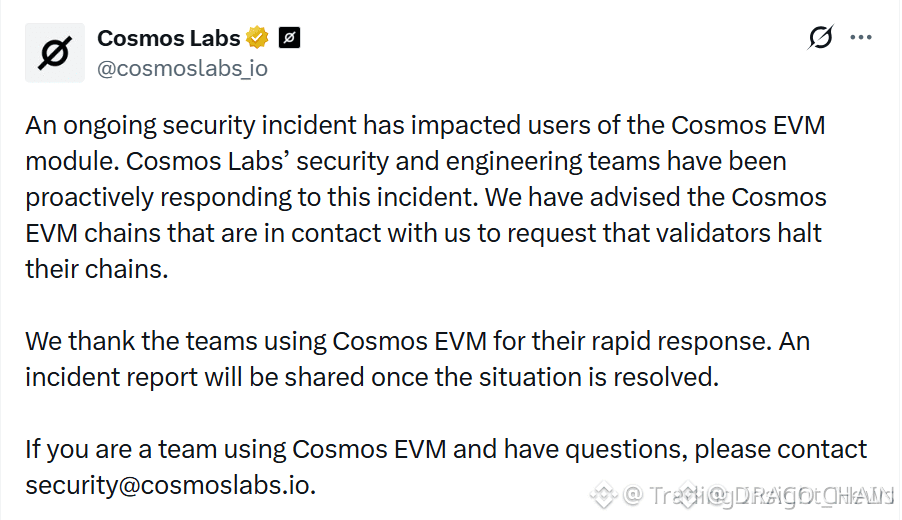
🚨 $ATOM CRITICAL EXPLOIT: COSMOS EVM SECURITY BREACH TRIGGERS MULTI-CHAIN HALTS 📉
Cosmos Labs has confirmed a severe vulnerability within the Cosmos EVM module, forcing multiple validator networks across the ecosystem into emergency halts. 🔍 Institutional risk models are shifting into capital preservation as smart money assesses the full scope of structural vulnerability across interconnected chains. ⚠️
When infrastructure layers experience systemic failure, liquidity cascades rapidly follow, leaving exposed order flow vulnerable to contagion. 📊 Project teams utilizing the EVM architecture are undergoing immediate security audits while market participants monitor for potential cascade risks. 📌
🤔 Are you withdrawing liquidity from affected Cosmos EVM chains or waiting for official mitigation updates? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ATOM #Cosmos #SecurityAlert #Crypto
🚨 🛡️
126
·
--
🚨 A $3.8 million hack… and it ends with an unexpected story
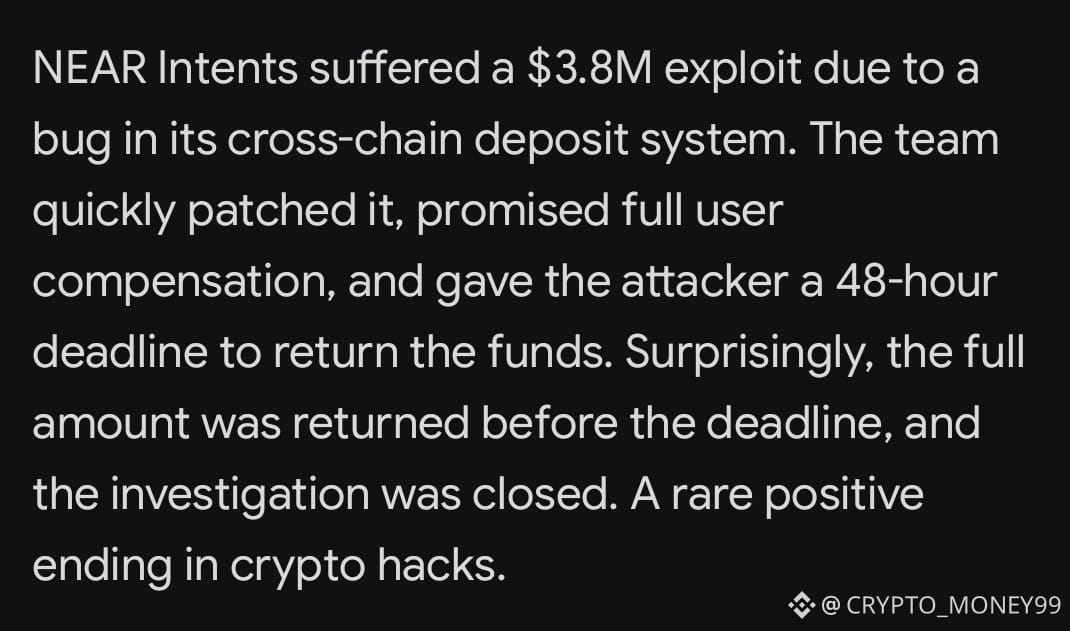
A few days ago, the NEAR Intents protocol suffered an exploitation of a vulnerability in its cross-chain deposit and withdrawal system.
The attacker withdrew about $3.8 million USDT from a contract on the network within just a few hours.
Most stories end right here: lost funds, long investigations, and delayed compensation.
But this time, things were different.
The team halted services immediately, patched the vulnerability, and stated clearly:
“Funds will be fully reimbursed.”
Then they did something bolder…
They identified the responsible party and gave them only a 48-hour deadline to return everything.
The result?
Before the deadline even ended, the funds were fully returned.
A large portion came back in the form of Bitcoin, and the investigation was officially closed.
Even the attacker left a message on-chain saying they were wrong, thanking the team for handling it professionally, and advising to use Bug Bounties instead of hacking.
The takeaway is clear:
Not every hack ends in disaster.
Speed in fixing + transparency + smart pressure… sometimes can turn loss into a rare success story in the crypto world.
What do you think? Should this model become the norm?
#SecurityAlert #Near #crypto #USDT #Binance
1
111

·
--
🚨 THE PPV2 EXPLOIT IS STILL DRAINING $ETH WALLETS SO REVOKE YOUR APPROVALS NOW! ⚠️
The Payment Processor V2 exploit is actively draining funds on-chain, and attackers are getting ruthless. Even if your wallet survived the initial September wave, open contract approvals mean your assets remain completely exposed to automated drainers. 🩸
Exploiters are now tipping block builders up to 99% of stolen proceeds to guarantee execution, making front-run rescues virtually impossible the moment an offer is accepted. If you trade on-chain, revoke legacy permissions immediately before signing your next deal. 🔍
💬 Have you cleared your active contract approvals today, or are you leaving your wallet exposed to silent MEV drainers? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #CryptoSecurity #OnChain #SecurityAlert
⚠️ 👁️
15

·
--
Chinese Version:
The NEAR Intents platform under the NEAR protocol has been hacked! Loss of $3.8 million! It is reported that this vulnerability is related to a previous incident involving assistance with Bitget’s security breach. The platform promises to compensate users, but this move really makes people nervous. Here we go again with DeFi security—old problems are back. Everyone, stay alert! #DeFiHack #SecurityAlert $NEAR
NEAR's NEAR Intents platform just got hit with a $3.8M exploit! The bug came from assisting with Bitget's security breach. They promise to compensate affected users, but this shows even helping others can backfire in crypto. Stay vigilant out there! #SecurityAlert #DeFiHack $NEAR
177
·
--
CRITICAL ALERT: APPLE PATCHES ZERO-DAY EXPLOIT TARGETING YOUR $BTC AND CRYPTO WALLETS! 🚨 ⚡
🚨 Black-hat hackers are actively exploiting a critical zero-day vulnerability across older iOS and macOS builds to drain self-custody crypto wallets. 🛡️ SlowMist security researchers confirmed targeted attacks are already live in the wild, putting mobile wallet assets directly in the crosshairs.
🔒 Apple just pushed an urgent system patch to neutralize this high-level exploit. 💡 If you execute trades or hold private keys on your mobile devices, update your firmware immediately, avoid unverified Safari links, and restrict unknown app permissions. 💬 Have you already updated your devices, or are you still running your wallet on outdated firmware? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #CryptoSecurity #SecurityAlert #CryptoWallets
⚡ 🛡️
7

·
--
🚨 DYORSWAP confirms over 200 ETH paid in compensation after fake GIWA network scam. Upbit’s Dunamu says GIWA mainnet not live. ETH holders face phishing risks via spoofed chains. Stay alert—verify contract addresses before interacting. How do you protect yourself from fake network scams? #SecurityAlert
$ETH #TradingSignal #CryptoAnalysis
$ETH #TradingSignal #CryptoAnalysis
10

Alert: 12.4M XRP Hack — D'CENT Took Action but the Funds Disappeared! 🚨
The second-largest XRP hack of 2026! 12.4M XRP was withdrawn from 7,393 D'CENT app wallets over 10 days, from September 15 to 25.
How? 6 waves of theft using a compromised recovery phrase. The attackers first manually drained the large wallets, then used automated scripts.
6.3M $XRP was swapped into Ethereum via THORChain, along with $BTC, $ETH, $Tron, and $XLM that were also seized.
The action taken: D'CENT released an initial report on September 17, concealed the root cause for security reasons, added a safety check to the latest app version, and urged all users to create a new recovery phrase and transfer assets immediately. IoTrust received more than 110 reports.
Do you still have $XRP in your D'CENT? Check now!
Please stay tuned
$XRP #XRP #CryptoHack #SecurityAlert #DCENT
#hackersdrainover12.4mxrpfromdcentwallets
1
2.2k
·
--
🚨 $340K API EXPLOIT SWEEPS $ONE AS FORGED DOCUMENT ATTACK BYPASSES 2FA! 💣
A brutal $340,000 compromise just exposed a dangerous loophole in off-chain account security. 🔍 Attackers leveraged forged verification documents to override security settings, but the real structural failure happened when lingering API keys remained active after the account freeze was lifted.
The instant the 24-hour withdrawal lock expired, exploiters drained over 322k USDT alongside 9.1M $ONE directly through the compromised API without prompting 2FA confirmations. ⚡ This sharp incident highlights why active key audits are just as vital as cold storage discipline.
💡 Have you inspected your active API management permissions today to guarantee zero rogue access? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ONE #SecurityAlert #Crypto #RiskManagement
🛡️ ⚡
142
·
--
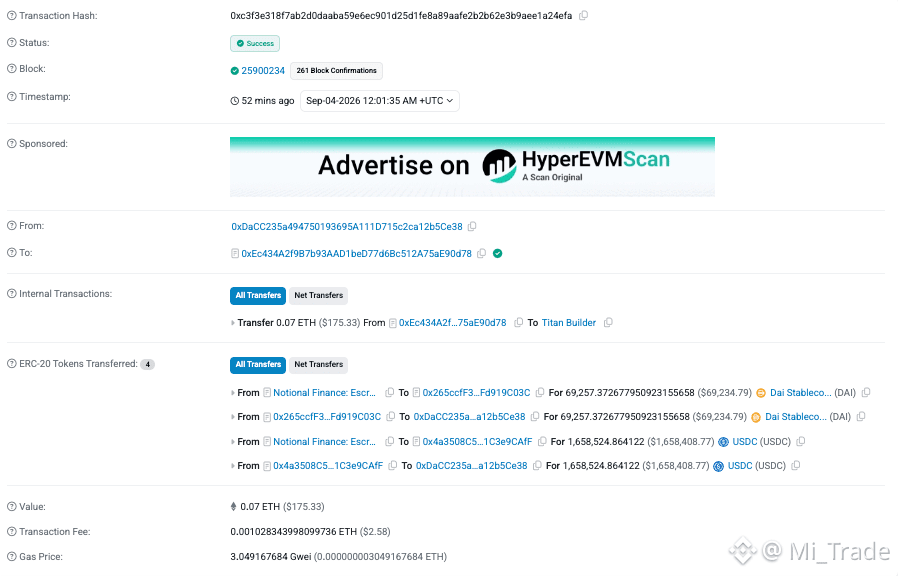
Notional Finance has just recorded a serious security incident involving a margin (escrow) contract.
According to data from PeckShieldAlert, approximately $1.7 million in DAI and USDC was illicitly withdrawn. The attacker swapped this amount into 689.2 $ETH v and then moved the entire funds into Tornado Cash to erase the trail.
👀 Market Watch: $ETH, $USDC
Users should exercise caution and monitor official announcements from the project.
#SecurityAlert #CryptoNews
Notional Finance has just recorded a serious security incident involving a margin (escrow) contract.
According to data from PeckShieldAlert, approximately $1.7 million in DAI and USDC was illicitly withdrawn. The attacker swapped this amount into 689.2 $ETH v and then moved the entire funds into Tornado Cash to erase the trail.
👀 Market Watch: $ETH , $USDC
Users should exercise caution and monitor official announcements from the project.
#SecurityAlert #CryptoNews
140
🔐 MY BINANCE ACCOUNT IS UNHACKABLE 🔐
Hackers are pulling, but my shield is STRONG! 🛡️
Here are my 5 Security Tips to keep your account SAFE:
1️⃣ Enable 2FA - Use Google Authenticator, not SMS.
2️⃣ Anti-Phishing Code - Set it in Binance Security settings.
3️⃣ Never Share - Binance will NEVER ask for your password.
4️⃣ Whitelist Address - Enable Withdrawal Whitelist.
5️⃣ Check URL - Always login at cf-workers-proxy-cyt.pages.dev only.
Stay SAFU!
#SecurityAlert
2
37
·
--
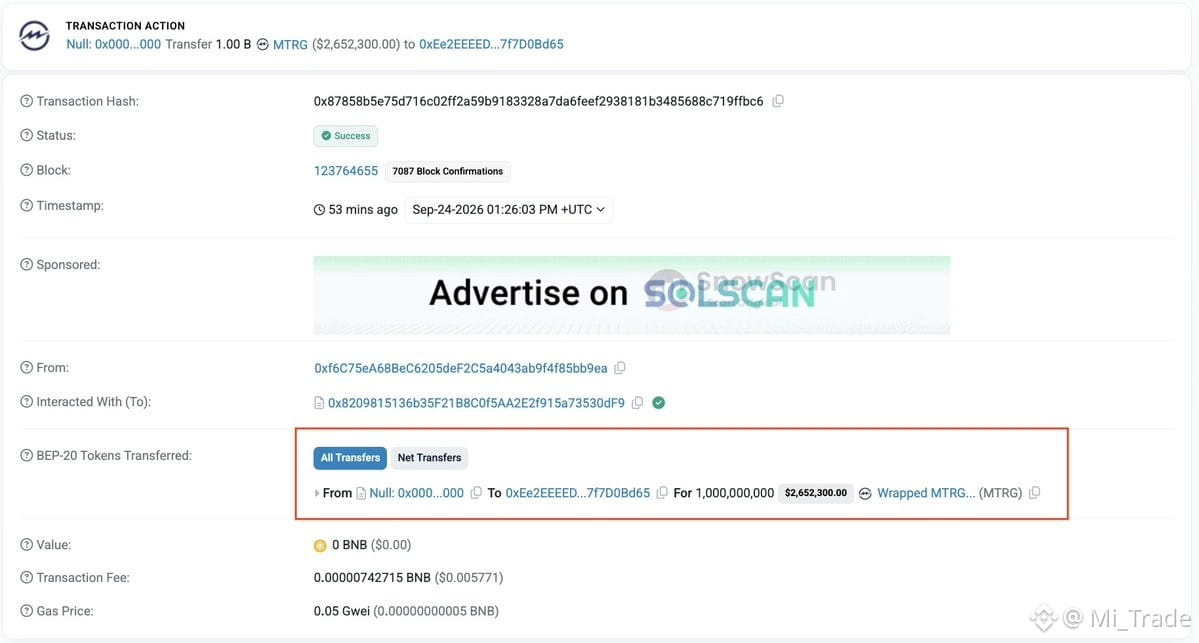
PeckShieldAlert has just issued a warning about a serious security incident related to the Meter.io project.
Specifically, more than 1 billion tokens #MTRG đ were illicitly minted on the #BNBChain network. Shortly after this information was released, the price of #MTRG recorded a sharp drop of -74%.
👀 Market Watch:
$MTRG
Investors should be cautious and closely monitor official announcements from the project to stay updated on the situation.
#CryptoNews #SecurityAlert
40

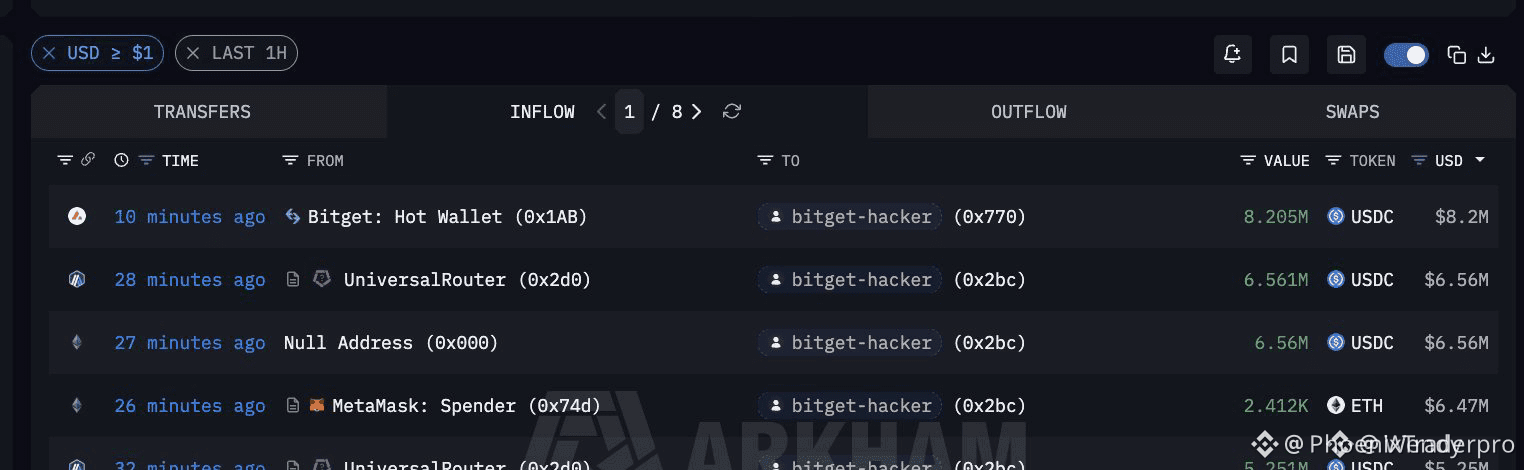
🚨 ONGOING SECURITY BREACH SURFACES AS ATTACKER DRAINS ANOTHER $8M FROM $CRYPTO POOLS! ⚠️
The exploit saga deepens as smart contract vulnerabilities remain actively exploited. 🚨 The attacker just siphoned an additional $8M out of protocol reserves, proving that compromised access key channels are still wide open.
Smart money is pulling back liquidity rapidly while watching order flow for sudden dump spikes or laundering routes through mixing services. 📉 When contract integrity breaks, immediate risk preservation trumps every technical pattern on the chart.
Stay nimble and keep an eye on active treasury movements before deploying fresh capital. 🔍 Are you pulling your capital to safety, or waiting to bid the eventual capitulation wick? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #Crypto #SecurityAlert #DeFi #RiskManagement #MarketUpdate
🚨 🛡️
10
·
--
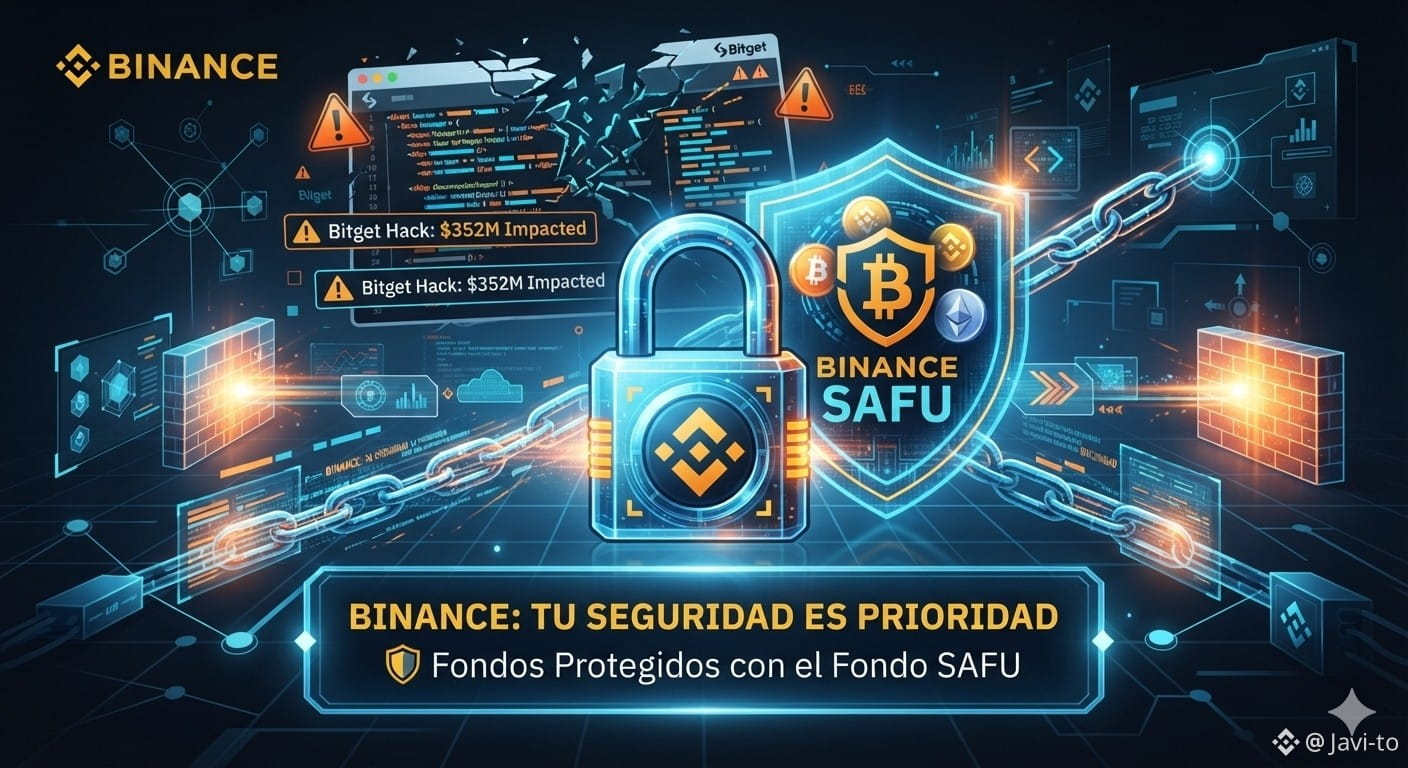
🚨 Are your funds really safe? The recent million-dollar hack to Bitget for $352 million set off alarms across the crypto world. Although its CEO, Gracy Chen, said that users’ capital is backed by its protection fund, this event reminds us how important it is to choose platforms with the highest level of security infrastructure. [1, 2, 3, 4]
At Binance, protection is not a promise—it’s an active standard. With the SAFU fund (Safe Asset Fund for Users), strict real-time wallet monitoring, and 1:1 Proof of Reserves (PoR), your peace of mind is our top priority.
#SecurityAlert #SecurityTokenization
{spot}(DOGEUSDT)
{spot}(SOLUSDT)
{spot}(PEPEUSDT)
🔒 Your security first!
🚨 Are your funds really safe? The recent million-dollar hack to Bitget for $352 million set off alarms across the crypto world. Although its CEO, Gracy Chen, said that users’ capital is backed by its protection fund, this event reminds us how important it is to choose platforms with the highest level of security infrastructure. [1, 2, 3, 4]
At Binance, protection is not a promise—it’s an active standard. With the SAFU fund (Safe Asset Fund for Users), strict real-time wallet monitoring, and 1:1 Proof of Reserves (PoR), your peace of mind is our top priority.
#SecurityAlert #SecurityTokenization
🔒 Your security first!
At Binance, protection is not a promise—it’s an active standard. With the SAFU fund (Safe Asset Fund for Users), strict real-time wallet monitoring, and 1:1 Proof of Reserves (PoR), your peace of mind is our top priority.
#SecurityAlert #SecurityTokenization
🔒 Your security first!
2
392

·
--
🚨 $CRYPTO PLATFORM BREACH EXPOSES $351M LIQUIDITY DRAIN IN ADVANCED EXPLOIT 🔍
Preliminary investigation into the recent $351.6M exploit on a top-tier exchange points toward state-sponsored cyber footprint patterns. 📊 System-level access allowed direct fund transfers without compromising hot or cold wallet private keys, ruling out insider manipulation at this stage.
💡 Institutional infrastructure risk remains a crucial variable when assessing market-wide liquidity stability. 🔍 As order flow normalizes, monitoring exchange proof-of-reserves and system integrity becomes essential for managing systemic tail risk. 💬 How is this systemic security event impacting your allocation strategy across central order books? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #CRYPTO #SecurityAlert #MarketStructure #RiskManagement
🛡️ 🔍
13
·
--
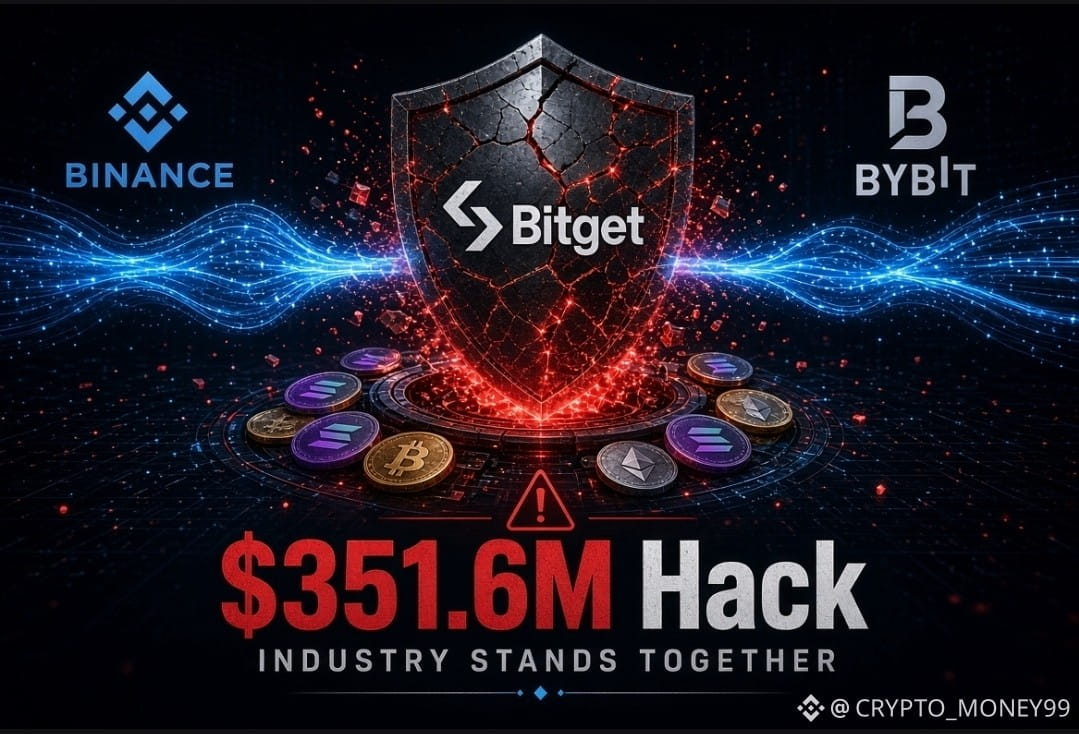
🚨 Bitget hacked for $351.6 million… and the industry unites
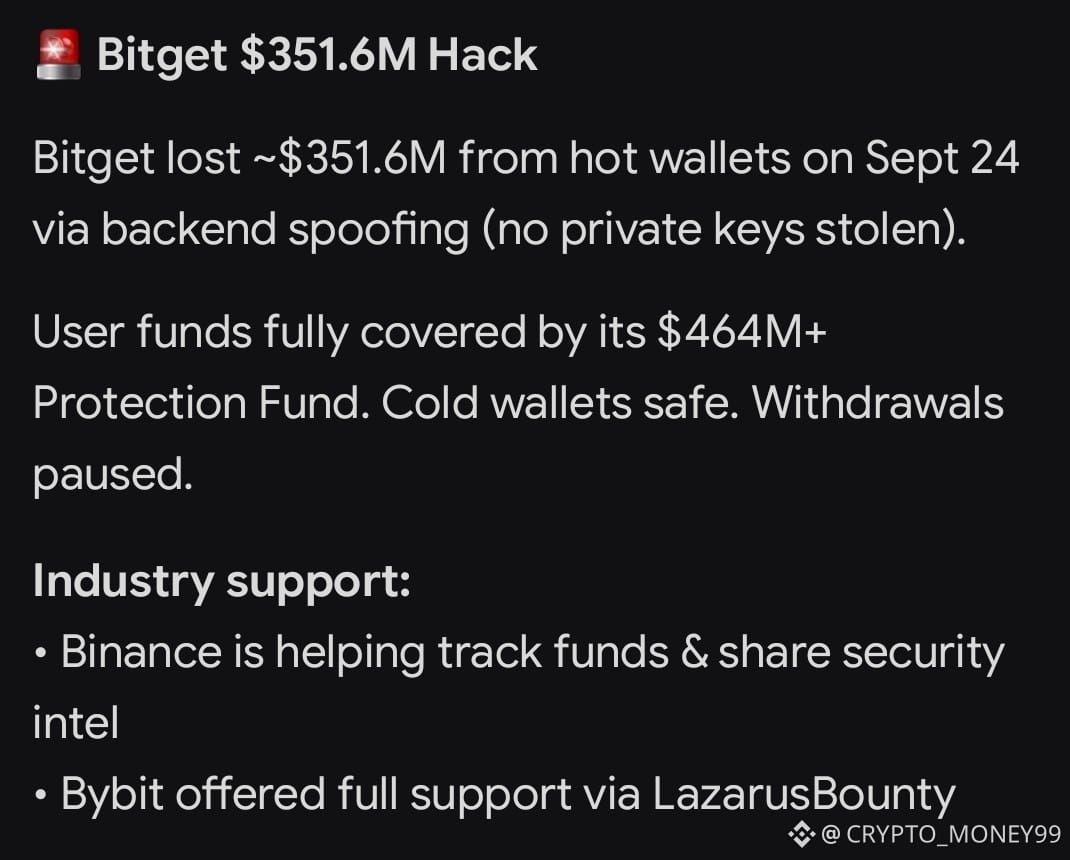
On September 24, Bitget suffered a breach affecting hot wallets worth approximately $351.6 million.
Private keys were not stolen; the attack targeted the backend system by forging transaction data.
Key points:
• Users’ funds are safe and fully covered by the Protection Fund (over $464 million).
• Cold wallets were not affected.
• Withdrawals are temporarily paused, while trading and deposits continue.
What stands out in this incident is the stance taken by industry leaders:
🔹 Binance (via Co-CEO Richard Teng): announced that Binance’s security team has been working closely with Bitget since the very first moment, sharing security information, tracking the movement of stolen funds, and supporting recovery efforts.
🔹 Bybit (via Ben Zhou): provided full support and activated the LazarusBounty platform to track the funds, confirming that Bitget had helped them previously in a similar incident.
This collaboration reminds us that exchange attacks are no longer a solitary matter… but a collective battle between the industry and the attackers.
What do you think? Is having Protection Funds enough, or is reliance on hot wallets still a major weakness?
#SecurityAlert #HackerNews #crypto #Binance #BTC
4
2.2k

·
--
🚨 $1.8M DRAINED FROM PAYY NETWORK AS ATTACKER ROUTES STOLEN FUNDS TO $ETH 💣
🔍 On-chain monitors just caught a slick exploit trail where privacy stablecoin protocol Payy Network suffered a $1.8M USDC drain. The attacker primed their wallet via Railgun privacy protocol, converted the hijacked stablecoins directly into $ETH , and fractured the payload across three distinct destination addresses.
📊 Privacy protocols continue to grant bad actors a crucial head start to wash liquidity before re-entering major layer-1 assets. Order flow never lies, and watching where these ETH clusters attempt to cash out next is vital for anticipating sudden localized sell pressure. 💬 Do privacy rails make on-chain defense an uphill battle, or is this just brutal market punishment for weak smart contracts? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #USDC #SecurityAlert #DeFi #Crypto
👁️ 🛡️
11
·
--
🚨 CRITICAL SECURITY WARNING FOR ALL $BTC AND CRYPTO HOLDERS ON IOS! ⚠️
A malicious third-party app called FomoPeek is actively exploiting iOS vulnerabilities to target crypto users. ⚠️ Security intelligence confirms the app gains elevated root privileges, exposing private keys, seed phrases, and exchange credentials stored on the device. 🛡️
If you installed this application, act immediately. Delete FomoPeek, update your iOS system software, and sweep your $ETH assets to a brand-new wallet generated on a safe device before unauthorized actors access your vault. 🏦
Tight device security protects your capital just as much as disciplined risk management. 💬 Have you checked your installed mobile apps today to verify your self-custody setup is secure? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #ETH #SecurityAlert #CryptoSecurity #SelfCustody
🚨 🛡️
10
·
--
🚨 SECURITY ALERT: FOMOPEEK IOS EXPLOIT RISKS SELF-CUSTODY $BTC AND SEED PHRASES ⚠️
Institutional risk management extends beyond chart structure down to device security. 🚨 Critical security advisories flag FomoPeek versions 1.1–1.2 on iOS containing malicious vector code capable of escalating privileges to compromise global operational security across your device. 🔍
This is not an isolated wallet breach; elevated local permissions expose private keys, seed phrases, and credential stores across all installed applications. 🛡️ Immediate mitigation requires purging the application, updating iOS, and rotating self-custody funds into newly generated keys on an uncompromised environment. 💡
💬 Have you audited your active iOS devices for this compromised application footprint today? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #SecurityAlert #SelfCustody #CryptoSecurity
🛡️ 💡
34
·
--
🚨 CRITICAL SECURITY WARNING FOR ALL $BTC HOLDERS USING FOMOPEEK APP! 🚨
A devastating iOS kernel exploit embedded in FomoPeek versions 1.1 through 1.2 is actively breaching device sandboxes to decrypt native Keychain data. 🚨 SlowMist and a top-tier exchange security team confirmed the malicious code executes automated remote commands, granting attackers full access to private keys and seed phrases. 🛡️
If you have ever touched this application, generate a fresh wallet on a clean device immediately and migrate your funds before liquidity is drained. 🔍 Security hygiene is the ultimate edge in crypto, and protecting your capital comes before catching the next leg up. 💬 Have you audited your wallet permissions and app access lately? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #SecurityAlert #Crypto #WalletSecurity #RiskManagement
🚨 🛡️
19

·
--
🚨 $BTC ALERT: FAKE HARDWARE WALLET WARNINGS SPREAD VIA EMAIL BREACH 🦈
📊 The breach centers on email infrastructure, not the wallets themselves. Trezor confirmed a compromised mail service, while BitBox flagged a shared newsletter provider targeting multiple Bitcoin firms. 📌 This supply‑chain slip allows attackers to masquerade as trusted brands, leveraging brand credibility to push fraudulent security alerts.
🔍 Treat any unexpected wallet security email as unverified: pause, cross‑check through official channels, and never act on urgent links or requests. 💡 The hardware remains secure, but the communication layer is now a high‑risk vector.
💬 How are you reinforcing verification steps for critical alerts? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #SecurityAlert #CryptoSafety #Phishing
🔥 💎
53
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#ZcashETFPostsFirstWeeklyOutflow$93.6M
23,039 views
63 Discussing
2
#GreekPoliceBustCryptoScamRingArrest17
31,175 views
354 Discussing
3
#BitcoinRejectedAt$87K
99,148 views
125 Discussing
4
#FedOctoberRateHikeOddsFallTo17%
66,154 views
718 Discussing
5
#NvidiaHitsRecordHighUp2.4%
38,384 views
502 Discussing
6
#CanaryFilesAmendedS1ForPEPEETF
12,977 views
335 Discussing
7
#USRussiaUkraineTalksReportedlyIncludeLukoilOilDeal
21,915 views
371 Discussing
8
#BitcoinParesGainsAfterRallyTo$86.5K
43,582 views
157 Discussing
9
#CerebrasSinksNearly20%OnReportNvidiaToPowerOpenAI
102,346 views
997 Discussing
10
#SECProposesCryptoCustodyRules
135,618 views
1,241 Discussing