
#safepal
safepal
107,646 views
248 Discussing
Hot
Latest
·
--
Bullish
🚀 $SFP
{spot}(SFPUSDT)
— BREAKOUT MOMENTUM 🔥
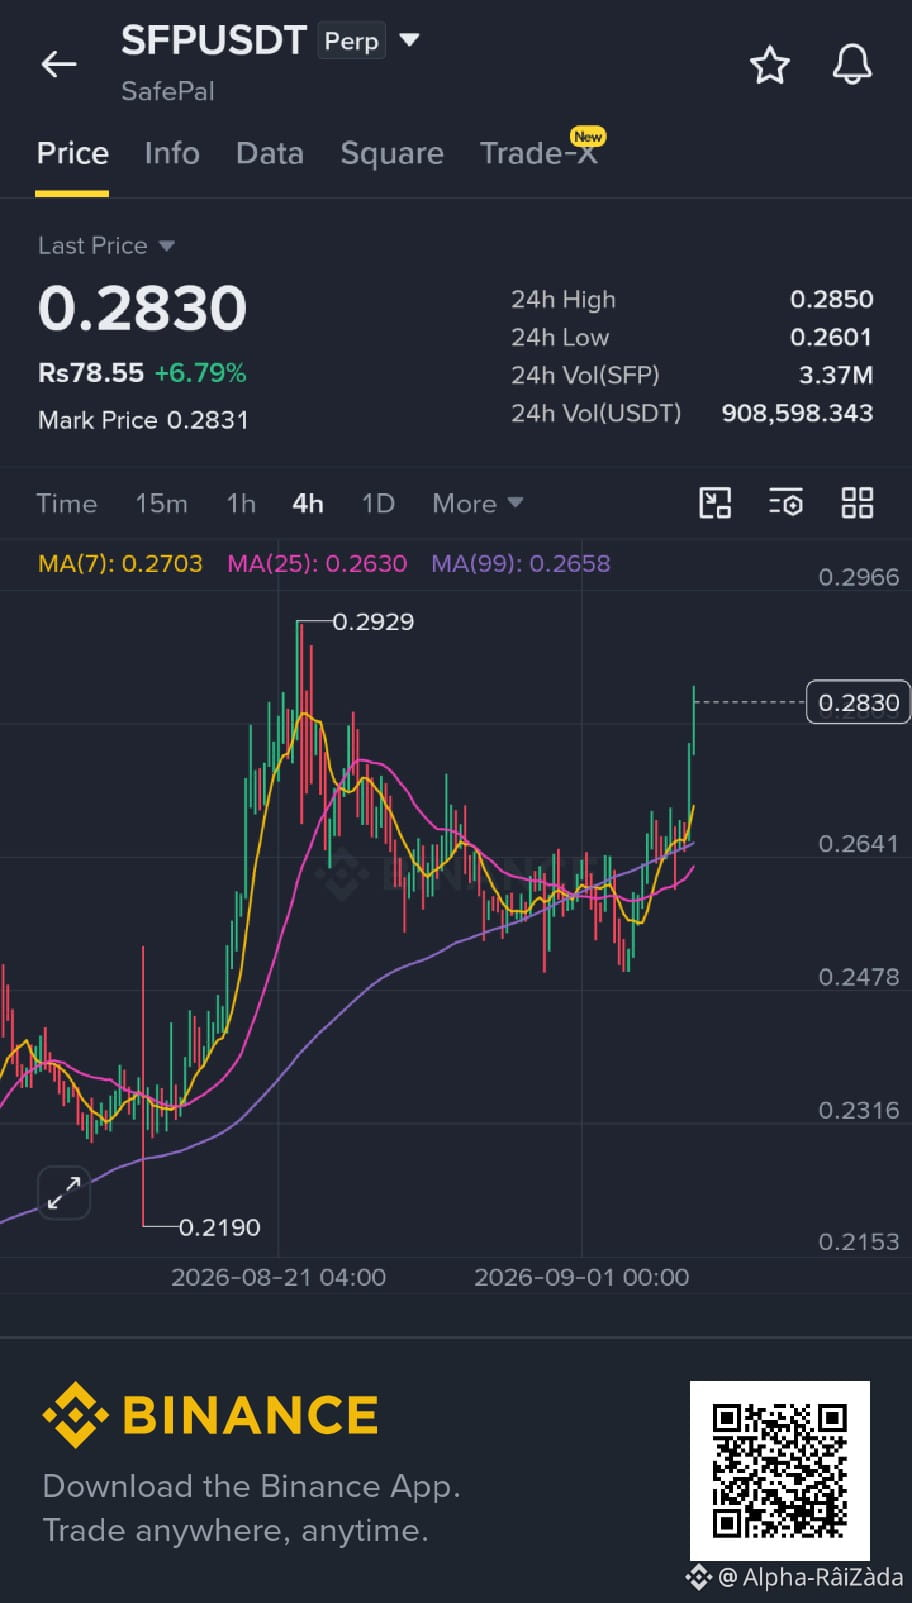
$SFP has pushed out of the $0.26–$0.27 consolidation range and is testing the $0.285 resistance. Current market data also shows SFP trading near the $0.28 area with positive momentum.
📍 ENTRY: $0.280–$0.285
🎯 TP1: $0.290
🎯 TP2: $0.300
🎯 TP3: $0.315
🛑 SL: $0.272
🔑 Key: Hold above $0.28 → breakout continuation remains in focus.
⚠️ Wait for confirmation/retest and avoid chasing. DYOR • NFA
#SFP #SafePal #Breakout #LongSetup
🚀 $SFP
— BREAKOUT MOMENTUM 🔥
$SFP has pushed out of the $0.26–$0.27 consolidation range and is testing the $0.285 resistance. Current market data also shows SFP trading near the $0.28 area with positive momentum.
📍 ENTRY: $0.280–$0.285
🎯 TP1: $0.290
🎯 TP2: $0.300
🎯 TP3: $0.315
🛑 SL: $0.272
🔑 Key: Hold above $0.28 → breakout continuation remains in focus.
⚠️ Wait for confirmation/retest and avoid chasing. DYOR • NFA
#SFP #SafePal #Breakout #LongSetup
— BREAKOUT MOMENTUM 🔥
$SFP has pushed out of the $0.26–$0.27 consolidation range and is testing the $0.285 resistance. Current market data also shows SFP trading near the $0.28 area with positive momentum.
📍 ENTRY: $0.280–$0.285
🎯 TP1: $0.290
🎯 TP2: $0.300
🎯 TP3: $0.315
🛑 SL: $0.272
🔑 Key: Hold above $0.28 → breakout continuation remains in focus.
⚠️ Wait for confirmation/retest and avoid chasing. DYOR • NFA
#SFP #SafePal #Breakout #LongSetup
1

🚨 SafePal is bringing in outside security firms after the data leak incident.
SafePal said they are currently:
🔎 Tracking scam websites and fake accounts on a daily basis
🛡️ Choosing 1 of 4 anti-phishing companies to help handle takedowns faster
🌑 Continuing to monitor the dark web to detect leaked data being sold or publicly posted
🔐 Choosing 1 of 3 independent security organizations to conduct a comprehensive audit of the ordering system
At the same time, SafePal also said that its ordering and shipping process is being reviewed to reduce the amount of data stored.
A particularly important warning:
SafePal will never ask for a seed phrase/recovery phrase.
If you receive a message requesting your seed phrase, to scan a QR code, or to click on a suspicious link:
Don’t do it. 🚨
In cases involving crypto wallets, sometimes data leaks are only the first step—what’s more dangerous next is the phishing.
If you’re using SafePal, make sure to carefully check every communication channel before interacting.
Not your seed phrase, not your keys.
STAYSAFE
#BrainrotCrypto #SafePal
🚨 SafePal is bringing in outside security firms after the data leak incident.
SafePal said they are currently:
🔎 Tracking scam websites and fake accounts on a daily basis
🛡️ Choosing 1 of 4 anti-phishing companies to help handle takedowns faster
🌑 Continuing to monitor the dark web to detect leaked data being sold or publicly posted
🔐 Choosing 1 of 3 independent security organizations to conduct a comprehensive audit of the ordering system
At the same time, SafePal also said that its ordering and shipping process is being reviewed to reduce the amount of data stored.
A particularly important warning:
SafePal will never ask for a seed phrase/recovery phrase.
If you receive a message requesting your seed phrase, to scan a QR code, or to click on a suspicious link:
Don’t do it. 🚨
In cases involving crypto wallets, sometimes data leaks are only the first step—what’s more dangerous next is the phishing.
If you’re using SafePal, make sure to carefully check every communication channel before interacting.
Not your seed phrase, not your keys.
STAYSAFE
#BrainrotCrypto #SafePal
SafePal said they are currently:
🔎 Tracking scam websites and fake accounts on a daily basis
🛡️ Choosing 1 of 4 anti-phishing companies to help handle takedowns faster
🌑 Continuing to monitor the dark web to detect leaked data being sold or publicly posted
🔐 Choosing 1 of 3 independent security organizations to conduct a comprehensive audit of the ordering system
At the same time, SafePal also said that its ordering and shipping process is being reviewed to reduce the amount of data stored.
A particularly important warning:
SafePal will never ask for a seed phrase/recovery phrase.
If you receive a message requesting your seed phrase, to scan a QR code, or to click on a suspicious link:
Don’t do it. 🚨
In cases involving crypto wallets, sometimes data leaks are only the first step—what’s more dangerous next is the phishing.
If you’re using SafePal, make sure to carefully check every communication channel before interacting.
Not your seed phrase, not your keys.
STAYSAFE
#BrainrotCrypto #SafePal
469
·
--
Three hardware-wallet incidents in three weeks: the exposure surface has shifted from keys to identityOn August 16, SafePal disclosed an authorization flaw in its order lookup system: by modifying the order number, users can view other people’s order information. About 39,798 customers are affected. The leaked content includes names, email addresses, phone numbers, shipping addresses, and purchase details, covering orders placed between March 2, 2025 and April 11, 2026. Private keys, recovery mnemonics, and wallet passwords were not affected.
SafePal’s remediation actions are worth recording: it has taken down more than 30 phishing sites built using this batch of data, shortened the retention period of personal data to 90 days, notified affected customers one by one, and hired an independent security company to audit and verify the remediation results.
Three hardware-wallet incidents in three weeks: the exposure surface has shifted from keys to identity
On August 16, SafePal disclosed an authorization flaw in its order lookup system: by modifying the order number, users can view other people’s order information. About 39,798 customers are affected. The leaked content includes names, email addresses, phone numbers, shipping addresses, and purchase details, covering orders placed between March 2, 2025 and April 11, 2026. Private keys, recovery mnemonics, and wallet passwords were not affected.
SafePal’s remediation actions are worth recording: it has taken down more than 30 phishing sites built using this batch of data, shortened the retention period of personal data to 90 days, notified affected customers one by one, and hired an independent security company to audit and verify the remediation results.
SafePal’s remediation actions are worth recording: it has taken down more than 30 phishing sites built using this batch of data, shortened the retention period of personal data to 90 days, notified affected customers one by one, and hired an independent security company to audit and verify the remediation results.
1
92
SafePal officially integrates the Robinhood L2 mainnet, making the RWAFi path wider and wider.
In addition to connecting L2, SafePal has already launched native stock token trading on the Robinhood Chain. Going forward, it will also partner with perpetual DEX to deepen on-chain liquidity and trading depth together.
Combined with tokenized-asset protocols previously integrated, such as xStocks and Ondo, users can now directly access on-chain exposure to NVIDIA, Tesla, and SpaceX stocks—as well as commodities like the S&P 500 ETF and gold—right within the wallet.
Personal perspective: the wallet is no longer just a sending/receiving tool; it’s gradually becoming a “gateway to on-chain brokerage.” When traditional assets are moved onto the chain, whoever can provide the smoothest deposit + trading + custody closed-loop will capture the next wave of RWA user growth.
#SafePal #RWA #Robinhood
SafePal officially integrates the Robinhood L2 mainnet, making the RWAFi path wider and wider.
In addition to connecting L2, SafePal has already launched native stock token trading on the Robinhood Chain. Going forward, it will also partner with perpetual DEX to deepen on-chain liquidity and trading depth together.
Combined with tokenized-asset protocols previously integrated, such as xStocks and Ondo, users can now directly access on-chain exposure to NVIDIA, Tesla, and SpaceX stocks—as well as commodities like the S&P 500 ETF and gold—right within the wallet.
Personal perspective: the wallet is no longer just a sending/receiving tool; it’s gradually becoming a “gateway to on-chain brokerage.” When traditional assets are moved onto the chain, whoever can provide the smoothest deposit + trading + custody closed-loop will capture the next wave of RWA user growth.
#SafePal #RWA #Robinhood
In addition to connecting L2, SafePal has already launched native stock token trading on the Robinhood Chain. Going forward, it will also partner with perpetual DEX to deepen on-chain liquidity and trading depth together.
Combined with tokenized-asset protocols previously integrated, such as xStocks and Ondo, users can now directly access on-chain exposure to NVIDIA, Tesla, and SpaceX stocks—as well as commodities like the S&P 500 ETF and gold—right within the wallet.
Personal perspective: the wallet is no longer just a sending/receiving tool; it’s gradually becoming a “gateway to on-chain brokerage.” When traditional assets are moved onto the chain, whoever can provide the smoothest deposit + trading + custody closed-loop will capture the next wave of RWA user growth.
#SafePal #RWA #Robinhood
4
·
--
🚨 SAFEPAL DATA EXPOSURE AFFECTS 40K USERS — $PORTAL & $DOLO WATCHED CLOSELY ⚡
🔍 The SafePal breach is a classic “keys intact, optics hit” event — client information exposed, but private keys and seed phrases untouched. That narrows the fundamental damage, but the optics still create a risk-off overhang across $PORTAL and $DOLO liquidity pools. 📊
💡 Institutional traders are watching whether this stays an isolated reputation event or morphs into broader trust concerns. No key compromise means technical structure remains the primary driver. 📌 Watch for a sharp squeeze if the next update confirms zero wallet compromise. 💬 Are you buying the headline dip or trimming risk until confirmation? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #PORTAL #DOLO #SafePal #CryptoNews #Binance
⚖️ 🔒
🚨 SAFEPAL DATA EXPOSURE AFFECTS 40K USERS — $PORTAL & $DOLO WATCHED CLOSELY ⚡
🔍 The SafePal breach is a classic “keys intact, optics hit” event — client information exposed, but private keys and seed phrases untouched. That narrows the fundamental damage, but the optics still create a risk-off overhang across $PORTAL and $DOLO liquidity pools. 📊
💡 Institutional traders are watching whether this stays an isolated reputation event or morphs into broader trust concerns. No key compromise means technical structure remains the primary driver. 📌 Watch for a sharp squeeze if the next update confirms zero wallet compromise. 💬 Are you buying the headline dip or trimming risk until confirmation? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #PORTAL #DOLO #SafePal #CryptoNews #Binance
⚖️ 🔒
🔍 The SafePal breach is a classic “keys intact, optics hit” event — client information exposed, but private keys and seed phrases untouched. That narrows the fundamental damage, but the optics still create a risk-off overhang across $PORTAL and $DOLO liquidity pools. 📊
💡 Institutional traders are watching whether this stays an isolated reputation event or morphs into broader trust concerns. No key compromise means technical structure remains the primary driver. 📌 Watch for a sharp squeeze if the next update confirms zero wallet compromise. 💬 Are you buying the headline dip or trimming risk until confirmation? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #PORTAL #DOLO #SafePal #CryptoNews #Binance
⚖️ 🔒
128
·
--
Bullish
$SFP
{spot}(SFPUSDT)
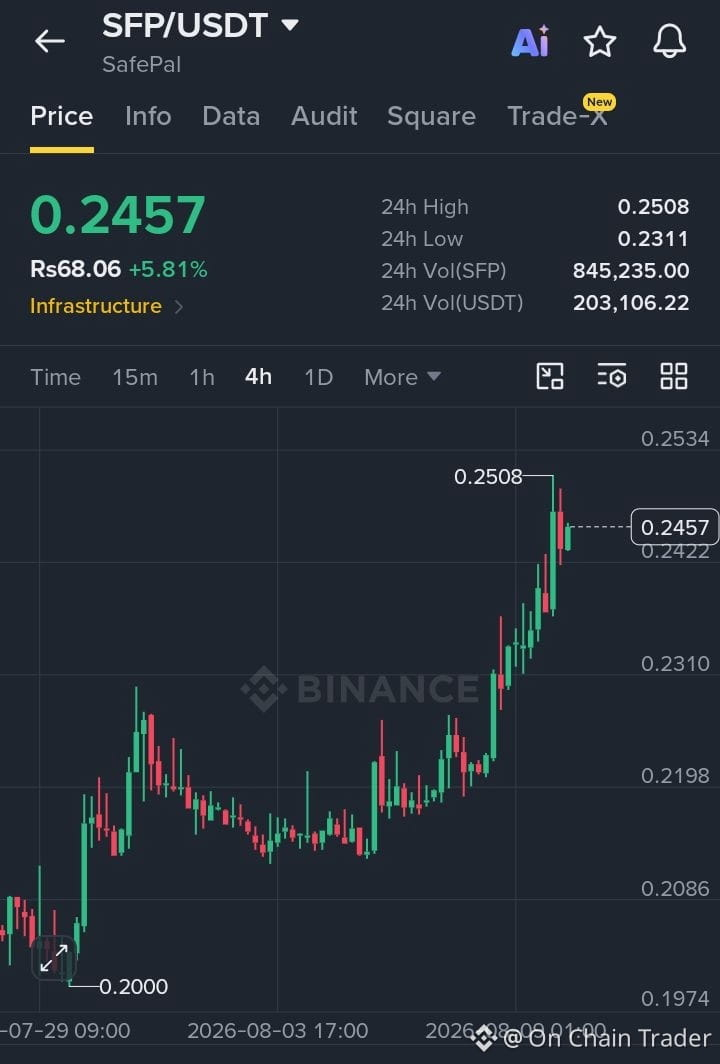
/USDT — STRONG BULLISH SETUP
SFP is breaking higher with strong momentum and holding above $0.2420.
Entry: $0.2410–$0.2450
TP1: $0.2508 | TP2: $0.2600 | TP3: $0.2750
SL: $0.2320
Bias: BULLISH — breakout above $0.2508 can open the door to another leg up.
#SFP #SafePal #Crypto #BinanceSquare
$SFP
/USDT — STRONG BULLISH SETUP
SFP is breaking higher with strong momentum and holding above $0.2420.
Entry: $0.2410–$0.2450
TP1: $0.2508 | TP2: $0.2600 | TP3: $0.2750
SL: $0.2320
Bias: BULLISH — breakout above $0.2508 can open the door to another leg up.
#SFP #SafePal #Crypto #BinanceSquare
/USDT — STRONG BULLISH SETUP
SFP is breaking higher with strong momentum and holding above $0.2420.
Entry: $0.2410–$0.2450
TP1: $0.2508 | TP2: $0.2600 | TP3: $0.2750
SL: $0.2320
Bias: BULLISH — breakout above $0.2508 can open the door to another leg up.
#SFP #SafePal #Crypto #BinanceSquare
1
105
·
--
🚨 SAFEPAL VENDOR BREACH EXPOSES 40K CUSTOMERS WHILE $SFP FUNDS REMAIN SAFE! 🛡️
A third-party supply chain flaw just leaked personal shipping details for 39,798 hardware wallet buyers. While private keys and seed phrases remain untouched in cold storage, physical delivery data is now floating in bad actors' hands. 🔍
This highlights the classic supply chain blind spot where e-commerce logistics expose offline holders to targeted phishing and social engineering. Smart money stays alert when fake brand communications inevitably start flooding inboxes. 💡
💬 Are you scrubbing your digital footprint when ordering hardware security, or do you rely entirely on cold storage silicon? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SFP #SecurityAlert #CryptoSecurity #SafePal
🎯 🛡️
🚨 SAFEPAL VENDOR BREACH EXPOSES 40K CUSTOMERS WHILE $SFP FUNDS REMAIN SAFE! 🛡️
A third-party supply chain flaw just leaked personal shipping details for 39,798 hardware wallet buyers. While private keys and seed phrases remain untouched in cold storage, physical delivery data is now floating in bad actors' hands. 🔍
This highlights the classic supply chain blind spot where e-commerce logistics expose offline holders to targeted phishing and social engineering. Smart money stays alert when fake brand communications inevitably start flooding inboxes. 💡
💬 Are you scrubbing your digital footprint when ordering hardware security, or do you rely entirely on cold storage silicon? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SFP #SecurityAlert #CryptoSecurity #SafePal
🎯 🛡️
A third-party supply chain flaw just leaked personal shipping details for 39,798 hardware wallet buyers. While private keys and seed phrases remain untouched in cold storage, physical delivery data is now floating in bad actors' hands. 🔍
This highlights the classic supply chain blind spot where e-commerce logistics expose offline holders to targeted phishing and social engineering. Smart money stays alert when fake brand communications inevitably start flooding inboxes. 💡
💬 Are you scrubbing your digital footprint when ordering hardware security, or do you rely entirely on cold storage silicon? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SFP #SecurityAlert #CryptoSecurity #SafePal
🎯 🛡️
40

·
--
BIG NEWS😐
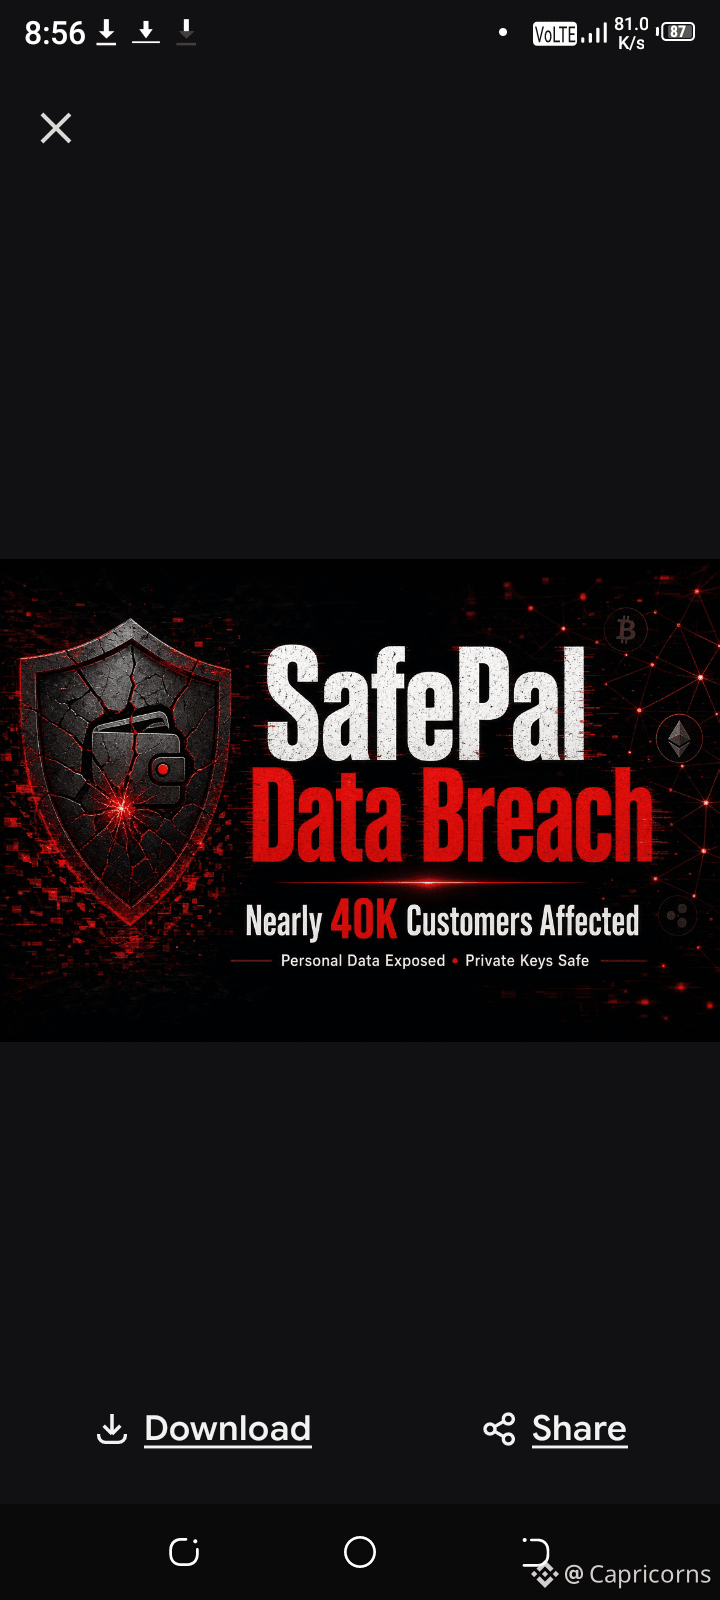
🚨 SafePal Data Breach: Nearly 40K Customers Affected
Crypto wallet provider SafePal has disclosed a data breach affecting 39,798 customers, exposing names, addresses and contact details linked to orders.
🔐 The good news: Private keys, seed phrases, passwords and crypto funds were not compromised.
⚠️ The bigger risk now? Phishing and impersonation scams targeting affected users.
Crypto security isn’t just about protecting your keys — your personal data matters too.
#SafePal #CryptoNewss
BIG NEWS😐
🚨 SafePal Data Breach: Nearly 40K Customers Affected
Crypto wallet provider SafePal has disclosed a data breach affecting 39,798 customers, exposing names, addresses and contact details linked to orders.
🔐 The good news: Private keys, seed phrases, passwords and crypto funds were not compromised.
⚠️ The bigger risk now? Phishing and impersonation scams targeting affected users.
Crypto security isn’t just about protecting your keys — your personal data matters too.
#SafePal #CryptoNewss
🚨 SafePal Data Breach: Nearly 40K Customers Affected
Crypto wallet provider SafePal has disclosed a data breach affecting 39,798 customers, exposing names, addresses and contact details linked to orders.
🔐 The good news: Private keys, seed phrases, passwords and crypto funds were not compromised.
⚠️ The bigger risk now? Phishing and impersonation scams targeting affected users.
Crypto security isn’t just about protecting your keys — your personal data matters too.
#SafePal #CryptoNewss
53

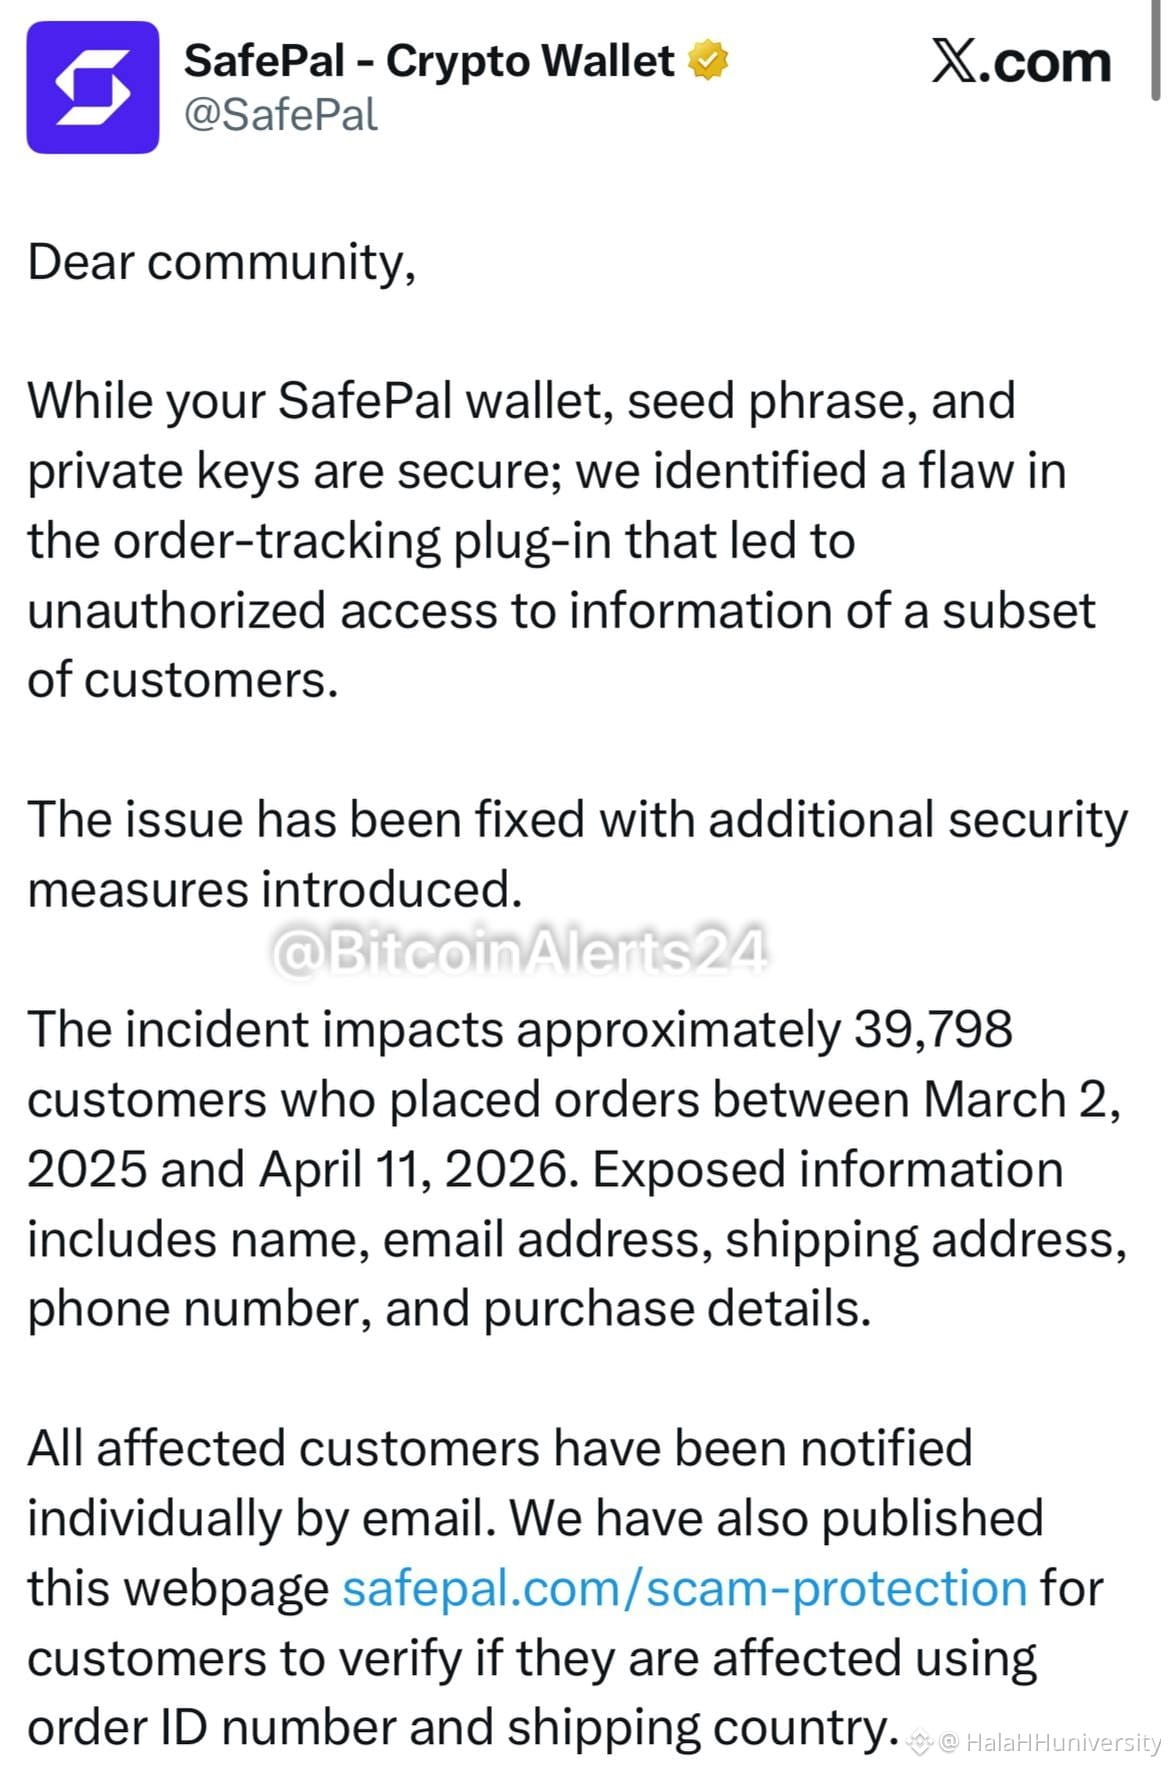
SafePal Official Twitter Discloses: Its Order Tracking Plugin Reportedly Has a Security Vulnerability, With 39,798 Customers’ Information Accessed Without Authorization Between March 2, 2025 and April 11, 2026.
The leaked data includes sensitive fields such as names, email addresses, shipping addresses, phone numbers, and purchase details, covering a fairly wide scope. At present, SafePal states that it has completed the fix by introducing additional security measures, and has sent separate email notifications to all affected users; the investigation is still ongoing.
From a user’s perspective, this incident again reminds us of several key points:
1. Third-party plugins are the attack surface in a wallet ecosystem that is easiest to overlook. Even if the main application is as tightly secured as possible, as long as a flaw exists in any part of the supply chain, user data could be leaked in bulk.
2. Even for non-custodial wallet brands, they often still need to maintain Web2 backend systems such as e-commerce, logistics, and order management—and these systems are also subject to traditional data security standards. If they are not properly managed, the damage is not only to brand reputation, but also to real compliance costs in terms of money.
3. After users receive the relevant notifications, they should immediately check for phishing risks. Attackers often conduct secondary scams using phrases such as “resend the order” and “security update.” Do not click links in unfamiliar emails.
Trust in the Web3 industry is built slowly, but can collapse in an instant. We hope more project teams will prioritize infrastructure security even further while pursuing functional iterations.
#SafePal #Web3安全 #privacy protection
SafePal Official Twitter Discloses: Its Order Tracking Plugin Reportedly Has a Security Vulnerability, With 39,798 Customers’ Information Accessed Without Authorization Between March 2, 2025 and April 11, 2026.
The leaked data includes sensitive fields such as names, email addresses, shipping addresses, phone numbers, and purchase details, covering a fairly wide scope. At present, SafePal states that it has completed the fix by introducing additional security measures, and has sent separate email notifications to all affected users; the investigation is still ongoing.
From a user’s perspective, this incident again reminds us of several key points:
1. Third-party plugins are the attack surface in a wallet ecosystem that is easiest to overlook. Even if the main application is as tightly secured as possible, as long as a flaw exists in any part of the supply chain, user data could be leaked in bulk.
2. Even for non-custodial wallet brands, they often still need to maintain Web2 backend systems such as e-commerce, logistics, and order management—and these systems are also subject to traditional data security standards. If they are not properly managed, the damage is not only to brand reputation, but also to real compliance costs in terms of money.
3. After users receive the relevant notifications, they should immediately check for phishing risks. Attackers often conduct secondary scams using phrases such as “resend the order” and “security update.” Do not click links in unfamiliar emails.
Trust in the Web3 industry is built slowly, but can collapse in an instant. We hope more project teams will prioritize infrastructure security even further while pursuing functional iterations.
#SafePal #Web3安全 #privacy protection
The leaked data includes sensitive fields such as names, email addresses, shipping addresses, phone numbers, and purchase details, covering a fairly wide scope. At present, SafePal states that it has completed the fix by introducing additional security measures, and has sent separate email notifications to all affected users; the investigation is still ongoing.
From a user’s perspective, this incident again reminds us of several key points:
1. Third-party plugins are the attack surface in a wallet ecosystem that is easiest to overlook. Even if the main application is as tightly secured as possible, as long as a flaw exists in any part of the supply chain, user data could be leaked in bulk.
2. Even for non-custodial wallet brands, they often still need to maintain Web2 backend systems such as e-commerce, logistics, and order management—and these systems are also subject to traditional data security standards. If they are not properly managed, the damage is not only to brand reputation, but also to real compliance costs in terms of money.
3. After users receive the relevant notifications, they should immediately check for phishing risks. Attackers often conduct secondary scams using phrases such as “resend the order” and “security update.” Do not click links in unfamiliar emails.
Trust in the Web3 industry is built slowly, but can collapse in an instant. We hope more project teams will prioritize infrastructure security even further while pursuing functional iterations.
#SafePal #Web3安全 #privacy protection
31

SafePal data leak affects 40k customers
- Data leak: 40,000 accounts exposed order information
- Private keys, seed phrases, and crypto assets are not affected
#SafePal #CryptoSecurity #BTC #ETH
$btc $eth
#vlikevn Titanbot
Source: CoinDesk
SafePal data leak affects 40k customers
- Data leak: 40,000 accounts exposed order information
- Private keys, seed phrases, and crypto assets are not affected
#SafePal #CryptoSecurity #BTC #ETH
$btc $eth
#vlikevn Titanbot
Source: CoinDesk
- Data leak: 40,000 accounts exposed order information
- Private keys, seed phrases, and crypto assets are not affected
#SafePal #CryptoSecurity #BTC #ETH
$btc $eth
#vlikevn Titanbot
Source: CoinDesk
113
·
--
Bearish
SafePal reveals a data breach involving around 40,000 customers
SafePal announced a security incident that exposed personal data for approximately 40,000 customers, including names, residential addresses, and phone numbers.
According to the company, a vulnerability in an order-tracking system was exploited to gain unauthorized access to order data for more than a year. More than 30 phishing sites associated with the leaked data were also detected and taken down.
🔐 Most important: SafePal confirms that users’ Seed Phrases, private keys, and funds were not affected.
However, the incident highlights an important point in the Web3 world:
Protecting assets doesn’t only mean protecting private keys—it also means protecting personal data from being exploited in phishing and social engineering attacks.
If you are among those affected, avoid any messages or links that ask you for a Seed Phrase or Private Key, or claim you need to “secure” your funds.
In crypto, the attack may start with personal information… and end with an attempt to access your money.
{future}(SFPUSDT)
#SafePal #CryptoSecurity
#CyberSecurity #Web3
SafePal reveals a data breach involving around 40,000 customers
SafePal announced a security incident that exposed personal data for approximately 40,000 customers, including names, residential addresses, and phone numbers.
According to the company, a vulnerability in an order-tracking system was exploited to gain unauthorized access to order data for more than a year. More than 30 phishing sites associated with the leaked data were also detected and taken down.
🔐 Most important: SafePal confirms that users’ Seed Phrases, private keys, and funds were not affected.
However, the incident highlights an important point in the Web3 world:
Protecting assets doesn’t only mean protecting private keys—it also means protecting personal data from being exploited in phishing and social engineering attacks.
If you are among those affected, avoid any messages or links that ask you for a Seed Phrase or Private Key, or claim you need to “secure” your funds.
In crypto, the attack may start with personal information… and end with an attempt to access your money.
#SafePal #CryptoSecurity
#CyberSecurity #Web3
SafePal announced a security incident that exposed personal data for approximately 40,000 customers, including names, residential addresses, and phone numbers.
According to the company, a vulnerability in an order-tracking system was exploited to gain unauthorized access to order data for more than a year. More than 30 phishing sites associated with the leaked data were also detected and taken down.
🔐 Most important: SafePal confirms that users’ Seed Phrases, private keys, and funds were not affected.
However, the incident highlights an important point in the Web3 world:
Protecting assets doesn’t only mean protecting private keys—it also means protecting personal data from being exploited in phishing and social engineering attacks.
If you are among those affected, avoid any messages or links that ask you for a Seed Phrase or Private Key, or claim you need to “secure” your funds.
In crypto, the attack may start with personal information… and end with an attempt to access your money.
#SafePal #CryptoSecurity
#CyberSecurity #Web3
2
225
SafePal Wallet has recently disclosed a data security incident. In a post, its official account stated that a vulnerability was found in an order-tracking plugin, which led to unauthorized access to some customers’ information.
According to the official statement, the incident affected approximately 39,798 customers, with the time window concentrated between March 2, 2025, and April 11, 2026. The exposed information includes: names, email addresses, shipping addresses, phone numbers, and purchase details, among others.
SafePal has since implemented additional security measures to complete the fix and has sent separate email notifications to all affected customers. The company stated that it will continue to release the latest updates on the investigation.
From a user’s perspective, the following steps are recommended for the potentially affected users:
1. Watch for whether you received an official SafePal email notification, and be cautious of phishing emails impersonating customer support.
2. For the email addresses and passwords involved, change them promptly and enable two-factor authentication.
3. Be wary of unknown calls or text messages claiming “order issues,” and avoid any further disclosure of personal financial information.
4. Monitor ongoing investigation updates through official channels and check whether additional identity protection measures are required.
Wallet security is not only about protecting on-chain assets—every plugin and third-party component in the user experience can also become an attack surface. This incident once again highlights to the entire Web3 industry: security audits for front-end components cannot be overlooked.
#SafePal #钱包安全 #Web3
SafePal Wallet has recently disclosed a data security incident. In a post, its official account stated that a vulnerability was found in an order-tracking plugin, which led to unauthorized access to some customers’ information.
According to the official statement, the incident affected approximately 39,798 customers, with the time window concentrated between March 2, 2025, and April 11, 2026. The exposed information includes: names, email addresses, shipping addresses, phone numbers, and purchase details, among others.
SafePal has since implemented additional security measures to complete the fix and has sent separate email notifications to all affected customers. The company stated that it will continue to release the latest updates on the investigation.
From a user’s perspective, the following steps are recommended for the potentially affected users:
1. Watch for whether you received an official SafePal email notification, and be cautious of phishing emails impersonating customer support.
2. For the email addresses and passwords involved, change them promptly and enable two-factor authentication.
3. Be wary of unknown calls or text messages claiming “order issues,” and avoid any further disclosure of personal financial information.
4. Monitor ongoing investigation updates through official channels and check whether additional identity protection measures are required.
Wallet security is not only about protecting on-chain assets—every plugin and third-party component in the user experience can also become an attack surface. This incident once again highlights to the entire Web3 industry: security audits for front-end components cannot be overlooked.
#SafePal #钱包安全 #Web3
According to the official statement, the incident affected approximately 39,798 customers, with the time window concentrated between March 2, 2025, and April 11, 2026. The exposed information includes: names, email addresses, shipping addresses, phone numbers, and purchase details, among others.
SafePal has since implemented additional security measures to complete the fix and has sent separate email notifications to all affected customers. The company stated that it will continue to release the latest updates on the investigation.
From a user’s perspective, the following steps are recommended for the potentially affected users:
1. Watch for whether you received an official SafePal email notification, and be cautious of phishing emails impersonating customer support.
2. For the email addresses and passwords involved, change them promptly and enable two-factor authentication.
3. Be wary of unknown calls or text messages claiming “order issues,” and avoid any further disclosure of personal financial information.
4. Monitor ongoing investigation updates through official channels and check whether additional identity protection measures are required.
Wallet security is not only about protecting on-chain assets—every plugin and third-party component in the user experience can also become an attack surface. This incident once again highlights to the entire Web3 industry: security audits for front-end components cannot be overlooked.
#SafePal #钱包安全 #Web3
24
·
--
Bullish
🚨 ALERT: @SafePal has disclosed a data breach affecting 39,798 customers.
While funds and wallet credentials are reportedly safe, users should stay alert for phishing attempts from scammers impersonating SafePal staff. Verify messages through official channels before sharing any information. #SafePal #CryptoSecurity #Phishing
🚨 ALERT: @SafePal has disclosed a data breach affecting 39,798 customers.
While funds and wallet credentials are reportedly safe, users should stay alert for phishing attempts from scammers impersonating SafePal staff. Verify messages through official channels before sharing any information. #SafePal #CryptoSecurity #Phishing
While funds and wallet credentials are reportedly safe, users should stay alert for phishing attempts from scammers impersonating SafePal staff. Verify messages through official channels before sharing any information. #SafePal #CryptoSecurity #Phishing
1
4
99
·
--
Bullish
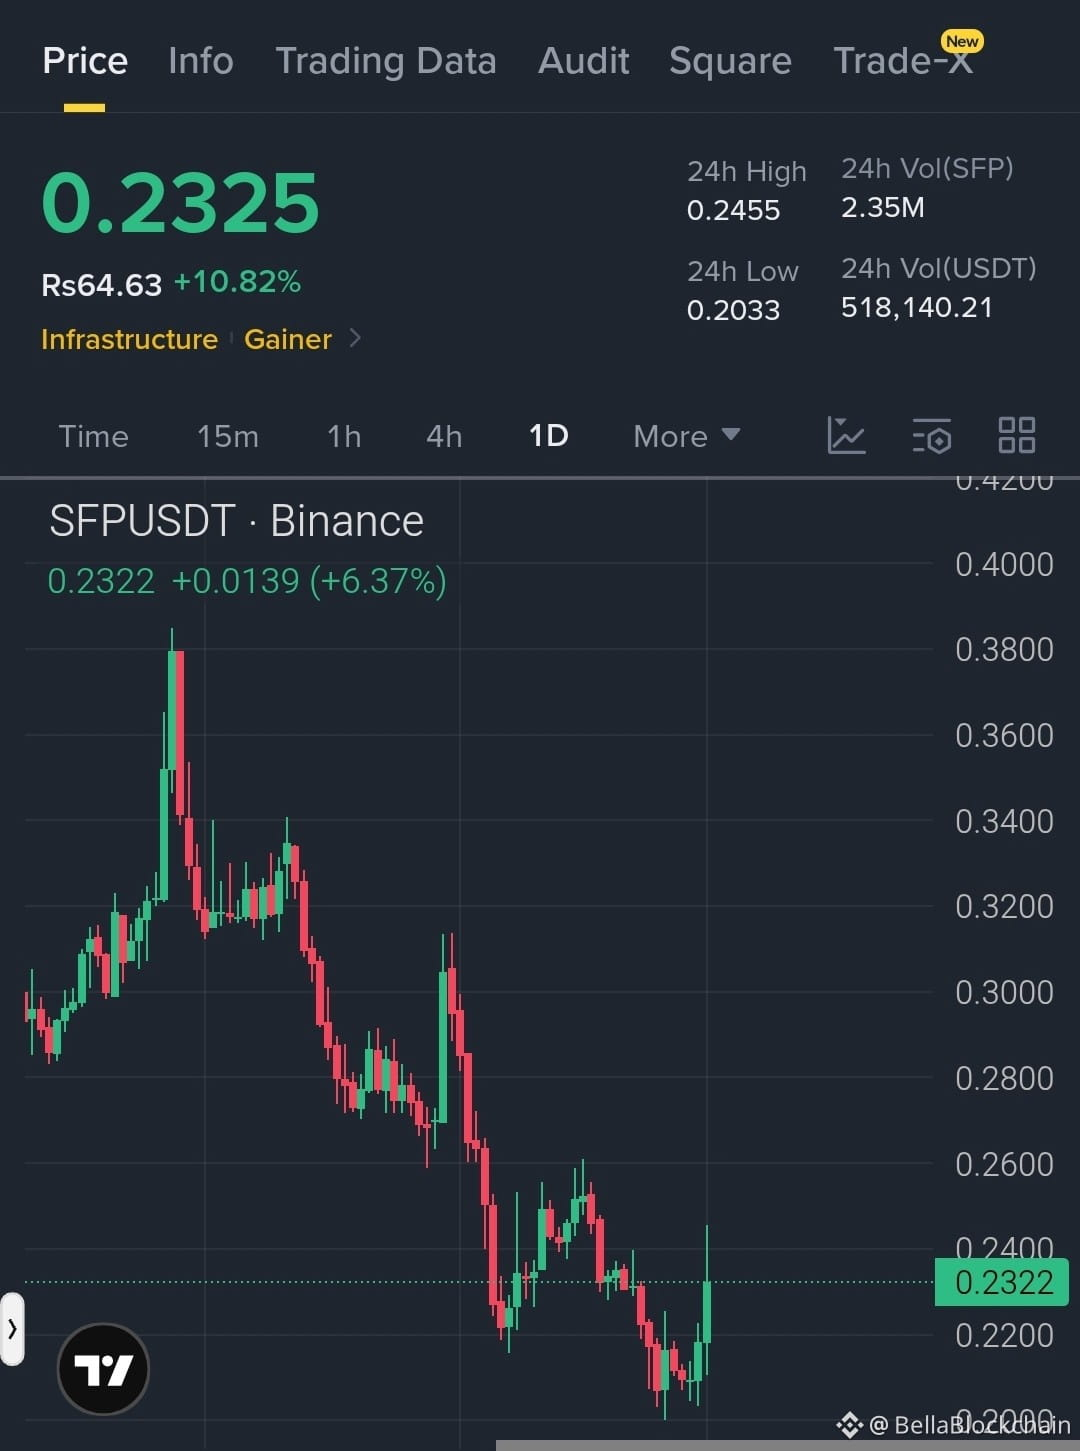
$SFP is showing strong signs of a bullish reversal after establishing a solid support base near the 0.2000 level. The recent price action demonstrates a clean breakout from local consolidation with building momentum, positioning the token for a sustained upward continuation toward key overhead resistance and liquidity zones.
* Target 1: 0.2600
* Target 2: 0.3000
* Target 3: 0.3400
#SFP #SafePal #Altcoins
$SFP
{future}(SFPUSDT)
$SFP is showing strong signs of a bullish reversal after establishing a solid support base near the 0.2000 level. The recent price action demonstrates a clean breakout from local consolidation with building momentum, positioning the token for a sustained upward continuation toward key overhead resistance and liquidity zones.
* Target 1: 0.2600
* Target 2: 0.3000
* Target 3: 0.3400
#SFP #SafePal #Altcoins
$SFP
* Target 1: 0.2600
* Target 2: 0.3000
* Target 3: 0.3400
#SFP #SafePal #Altcoins
$SFP
1
21
SafePal has officially integrated with the Robinhood L2 mainnet, pushing the RWAFi roadmap forward another big step.
This time, it’s not just compatibility at the wallet layer—SafePal has already launched native stock token trading on the Robinhood Chain. Going forward, it will also work with the perpetual DEX to deepen on-chain liquidity and trading depth.
Combined with previously integrated tokenized asset providers like xStocks and Ondo, users can now directly buy star stocks such as NVIDIA, Tesla, and SpaceX on-chain. Even S&P 500 ETFs and gold can be configured with a single click.
For everyday users, the significance is quite straightforward: core traditional assets from the U.S. stock market and commodities are being moved into on-chain wallets, sharing the same trading and settlement logic as crypto assets. The pace at which RWAFi is moving from narrative to usable products is clearly accelerating.
Next to watch is whether, after the perpetual DEX goes live, the depth of stock tokens can truly support real trading demand—and whether the Robinhood L2 ecosystem can attract more traditional asset issuers to enter the space.
#RWA #SafePal #RobinhoodChain
SafePal has officially integrated with the Robinhood L2 mainnet, pushing the RWAFi roadmap forward another big step.
This time, it’s not just compatibility at the wallet layer—SafePal has already launched native stock token trading on the Robinhood Chain. Going forward, it will also work with the perpetual DEX to deepen on-chain liquidity and trading depth.
Combined with previously integrated tokenized asset providers like xStocks and Ondo, users can now directly buy star stocks such as NVIDIA, Tesla, and SpaceX on-chain. Even S&P 500 ETFs and gold can be configured with a single click.
For everyday users, the significance is quite straightforward: core traditional assets from the U.S. stock market and commodities are being moved into on-chain wallets, sharing the same trading and settlement logic as crypto assets. The pace at which RWAFi is moving from narrative to usable products is clearly accelerating.
Next to watch is whether, after the perpetual DEX goes live, the depth of stock tokens can truly support real trading demand—and whether the Robinhood L2 ecosystem can attract more traditional asset issuers to enter the space.
#RWA #SafePal #RobinhoodChain
This time, it’s not just compatibility at the wallet layer—SafePal has already launched native stock token trading on the Robinhood Chain. Going forward, it will also work with the perpetual DEX to deepen on-chain liquidity and trading depth.
Combined with previously integrated tokenized asset providers like xStocks and Ondo, users can now directly buy star stocks such as NVIDIA, Tesla, and SpaceX on-chain. Even S&P 500 ETFs and gold can be configured with a single click.
For everyday users, the significance is quite straightforward: core traditional assets from the U.S. stock market and commodities are being moved into on-chain wallets, sharing the same trading and settlement logic as crypto assets. The pace at which RWAFi is moving from narrative to usable products is clearly accelerating.
Next to watch is whether, after the perpetual DEX goes live, the depth of stock tokens can truly support real trading demand—and whether the Robinhood L2 ecosystem can attract more traditional asset issuers to enter the space.
#RWA #SafePal #RobinhoodChain
5

·
--
Bullish
👀 Q2 2026 was record-breaking in terms of the number of hacks with #krypto . April–June saw 85 attacks—the highest in the history of observations!
Since the start of 2026, the industry has already recorded 121 breaches, and total losses have reached about $942M. And that’s exactly why wallet security isn’t an “option”, it’s the “foundation”!
🔥 “#SafePal X1” is a hardware wallet that keeps your Private Keys off your phone and computer!
In practice, this means you have to physically confirm the transaction on the device, so phishing, scam links, or an infected browser have a much harder job.
For people who follow me and want to secure their crypto assets better, I have a -50% code to buy the SafePal X1 from the official store @SafePal .
⚡️ Price - $69.99 + $9 shipping. With the code ➣ $38.99 for a new hardware wallet. Code ➣ OLEK@SFP
With #crypto you can make a lot, but one bad signature is enough to lose everything. It’s better to secure your wallet in advance than to regret it later.
❗️ Follow for more! #Kryptowaluty #DeFi $SFP
{spot}(SFPUSDT)
👀 Q2 2026 was record-breaking in terms of the number of hacks with #krypto . April–June saw 85 attacks—the highest in the history of observations!
Since the start of 2026, the industry has already recorded 121 breaches, and total losses have reached about $942M. And that’s exactly why wallet security isn’t an “option”, it’s the “foundation”!
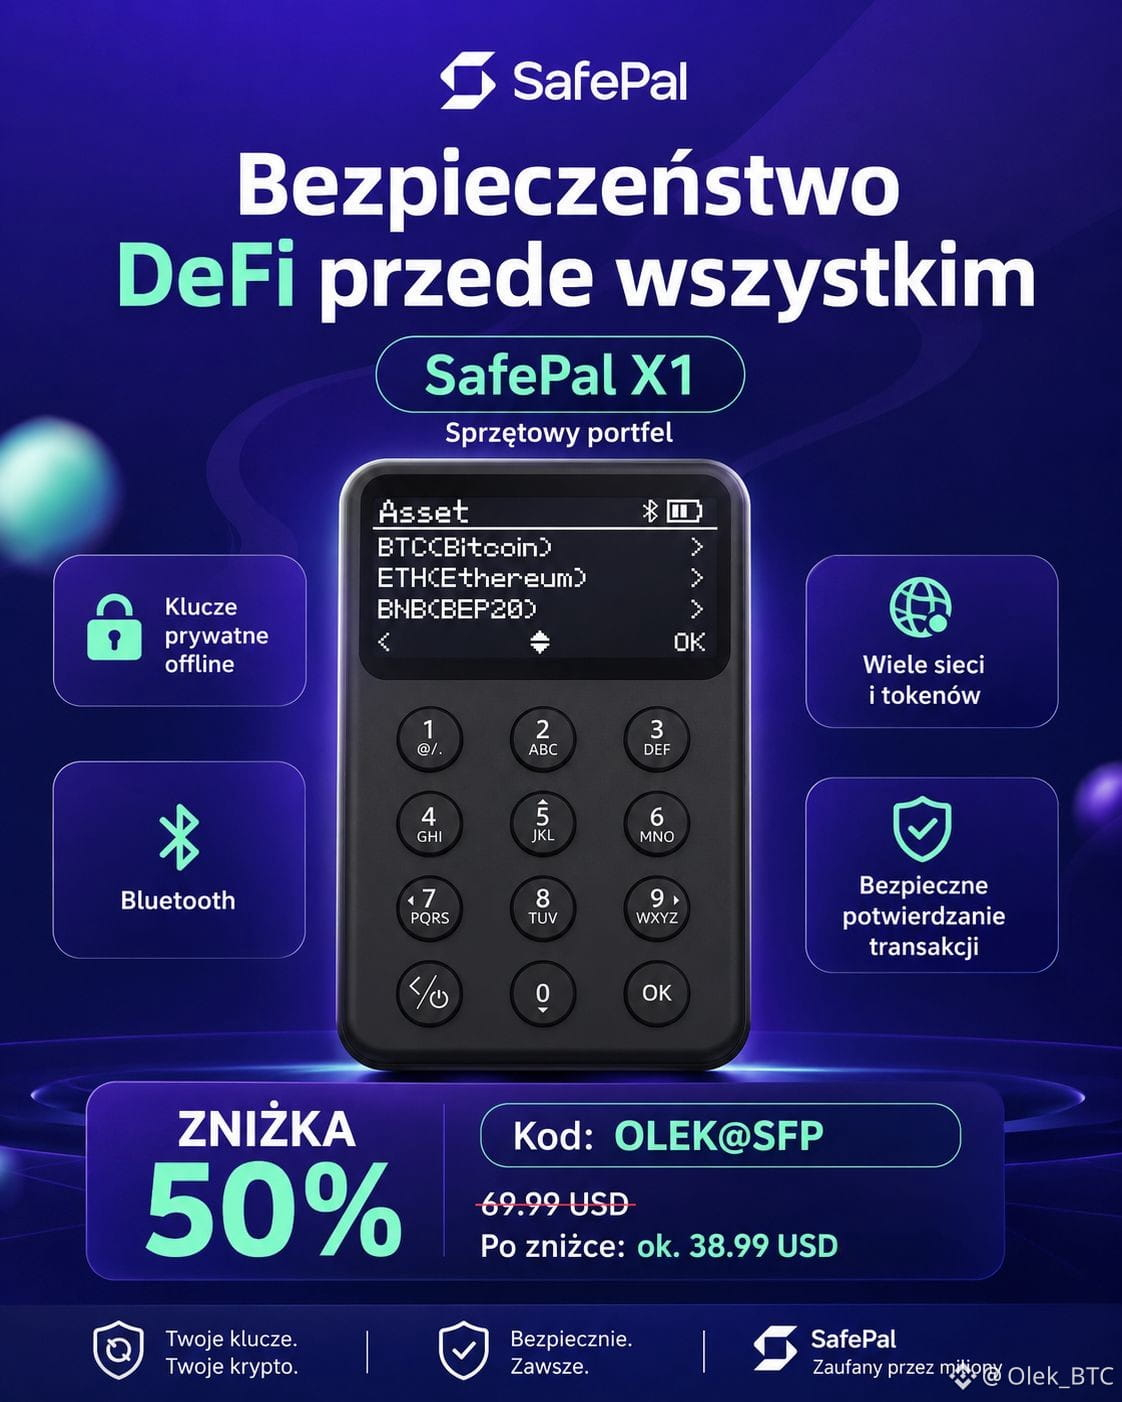
🔥 “#SafePal X1” is a hardware wallet that keeps your Private Keys off your phone and computer!
In practice, this means you have to physically confirm the transaction on the device, so phishing, scam links, or an infected browser have a much harder job.
For people who follow me and want to secure their crypto assets better, I have a -50% code to buy the SafePal X1 from the official store @SafePal .
⚡️ Price - $69.99 + $9 shipping. With the code ➣ $38.99 for a new hardware wallet. Code ➣ OLEK@SFP
With #crypto you can make a lot, but one bad signature is enough to lose everything. It’s better to secure your wallet in advance than to regret it later.
❗️ Follow for more! #Kryptowaluty #DeFi $SFP
Since the start of 2026, the industry has already recorded 121 breaches, and total losses have reached about $942M. And that’s exactly why wallet security isn’t an “option”, it’s the “foundation”!
🔥 “#SafePal X1” is a hardware wallet that keeps your Private Keys off your phone and computer!
In practice, this means you have to physically confirm the transaction on the device, so phishing, scam links, or an infected browser have a much harder job.
For people who follow me and want to secure their crypto assets better, I have a -50% code to buy the SafePal X1 from the official store @SafePal .
⚡️ Price - $69.99 + $9 shipping. With the code ➣ $38.99 for a new hardware wallet. Code ➣ OLEK@SFP
With #crypto you can make a lot, but one bad signature is enough to lose everything. It’s better to secure your wallet in advance than to regret it later.
❗️ Follow for more! #Kryptowaluty #DeFi $SFP
142

·
--
Binance invests in @SafePalCN hardware wallets, and there has been a data leak involving customer delivery information.
As of last year, most people’s general understanding was that hardware wallets are highly secure—physically isolated and not easily stolen.
This year, three consecutive hardware wallet security incidents have already shattered that previous belief.
As the industry has developed, hackers have increasingly set their sights on the hardware wallet sector, targeting some ancient big whales.
After all, many people store large amounts of funds in hardware wallets.
A hardware wallet’s private keys may be破解 one by one, and the recipient information for hardware wallet deliveries may be leaked.
There is no absolutely secure place to store them.
At the moment, perhaps only major exchanges like Binance can offer some backup coverage for users, which may be a bit better.
#SafePal数据泄露4万用户 #safepal
Binance invests in @SafePalCN hardware wallets, and there has been a data leak involving customer delivery information.
As of last year, most people’s general understanding was that hardware wallets are highly secure—physically isolated and not easily stolen.
This year, three consecutive hardware wallet security incidents have already shattered that previous belief.
As the industry has developed, hackers have increasingly set their sights on the hardware wallet sector, targeting some ancient big whales.
After all, many people store large amounts of funds in hardware wallets.
A hardware wallet’s private keys may be破解 one by one, and the recipient information for hardware wallet deliveries may be leaked.
There is no absolutely secure place to store them.
At the moment, perhaps only major exchanges like Binance can offer some backup coverage for users, which may be a bit better.
#SafePal数据泄露4万用户 #safepal
As of last year, most people’s general understanding was that hardware wallets are highly secure—physically isolated and not easily stolen.
This year, three consecutive hardware wallet security incidents have already shattered that previous belief.
As the industry has developed, hackers have increasingly set their sights on the hardware wallet sector, targeting some ancient big whales.
After all, many people store large amounts of funds in hardware wallets.
A hardware wallet’s private keys may be破解 one by one, and the recipient information for hardware wallet deliveries may be leaked.
There is no absolutely secure place to store them.
At the moment, perhaps only major exchanges like Binance can offer some backup coverage for users, which may be a bit better.
#SafePal数据泄露4万用户 #safepal
206
2
14
206
SafePal reported a flaw that exposed data from nearly 40,000 customers.
However, no private key or seed phrase was compromised 🚨. #SafePal
SafePal reported a flaw that exposed data from nearly 40,000 customers.
However, no private key or seed phrase was compromised 🚨. #SafePal
However, no private key or seed phrase was compromised 🚨. #SafePal
115
·
--
SafePal confirmed a data breach that disclosed order information for approximately 39,798 customers, but it did not directly result in compromising wallets or private keys.
The breach was caused by a vulnerability in adding order-tracking, which led to the leakage of names, contact details, and purchase data for orders between March 2025 and April 2026.
Recovery phrases for the wallet, private keys, and funds remain safe, but the exposed data increases the risk of phishing scams and identity impersonation, similar to recent incidents involving Trezor and Ledger.
Affected and unaffected users alike should strengthen their security measures, handle with caution any unsolicited messages claiming to be from “SafePal,” and monitor ongoing audits and content removal efforts#SafePal $BTC $SOL $ETH
SafePal confirmed a data breach that disclosed order information for approximately 39,798 customers, but it did not directly result in compromising wallets or private keys.
The breach was caused by a vulnerability in adding order-tracking, which led to the leakage of names, contact details, and purchase data for orders between March 2025 and April 2026.
Recovery phrases for the wallet, private keys, and funds remain safe, but the exposed data increases the risk of phishing scams and identity impersonation, similar to recent incidents involving Trezor and Ledger.
Affected and unaffected users alike should strengthen their security measures, handle with caution any unsolicited messages claiming to be from “SafePal,” and monitor ongoing audits and content removal efforts#SafePal $BTC $SOL $ETH
The breach was caused by a vulnerability in adding order-tracking, which led to the leakage of names, contact details, and purchase data for orders between March 2025 and April 2026.
Recovery phrases for the wallet, private keys, and funds remain safe, but the exposed data increases the risk of phishing scams and identity impersonation, similar to recent incidents involving Trezor and Ledger.
Affected and unaffected users alike should strengthen their security measures, handle with caution any unsolicited messages claiming to be from “SafePal,” and monitor ongoing audits and content removal efforts#SafePal $BTC $SOL $ETH

انت وحظك
From Black robe
22
·
--
⚡ Security breach affects about 39,798 customers in #SafePal
📊 SafePal was exposed to a security breach through a vulnerability in its order tracking add-on that led to the disclosure of data for around 39,798 customers, including names, email addresses, shipping addresses, phone numbers, and purchase details.
💻 SafePal confirmed that wallets, recovery phrases, and private keys were not affected, and that the vulnerability has been fixed with strengthened security measures.
🚨 Customers are advised to update their information and monitor their accounts closely in light of this security breach.
⚡ Security breach affects about 39,798 customers in #SafePal
📊 SafePal was exposed to a security breach through a vulnerability in its order tracking add-on that led to the disclosure of data for around 39,798 customers, including names, email addresses, shipping addresses, phone numbers, and purchase details.
💻 SafePal confirmed that wallets, recovery phrases, and private keys were not affected, and that the vulnerability has been fixed with strengthened security measures.
🚨 Customers are advised to update their information and monitor their accounts closely in light of this security breach.
📊 SafePal was exposed to a security breach through a vulnerability in its order tracking add-on that led to the disclosure of data for around 39,798 customers, including names, email addresses, shipping addresses, phone numbers, and purchase details.
💻 SafePal confirmed that wallets, recovery phrases, and private keys were not affected, and that the vulnerability has been fixed with strengthened security measures.
🚨 Customers are advised to update their information and monitor their accounts closely in light of this security breach.
1
902
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#AIStocksWhatNext
574,005 views
4,318 Discussing
2
#21SharesLaunchesEuropesFirstZcashETP
1,915 views
139 Discussing
3
#CardanoJoinsX402PaymentStandard
1,510 views
125 Discussing
4
#BitcoinTops$87KAtEightMonthHigh
4,133 views
58 Discussing
5
#ZECBreaksAbove$1600AtRecordHigh
1,937 views
47 Discussing
6
#BitwiseNEARStakingETPAssetsTop$100M
19,906 views
67 Discussing
7
#BitcoinBreaksAboveMayHighNears$86K
25,732 views
251 Discussing
8
#DogecoinRises15%
91,426 views
1,544 Discussing
9
#$14BBitcoinOptionsExpireFriday
7,507 views
109 Discussing
10
#BNBMarketCapPassesBNYMellon
55,813 views
1,213 Discussing