
#ciberseguridad
ciberseguridad
327,268 views
405 Discussing
Hot
Latest

·
--
Bearish
🚨 CYBERCRIME CRACKDOWN: GOOTLOADER INFRASTRUCTURE DISMANTLED 🚨
U.S. authorities, together with international partners, have dealt a major blow to one of the most persistent malware networks in recent years. The Department of Justice confirmed the takedown of Gootloader on more than 100 servers and the seizure of key domains used to distribute it.
📊 The damage in numbers (2018–2026):
• More than 25,000 computers infected worldwide.
• 44 ransomware attack victims in the U.S. alone.
• Estimated losses of USD $28.8 million in reported damages.
🔍 How did it operate?
Gootloader infected computers (often through compromised WordPress sites) and added the devices to a botnet. The operators not only controlled the computers but also sold access to other criminals to deploy ransomware.
🤝 The operation:
The action, coordinated with Shadowserver and technical organizations, aimed to disrupt the distribution and control of the malware. However, authorities warn that this does not eliminate all risks or identify everyone responsible, so vigilance remains essential.
💡 A lesson for the crypto ecosystem:
Operational security is essential. A compromised device can be a gateway for attacks that put your digital assets at risk. Keep your systems up to date, be wary of suspicious files, and always use two-factor authentication (2FA).
#BinanceSquare #ciberseguridad $BTC $ETC
🚨 CYBERCRIME CRACKDOWN: GOOTLOADER INFRASTRUCTURE DISMANTLED 🚨
U.S. authorities, together with international partners, have dealt a major blow to one of the most persistent malware networks in recent years. The Department of Justice confirmed the takedown of Gootloader on more than 100 servers and the seizure of key domains used to distribute it.
📊 The damage in numbers (2018–2026):
• More than 25,000 computers infected worldwide.
• 44 ransomware attack victims in the U.S. alone.
• Estimated losses of USD $28.8 million in reported damages.
🔍 How did it operate?
Gootloader infected computers (often through compromised WordPress sites) and added the devices to a botnet. The operators not only controlled the computers but also sold access to other criminals to deploy ransomware.
🤝 The operation:
The action, coordinated with Shadowserver and technical organizations, aimed to disrupt the distribution and control of the malware. However, authorities warn that this does not eliminate all risks or identify everyone responsible, so vigilance remains essential.
💡 A lesson for the crypto ecosystem:
Operational security is essential. A compromised device can be a gateway for attacks that put your digital assets at risk. Keep your systems up to date, be wary of suspicious files, and always use two-factor authentication (2FA).
#BinanceSquare #ciberseguridad $BTC $ETC
U.S. authorities, together with international partners, have dealt a major blow to one of the most persistent malware networks in recent years. The Department of Justice confirmed the takedown of Gootloader on more than 100 servers and the seizure of key domains used to distribute it.
📊 The damage in numbers (2018–2026):
• More than 25,000 computers infected worldwide.
• 44 ransomware attack victims in the U.S. alone.
• Estimated losses of USD $28.8 million in reported damages.
🔍 How did it operate?
Gootloader infected computers (often through compromised WordPress sites) and added the devices to a botnet. The operators not only controlled the computers but also sold access to other criminals to deploy ransomware.
🤝 The operation:
The action, coordinated with Shadowserver and technical organizations, aimed to disrupt the distribution and control of the malware. However, authorities warn that this does not eliminate all risks or identify everyone responsible, so vigilance remains essential.
💡 A lesson for the crypto ecosystem:
Operational security is essential. A compromised device can be a gateway for attacks that put your digital assets at risk. Keep your systems up to date, be wary of suspicious files, and always use two-factor authentication (2FA).
#BinanceSquare #ciberseguridad $BTC $ETC
124

·
--
🚨 $BTC SHOCKING! 46,000 TSMC EMPLOYEES’ DATA SOLD FOR JUST 3 BITCOINS
TSMC, the giant that makes the world’s chips, confirmed today that hackers leaked the data of around 46,000 current and former employees and put it up for sale for just 3 BTC. To me, the serious issue isn’t the ransom price—it’s that the leak came through an external cloud provider: the link nobody was watching is the one that broke.
Look at the detail nobody is paying attention to:
→ 6.9 GB of data for sale: the leaked sample contains 499 records with 19 fields each, including ID numbers, bank accounts, addresses, and emergency contacts.
→ The hackers gave them a week: if nobody pays the 3 BTC (about $215,000), they’ll publish the entire database for free.
→ TSMC shares fell 1.55% on Thursday, and this isn’t the first time: in June 2023, LockBit demanded $70 million over an attack on a TSMC supplier.
Do you think TSMC will pay the 3 BTC or let them publish the data? 👇
$BTC
#Bitcoin #TSMC #Cybersecurity
🚨 $BTC SHOCKING! 46,000 TSMC EMPLOYEES’ DATA SOLD FOR JUST 3 BITCOINS
TSMC, the giant that makes the world’s chips, confirmed today that hackers leaked the data of around 46,000 current and former employees and put it up for sale for just 3 BTC. To me, the serious issue isn’t the ransom price—it’s that the leak came through an external cloud provider: the link nobody was watching is the one that broke.
Look at the detail nobody is paying attention to:
→ 6.9 GB of data for sale: the leaked sample contains 499 records with 19 fields each, including ID numbers, bank accounts, addresses, and emergency contacts.
→ The hackers gave them a week: if nobody pays the 3 BTC (about $215,000), they’ll publish the entire database for free.
→ TSMC shares fell 1.55% on Thursday, and this isn’t the first time: in June 2023, LockBit demanded $70 million over an attack on a TSMC supplier.
Do you think TSMC will pay the 3 BTC or let them publish the data? 👇
$BTC
#Bitcoin #TSMC #Cybersecurity
TSMC, the giant that makes the world’s chips, confirmed today that hackers leaked the data of around 46,000 current and former employees and put it up for sale for just 3 BTC. To me, the serious issue isn’t the ransom price—it’s that the leak came through an external cloud provider: the link nobody was watching is the one that broke.
Look at the detail nobody is paying attention to:
→ 6.9 GB of data for sale: the leaked sample contains 499 records with 19 fields each, including ID numbers, bank accounts, addresses, and emergency contacts.
→ The hackers gave them a week: if nobody pays the 3 BTC (about $215,000), they’ll publish the entire database for free.
→ TSMC shares fell 1.55% on Thursday, and this isn’t the first time: in June 2023, LockBit demanded $70 million over an attack on a TSMC supplier.
Do you think TSMC will pay the 3 BTC or let them publish the data? 👇
$BTC
#Bitcoin #TSMC #Cybersecurity
5.7k
🚨 UNITED STATES SEIZES $1.2 BILLION IN CRYPTOCURRENCY STOLEN BY NORTH KOREA: 🇺🇸💰
The Department of Justice announced today the court-ordered seizure of more than $1.2 billion in digital assets stolen by North Korean hackers.
This financial blow is part of the response to the historic theft of more than $6 billion suffered by the Binance platform in late October. 🛡️💻🔒
In a parallel operation, U.S. authorities also dismantled a sophisticated deepfake video scam network used to steal another $400 million. 🕵️♂️🎭🚫
With support from the private sector, the total frozen in connection with this cyberattack has now reached more than $2.7 billion. ❄️📊🌐
Investigations remain ongoing to track down the rest of the funds as the digital ecosystem strengthens its measures against international cybercrime. 🔍🚀⚖️
#Criptomonedas #Binance #Ciberseguridad #NoticiasCripto #Tecnologia
$BTC
{future}(BTCUSDT)
$BNB
{future}(BNBUSDT)
$ETH
{future}(ETHUSDT)
🚨 UNITED STATES SEIZES $1.2 BILLION IN CRYPTOCURRENCY STOLEN BY NORTH KOREA: 🇺🇸💰
The Department of Justice announced today the court-ordered seizure of more than $1.2 billion in digital assets stolen by North Korean hackers.
This financial blow is part of the response to the historic theft of more than $6 billion suffered by the Binance platform in late October. 🛡️💻🔒
In a parallel operation, U.S. authorities also dismantled a sophisticated deepfake video scam network used to steal another $400 million. 🕵️♂️🎭🚫
With support from the private sector, the total frozen in connection with this cyberattack has now reached more than $2.7 billion. ❄️📊🌐
Investigations remain ongoing to track down the rest of the funds as the digital ecosystem strengthens its measures against international cybercrime. 🔍🚀⚖️
#Criptomonedas #Binance #Ciberseguridad #NoticiasCripto #Tecnologia
$BTC
$BNB
$ETH
The Department of Justice announced today the court-ordered seizure of more than $1.2 billion in digital assets stolen by North Korean hackers.
This financial blow is part of the response to the historic theft of more than $6 billion suffered by the Binance platform in late October. 🛡️💻🔒
In a parallel operation, U.S. authorities also dismantled a sophisticated deepfake video scam network used to steal another $400 million. 🕵️♂️🎭🚫
With support from the private sector, the total frozen in connection with this cyberattack has now reached more than $2.7 billion. ❄️📊🌐
Investigations remain ongoing to track down the rest of the funds as the digital ecosystem strengthens its measures against international cybercrime. 🔍🚀⚖️
#Criptomonedas #Binance #Ciberseguridad #NoticiasCripto #Tecnologia
$BTC
$BNB
$ETH
132
·
--
#AlertaMundial
🚨 Cybersecurity Alert! TSMC hit by attack and Bitcoin extortion 💻₿
Digital security is once again in the eye of the storm after a new incident rocked the Taiwanese tech giant.
🔍 What exactly happened?
Taiwan Semiconductor Manufacturing Company (TSMC) officially confirmed that its systems suffered a security breach. According to reports published by Jiemian News, a hacker managed to access and obtain confidential information belonging to the company’s employees.
💰 The ransom demand
To prevent the stolen data from being disclosed or compromised, the cyberattacker demanded a ransom payment equivalent to 3 Bitcoins ($BTC ). Although the amount may seem modest compared with the size of this semiconductor giant, the incident highlights the ongoing risks faced by the world’s most critical technology infrastructure.
🛡️ The challenge of data protection
This incident serves as a reminder of the importance of strengthening corporate cybersecurity protocols. Even global innovation leaders are vulnerable to increasingly sophisticated digital threats.
Do you think big tech companies invest enough in protecting their employees’ data?
Share your thoughts 👇💬
#TSMC #ciberseguridad #NoticiasTech
#AlertaMundial
🚨 Cybersecurity Alert! TSMC hit by attack and Bitcoin extortion 💻₿
Digital security is once again in the eye of the storm after a new incident rocked the Taiwanese tech giant.
🔍 What exactly happened?
Taiwan Semiconductor Manufacturing Company (TSMC) officially confirmed that its systems suffered a security breach. According to reports published by Jiemian News, a hacker managed to access and obtain confidential information belonging to the company’s employees.
💰 The ransom demand
To prevent the stolen data from being disclosed or compromised, the cyberattacker demanded a ransom payment equivalent to 3 Bitcoins ($BTC ). Although the amount may seem modest compared with the size of this semiconductor giant, the incident highlights the ongoing risks faced by the world’s most critical technology infrastructure.
🛡️ The challenge of data protection
This incident serves as a reminder of the importance of strengthening corporate cybersecurity protocols. Even global innovation leaders are vulnerable to increasingly sophisticated digital threats.
Do you think big tech companies invest enough in protecting their employees’ data?
Share your thoughts 👇💬
#TSMC #ciberseguridad #NoticiasTech
🚨 Cybersecurity Alert! TSMC hit by attack and Bitcoin extortion 💻₿
Digital security is once again in the eye of the storm after a new incident rocked the Taiwanese tech giant.
🔍 What exactly happened?
Taiwan Semiconductor Manufacturing Company (TSMC) officially confirmed that its systems suffered a security breach. According to reports published by Jiemian News, a hacker managed to access and obtain confidential information belonging to the company’s employees.
💰 The ransom demand
To prevent the stolen data from being disclosed or compromised, the cyberattacker demanded a ransom payment equivalent to 3 Bitcoins ($BTC ). Although the amount may seem modest compared with the size of this semiconductor giant, the incident highlights the ongoing risks faced by the world’s most critical technology infrastructure.
🛡️ The challenge of data protection
This incident serves as a reminder of the importance of strengthening corporate cybersecurity protocols. Even global innovation leaders are vulnerable to increasingly sophisticated digital threats.
Do you think big tech companies invest enough in protecting their employees’ data?
Share your thoughts 👇💬
#TSMC #ciberseguridad #NoticiasTech
3
367
·
--
Coordinated intrusion into seven South Korean banks (Sep–Oct 2026) exposed data on 66k–67k citizens and 2.2k companies. The attack, attributed to an individual Chinese operator, used ARTEX, an autonomous penetration-testing framework, and a modified version of Claude Code to redirect requests to DeepSeek infrastructure.
— Analysis by EmeDotEme
#EmeDotEme #Ciberseguridad #SouthKorea
Coordinated intrusion into seven South Korean banks (Sep–Oct 2026) exposed data on 66k–67k citizens and 2.2k companies. The attack, attributed to an individual Chinese operator, used ARTEX, an autonomous penetration-testing framework, and a modified version of Claude Code to redirect requests to DeepSeek infrastructure.
— Analysis by EmeDotEme
#EmeDotEme #Ciberseguridad #SouthKorea
— Analysis by EmeDotEme
#EmeDotEme #Ciberseguridad #SouthKorea
121
·
--
On November 7, 2026, Gnosis Pay suffered a cyber intrusion into its card system, exposing users’ confidential data. The breach, reported by CriptoNoticias, compromises confidentiality and facilitates secondary attacks, such as personalized fraud. The extracted data could link personal identities to active payment accounts, increasing the risk to cardholders.
— Analysis by EmeDotEme
#EmeDotEme #Ciberseguridad #GnosisPay
On November 7, 2026, Gnosis Pay suffered a cyber intrusion into its card system, exposing users’ confidential data. The breach, reported by CriptoNoticias, compromises confidentiality and facilitates secondary attacks, such as personalized fraud. The extracted data could link personal identities to active payment accounts, increasing the risk to cardholders.
— Analysis by EmeDotEme
#EmeDotEme #Ciberseguridad #GnosisPay
— Analysis by EmeDotEme
#EmeDotEme #Ciberseguridad #GnosisPay
140
·
--
Ondrej Surý, PHP maintainer for Debian, distributed critical patches in late October 2026, mitigating two PHP vulnerabilities affecting 70% of websites. The preventive action thwarted mass cyberattacks following a leak of technical details in August 2026, which exposed millions of portals to hijacking and data extraction. His intervention accelerated security updates for older versions, preventing widespread outages.
— Analysis by EmeDotEme
#EmeDotEme #Ciberseguridad #OpenSource
Ondrej Surý, PHP maintainer for Debian, distributed critical patches in late October 2026, mitigating two PHP vulnerabilities affecting 70% of websites. The preventive action thwarted mass cyberattacks following a leak of technical details in August 2026, which exposed millions of portals to hijacking and data extraction. His intervention accelerated security updates for older versions, preventing widespread outages.
— Analysis by EmeDotEme
#EmeDotEme #Ciberseguridad #OpenSource
— Analysis by EmeDotEme
#EmeDotEme #Ciberseguridad #OpenSource
88
·
--
The FBI attributes the theft of $6.3B–$6.43B from Binance on October 29, 2026, to North Korean hackers, surpassing the $1.46B attack on Bybit in February 2025. The funds were converted and dispersed across DeFi. 82% of the stolen assets came from the Bitcoin and Ethereum networks.
— Analysis by EmeDotEme
#EmeDotEme #Criptomonedas #Cybersecurity
The FBI attributes the theft of $6.3B–$6.43B from Binance on October 29, 2026, to North Korean hackers, surpassing the $1.46B attack on Bybit in February 2025. The funds were converted and dispersed across DeFi. 82% of the stolen assets came from the Bitcoin and Ethereum networks.
— Analysis by EmeDotEme
#EmeDotEme #Criptomonedas #Cybersecurity
— Analysis by EmeDotEme
#EmeDotEme #Criptomonedas #Cybersecurity
110

·
--
There’s a group of hackers making headlines.
They’re called TraderTraitor, and they’re behind several massive thefts in the crypto sector.
The figures they’re dealing with are staggering. They’re linked to attacks that have caused around $6.3 billion in losses.
It’s shocking to see how a single group can hit the market so hard.
Have you heard of this group before?
$BTC
#ciberseguridad #crypto
There’s a group of hackers making headlines.
They’re called TraderTraitor, and they’re behind several massive thefts in the crypto sector.
The figures they’re dealing with are staggering. They’re linked to attacks that have caused around $6.3 billion in losses.
It’s shocking to see how a single group can hit the market so hard.
Have you heard of this group before?
$BTC
#ciberseguridad #crypto
They’re called TraderTraitor, and they’re behind several massive thefts in the crypto sector.
The figures they’re dealing with are staggering. They’re linked to attacks that have caused around $6.3 billion in losses.
It’s shocking to see how a single group can hit the market so hard.
Have you heard of this group before?
$BTC
#ciberseguridad #crypto
45

Article
Binance explains how it was robbed: tampered packages, a fake job interview, and an internal AI toolBinance has published its initial report on the October 29 attack. It estimates the impact at around $6.34 billion, of which around $2.85 billion has been frozen or intercepted, “subject to reconciliation and price volatility.” According to the report, by October 31 it had replenished 98% of the affected tokens and will absorb the loss, not its users.
How the attack was prepared, according to Binance:
🔹 June: An engineer on the wallet team installed a tampered Homebrew package while searching for an AI programming tool.
Binance explains how it was robbed: tampered packages, a fake job interview, and an internal AI tool
Binance has published its initial report on the October 29 attack. It estimates the impact at around $6.34 billion, of which around $2.85 billion has been frozen or intercepted, “subject to reconciliation and price volatility.” According to the report, by October 31 it had replenished 98% of the affected tokens and will absorb the loss, not its users.
How the attack was prepared, according to Binance:
🔹 June: An engineer on the wallet team installed a tampered Homebrew package while searching for an AI programming tool.
How the attack was prepared, according to Binance:
🔹 June: An engineer on the wallet team installed a tampered Homebrew package while searching for an AI programming tool.
2
5.8k
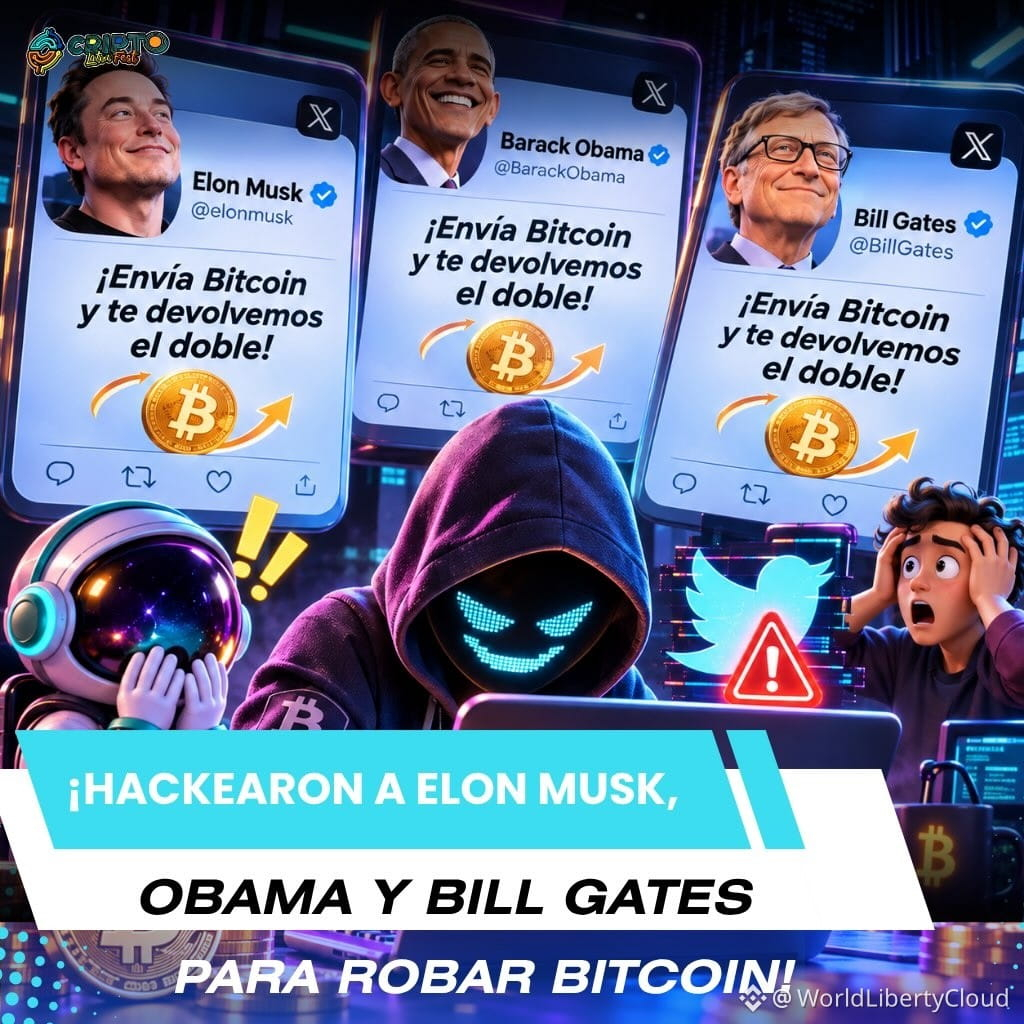
🚨🐦 ELON MUSK, OBAMA AND BILL GATES WERE HACKED TO STEAL BITCOIN! 😱💰💻
Can you imagine logging into Twitter and seeing Elon Musk, Barack Obama and Bill Gates giving away Bitcoin? 🤯₿
Well, in July 2020, something happened that seemed straight out of a movie! 🎬🔥
👨💻 A group of hackers managed to take control of verified accounts belonging to some of the most famous people in the world. 🌎🔓
Among them were Elon Musk, Barack Obama, Bill Gates and other well-known figures. 😳
💸 Their plan? Post messages promising something that sounded too good to be true:
🤑 “SEND BITCOIN AND WE’LL GIVE YOU DOUBLE BACK!” 🚀💰
And incredible as it may seem… SOME PEOPLE FELL FOR THE SCAM! 😱💀
💰 The attackers managed to receive more than $100,000 in Bitcoin through the scam.
🐦 Twitter had to step in and temporarily restrict some features of verified accounts to contain the attack. 🚨🔐
🤯 THE CRAZIEST PART!
They didn’t hack Bitcoin. They hacked celebrities’ accounts to take advantage of their followers’ trust. 💻🎭
🔥 ONE ATTACK. CELEBRITY ACCOUNTS COMPROMISED. AND THOUSANDS OF DOLLARS IN BITCOIN STOLEN. ₿💥
👇😂 WOULD YOU HAVE BELIEVED ELON MUSK WAS GIVING AWAY BITCOIN? 👀💸
#Bitcoin #ElonMusk #TwitterHack #Crypto #Crypto Blockchain #BitcoinStories #Ciberseguridad #CriptoLatinFest #worldlibertycloud
🚨🐦 ELON MUSK, OBAMA AND BILL GATES WERE HACKED TO STEAL BITCOIN! 😱💰💻
Can you imagine logging into Twitter and seeing Elon Musk, Barack Obama and Bill Gates giving away Bitcoin? 🤯₿
Well, in July 2020, something happened that seemed straight out of a movie! 🎬🔥
👨💻 A group of hackers managed to take control of verified accounts belonging to some of the most famous people in the world. 🌎🔓
Among them were Elon Musk, Barack Obama, Bill Gates and other well-known figures. 😳
💸 Their plan? Post messages promising something that sounded too good to be true:
🤑 “SEND BITCOIN AND WE’LL GIVE YOU DOUBLE BACK!” 🚀💰
And incredible as it may seem… SOME PEOPLE FELL FOR THE SCAM! 😱💀
💰 The attackers managed to receive more than $100,000 in Bitcoin through the scam.
🐦 Twitter had to step in and temporarily restrict some features of verified accounts to contain the attack. 🚨🔐
🤯 THE CRAZIEST PART!
They didn’t hack Bitcoin. They hacked celebrities’ accounts to take advantage of their followers’ trust. 💻🎭
🔥 ONE ATTACK. CELEBRITY ACCOUNTS COMPROMISED. AND THOUSANDS OF DOLLARS IN BITCOIN STOLEN. ₿💥
👇😂 WOULD YOU HAVE BELIEVED ELON MUSK WAS GIVING AWAY BITCOIN? 👀💸
#Bitcoin #ElonMusk #TwitterHack #Crypto #Crypto Blockchain #BitcoinStories #Ciberseguridad #CriptoLatinFest #worldlibertycloud
Can you imagine logging into Twitter and seeing Elon Musk, Barack Obama and Bill Gates giving away Bitcoin? 🤯₿
Well, in July 2020, something happened that seemed straight out of a movie! 🎬🔥
👨💻 A group of hackers managed to take control of verified accounts belonging to some of the most famous people in the world. 🌎🔓
Among them were Elon Musk, Barack Obama, Bill Gates and other well-known figures. 😳
💸 Their plan? Post messages promising something that sounded too good to be true:
🤑 “SEND BITCOIN AND WE’LL GIVE YOU DOUBLE BACK!” 🚀💰
And incredible as it may seem… SOME PEOPLE FELL FOR THE SCAM! 😱💀
💰 The attackers managed to receive more than $100,000 in Bitcoin through the scam.
🐦 Twitter had to step in and temporarily restrict some features of verified accounts to contain the attack. 🚨🔐
🤯 THE CRAZIEST PART!
They didn’t hack Bitcoin. They hacked celebrities’ accounts to take advantage of their followers’ trust. 💻🎭
🔥 ONE ATTACK. CELEBRITY ACCOUNTS COMPROMISED. AND THOUSANDS OF DOLLARS IN BITCOIN STOLEN. ₿💥
👇😂 WOULD YOU HAVE BELIEVED ELON MUSK WAS GIVING AWAY BITCOIN? 👀💸
#Bitcoin #ElonMusk #TwitterHack #Crypto #Crypto Blockchain #BitcoinStories #Ciberseguridad #CriptoLatinFest #worldlibertycloud
1
3
695

Still thinking about what happened a few days ago with the exploit/theft on the platform... and honestly, it’s impossible not to stop and think. 🛡️📉
Beyond the red numbers, the speculation, and what the headlines are saying, this kind of blow leaves all of us who are part of the ecosystem day to day with a huge lesson: security is never negotiable.
In this world, trust is good, but verifying and taking custody of your assets yourself is the only thing that gives us a little peace of mind in front of the screen.
Markets go up and down, trends change every week, but protecting our capital is the one rule we must never break.
How did this news make you feel? Are you the kind of person who prefers to move everything to a hardware wallet after a scare like this, or do you trust the exchanges’ security measures?
I’m reading your comments! 👇☕
(And as always: manage your risk, protect your funds; this is not financial advice)
#Criptomonedas #Ciberseguridad #Binance #CryptoNews #Web3 $
Still thinking about what happened a few days ago with the exploit/theft on the platform... and honestly, it’s impossible not to stop and think. 🛡️📉
Beyond the red numbers, the speculation, and what the headlines are saying, this kind of blow leaves all of us who are part of the ecosystem day to day with a huge lesson: security is never negotiable.
In this world, trust is good, but verifying and taking custody of your assets yourself is the only thing that gives us a little peace of mind in front of the screen.
Markets go up and down, trends change every week, but protecting our capital is the one rule we must never break.
How did this news make you feel? Are you the kind of person who prefers to move everything to a hardware wallet after a scare like this, or do you trust the exchanges’ security measures?
I’m reading your comments! 👇☕
(And as always: manage your risk, protect your funds; this is not financial advice)
#Criptomonedas #Ciberseguridad #Binance #CryptoNews #Web3 $
Beyond the red numbers, the speculation, and what the headlines are saying, this kind of blow leaves all of us who are part of the ecosystem day to day with a huge lesson: security is never negotiable.
In this world, trust is good, but verifying and taking custody of your assets yourself is the only thing that gives us a little peace of mind in front of the screen.
Markets go up and down, trends change every week, but protecting our capital is the one rule we must never break.
How did this news make you feel? Are you the kind of person who prefers to move everything to a hardware wallet after a scare like this, or do you trust the exchanges’ security measures?
I’m reading your comments! 👇☕
(And as always: manage your risk, protect your funds; this is not financial advice)
#Criptomonedas #Ciberseguridad #Binance #CryptoNews #Web3 $

Sigueme
From Karleen Seyer pM11
2
25
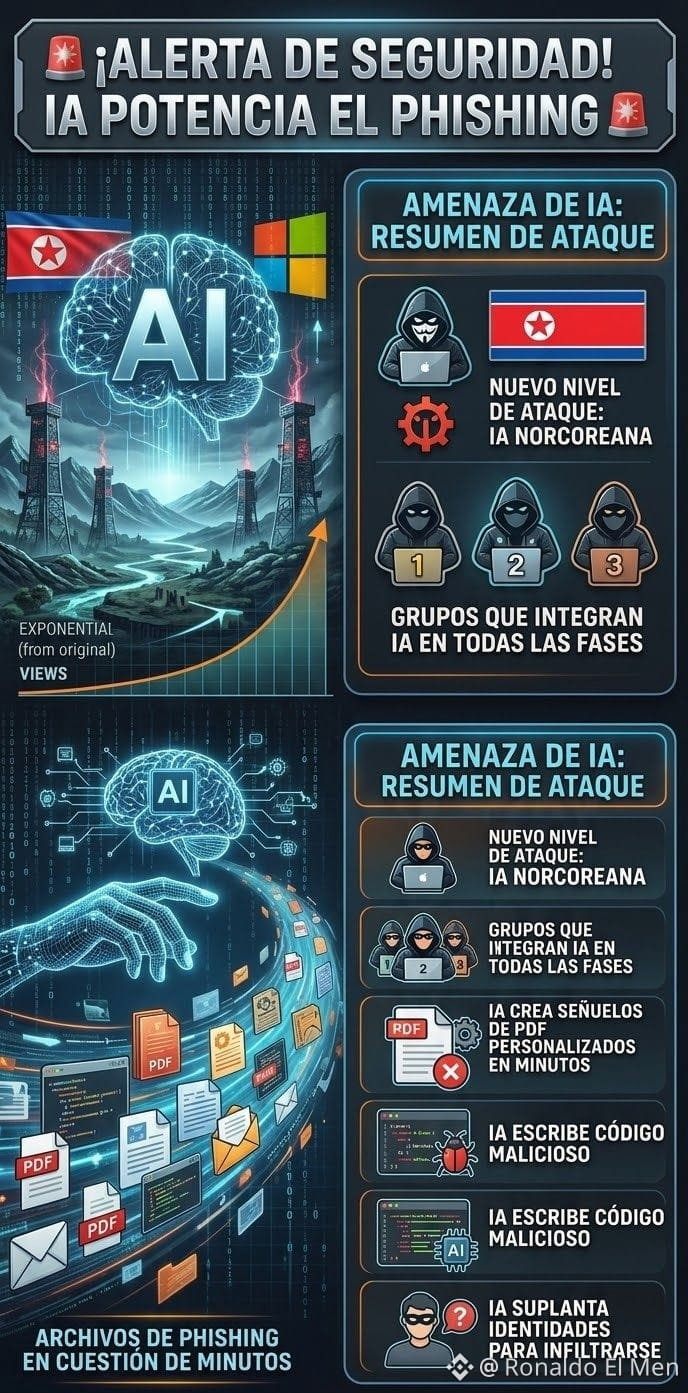
🚨 Cybersecurity and Crypto: AI is now hackers’ primary weapon!
Microsoft issued a key warning on October 30: North Korean hacking groups are using artificial intelligence to generate dozens of phishing files in a matter of minutes.
According to security reports monitored by Microsoft, three of these groups have integrated AI into every phase of their attacks. How do they operate?
Tailored lures: They create personalized, highly convincing PDF documents in minutes.
Malicious code: They use AI to write scripts and dangerous code faster.
Impersonation: They infiltrate companies and ecosystems by pretending to be legitimate entities.
In the crypto and Web3 world, where every click counts, AI-powered social engineering forces us to take extra precautions. Never download suspicious files or connect your wallet to links from dubious sources.
How safe do you feel against these new automated tactics used by cybercriminals? I’m reading your comments! 👇
$BTC $ETH $BNB
{spot}(BNBUSDT)
#ciberseguridad #phishing #InteligenciaArtificiala #BinanceSquareTips #SeguridadFinanciera
🚨 Cybersecurity and Crypto: AI is now hackers’ primary weapon!
Microsoft issued a key warning on October 30: North Korean hacking groups are using artificial intelligence to generate dozens of phishing files in a matter of minutes.
According to security reports monitored by Microsoft, three of these groups have integrated AI into every phase of their attacks. How do they operate?
Tailored lures: They create personalized, highly convincing PDF documents in minutes.
Malicious code: They use AI to write scripts and dangerous code faster.
Impersonation: They infiltrate companies and ecosystems by pretending to be legitimate entities.
In the crypto and Web3 world, where every click counts, AI-powered social engineering forces us to take extra precautions. Never download suspicious files or connect your wallet to links from dubious sources.
How safe do you feel against these new automated tactics used by cybercriminals? I’m reading your comments! 👇
$BTC $ETH $BNB
#ciberseguridad #phishing #InteligenciaArtificiala #BinanceSquareTips #SeguridadFinanciera
Microsoft issued a key warning on October 30: North Korean hacking groups are using artificial intelligence to generate dozens of phishing files in a matter of minutes.
According to security reports monitored by Microsoft, three of these groups have integrated AI into every phase of their attacks. How do they operate?
Tailored lures: They create personalized, highly convincing PDF documents in minutes.
Malicious code: They use AI to write scripts and dangerous code faster.
Impersonation: They infiltrate companies and ecosystems by pretending to be legitimate entities.
In the crypto and Web3 world, where every click counts, AI-powered social engineering forces us to take extra precautions. Never download suspicious files or connect your wallet to links from dubious sources.
How safe do you feel against these new automated tactics used by cybercriminals? I’m reading your comments! 👇
$BTC $ETH $BNB
#ciberseguridad #phishing #InteligenciaArtificiala #BinanceSquareTips #SeguridadFinanciera
1
110
·
--
Binance suffered a theft of 18,270 ($1.4B) on 31/10/2026, attributed to North Korean actors. This amount exceeds Tesla's reserves and comes close to SpaceX's, falling 442 short of its holdings. The incident doubles El Salvador's national reserve, highlighting the vulnerability of centralized infrastructure and the scale of the diverted capital.
— Analysis by EmeDotEme
#EmeDotEme #Bitcoin #Cybersecurity
Binance suffered a theft of 18,270 ($1.4B) on 31/10/2026, attributed to North Korean actors. This amount exceeds Tesla's reserves and comes close to SpaceX's, falling 442 short of its holdings. The incident doubles El Salvador's national reserve, highlighting the vulnerability of centralized infrastructure and the scale of the diverted capital.
— Analysis by EmeDotEme
#EmeDotEme #Bitcoin #Cybersecurity
— Analysis by EmeDotEme
#EmeDotEme #Bitcoin #Cybersecurity
49
·
--
The analytics firm Chainalysis has just confirmed a security incident.
The attackers managed to access non-sensitive user data.
The exposed information includes names, email addresses, and some user IDs.
It’s curious that a company specifically focused on cybersecurity would experience this kind of problem.
Are you surprised this happened at a firm of this caliber?
$BTC #Chainalysis #Cybersecurity
The analytics firm Chainalysis has just confirmed a security incident.
The attackers managed to access non-sensitive user data.
The exposed information includes names, email addresses, and some user IDs.
It’s curious that a company specifically focused on cybersecurity would experience this kind of problem.
Are you surprised this happened at a firm of this caliber?
$BTC #Chainalysis #Cybersecurity
The attackers managed to access non-sensitive user data.
The exposed information includes names, email addresses, and some user IDs.
It’s curious that a company specifically focused on cybersecurity would experience this kind of problem.
Are you surprised this happened at a firm of this caliber?
$BTC #Chainalysis #Cybersecurity
150
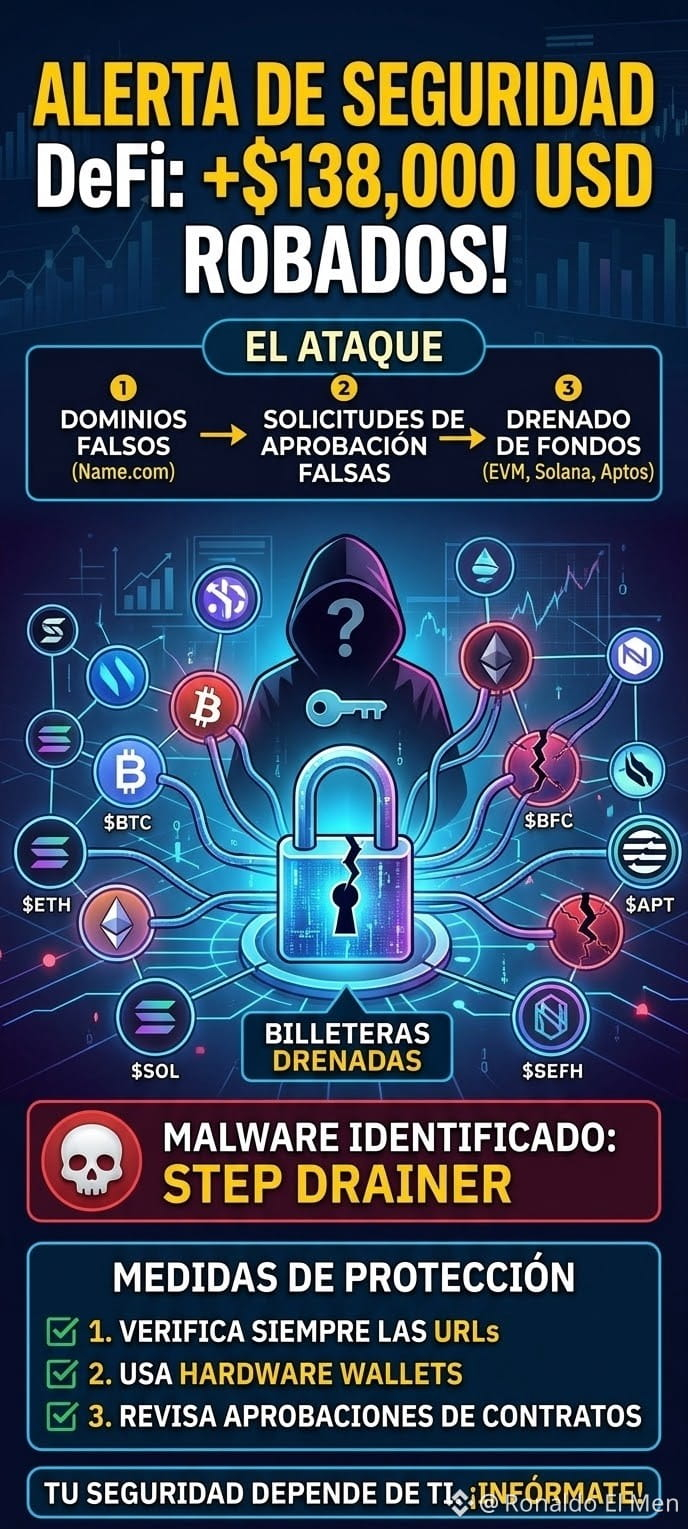
🚨 Cybersecurity Alert in the DeFi Ecosystem!
A group of hackers managed to breach 12 DeFi sites this weekend through domains registered on Name.com, using the dangerous Step Drainer malware to drain visitors’ wallets. More than $138,000 USD in stolen funds have already been traced to three wallets on EVM chains (not including potential losses on Solana or Aptos).
#ciberseguridad #DeFi #BinanceSquareFamily #EstafasCrypto #SeguridadCrypto
pto
🚨 Cybersecurity Alert in the DeFi Ecosystem!
A group of hackers managed to breach 12 DeFi sites this weekend through domains registered on Name.com, using the dangerous Step Drainer malware to drain visitors’ wallets. More than $138,000 USD in stolen funds have already been traced to three wallets on EVM chains (not including potential losses on Solana or Aptos).
#ciberseguridad #DeFi #BinanceSquareFamily #EstafasCrypto #SeguridadCrypto
pto
A group of hackers managed to breach 12 DeFi sites this weekend through domains registered on Name.com, using the dangerous Step Drainer malware to drain visitors’ wallets. More than $138,000 USD in stolen funds have already been traced to three wallets on EVM chains (not including potential losses on Solana or Aptos).
#ciberseguridad #DeFi #BinanceSquareFamily #EstafasCrypto #SeguridadCrypto
pto
2
335
Article
The blockchain didn’t fail; access did: the lesson from the Binance hackThe safe held. That’s the idea Marta Ambor explores in her column for Territorio Blockchain about the theft of some $6.3 billion from Binance on October 29, more than four times what was taken from Bybit in February 2025.
Exchanges keep most of their funds in cold wallets, disconnected from the internet, and use hot wallets with automated signing to process withdrawals instantly. The attacker didn’t touch the cold wallets. According to Binance, they gained access through an engineer’s laptop, moved to an internal service, and ordered withdrawals that no one had authorized. The company maintains that no private keys were leaked. TRM Labs suggests that the machine doing the signing was under the attacker’s control and attributes the attack, with high confidence, to TraderTraitor, a group linked to North Korea. Binance has not confirmed this.
The blockchain didn’t fail; access did: the lesson from the Binance hack
The safe held. That’s the idea Marta Ambor explores in her column for Territorio Blockchain about the theft of some $6.3 billion from Binance on October 29, more than four times what was taken from Bybit in February 2025.
Exchanges keep most of their funds in cold wallets, disconnected from the internet, and use hot wallets with automated signing to process withdrawals instantly. The attacker didn’t touch the cold wallets. According to Binance, they gained access through an engineer’s laptop, moved to an internal service, and ordered withdrawals that no one had authorized. The company maintains that no private keys were leaked. TRM Labs suggests that the machine doing the signing was under the attacker’s control and attributes the attack, with high confidence, to TraderTraitor, a group linked to North Korea. Binance has not confirmed this.
Exchanges keep most of their funds in cold wallets, disconnected from the internet, and use hot wallets with automated signing to process withdrawals instantly. The attacker didn’t touch the cold wallets. According to Binance, they gained access through an engineer’s laptop, moved to an internal service, and ordered withdrawals that no one had authorized. The company maintains that no private keys were leaked. TRM Labs suggests that the machine doing the signing was under the attacker’s control and attributes the attack, with high confidence, to TraderTraitor, a group linked to North Korea. Binance has not confirmed this.
2
838
Article
The Binance hack explained: how they got in, who’s being blamed, and what has been frozenOn Thursday, October 29, $6.3 billion left Binance in about twenty minutes—four times the amount taken in the attack on Bybit. In the latest Territorio Blockchain livestream, I go over what’s known so far.
What I cover in the video:
• How it started: according to Binance itself, with an employee’s laptop
• What a hot wallet is and why, because it’s connected to the internet, it accounts for a large share of an exchange’s operational risk
• Who’s being blamed: TRM Labs points to North Korea
The Binance hack explained: how they got in, who’s being blamed, and what has been frozen
On Thursday, October 29, $6.3 billion left Binance in about twenty minutes—four times the amount taken in the attack on Bybit. In the latest Territorio Blockchain livestream, I go over what’s known so far.
What I cover in the video:
• How it started: according to Binance itself, with an employee’s laptop
• What a hot wallet is and why, because it’s connected to the internet, it accounts for a large share of an exchange’s operational risk
• Who’s being blamed: TRM Labs points to North Korea
What I cover in the video:
• How it started: according to Binance itself, with an employee’s laptop
• What a hot wallet is and why, because it’s connected to the internet, it accounts for a large share of an exchange’s operational risk
• Who’s being blamed: TRM Labs points to North Korea
1
4
7.1k

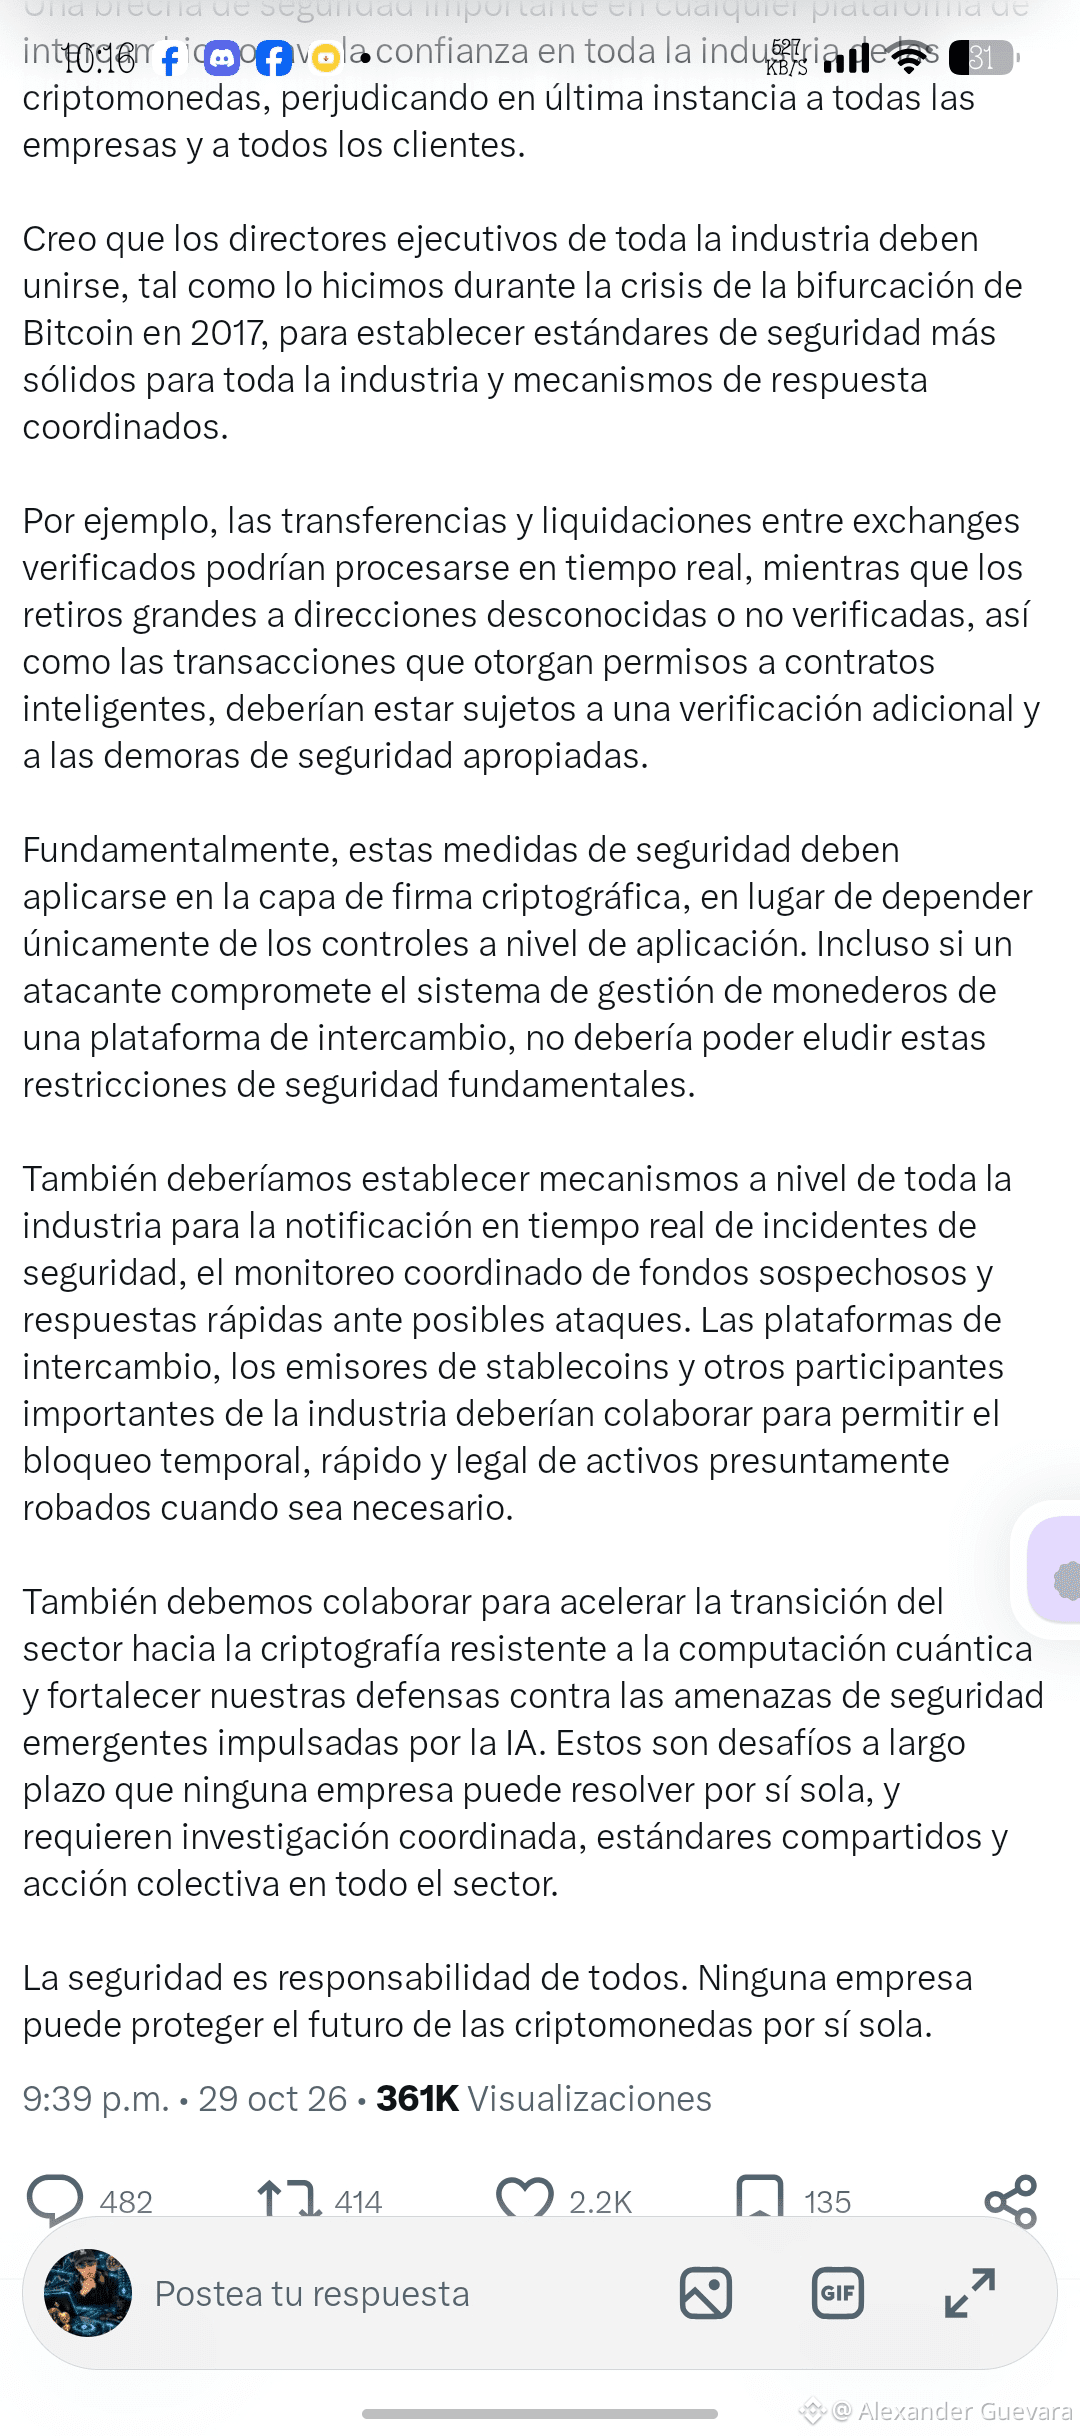
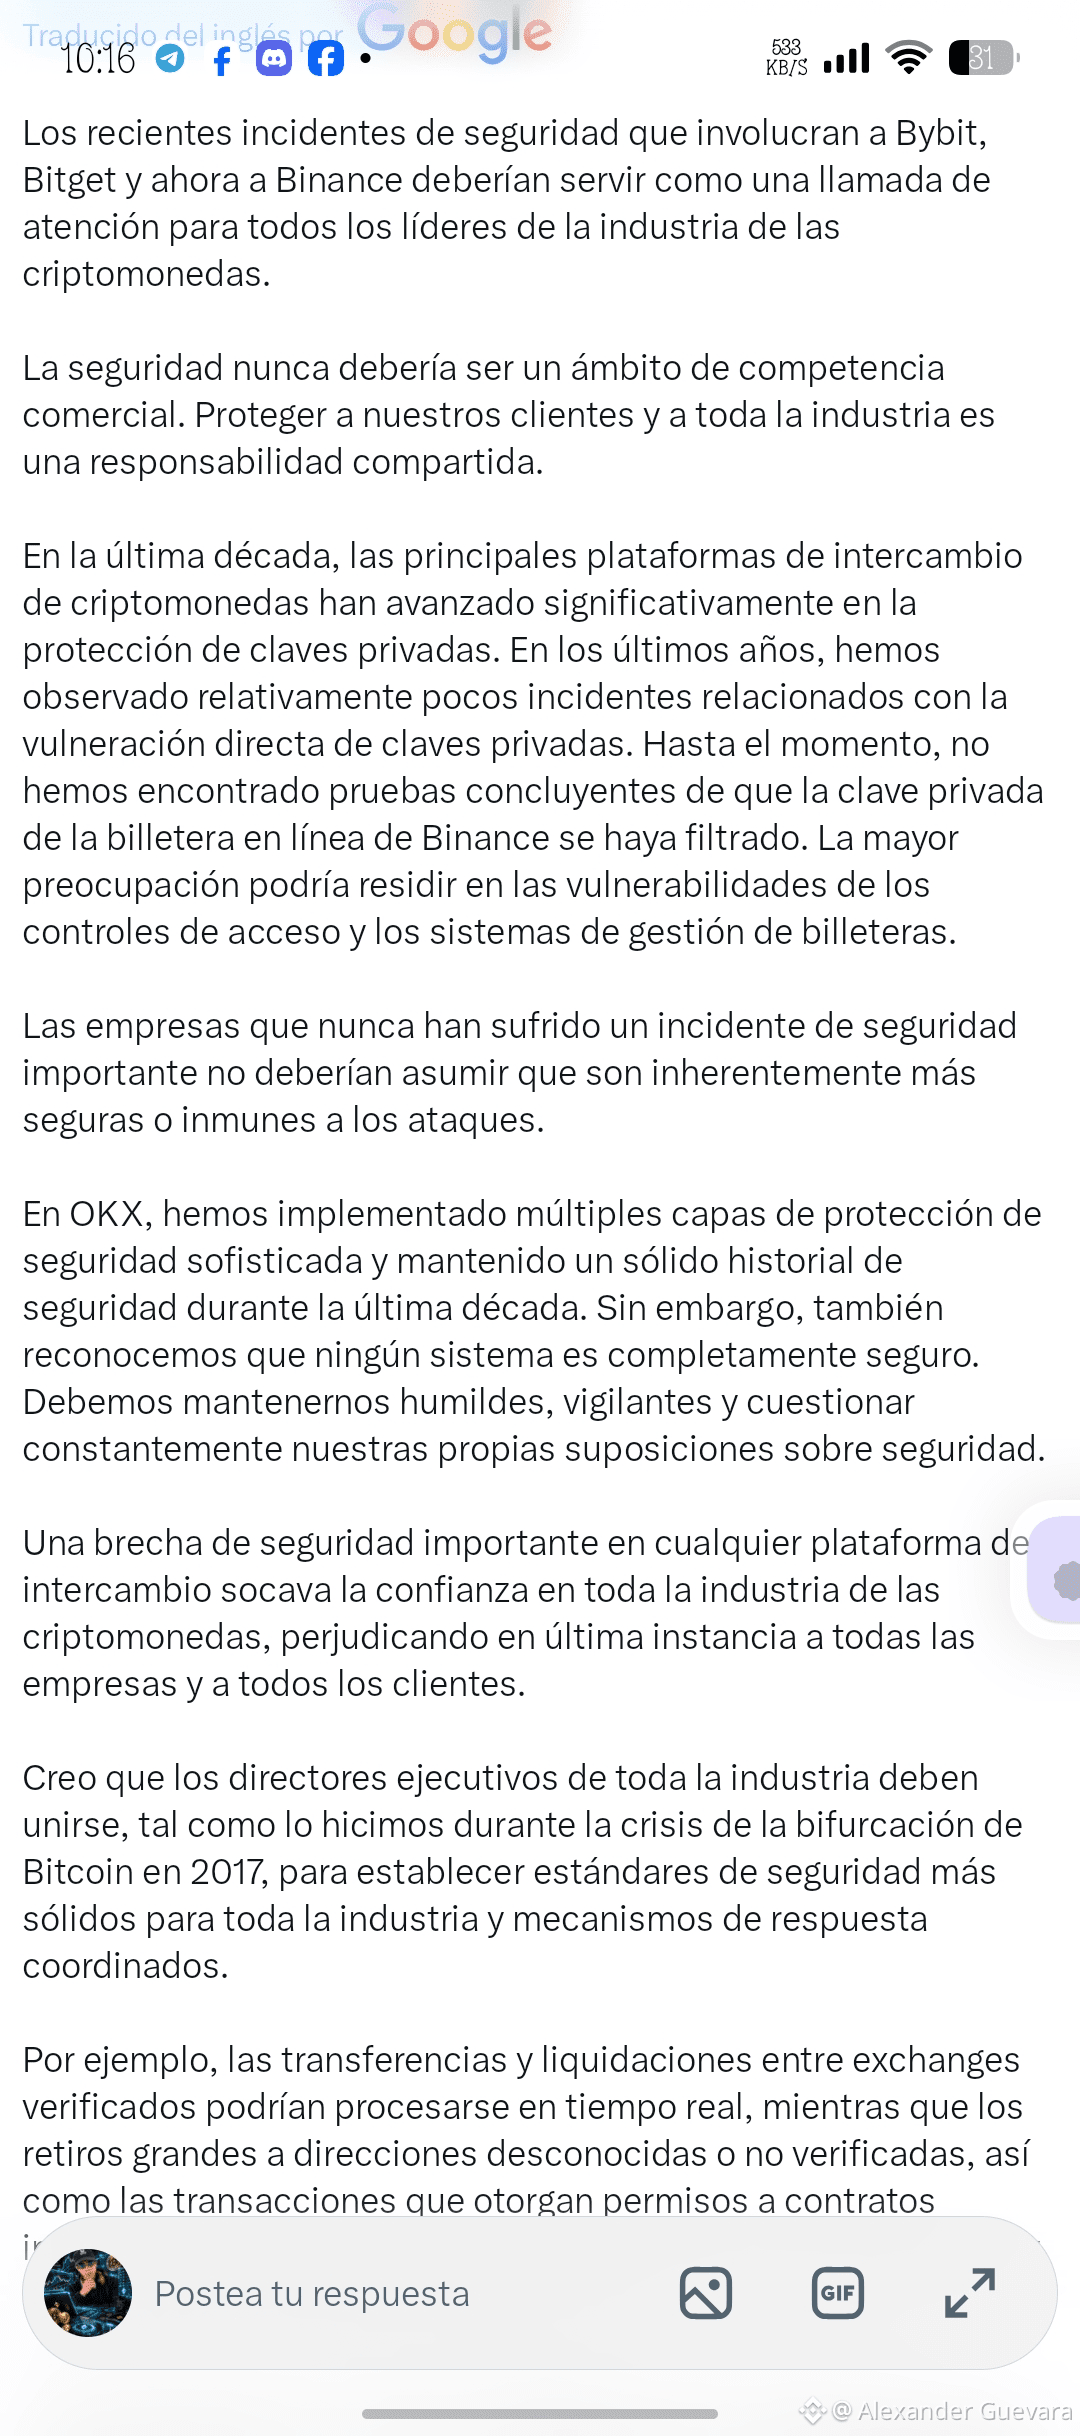
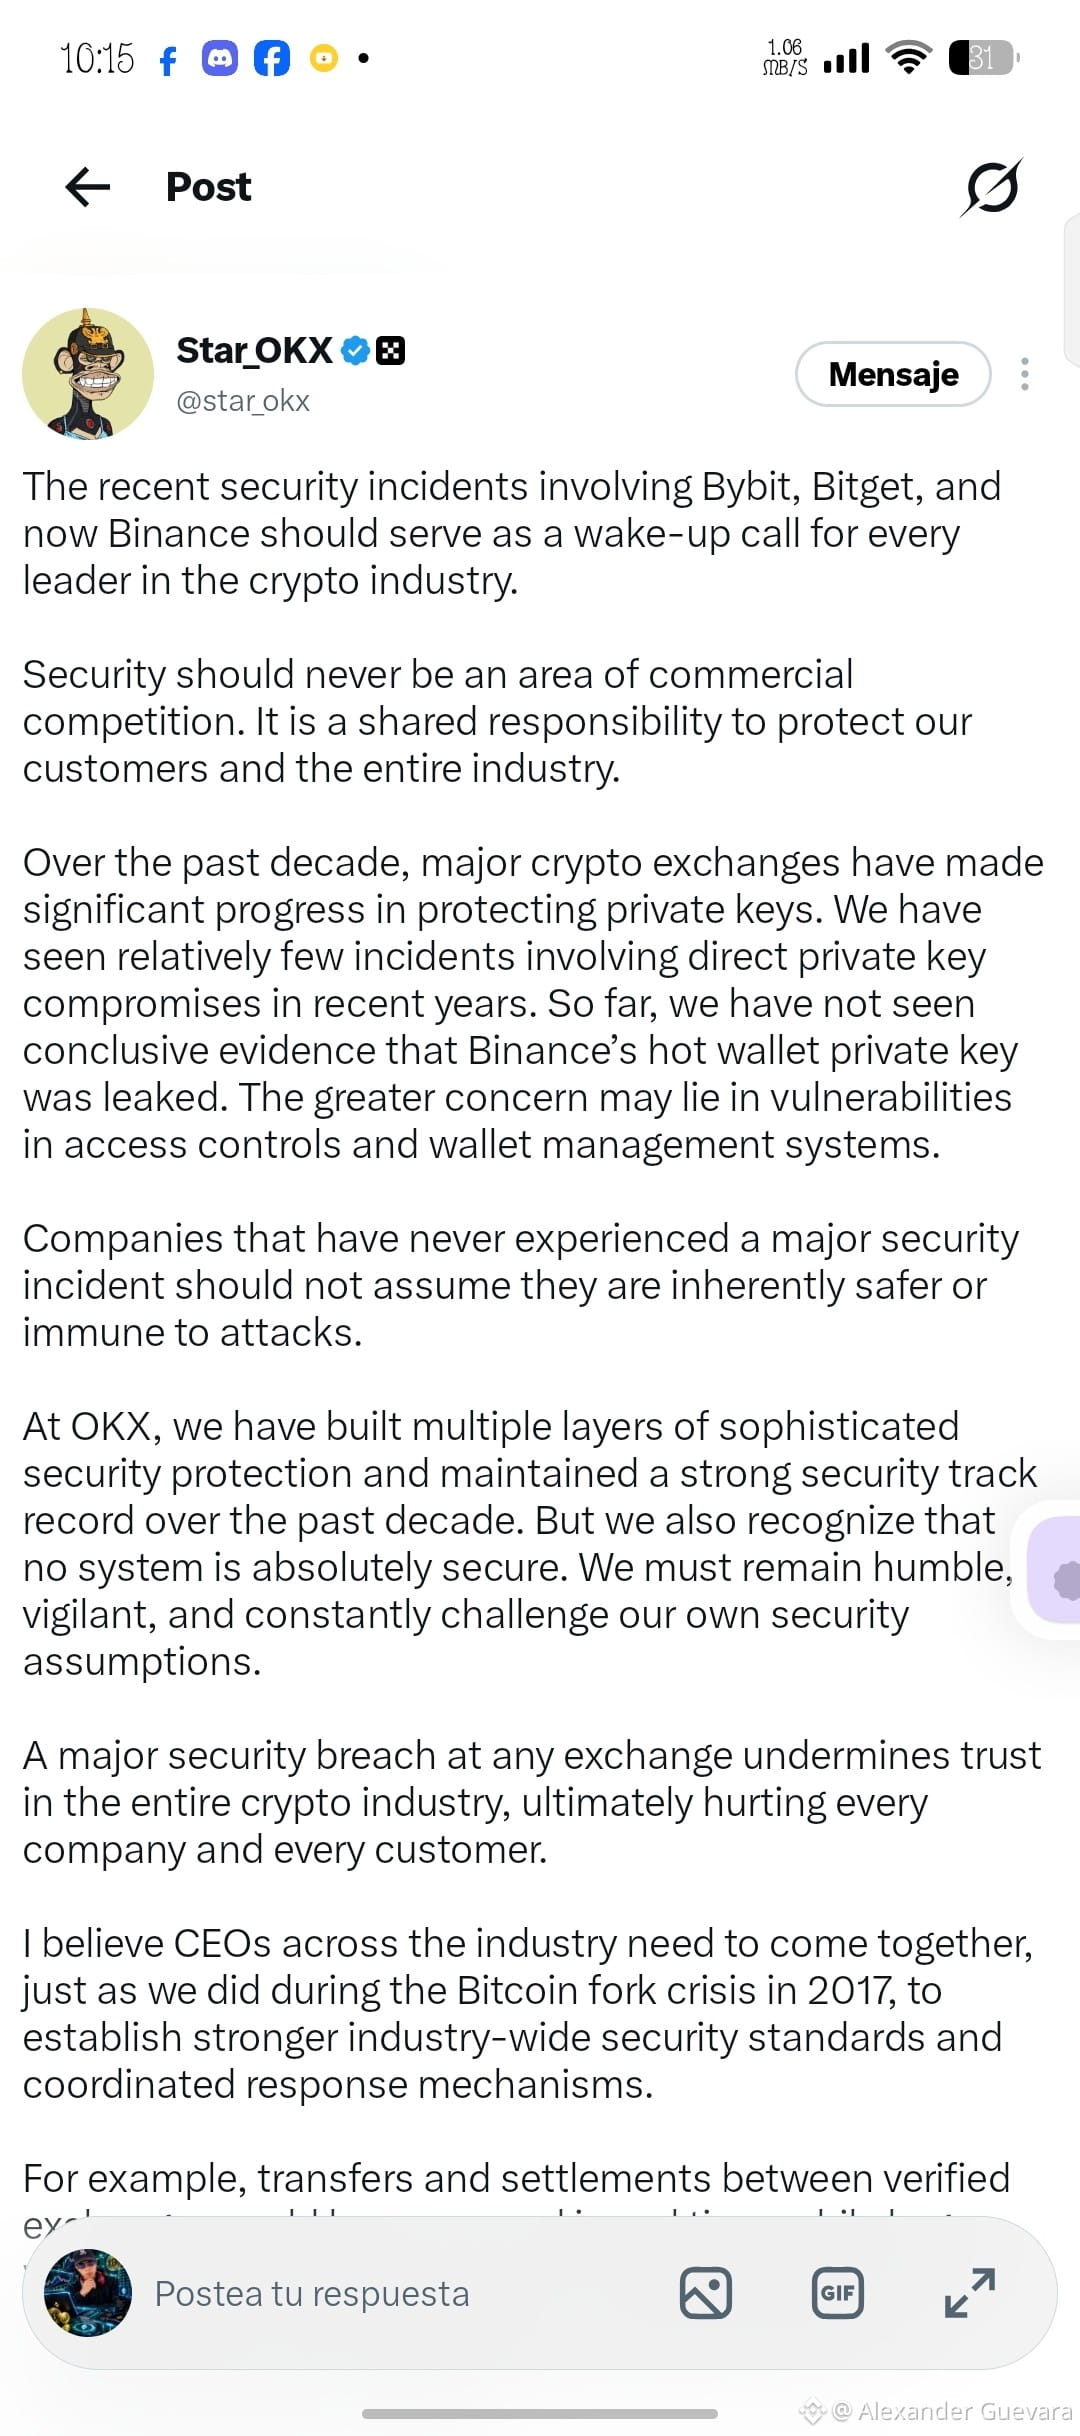
🚨 Security is not a competitive advantage: it’s a shared responsibility 🤝
Recent incidents in the crypto industry remind us that a breach at any exchange affects the trust of the entire ecosystem.
No platform is immune, and no platform can solve this alone.
It’s time for industry leaders to unite—just as we did in 2017—to create a united front:
Strategic alliances: Establish strong security standards and coordinated response protocols among exchanges.
Early alerts: Real-time monitoring of suspicious funds and temporary blocking of stolen assets in collaboration with stablecoin issuers.
Strict controls: Security delays and additional verification for large withdrawals to unknown addresses.
A vision for the future: Accelerate the transition to quantum-resistant cryptography in the face of AI threats.
Security protects us all.
What do you think of this global collaboration initiative? 👇
#BinanceSquare #ciberseguridad #crypto #blockchain #CEO
@heyi @CZ @richardteng @Binance_Announcement @Binance_News
{web3_wallet_create}(10x75231f58b43240c9718dd58b4967c5114342a86c)
$BNB $BTC $BNCB
🚨 Security is not a competitive advantage: it’s a shared responsibility 🤝
Recent incidents in the crypto industry remind us that a breach at any exchange affects the trust of the entire ecosystem.
No platform is immune, and no platform can solve this alone.
It’s time for industry leaders to unite—just as we did in 2017—to create a united front:
Strategic alliances: Establish strong security standards and coordinated response protocols among exchanges.
Early alerts: Real-time monitoring of suspicious funds and temporary blocking of stolen assets in collaboration with stablecoin issuers.
Strict controls: Security delays and additional verification for large withdrawals to unknown addresses.
A vision for the future: Accelerate the transition to quantum-resistant cryptography in the face of AI threats.
Security protects us all.
What do you think of this global collaboration initiative? 👇
#BinanceSquare #ciberseguridad #crypto #blockchain #CEO
@Yi He @CZ @Richard Teng @Binance Announcement @Binance News
$BNB $BTC $BNCB
Recent incidents in the crypto industry remind us that a breach at any exchange affects the trust of the entire ecosystem.
No platform is immune, and no platform can solve this alone.
It’s time for industry leaders to unite—just as we did in 2017—to create a united front:
Strategic alliances: Establish strong security standards and coordinated response protocols among exchanges.
Early alerts: Real-time monitoring of suspicious funds and temporary blocking of stolen assets in collaboration with stablecoin issuers.
Strict controls: Security delays and additional verification for large withdrawals to unknown addresses.
A vision for the future: Accelerate the transition to quantum-resistant cryptography in the face of AI threats.
Security protects us all.
What do you think of this global collaboration initiative? 👇
#BinanceSquare #ciberseguridad #crypto #blockchain #CEO
@Yi He @CZ @Richard Teng @Binance Announcement @Binance News
$BNB $BTC $BNCB
134
·
--
Bearish
🚨 ELON MUSK WARNS THAT EVERY DAY IS A ZERO-DAY AFTER THE HISTORIC BINANCE HACK 🚨⚠️
The digital financial world is on high alert 📉🌐 after the massive cyberattack 💻🔐 that rocked the platform was confirmed. It is already being considered the largest theft in history 💸📊.
Amid this alarming situation 🚨📱, statements from key figures and the freezing of assets by tech giants 🏦 have sparked debate about cybersecurity 🕵️♂️ and the fragility of current systems in the face of unstoppable threats 🤖⚡.
#binance #ciberseguridad #Criptomonedas
🚨 ELON MUSK WARNS THAT EVERY DAY IS A ZERO-DAY AFTER THE HISTORIC BINANCE HACK 🚨⚠️
The digital financial world is on high alert 📉🌐 after the massive cyberattack 💻🔐 that rocked the platform was confirmed. It is already being considered the largest theft in history 💸📊.
Amid this alarming situation 🚨📱, statements from key figures and the freezing of assets by tech giants 🏦 have sparked debate about cybersecurity 🕵️♂️ and the fragility of current systems in the face of unstoppable threats 🤖⚡.
#binance #ciberseguridad #Criptomonedas
The digital financial world is on high alert 📉🌐 after the massive cyberattack 💻🔐 that rocked the platform was confirmed. It is already being considered the largest theft in history 💸📊.
Amid this alarming situation 🚨📱, statements from key figures and the freezing of assets by tech giants 🏦 have sparked debate about cybersecurity 🕵️♂️ and the fragility of current systems in the face of unstoppable threats 🤖⚡.
#binance #ciberseguridad #Criptomonedas
60
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#CryptoSelloffTriggersMultipleWhaleLiquidations
169,455 views
1,746 Discussing
2
#USSpotXRPETFsSeeLargestWeeklyOutflowIn8Months
153,290 views
1,534 Discussing
3
#WillFOMCMinutesReinforceRateHikeExpectations?
44,325 views
727 Discussing
4
#BitcoinActiveSupplyInProfitDropsBelow45%
229,133 views
1,786 Discussing
5
#TONStrategyReports$23.97MQ3NetLoss
20,147 views
149 Discussing
6
#KavaSaysAbnormalActivityLimitedToKavaLend
152,351 views
1,016 Discussing
7
#WORPTLetsTouristsConvertCryptoToThaiBaht
54,232 views
410 Discussing
8
#WhoWillSucceedJensenHuangatNvidia?
352,317 views
2,154 Discussing
9
#WhatWillDriveCryptoandStocks’NextRebound?
880,528 views
3,965 Discussing
10
#TradFiForBeginners
847,928 views
4,978 Discussing