

#keystonewebsitebreachexposesbuyersshippingaddresses
keystonewebsitebreachexposesbuyersshippingaddresses
2,199 views
45 Discussing
Hot
Latest
·
--
Bullish
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
🚨 SECURITY ALERT: Keystone Website Breach Exposes Buyers' Shipping Addresses! 📦🔐
Popular cryptocurrency hardware wallet manufacturer Keystone has officially disclosed a major security breach affecting its online web store, raising serious privacy and physical security concerns for buyers.
$ZEC
{future}(ZECUSDT)
Here is what went down and what you need to know:
$ETH
{future}(ETHUSDT)
The Incident: Keystone detected unauthorized access to its official website. After reviewing API activity tied to its Shopify-powered storefront, the company confirmed that an unauthorized third party managed to extract customer data.
$ASTER
{future}(ASTERUSDT)
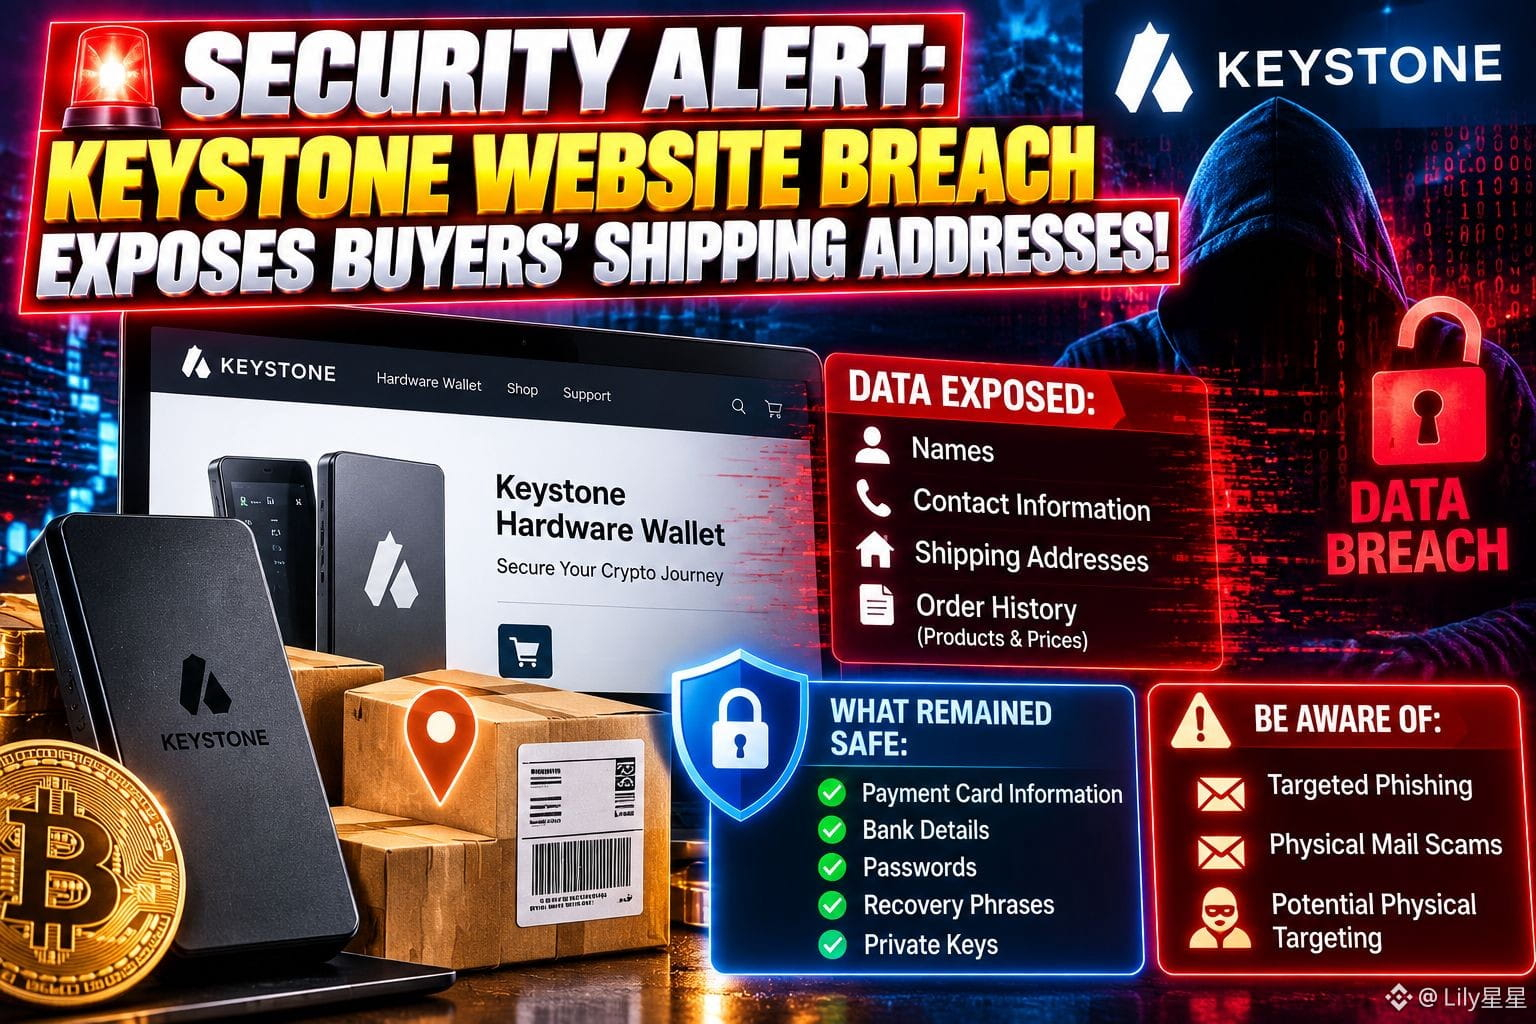
What Data Was Exposed: The leaked records include customer names, contact information, shipping/delivery addresses, and specific order history (such as purchased products and prices).
What Remained Safe: Keystone explicitly confirmed that payment card information, bank details, passwords, and most importantly—wallet recovery phrases and private keys—were NOT compromised.
🛡️ What Should Affected Users Do?
Do NOT Reset Your Device: Your crypto funds and recovery seed phrases are secure on your hardware wallet. You do not need to move funds or reset your device unless you notice suspicious on-chain activity unrelated to this.
Stay Hyper-Vigilant: Treat any communication (emails, text messages, or physical mail) referencing your Keystone purchase with extreme skepticism. Never input your 24-word recovery phrase into any website or app.
Stay safe, verify every message, and keep your guard up! 🔒
⚠️ Disclaimer: This is not financial or security advice. Always Lilly.
#BinancePick #EarningsSeason #ElectrumWalletBugLetRogueServersStealFunds
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
🚨 SECURITY ALERT: Keystone Website Breach Exposes Buyers' Shipping Addresses! 📦🔐
Popular cryptocurrency hardware wallet manufacturer Keystone has officially disclosed a major security breach affecting its online web store, raising serious privacy and physical security concerns for buyers.
$ZEC
Here is what went down and what you need to know:
$ETH
The Incident: Keystone detected unauthorized access to its official website. After reviewing API activity tied to its Shopify-powered storefront, the company confirmed that an unauthorized third party managed to extract customer data.
$ASTER
What Data Was Exposed: The leaked records include customer names, contact information, shipping/delivery addresses, and specific order history (such as purchased products and prices).
What Remained Safe: Keystone explicitly confirmed that payment card information, bank details, passwords, and most importantly—wallet recovery phrases and private keys—were NOT compromised.
🛡️ What Should Affected Users Do?
Do NOT Reset Your Device: Your crypto funds and recovery seed phrases are secure on your hardware wallet. You do not need to move funds or reset your device unless you notice suspicious on-chain activity unrelated to this.
Stay Hyper-Vigilant: Treat any communication (emails, text messages, or physical mail) referencing your Keystone purchase with extreme skepticism. Never input your 24-word recovery phrase into any website or app.
Stay safe, verify every message, and keep your guard up! 🔒
⚠️ Disclaimer: This is not financial or security advice. Always Lilly.
#BinancePick #EarningsSeason #ElectrumWalletBugLetRogueServersStealFunds
1
190
·
--
#KeystoneWebsiteBreachExposesBuyersShippingAddresses #BMT
🚨 #KeystoneBreach: Crypto Security Alert
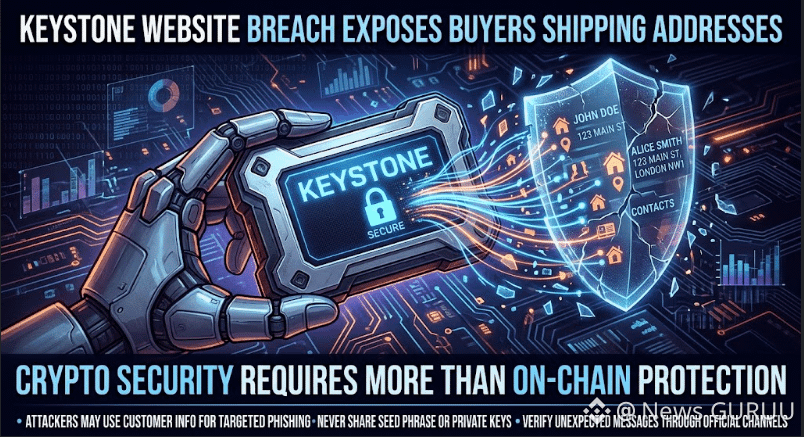
Keystone reportedly suffered a website breach exposing customer contact details, shipping addresses, and purchase records. The company says private keys, seed phrases, passwords, and payment details were not affected.
⚠️ Key risks: Targeted phishing and fake security messages.
🔐 Stay safe:
• Never share your seed phrase or private keys.
• Verify messages through official channels.
• Avoid suspicious links and requests to transfer funds.
📌 This appears to be a data privacy incident, not a confirmed blockchain exploit or theft of customer funds. The full scope remains unclear.
💬 Should hardware wallet companies collect less customer data?."CLICK ON THE BELOW YELLOW COIN TAG TO GO TO DESIRED TRADING PAGE TO GET BENEFIT TRADE"$DODO $BMT $BREV
{spot}(BREVUSDT)
{spot}(BMTUSDT)
{spot}(DODOUSDT)
#KeystoneWebsiteBreachExposesBuyersShippingAddresses #BMT
🚨 #KeystoneBreach: Crypto Security Alert
Keystone reportedly suffered a website breach exposing customer contact details, shipping addresses, and purchase records. The company says private keys, seed phrases, passwords, and payment details were not affected.
⚠️ Key risks: Targeted phishing and fake security messages.
🔐 Stay safe:
• Never share your seed phrase or private keys.
• Verify messages through official channels.
• Avoid suspicious links and requests to transfer funds.
📌 This appears to be a data privacy incident, not a confirmed blockchain exploit or theft of customer funds. The full scope remains unclear.
💬 Should hardware wallet companies collect less customer data?."CLICK ON THE BELOW YELLOW COIN TAG TO GO TO DESIRED TRADING PAGE TO GET BENEFIT TRADE"$DODO $BMT $BREV
1
25


#KeystoneWebsiteBreachExposesBuyersShippingAddresses
🔐⚠️ Keystone Website Breach Exposes Crypto Buyers’ Shipping Addresses ⚠️🔐
Sometimes, the biggest security risk isn't inside your wallet. It's the address where you keep it.
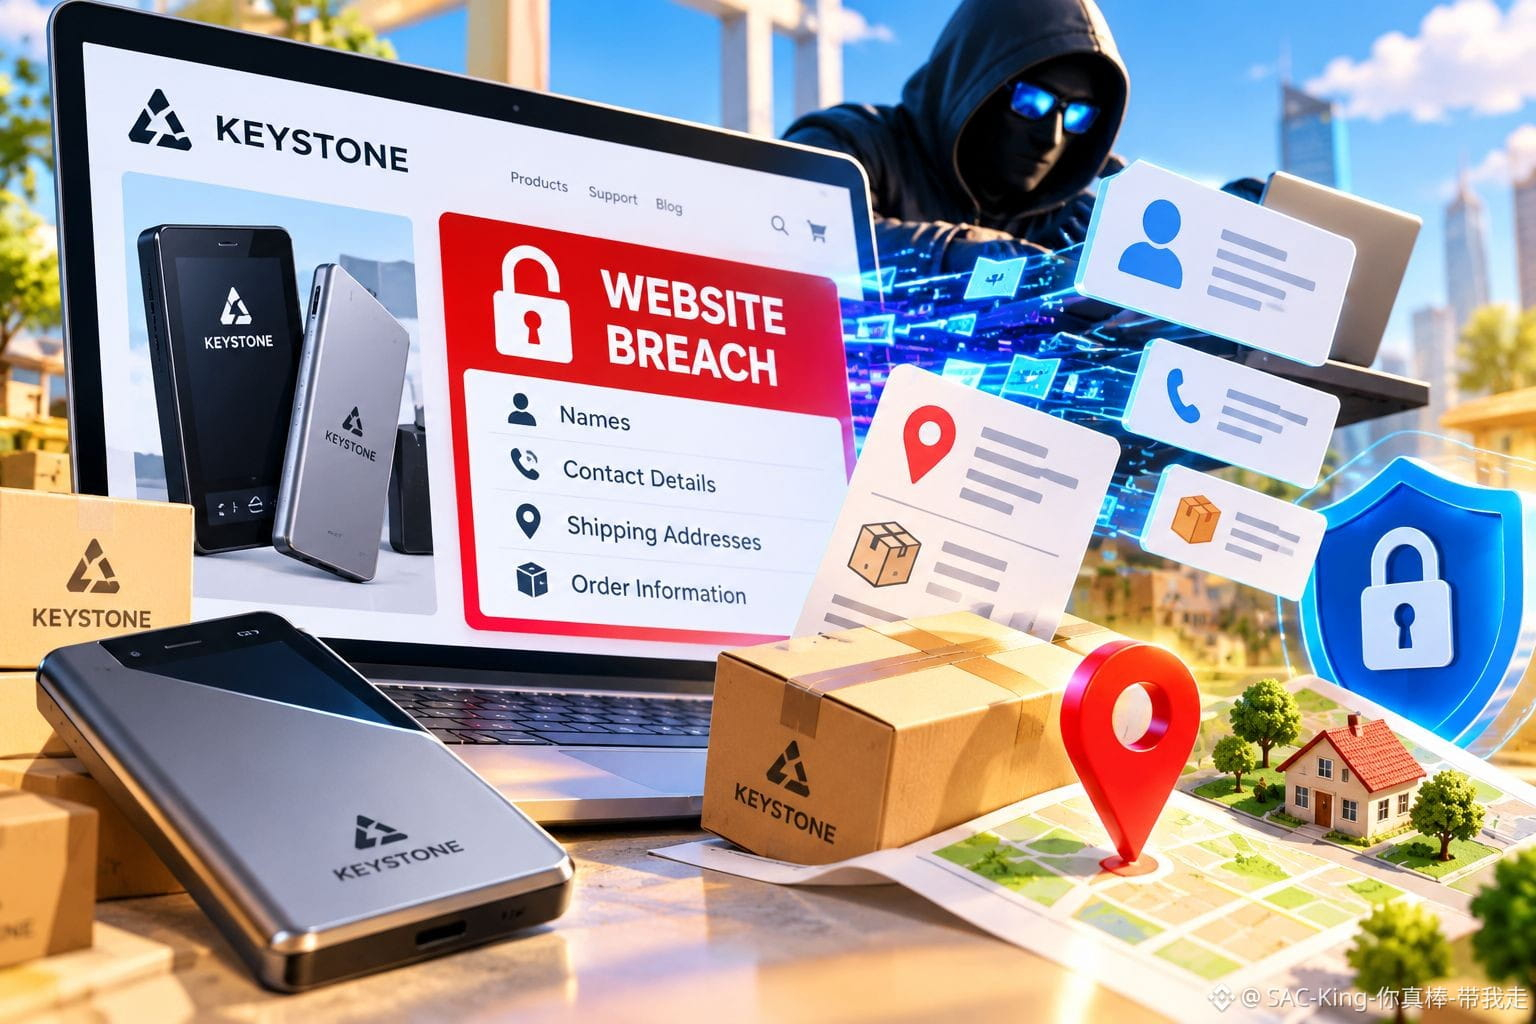
Keystone, a cryptocurrency hardware wallet manufacturer, has disclosed a website breach that exposed customers’ names, contact details, shipping addresses, and order information.
The company detected unauthorized access on October 20 and confirmed the data exposure on October 23, 2026, after reviewing activity involving its Shopify-powered store.
Keystone says payment details, recovery phrases, private keys, and wallet passwords were not exposed. It has blocked the unauthorized access, fixed the vulnerability, and begun notifying affected customers. The number of affected users remains undisclosed.
But here's the bigger concern: knowing someone's identity, home address, and hardware wallet purchase can help criminals craft convincing phishing attacks or potentially target crypto holders in the real world.
My Take: Self-custody protects control over your crypto, but it cannot protect personal information leaked by a third-party service. Your security is only as strong as the weakest link connecting your digital assets to your real identity.
If you purchased from Keystone, verify alerts through official channels, ignore unsolicited refund or replacement offers, and never share your recovery phrase. No legitimate support agent needs it.
True crypto security means protecting both your assets and the personal information that could make you a target.
Should hardware wallet companies be held to stricter data-deletion standards after a customer's order is completed?
Disclaimer: This post is for educational purposes only and is not financial or security advice.
#CryptoSecurity #DataBreach #GrowWithSAC $QNT $ENA $PYTH
171
🔎 Keystone has blocked the unauthorized access, fixed the vulnerability, and begun notifying affected customers. However, the company has not publicly disclosed how many people were affected or explained the full technical cause. $BTC $SOL
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
🔎 Keystone has blocked the unauthorized access, fixed the vulnerability, and begun notifying affected customers. However, the company has not publicly disclosed how many people were affected or explained the full technical cause. $BTC $SOL
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
12
⚠️ A crypto wallet company’s customer database can become a target even when the wallet itself remains secure. Keystone says recovery phrases, private keys, wallet passwords, and payment details were not exposed. $BTC $ETH
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
⚠️ A crypto wallet company’s customer database can become a target even when the wallet itself remains secure. Keystone says recovery phrases, private keys, wallet passwords, and payment details were not exposed. $BTC $ETH
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
11
🔐 Keystone, a crypto hardware wallet maker, disclosed a website breach that exposed customers’ names, contact details, shipping addresses, and purchase records. The company detected unauthorized access on October 20 and confirmed the data theft on October 23, 2026. $BTC
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
10

·
--
🚨 Keystone says its website breach exposed shipping addresses and order details—not private keys. That doesn't make the leak harmless.
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
Keystone confirmed that an unauthorized third party obtained customer information from its Shopify-based store.
The exposed information included names, contact details, shipping addresses and order details, including the products purchased and their prices.
The company said payment-card information, bank details, recovery phrases, private keys and wallet passwords were not exposed. It has not publicly disclosed how many customers were affected.
There's another detail worth examining.
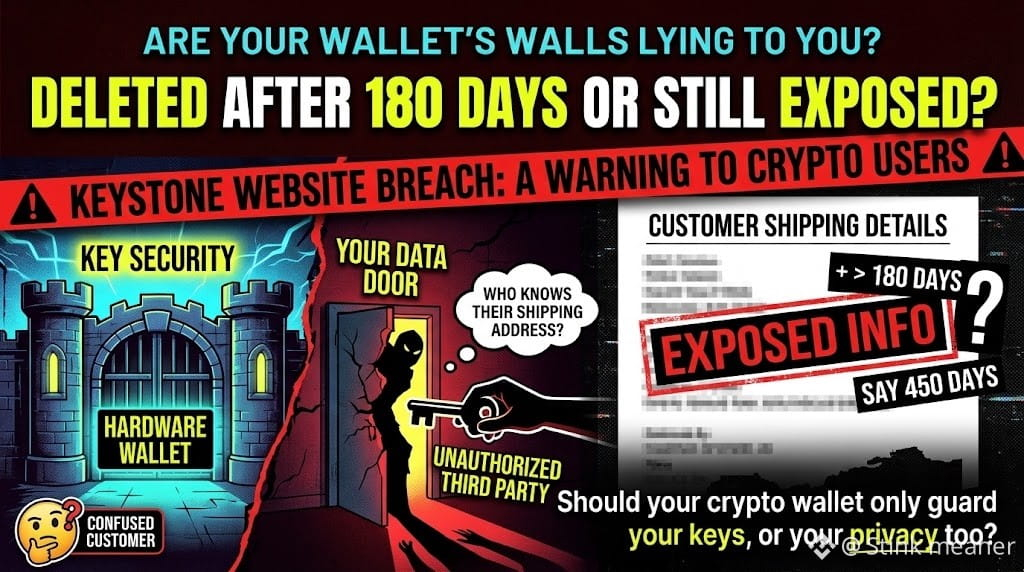
Keystone had promoted a policy of deleting shipping information 180 days after an order. Some customers subsequently claimed that information connected to older orders was exposed. The company has not yet provided a full public explanation of the breach's scope or how the older records remained accessible.
A hardware wallet can protect the keys that control funds while the surrounding customer database creates a separate privacy risk.
Exposed purchase and address information can also help scammers construct convincing phishing messages or target crypto users more precisely.
Should hardware-wallet manufacturers be judged primarily on key security—or on how well they protect the personal information that identifies their customers?
DYOR, Not financial advice.
$BNB $ETH $BTC
{future}(BTCUSDT)
{future}(ETHUSDT)
{future}(BNBUSDT)
#ElectrumWalletBugLetRogueServersStealFunds #ElectrumFixesHighRiskExploitInVersionsBefore4.8.3
#CryptoSecurity #HardwareWallets
🚨 Keystone says its website breach exposed shipping addresses and order details—not private keys. That doesn't make the leak harmless.
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
Keystone confirmed that an unauthorized third party obtained customer information from its Shopify-based store.
The exposed information included names, contact details, shipping addresses and order details, including the products purchased and their prices.
The company said payment-card information, bank details, recovery phrases, private keys and wallet passwords were not exposed. It has not publicly disclosed how many customers were affected.
There's another detail worth examining.
Keystone had promoted a policy of deleting shipping information 180 days after an order. Some customers subsequently claimed that information connected to older orders was exposed. The company has not yet provided a full public explanation of the breach's scope or how the older records remained accessible.
A hardware wallet can protect the keys that control funds while the surrounding customer database creates a separate privacy risk.
Exposed purchase and address information can also help scammers construct convincing phishing messages or target crypto users more precisely.
Should hardware-wallet manufacturers be judged primarily on key security—or on how well they protect the personal information that identifies their customers?
DYOR, Not financial advice.
$BNB $ETH $BTC
#ElectrumWalletBugLetRogueServersStealFunds #ElectrumFixesHighRiskExploitInVersionsBefore4.8.3
#CryptoSecurity #HardwareWallets
1
60
·
--
🚨 KEYSTONE WEBSITE BREACH RAISES A SERIOUS PRIVACY WARNING
A website security breach can expose far more than customers expect
Reports about the Keystone website breach indicate that buyers shipping addresses may have been exposed, raising concerns about customer privacy and data security
The risk goes beyond unwanted messages because exposed delivery details can potentially be abused for phishing scams, impersonation, or targeted social engineering
For affected buyers, the priority is to watch for suspicious delivery notifications, unexpected messages, and requests for personal or financial information
Never trust a link simply because a message appears to come from a delivery company or a familiar brand
The bigger lesson is clear
In the digital economy, protecting customer data is just as important as protecting customer funds
Do you think companies should face stronger penalties when customer shipping information is exposed
#KeystoneWebsiteBreachExposesBuyersShippingAddresses $BTC
{spot}(BTCUSDT)
🚨 KEYSTONE WEBSITE BREACH RAISES A SERIOUS PRIVACY WARNING
A website security breach can expose far more than customers expect
Reports about the Keystone website breach indicate that buyers shipping addresses may have been exposed, raising concerns about customer privacy and data security
The risk goes beyond unwanted messages because exposed delivery details can potentially be abused for phishing scams, impersonation, or targeted social engineering
For affected buyers, the priority is to watch for suspicious delivery notifications, unexpected messages, and requests for personal or financial information
Never trust a link simply because a message appears to come from a delivery company or a familiar brand
The bigger lesson is clear
In the digital economy, protecting customer data is just as important as protecting customer funds
Do you think companies should face stronger penalties when customer shipping information is exposed
#KeystoneWebsiteBreachExposesBuyersShippingAddresses $BTC
63
·
--
A significant data breach has occurred at Keystone, leading to the exposure of sensitive buyer shipping addresses. This incident raises serious concerns about data security within the e-commerce ecosystem and highlights the ongoing risks faced by consumers online. Such breaches can lead to identity theft, phishing attempts, and other malicious activities. Users are advised to remain vigilant and monitor their accounts for any suspicious activity. This event underscores the critical importance of robust cybersecurity measures for all platforms handling personal data.
While this breach directly impacts users of Keystone, it serves as a stark reminder for the broader crypto community about the need for secure practices, especially when dealing with personal information related to transactions or platform access. Always use strong, unique passwords and enable two-factor authentication wherever possible.
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
64

·
--
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
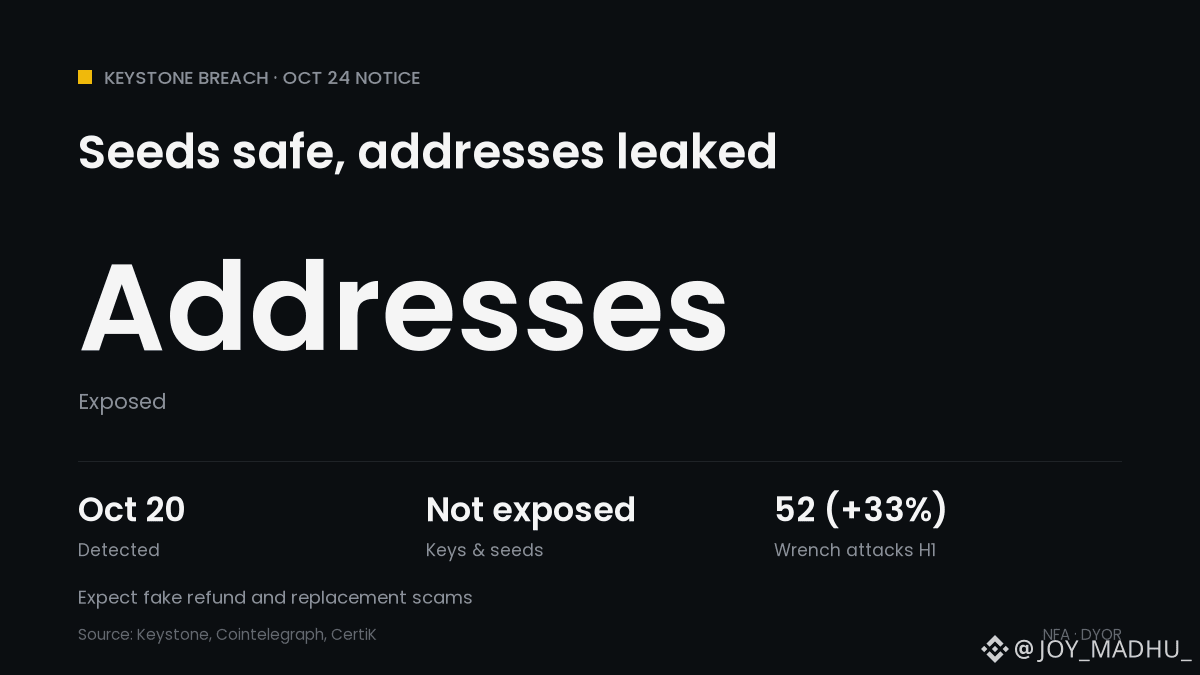
📦 Keystone Leak: Your Seed Is Safe, Your Address Isn't
📅 Oct 20: unauthorized access to Keystone's Shopify store detected
🔍 Oct 23: confirmed a third party took customer shipping data
📄 Exposed: names, contacts, addresses, order items and prices
✅ Not exposed: recovery phrases, private keys, wallet passwords, payment data
⚠️ Some buyers from 2024 got notices, despite a 180-day deletion policy
📞 Users already report scam calls citing old orders
📊 CertiK counted 52 wrench attacks in H1 2026, up 33% year on year
What it means for crypto: no funds lost and $BTC security isn't the issue, but a leaked buyer list marks people as likely holders. Keystone will never ask for your seed.
Would you buy a hardware wallet under a PO box or alias address? 👇
$BTC
#KeystoneWebsiteBreachExposesBuyersShippingAddresses #CryptoNews #WalletSecurity #Bitcoin
31
·
--
Bullish
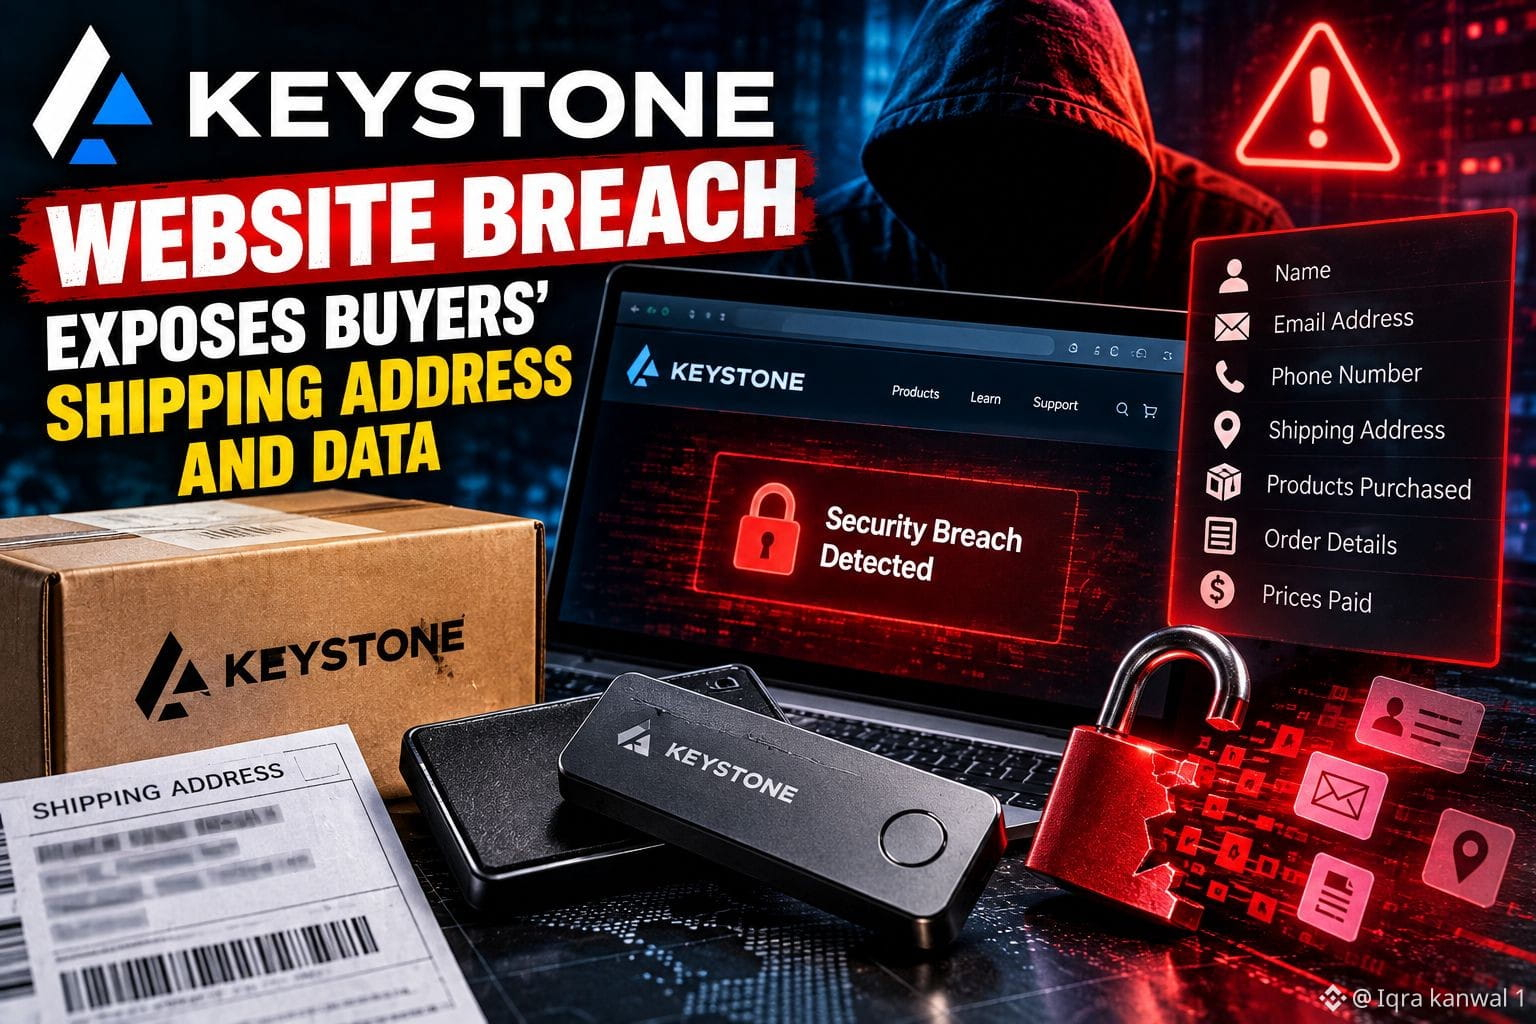
#KeystoneWebsiteBreachExposesBuyersShippingAddresses 🚨 Keystone Website Breach: A Reminder That Crypto Privacy Goes Beyond Private Keys
Keystone has disclosed a website breach that exposed customer names, contact details, shipping addresses and order information, including products purchased and prices paid. The company says it detected unauthorized access on October 20 and confirmed the data exposure on October 23.
According to Keystone, payment details, wallet passwords, private keys and recovery phrases were not compromised. That distinction matters: the incident does not automatically mean customers’ crypto funds are at risk. However, linking a real-world address to a hardware wallet purchase can create a serious privacy and security concern.
The biggest immediate risk may be targeted phishing. Attackers could use genuine order details to impersonate support teams, offer fake replacements or send convincing messages designed to steal recovery phrases.
Keystone says it has blocked the unauthorized access, fixed the vulnerability and started notifying affected customers. The number of people impacted and the full technical details have not yet been publicly established. Questions have also emerged about the company’s stated 180-day data-retention policy.
For users, the practical response is clear:
🔹 Never share your seed phrase or private keys.
🔹 Ignore unexpected refund, replacement or recovery offers.
🔹 Avoid links in unsolicited messages; contact support through the official website.
🔹 Don’t reset your wallet or move funds solely because of this shop breach.
The wider lesson for crypto security: self-custody protects control of assets, but it cannot eliminate risks created by customer databases and shipping records. Privacy is part of security, too.
#Keystone #CryptoSecurity #DataBreach #HardwareWallet #Bitcoin #CryptoNews
$NIL $ENA $REZ
{future}(REZUSDT)
{future}(ENAUSDT)
{future}(NILUSDT)
#KeystoneWebsiteBreachExposesBuyersShippingAddresses 🚨 Keystone Website Breach: A Reminder That Crypto Privacy Goes Beyond Private Keys
Keystone has disclosed a website breach that exposed customer names, contact details, shipping addresses and order information, including products purchased and prices paid. The company says it detected unauthorized access on October 20 and confirmed the data exposure on October 23.
According to Keystone, payment details, wallet passwords, private keys and recovery phrases were not compromised. That distinction matters: the incident does not automatically mean customers’ crypto funds are at risk. However, linking a real-world address to a hardware wallet purchase can create a serious privacy and security concern.
The biggest immediate risk may be targeted phishing. Attackers could use genuine order details to impersonate support teams, offer fake replacements or send convincing messages designed to steal recovery phrases.
Keystone says it has blocked the unauthorized access, fixed the vulnerability and started notifying affected customers. The number of people impacted and the full technical details have not yet been publicly established. Questions have also emerged about the company’s stated 180-day data-retention policy.
For users, the practical response is clear:
🔹 Never share your seed phrase or private keys.
🔹 Ignore unexpected refund, replacement or recovery offers.
🔹 Avoid links in unsolicited messages; contact support through the official website.
🔹 Don’t reset your wallet or move funds solely because of this shop breach.
The wider lesson for crypto security: self-custody protects control of assets, but it cannot eliminate risks created by customer databases and shipping records. Privacy is part of security, too.
#Keystone #CryptoSecurity #DataBreach #HardwareWallet #Bitcoin #CryptoNews
$NIL $ENA $REZ
237
·
--
Bullish
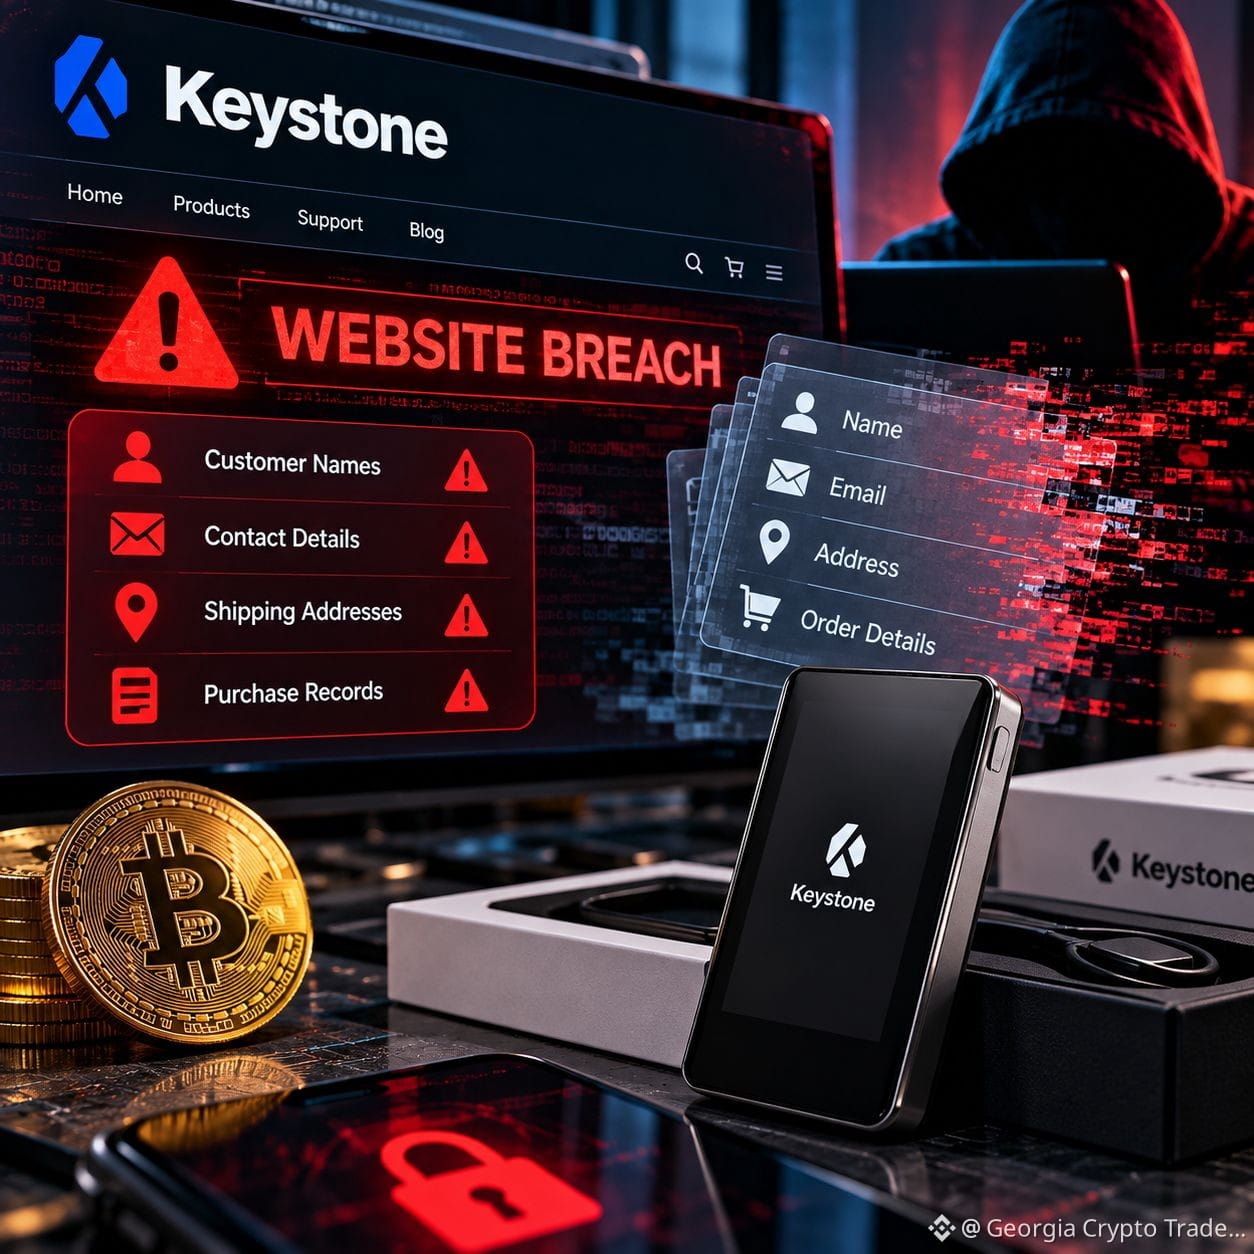
#KeystoneWebsiteBreachExposesBuyersShippingAddresses 🚨 #KeystoneBreach: A Reminder About Crypto Security
Keystone reportedly suffered a website breach exposing customer names, contact details, shipping addresses, and purchase records. The company says private keys, recovery phrases, passwords, and payment details were not compromised.
🔎 Why should crypto users care?
The main risk is targeted phishing. Attackers with real customer information can send convincing messages about refunds, replacement devices, or wallet security.
📊 Key takeaways:
• Data exposure can create risks even when wallet credentials remain safe.
• Never share your seed phrase or private keys.
• Verify unexpected messages through official channels.
• Avoid suspicious links and requests to move funds.
• Hardware wallets protect private keys, but cannot eliminate every security risk.
⚠️ Keystone says it addressed the vulnerability and is investigating the incident. The full scope remains unclear.
Trader’s perspective: this is a cybersecurity concern, not evidence of a confirmed blockchain exploit or stolen customer funds. Avoid confusing personal-data exposure with direct wallet compromise.
Crypto security requires more than protecting assets on-chain. Customer databases, shipping information, and account privacy also matter.
Should hardware wallet companies collect and retain less customer data?
#CryptoSecurity #Keystone #Bitcoin #SelfCustody #BinanceSquare
$BMT $BREV $DODO
{spot}(DODOUSDT)
{future}(BREVUSDT)
{future}(BMTUSDT)
#KeystoneWebsiteBreachExposesBuyersShippingAddresses 🚨 #KeystoneBreach: A Reminder About Crypto Security
Keystone reportedly suffered a website breach exposing customer names, contact details, shipping addresses, and purchase records. The company says private keys, recovery phrases, passwords, and payment details were not compromised.
🔎 Why should crypto users care?
The main risk is targeted phishing. Attackers with real customer information can send convincing messages about refunds, replacement devices, or wallet security.
📊 Key takeaways:
• Data exposure can create risks even when wallet credentials remain safe.
• Never share your seed phrase or private keys.
• Verify unexpected messages through official channels.
• Avoid suspicious links and requests to move funds.
• Hardware wallets protect private keys, but cannot eliminate every security risk.
⚠️ Keystone says it addressed the vulnerability and is investigating the incident. The full scope remains unclear.
Trader’s perspective: this is a cybersecurity concern, not evidence of a confirmed blockchain exploit or stolen customer funds. Avoid confusing personal-data exposure with direct wallet compromise.
Crypto security requires more than protecting assets on-chain. Customer databases, shipping information, and account privacy also matter.
Should hardware wallet companies collect and retain less customer data?
#CryptoSecurity #Keystone #Bitcoin #SelfCustody #BinanceSquare
$BMT $BREV $DODO
299
·
--
Bullish
#KeystoneWebsiteBreachExposesBuyersShippingAddresses 🚨 BREAKING KEYSTONE DATA BREACH EXPOSES HARDWARE WALLET BUYERS’ ADDRESSES!
🔐 A new security incident is raising serious questions about customer privacy in the crypto industry.
Keystone, a hardware wallet manufacturer, has confirmed that unauthorized access to its website exposed customer information, including shipping addresses and purchase records.
📌 WHAT WAS EXPOSED?
🔴 Customer names and contact details
🔴 Shipping addresses
🔴 Purchased products and order prices
✅ WHAT DOES KEYSTONE SAY WAS SAFE?
The company says payment card details, bank information, wallet passwords, private keys, and recovery phrases were not exposed in this incident.
⚠️ WHY THIS MATTERS
Even when crypto wallet keys remain secure, leaked personal information can create another risk: targeted phishing and impersonation scams.
Attackers may use real order details to make fake emails, calls, or replacement-device offers appear legitimate. Keystone says it has blocked unauthorized access, fixed the vulnerability, and started notifying affected customers.
🛡️ THE KEY TAKEAWAY
Crypto security is not just about protecting private keys. Protecting customer data is also essential for the safety and trust of the entire ecosystem.
Never share your recovery phrase or private keys with anyone, and treat unexpected wallet-security messages with caution.
💬 YOUR TAKE:
Should hardware wallet companies be held to stricter standards for customer data protection?
Share your thoughts below. 👇
#CryptoSecurity #Keystone #CryptoNews #Blockchain #BinanceSquare
$XAU $XAG $QNT
{future}(QNTUSDT)
{future}(XAGUSDT)
{future}(XAUUSDT)
#KeystoneWebsiteBreachExposesBuyersShippingAddresses 🚨 BREAKING KEYSTONE DATA BREACH EXPOSES HARDWARE WALLET BUYERS’ ADDRESSES!
🔐 A new security incident is raising serious questions about customer privacy in the crypto industry.
Keystone, a hardware wallet manufacturer, has confirmed that unauthorized access to its website exposed customer information, including shipping addresses and purchase records.
📌 WHAT WAS EXPOSED?
🔴 Customer names and contact details
🔴 Shipping addresses
🔴 Purchased products and order prices
✅ WHAT DOES KEYSTONE SAY WAS SAFE?
The company says payment card details, bank information, wallet passwords, private keys, and recovery phrases were not exposed in this incident.
⚠️ WHY THIS MATTERS
Even when crypto wallet keys remain secure, leaked personal information can create another risk: targeted phishing and impersonation scams.
Attackers may use real order details to make fake emails, calls, or replacement-device offers appear legitimate. Keystone says it has blocked unauthorized access, fixed the vulnerability, and started notifying affected customers.
🛡️ THE KEY TAKEAWAY
Crypto security is not just about protecting private keys. Protecting customer data is also essential for the safety and trust of the entire ecosystem.
Never share your recovery phrase or private keys with anyone, and treat unexpected wallet-security messages with caution.
💬 YOUR TAKE:
Should hardware wallet companies be held to stricter standards for customer data protection?
Share your thoughts below. 👇
#CryptoSecurity #Keystone #CryptoNews #Blockchain #BinanceSquare
$XAU $XAG $QNT
1
391
·
--
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
🚨 Data Breach at Hardware Wallet Giant Keystone! 📦🔓
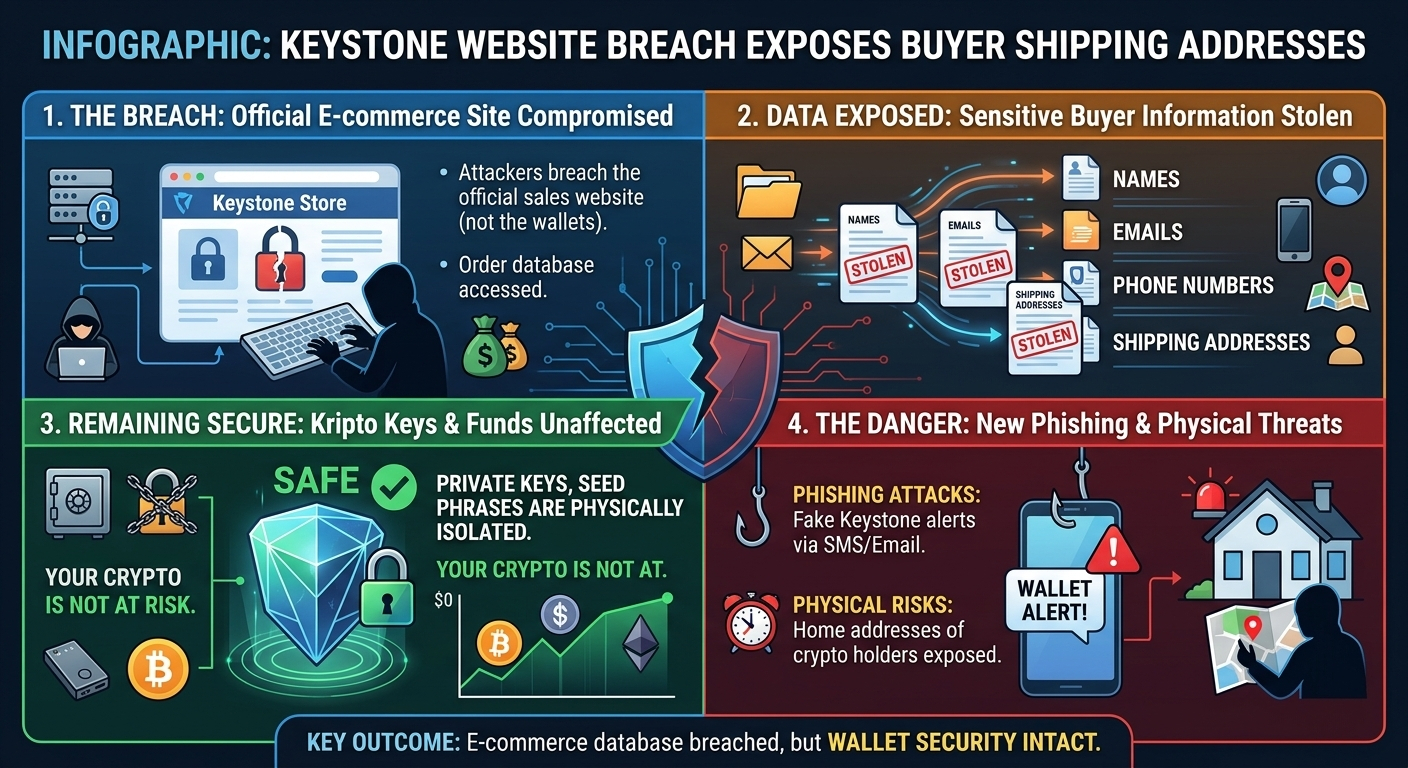
🌐 Shopping Website Hacked: The official sales website for Keystone hardware wallets, used to store crypto assets as securely as possible, was hit by a cyberattack. 💻📍 Confidential Information Exposed: As a result of the data breach, hackers obtained the names, email addresses, phone numbers, and home/work delivery addresses of customers who had shopped on the website. 🛑🔑 Crypto Safe: The attack affected only the e-commerce infrastructure. The cryptocurrencies in users’ wallets, private keys, and recovery phrases (seed phrases) were not harmed at all, as they are isolated in hardware. 🛡️
⚠️ What Major Threats Do Investors Face?
🎣 Phishing Attacks: Hackers may use the leaked email addresses and phone numbers to send fake panic-inducing messages such as, “Your wallet is at risk. Click this link immediately to update it.” 🎣🏠 Risk of Becoming a Physical Target: The exposure of home addresses belonging to cryptocurrency owners could leave them vulnerable to targeted attacks such as physical theft or extortion. 🗺️💣
🛡️ What Should Victims Do? (Urgent Security Measures)
🚫 Don’t Trust Messages: Never respond to any email or SMS that appears to come from Keystone or another organization and asks for your recovery phrase (seed phrase). 🙅♂️👁️ Enable Two-Factor Authentication: Maximize the security of your email and exchange accounts by enabling two-factor authentication (2FA). 🔐📦 Secure Delivery Locations: From now on, when ordering a hardware wallet, consider using parcel lockers or a fictitious name/work address instead of your home address. 📮
$BNB $SOL $ETH
{future}(ETHUSDT)
{future}(SOLUSDT)
{future}(BNBUSDT)
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
🚨 Data Breach at Hardware Wallet Giant Keystone! 📦🔓
🌐 Shopping Website Hacked: The official sales website for Keystone hardware wallets, used to store crypto assets as securely as possible, was hit by a cyberattack. 💻📍 Confidential Information Exposed: As a result of the data breach, hackers obtained the names, email addresses, phone numbers, and home/work delivery addresses of customers who had shopped on the website. 🛑🔑 Crypto Safe: The attack affected only the e-commerce infrastructure. The cryptocurrencies in users’ wallets, private keys, and recovery phrases (seed phrases) were not harmed at all, as they are isolated in hardware. 🛡️
⚠️ What Major Threats Do Investors Face?
🎣 Phishing Attacks: Hackers may use the leaked email addresses and phone numbers to send fake panic-inducing messages such as, “Your wallet is at risk. Click this link immediately to update it.” 🎣🏠 Risk of Becoming a Physical Target: The exposure of home addresses belonging to cryptocurrency owners could leave them vulnerable to targeted attacks such as physical theft or extortion. 🗺️💣
🛡️ What Should Victims Do? (Urgent Security Measures)
🚫 Don’t Trust Messages: Never respond to any email or SMS that appears to come from Keystone or another organization and asks for your recovery phrase (seed phrase). 🙅♂️👁️ Enable Two-Factor Authentication: Maximize the security of your email and exchange accounts by enabling two-factor authentication (2FA). 🔐📦 Secure Delivery Locations: From now on, when ordering a hardware wallet, consider using parcel lockers or a fictitious name/work address instead of your home address. 📮
$BNB $SOL $ETH
37

·
--
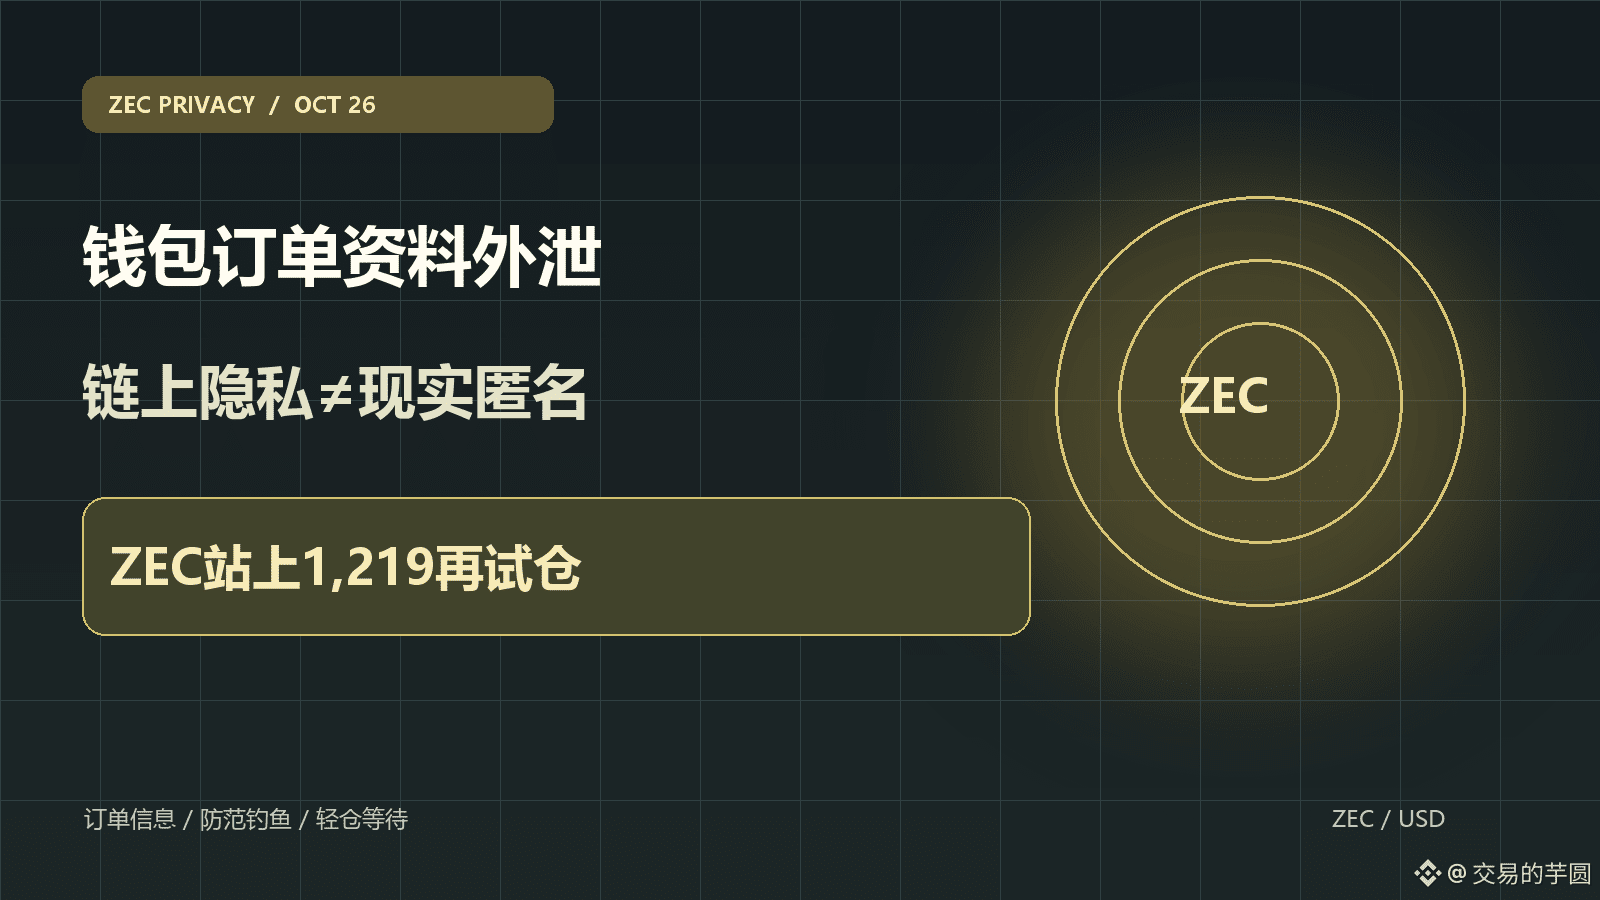
Keystone Order Data Leak|On-chain privacy on ZEC does not mean real-world anonymity|My choice is to guard against phishing first, then watch the price
I remain cautious about ZEC, and I do not interpret a customer data incident at a wallet manufacturer as evidence that the Zcash network was compromised. In an official statement on October 24, Keystone said it discovered unauthorized access to its website on October 20, and confirmed on the 23rd, after reviewing activity on its Shopify interface, that a third party had obtained customer shipping information. According to the company, the data involved names, contact details, shipping addresses, and order items and prices; bank card details, recovery phrases, private keys, and wallet passwords were not included in the data in question. The company said it had blocked the access, addressed the vulnerability, and notified affected customers. A full investigation report has yet to be released. At this point, there is no information on the number of people affected, the specific method of intrusion, or the results of independent forensic analysis. So I will describe “keys were not leaked” only as the company’s disclosure, not as a conclusion verified by an external party.
The real reminder this trending topic offers about ZEC is the boundary of privacy. Zcash shielded transactions can protect some on-chain information, but if real-world purchase records link a person’s name and address to ownership of a hardware wallet, phishers can still impersonate customer support and use “refunds,” “replacements,” or “address corrections” to trick users into handing over their recovery phrases. Even if on-chain balances were not directly exposed by this incident, the risk of targeted social engineering increases. ZEC holders should verify notifications by manually entering the official website address, avoid unexpected links in texts or emails, never share their recovery phrase with anyone, and never enter it into a device of unknown origin. Security precautions and trading decisions should be kept separate; panic transfers can create new losses of their own.
At the time of writing, ZEC/USD on Kraken was around $1,203, with a UTC open of $1,212.09, an intraday high of $1,218.76, and a low of $1,176.53. The price was below the open, but there is no evidence that this decline was caused by Keystone’s statement; ZEC is also affected by overall risk appetite, liquidity, and upcoming project events. The upper level of $1,219 is where I’m watching to see whether buyers can regain control of the intraday range, while $1,176 is the risk boundary. If the price breaks above the upper level but quickly falls back below it, the bullish outlook is invalidated. If it loses the lower level, I won’t catch a falling knife just because of the “privacy narrative.” The trending hashtag #KeystoneWebsiteBreachExposesBuyersShippingAddresses describes order data, not an incident involving the ZEC mainnet.
If I were trading this myself: I would stay out for now. I would only set up a plan for a small spot long position in the direction of the trend, capped at 3% of total capital, with no leverage. I would enter in two tranches only if the hourly candle closes above $1,219 and the following hour’s retest holds above $1,210. The first target is $1,245, where I would sell half; the second target is $1,275, where I would raise the protective stop on the remaining position. I would set the initial stop at $1,188. If the price closes back below $1,210 after entry, or if a formal follow-up investigation into the security incident reveals risks beyond what has been disclosed so far, I would close the position early. Without an entry trigger, I would continue to wait and would never present a trade plan as a profitable trade already made.
Sources: Keystone’s official statement of October 24 and subsequent investigation updates, Zcash Foundation materials, and live Kraken ZEC/USD prices. #KeystoneWebsiteBreachExposesBuyersShippingAddresses #ZEC
The above is solely my personal market commentary and does not constitute investment advice.
5

#KeystoneWebsiteBreachExposesBuyersShippingAddresses
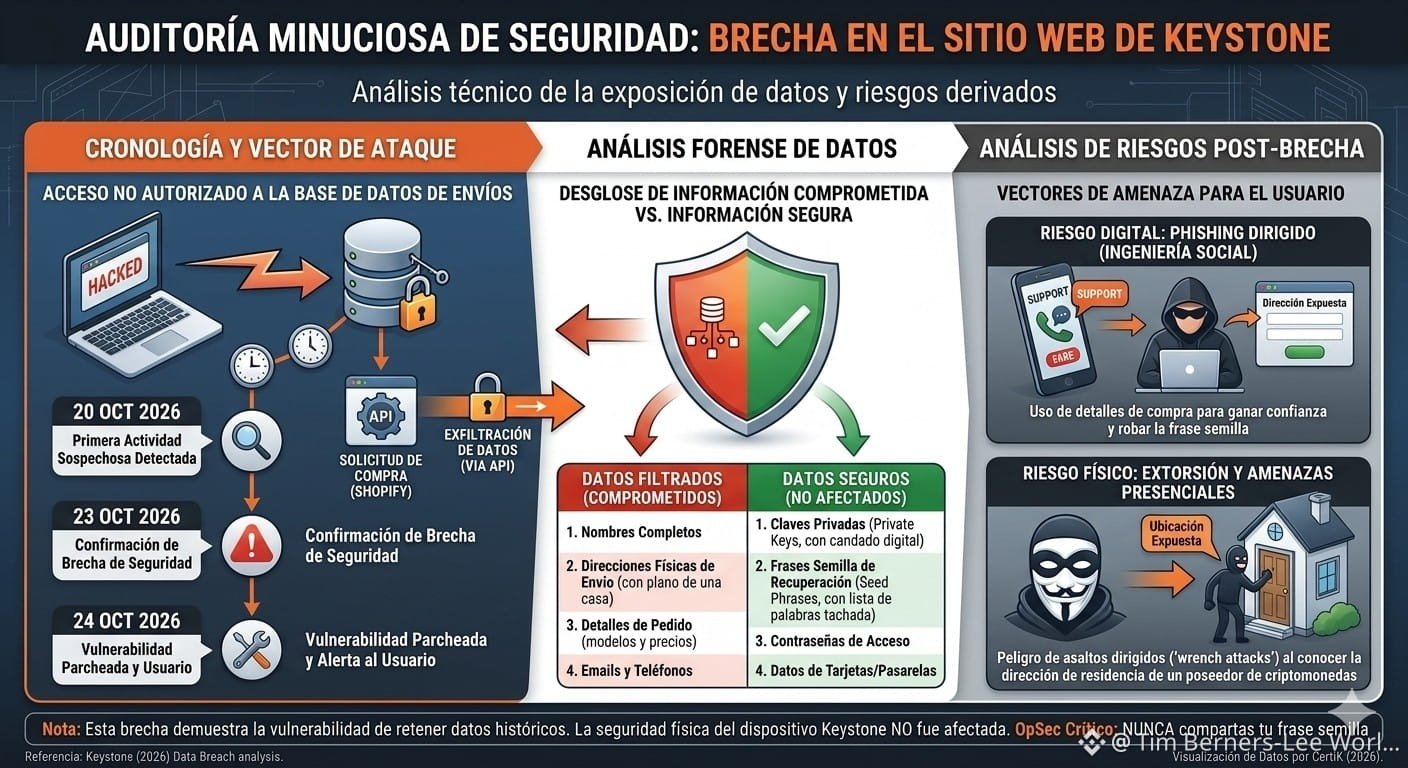
⚠️The Great Controversy: Data Retention Under Scrutiny
⚠️Exfiltrated (Compromised) Data Secure Data (NOT Affected)
Buyers’ full names. Private keys.
Physical shipping and home delivery addresses. Seed phrases.
Precise order details (models purchased and prices). Passwords for accessing wallet apps.
Contact information (email addresses and phone numbers). Bank details, credit cards, or payment gateways.
⚠️The incident has sparked a wave of outrage and distrust on social media over the company’s privacy policies. In 2023, Keystone publicly announced that it would reduce its data retention period to just 180 days after purchase, a measure specifically designed to mitigate the impact of large-scale hacks (such as the one its competitor Ledger suffered in the past).
⚠️However, multiple customers reported on platform X that they had received the vulnerability notification despite having purchased their wallets in 2024 or earlier, empirically demonstrating that the company had not deleted historical records as promised. This has opened a debate about the accuracy of hardware wallet providers’ data storage policies. $BTC $ETH
{spot}(ETHUSDT)
{spot}(BTCUSDT)
#KeystoneWebsiteBreachExposesBuyersShippingAddresses
⚠️The Great Controversy: Data Retention Under Scrutiny
⚠️Exfiltrated (Compromised) Data Secure Data (NOT Affected)
Buyers’ full names. Private keys.
Physical shipping and home delivery addresses. Seed phrases.
Precise order details (models purchased and prices). Passwords for accessing wallet apps.
Contact information (email addresses and phone numbers). Bank details, credit cards, or payment gateways.
⚠️The incident has sparked a wave of outrage and distrust on social media over the company’s privacy policies. In 2023, Keystone publicly announced that it would reduce its data retention period to just 180 days after purchase, a measure specifically designed to mitigate the impact of large-scale hacks (such as the one its competitor Ledger suffered in the past).
⚠️However, multiple customers reported on platform X that they had received the vulnerability notification despite having purchased their wallets in 2024 or earlier, empirically demonstrating that the company had not deleted historical records as promised. This has opened a debate about the accuracy of hardware wallet providers’ data storage policies. $BTC $ETH
ABO3ZAM:
طرح ممتاز وضروري يا غالي، خصوصاً في وقت نحتاج فيه نحمي بياناتنا مثل ما نؤمن أرباحنا عند أول مقاومة. ديروا بالكم ولا تخلون السيولة عرضة للمخاطر. 🎯
4
129
·
--
Bearish
🚨 $TUT IS STRUGGLING TO RECOVER — ANOTHER LEG DOWN COMING? 📉🔥
TUT keeps trading below both key EMAs on the 1H and 4H charts.
Bulls aren't showing much strength, and sellers still have the advantage. 👀
But chasing the dump? That's how traders get trapped.
🔴 SHORT $TUT/USDT SETUP
🎯 Entry: $0.0167217 – $0.0167783
✅ TP1: $0.0162366 (-3.1%)
✅ TP2: $0.0158944 (-5.1%)
✅ TP3: $0.0153810 (-8.2%)
🛑 Stop Loss: $0.0174345 (+4.1%)
🔥 THE GAME PLAN:
Wait for a bounce into the entry zone.
📉 Take 50% profit at TP1.
📉 Close another 25% at TP2.
📉 Let the remaining 25% run toward TP3.
🔒 Move SL to breakeven after TP1.
💥 WHAT COULD HAPPEN NEXT?
🐻 BEARISH: Price rejects the entry zone → Selling accelerates → $0.01538 comes into play.
🐂 BULLISH: Buyers reclaim resistance → Shorts get squeezed → The bearish setup weakens.
⚠️ THE REAL TRAP?
Shorting too late, right before a relief bounce.
👇 WHAT'S YOUR MOVE?
SHORT THE BOUNCE OR WAIT FOR A CLEAN BREAKDOWN? 👀🔥
{future}(TUTUSDT)
#BinancePick #EarningsSeason #ArgentineCourtDismissesLIBRACaseAgainstMilei #SKHynixReportedlyPlansSpecialDividendFromKioxiaStakeSale #KeystoneWebsiteBreachExposesBuyersShippingAddresses
🚨 $TUT IS STRUGGLING TO RECOVER — ANOTHER LEG DOWN COMING? 📉🔥
TUT keeps trading below both key EMAs on the 1H and 4H charts.
Bulls aren't showing much strength, and sellers still have the advantage. 👀
But chasing the dump? That's how traders get trapped.
🔴 SHORT $TUT /USDT SETUP
🎯 Entry: $0.0167217 – $0.0167783
✅ TP1: $0.0162366 (-3.1%)
✅ TP2: $0.0158944 (-5.1%)
✅ TP3: $0.0153810 (-8.2%)
🛑 Stop Loss: $0.0174345 (+4.1%)
🔥 THE GAME PLAN:
Wait for a bounce into the entry zone.
📉 Take 50% profit at TP1.
📉 Close another 25% at TP2.
📉 Let the remaining 25% run toward TP3.
🔒 Move SL to breakeven after TP1.
💥 WHAT COULD HAPPEN NEXT?
🐻 BEARISH: Price rejects the entry zone → Selling accelerates → $0.01538 comes into play.
🐂 BULLISH: Buyers reclaim resistance → Shorts get squeezed → The bearish setup weakens.
⚠️ THE REAL TRAP?
Shorting too late, right before a relief bounce.
👇 WHAT'S YOUR MOVE?
SHORT THE BOUNCE OR WAIT FOR A CLEAN BREAKDOWN? 👀🔥
#BinancePick #EarningsSeason #ArgentineCourtDismissesLIBRACaseAgainstMilei #SKHynixReportedlyPlansSpecialDividendFromKioxiaStakeSale #KeystoneWebsiteBreachExposesBuyersShippingAddresses
Tim Berners-Lee WorldWideWeb The World Archie EFF ARPANET:
@BiBi Fact Check this content
1
283
·
--
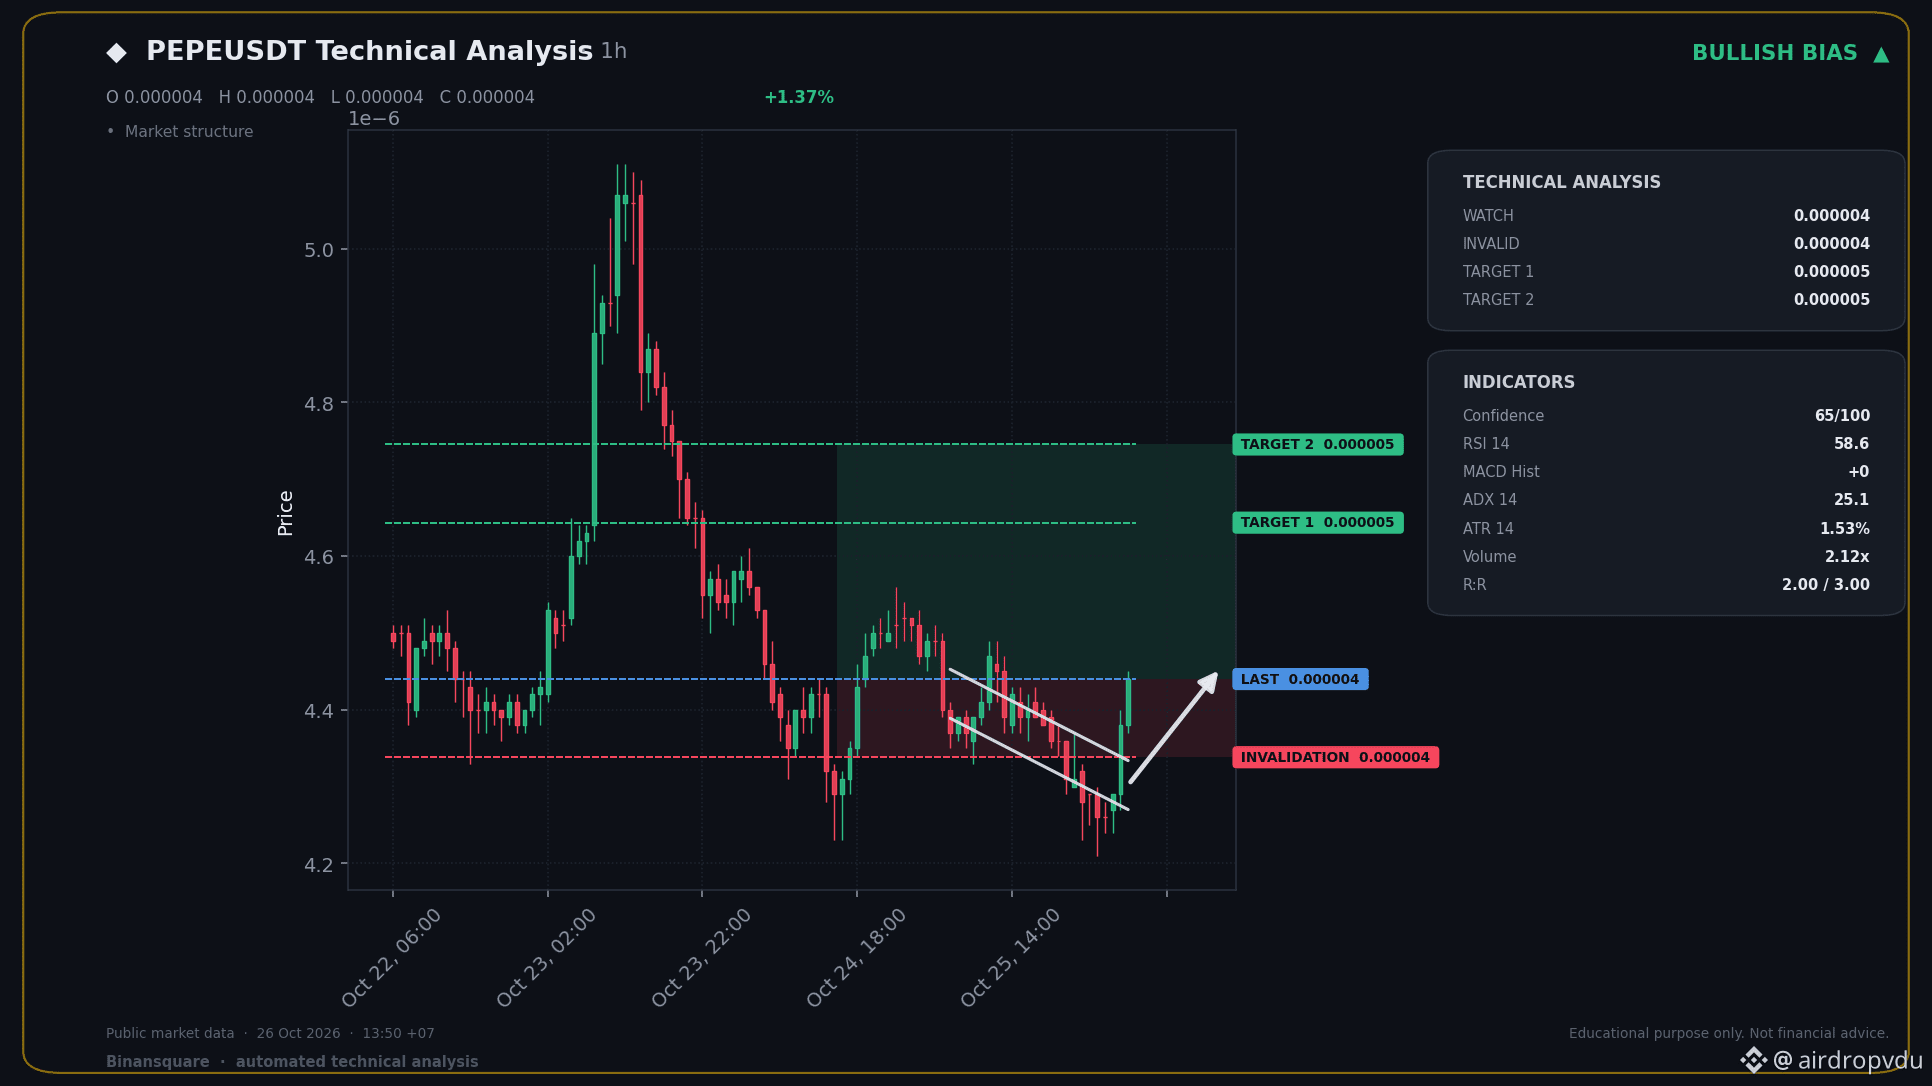
📈 BIG LONG NOW - PEPEUSDT
📍 KEY LEVELS
Entry: 0.000004
🛑 SL: 0.000004
🎯 TP1: 0.000005
🎯 TP2: 0.000005
This dip's already snapping back with momentum shifting back to bullish. RSI's got room left before hitting overbought territory.
This signal was generated automatically from technical indicators. It does not guarantee profit and is not investment advice. Always manage your own risk and DYOR.
$PEPE
#ElectrumWalletBugLetRogueServersStealFunds #KeystoneWebsiteBreachExposesBuyersShippingAddresses
1
146
·
--
Bearish
🚨 $HEMI KEEPS BLEEDING — ARE BEARS ABOUT TO PUSH IT EVEN LOWER? 📉🔥
HEMI is stuck in a bearish trend across multiple timeframes, and buyers are struggling to fight back.
Another drop could be coming, but chasing red candles is risky. 👀
🔴 SHORT $HEMI/USDT SETUP
🎯 Entry: $0.0044797 – $0.0044943
✅ TP1: $0.0043528 (-3.0%)
✅ TP2: $0.0042634 (-5.0%)
✅ TP3: $0.0041292 (-8.0%)
🛑 Stop Loss: $0.0046659 (+4.0%)
🔥 THE PLAN:
Wait for price to bounce into the entry zone. No chasing the dump.
📉 Close 50% at TP1.
📉 Take another 25% at TP2.
📉 Let the final 25% run toward TP3.
🔒 Move SL to breakeven after TP1.
💥 HERE'S WHAT MATTERS:
🐻 BEARISH: Price rejects the entry zone → Sellers regain control → $0.00413 becomes the next downside target.
🐂 BULLISH: Buyers reclaim resistance → Short squeeze risk increases → A break above $0.0046659 invalidates the setup.
⚠️ THE BIGGEST TRAP?
Shorting after a big drop, only to get caught in a sudden relief rally.
👇 WHAT'S YOUR CALL?
SHORT $HEMI NOW OR WAIT FOR THE BOUNCE? 👀🔥
{future}(HEMIUSDT)
#BinancePick #EarningsSeason #ArgentineCourtDismissesLIBRACaseAgainstMilei #SKHynixReportedlyPlansSpecialDividendFromKioxiaStakeSale #KeystoneWebsiteBreachExposesBuyersShippingAddresses
🚨 $HEMI KEEPS BLEEDING — ARE BEARS ABOUT TO PUSH IT EVEN LOWER? 📉🔥
HEMI is stuck in a bearish trend across multiple timeframes, and buyers are struggling to fight back.
Another drop could be coming, but chasing red candles is risky. 👀
🔴 SHORT $HEMI /USDT SETUP
🎯 Entry: $0.0044797 – $0.0044943
✅ TP1: $0.0043528 (-3.0%)
✅ TP2: $0.0042634 (-5.0%)
✅ TP3: $0.0041292 (-8.0%)
🛑 Stop Loss: $0.0046659 (+4.0%)
🔥 THE PLAN:
Wait for price to bounce into the entry zone. No chasing the dump.
📉 Close 50% at TP1.
📉 Take another 25% at TP2.
📉 Let the final 25% run toward TP3.
🔒 Move SL to breakeven after TP1.
💥 HERE'S WHAT MATTERS:
🐻 BEARISH: Price rejects the entry zone → Sellers regain control → $0.00413 becomes the next downside target.
🐂 BULLISH: Buyers reclaim resistance → Short squeeze risk increases → A break above $0.0046659 invalidates the setup.
⚠️ THE BIGGEST TRAP?
Shorting after a big drop, only to get caught in a sudden relief rally.
👇 WHAT'S YOUR CALL?
SHORT $HEMI NOW OR WAIT FOR THE BOUNCE? 👀🔥
#BinancePick #EarningsSeason #ArgentineCourtDismissesLIBRACaseAgainstMilei #SKHynixReportedlyPlansSpecialDividendFromKioxiaStakeSale #KeystoneWebsiteBreachExposesBuyersShippingAddresses
ABO3ZAM:
تحليل موفق يا كيم، لكن انتبه من الديليات اللي تصير بعد الكسر، يفضل تنتظر إغلاق شمعة الأربع ساعات تحت الدعم عشان تتأكد إن السيولة فعلاً خرجت من السهم. 🎯
2
1
211
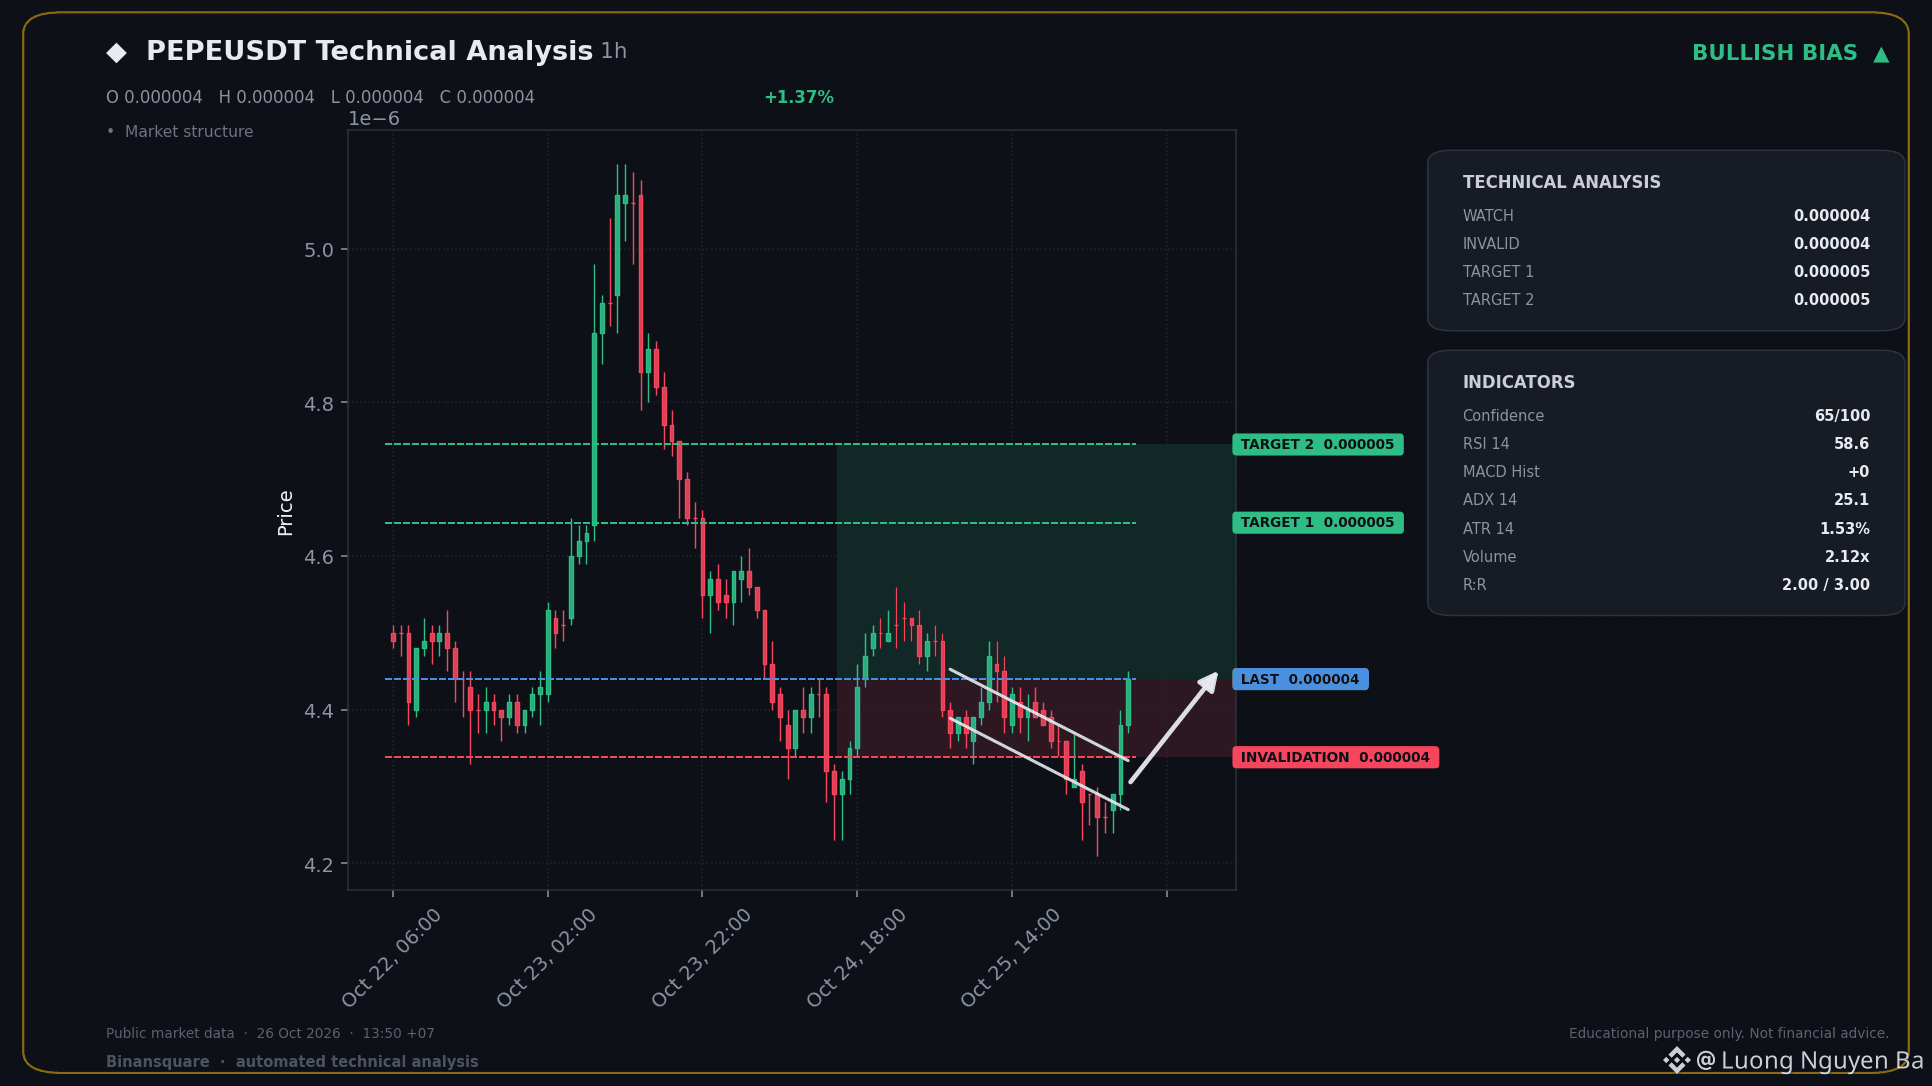
📈 BIG LONG NOW - PEPEUSDT
📍 KEY LEVELS
Entry: 0.000004
🛑 SL: 0.000004
🎯 TP1: 0.000005
🎯 TP2: 0.000005
This dip's already snapping back with momentum shifting back to bullish. RSI's got room left before hitting overbought territory.
This signal was generated automatically from technical indicators. It does not guarantee profit and is not investment advice. Always manage your own risk and DYOR.
$PEPE
#ElectrumWalletBugLetRogueServersStealFunds #KeystoneWebsiteBreachExposesBuyersShippingAddresses
1
143
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#BinancePick
2.8M views
146,853 Discussing
2
#EarningsSeason
5.1M views
25,096 Discussing
3
#AnthropicTTMRevenueGrewAbout1200%
328 views
58 Discussing
4
#AnthropicS1ExpectedToday
2,042 views
85 Discussing
5
#SouthKoreaReportedlyWeighsFourthCryptoTaxDelay
10,595 views
256 Discussing
6
#FranklinTempletonFilesForTwoDividendToBitcoinETFs
17,254 views
379 Discussing
7
#StrategyMSTRSurpassesNasdaqInMarketCap
14,056 views
298 Discussing
8
#CanadaProposesStablecoinRedemptionWithin3BusinessDays
651 views
30 Discussing
9
#ElectrumWalletBugLetRogueServersStealFunds
18,808 views
397 Discussing
10
#ArgentineCourtDismissesLIBRACaseAgainstMilei
29,445 views
480 Discussing