
#cosmosevm
cosmosevm
4,391 views
18 Discussing
Hot
Latest
·
--
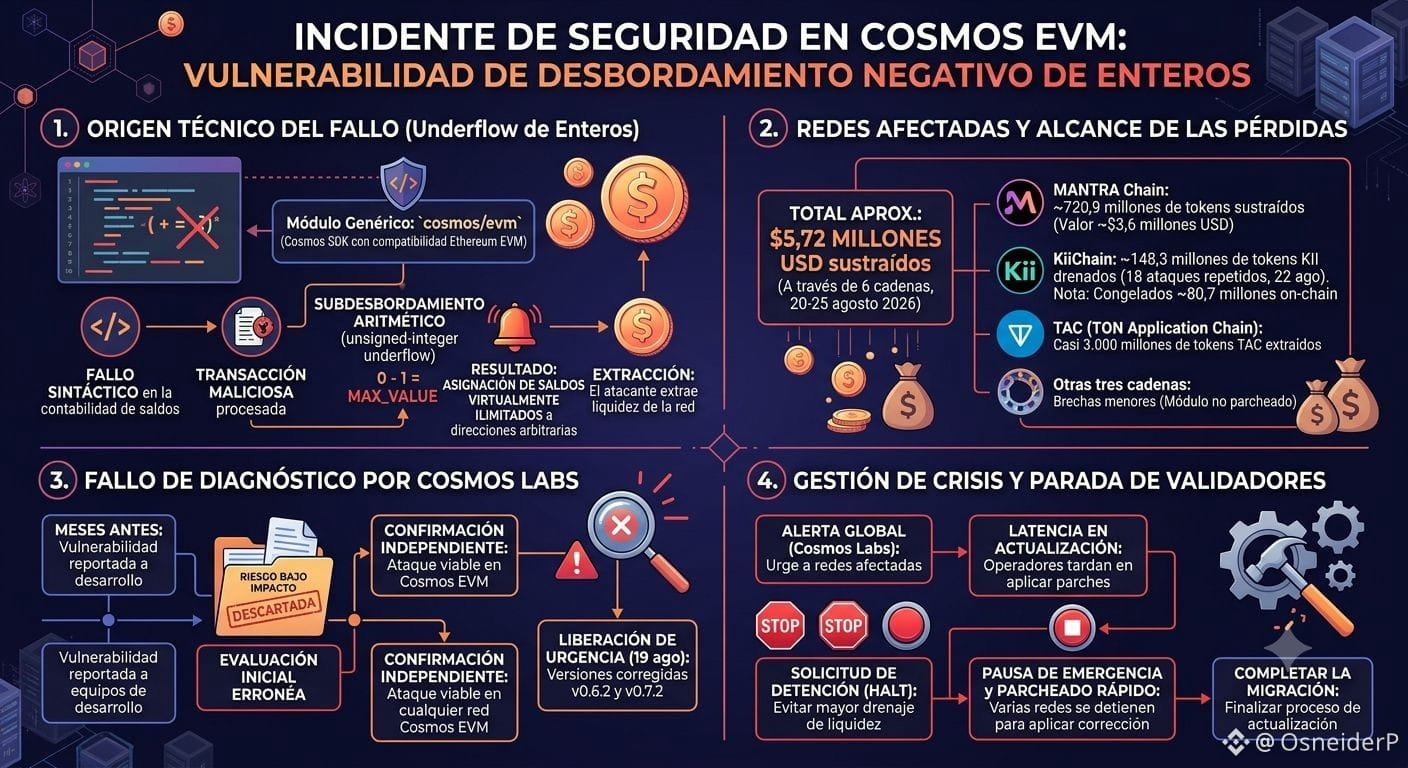
🚨 An error in Cosmos EVM drains 5.7 million dollars across six chains 🚨
The exploit in Cosmos EVM highlights the structural risks associated with reusing shared code modules in multichain architectures. Although the fix through patches v0.6.2/v0.7.2 and the coordinated shutdown of validators halted the spread of the attack, the initial misjudgment by the auditing teams underscores the need to strengthen vulnerability disclosure protocols and the speed of updates on decentralized networks.
#CosmosEVM #CryptoNewss #BinanceSquare
🚨 An error in Cosmos EVM drains 5.7 million dollars across six chains 🚨
The exploit in Cosmos EVM highlights the structural risks associated with reusing shared code modules in multichain architectures. Although the fix through patches v0.6.2/v0.7.2 and the coordinated shutdown of validators halted the spread of the attack, the initial misjudgment by the auditing teams underscores the need to strengthen vulnerability disclosure protocols and the speed of updates on decentralized networks.
#CosmosEVM #CryptoNewss #BinanceSquare
The exploit in Cosmos EVM highlights the structural risks associated with reusing shared code modules in multichain architectures. Although the fix through patches v0.6.2/v0.7.2 and the coordinated shutdown of validators halted the spread of the attack, the initial misjudgment by the auditing teams underscores the need to strengthen vulnerability disclosure protocols and the speed of updates on decentralized networks.
#CosmosEVM #CryptoNewss #BinanceSquare
275
·
--
Verified
🚨 MANTRA has frozen its blockchain following a Cosmos EVM incident, with validators instructed to keep mainnet nodes offline pending an official restart. The token has hit a new low amid the disruption. This suspension raises concerns about network reliability and could pressure short-term sentiment until operations resume. Is the freeze a necessary safeguard—or a sign of deeper instability? #MANTRA #CosmosEVM
🚨 MANTRA has frozen its blockchain following a Cosmos EVM incident, with validators instructed to keep mainnet nodes offline pending an official restart. The token has hit a new low amid the disruption. This suspension raises concerns about network reliability and could pressure short-term sentiment until operations resume. Is the freeze a necessary safeguard—or a sign of deeper instability? #MANTRA #CosmosEVM
319
·
--
🚨 Cosmos EVM bug just cost the ecosystem $5.7M — here’s what happened
A critical integer underflow flaw in the Cosmos EVM module let attackers manipulate account balances and drain funds without minting new tokens — no exploit-detection red flags, just quiet balance manipulation.
📅 Timeline:
• Bug reported via bounty program → Cosmos Labs applied a silent fix in May, no public advisory
• An independent researcher later found it affected ALL Cosmos EVM chains
• Patch released Aug 19
• Attackers struck ~20 hours later, Aug 20–25
• Total damage: ~$5.7M across six blockchains
💥 Hit hardest: MANTRA (~$3.6M), plus TAC and KiiChain among others
🛠️ The response: Cosmos Labs scrambled to coordinate with ~40 chains, helping 13 patch or halt operations in time. The rest weren’t so lucky.
🔍 The real lesson here isn’t just “another exploit” — it’s shared software risk.
When dozens of chains run the same underlying module, one silent, underestimated bug becomes a coordinated attack surface across the entire ecosystem. Cosmos Labs has said it’s overhauling its vulnerability disclosure process.
If you’re holding or building on any Cosmos EVM chain, this is worth reading in full — communication gaps between “we patched it quietly” and “here’s a public advisory” are exactly what attackers wait for.
⚠️ Not financial advice. Always verify chain-specific security updates directly from official sources.
#Cosmos #CosmosEVM #CryptoSecurity #DeFiHack #MANTRA $ATOM
{spot}(ATOMUSDT)
{spot}(MANTRAUSDT)
🚨 Cosmos EVM bug just cost the ecosystem $5.7M — here’s what happened
A critical integer underflow flaw in the Cosmos EVM module let attackers manipulate account balances and drain funds without minting new tokens — no exploit-detection red flags, just quiet balance manipulation.
📅 Timeline:
• Bug reported via bounty program → Cosmos Labs applied a silent fix in May, no public advisory
• An independent researcher later found it affected ALL Cosmos EVM chains
• Patch released Aug 19
• Attackers struck ~20 hours later, Aug 20–25
• Total damage: ~$5.7M across six blockchains
💥 Hit hardest: MANTRA (~$3.6M), plus TAC and KiiChain among others
🛠️ The response: Cosmos Labs scrambled to coordinate with ~40 chains, helping 13 patch or halt operations in time. The rest weren’t so lucky.
🔍 The real lesson here isn’t just “another exploit” — it’s shared software risk.
When dozens of chains run the same underlying module, one silent, underestimated bug becomes a coordinated attack surface across the entire ecosystem. Cosmos Labs has said it’s overhauling its vulnerability disclosure process.
If you’re holding or building on any Cosmos EVM chain, this is worth reading in full — communication gaps between “we patched it quietly” and “here’s a public advisory” are exactly what attackers wait for.
⚠️ Not financial advice. Always verify chain-specific security updates directly from official sources.
#Cosmos #CosmosEVM #CryptoSecurity #DeFiHack #MANTRA $ATOM
A critical integer underflow flaw in the Cosmos EVM module let attackers manipulate account balances and drain funds without minting new tokens — no exploit-detection red flags, just quiet balance manipulation.
📅 Timeline:
• Bug reported via bounty program → Cosmos Labs applied a silent fix in May, no public advisory
• An independent researcher later found it affected ALL Cosmos EVM chains
• Patch released Aug 19
• Attackers struck ~20 hours later, Aug 20–25
• Total damage: ~$5.7M across six blockchains
💥 Hit hardest: MANTRA (~$3.6M), plus TAC and KiiChain among others
🛠️ The response: Cosmos Labs scrambled to coordinate with ~40 chains, helping 13 patch or halt operations in time. The rest weren’t so lucky.
🔍 The real lesson here isn’t just “another exploit” — it’s shared software risk.
When dozens of chains run the same underlying module, one silent, underestimated bug becomes a coordinated attack surface across the entire ecosystem. Cosmos Labs has said it’s overhauling its vulnerability disclosure process.
If you’re holding or building on any Cosmos EVM chain, this is worth reading in full — communication gaps between “we patched it quietly” and “here’s a public advisory” are exactly what attackers wait for.
⚠️ Not financial advice. Always verify chain-specific security updates directly from official sources.
#Cosmos #CosmosEVM #CryptoSecurity #DeFiHack #MANTRA $ATOM
265

🔎 NES Hack & Migration — What I Found
I’ve been investigating the recent NES (Nesa) incident and found some interesting on-chain evidence.
On August 24, Nesa reported malicious activity involving an L1 vulnerability and said they were working on a fix and recovery.
I found:
🔴 Old side: ~62.904M NES was sent to the Null Address, effectively removing the tokens.
🟢 New Ethereum contract: ~62.904M NES was minted from the Null Address → Gnosis Safe.
The amounts are extremely close, and that Gnosis Safe now holds around 62.9M NES.
This makes the migration/recovery theory very interesting:
Exploit → liquidity isolated → old supply removed → new Ethereum contract → corresponding NES created → Gnosis Safe → new liquidity rebuilt → exchanges migrate → trading resumes.
I’m also seeing new NES/USDT & NES/USDC pools and activity through Uniswap V4, LI.FI and DEX aggregators, showing that the new ecosystem is being rebuilt.
⚠️ However, I’m not saying everything is fixed yet.
The biggest confirmation will be when users can:
BUY → SELL → DEPOSIT → WITHDRAW
normally again, with healthy liquidity.
For now, the matching ~62.9M NES movements are the biggest clue I’ve found.
I’ll keep watching the wallets, liquidity and migration activity.
DYOR. Not financial advice.
#NES #Nesa #Ethereum #DeFi @CZ #CosmosEVM
🔎 NES Hack & Migration — What I Found
I’ve been investigating the recent NES (Nesa) incident and found some interesting on-chain evidence.
On August 24, Nesa reported malicious activity involving an L1 vulnerability and said they were working on a fix and recovery.
I found:
🔴 Old side: ~62.904M NES was sent to the Null Address, effectively removing the tokens.
🟢 New Ethereum contract: ~62.904M NES was minted from the Null Address → Gnosis Safe.
The amounts are extremely close, and that Gnosis Safe now holds around 62.9M NES.
This makes the migration/recovery theory very interesting:
Exploit → liquidity isolated → old supply removed → new Ethereum contract → corresponding NES created → Gnosis Safe → new liquidity rebuilt → exchanges migrate → trading resumes.
I’m also seeing new NES/USDT & NES/USDC pools and activity through Uniswap V4, LI.FI and DEX aggregators, showing that the new ecosystem is being rebuilt.
⚠️ However, I’m not saying everything is fixed yet.
The biggest confirmation will be when users can:
BUY → SELL → DEPOSIT → WITHDRAW
normally again, with healthy liquidity.
For now, the matching ~62.9M NES movements are the biggest clue I’ve found.
I’ll keep watching the wallets, liquidity and migration activity.
DYOR. Not financial advice.
#NES #Nesa #Ethereum #DeFi @CZ #CosmosEVM
I’ve been investigating the recent NES (Nesa) incident and found some interesting on-chain evidence.
On August 24, Nesa reported malicious activity involving an L1 vulnerability and said they were working on a fix and recovery.
I found:
🔴 Old side: ~62.904M NES was sent to the Null Address, effectively removing the tokens.
🟢 New Ethereum contract: ~62.904M NES was minted from the Null Address → Gnosis Safe.
The amounts are extremely close, and that Gnosis Safe now holds around 62.9M NES.
This makes the migration/recovery theory very interesting:
Exploit → liquidity isolated → old supply removed → new Ethereum contract → corresponding NES created → Gnosis Safe → new liquidity rebuilt → exchanges migrate → trading resumes.
I’m also seeing new NES/USDT & NES/USDC pools and activity through Uniswap V4, LI.FI and DEX aggregators, showing that the new ecosystem is being rebuilt.
⚠️ However, I’m not saying everything is fixed yet.
The biggest confirmation will be when users can:
BUY → SELL → DEPOSIT → WITHDRAW
normally again, with healthy liquidity.
For now, the matching ~62.9M NES movements are the biggest clue I’ve found.
I’ll keep watching the wallets, liquidity and migration activity.
DYOR. Not financial advice.
#NES #Nesa #Ethereum #DeFi @CZ #CosmosEVM
2
9
2.2k
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#CardanoAddedToX402KitForADAPayments
1,630 views
137 Discussing
2
#XRPRises8%
9,594 views
474 Discussing
3
#AMDHits$1TrillionMarketCap
227 views
23 Discussing
4
#BitcoinSpotETFs$999MNetInflow
586 views
37 Discussing
5
#AppleGoogleSeekStablecoinTokenizedDepositTalent
6,297 views
359 Discussing
6
#NvidiaToBuyAnother$1.5BSBEnergySharesPreIPO
1,256 views
32 Discussing
7
#AgoraGetsPreliminaryOCCApprovalForTrustBank
3,795 views
175 Discussing
8
#NEARRisesNearly80%InAWeek
73,246 views
1,327 Discussing
9
#MultiversXPlansHardForkRecovery
57,599 views
1,002 Discussing
10
#CircleLaunchesInstitutionalBTCBackedBorrowing
50,450 views
987 Discussing