
C Y R O N
5.5k Posts
C Y R O N
Report
Block User
Binance KOL & Web3 Mentor
XPL Holder
Frequent Trader
4.8 Years
291 Following
18.2K+ Followers
18.0K+ Liked
Posts
All
Quotes
Videos
Live
·
--
Bullish
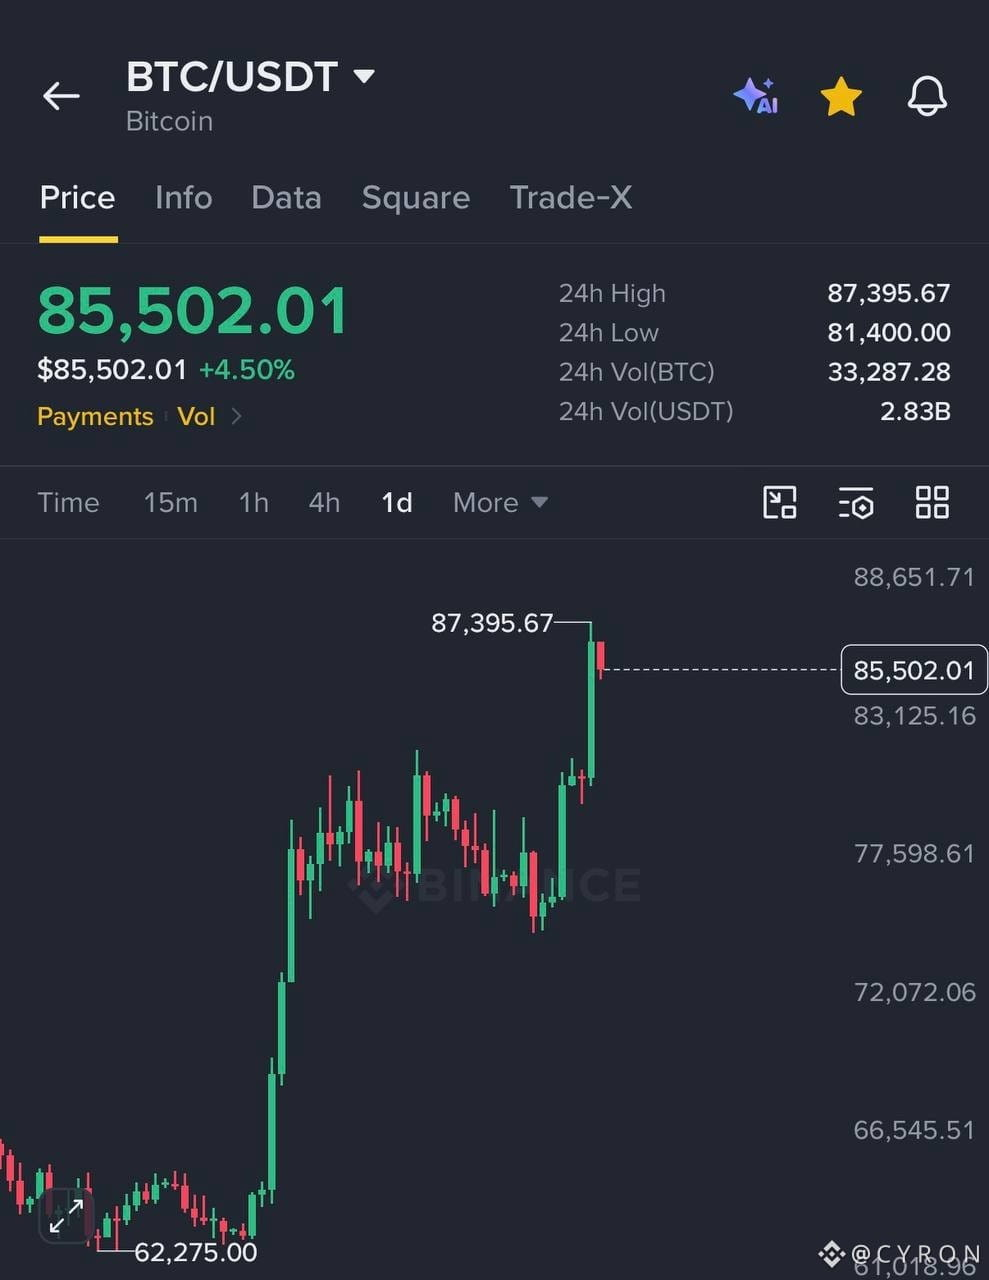
$BTC just closed above $86,000 for the first time in nearly 8 months.
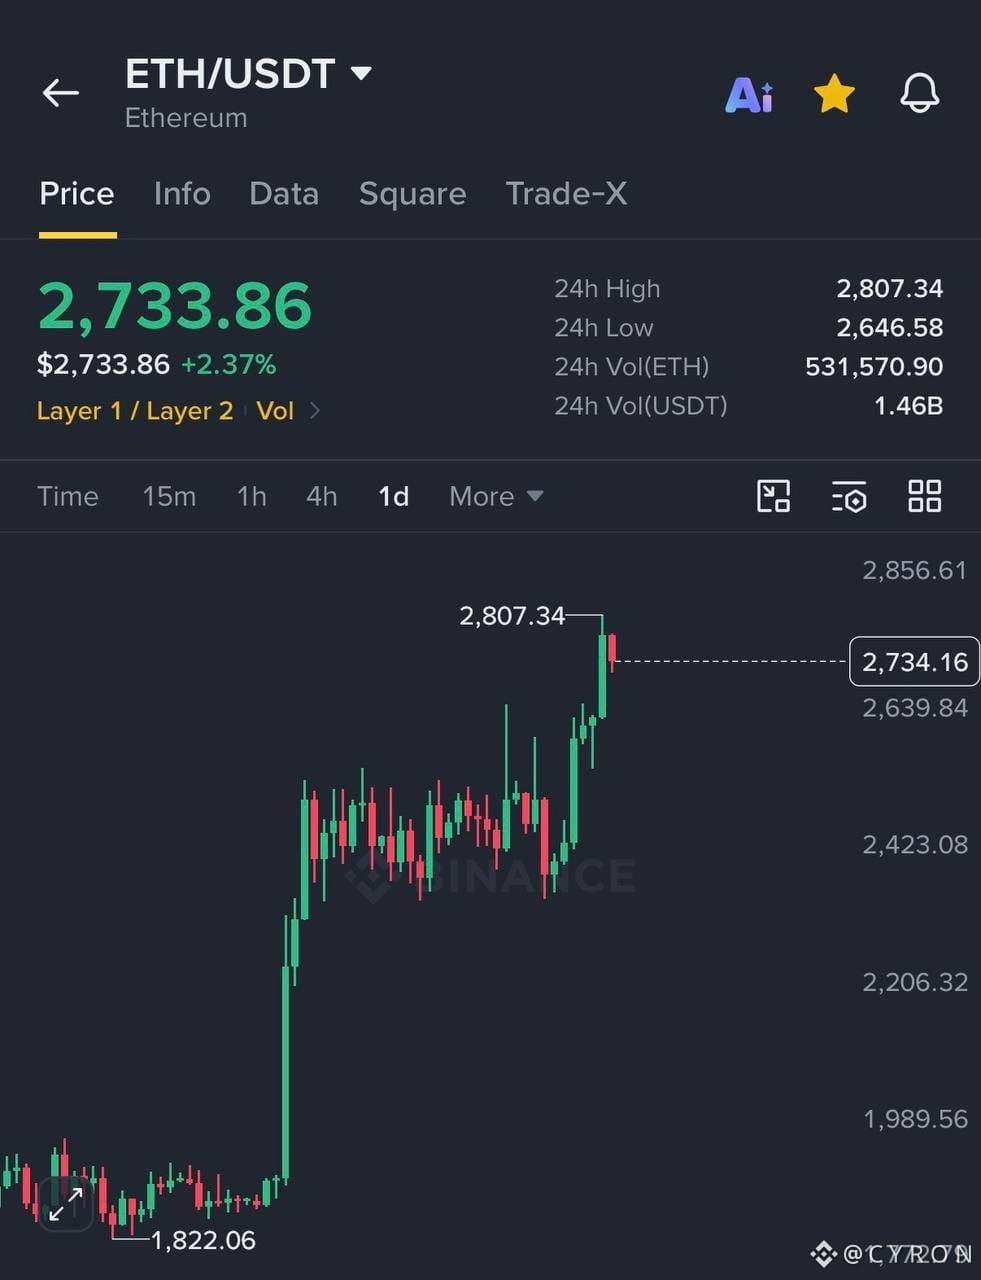
$ETH is back above $2,700 too.
BTC is now roughly $7.3K above its 50-week MA, a pretty notable shift after months of weakness and consolidation.
The market structure is starting to look very different.
One thing is clear: momentum is back, and the next few weekly closes will be important.
After all that chop…
Feels like we’re finally back. 👀🔥
{spot}(BTCUSDT)
{spot}(ETHUSDT)
#CardanoAddedToX402KitForADAPayments
#XRPRises8%
$BTC just closed above $86,000 for the first time in nearly 8 months.
$ETH is back above $2,700 too.
BTC is now roughly $7.3K above its 50-week MA, a pretty notable shift after months of weakness and consolidation.
The market structure is starting to look very different.
One thing is clear: momentum is back, and the next few weekly closes will be important.
After all that chop…
Feels like we’re finally back. 👀🔥
#CardanoAddedToX402KitForADAPayments
#XRPRises8%
$ETH is back above $2,700 too.
BTC is now roughly $7.3K above its 50-week MA, a pretty notable shift after months of weakness and consolidation.
The market structure is starting to look very different.
One thing is clear: momentum is back, and the next few weekly closes will be important.
After all that chop…
Feels like we’re finally back. 👀🔥
#CardanoAddedToX402KitForADAPayments
#XRPRises8%
171
·
--
Bullish
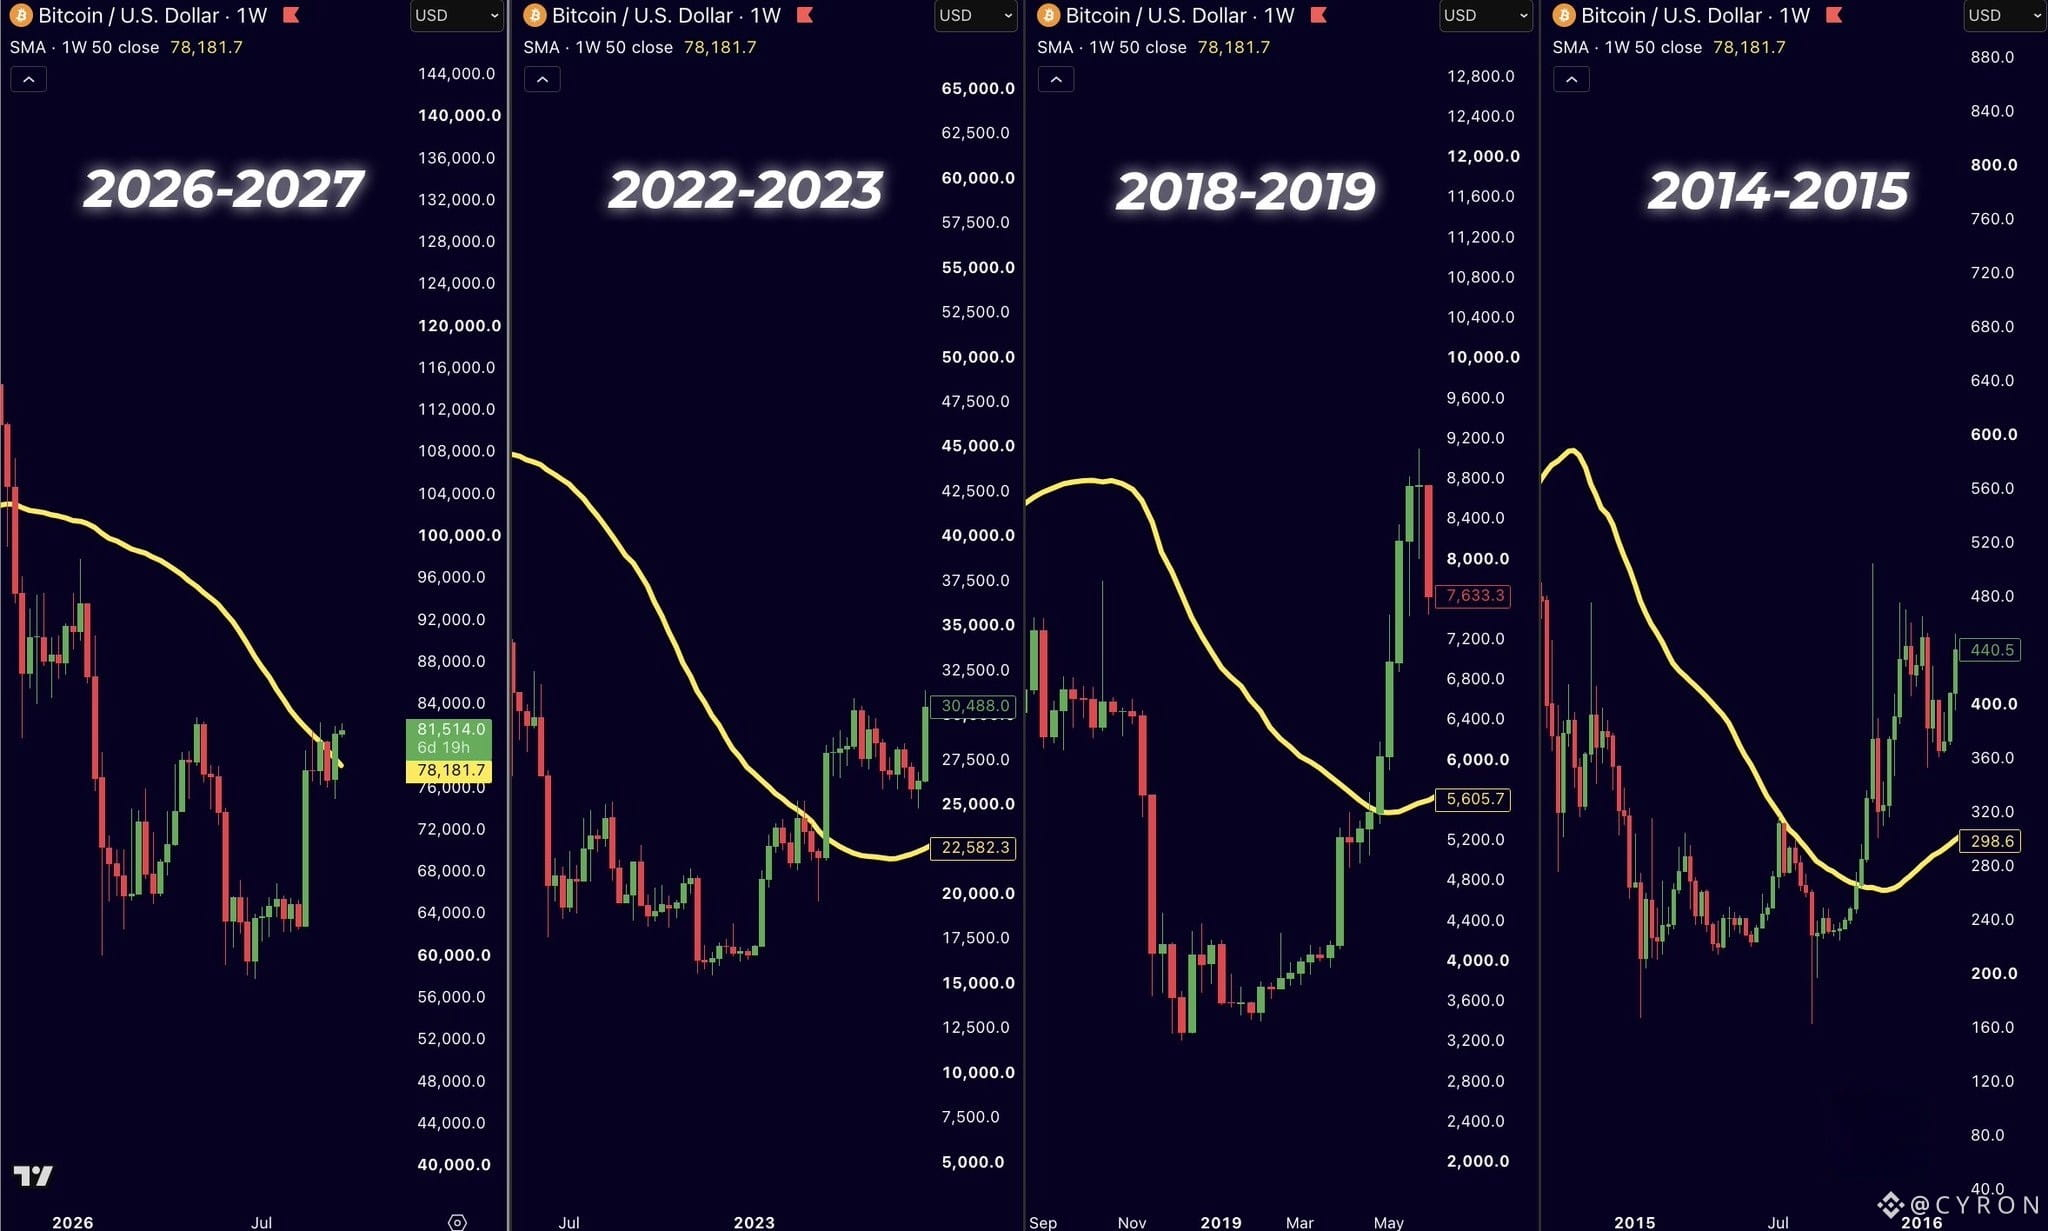
🚨 $BTC just closed above the 50-week MA.
Bitcoin is currently around $81.5K after reclaiming the 50W MA near $78.2K.
This is an important level because previous major cycle recoveries also saw BTC reclaim the 50-week moving average before stronger upside followed.
But one weekly close isn't enough to call a trend change.
The next thing to watch is whether BTC can hold above the 50W MA and eventually reclaim the $84K resistance area.
If that happens, the setup gets a lot more interesting. 👀
{spot}(BTCUSDT)
#SaylorHintsStrategyBitcoinBuy
#BTCBreaks80K
#BitcoinMarketCapTopsTesla
🚨 $BTC just closed above the 50-week MA.
Bitcoin is currently around $81.5K after reclaiming the 50W MA near $78.2K.
This is an important level because previous major cycle recoveries also saw BTC reclaim the 50-week moving average before stronger upside followed.
But one weekly close isn't enough to call a trend change.
The next thing to watch is whether BTC can hold above the 50W MA and eventually reclaim the $84K resistance area.
If that happens, the setup gets a lot more interesting. 👀
#SaylorHintsStrategyBitcoinBuy
#BTCBreaks80K
#BitcoinMarketCapTopsTesla
Bitcoin is currently around $81.5K after reclaiming the 50W MA near $78.2K.
This is an important level because previous major cycle recoveries also saw BTC reclaim the 50-week moving average before stronger upside followed.
But one weekly close isn't enough to call a trend change.
The next thing to watch is whether BTC can hold above the 50W MA and eventually reclaim the $84K resistance area.
If that happens, the setup gets a lot more interesting. 👀
#SaylorHintsStrategyBitcoinBuy
#BTCBreaks80K
#BitcoinMarketCapTopsTesla
2
3.4k
·
--
Bullish
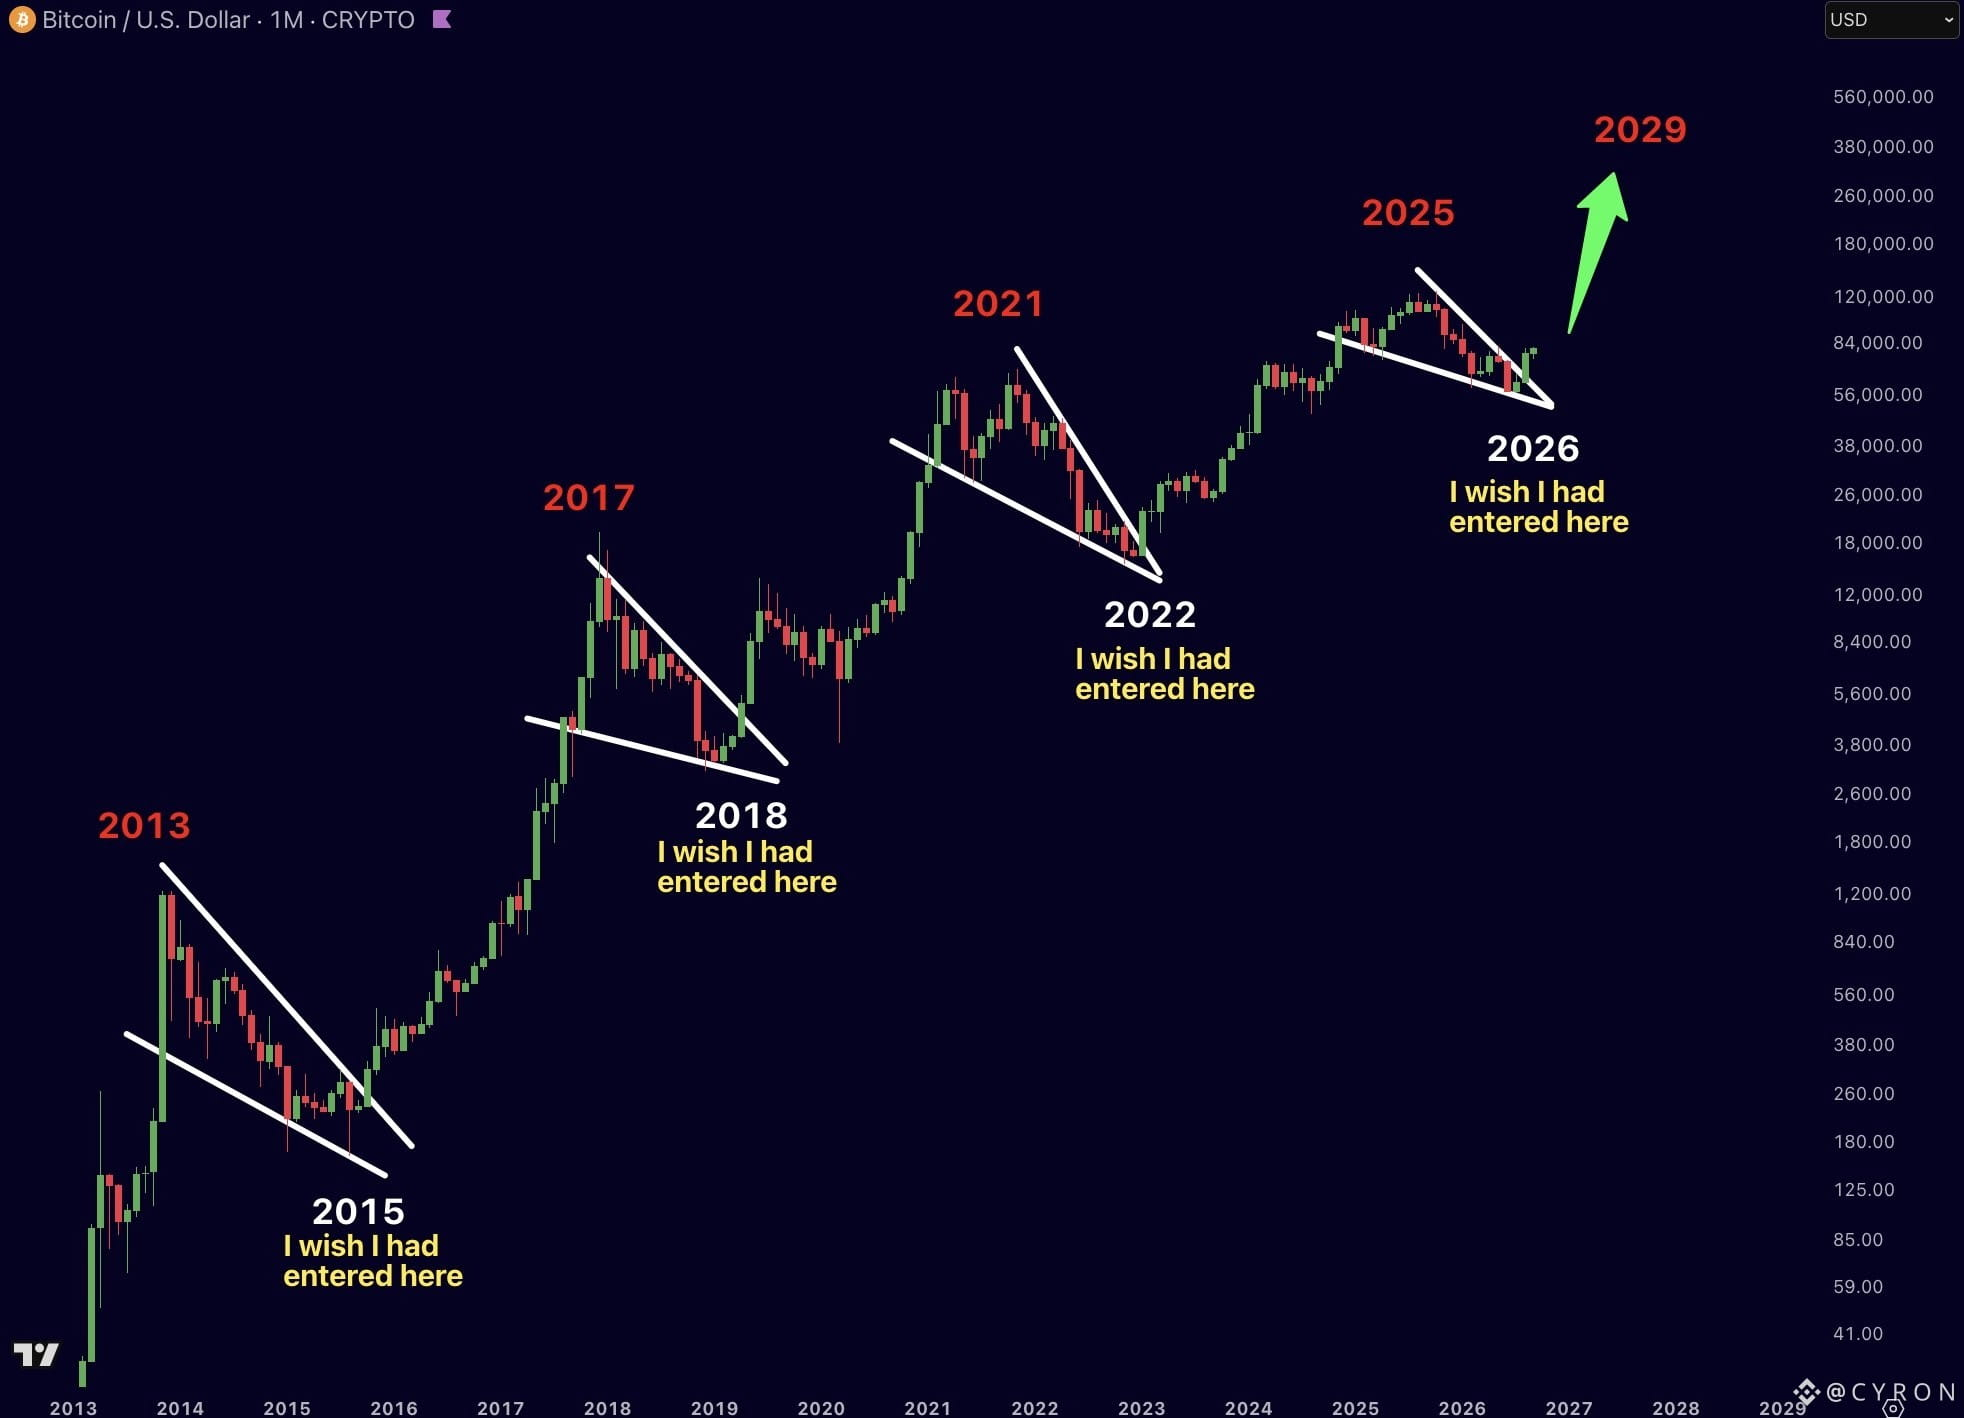
$BTC is starting to break out of its falling wedge.
What caught my attention is that similar structures appeared around the end of the 2013, 2017 and 2021 cycles.
Those breakouts were followed by major moves higher, although the pattern itself doesn’t guarantee the same outcome every time.
Now we’re seeing a similar setup in 2026.
Could this be another cycle turning point?
History doesn’t repeat perfectly, but sometimes the similarities are hard to ignore. 👀
{spot}(BTCUSDT)
#BTCBreaks80K
#BitcoinMarketCapTopsTesla
$BTC is starting to break out of its falling wedge.
What caught my attention is that similar structures appeared around the end of the 2013, 2017 and 2021 cycles.
Those breakouts were followed by major moves higher, although the pattern itself doesn’t guarantee the same outcome every time.
Now we’re seeing a similar setup in 2026.
Could this be another cycle turning point?
History doesn’t repeat perfectly, but sometimes the similarities are hard to ignore. 👀
#BTCBreaks80K
#BitcoinMarketCapTopsTesla
What caught my attention is that similar structures appeared around the end of the 2013, 2017 and 2021 cycles.
Those breakouts were followed by major moves higher, although the pattern itself doesn’t guarantee the same outcome every time.
Now we’re seeing a similar setup in 2026.
Could this be another cycle turning point?
History doesn’t repeat perfectly, but sometimes the similarities are hard to ignore. 👀
#BTCBreaks80K
#BitcoinMarketCapTopsTesla
224
·
--
Bullish
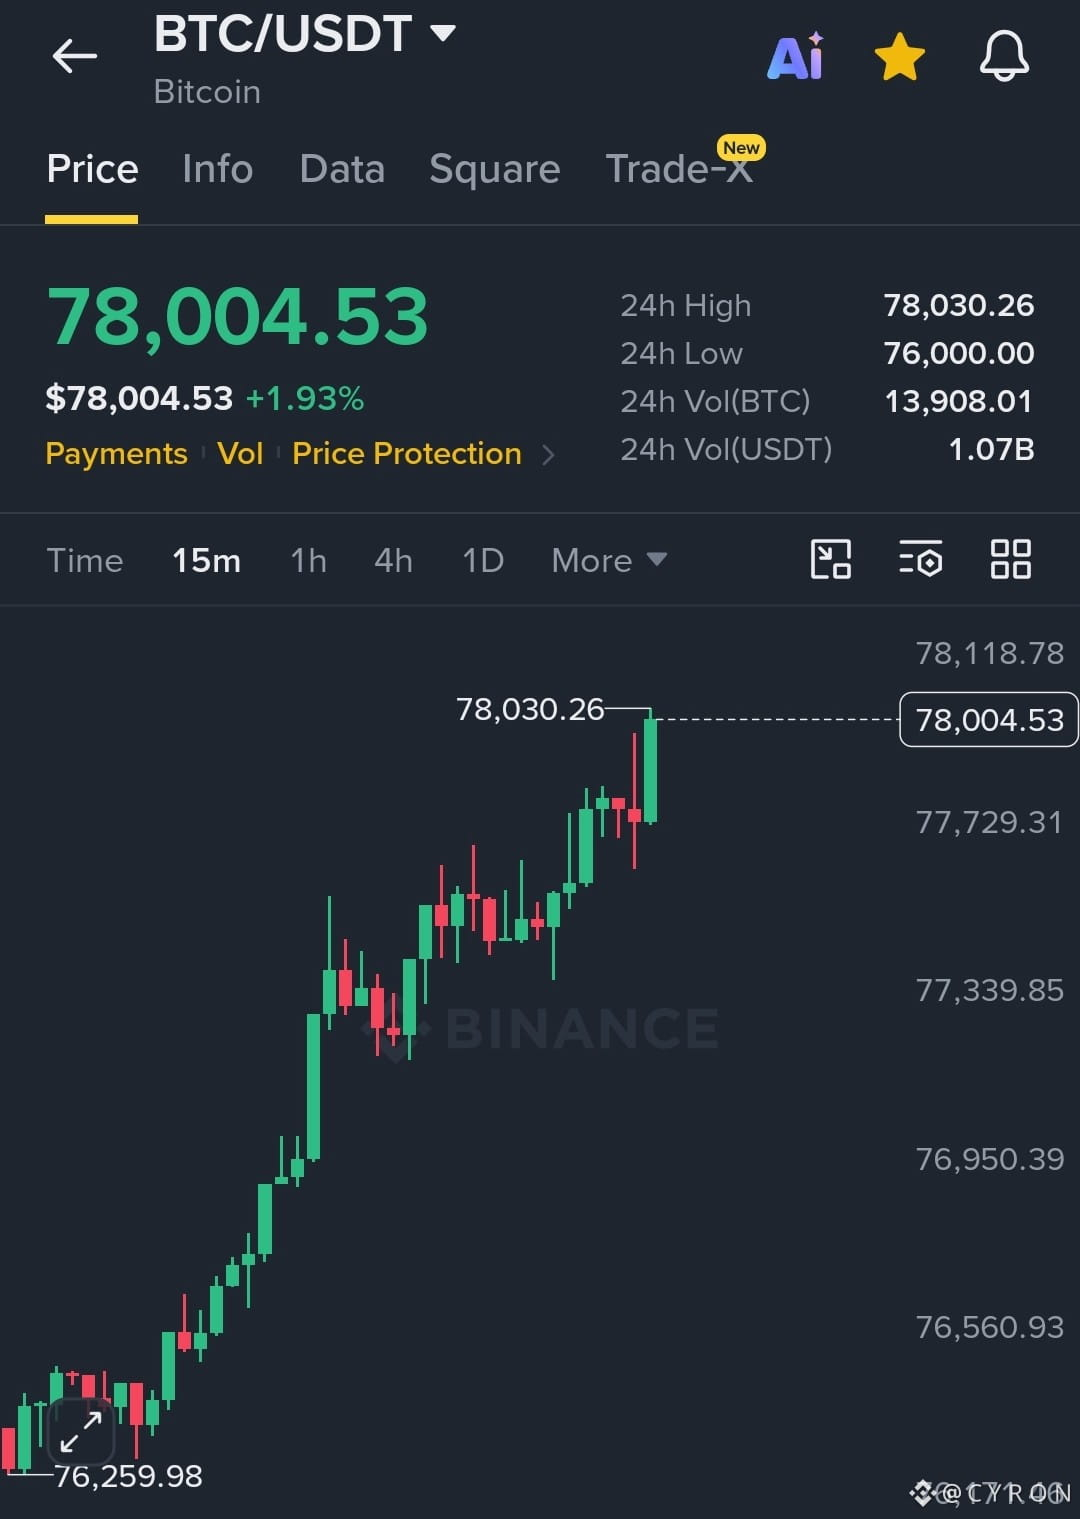
$BTC back at $78,000.
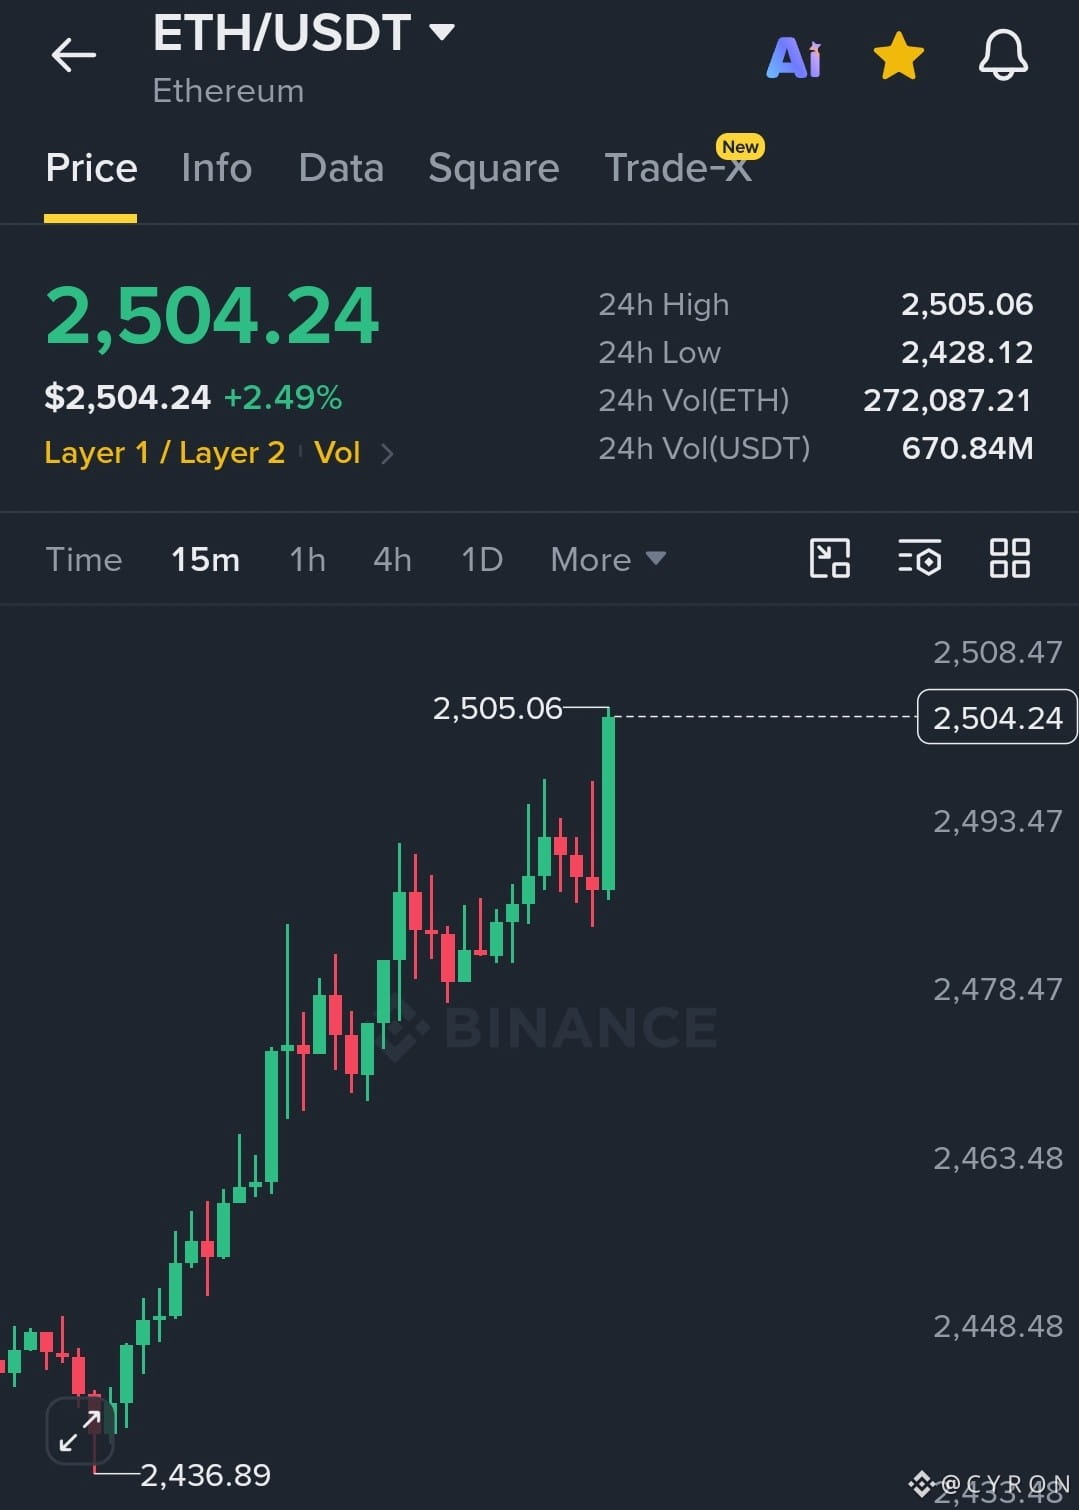
$ETH back above $2,500.
After all the chop and uncertainty, seeing both majors reclaim these levels feels good.
Now the interesting part starts — can they actually hold these levels and build from here?
Either way, the market finally feels like it has some energy again.
We’re back. 👀🔥
{spot}(BTCUSDT)
{spot}(ETHUSDT)
#BOJHikesRatesTo31YearHigh
#ChainlinkPowersBottomlinePaymentPlatform
$BTC back at $78,000.
$ETH back above $2,500.
After all the chop and uncertainty, seeing both majors reclaim these levels feels good.
Now the interesting part starts — can they actually hold these levels and build from here?
Either way, the market finally feels like it has some energy again.
We’re back. 👀🔥
#BOJHikesRatesTo31YearHigh
#ChainlinkPowersBottomlinePaymentPlatform
$ETH back above $2,500.
After all the chop and uncertainty, seeing both majors reclaim these levels feels good.
Now the interesting part starts — can they actually hold these levels and build from here?
Either way, the market finally feels like it has some energy again.
We’re back. 👀🔥
#BOJHikesRatesTo31YearHigh
#ChainlinkPowersBottomlinePaymentPlatform
1
1
208
·
--
Bearish
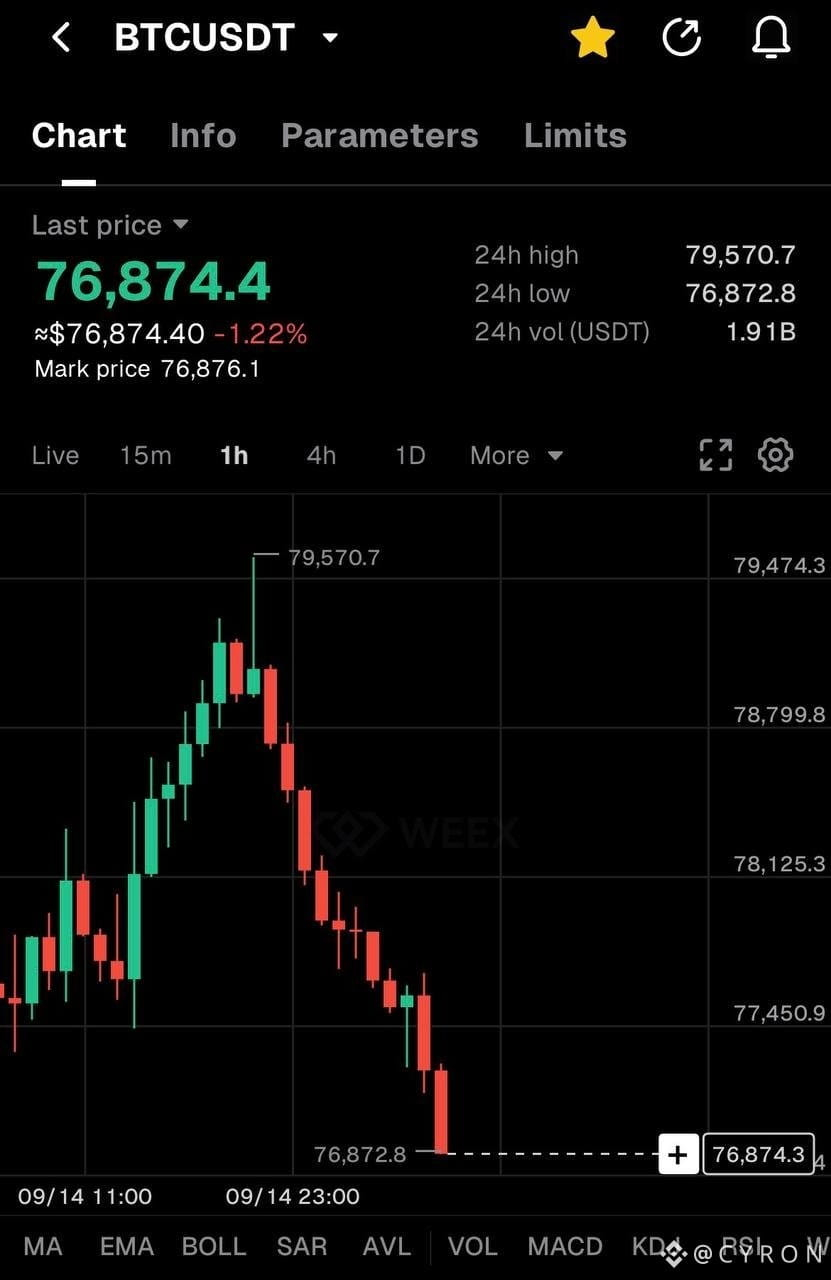
🚨 BITCOIN JUST LOST $77,000.
Selling pressure is accelerating.
$75,000 is now the key level bulls need to defend.
Lose $75K, and the downside could open up fast.
This is a level I’m watching closely.
{spot}(BTCUSDT)
#SolanaTransactionV1GoesLiveOnMainnet
#FedHikeOddsRiseTo89%
🚨 BITCOIN JUST LOST $77,000.
Selling pressure is accelerating.
$75,000 is now the key level bulls need to defend.
Lose $75K, and the downside could open up fast.
This is a level I’m watching closely.
#SolanaTransactionV1GoesLiveOnMainnet
#FedHikeOddsRiseTo89%
Selling pressure is accelerating.
$75,000 is now the key level bulls need to defend.
Lose $75K, and the downside could open up fast.
This is a level I’m watching closely.
#SolanaTransactionV1GoesLiveOnMainnet
#FedHikeOddsRiseTo89%
1
139
·
--
Bullish
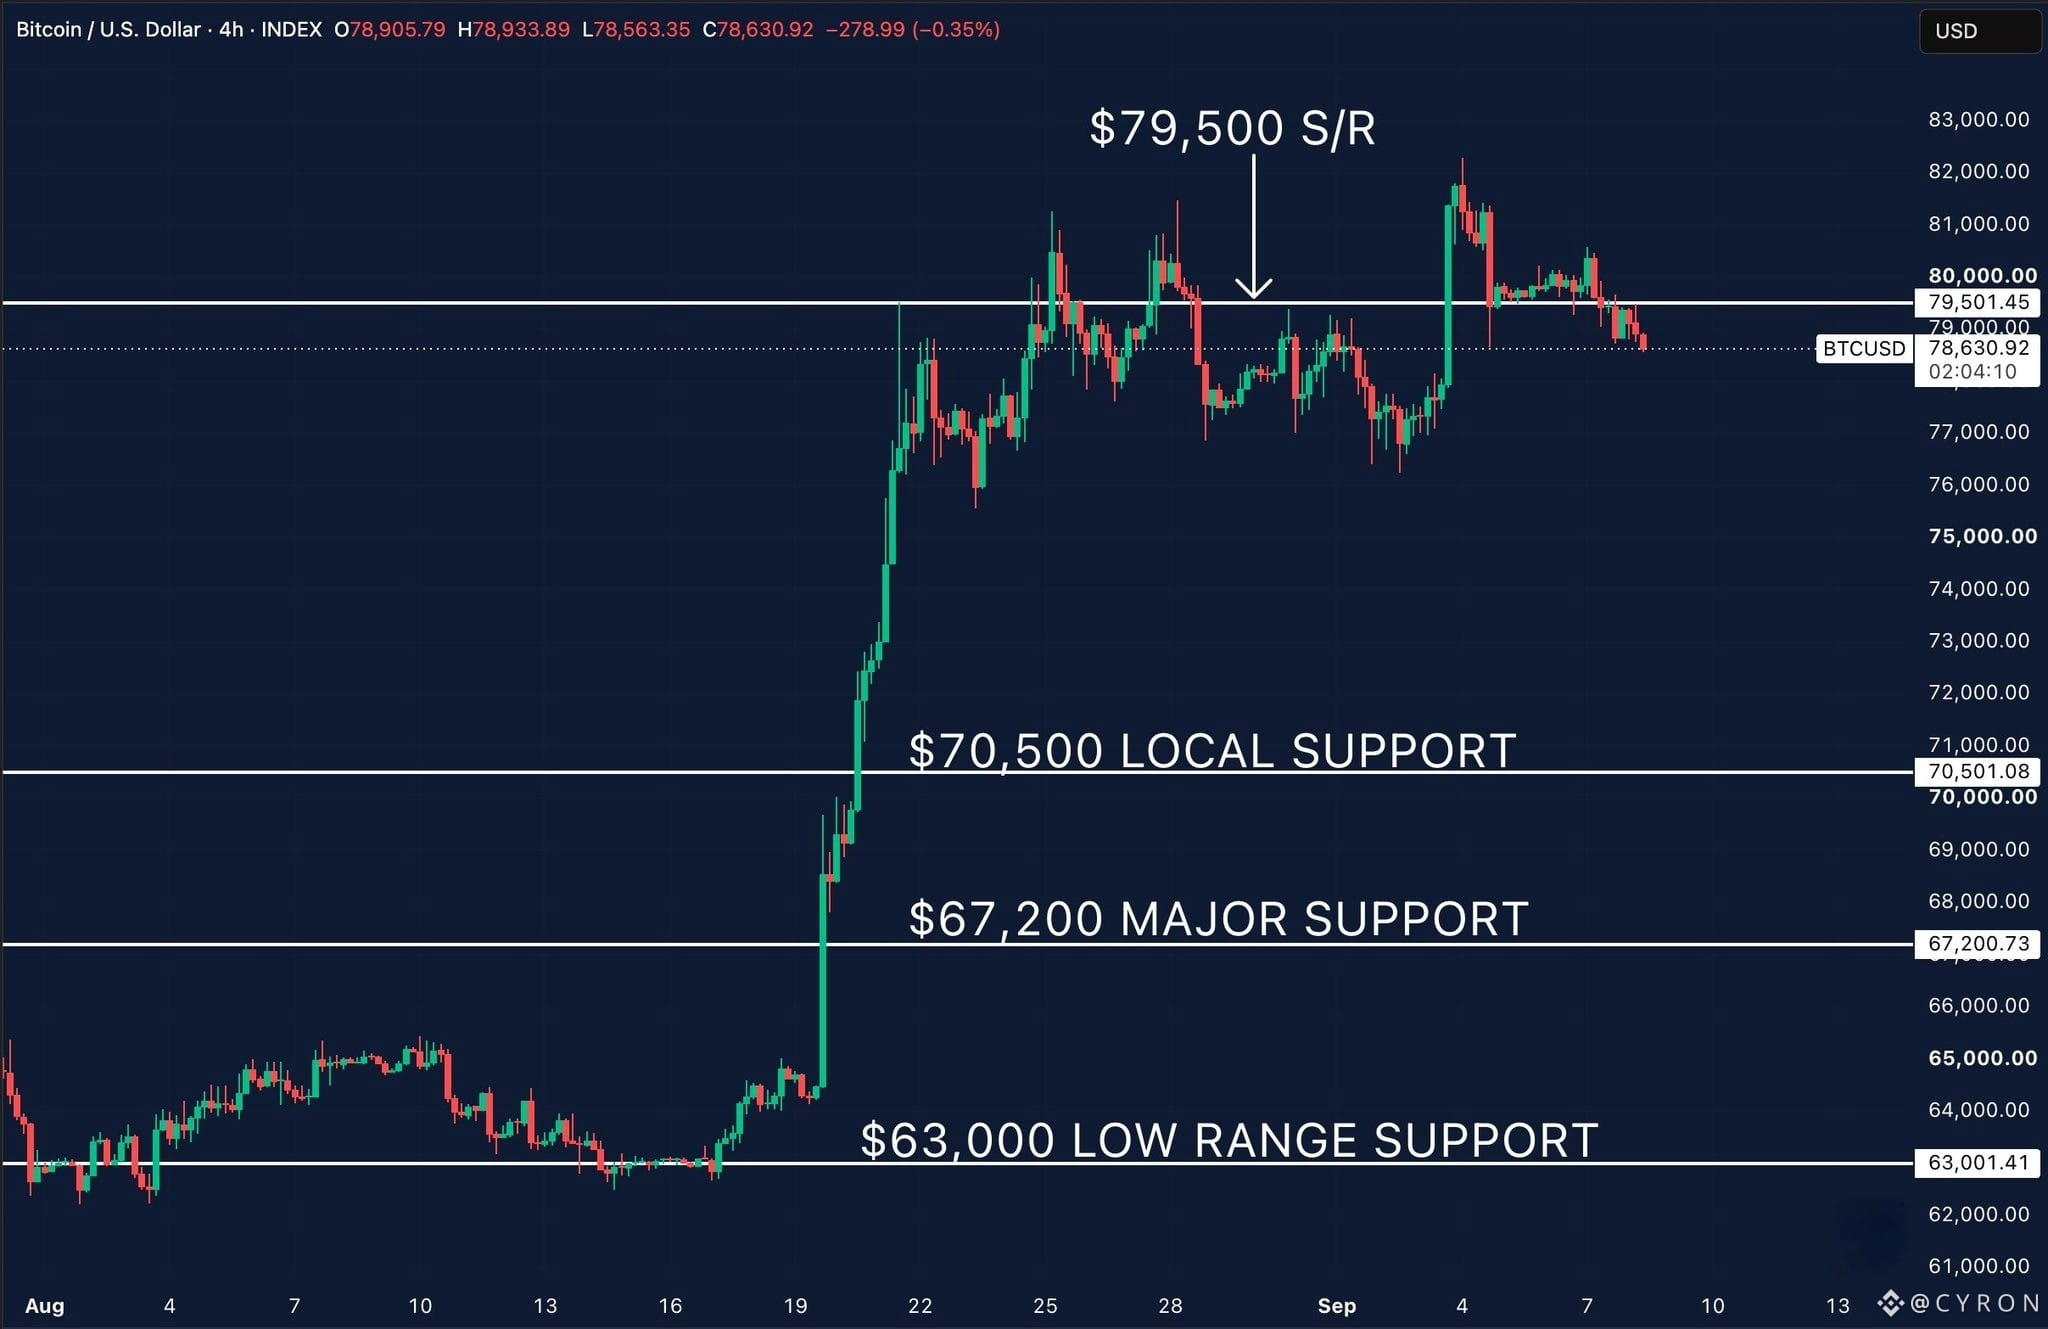
Bitcoin is at a key level.
$79,500 has flipped from support into resistance after $BTC failed to hold above it.
If we reclaim $79.5K and hold, I’d be looking for a move back towards $81K+.
If we lose $78K, I’d expect the liquidity below to get taken first.
Simple levels to watch.
$79.5K reclaim = bullish.
$78K loss = bearish.
Until then, I’m waiting...
{spot}(BTCUSDT)
#SaudiHaltsSouthernEnergySitesAfterAttacks
#YenBreaks155NearingYearHigh
#USIranTradeTankerStrikesEscalate
Bitcoin is at a key level.
$79,500 has flipped from support into resistance after $BTC failed to hold above it.
If we reclaim $79.5K and hold, I’d be looking for a move back towards $81K+.
If we lose $78K, I’d expect the liquidity below to get taken first.
Simple levels to watch.
$79.5K reclaim = bullish.
$78K loss = bearish.
Until then, I’m waiting...
#SaudiHaltsSouthernEnergySitesAfterAttacks
#YenBreaks155NearingYearHigh
#USIranTradeTankerStrikesEscalate
$79,500 has flipped from support into resistance after $BTC failed to hold above it.
If we reclaim $79.5K and hold, I’d be looking for a move back towards $81K+.
If we lose $78K, I’d expect the liquidity below to get taken first.
Simple levels to watch.
$79.5K reclaim = bullish.
$78K loss = bearish.
Until then, I’m waiting...
#SaudiHaltsSouthernEnergySitesAfterAttacks
#YenBreaks155NearingYearHigh
#USIranTradeTankerStrikesEscalate
116
·
--
Bullish
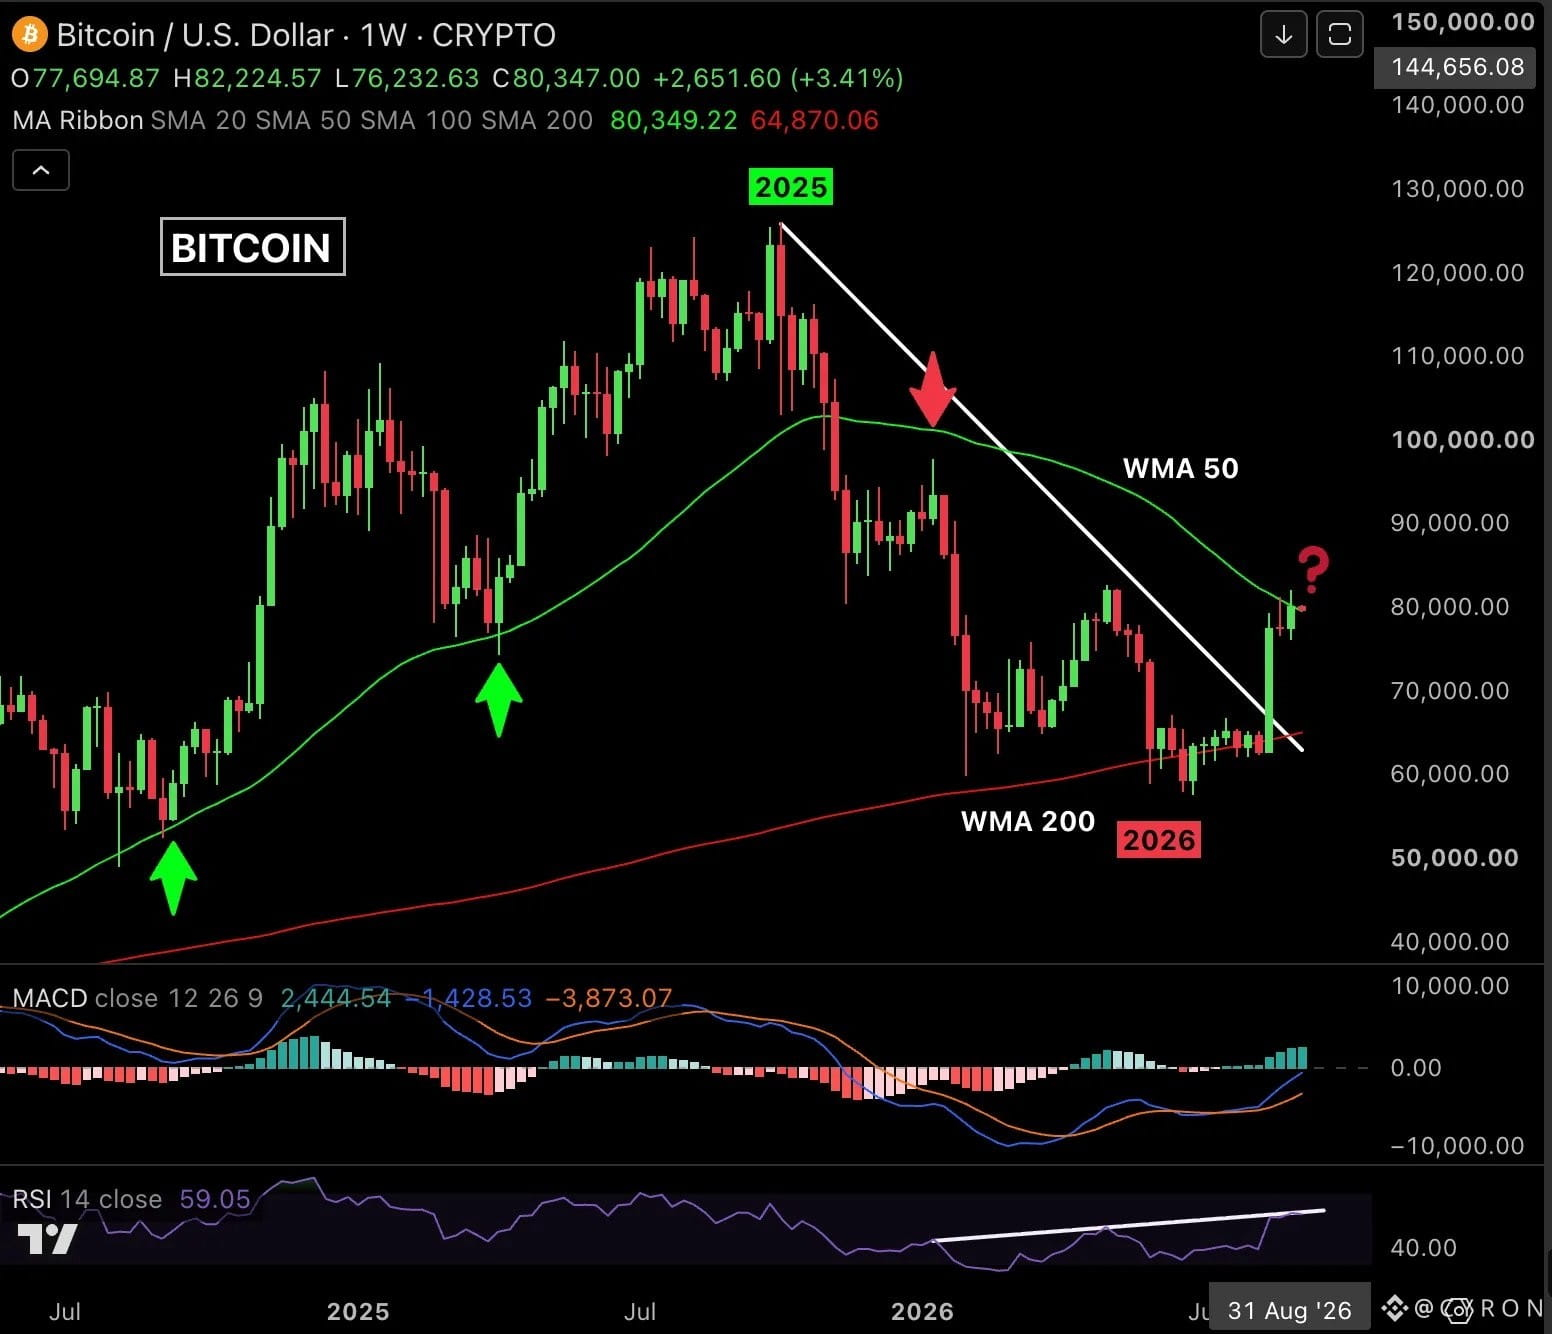
BITCOIN WEEKLY ANALYSIS
Bitcoin closed the week right around the Weekly MA 50 near $80,349.
This is a major test for $BTC , not a confirmed breakout yet.
Here’s what I’m watching next 🧵
{spot}(BTCUSDT)
#USIranTradeTankerStrikesEscalate
#IMFSaysElSalvadorBTCNoPublicFunds
#IranSaysItHit3USShips3Tankers
BITCOIN WEEKLY ANALYSIS
Bitcoin closed the week right around the Weekly MA 50 near $80,349.
This is a major test for $BTC , not a confirmed breakout yet.
Here’s what I’m watching next 🧵
#USIranTradeTankerStrikesEscalate
#IMFSaysElSalvadorBTCNoPublicFunds
#IranSaysItHit3USShips3Tankers
Bitcoin closed the week right around the Weekly MA 50 near $80,349.
This is a major test for $BTC , not a confirmed breakout yet.
Here’s what I’m watching next 🧵
#USIranTradeTankerStrikesEscalate
#IMFSaysElSalvadorBTCNoPublicFunds
#IranSaysItHit3USShips3Tankers
216
·
--
Bullish
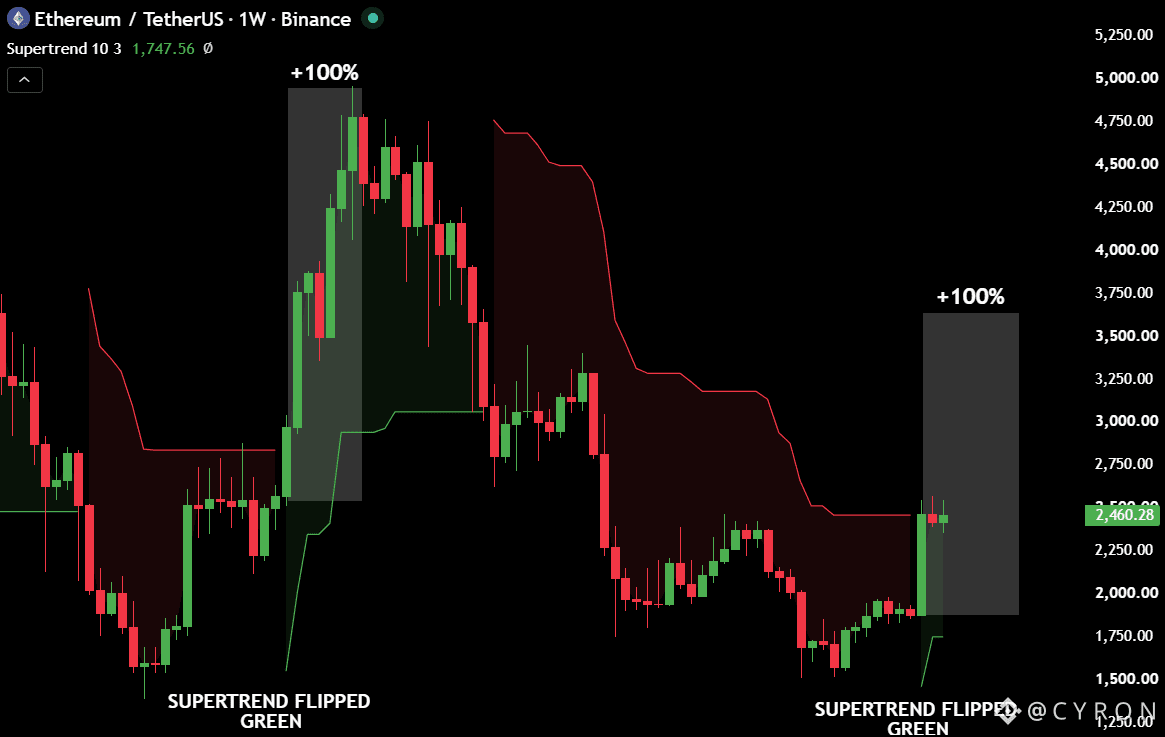
$ETH weekly Supertrend has flipped green. 🟢
The last time this happened, ETH pumped over 100% in just 6 weeks.
If history repeats, a similar move could put ETH around $3,600 by October.
One signal doesn't guarantee the same outcome.
But this is definitely worth watching. 👀
{spot}(ETHUSDT)
#ZECHitsANewAllTimeHigh
#BitcoinETFsBiggestDailyInflowSinceJanuary
#USAugustJobGrowthNearlyTriplesForecast
$ETH weekly Supertrend has flipped green. 🟢
The last time this happened, ETH pumped over 100% in just 6 weeks.
If history repeats, a similar move could put ETH around $3,600 by October.
One signal doesn't guarantee the same outcome.
But this is definitely worth watching. 👀
#ZECHitsANewAllTimeHigh
#BitcoinETFsBiggestDailyInflowSinceJanuary
#USAugustJobGrowthNearlyTriplesForecast
The last time this happened, ETH pumped over 100% in just 6 weeks.
If history repeats, a similar move could put ETH around $3,600 by October.
One signal doesn't guarantee the same outcome.
But this is definitely worth watching. 👀
#ZECHitsANewAllTimeHigh
#BitcoinETFsBiggestDailyInflowSinceJanuary
#USAugustJobGrowthNearlyTriplesForecast
162
·
--
Bullish
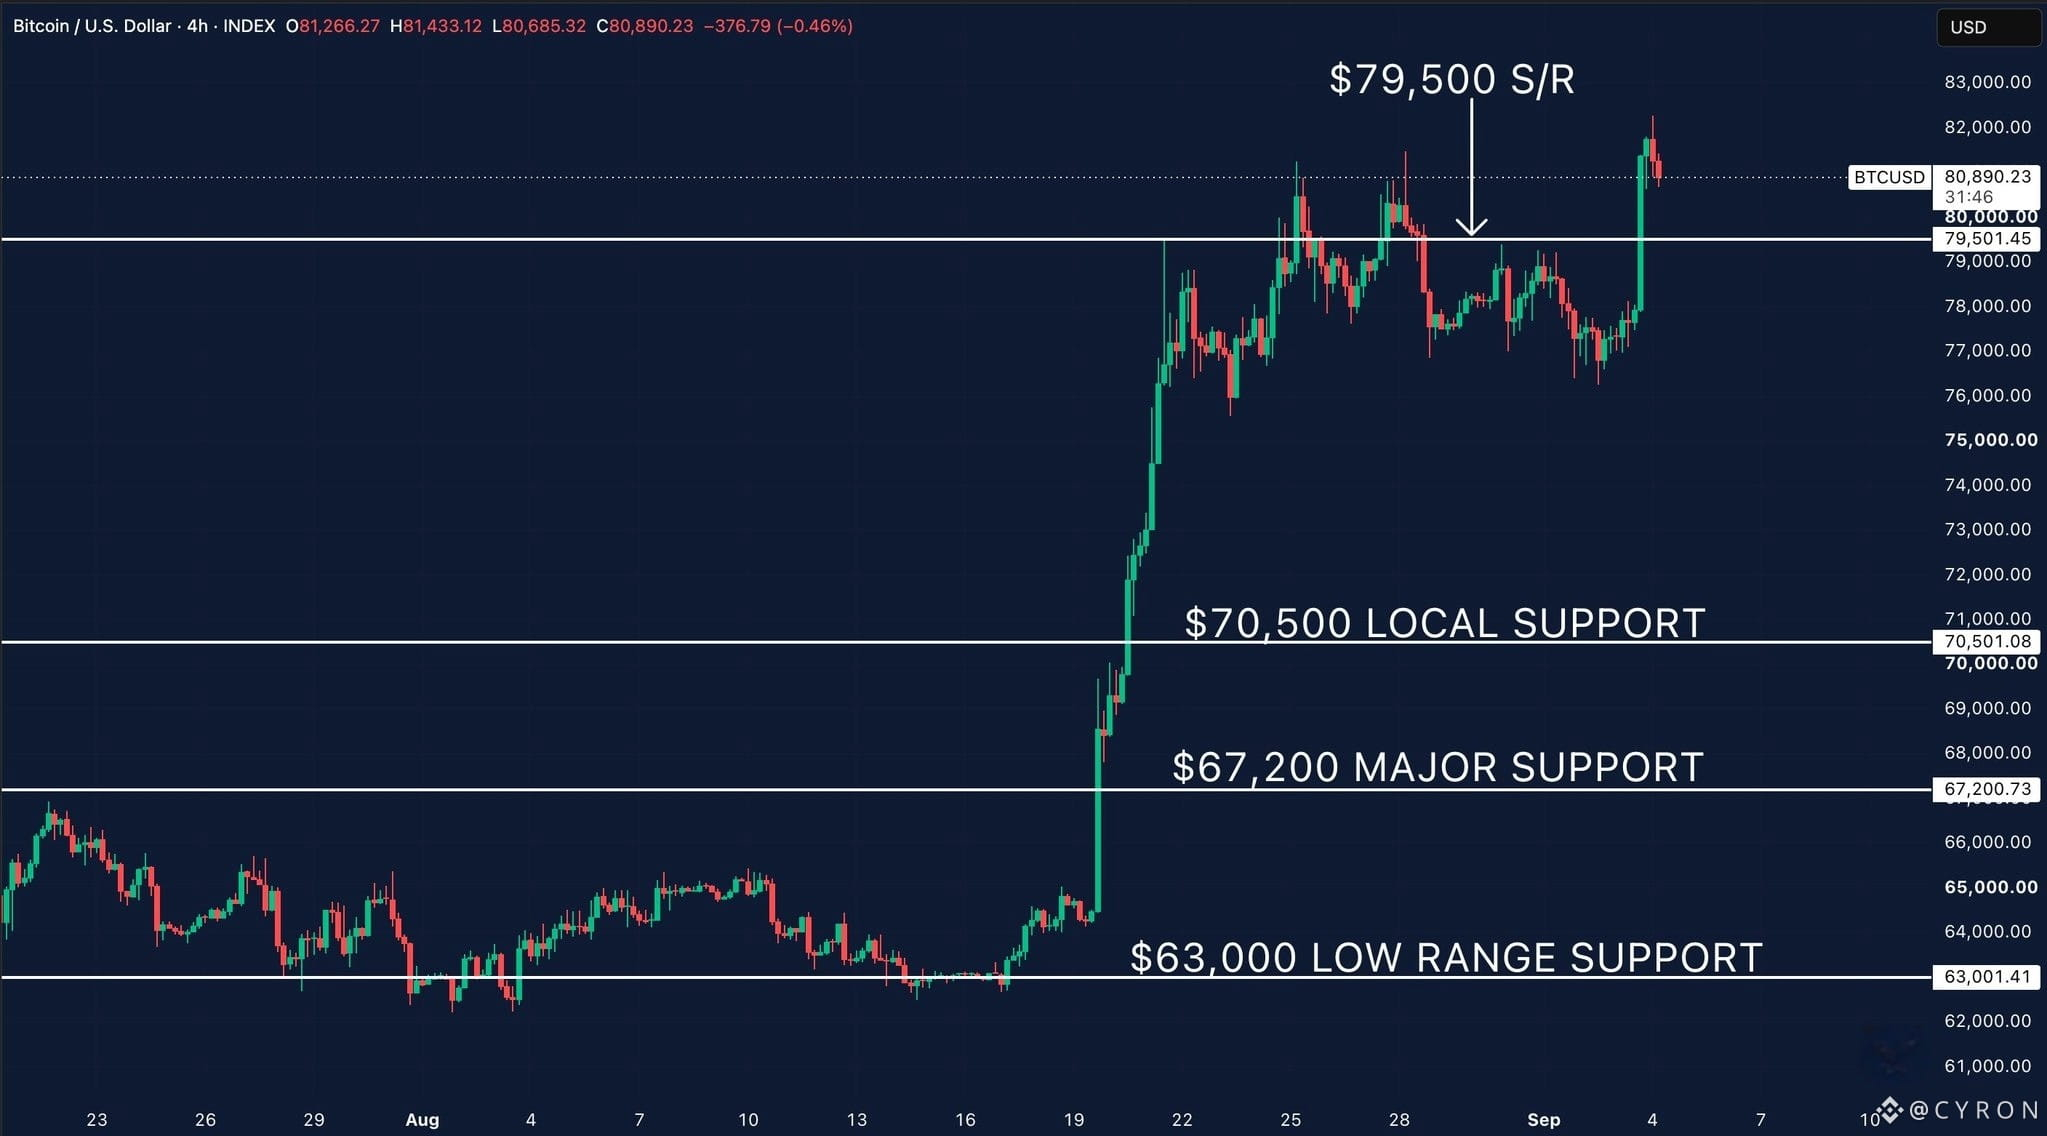
BITCOIN JUST FLIPPED $79,500 INTO SUPPORT 🚨
Bitcoin broke through the $79,500 resistance I’ve been watching and pushed above $80K.
$BTC is now trading around $80.9K after briefly reaching above $82K.
The key level now is simple: $79.5K.
If Bitcoin holds above it, I’m watching $82K next.
Lose $79.5K, and this breakout starts looking a lot less convincing.
For now, the structure has improved significantly.
{spot}(BTCUSDT)
#USWeeklyInitialJoblessClaimsRiseTo206000
#HousePressesSenateOnCLARITYAct
BITCOIN JUST FLIPPED $79,500 INTO SUPPORT 🚨
Bitcoin broke through the $79,500 resistance I’ve been watching and pushed above $80K.
$BTC is now trading around $80.9K after briefly reaching above $82K.
The key level now is simple: $79.5K.
If Bitcoin holds above it, I’m watching $82K next.
Lose $79.5K, and this breakout starts looking a lot less convincing.
For now, the structure has improved significantly.
#USWeeklyInitialJoblessClaimsRiseTo206000
#HousePressesSenateOnCLARITYAct
Bitcoin broke through the $79,500 resistance I’ve been watching and pushed above $80K.
$BTC is now trading around $80.9K after briefly reaching above $82K.
The key level now is simple: $79.5K.
If Bitcoin holds above it, I’m watching $82K next.
Lose $79.5K, and this breakout starts looking a lot less convincing.
For now, the structure has improved significantly.
#USWeeklyInitialJoblessClaimsRiseTo206000
#HousePressesSenateOnCLARITYAct
1
1
142
·
--
Bullish
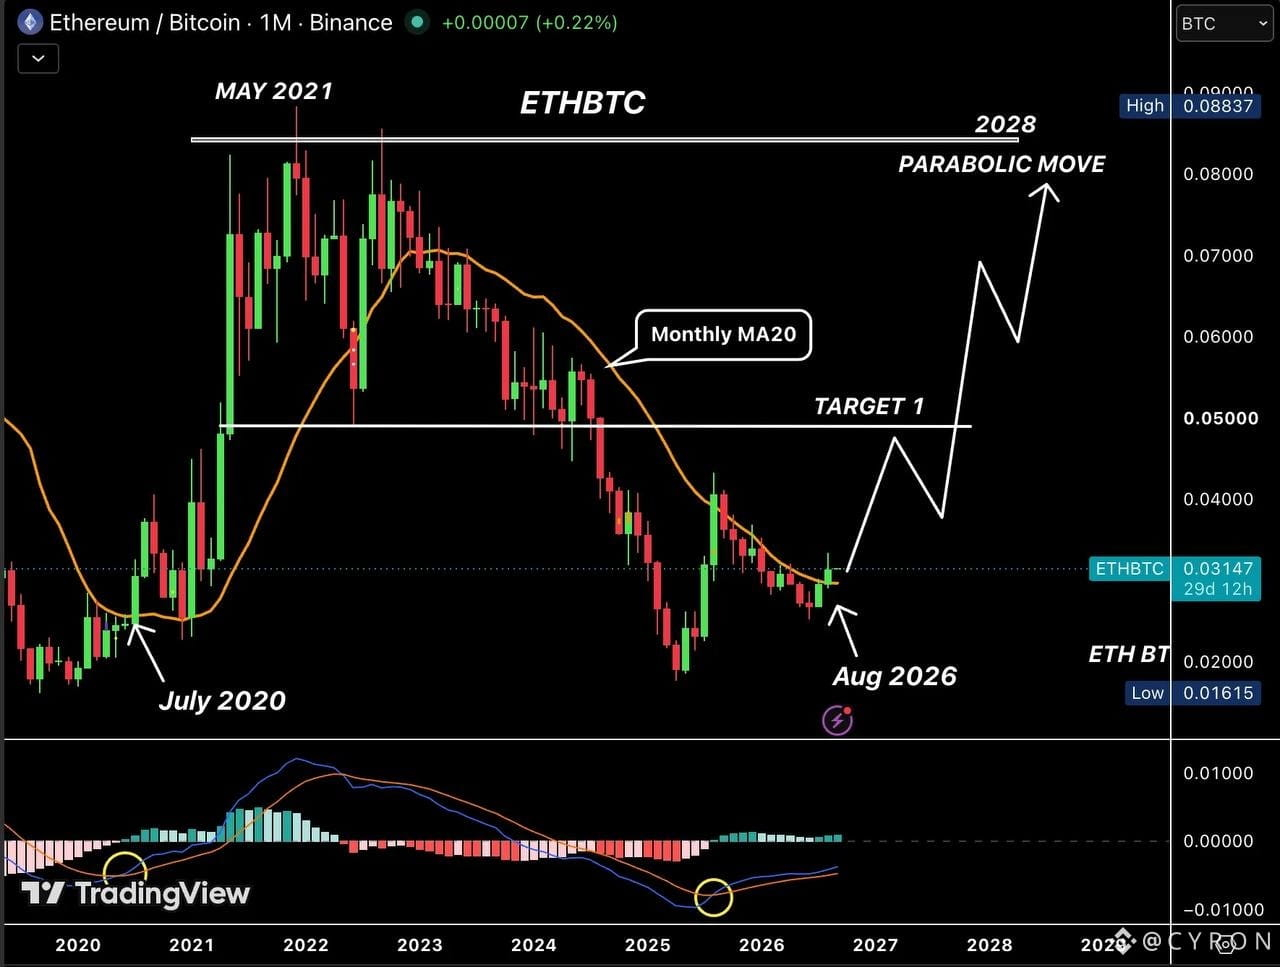
ETH/BTC monthly chart is starting to look interesting.
Price has closed above the MA 20.
The last clean reclaim of this level came in July 2020.
What followed?
ETH/BTC: 0.0315 → 0.088
ETH: $225 → $4,372
In August 2025, price also touched this average but failed to hold it and eventually dumped back toward the lows.
That’s the key difference now.
ETH/BTC needs to stay above the MA 20.
MACD is also turning up from a similar area to the one that preceded the 2020 breakout.
If the hold works:
First target → 0.050
Stretch target → 0.088
Meanwhile, ISM came in at 54.6 vs 55.2 expected, showing growth is still holding up but slowing.
If macro conditions continue moving toward easier monetary policy, ETH could have more room to outperform.
This setup is definitely worth watching. 👀
{spot}(BTCUSDT)
{spot}(ETHUSDT)
#BitcoinETFBuyersReturn
#FedHikeOddsRiseTo68%
#G20StatementCitesDigitalAssets
ETH/BTC monthly chart is starting to look interesting.
Price has closed above the MA 20.
The last clean reclaim of this level came in July 2020.
What followed?
ETH/BTC: 0.0315 → 0.088
ETH: $225 → $4,372
In August 2025, price also touched this average but failed to hold it and eventually dumped back toward the lows.
That’s the key difference now.
ETH/BTC needs to stay above the MA 20.
MACD is also turning up from a similar area to the one that preceded the 2020 breakout.
If the hold works:
First target → 0.050
Stretch target → 0.088
Meanwhile, ISM came in at 54.6 vs 55.2 expected, showing growth is still holding up but slowing.
If macro conditions continue moving toward easier monetary policy, ETH could have more room to outperform.
This setup is definitely worth watching. 👀
#BitcoinETFBuyersReturn
#FedHikeOddsRiseTo68%
#G20StatementCitesDigitalAssets
Price has closed above the MA 20.
The last clean reclaim of this level came in July 2020.
What followed?
ETH/BTC: 0.0315 → 0.088
ETH: $225 → $4,372
In August 2025, price also touched this average but failed to hold it and eventually dumped back toward the lows.
That’s the key difference now.
ETH/BTC needs to stay above the MA 20.
MACD is also turning up from a similar area to the one that preceded the 2020 breakout.
If the hold works:
First target → 0.050
Stretch target → 0.088
Meanwhile, ISM came in at 54.6 vs 55.2 expected, showing growth is still holding up but slowing.
If macro conditions continue moving toward easier monetary policy, ETH could have more room to outperform.
This setup is definitely worth watching. 👀
#BitcoinETFBuyersReturn
#FedHikeOddsRiseTo68%
#G20StatementCitesDigitalAssets
1
110
·
--
Bullish
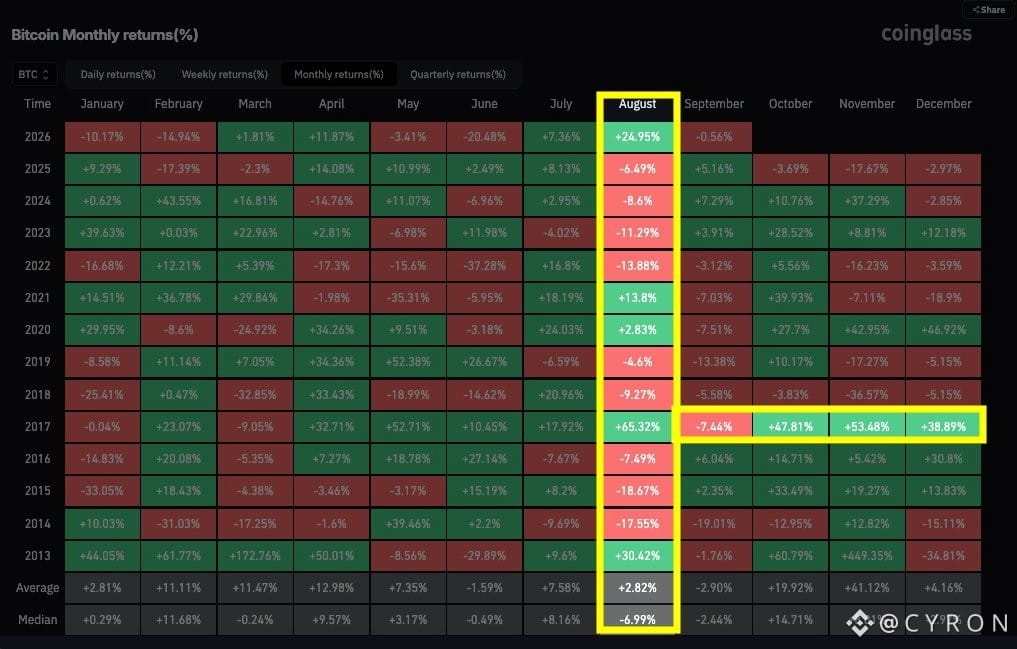
Bitcoin just had its BEST August since 2017.
August 2026: +24.95%
August 2017: +65.32%
But here's what happened after August 2017:
October: +47.81%
November: +53.48%
December: +38.89%
History doesn't have to repeat.
But when you see a setup like this, it's hard not to pay attention. 👀
{spot}(BTCUSDT)
#ARBRises30%OnRobinhoodChainRevenue
#Japan10YYieldHits3%FirstSince1996
#WTIOilRisesAsOpenInterestShrinks
Bitcoin just had its BEST August since 2017.
August 2026: +24.95%
August 2017: +65.32%
But here's what happened after August 2017:
October: +47.81%
November: +53.48%
December: +38.89%
History doesn't have to repeat.
But when you see a setup like this, it's hard not to pay attention. 👀
#ARBRises30%OnRobinhoodChainRevenue
#Japan10YYieldHits3%FirstSince1996
#WTIOilRisesAsOpenInterestShrinks
August 2026: +24.95%
August 2017: +65.32%
But here's what happened after August 2017:
October: +47.81%
November: +53.48%
December: +38.89%
History doesn't have to repeat.
But when you see a setup like this, it's hard not to pay attention. 👀
#ARBRises30%OnRobinhoodChainRevenue
#Japan10YYieldHits3%FirstSince1996
#WTIOilRisesAsOpenInterestShrinks
183
·
--
Bearish
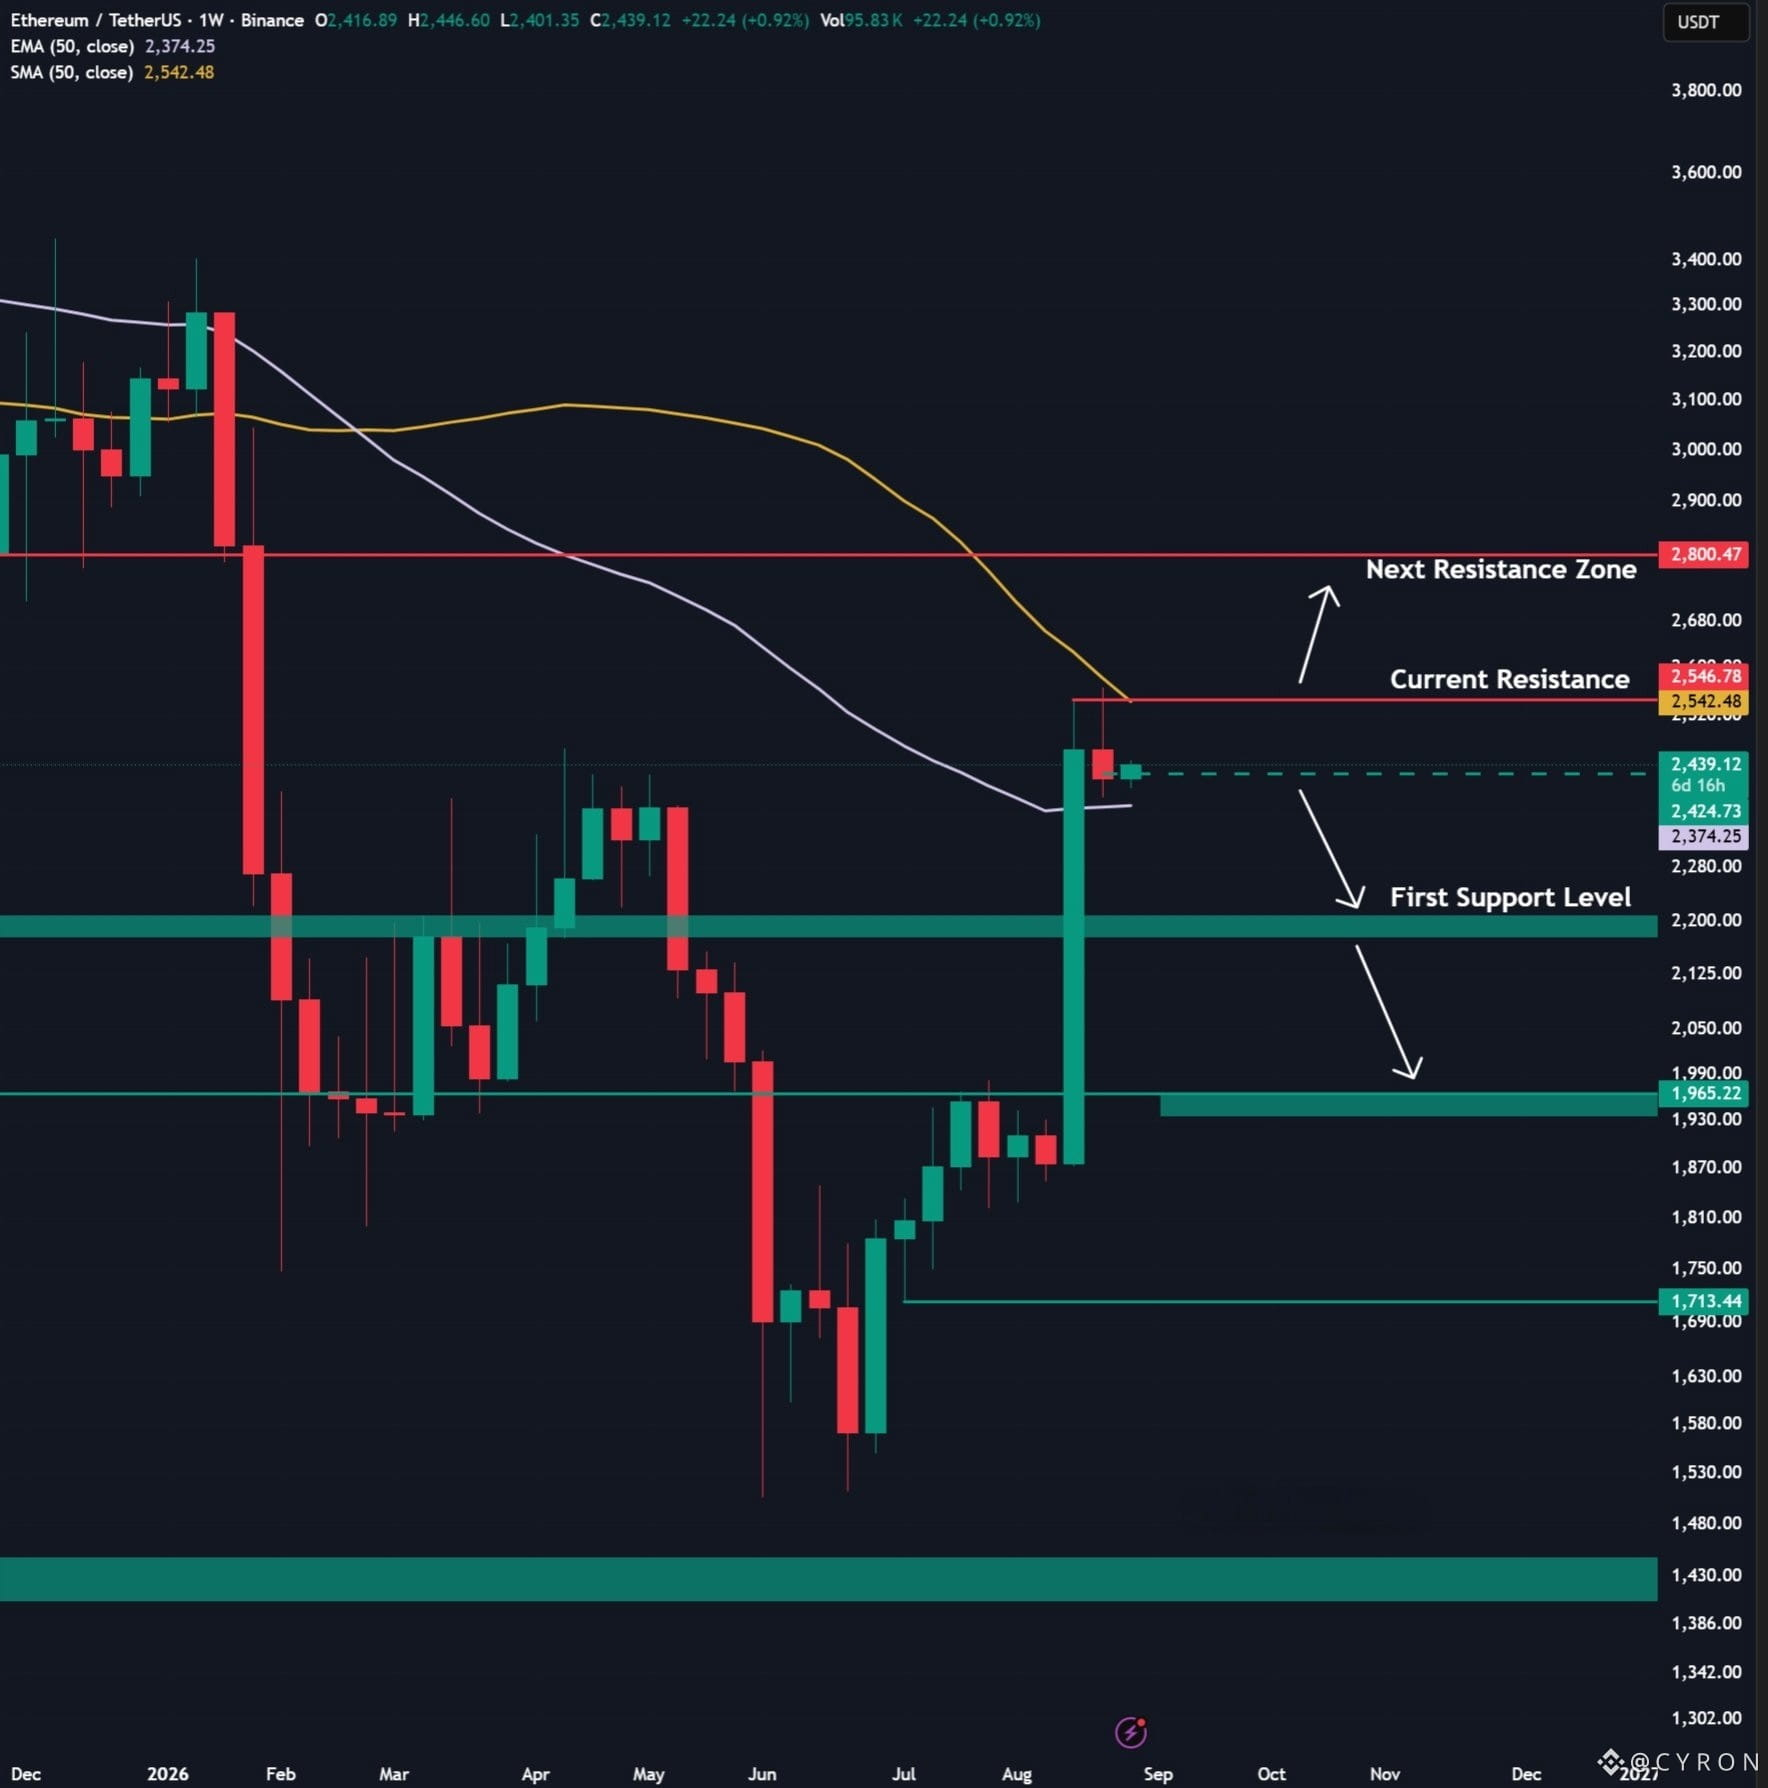
$ETH tried to break above the $2,550 level but failed again.
For now, I think most of Ethereum's short-term upside may already be priced in.
Expecting more chop around these levels, with the possibility of one more small capitulation before a proper reversal.
Patience here.
{spot}(ETHUSDT)
#SKHynixStudiesJapanMemoryChipVenture
#KospiDrops3.6%AsSamsungSKHynixWeaken
#UKReleasesFirstCryptoGainsTaxStats
$ETH tried to break above the $2,550 level but failed again.
For now, I think most of Ethereum's short-term upside may already be priced in.
Expecting more chop around these levels, with the possibility of one more small capitulation before a proper reversal.
Patience here.
#SKHynixStudiesJapanMemoryChipVenture
#KospiDrops3.6%AsSamsungSKHynixWeaken
#UKReleasesFirstCryptoGainsTaxStats
For now, I think most of Ethereum's short-term upside may already be priced in.
Expecting more chop around these levels, with the possibility of one more small capitulation before a proper reversal.
Patience here.
#SKHynixStudiesJapanMemoryChipVenture
#KospiDrops3.6%AsSamsungSKHynixWeaken
#UKReleasesFirstCryptoGainsTaxStats
143
·
--
Bullish
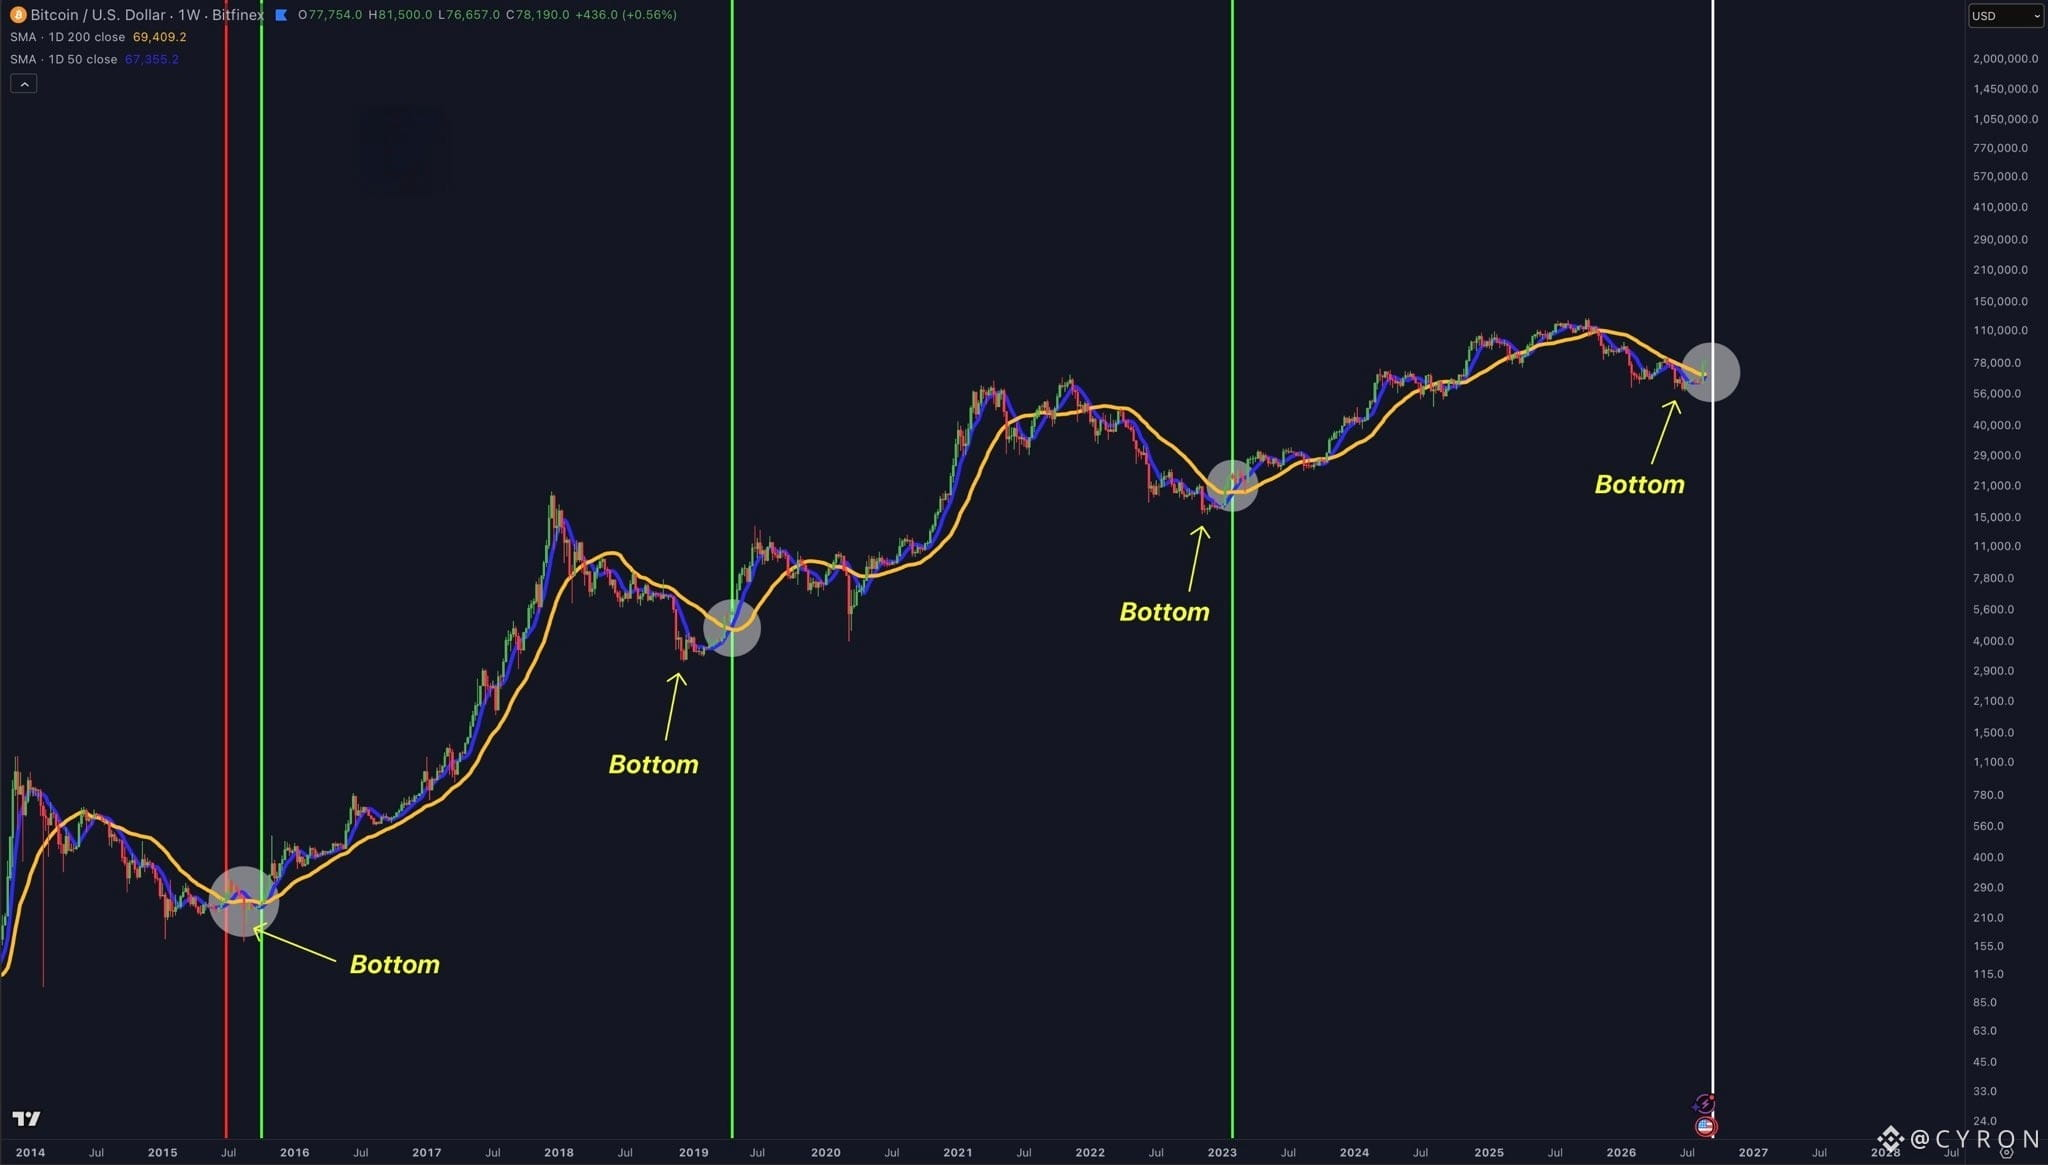
BITCOIN GOLDEN CROSS INCOMING.
If $BTC can hold here or continue higher into September, the daily Golden Cross will officially confirm.
It has flashed 4 times near the end of bear markets.
3 times, it got the direction right.
Could Bitcoin be setting up for another major trend reversal? 🚀
{spot}(BTCUSDT)
#KoreaSingleStockLeveragedETFTradingFalls
#VietnamPilotsCryptoAssetMarket
#GoldFalls3.24%ThisWeek
BITCOIN GOLDEN CROSS INCOMING.
If $BTC can hold here or continue higher into September, the daily Golden Cross will officially confirm.
It has flashed 4 times near the end of bear markets.
3 times, it got the direction right.
Could Bitcoin be setting up for another major trend reversal? 🚀
#KoreaSingleStockLeveragedETFTradingFalls
#VietnamPilotsCryptoAssetMarket
#GoldFalls3.24%ThisWeek
If $BTC can hold here or continue higher into September, the daily Golden Cross will officially confirm.
It has flashed 4 times near the end of bear markets.
3 times, it got the direction right.
Could Bitcoin be setting up for another major trend reversal? 🚀
#KoreaSingleStockLeveragedETFTradingFalls
#VietnamPilotsCryptoAssetMarket
#GoldFalls3.24%ThisWeek
116
·
--
Bullish
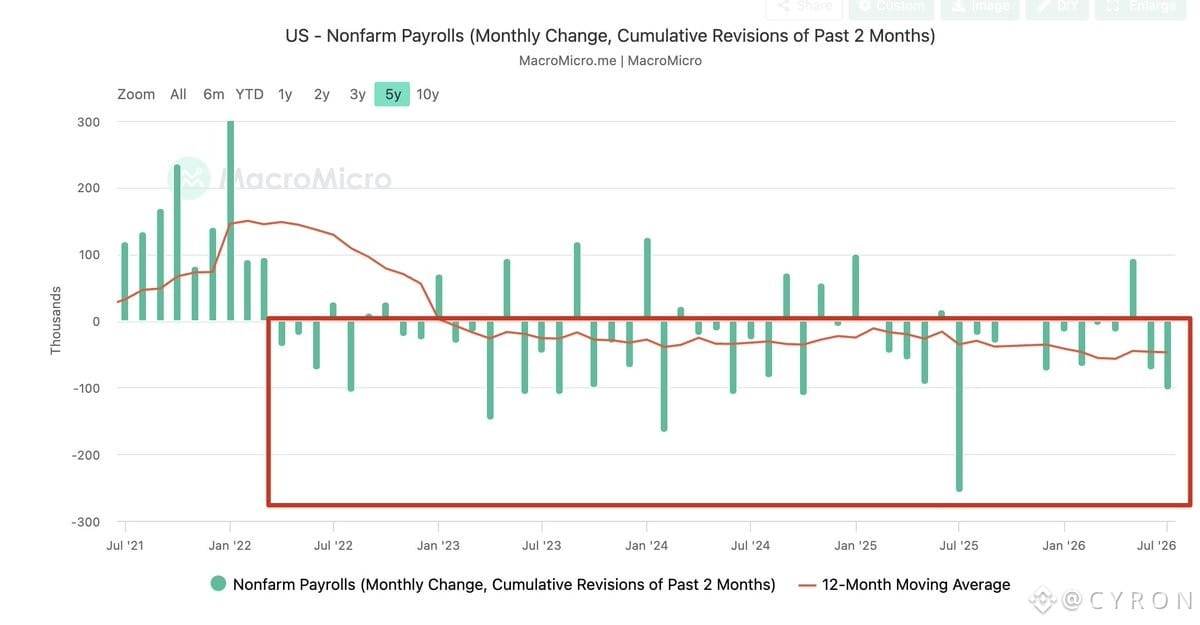
Here's the trend over the past few years.
Non-farm payroll data is always subject to revision because the initial number is only an early estimate.
The revised numbers can show a very different picture.
Since 2022, we've seen a clear pattern of mostly downward revisions.
For example, a report showing +50K jobs could later be revised down to +25K.
That would mean the labor market was weaker than initially reported.
Now, the 2025 annual NFP revision stands at -911K jobs, highlighting just how large these adjustments can be.
So if today's NFP data comes in strong, the market may see less reason for the Fed to cut rates.
That could put pressure on risk assets like $BTC
{spot}(BTCUSDT)
#SOLJumps20%OnTheWeek
#CaliforniaBillWouldBarOfficialMemeCoins
#TRONMainnetActivatesTVMPragueOsaka
Here's the trend over the past few years.
Non-farm payroll data is always subject to revision because the initial number is only an early estimate.
The revised numbers can show a very different picture.
Since 2022, we've seen a clear pattern of mostly downward revisions.
For example, a report showing +50K jobs could later be revised down to +25K.
That would mean the labor market was weaker than initially reported.
Now, the 2025 annual NFP revision stands at -911K jobs, highlighting just how large these adjustments can be.
So if today's NFP data comes in strong, the market may see less reason for the Fed to cut rates.
That could put pressure on risk assets like $BTC
#SOLJumps20%OnTheWeek
#CaliforniaBillWouldBarOfficialMemeCoins
#TRONMainnetActivatesTVMPragueOsaka
Non-farm payroll data is always subject to revision because the initial number is only an early estimate.
The revised numbers can show a very different picture.
Since 2022, we've seen a clear pattern of mostly downward revisions.
For example, a report showing +50K jobs could later be revised down to +25K.
That would mean the labor market was weaker than initially reported.
Now, the 2025 annual NFP revision stands at -911K jobs, highlighting just how large these adjustments can be.
So if today's NFP data comes in strong, the market may see less reason for the Fed to cut rates.
That could put pressure on risk assets like $BTC
#SOLJumps20%OnTheWeek
#CaliforniaBillWouldBarOfficialMemeCoins
#TRONMainnetActivatesTVMPragueOsaka
114
·
--
Bullish
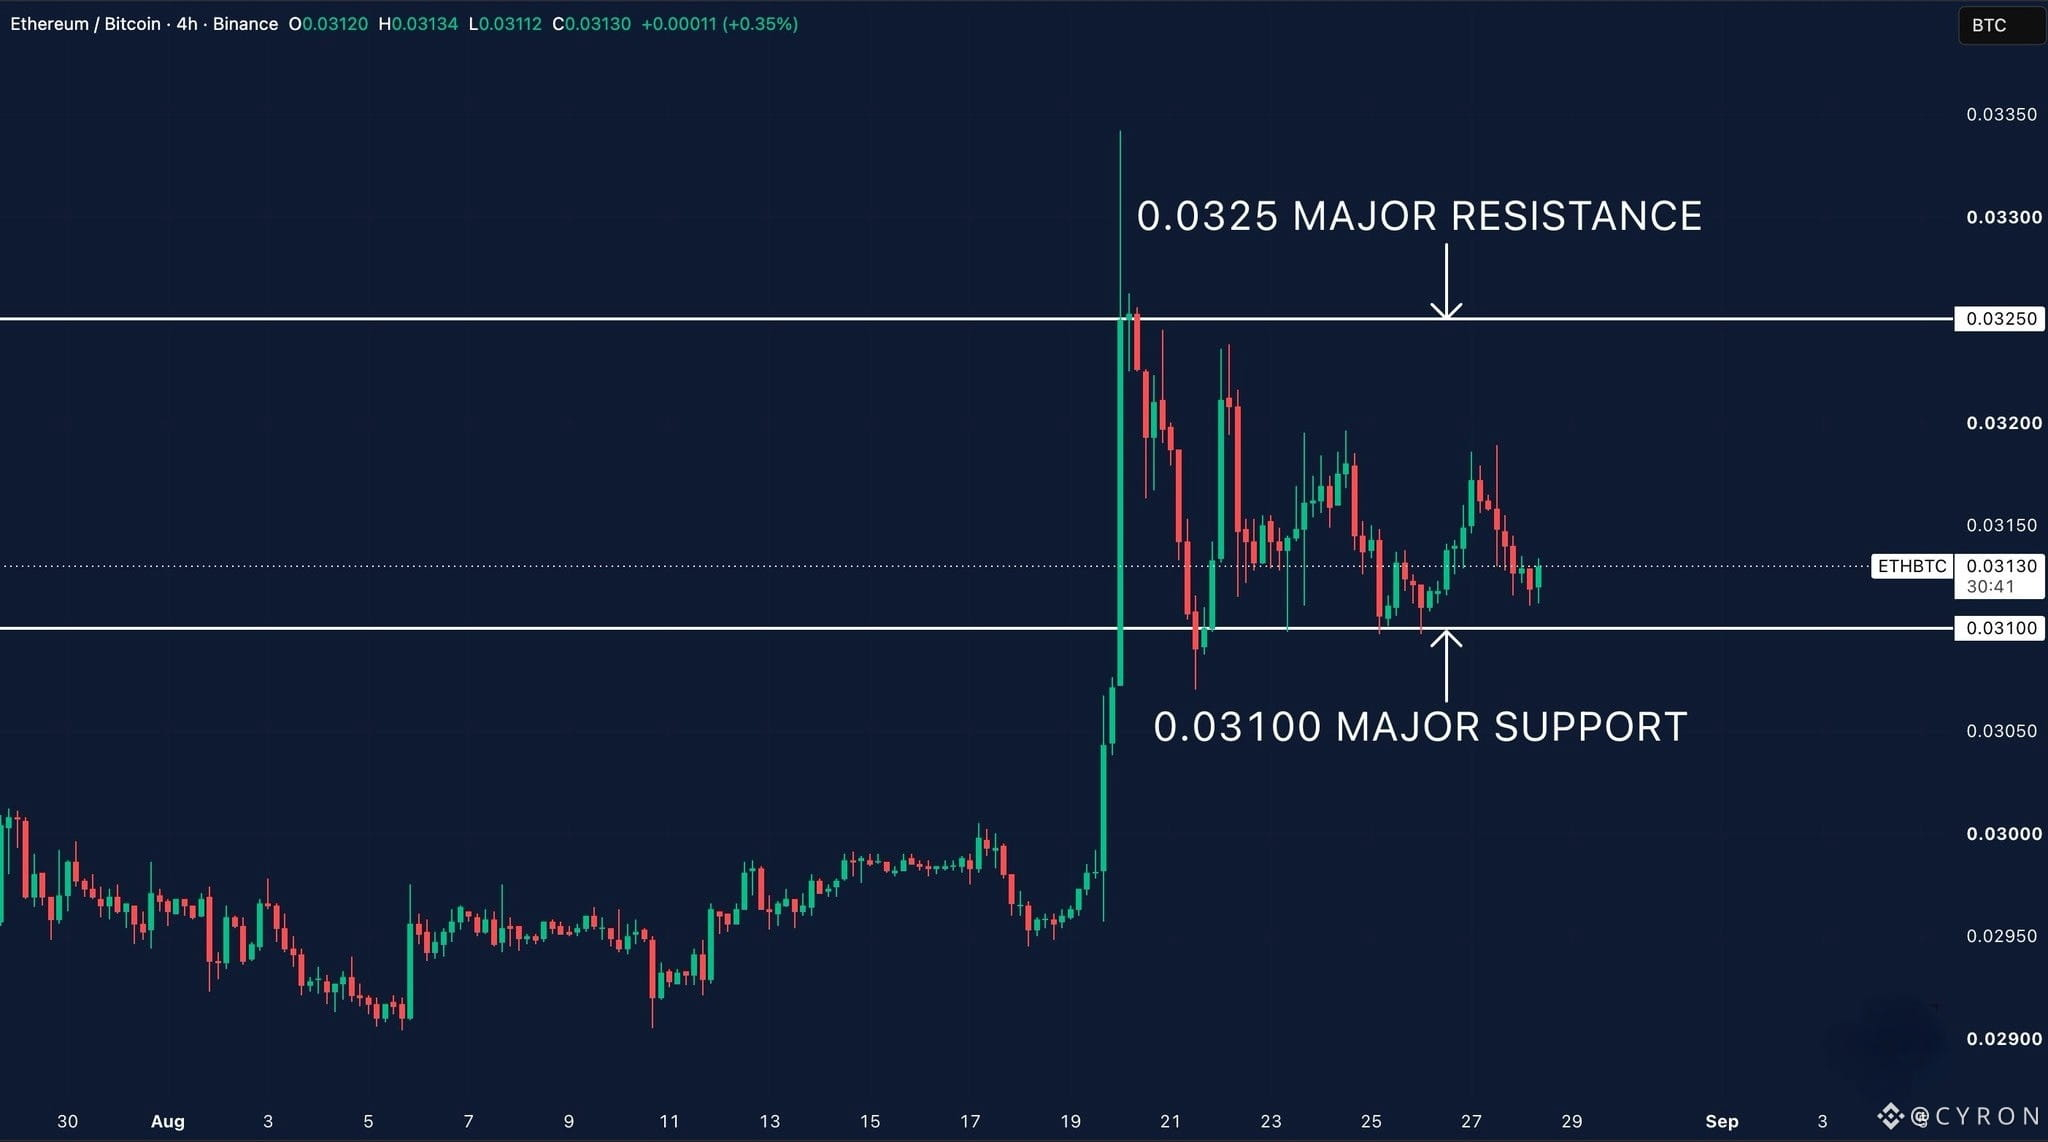
ETH/BTC is holding a level that could matter for the next move.
The 0.03100 support has been tested multiple times, and so far, buyers are defending it.
Hold above here → 0.03250 is next.
Break 0.03250 cleanly → ETH could start showing stronger relative performance against BTC.
Lose 0.03100 → the setup changes.
For now, ETH/BTC is still holding its breakout.
Patience before chasing.
{spot}(ETHUSDT)
{spot}(BTCUSDT)
#GoldRisesAbout14%InAugust
#KospiFallsAsAITradingEuphoriaCools
#TaiwanTAIEXRetakes46500OnChipRally
ETH/BTC is holding a level that could matter for the next move.
The 0.03100 support has been tested multiple times, and so far, buyers are defending it.
Hold above here → 0.03250 is next.
Break 0.03250 cleanly → ETH could start showing stronger relative performance against BTC.
Lose 0.03100 → the setup changes.
For now, ETH/BTC is still holding its breakout.
Patience before chasing.
#GoldRisesAbout14%InAugust
#KospiFallsAsAITradingEuphoriaCools
#TaiwanTAIEXRetakes46500OnChipRally
The 0.03100 support has been tested multiple times, and so far, buyers are defending it.
Hold above here → 0.03250 is next.
Break 0.03250 cleanly → ETH could start showing stronger relative performance against BTC.
Lose 0.03100 → the setup changes.
For now, ETH/BTC is still holding its breakout.
Patience before chasing.
#GoldRisesAbout14%InAugust
#KospiFallsAsAITradingEuphoriaCools
#TaiwanTAIEXRetakes46500OnChipRally
120
·
--
Bearish
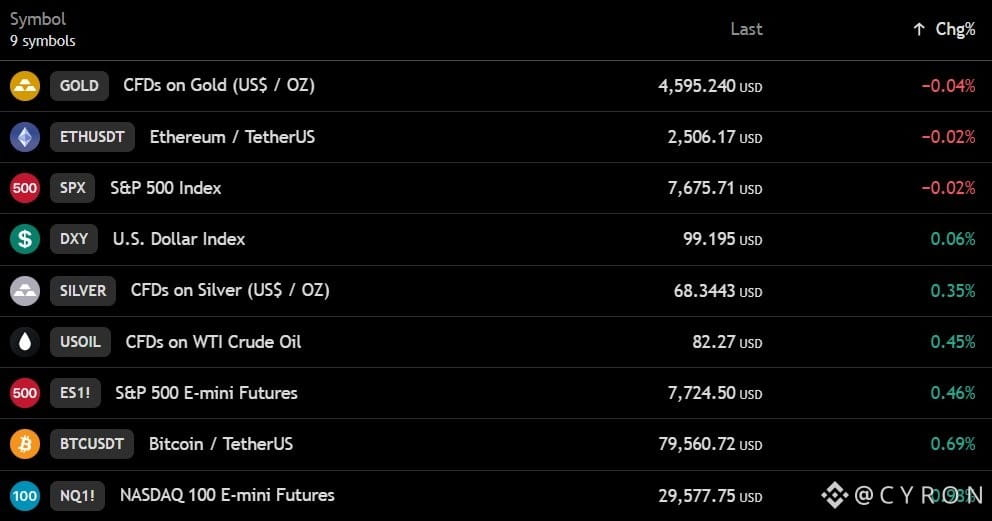
$BTC has dropped below $80,000.
Meanwhile, U.S. stock futures are trading higher, with Oil and the DXY also moving up.
Pre-market update:
▫️ Nasdaq futures: +0.98% 🟠
▫️ S&P 500 futures: +0.46% 🟠
Bitcoin is showing some weakness despite a positive start for broader markets.
{spot}(BTCUSDT)
#KospiClosesAtRecordHigh
#ChinaOpposesUSProposed7.5%Tariff
#BankOfKoreaHikesRatesTo3%
$BTC has dropped below $80,000.
Meanwhile, U.S. stock futures are trading higher, with Oil and the DXY also moving up.
Pre-market update:
▫️ Nasdaq futures: +0.98% 🟠
▫️ S&P 500 futures: +0.46% 🟠
Bitcoin is showing some weakness despite a positive start for broader markets.
#KospiClosesAtRecordHigh
#ChinaOpposesUSProposed7.5%Tariff
#BankOfKoreaHikesRatesTo3%
Meanwhile, U.S. stock futures are trading higher, with Oil and the DXY also moving up.
Pre-market update:
▫️ Nasdaq futures: +0.98% 🟠
▫️ S&P 500 futures: +0.46% 🟠
Bitcoin is showing some weakness despite a positive start for broader markets.
#KospiClosesAtRecordHigh
#ChinaOpposesUSProposed7.5%Tariff
#BankOfKoreaHikesRatesTo3%
2
325
·
--
Bullish
Went through the CreatorPad task on @Dusk_Foundation this week and the thing that stuck with me wasn't in the task brief at all, it was that the $DUSK bridge has now been paused for over ten days and nobody at Dusk seems in a rush to reopen it. #dusk
Quick context for anyone who missed it: on August 16 the team flagged unusual activity on a wallet used for bridge operations, recycled the affected addresses, and pushed a recipient blocklist through the Web Wallet after part of the flow touched Binance. DuskDS mainnet itself never stopped producing blocks. That's the part I kept coming back to.
I'd assumed a privacy-focused L1 concentrated its risk in one place, the base layer. Watching the chain run clean while the bridge sat frozen made it obvious that's not how the trust boundaries actually split here. The bridge is its own liability, held to its own timeline, independent of consensus health.
Binance users were arguably protected first, just by the blocklist existing before withdrawals could route through. Everyone else is still waiting on "temporarily."
Not sure what the actual threshold is before "temporary" starts meaning something else.
{spot}(DUSKUSDT)
{spot}(BMTUSDT)
{spot}(EDENUSDT)
Which matters more here?
Went through the CreatorPad task on @Dusk this week and the thing that stuck with me wasn't in the task brief at all, it was that the $DUSK bridge has now been paused for over ten days and nobody at Dusk seems in a rush to reopen it. #dusk
Quick context for anyone who missed it: on August 16 the team flagged unusual activity on a wallet used for bridge operations, recycled the affected addresses, and pushed a recipient blocklist through the Web Wallet after part of the flow touched Binance. DuskDS mainnet itself never stopped producing blocks. That's the part I kept coming back to.
I'd assumed a privacy-focused L1 concentrated its risk in one place, the base layer. Watching the chain run clean while the bridge sat frozen made it obvious that's not how the trust boundaries actually split here. The bridge is its own liability, held to its own timeline, independent of consensus health.
Binance users were arguably protected first, just by the blocklist existing before withdrawals could route through. Everyone else is still waiting on "temporarily."
Not sure what the actual threshold is before "temporary" starts meaning something else.
Which matters more here?
Quick context for anyone who missed it: on August 16 the team flagged unusual activity on a wallet used for bridge operations, recycled the affected addresses, and pushed a recipient blocklist through the Web Wallet after part of the flow touched Binance. DuskDS mainnet itself never stopped producing blocks. That's the part I kept coming back to.
I'd assumed a privacy-focused L1 concentrated its risk in one place, the base layer. Watching the chain run clean while the bridge sat frozen made it obvious that's not how the trust boundaries actually split here. The bridge is its own liability, held to its own timeline, independent of consensus health.
Binance users were arguably protected first, just by the blocklist existing before withdrawals could route through. Everyone else is still waiting on "temporarily."
Not sure what the actual threshold is before "temporary" starts meaning something else.
Which matters more here?
🟢 Mainnet's clean uptime
100%
🔴 Bridge still closed
0%
⚖️ Both equally
0%
🤷 Too early to say
0%
1 votes • Voting closed
1
1
192
·
--
Bullish
Ran a small transfer through Dusk's Web Wallet earlier this week while wrapping up a CreatorPad task, and got stopped mid-flow by a blocklist warning I wasn't expecting. Nothing dramatic, just a red flag before the transaction would submit. For a chain built around $DUSK 's selective-disclosure privacy model, #dusk , @Dusk_Foundation , that felt like an odd thing to run into.
Turns out the warning traces back to the recipient blocklist the team shipped to the Web Wallet after the mid-August incident involving a compromised bridge operations wallet. It screens outgoing transfers against known flagged addresses before you can send.
I'd assumed privacy-first meant fewer checkpoints, not more. Watching it actually fire on a real attempt changed that a little. The mechanism only works if someone is maintaining and updating that list in near real time, which means there's a curatorial layer sitting quietly underneath the "confidential by default" pitch.
Not saying that's wrong, just noticing it. Selective disclosure and address screening aren't the same thing, but they're now living in the same wallet. Still working out how comfortable I am with that, and who exactly decides what gets added to the list going forward.
{spot}(DUSKUSDT)
{spot}(ONGUSDT)
{spot}(JASMYUSDT)
Which part of this stood out most to you? 👀
Ran a small transfer through Dusk's Web Wallet earlier this week while wrapping up a CreatorPad task, and got stopped mid-flow by a blocklist warning I wasn't expecting. Nothing dramatic, just a red flag before the transaction would submit. For a chain built around $DUSK 's selective-disclosure privacy model, #dusk , @Dusk , that felt like an odd thing to run into.
Turns out the warning traces back to the recipient blocklist the team shipped to the Web Wallet after the mid-August incident involving a compromised bridge operations wallet. It screens outgoing transfers against known flagged addresses before you can send.
I'd assumed privacy-first meant fewer checkpoints, not more. Watching it actually fire on a real attempt changed that a little. The mechanism only works if someone is maintaining and updating that list in near real time, which means there's a curatorial layer sitting quietly underneath the "confidential by default" pitch.
Not saying that's wrong, just noticing it. Selective disclosure and address screening aren't the same thing, but they're now living in the same wallet. Still working out how comfortable I am with that, and who exactly decides what gets added to the list going forward.
Which part of this stood out most to you? 👀
Turns out the warning traces back to the recipient blocklist the team shipped to the Web Wallet after the mid-August incident involving a compromised bridge operations wallet. It screens outgoing transfers against known flagged addresses before you can send.
I'd assumed privacy-first meant fewer checkpoints, not more. Watching it actually fire on a real attempt changed that a little. The mechanism only works if someone is maintaining and updating that list in near real time, which means there's a curatorial layer sitting quietly underneath the "confidential by default" pitch.
Not saying that's wrong, just noticing it. Selective disclosure and address screening aren't the same thing, but they're now living in the same wallet. Still working out how comfortable I am with that, and who exactly decides what gets added to the list going forward.
Which part of this stood out most to you? 👀
🚫 The blocklist itself
50%
🔑 Who maintains the list
50%
⚖️ Privacy vs. gatekeeping
0%
💭 Something else
0%
2 votes • Voting closed
1
1
193
·
--
Bullish
Checked the Dusk bridge status page again this week and it's still showing paused, same as it's been since the August 16th incident where the team flagged suspicious activity on a wallet used for bridge operations. That's the detail that stuck with me while wrapping up this CreatorPad task on @Dusk_Foundation , $DUSK , #dusk : nine-plus days on, the addresses are recycled, the blocklist is live, but the bridge itself hasn't come back online.
The official line was clean, not a protocol-level issue, DuskDS kept producing blocks normally, no user funds affected. And technically that's true. But I went in assuming "not a protocol bug" meant "quick fix." It didn't. Operational infrastructure managed by a team, even on a chain built around deterministic settlement and audit-grade privacy, still moves on human timelines once something touches a centralized flow.
What struck me more than the incident itself was the gap between how confidently reassuring the messaging is and how long the actual remediation is taking. Those two things aren't necessarily in tension, but they read differently side by side.
Not sure yet whether this is just careful process or something more structural about how bridges get treated post-incident. Watching to see when it actually reopens.
{spot}(DUSKUSDT)
{spot}(ZROUSDT)
{spot}(ENAUSDT)
Which part stands out to you? 🤔
Checked the Dusk bridge status page again this week and it's still showing paused, same as it's been since the August 16th incident where the team flagged suspicious activity on a wallet used for bridge operations. That's the detail that stuck with me while wrapping up this CreatorPad task on @Dusk , $DUSK , #dusk : nine-plus days on, the addresses are recycled, the blocklist is live, but the bridge itself hasn't come back online.
The official line was clean, not a protocol-level issue, DuskDS kept producing blocks normally, no user funds affected. And technically that's true. But I went in assuming "not a protocol bug" meant "quick fix." It didn't. Operational infrastructure managed by a team, even on a chain built around deterministic settlement and audit-grade privacy, still moves on human timelines once something touches a centralized flow.
What struck me more than the incident itself was the gap between how confidently reassuring the messaging is and how long the actual remediation is taking. Those two things aren't necessarily in tension, but they read differently side by side.
Not sure yet whether this is just careful process or something more structural about how bridges get treated post-incident. Watching to see when it actually reopens.
Which part stands out to you? 🤔
The official line was clean, not a protocol-level issue, DuskDS kept producing blocks normally, no user funds affected. And technically that's true. But I went in assuming "not a protocol bug" meant "quick fix." It didn't. Operational infrastructure managed by a team, even on a chain built around deterministic settlement and audit-grade privacy, still moves on human timelines once something touches a centralized flow.
What struck me more than the incident itself was the gap between how confidently reassuring the messaging is and how long the actual remediation is taking. Those two things aren't necessarily in tension, but they read differently side by side.
Not sure yet whether this is just careful process or something more structural about how bridges get treated post-incident. Watching to see when it actually reopens.
Which part stands out to you? 🤔
🛠️ The framing
50%
⏳ The timeline
0%
🔐 Wallet risk
0%
🤷 Just normal caution
50%
2 votes • Voting closed
4
6
307
·
--
Bullish
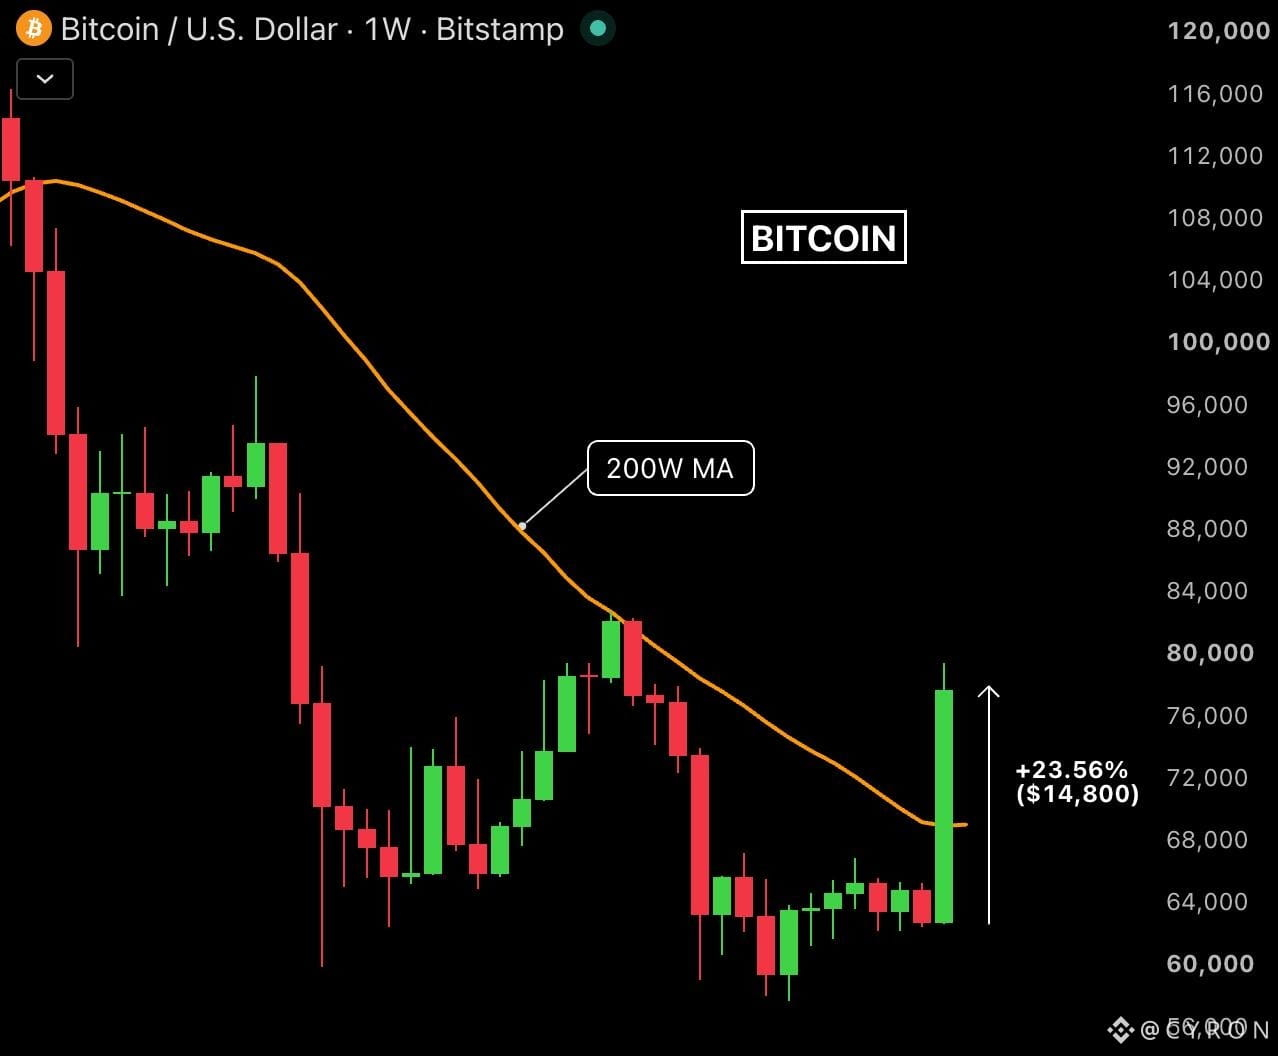
🚨 BREAKING:
Bitcoin just printed its largest weekly candle since March 2023.
$BTC gained 23.56%, adding roughly $14,800 in just one week.
That's a massive move for Bitcoin in such a short period.
The momentum is back. 🚀
{spot}(BTCUSDT)
#BitcoinStrongestWeekSinceMarch2023
#CanadaUSTradeTalksCollapse
🚨 BREAKING:
Bitcoin just printed its largest weekly candle since March 2023.
$BTC gained 23.56%, adding roughly $14,800 in just one week.
That's a massive move for Bitcoin in such a short period.
The momentum is back. 🚀
#BitcoinStrongestWeekSinceMarch2023
#CanadaUSTradeTalksCollapse
Bitcoin just printed its largest weekly candle since March 2023.
$BTC gained 23.56%, adding roughly $14,800 in just one week.
That's a massive move for Bitcoin in such a short period.
The momentum is back. 🚀
#BitcoinStrongestWeekSinceMarch2023
#CanadaUSTradeTalksCollapse
2
122
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
AIStocksWhatNext
415,104 views
3,205 Discussing
Share & Win Traffic Reward in our Trending Hashtag Campaign
✨Topic: What Other Investment Opportunities Remain as AI Stocks Keep Rising?
👉How to Join:
Publish a short post or article with hashtag #AIStocksWhatNext
Share whether you’re bullish or bearish, and post your AI stock holdings or trade — using the trade widget may improve your eligibility.
You can also strengthen your post by sharing data or charts, and avoiding AI-generated images.
✍️Create content based on the below angles:
- Nvidia says chip sales will double next year, and top AI companies keep hitting record revenue, the compute spend behind it is just as staggering. Is AI demand really taking off? And how long can it last? AI stocks are up across the board. Is this a real breakout, or just a short-term bounce?
- Industry leaders are calling to slow down AI development, while Trump plans to build an “AI Force”, claiming AI could account for 25% of U.S. GDP in the future. Whose side are you on? Will state-level backing be a long-term win for AI stocks?
- Are you buying AI stocks? Share your AI-related trade/holdings with our trade sharing widget.
⏰Campaign Period:
- 2026-09-22 7:00 - 2026-09-24 4:00 UTC
🎁Reward:
- Qualified posts that comply with the above guidelines and contain more than 100 words will be reviewed and may receive a random traffic boost of 500 to 3,000 views. You will receive a notification from your feed secretary if your post is selected.
- Get a chance to have your article featured on Binance Square Official
Need ideas for your post? Visit the topic page #AIStocksWhatNext or the Square Guide on How to Post for Better Reach.
Binance Square Official
·390 Likes
·967.3k views
BitwiseNEARStakingETPAssetsTop$100M
1,467 views
29 Discussing
BitcoinBreaksAboveMayHighNears$86K
18,100 views
214 Discussing