🚨The Crypto Job Interview Trap...
#HackerAlert
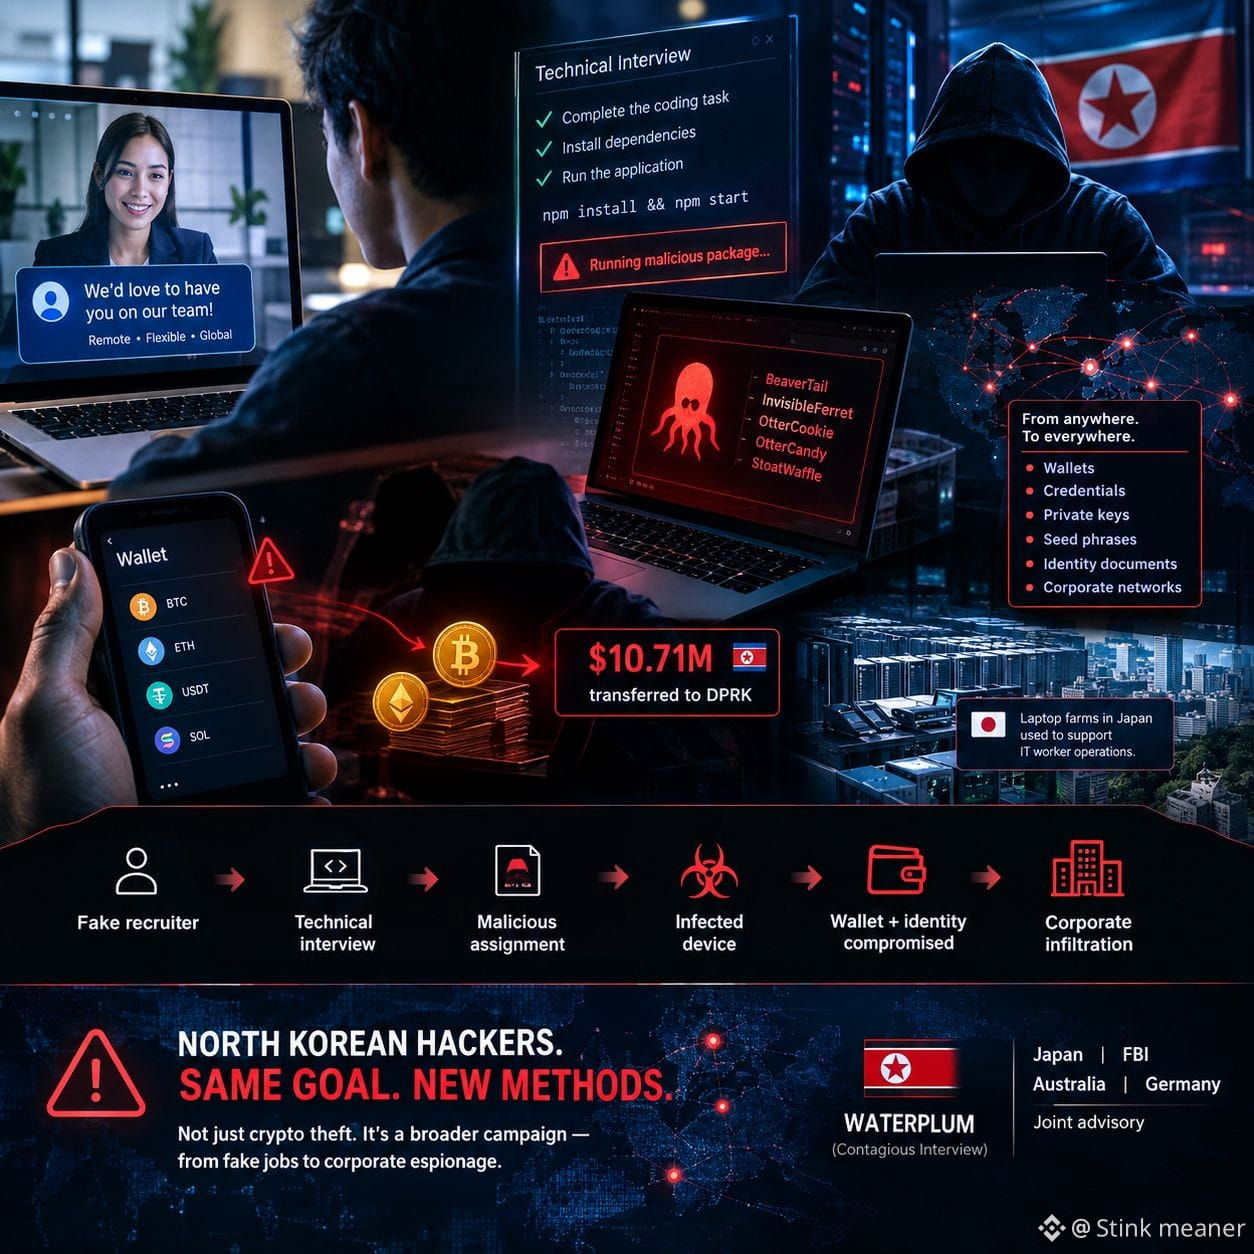
Japan, the FBI, Australia and Germany have just attributed a global campaign to North Korean-linked WaterPlum, also known as Contagious Interview.
The numbers are uncomfortable:
30,000+ devices infected
100+ countries affected
7,000+ crypto wallets compromised for funds or credentials
¥1.7B ($10.71M) in crypto transferred to the DPRK
The targets weren't random users.
They included developers, engineers, web designers and crypto/Web3 professionals.
The attack chain is where this gets interesting:
fake recruiter
→ technical interview
→ malicious coding assignment
→ NPM/developer-platform malware
→ backdoor
→ wallet credentials + private keys + seed phrases
The attackers also harvested browser credentials, keystrokes, screenshots and identity documents.
And the wallet theft may only be the first objective.
The joint advisory says compromised machines can provide access into the companies where those developers work — creating opportunities for IP theft, espionage and lateral movement.
That's the bigger loop:
fake job → infected developer → compromised wallet → compromised identity → potential corporate access.
Japan also says investigators dismantled a domestic “laptop farm” connected to North Korean IT-worker operations, showing how the recruitment/infiltration ecosystem can extend beyond a single phishing campaign.
North Korea's crypto operation is already measured in billions: Chainalysis estimated $2.02B stolen in 2025 alone.
So this isn't just another wallet-draining story.
For crypto companies, the attack surface may begin before an employee even gets hired.
And for developers:
a coding test is no longer automatically a safe file to run.
$BTC $ETH $BNB
#BOJRaisesRatesTo31YearHigh #Web3 #BuffettStepsDownAsBerkshireChairman #BinanceSquare
#HackerAlert
Japan, the FBI, Australia and Germany have just attributed a global campaign to North Korean-linked WaterPlum, also known as Contagious Interview.
The numbers are uncomfortable:
30,000+ devices infected
100+ countries affected
7,000+ crypto wallets compromised for funds or credentials
¥1.7B ($10.71M) in crypto transferred to the DPRK
The targets weren't random users.
They included developers, engineers, web designers and crypto/Web3 professionals.
The attack chain is where this gets interesting:
fake recruiter
→ technical interview
→ malicious coding assignment
→ NPM/developer-platform malware
→ backdoor
→ wallet credentials + private keys + seed phrases
The attackers also harvested browser credentials, keystrokes, screenshots and identity documents.
And the wallet theft may only be the first objective.
The joint advisory says compromised machines can provide access into the companies where those developers work — creating opportunities for IP theft, espionage and lateral movement.
That's the bigger loop:
fake job → infected developer → compromised wallet → compromised identity → potential corporate access.
Japan also says investigators dismantled a domestic “laptop farm” connected to North Korean IT-worker operations, showing how the recruitment/infiltration ecosystem can extend beyond a single phishing campaign.
North Korea's crypto operation is already measured in billions: Chainalysis estimated $2.02B stolen in 2025 alone.
So this isn't just another wallet-draining story.
For crypto companies, the attack surface may begin before an employee even gets hired.
And for developers:
a coding test is no longer automatically a safe file to run.
$BTC $ETH $BNB
#BOJRaisesRatesTo31YearHigh #Web3 #BuffettStepsDownAsBerkshireChairman #BinanceSquare