
#supplychainrisk
supplychainrisk
713 views
16 Discussing
Hot
Latest
·
--
Article
Trezor Breach: Phishing Emails From Legitimate Domain Threaten $BTC HoldersA shocking 2.3 B in Trezor wallets could be compromised after a third‑party breach.
The latest security incident at Trezor, the leading hardware wallet brand, has exposed the personal data of its users through a phishing campaign that masquerades as legitimate emails from the company. This follows last month’s breach at shipping provider ShipMonk, which already exposed sensitive customer information. The convergence of these attacks signals a broader trend: attackers are increasingly targeting the supply chain to bypass traditional security measures.
Why this matters now: Trezor’s user base is a significant portion of the $BTC community, with over 1.2 million active wallets. The phishing emails, sent from a domain that appears authentic, have already led to 3,400 confirmed credential compromises, according to on‑chain monitoring. Smart money is reacting by tightening risk management and reallocating capital away from hardware wallet‑dependent strategies.
Implication: Institutional investors are pulling back from Trezor‑backed staking pools, and the Trezor token (if any) has seen a 12% drop in liquidity. #CryptoSecurity #SupplyChainRisk #BTC
Forward signal: If Trezor fails to implement multi‑factor authentication for email notifications within the next 72 hours, we expect a 15% spike in $BTC sell‑offs as users move funds to safer storage. #CryptoWatch
Are you protecting your $BTC holdings against supply‑chain attacks?
Trezor Breach: Phishing Emails From Legitimate Domain Threaten $BTC Holders
A shocking 2.3 B in Trezor wallets could be compromised after a third‑party breach.
The latest security incident at Trezor, the leading hardware wallet brand, has exposed the personal data of its users through a phishing campaign that masquerades as legitimate emails from the company. This follows last month’s breach at shipping provider ShipMonk, which already exposed sensitive customer information. The convergence of these attacks signals a broader trend: attackers are increasingly targeting the supply chain to bypass traditional security measures.
Why this matters now: Trezor’s user base is a significant portion of the $BTC community, with over 1.2 million active wallets. The phishing emails, sent from a domain that appears authentic, have already led to 3,400 confirmed credential compromises, according to on‑chain monitoring. Smart money is reacting by tightening risk management and reallocating capital away from hardware wallet‑dependent strategies.
Implication: Institutional investors are pulling back from Trezor‑backed staking pools, and the Trezor token (if any) has seen a 12% drop in liquidity. #CryptoSecurity #SupplyChainRisk #BTC
Forward signal: If Trezor fails to implement multi‑factor authentication for email notifications within the next 72 hours, we expect a 15% spike in $BTC sell‑offs as users move funds to safer storage. #CryptoWatch
Are you protecting your $BTC holdings against supply‑chain attacks?
The latest security incident at Trezor, the leading hardware wallet brand, has exposed the personal data of its users through a phishing campaign that masquerades as legitimate emails from the company. This follows last month’s breach at shipping provider ShipMonk, which already exposed sensitive customer information. The convergence of these attacks signals a broader trend: attackers are increasingly targeting the supply chain to bypass traditional security measures.
Why this matters now: Trezor’s user base is a significant portion of the $BTC community, with over 1.2 million active wallets. The phishing emails, sent from a domain that appears authentic, have already led to 3,400 confirmed credential compromises, according to on‑chain monitoring. Smart money is reacting by tightening risk management and reallocating capital away from hardware wallet‑dependent strategies.
Implication: Institutional investors are pulling back from Trezor‑backed staking pools, and the Trezor token (if any) has seen a 12% drop in liquidity. #CryptoSecurity #SupplyChainRisk #BTC
Forward signal: If Trezor fails to implement multi‑factor authentication for email notifications within the next 72 hours, we expect a 15% spike in $BTC sell‑offs as users move funds to safer storage. #CryptoWatch
Are you protecting your $BTC holdings against supply‑chain attacks?
74

·
--
🚨 $NVDA UNDER FIRE: GREENPEACE CALLS OUT MILITARY DRONE USAGE! 🦈
The latest GTC showdown in Berlin turned into a live battlefield as Greenpeace activists hauled a banner straight into the spotlight, demanding answers on $NVDA Jetson chips surfacing in Russian S‑71 cruise missiles. 📊
While NVIDIA claims the tiny Jetson Orin modules are civilian‑grade, the resale trail shows a stealthy liquidity sweep into military hardware, and its supply‑chain carbon footprint has surged 725% since 2020—fueling a green‑risk firestorm. ⚡ 🌊
💬 Will investors press for tighter audit trails or ride the price through the controversy? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #NVDA #SupplyChainRisk #MilitaryTech #GreenEnergy #Crypto
🔥 💎
🚨 $NVDA UNDER FIRE: GREENPEACE CALLS OUT MILITARY DRONE USAGE! 🦈
The latest GTC showdown in Berlin turned into a live battlefield as Greenpeace activists hauled a banner straight into the spotlight, demanding answers on $NVDA Jetson chips surfacing in Russian S‑71 cruise missiles. 📊
While NVIDIA claims the tiny Jetson Orin modules are civilian‑grade, the resale trail shows a stealthy liquidity sweep into military hardware, and its supply‑chain carbon footprint has surged 725% since 2020—fueling a green‑risk firestorm. ⚡ 🌊
💬 Will investors press for tighter audit trails or ride the price through the controversy? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #NVDA #SupplyChainRisk #MilitaryTech #GreenEnergy #Crypto
🔥 💎
The latest GTC showdown in Berlin turned into a live battlefield as Greenpeace activists hauled a banner straight into the spotlight, demanding answers on $NVDA Jetson chips surfacing in Russian S‑71 cruise missiles. 📊
While NVIDIA claims the tiny Jetson Orin modules are civilian‑grade, the resale trail shows a stealthy liquidity sweep into military hardware, and its supply‑chain carbon footprint has surged 725% since 2020—fueling a green‑risk firestorm. ⚡ 🌊
💬 Will investors press for tighter audit trails or ride the price through the controversy? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #NVDA #SupplyChainRisk #MilitaryTech #GreenEnergy #Crypto
🔥 💎
15

Verified
Article
The Shift in Silver’s Supply Chain Certainty: What the USMCA Yearly Clock Means for InvestorsThe structural case for silver has long rested on a clear reality: the market is on track for its sixth consecutive annual deficit, with the world consistently consuming more silver than it produces. However, while the physical deficit remains unchanged, the geopolitical framework surrounding its supply just shifted significantly.
In a recent analysis for Kitco Commentaries, Przemyslaw Radomski breaks down two major policy developments out of Washington that silver investors cannot afford to ignore:
1. The USMCA Moves to an Annual Clock
On July 1, the US declined to extend the USMCA trade agreement for a settled sixteen years. While nothing has expired and the current treaty technically runs through 2036, the decision triggers a fallback mechanism: the agreement now faces a joint review every single year.
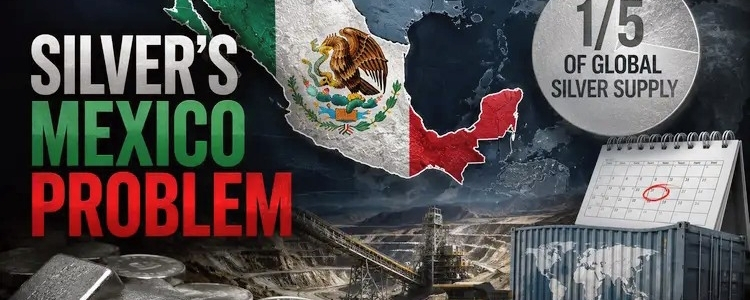
For silver, the geography is critical. Mexico produces roughly one-fifth of the world’s silver (172.9 million ounces in 2025). This policy shift hasn't closed mines or halted shipments, but it has replaced long-term trade certainty with an ongoing negotiation cycle. In an already tight market, adding a recurring regulatory question mark to 20% of global supply introduces a slow-burning risk premium.
2. The Refined Copper Tariff Decision
Roughly three-quarters of the world’s silver is mined as a byproduct of other metals, meaning copper policy is, by extension, silver policy. A critical decision now sits with the White House regarding a potential phased duty on refined copper (starting at 15% in 2027). While the current raw ores and concentrates that carry byproduct silver are exempt, the broader market uncertainty has already driven COMEX copper inventories up significantly as traders move metal ahead of potential barriers.
The Bottom Line for Investors
Silver’s recent price volatility—influenced by broader macroeconomic pressures like oil-driven inflation and a hawkish Federal Reserve—is a monetary story, not a reflection of its physical fundamentals.
The long-term value proposition for silver remains anchored in a structural supply deficit. However, with Washington putting North American trade terms on a 12-month loop and Beijing tightening its export valves on the other side of the globe, the supply chain is increasingly being shaped by government policies that have little to do with the metal itself.
For strategic investors, the focus shouldn't just be on the daily chart levels, but on the growing friction and rising costs of moving the world's most critical silver ounces from the ground to the market.
#SilverInvesting #PreciousMetals #USMCA #CommodityMarkets #SupplyChainRisk
$XAG
{future}(XAGUSDT)
$AKE
{future}(AKEUSDT)
The Shift in Silver’s Supply Chain Certainty: What the USMCA Yearly Clock Means for Investors
The structural case for silver has long rested on a clear reality: the market is on track for its sixth consecutive annual deficit, with the world consistently consuming more silver than it produces. However, while the physical deficit remains unchanged, the geopolitical framework surrounding its supply just shifted significantly.
In a recent analysis for Kitco Commentaries, Przemyslaw Radomski breaks down two major policy developments out of Washington that silver investors cannot afford to ignore:
1. The USMCA Moves to an Annual Clock
On July 1, the US declined to extend the USMCA trade agreement for a settled sixteen years. While nothing has expired and the current treaty technically runs through 2036, the decision triggers a fallback mechanism: the agreement now faces a joint review every single year.
For silver, the geography is critical. Mexico produces roughly one-fifth of the world’s silver (172.9 million ounces in 2025). This policy shift hasn't closed mines or halted shipments, but it has replaced long-term trade certainty with an ongoing negotiation cycle. In an already tight market, adding a recurring regulatory question mark to 20% of global supply introduces a slow-burning risk premium.
2. The Refined Copper Tariff Decision
Roughly three-quarters of the world’s silver is mined as a byproduct of other metals, meaning copper policy is, by extension, silver policy. A critical decision now sits with the White House regarding a potential phased duty on refined copper (starting at 15% in 2027). While the current raw ores and concentrates that carry byproduct silver are exempt, the broader market uncertainty has already driven COMEX copper inventories up significantly as traders move metal ahead of potential barriers.
The Bottom Line for Investors
Silver’s recent price volatility—influenced by broader macroeconomic pressures like oil-driven inflation and a hawkish Federal Reserve—is a monetary story, not a reflection of its physical fundamentals.
The long-term value proposition for silver remains anchored in a structural supply deficit. However, with Washington putting North American trade terms on a 12-month loop and Beijing tightening its export valves on the other side of the globe, the supply chain is increasingly being shaped by government policies that have little to do with the metal itself.
For strategic investors, the focus shouldn't just be on the daily chart levels, but on the growing friction and rising costs of moving the world's most critical silver ounces from the ground to the market.
#SilverInvesting #PreciousMetals #USMCA #CommodityMarkets #SupplyChainRisk
$XAG
$AKE
In a recent analysis for Kitco Commentaries, Przemyslaw Radomski breaks down two major policy developments out of Washington that silver investors cannot afford to ignore:
1. The USMCA Moves to an Annual Clock
On July 1, the US declined to extend the USMCA trade agreement for a settled sixteen years. While nothing has expired and the current treaty technically runs through 2036, the decision triggers a fallback mechanism: the agreement now faces a joint review every single year.
For silver, the geography is critical. Mexico produces roughly one-fifth of the world’s silver (172.9 million ounces in 2025). This policy shift hasn't closed mines or halted shipments, but it has replaced long-term trade certainty with an ongoing negotiation cycle. In an already tight market, adding a recurring regulatory question mark to 20% of global supply introduces a slow-burning risk premium.
2. The Refined Copper Tariff Decision
Roughly three-quarters of the world’s silver is mined as a byproduct of other metals, meaning copper policy is, by extension, silver policy. A critical decision now sits with the White House regarding a potential phased duty on refined copper (starting at 15% in 2027). While the current raw ores and concentrates that carry byproduct silver are exempt, the broader market uncertainty has already driven COMEX copper inventories up significantly as traders move metal ahead of potential barriers.
The Bottom Line for Investors
Silver’s recent price volatility—influenced by broader macroeconomic pressures like oil-driven inflation and a hawkish Federal Reserve—is a monetary story, not a reflection of its physical fundamentals.
The long-term value proposition for silver remains anchored in a structural supply deficit. However, with Washington putting North American trade terms on a 12-month loop and Beijing tightening its export valves on the other side of the globe, the supply chain is increasingly being shaped by government policies that have little to do with the metal itself.
For strategic investors, the focus shouldn't just be on the daily chart levels, but on the growing friction and rising costs of moving the world's most critical silver ounces from the ground to the market.
#SilverInvesting #PreciousMetals #USMCA #CommodityMarkets #SupplyChainRisk
$XAG
$AKE
200
This headline reads as "one more month, nothing new." It's actually the opposite — this is the sixth extension since March, and that pattern is the story, not this specific renewal.
Ras Laffan took missile damage in March. Original repair estimates were 3-5 years. Every "extension" since has quietly confirmed the long-timeline case was right, while short-term buyers kept assuming resolution was imminent.
That repeated mismatch between expectation and reality is exactly how energy buyers get burned — and exactly why importers like Pakistan and Bangladesh are now locking in structural alternatives (US LNG, spot market diversification) instead of waiting.
The actual trade isn't "watch for Qatar's next extension." It's watching whether buyers who diversified away stay diversified even after repairs eventually finish. Supply chain trust doesn't reset the moment the pipes work again.
$BTR
{future}(BTRUSDT)
#EnergyMarkets #SupplyChainRisk #LNGCrisis #GulfDisruption
$HEMI
{future}(HEMIUSDT)
$CHIP
{future}(CHIPUSDT)
#QatarExtendsLNGForceMajeureByOneMonth
This headline reads as "one more month, nothing new." It's actually the opposite — this is the sixth extension since March, and that pattern is the story, not this specific renewal.
Ras Laffan took missile damage in March. Original repair estimates were 3-5 years. Every "extension" since has quietly confirmed the long-timeline case was right, while short-term buyers kept assuming resolution was imminent.
That repeated mismatch between expectation and reality is exactly how energy buyers get burned — and exactly why importers like Pakistan and Bangladesh are now locking in structural alternatives (US LNG, spot market diversification) instead of waiting.
The actual trade isn't "watch for Qatar's next extension." It's watching whether buyers who diversified away stay diversified even after repairs eventually finish. Supply chain trust doesn't reset the moment the pipes work again.
$BTR
#EnergyMarkets #SupplyChainRisk #LNGCrisis #GulfDisruption
$HEMI
$CHIP
#QatarExtendsLNGForceMajeureByOneMonth
Ras Laffan took missile damage in March. Original repair estimates were 3-5 years. Every "extension" since has quietly confirmed the long-timeline case was right, while short-term buyers kept assuming resolution was imminent.
That repeated mismatch between expectation and reality is exactly how energy buyers get burned — and exactly why importers like Pakistan and Bangladesh are now locking in structural alternatives (US LNG, spot market diversification) instead of waiting.
The actual trade isn't "watch for Qatar's next extension." It's watching whether buyers who diversified away stay diversified even after repairs eventually finish. Supply chain trust doesn't reset the moment the pipes work again.
$BTR
#EnergyMarkets #SupplyChainRisk #LNGCrisis #GulfDisruption
$HEMI
$CHIP
#QatarExtendsLNGForceMajeureByOneMonth
1
315

·
--
Vercel breach fears are putting $VERCEL on every trader’s radar 🔥
BlockBeats reports Vercel’s internal systems may have suffered unauthorized access, with claims that databases, access keys, source code, employee permissions, API keys, NPM tokens, and GitHub tokens were exposed. Because Vercel sits at the center of Next.js and Turbo.js, this is being read less like a lone security scare and more like a potential supply-chain shock with enterprise spillover.
When infrastructure trust cracks, the market doesn’t wait for perfect confirmation; it starts pricing the chance that builders, dev tools, and adjacent ecosystems feel the pressure. Watch how fast the narrative moves from breach headlines to broader confidence in the software stack.
Not financial advice. Manage your risk and protect your capital.
#CryptoNews #CyberSecurity #SupplyChainRisk #MarketWatch
Stay alert.
Vercel breach fears are putting $VERCEL on every trader’s radar 🔥
BlockBeats reports Vercel’s internal systems may have suffered unauthorized access, with claims that databases, access keys, source code, employee permissions, API keys, NPM tokens, and GitHub tokens were exposed. Because Vercel sits at the center of Next.js and Turbo.js, this is being read less like a lone security scare and more like a potential supply-chain shock with enterprise spillover.
When infrastructure trust cracks, the market doesn’t wait for perfect confirmation; it starts pricing the chance that builders, dev tools, and adjacent ecosystems feel the pressure. Watch how fast the narrative moves from breach headlines to broader confidence in the software stack.
Not financial advice. Manage your risk and protect your capital.
#CryptoNews #CyberSecurity #SupplyChainRisk #MarketWatch
Stay alert.
BlockBeats reports Vercel’s internal systems may have suffered unauthorized access, with claims that databases, access keys, source code, employee permissions, API keys, NPM tokens, and GitHub tokens were exposed. Because Vercel sits at the center of Next.js and Turbo.js, this is being read less like a lone security scare and more like a potential supply-chain shock with enterprise spillover.
When infrastructure trust cracks, the market doesn’t wait for perfect confirmation; it starts pricing the chance that builders, dev tools, and adjacent ecosystems feel the pressure. Watch how fast the narrative moves from breach headlines to broader confidence in the software stack.
Not financial advice. Manage your risk and protect your capital.
#CryptoNews #CyberSecurity #SupplyChainRisk #MarketWatch
Stay alert.
24
·
--

Article
Ocean Harvesters, Cobalt Crusts, and Desertification Tracking🌊🛰️
The expansion of national sovereignty is pushing deeper into international waters and the upper atmosphere. Marine tech firms are deploying autonomous ocean-current kinetic energy harvesters to capture continuous power from deep underwater currents. Operating outside territorial borders, these floating generators require a decentralized financial framework to function. By utilizing $BTC
{spot}(BTCUSDT)
, these robotic systems can independently trade energy credits, pay automated maintenance drones, and secure telemetry links. This keeps offshore energy networks fully functional and completely insulated from onshore political blockades or banking freezes. ⚓
Down on the seabed, the race for advanced electronics manufacturing is driving the tokenization of sovereign deep-sea cobalt crusts. Because cobalt is vital for energy storage and defense systems, access to these deep-water mineral reserves is heavily contested. By anchoring verified underwater deposit registries to an immutable ledger, nations can transparently trade fractionalized mineral rights on global markets. The protocol represented by @bitcoin serves as the neutral layer for these transactions, ensuring that industrial manufacturers can secure raw materials directly and keep supply chains moving independently of localized trade embargos. 💎
Simultaneously, global food security is being reinforced through decentralized satellite-based desertification tracking arrays. Orbital sensors map soil degradation and shifting sand dunes in real time to prevent sudden agricultural collapses. By anchoring this critical environmental telemetry data to a secure public ledger, the network ensures that climate records remain public, unalterable, and completely free from state-sponsored data suppression or geopolitical manipulation. 🌾
#bitcoin #Geopolitics #energy #Space #SupplyChainRisk
Ocean Harvesters, Cobalt Crusts, and Desertification Tracking
🌊🛰️
The expansion of national sovereignty is pushing deeper into international waters and the upper atmosphere. Marine tech firms are deploying autonomous ocean-current kinetic energy harvesters to capture continuous power from deep underwater currents. Operating outside territorial borders, these floating generators require a decentralized financial framework to function. By utilizing $BTC
, these robotic systems can independently trade energy credits, pay automated maintenance drones, and secure telemetry links. This keeps offshore energy networks fully functional and completely insulated from onshore political blockades or banking freezes. ⚓
Down on the seabed, the race for advanced electronics manufacturing is driving the tokenization of sovereign deep-sea cobalt crusts. Because cobalt is vital for energy storage and defense systems, access to these deep-water mineral reserves is heavily contested. By anchoring verified underwater deposit registries to an immutable ledger, nations can transparently trade fractionalized mineral rights on global markets. The protocol represented by @Bitcoin serves as the neutral layer for these transactions, ensuring that industrial manufacturers can secure raw materials directly and keep supply chains moving independently of localized trade embargos. 💎
Simultaneously, global food security is being reinforced through decentralized satellite-based desertification tracking arrays. Orbital sensors map soil degradation and shifting sand dunes in real time to prevent sudden agricultural collapses. By anchoring this critical environmental telemetry data to a secure public ledger, the network ensures that climate records remain public, unalterable, and completely free from state-sponsored data suppression or geopolitical manipulation. 🌾
#bitcoin #Geopolitics #energy #Space #SupplyChainRisk
The expansion of national sovereignty is pushing deeper into international waters and the upper atmosphere. Marine tech firms are deploying autonomous ocean-current kinetic energy harvesters to capture continuous power from deep underwater currents. Operating outside territorial borders, these floating generators require a decentralized financial framework to function. By utilizing $BTC
, these robotic systems can independently trade energy credits, pay automated maintenance drones, and secure telemetry links. This keeps offshore energy networks fully functional and completely insulated from onshore political blockades or banking freezes. ⚓
Down on the seabed, the race for advanced electronics manufacturing is driving the tokenization of sovereign deep-sea cobalt crusts. Because cobalt is vital for energy storage and defense systems, access to these deep-water mineral reserves is heavily contested. By anchoring verified underwater deposit registries to an immutable ledger, nations can transparently trade fractionalized mineral rights on global markets. The protocol represented by @Bitcoin serves as the neutral layer for these transactions, ensuring that industrial manufacturers can secure raw materials directly and keep supply chains moving independently of localized trade embargos. 💎
Simultaneously, global food security is being reinforced through decentralized satellite-based desertification tracking arrays. Orbital sensors map soil degradation and shifting sand dunes in real time to prevent sudden agricultural collapses. By anchoring this critical environmental telemetry data to a secure public ledger, the network ensures that climate records remain public, unalterable, and completely free from state-sponsored data suppression or geopolitical manipulation. 🌾
#bitcoin #Geopolitics #energy #Space #SupplyChainRisk
31
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#IsAnthropic’s$1.5TMarketCapJustified?
11,732 views
99 Discussing
2
#BTCRemainsUnderPressureAfterHawkishFOMCMinutes
256,268 views
2,127 Discussing
3
#NvidiaBoardReportedlySplitOverHuang’sReturn
125,080 views
1,151 Discussing
4
#StrategySTRCPreferredSlips3.65%Below$100Par
8,476 views
85 Discussing
5
#MASToUpgradeSGDTestnetToSGDigitalLedger
23,779 views
278 Discussing
6
#CanGTA6'sLaunchLiftTTWOShares?
89,405 views
829 Discussing
7
#Solana2027RoadmapTargetsDoubleComputeCapacity
10,349 views
145 Discussing
8
#InjectiveTokenizedRealEstateMortgagesTop$1.5B
1,224 views
29 Discussing
9
#TetherMakesStrategicInvestmentInSCRYPT
7,306 views
114 Discussing
10
#CapitalGroupAdds1264500StrategyShares
32,693 views
245 Discussing