
#safe
safe
326,061 views
1,663 Discussing
Hot
Latest
·
--
Not a single signature was given on the multisig, yet $6.45 million was transferred out—this time, there was nothing wrong with the Safe contract.
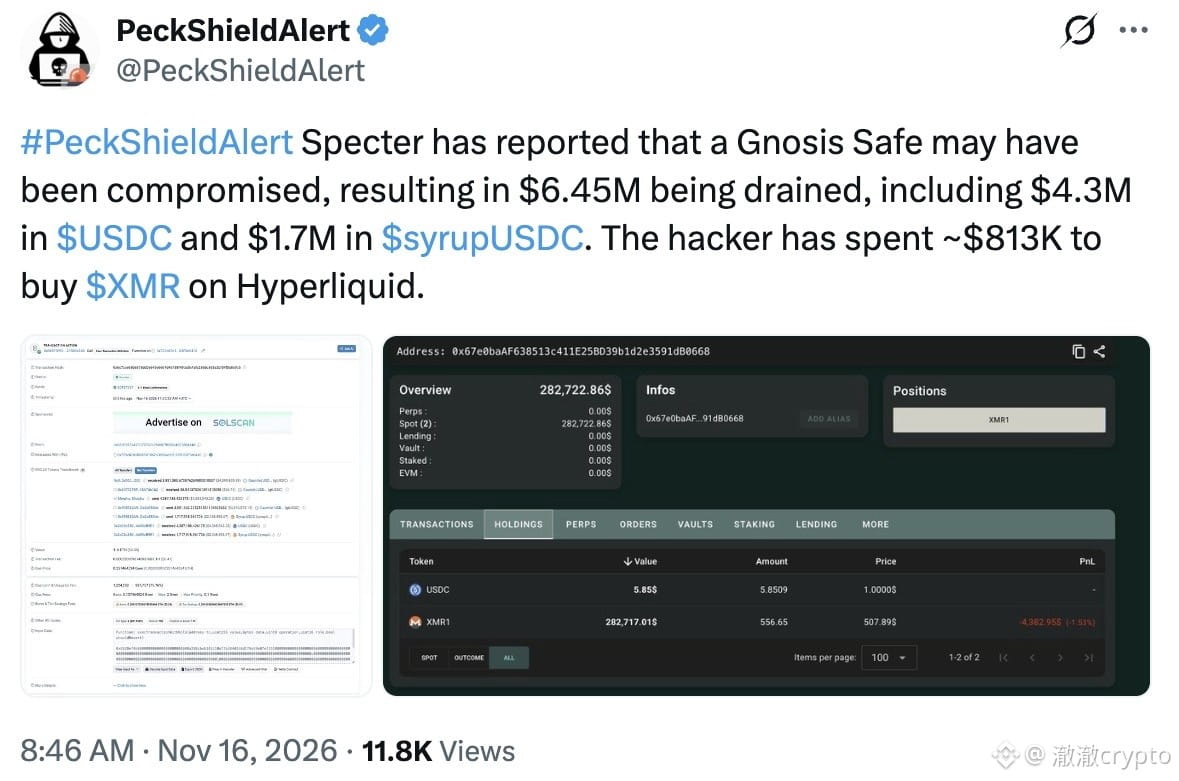
Here’s what happened: On Monday, November 16, a single transaction drained 4,387,188.43 USDC and 1,717,918.96 syrupUSDC from a Gnosis Safe multisig wallet, worth about $6.45 million in total (according to on-chain records, verified by Cointelegraph).
The funds were moved using the Zodiac Roles permissions module installed in the wallet itself, without requiring another signature from the owners.
The attacker then converted about $813,000 into Monero (XMR), while another roughly $1.2 million was laundered into XMR via Wagyu.
My take: This wasn’t Safe being hacked—it was a case of “keys + overly broad permissions” going wrong together.
A Zodiac co-founder said firsthand that the module had no vulnerability; a key belonging to a long-standing role member was suspected to have been stolen, and the wallet’s permissions were almost certainly configured to unintentionally allow the transfer.
What I’d do: If you use Safe as a team, check your Roles permissions list and immediately revoke any authorizations that exceed their intended scope.
What would change my mind: If further investigation finds a genuine vulnerability in the module itself, the assessment above no longer applies.
What do you think is the biggest multisig pitfall: contract vulnerabilities, or permissions configured incorrectly by users?
$BTC $ETH $SOL
#Safe #MultisigWallet
Not a single signature was given on the multisig, yet $6.45 million was transferred out—this time, there was nothing wrong with the Safe contract.
Here’s what happened: On Monday, November 16, a single transaction drained 4,387,188.43 USDC and 1,717,918.96 syrupUSDC from a Gnosis Safe multisig wallet, worth about $6.45 million in total (according to on-chain records, verified by Cointelegraph).
The funds were moved using the Zodiac Roles permissions module installed in the wallet itself, without requiring another signature from the owners.
The attacker then converted about $813,000 into Monero (XMR), while another roughly $1.2 million was laundered into XMR via Wagyu.
My take: This wasn’t Safe being hacked—it was a case of “keys + overly broad permissions” going wrong together.
A Zodiac co-founder said firsthand that the module had no vulnerability; a key belonging to a long-standing role member was suspected to have been stolen, and the wallet’s permissions were almost certainly configured to unintentionally allow the transfer.
What I’d do: If you use Safe as a team, check your Roles permissions list and immediately revoke any authorizations that exceed their intended scope.
What would change my mind: If further investigation finds a genuine vulnerability in the module itself, the assessment above no longer applies.
What do you think is the biggest multisig pitfall: contract vulnerabilities, or permissions configured incorrectly by users?
$BTC $ETH $SOL
#Safe #MultisigWallet
Here’s what happened: On Monday, November 16, a single transaction drained 4,387,188.43 USDC and 1,717,918.96 syrupUSDC from a Gnosis Safe multisig wallet, worth about $6.45 million in total (according to on-chain records, verified by Cointelegraph).
The funds were moved using the Zodiac Roles permissions module installed in the wallet itself, without requiring another signature from the owners.
The attacker then converted about $813,000 into Monero (XMR), while another roughly $1.2 million was laundered into XMR via Wagyu.
My take: This wasn’t Safe being hacked—it was a case of “keys + overly broad permissions” going wrong together.
A Zodiac co-founder said firsthand that the module had no vulnerability; a key belonging to a long-standing role member was suspected to have been stolen, and the wallet’s permissions were almost certainly configured to unintentionally allow the transfer.
What I’d do: If you use Safe as a team, check your Roles permissions list and immediately revoke any authorizations that exceed their intended scope.
What would change my mind: If further investigation finds a genuine vulnerability in the module itself, the assessment above no longer applies.
What do you think is the biggest multisig pitfall: contract vulnerabilities, or permissions configured incorrectly by users?
$BTC $ETH $SOL
#Safe #MultisigWallet
12

·
--
Article
Multisig wallet loses $6.45 million without a single signature from its owners$6.45 million was drained from a multisig wallet without a single signature.
On Monday, November 16, a Safe multisig wallet lost about $6.45 million, most of it comprising roughly $4.3 million in USDC and $1.7 million in syrupUSDC, with the rest made up of several hundred thousand dollars in other assets. Blockchain security firm PeckShield issued an alert that day, based on a tip from on-chain analyst Specter. The funds were transferred in a single transaction through a preconfigured authorization module called Zodiac Roles. Not one of the multisig’s owners had signed, yet the funds were gone.
That’s how a multisig wallet is supposed to work: several people have to approve a transfer; no single person can decide on their own. But this wallet had previously been configured with a “role authorization,” meaning a designated key could move funds on its own within the permissions that had been set, without needing to gather the owners’ signatures. A co-founder of Zodiac later responded that there was no vulnerability in the module’s contract itself; the transfer used a key belonging to a former role member, which had most likely been stolen. Combined with the wallet’s overly broad authorization policy, that’s how the door was opened. Safe also said its own contracts and wallet app were unaffected. This wasn’t the first time this year that someone had targeted a third-party module used with Safe.
Multisig wallet loses $6.45 million without a single signature from its owners
$6.45 million was drained from a multisig wallet without a single signature.
On Monday, November 16, a Safe multisig wallet lost about $6.45 million, most of it comprising roughly $4.3 million in USDC and $1.7 million in syrupUSDC, with the rest made up of several hundred thousand dollars in other assets. Blockchain security firm PeckShield issued an alert that day, based on a tip from on-chain analyst Specter. The funds were transferred in a single transaction through a preconfigured authorization module called Zodiac Roles. Not one of the multisig’s owners had signed, yet the funds were gone.
That’s how a multisig wallet is supposed to work: several people have to approve a transfer; no single person can decide on their own. But this wallet had previously been configured with a “role authorization,” meaning a designated key could move funds on its own within the permissions that had been set, without needing to gather the owners’ signatures. A co-founder of Zodiac later responded that there was no vulnerability in the module’s contract itself; the transfer used a key belonging to a former role member, which had most likely been stolen. Combined with the wallet’s overly broad authorization policy, that’s how the door was opened. Safe also said its own contracts and wallet app were unaffected. This wasn’t the first time this year that someone had targeted a third-party module used with Safe.
On Monday, November 16, a Safe multisig wallet lost about $6.45 million, most of it comprising roughly $4.3 million in USDC and $1.7 million in syrupUSDC, with the rest made up of several hundred thousand dollars in other assets. Blockchain security firm PeckShield issued an alert that day, based on a tip from on-chain analyst Specter. The funds were transferred in a single transaction through a preconfigured authorization module called Zodiac Roles. Not one of the multisig’s owners had signed, yet the funds were gone.
That’s how a multisig wallet is supposed to work: several people have to approve a transfer; no single person can decide on their own. But this wallet had previously been configured with a “role authorization,” meaning a designated key could move funds on its own within the permissions that had been set, without needing to gather the owners’ signatures. A co-founder of Zodiac later responded that there was no vulnerability in the module’s contract itself; the transfer used a key belonging to a former role member, which had most likely been stolen. Combined with the wallet’s overly broad authorization policy, that’s how the door was opened. Safe also said its own contracts and wallet app were unaffected. This wasn’t the first time this year that someone had targeted a third-party module used with Safe.
128
·
--
【No one signed the multisig wallet, yet $6.4 million was transferred in a single transaction! A Safe wallet was compromised through an “authorization module,” and some of the stolen funds have already been converted to Monero】
At around 7:30 p.m. on November 16 (Beijing time), a Safe multisig wallet on Ethereum requiring 2 of 4 signers transferred approximately 4.39 million USDC and 1.72 million syrupUSDC—about $6.44 million in total—in a single transaction without any signatures from its owners. The transfer was made through a Zodiac permissions module that had been enabled back in 2024. Some of the funds were subsequently converted into Monero, a privacy coin that is difficult to trace. So far, there appears to be no vulnerability in the contract itself; it is more likely that the private key of an address holding this permission for a long time was stolen, combined with the permission being set too broadly. If you’ve ever granted wallet permissions to a bot or fund manager, check whether it can transfer funds to external addresses.
#Safe #钱包安全 #HackAttack
【No one signed the multisig wallet, yet $6.4 million was transferred in a single transaction! A Safe wallet was compromised through an “authorization module,” and some of the stolen funds have already been converted to Monero】
At around 7:30 p.m. on November 16 (Beijing time), a Safe multisig wallet on Ethereum requiring 2 of 4 signers transferred approximately 4.39 million USDC and 1.72 million syrupUSDC—about $6.44 million in total—in a single transaction without any signatures from its owners. The transfer was made through a Zodiac permissions module that had been enabled back in 2024. Some of the funds were subsequently converted into Monero, a privacy coin that is difficult to trace. So far, there appears to be no vulnerability in the contract itself; it is more likely that the private key of an address holding this permission for a long time was stolen, combined with the permission being set too broadly. If you’ve ever granted wallet permissions to a bot or fund manager, check whether it can transfer funds to external addresses.
#Safe #钱包安全 #HackAttack
At around 7:30 p.m. on November 16 (Beijing time), a Safe multisig wallet on Ethereum requiring 2 of 4 signers transferred approximately 4.39 million USDC and 1.72 million syrupUSDC—about $6.44 million in total—in a single transaction without any signatures from its owners. The transfer was made through a Zodiac permissions module that had been enabled back in 2024. Some of the funds were subsequently converted into Monero, a privacy coin that is difficult to trace. So far, there appears to be no vulnerability in the contract itself; it is more likely that the private key of an address holding this permission for a long time was stolen, combined with the permission being set too broadly. If you’ve ever granted wallet permissions to a bot or fund manager, check whether it can transfer funds to external addresses.
#Safe #钱包安全 #HackAttack
94

$SAFE (Safe) spot check — the wallet token holding its low better than most today.
Price: ~$0.082, down ~5% in 24h, but still up ~6% over the last 7 days. 24h range $0.0817–$0.0869, market cap ~$65M.
Safe is the smart-account wallet behind most of crypto's multisig custody — real product, real usage — yet the token sits ~98% below its $3.63 ATH from April 2024. Down ~32% in 30 days, so it has not escaped this sell-off.
Levels: support $0.0817 (today's low), resistance $0.0869, then $0.09. Lose $0.0817 and the next stop is the $0.08 round number.
$BTC context: ~$69,335, down ~5.7% today after breaking below $70K, day low $67,568 — lowest since August. Fear & Greed at 20, and spot BTC ETF outflows are running 6 straight days.
Verdict: SAFE is holding up better than BTC today, but with the market this weak, spot buyers want $70K to flip back to support first.
Not financial advice. DYOR.
#Safe #Bitcoin #Crypto
$SAFE (Safe) spot check — the wallet token holding its low better than most today.
Price: ~$0.082, down ~5% in 24h, but still up ~6% over the last 7 days. 24h range $0.0817–$0.0869, market cap ~$65M.
Safe is the smart-account wallet behind most of crypto's multisig custody — real product, real usage — yet the token sits ~98% below its $3.63 ATH from April 2024. Down ~32% in 30 days, so it has not escaped this sell-off.
Levels: support $0.0817 (today's low), resistance $0.0869, then $0.09. Lose $0.0817 and the next stop is the $0.08 round number.
$BTC context: ~$69,335, down ~5.7% today after breaking below $70K, day low $67,568 — lowest since August. Fear & Greed at 20, and spot BTC ETF outflows are running 6 straight days.
Verdict: SAFE is holding up better than BTC today, but with the market this weak, spot buyers want $70K to flip back to support first.
Not financial advice. DYOR.
#Safe #Bitcoin #Crypto
Price: ~$0.082, down ~5% in 24h, but still up ~6% over the last 7 days. 24h range $0.0817–$0.0869, market cap ~$65M.
Safe is the smart-account wallet behind most of crypto's multisig custody — real product, real usage — yet the token sits ~98% below its $3.63 ATH from April 2024. Down ~32% in 30 days, so it has not escaped this sell-off.
Levels: support $0.0817 (today's low), resistance $0.0869, then $0.09. Lose $0.0817 and the next stop is the $0.08 round number.
$BTC context: ~$69,335, down ~5.7% today after breaking below $70K, day low $67,568 — lowest since August. Fear & Greed at 20, and spot BTC ETF outflows are running 6 straight days.
Verdict: SAFE is holding up better than BTC today, but with the market this weak, spot buyers want $70K to flip back to support first.
Not financial advice. DYOR.
#Safe #Bitcoin #Crypto
4
·
--
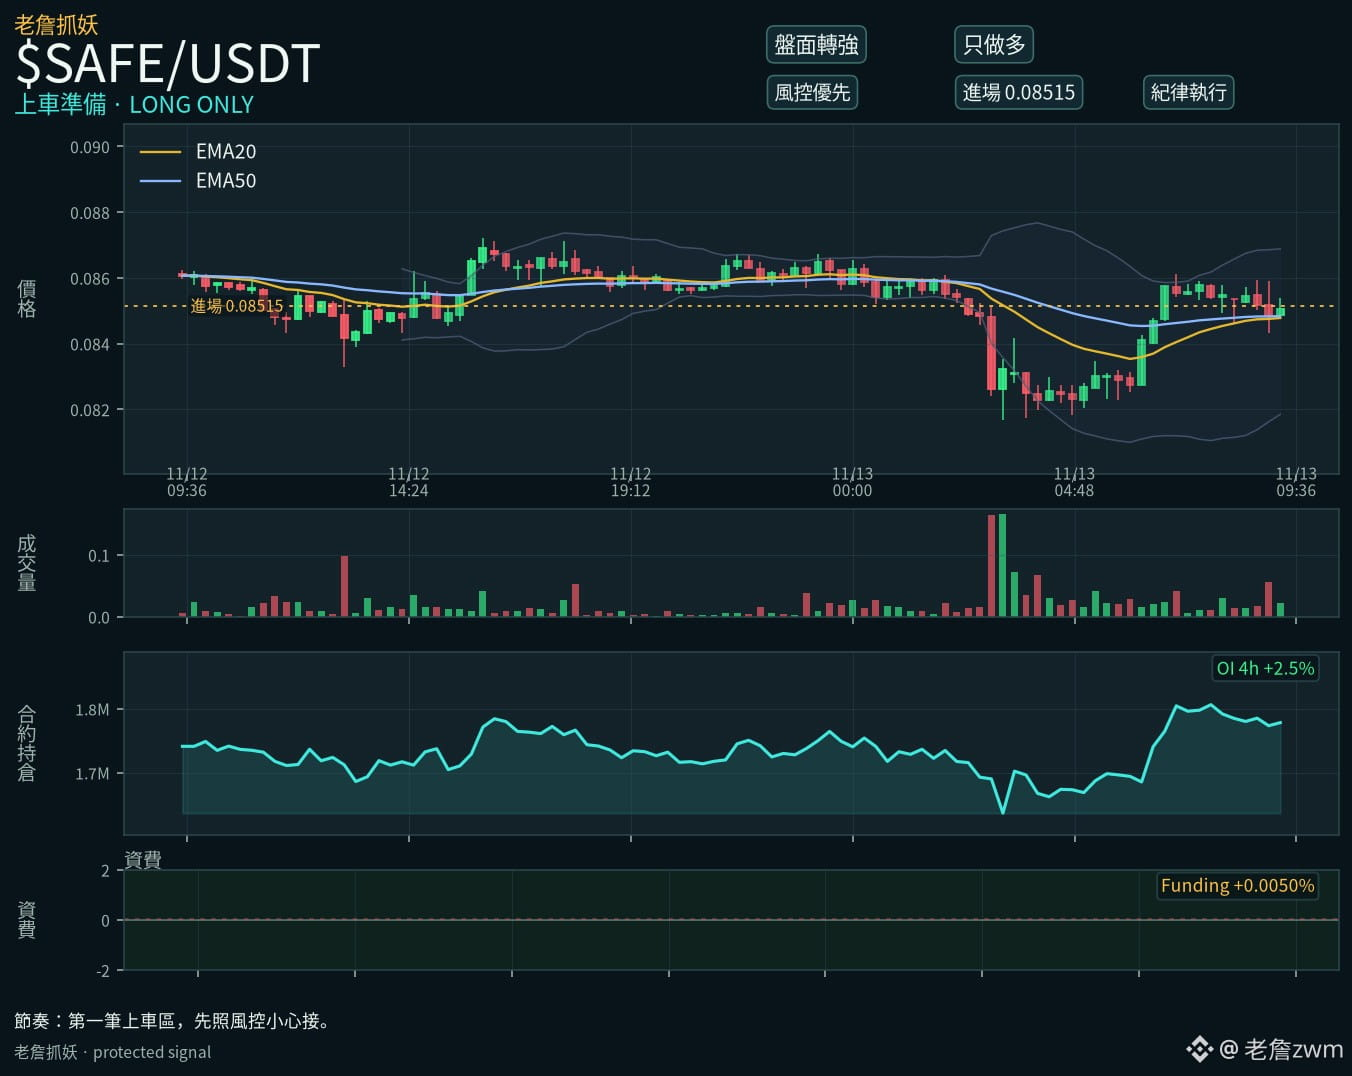
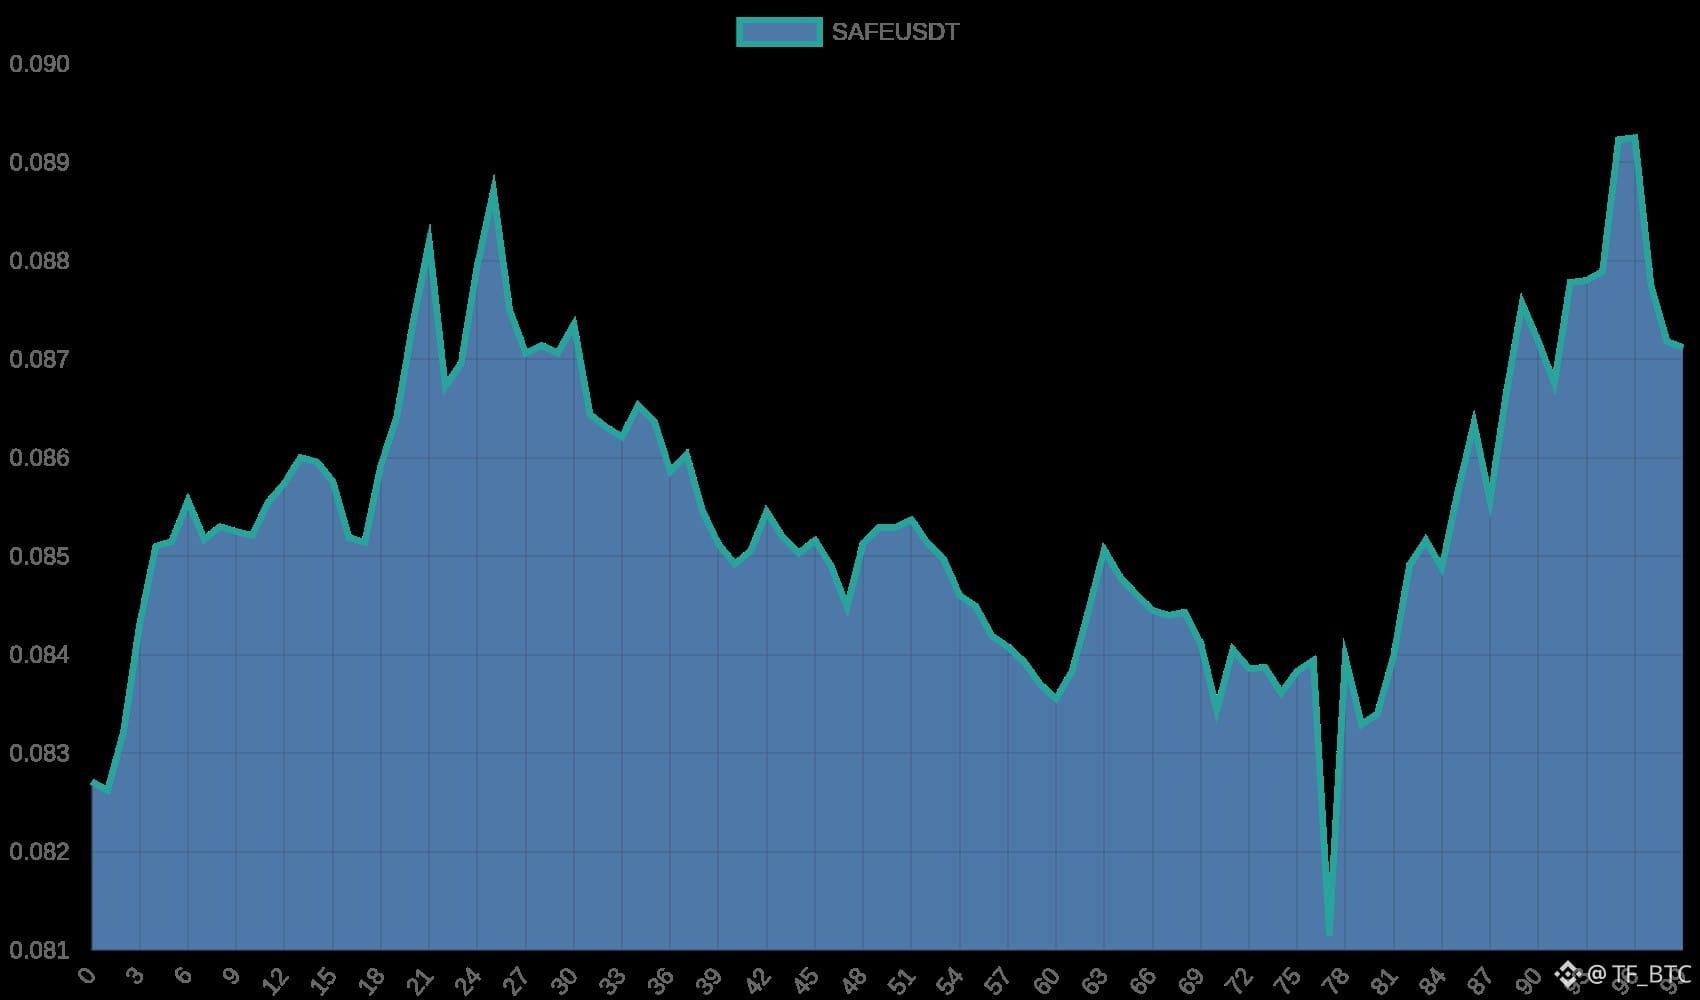
Good entry points often appear when nobody is paying attention.
$SAFE This looks interesting.
Buying pressure has been strong for 4 hours straight, and the price is just above the two-day low.
One thing to watch is that volume has been inconsistent.
Take a small position first, then wait for volume to pick up before deciding what to do next. Stop loss: 0.07238; first target: 0.09367. Take 30% off the table when it reaches the target.
#SAFE
Good entry points often appear when nobody is paying attention.
$SAFE This looks interesting.
Buying pressure has been strong for 4 hours straight, and the price is just above the two-day low.
One thing to watch is that volume has been inconsistent.
Take a small position first, then wait for volume to pick up before deciding what to do next. Stop loss: 0.07238; first target: 0.09367. Take 30% off the table when it reaches the target.
#SAFE
$SAFE This looks interesting.
Buying pressure has been strong for 4 hours straight, and the price is just above the two-day low.
One thing to watch is that volume has been inconsistent.
Take a small position first, then wait for volume to pick up before deciding what to do next. Stop loss: 0.07238; first target: 0.09367. Take 30% off the table when it reaches the target.
#SAFE
12

·
--
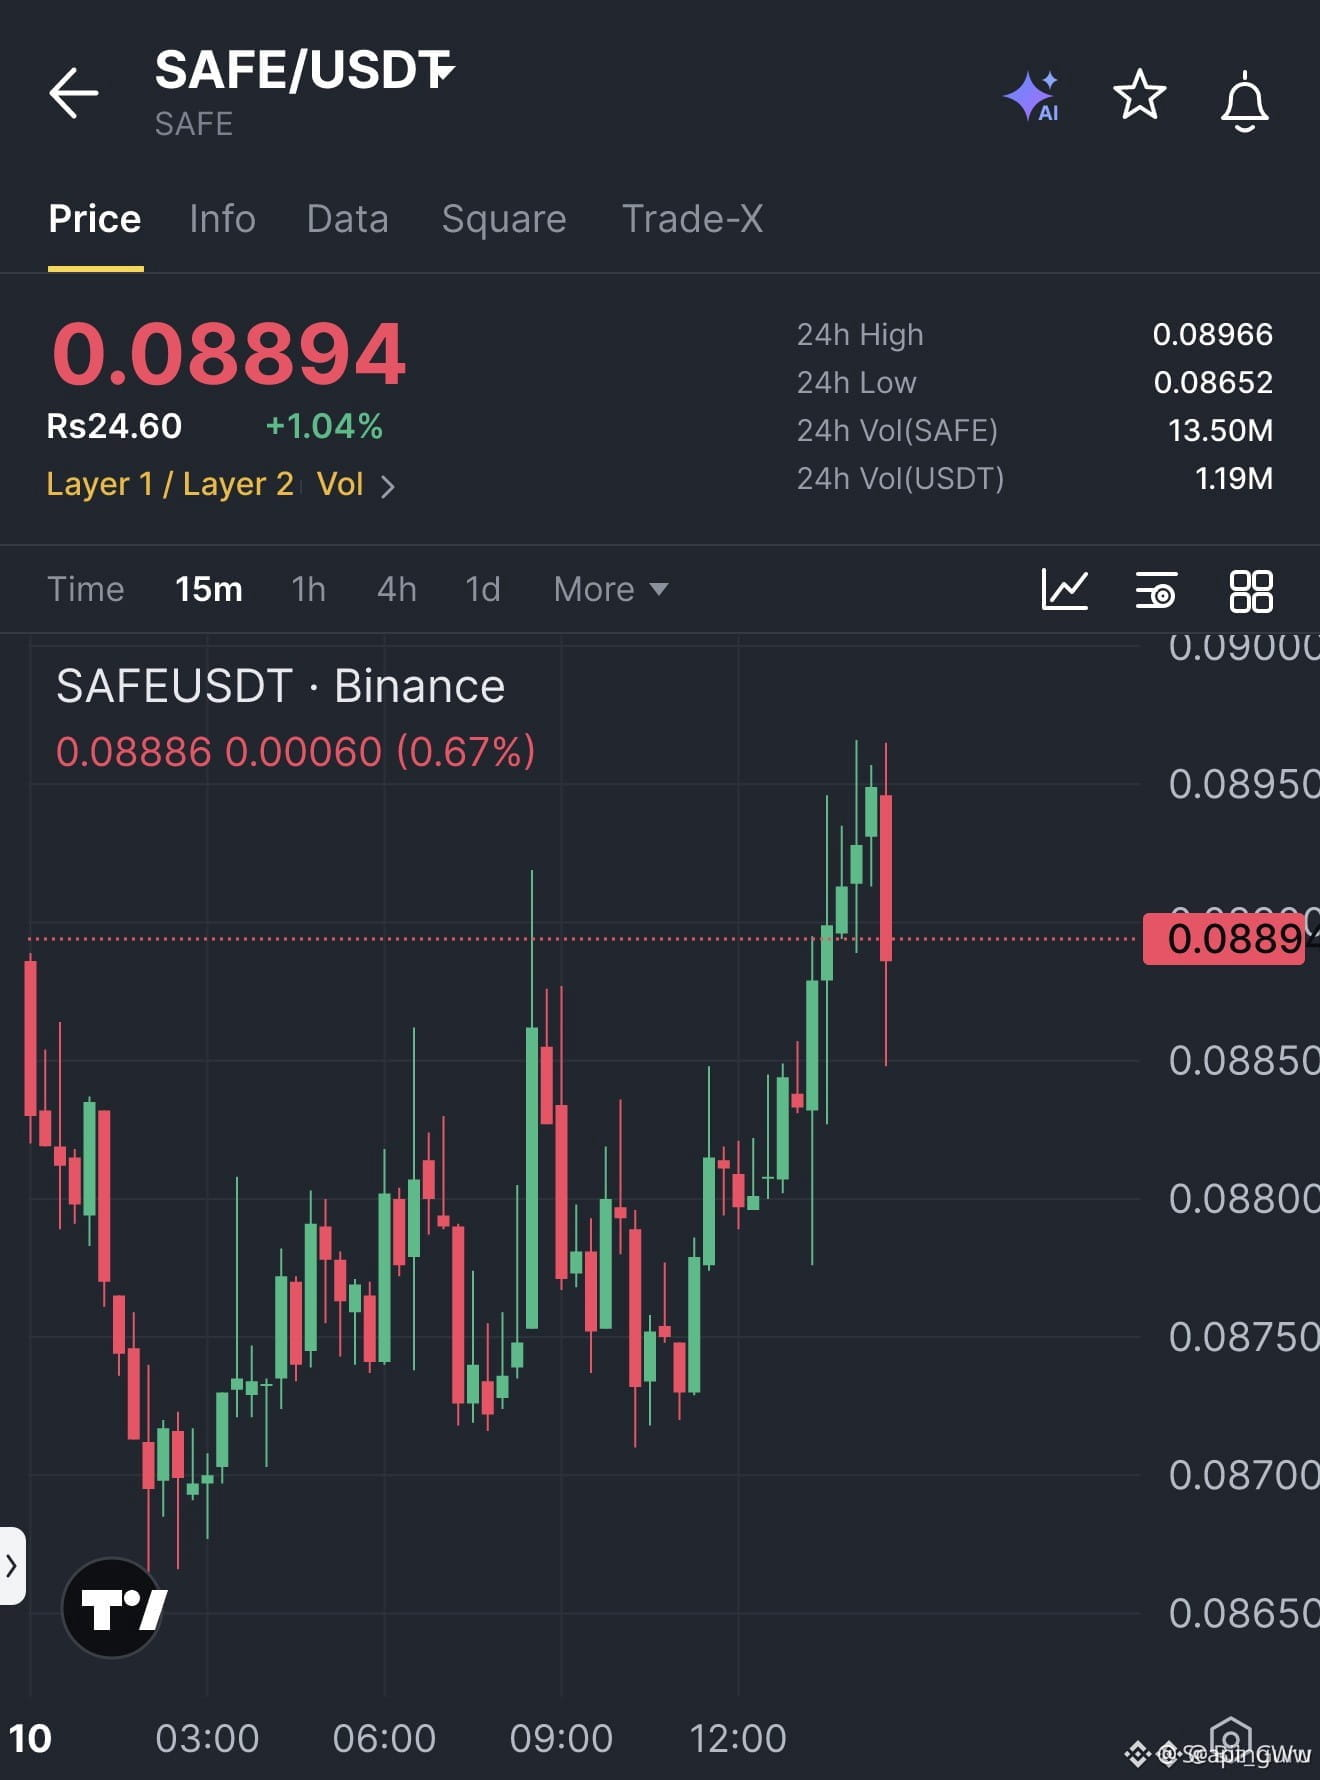
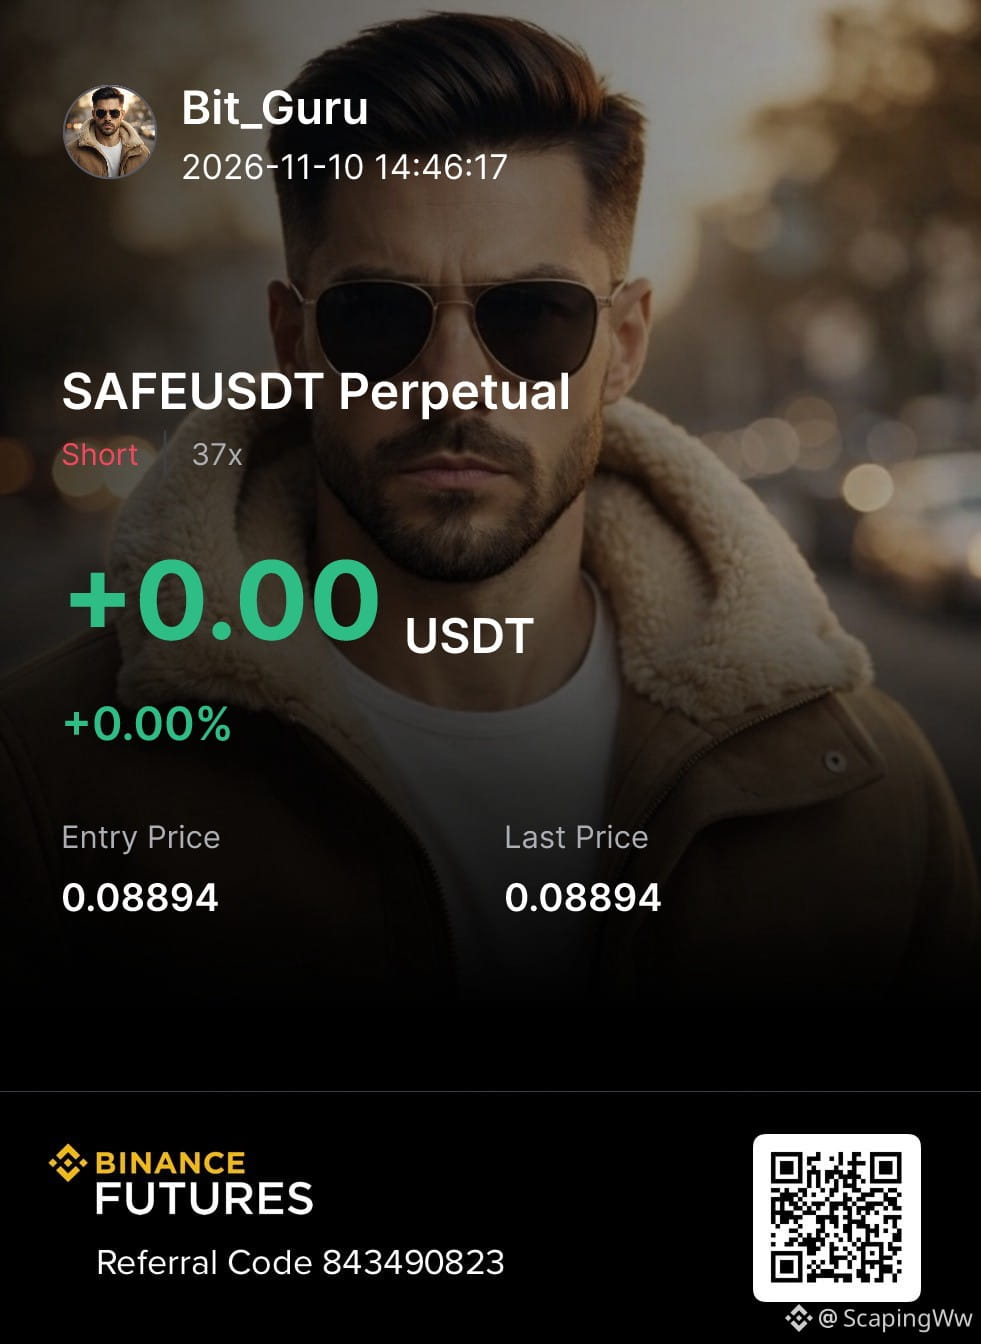
📉 $SAFE SELLERS CAPTURE CONTROL AFTER A SHARP EXHAUSTION RALLY! ⚡
Entry: 0.08894 ⚡
Target: 0.08578 🚀
Stop Loss: 0.08973 ⚠️
Exhaustion is finally creeping into the order books as buyers lose steam following a sustained vertical push. 📊 When previous candle lows fracture under heavy selling pressure, the shift in market structure opens a pristine window for downside continuation. ⚡
Execution requires strict discipline around our invalidation zone above the recent swing high. 📌 Are you fading this bounce or waiting for confirmation below the initial support level? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #ShortSetup #Crypto #PriceAction #Trading
📉 🦈
📉 $SAFE SELLERS CAPTURE CONTROL AFTER A SHARP EXHAUSTION RALLY! ⚡
Entry: 0.08894 ⚡
Target: 0.08578 🚀
Stop Loss: 0.08973 ⚠️
Exhaustion is finally creeping into the order books as buyers lose steam following a sustained vertical push. 📊 When previous candle lows fracture under heavy selling pressure, the shift in market structure opens a pristine window for downside continuation. ⚡
Execution requires strict discipline around our invalidation zone above the recent swing high. 📌 Are you fading this bounce or waiting for confirmation below the initial support level? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #ShortSetup #Crypto #PriceAction #Trading
📉 🦈
Entry: 0.08894 ⚡
Target: 0.08578 🚀
Stop Loss: 0.08973 ⚠️
Exhaustion is finally creeping into the order books as buyers lose steam following a sustained vertical push. 📊 When previous candle lows fracture under heavy selling pressure, the shift in market structure opens a pristine window for downside continuation. ⚡
Execution requires strict discipline around our invalidation zone above the recent swing high. 📌 Are you fading this bounce or waiting for confirmation below the initial support level? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #ShortSetup #Crypto #PriceAction #Trading
📉 🦈
13

·
--
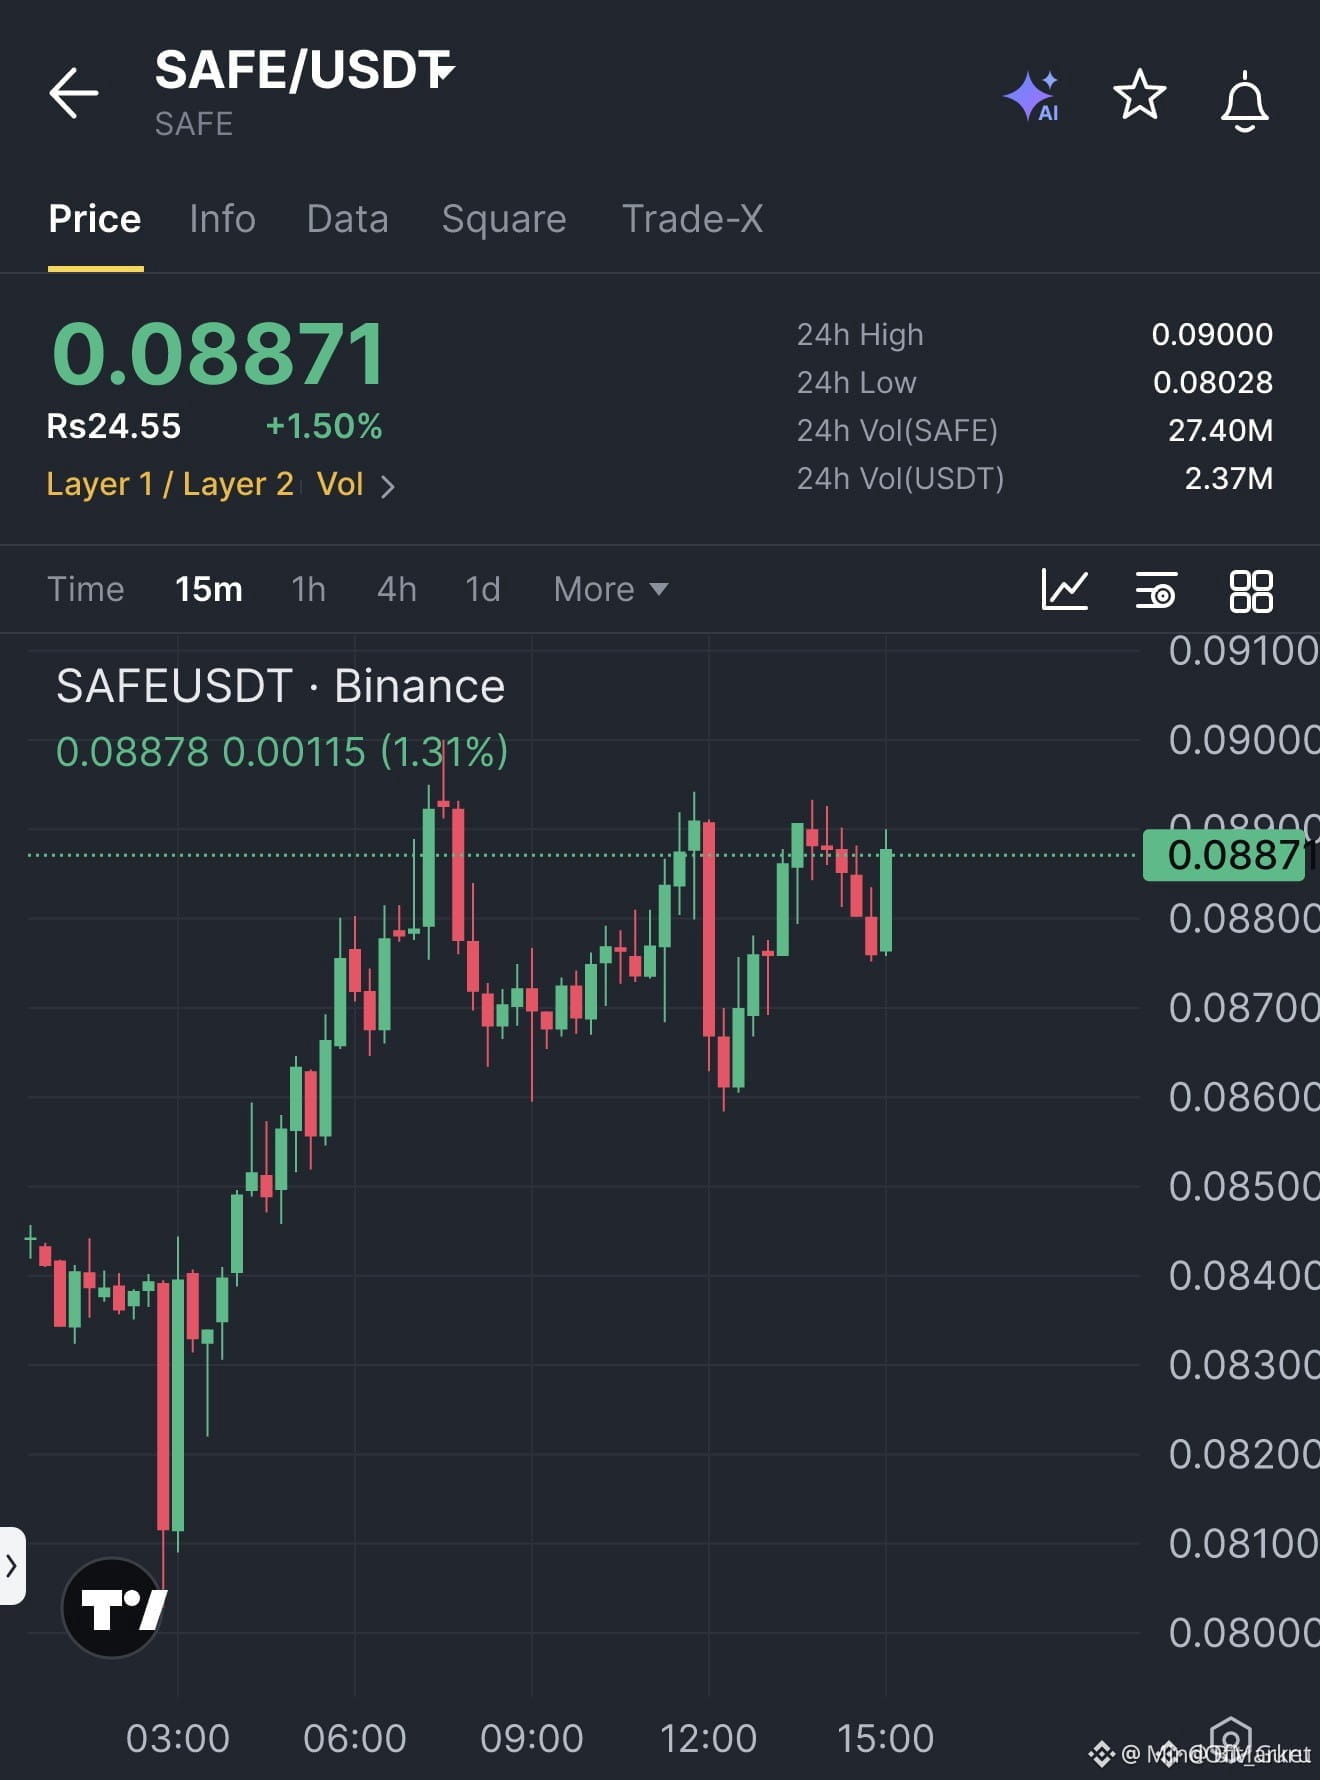
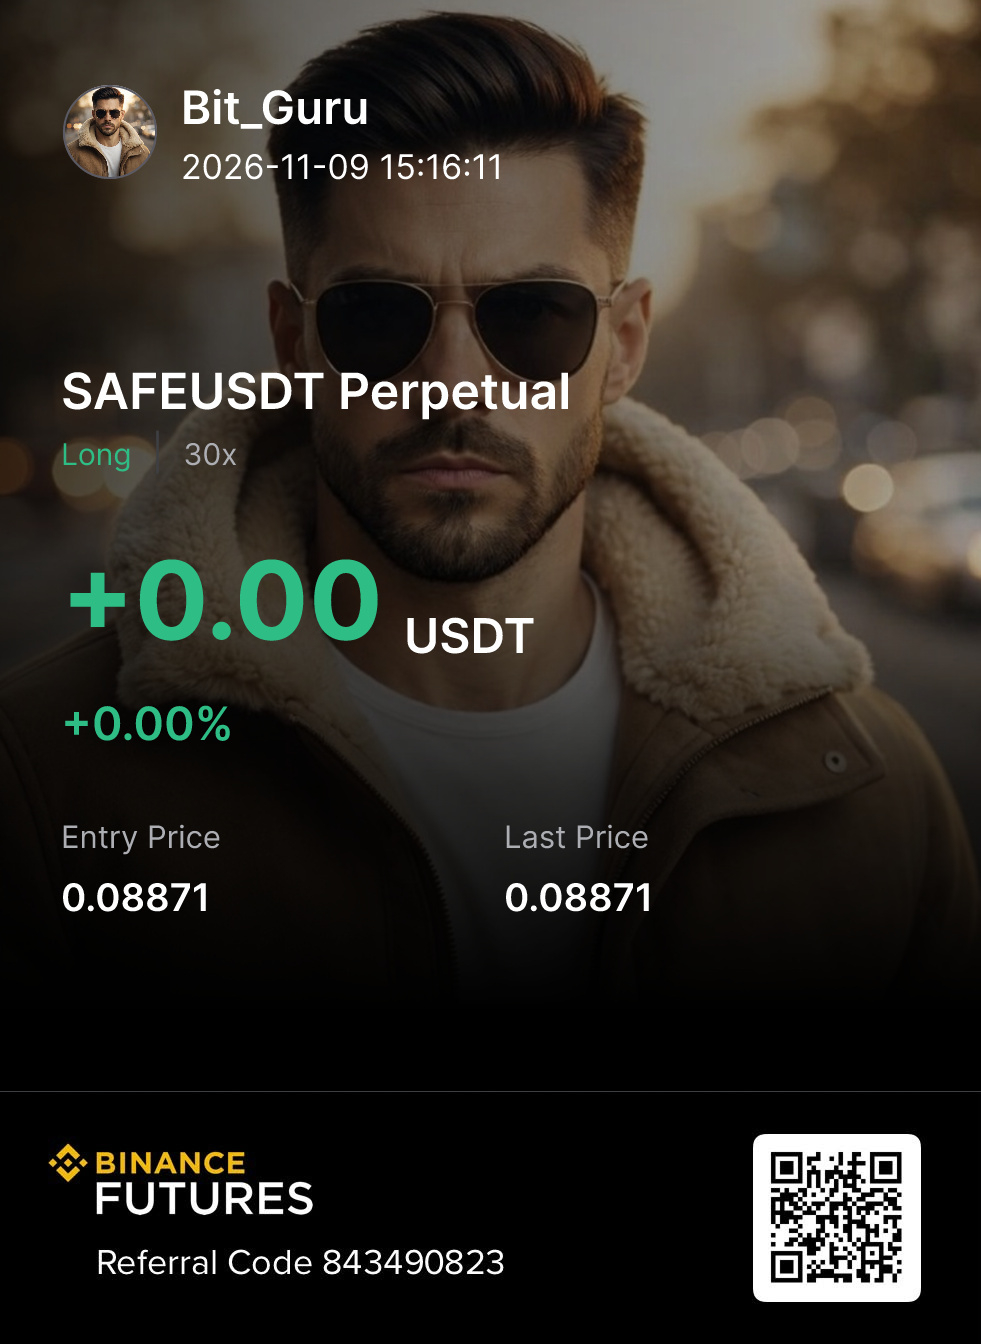
🦈 $SAFE SWEEPING LIQUIDITY AS SMART MONEY RECLAIMS KEY STRUCTURAL HIGHS! ⚡
Entry: 0.08871 ⚡
Target: 0.09068, 0.09199, 0.09395 🚀
Stop Loss: 0.0874 ⚠️
Institutional order flow is shifting as smart money aggressively absorbs supply following a sustained structural markdown across the order book. 📊 The sharp impulse break above the previous candle high confirms a clean liquidity sweep and a high-probability recovery trigger. 💡
Risk parameters are tightly defined below key institutional invalidation levels to protect capital while targeting sequential upper liquidity pools. 📌 Are you executing this structural reclaim now or waiting for a confirmation retest? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #SmartMoney #LongSetup #OrderBlock #Crypto
🦈 💎
🦈 $SAFE SWEEPING LIQUIDITY AS SMART MONEY RECLAIMS KEY STRUCTURAL HIGHS! ⚡
Entry: 0.08871 ⚡
Target: 0.09068, 0.09199, 0.09395 🚀
Stop Loss: 0.0874 ⚠️
Institutional order flow is shifting as smart money aggressively absorbs supply following a sustained structural markdown across the order book. 📊 The sharp impulse break above the previous candle high confirms a clean liquidity sweep and a high-probability recovery trigger. 💡
Risk parameters are tightly defined below key institutional invalidation levels to protect capital while targeting sequential upper liquidity pools. 📌 Are you executing this structural reclaim now or waiting for a confirmation retest? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #SmartMoney #LongSetup #OrderBlock #Crypto
🦈 💎
Entry: 0.08871 ⚡
Target: 0.09068, 0.09199, 0.09395 🚀
Stop Loss: 0.0874 ⚠️
Institutional order flow is shifting as smart money aggressively absorbs supply following a sustained structural markdown across the order book. 📊 The sharp impulse break above the previous candle high confirms a clean liquidity sweep and a high-probability recovery trigger. 💡
Risk parameters are tightly defined below key institutional invalidation levels to protect capital while targeting sequential upper liquidity pools. 📌 Are you executing this structural reclaim now or waiting for a confirmation retest? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #SmartMoney #LongSetup #OrderBlock #Crypto
🦈 💎
7

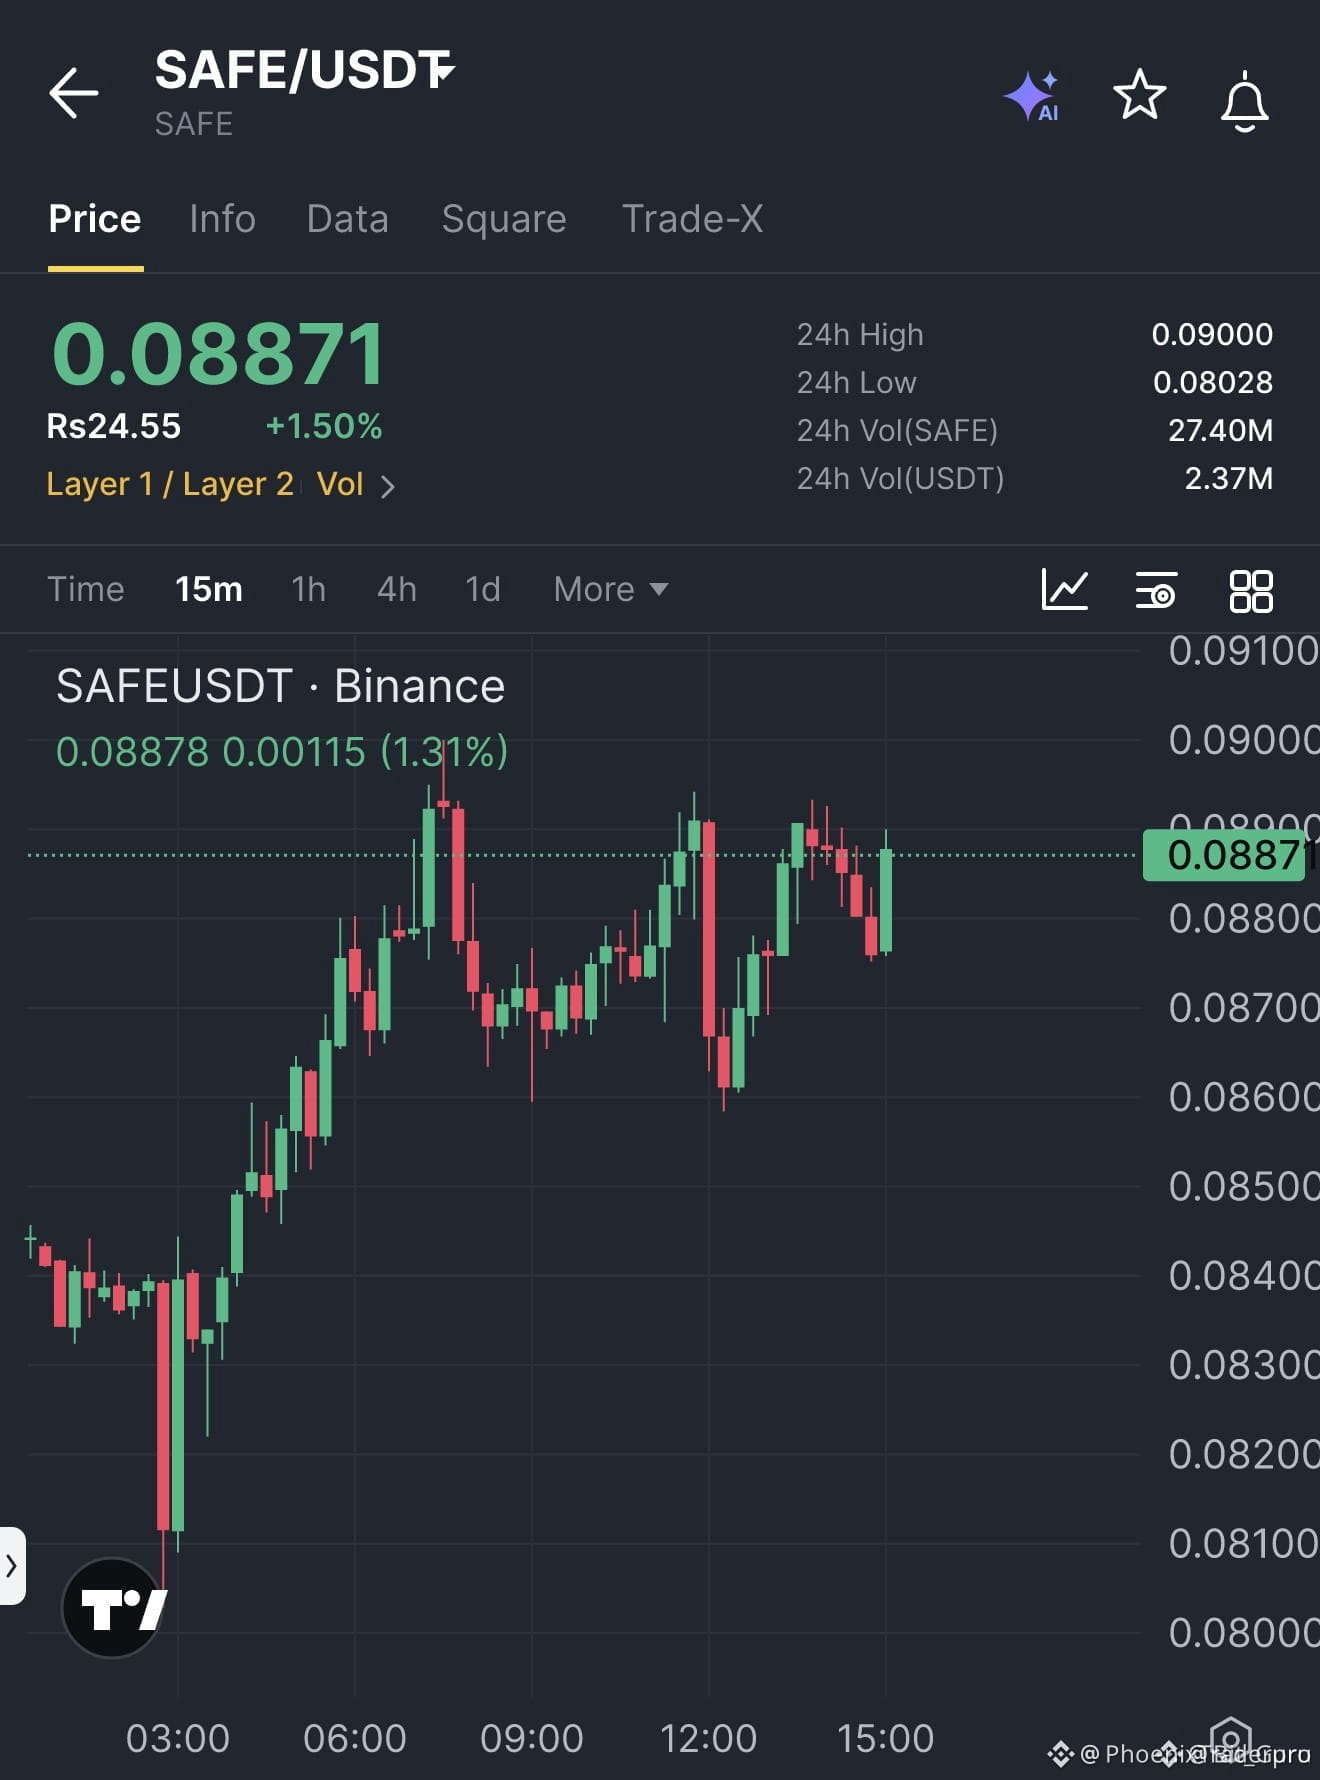
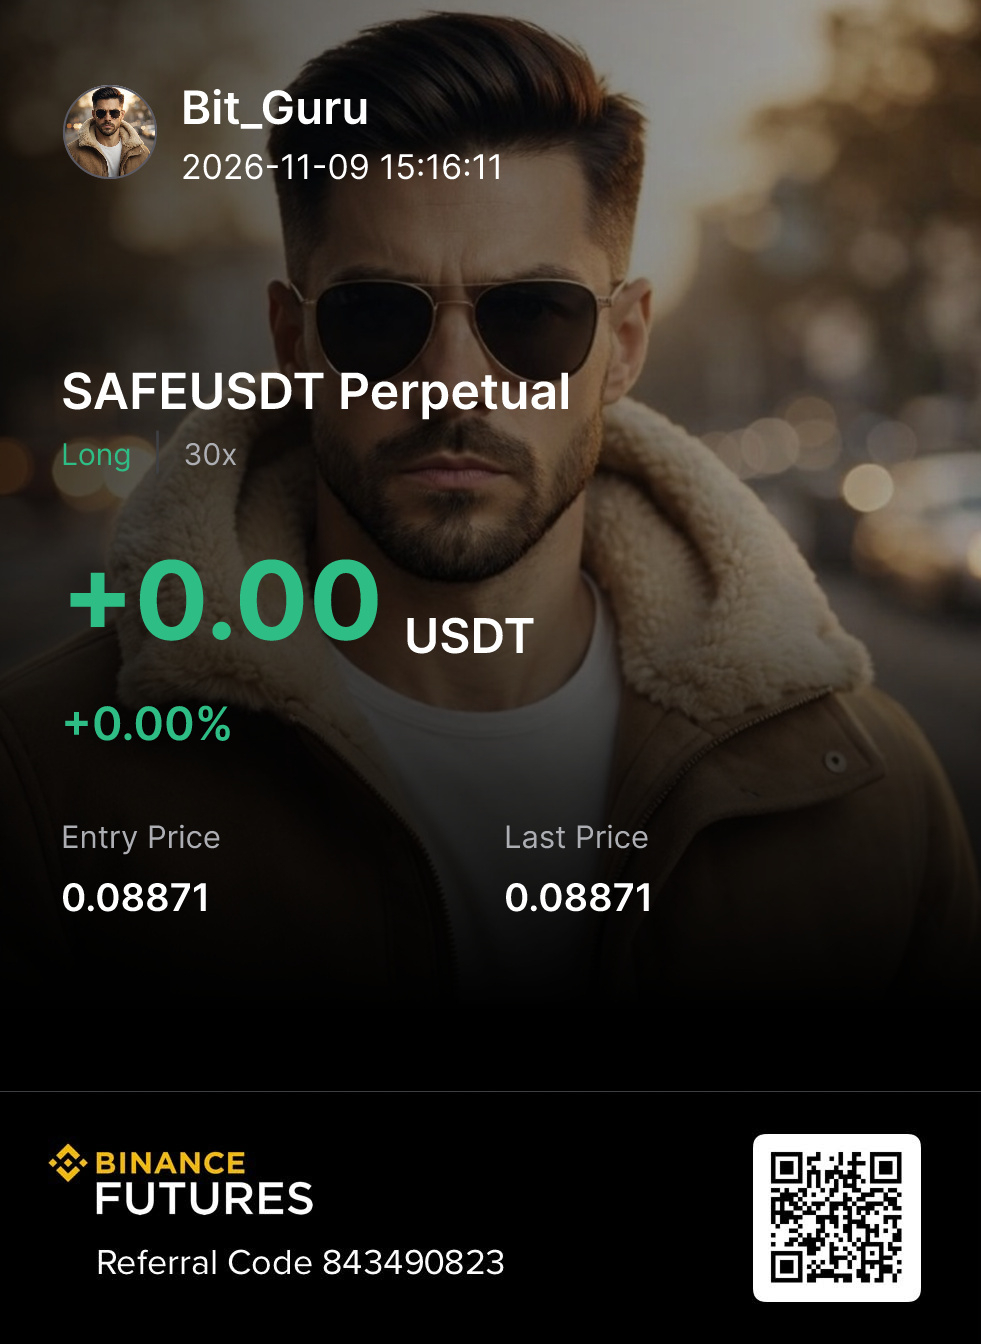
🚨 $SAFE BUYERS SHATTER RESISTANCE AFTER A BRUTAL FLUSH DOWN! 💥
Entry: 0.08871 ⚡
Target 1: 0.09068 🚀
Target 2: 0.09199 🎯
Target 3: 0.09395 💥
Stop Loss: 0.0874 ⚠️
Sellers exhausted themselves driving $SAFE down into a deep liquidity pocket, only for aggressive bids to sweep in and reclaim previous candle highs. This sudden structural shift confirms the recovery playbook is live as order flow flips in favor of the bulls.
Volume is ticking up across the board as momentum buyers step in to defend the breakout 📊 ⚡ 💬 Are you locking in early entries or waiting for confirmation near the upper targets? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #LongSetup #Crypto #Breakout
🔥 💎
🚨 $SAFE BUYERS SHATTER RESISTANCE AFTER A BRUTAL FLUSH DOWN! 💥
Entry: 0.08871 ⚡
Target 1: 0.09068 🚀
Target 2: 0.09199 🎯
Target 3: 0.09395 💥
Stop Loss: 0.0874 ⚠️
Sellers exhausted themselves driving $SAFE down into a deep liquidity pocket, only for aggressive bids to sweep in and reclaim previous candle highs. This sudden structural shift confirms the recovery playbook is live as order flow flips in favor of the bulls.
Volume is ticking up across the board as momentum buyers step in to defend the breakout 📊 ⚡ 💬 Are you locking in early entries or waiting for confirmation near the upper targets? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #LongSetup #Crypto #Breakout
🔥 💎
Entry: 0.08871 ⚡
Target 1: 0.09068 🚀
Target 2: 0.09199 🎯
Target 3: 0.09395 💥
Stop Loss: 0.0874 ⚠️
Sellers exhausted themselves driving $SAFE down into a deep liquidity pocket, only for aggressive bids to sweep in and reclaim previous candle highs. This sudden structural shift confirms the recovery playbook is live as order flow flips in favor of the bulls.
Volume is ticking up across the board as momentum buyers step in to defend the breakout 📊 ⚡ 💬 Are you locking in early entries or waiting for confirmation near the upper targets? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #LongSetup #Crypto #Breakout
🔥 💎
3
·
--
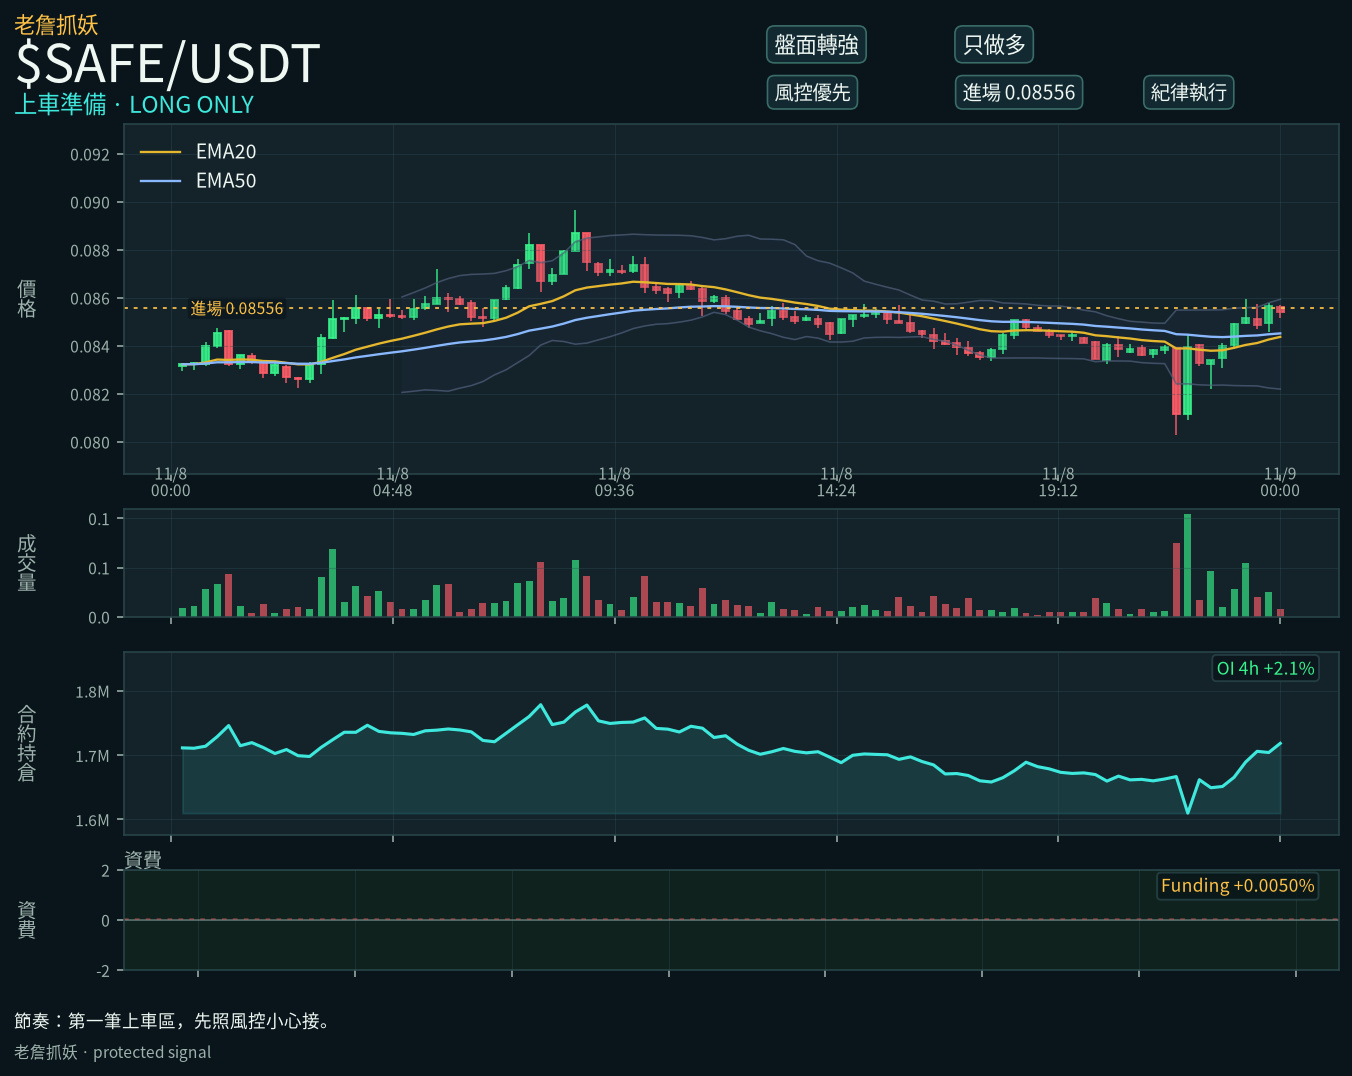
Plan your stop-loss first, then think about how much you can make
$SAFE People have started positioning early
New funds have come into the futures market within the past hour
The broader market hasn't stabilized yet, and trading volume is still a bit uneven
Cut your position in half, set the stop-loss at 0.07273, and take profit on 30% at 0.09412 first
#SAFE #wildcoin
Plan your stop-loss first, then think about how much you can make
$SAFE People have started positioning early
New funds have come into the futures market within the past hour
The broader market hasn't stabilized yet, and trading volume is still a bit uneven
Cut your position in half, set the stop-loss at 0.07273, and take profit on 30% at 0.09412 first
#SAFE #wildcoin
$SAFE People have started positioning early
New funds have come into the futures market within the past hour
The broader market hasn't stabilized yet, and trading volume is still a bit uneven
Cut your position in half, set the stop-loss at 0.07273, and take profit on 30% at 0.09412 first
#SAFE #wildcoin
89
·
--
🛡️ SECURITY AND IDENTITY MATTER IN WEB3!
$SAFE is connected to smart account and multisignature wallet infrastructure.
$MASK focuses on bringing Web3 features to social platforms.
$CYBER supports a social-focused Web3 ecosystem.
Adoption and practical utility are the metrics worth following.
#Safe #MaskNetwork #CyberConnect #Web3Social #CryptoUtility
🛡️ SECURITY AND IDENTITY MATTER IN WEB3!
$SAFE is connected to smart account and multisignature wallet infrastructure.
$MASK focuses on bringing Web3 features to social platforms.
$CYBER supports a social-focused Web3 ecosystem.
Adoption and practical utility are the metrics worth following.
#Safe #MaskNetwork #CyberConnect #Web3Social #CryptoUtility
$SAFE is connected to smart account and multisignature wallet infrastructure.
$MASK focuses on bringing Web3 features to social platforms.
$CYBER supports a social-focused Web3 ecosystem.
Adoption and practical utility are the metrics worth following.
#Safe #MaskNetwork #CyberConnect #Web3Social #CryptoUtility
1
28

·
--
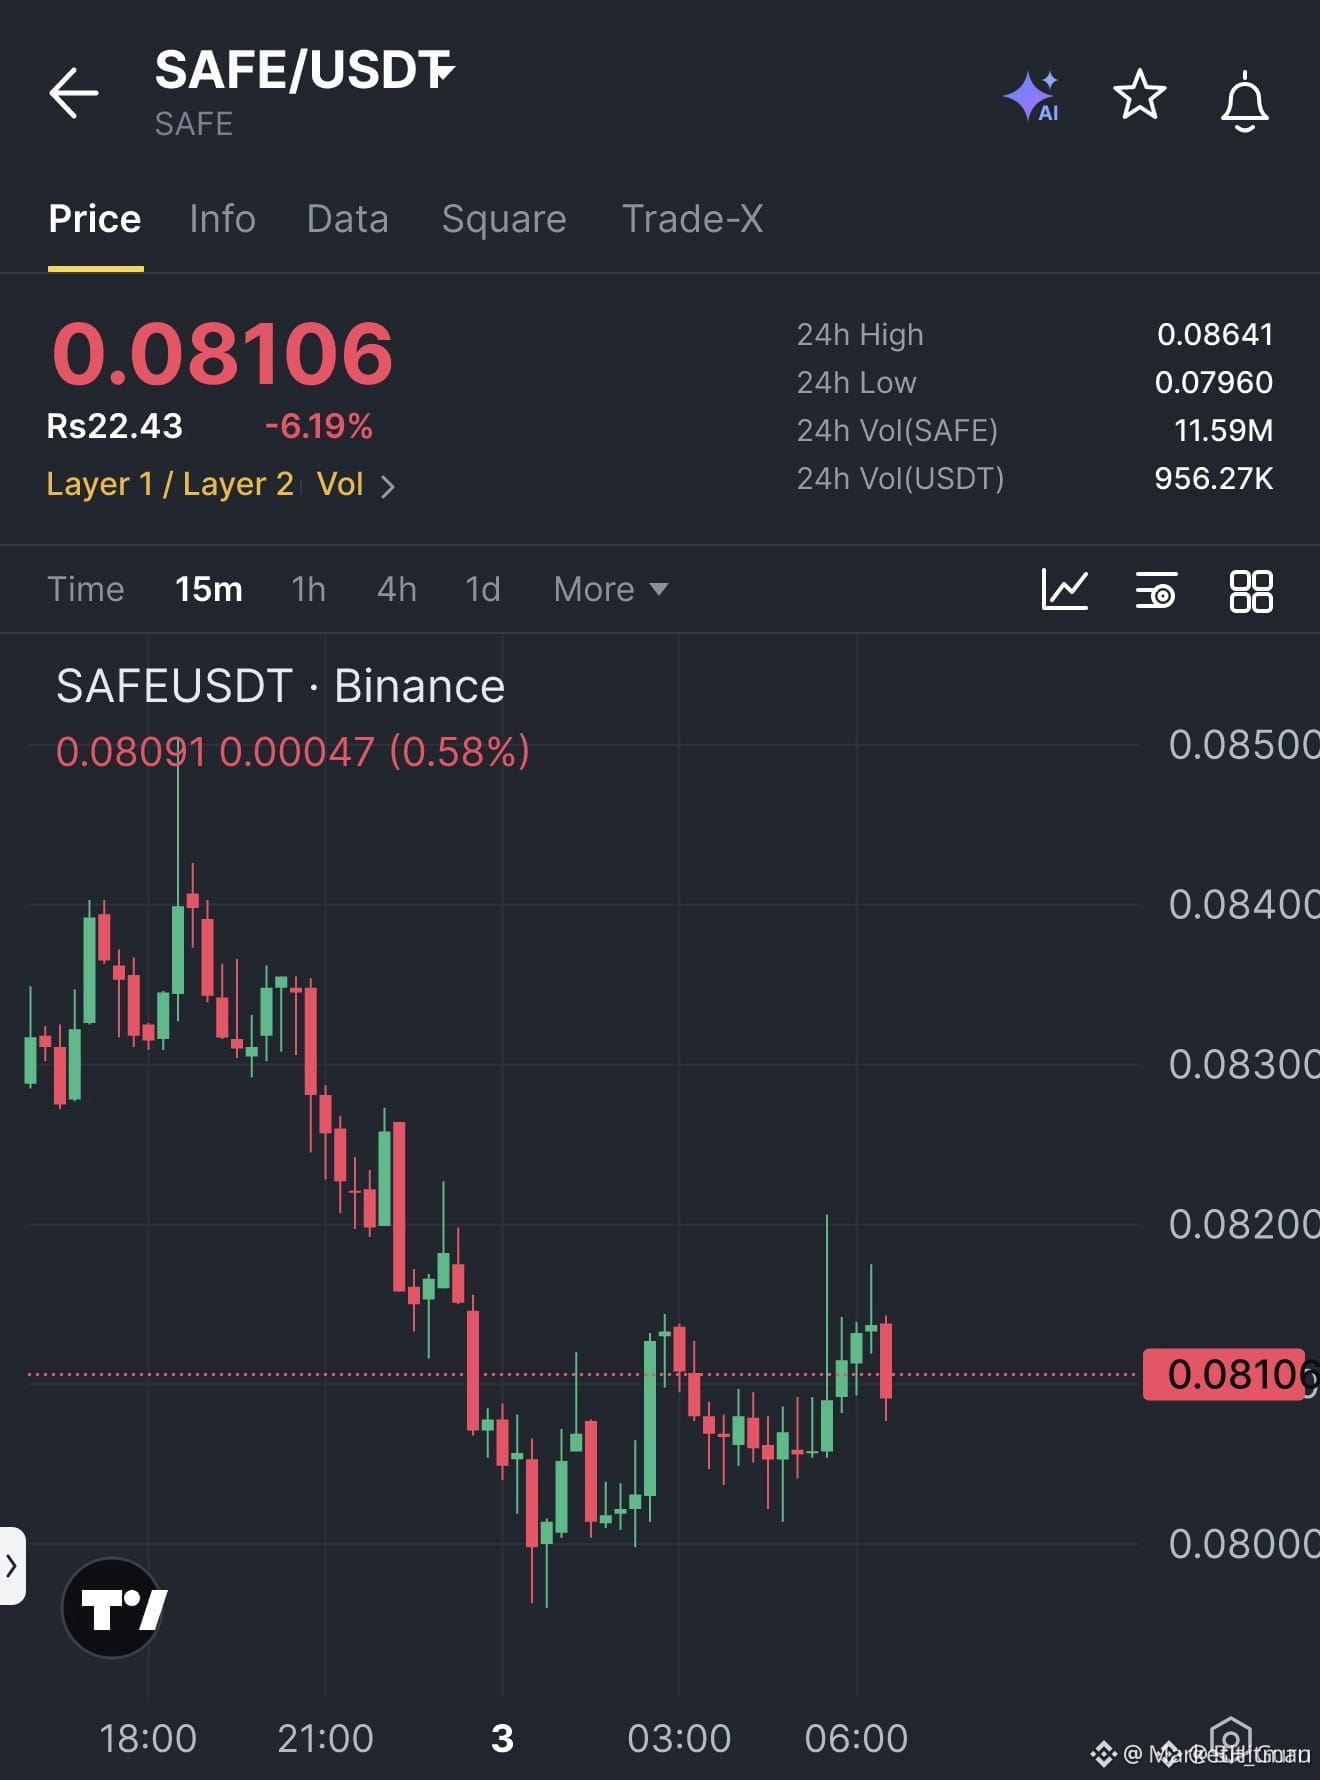
🔴 $SAFE SHORT SETUP FIRES WITH QUICK PULLBACK POTENTIAL! 🚀
Entry: 0.08106 ⚡
Stop Loss: 0.08181 ⚠️
Target: 0.07993, 0.07918, 0.07806 🚀
📊 Sellers just ripped the low of the previous candle after a hard‑fought rally, flipping the market into a clean short bias. The order flow shows a fresh liquidity sweep, with smart‑money whales swallowing the last sliver of buy pressure 🦈.
⚡ Entry sits at 0.08106, stop just above the broken low at 0.08181, and a tiered target ladder down to 0.07806 📌. Volume spikes on the 1‑hour chart confirm the momentum shift, while RSI drifts into oversold, signaling more downside potential.
💬 Are you ready to ride this pullback or waiting for a deeper dip? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #ShortSetup #Crypto #LiquiditySweep
🔥 💎
🔴 $SAFE SHORT SETUP FIRES WITH QUICK PULLBACK POTENTIAL! 🚀
Entry: 0.08106 ⚡
Stop Loss: 0.08181 ⚠️
Target: 0.07993, 0.07918, 0.07806 🚀
📊 Sellers just ripped the low of the previous candle after a hard‑fought rally, flipping the market into a clean short bias. The order flow shows a fresh liquidity sweep, with smart‑money whales swallowing the last sliver of buy pressure 🦈.
⚡ Entry sits at 0.08106, stop just above the broken low at 0.08181, and a tiered target ladder down to 0.07806 📌. Volume spikes on the 1‑hour chart confirm the momentum shift, while RSI drifts into oversold, signaling more downside potential.
💬 Are you ready to ride this pullback or waiting for a deeper dip? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #ShortSetup #Crypto #LiquiditySweep
🔥 💎
Entry: 0.08106 ⚡
Stop Loss: 0.08181 ⚠️
Target: 0.07993, 0.07918, 0.07806 🚀
📊 Sellers just ripped the low of the previous candle after a hard‑fought rally, flipping the market into a clean short bias. The order flow shows a fresh liquidity sweep, with smart‑money whales swallowing the last sliver of buy pressure 🦈.
⚡ Entry sits at 0.08106, stop just above the broken low at 0.08181, and a tiered target ladder down to 0.07806 📌. Volume spikes on the 1‑hour chart confirm the momentum shift, while RSI drifts into oversold, signaling more downside potential.
💬 Are you ready to ride this pullback or waiting for a deeper dip? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #ShortSetup #Crypto #LiquiditySweep
🔥 💎
10

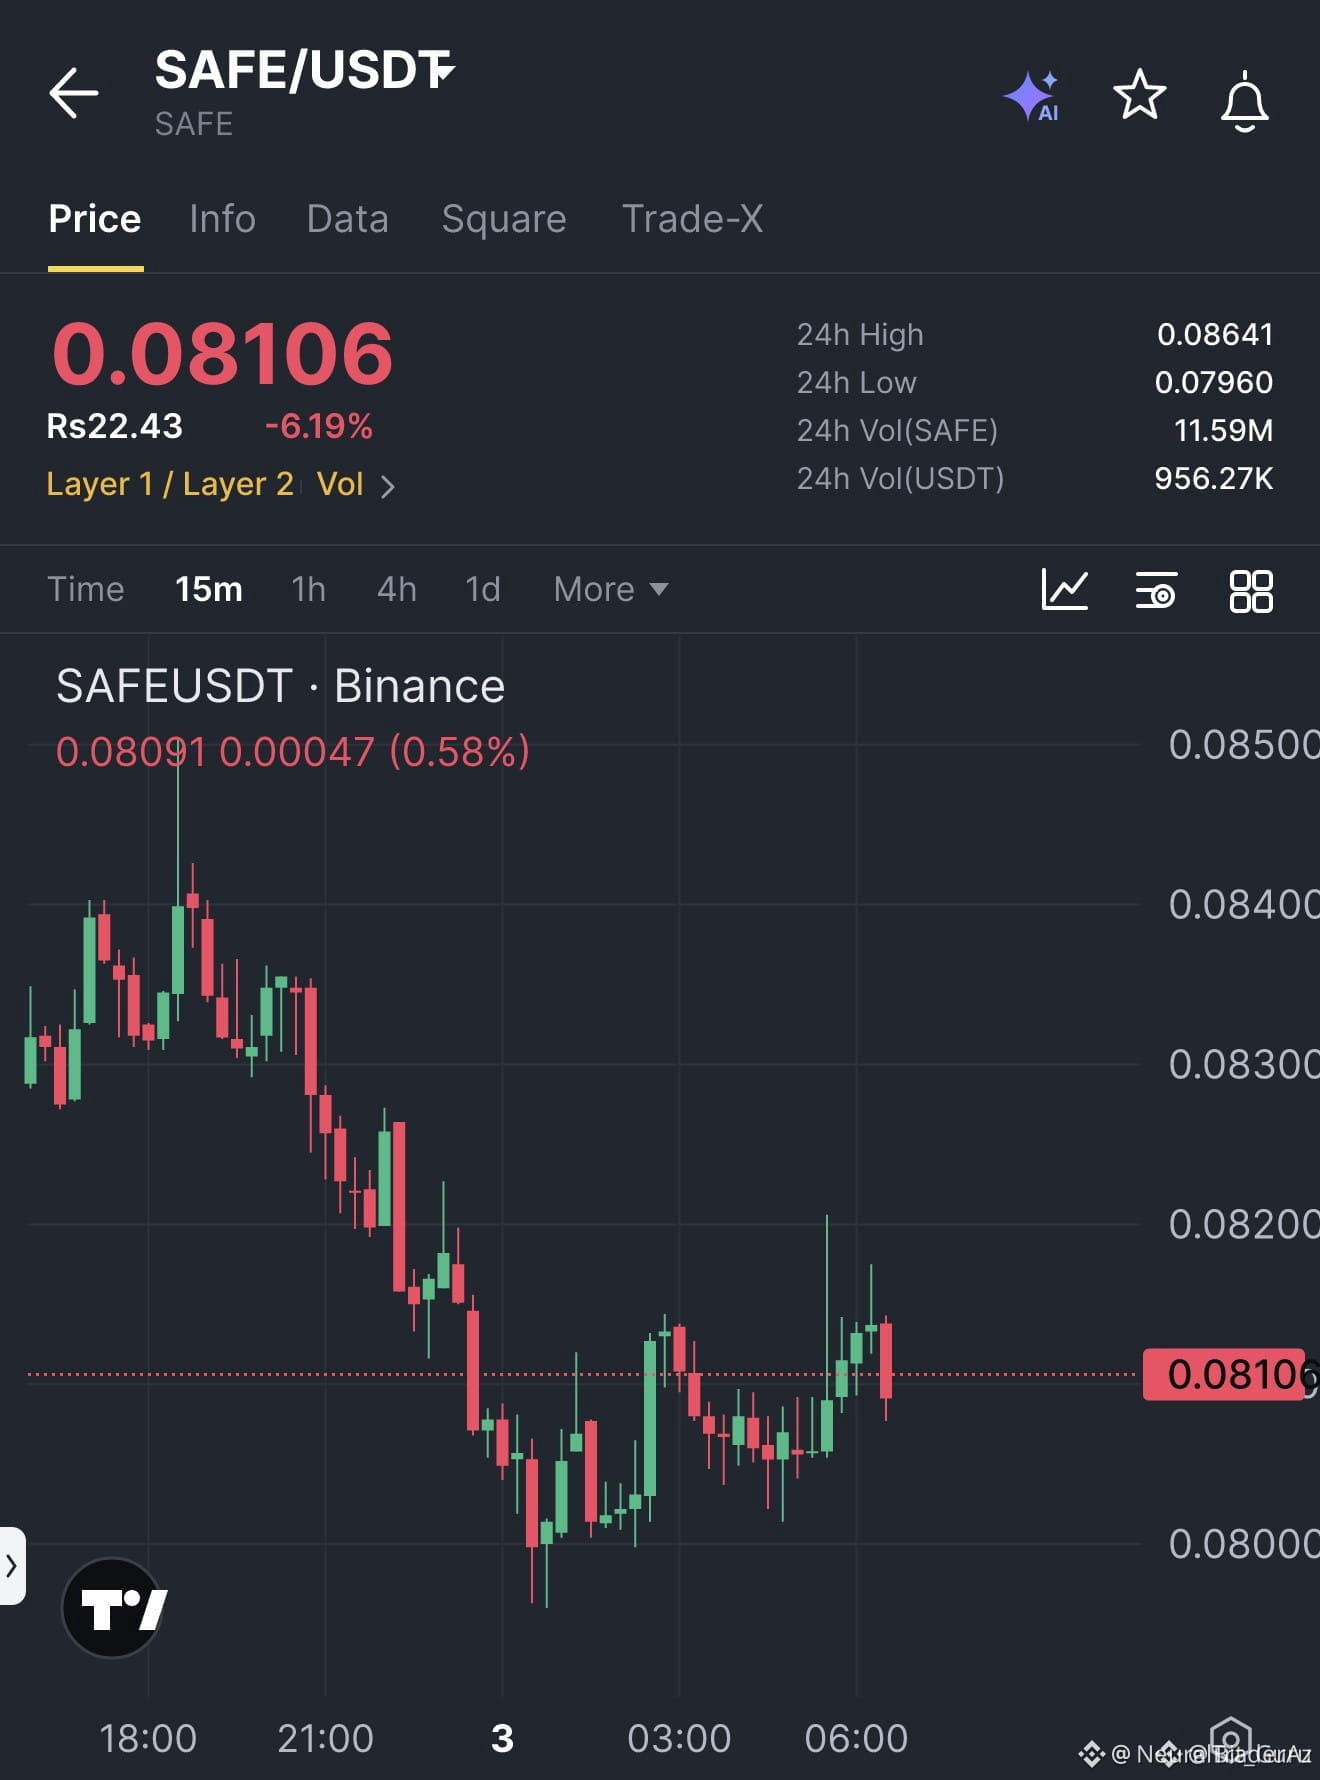
🔴🦈 $SAFE BEARISH LIQUIDITY SWEEP SET TO CRUSH ABOVE 0.08181!
Entry: 0.08106 ⚡
Target: 0.07993 🎯
Target: 0.07918 🎯
Target: 0.07806 🎯
Stop Loss: 0.08181 ⚠️
📊 Sellers shattered the prior candle low after a prolonged rise, exposing a fresh demand zone. 🦈 The breakout triggered a classic liquidity hunt, forcing the market into a controlled pull‑back. 📌 With order flow now aligning under the broken low, the short bias gains institutional backing and volume confirmation on the 4H.
💡 Risk‑to‑reward stacks neatly across three tiers, letting you scale out as price respects each liquidity pocket. 💬 Are you ready to short $SAFE on this liquidity bite? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #ShortSetup #LiquiditySweep #Crypto
🦈 🔥
🔴🦈 $SAFE BEARISH LIQUIDITY SWEEP SET TO CRUSH ABOVE 0.08181!
Entry: 0.08106 ⚡
Target: 0.07993 🎯
Target: 0.07918 🎯
Target: 0.07806 🎯
Stop Loss: 0.08181 ⚠️
📊 Sellers shattered the prior candle low after a prolonged rise, exposing a fresh demand zone. 🦈 The breakout triggered a classic liquidity hunt, forcing the market into a controlled pull‑back. 📌 With order flow now aligning under the broken low, the short bias gains institutional backing and volume confirmation on the 4H.
💡 Risk‑to‑reward stacks neatly across three tiers, letting you scale out as price respects each liquidity pocket. 💬 Are you ready to short $SAFE on this liquidity bite? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #ShortSetup #LiquiditySweep #Crypto
🦈 🔥
Entry: 0.08106 ⚡
Target: 0.07993 🎯
Target: 0.07918 🎯
Target: 0.07806 🎯
Stop Loss: 0.08181 ⚠️
📊 Sellers shattered the prior candle low after a prolonged rise, exposing a fresh demand zone. 🦈 The breakout triggered a classic liquidity hunt, forcing the market into a controlled pull‑back. 📌 With order flow now aligning under the broken low, the short bias gains institutional backing and volume confirmation on the 4H.
💡 Risk‑to‑reward stacks neatly across three tiers, letting you scale out as price respects each liquidity pocket. 💬 Are you ready to short $SAFE on this liquidity bite? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #SAFE #ShortSetup #LiquiditySweep #Crypto
🦈 🔥
5
·
--
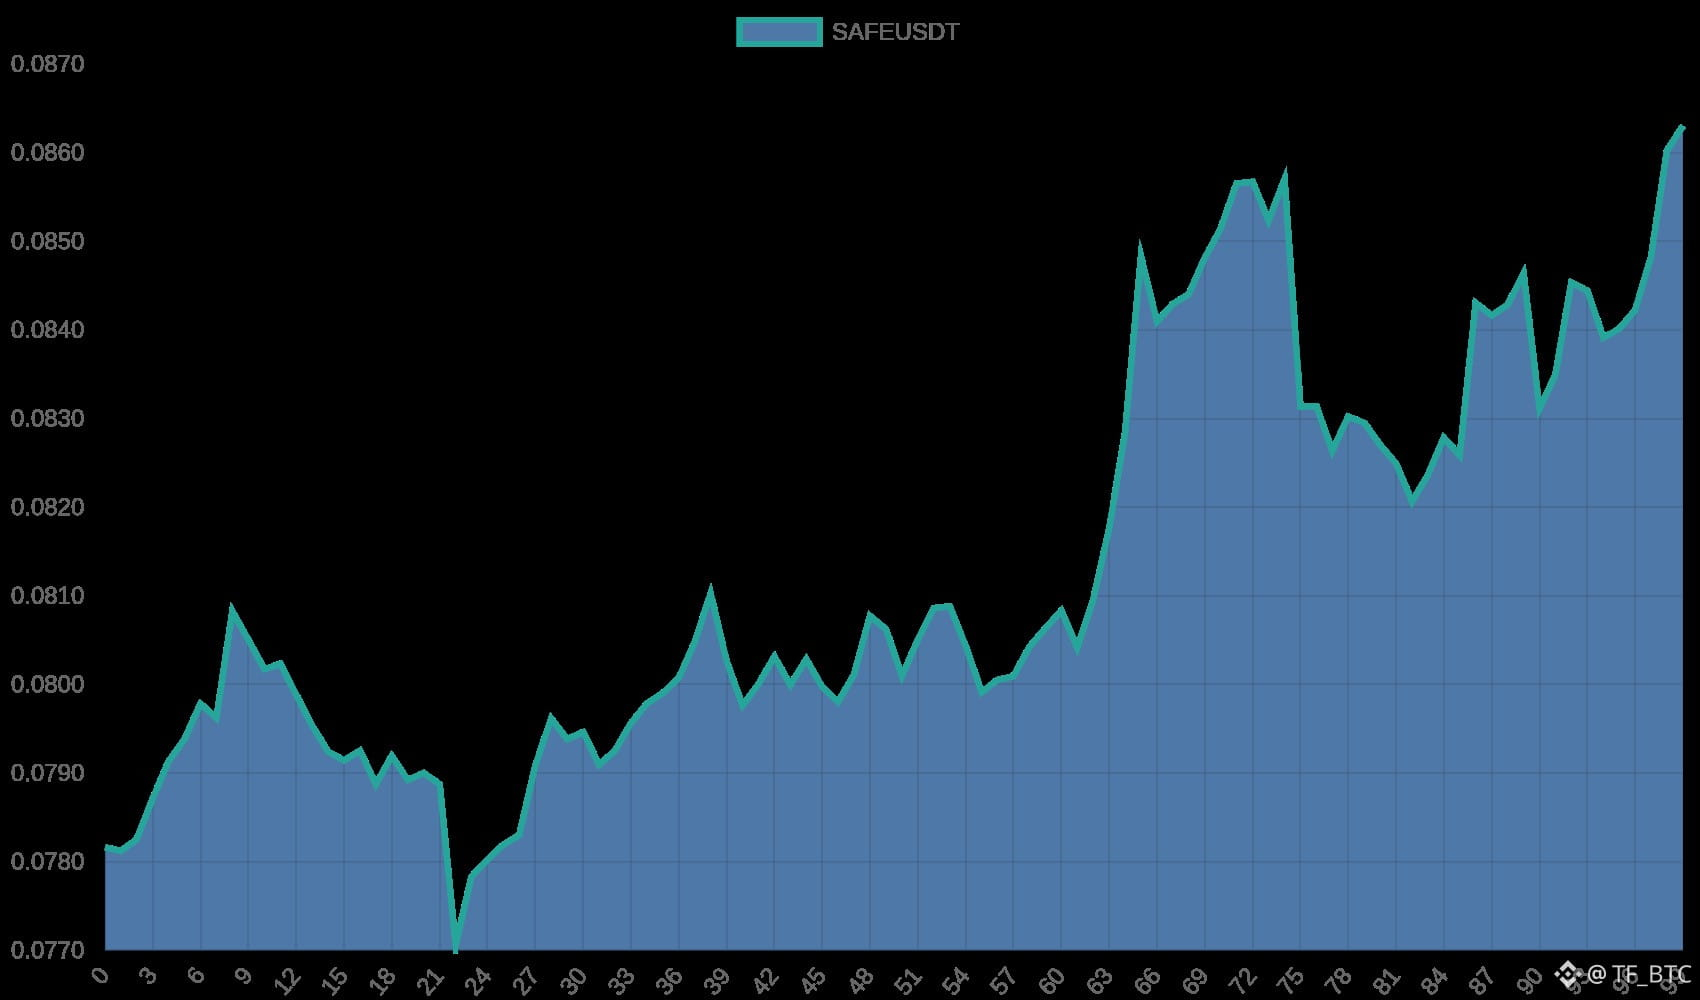
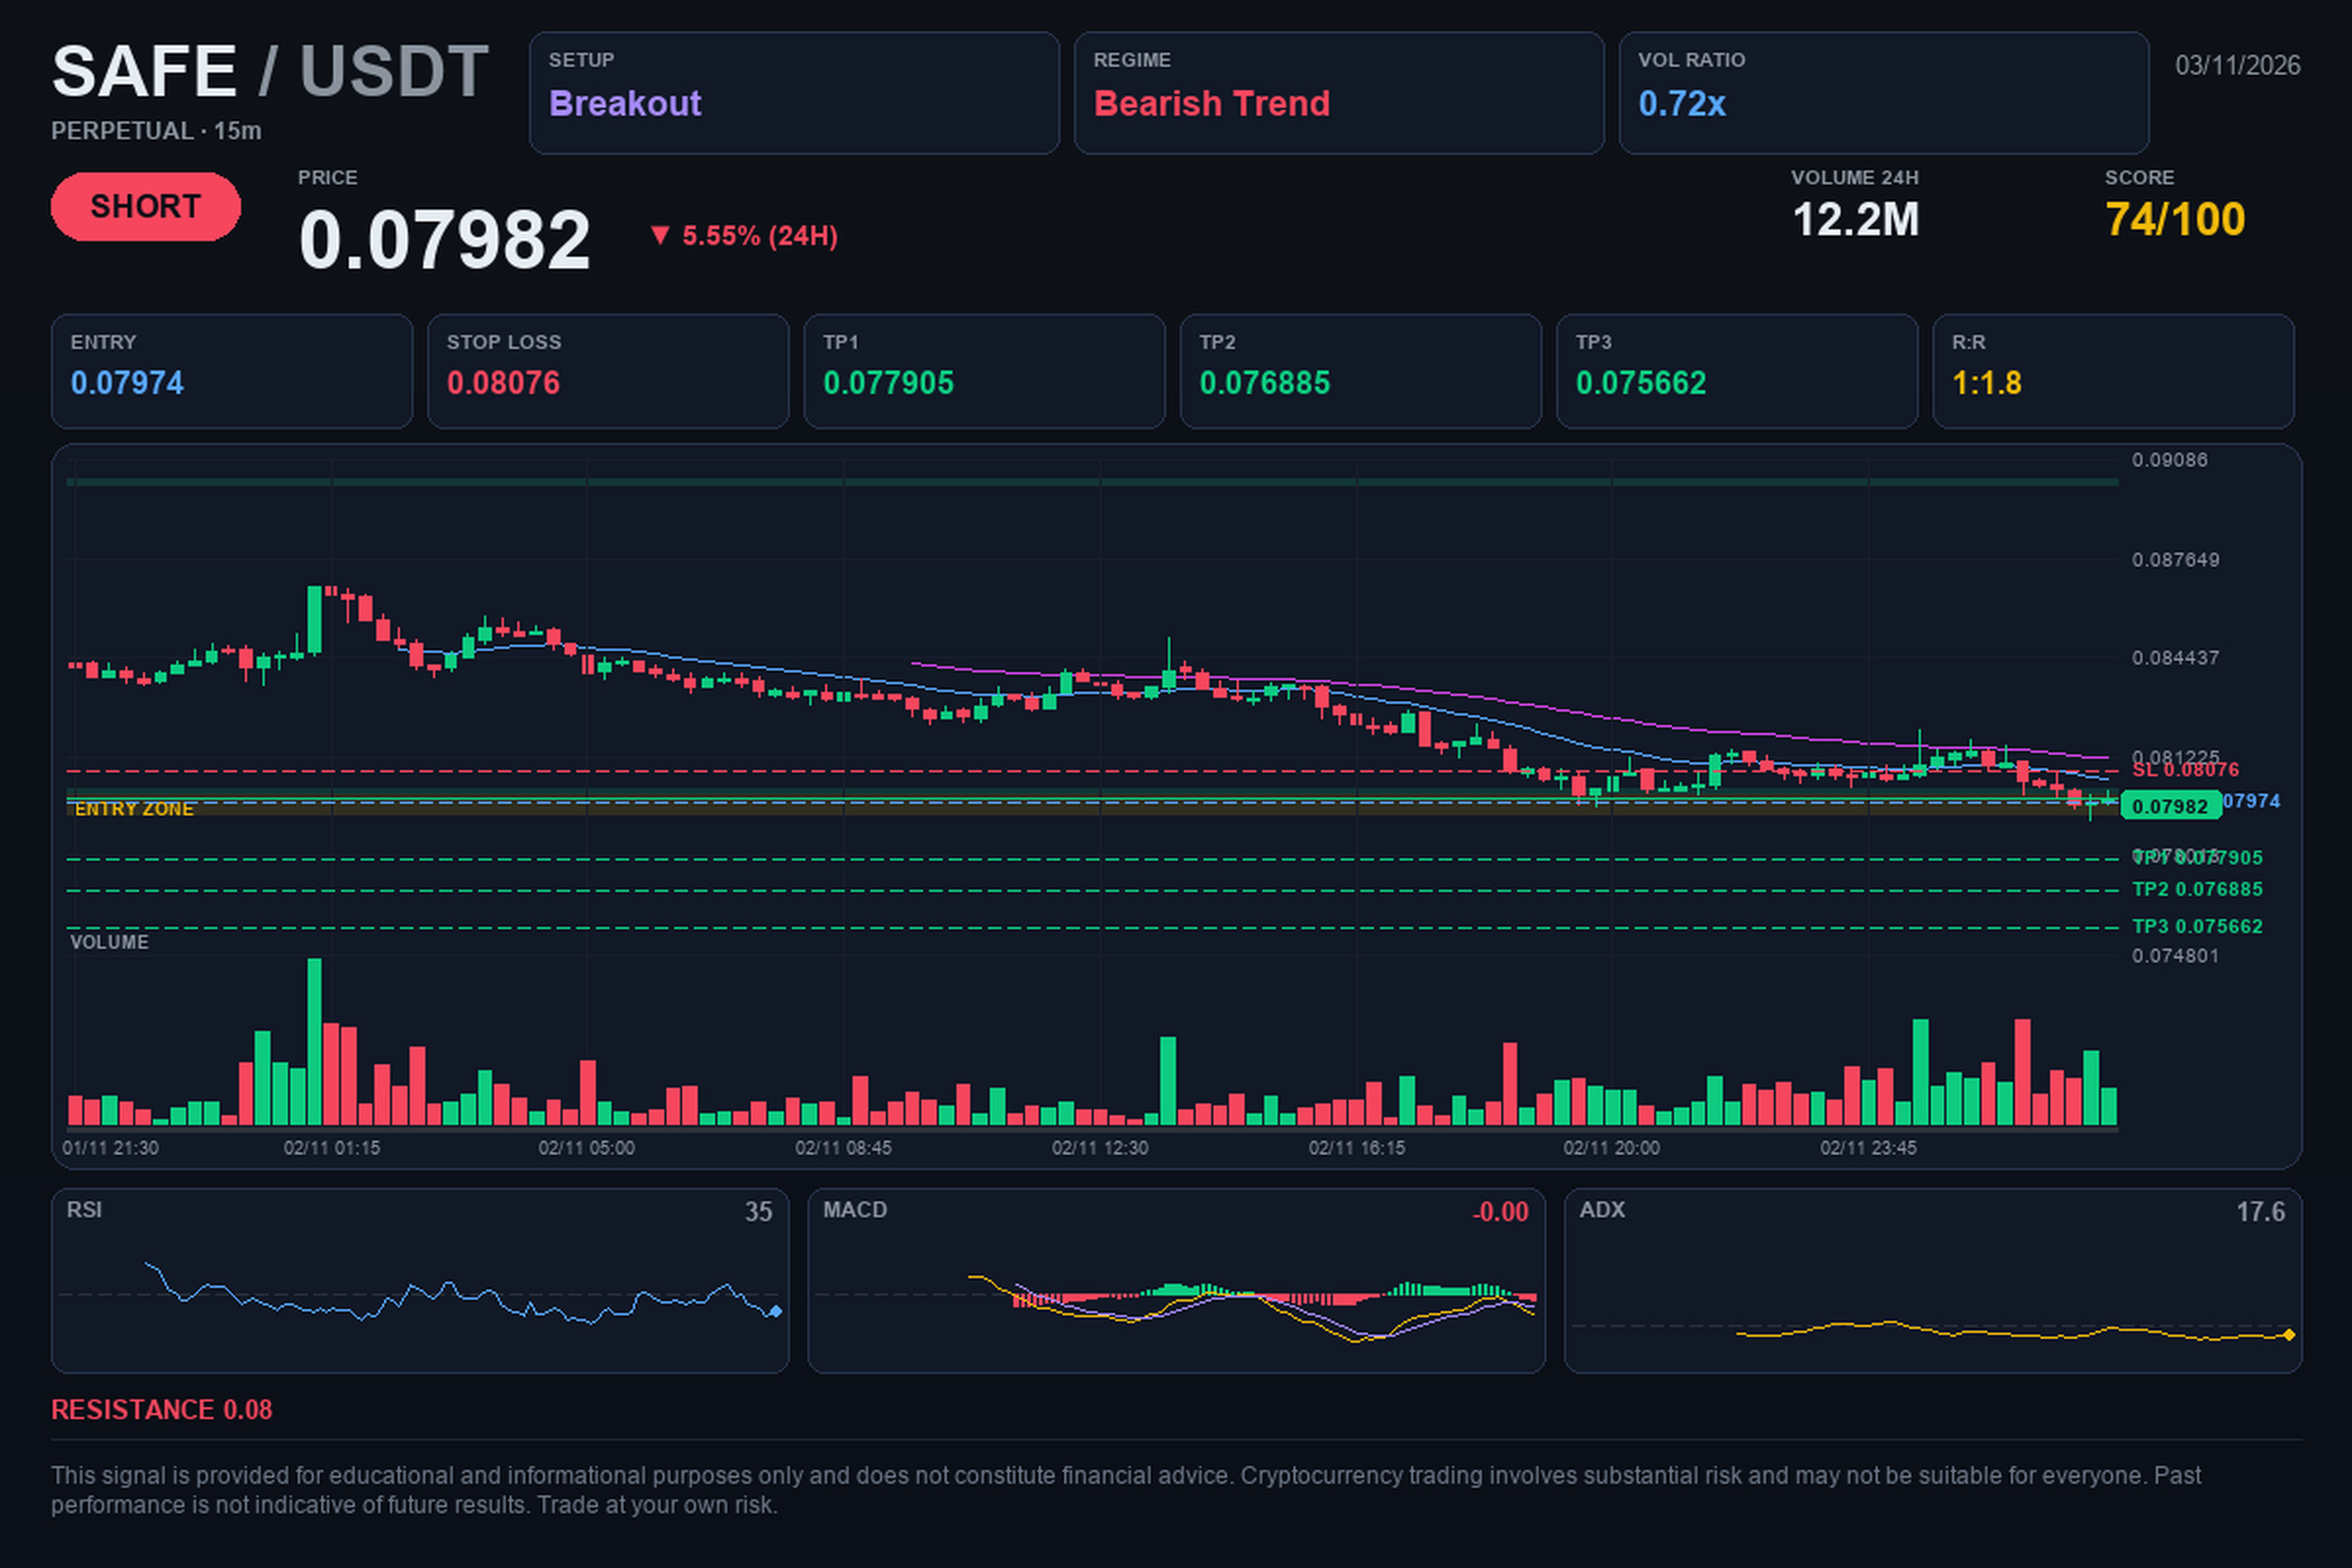
📢 $SAFE / USDT | 🔴 SHORT | ⭐ 74%
🎯 Target: $0.0779048. Will it reach it?
🎯 Trading levels:
🔴 Entry: $0.07974
🛑 Stop Loss: $0.08076
🏁 TP1: $0.077905
🏁 TP2: $0.076885
🏁 TP3: $0.075662
📈 Analysis:
The market shows a clear bearish structure, with confirmed support breaks across multiple timeframes. Selling pressure is supported by a significant increase in trading volume, which is above average, while the relative strength indicator remains at weak levels. This combination of factors suggests that sellers are in control in the short term.
⚖️ Risk/Reward: 1:1.8
⏱️ Timeframe: 15M
#crypto #SAFE #trading #Bearish
💡 This analysis is for educational purposes and does not constitute financial advice. Do your own research and make your decision calmly.
📢 $SAFE / USDT | 🔴 SHORT | ⭐ 74%
🎯 Target: $0.0779048. Will it reach it?
🎯 Trading levels:
🔴 Entry: $0.07974
🛑 Stop Loss: $0.08076
🏁 TP1: $0.077905
🏁 TP2: $0.076885
🏁 TP3: $0.075662
📈 Analysis:
The market shows a clear bearish structure, with confirmed support breaks across multiple timeframes. Selling pressure is supported by a significant increase in trading volume, which is above average, while the relative strength indicator remains at weak levels. This combination of factors suggests that sellers are in control in the short term.
⚖️ Risk/Reward: 1:1.8
⏱️ Timeframe: 15M
#crypto #SAFE #trading #Bearish
💡 This analysis is for educational purposes and does not constitute financial advice. Do your own research and make your decision calmly.
🎯 Target: $0.0779048. Will it reach it?
🎯 Trading levels:
🔴 Entry: $0.07974
🛑 Stop Loss: $0.08076
🏁 TP1: $0.077905
🏁 TP2: $0.076885
🏁 TP3: $0.075662
📈 Analysis:
The market shows a clear bearish structure, with confirmed support breaks across multiple timeframes. Selling pressure is supported by a significant increase in trading volume, which is above average, while the relative strength indicator remains at weak levels. This combination of factors suggests that sellers are in control in the short term.
⚖️ Risk/Reward: 1:1.8
⏱️ Timeframe: 15M
#crypto #SAFE #trading #Bearish
💡 This analysis is for educational purposes and does not constitute financial advice. Do your own research and make your decision calmly.
2
·
--
🔍 INFRASTRUCTURE AND SECURITY IN FOCUS! $SAFE , $SAGA , and $OMNI offer different approaches to blockchain infrastructure and ecosystem tooling. Review their current development, usage, and token economics. Strong narratives can create volatility in both directions, so plan for downside too.
#Safe #Saga #OmniNetwork #BlockchainTech #CryptoAnalysis
🔍 INFRASTRUCTURE AND SECURITY IN FOCUS! $SAFE , $SAGA , and $OMNI offer different approaches to blockchain infrastructure and ecosystem tooling. Review their current development, usage, and token economics. Strong narratives can create volatility in both directions, so plan for downside too.
#Safe #Saga #OmniNetwork #BlockchainTech #CryptoAnalysis
#Safe #Saga #OmniNetwork #BlockchainTech #CryptoAnalysis
1
31
·
--
🛡️ WALLET SECURITY AND DATA INFRASTRUCTURE MATTER!
$SAFE (SAFE) • $T (T) • $CXT.US (CXT)
SAFE is associated with smart-account security, T with threshold cryptography and decentralized services, and CXT with blockchain data infrastructure.
Security-focused technology still carries implementation, adoption, and market risks. Read project documentation and examine real usage before forming an investment view.
#Safe #Threshold #Covalent #CryptoSecuri #Web3
Disclaimer: This is for informational purposes only, not financial advice. Crypto assets are highly volatile. DYOR.
🛡️ WALLET SECURITY AND DATA INFRASTRUCTURE MATTER!
$SAFE (SAFE) • $T (T) • $CXT.US (CXT)
SAFE is associated with smart-account security, T with threshold cryptography and decentralized services, and CXT with blockchain data infrastructure.
Security-focused technology still carries implementation, adoption, and market risks. Read project documentation and examine real usage before forming an investment view.
#Safe #Threshold #Covalent #CryptoSecuri #Web3
Disclaimer: This is for informational purposes only, not financial advice. Crypto assets are highly volatile. DYOR.
$SAFE (SAFE) • $T (T) • $CXT.US (CXT)
SAFE is associated with smart-account security, T with threshold cryptography and decentralized services, and CXT with blockchain data infrastructure.
Security-focused technology still carries implementation, adoption, and market risks. Read project documentation and examine real usage before forming an investment view.
#Safe #Threshold #Covalent #CryptoSecuri #Web3
Disclaimer: This is for informational purposes only, not financial advice. Crypto assets are highly volatile. DYOR.
1
9
·
--
The hardware wallet space has a new development. Safe has announced that pre-orders are open for its Exclusive Hardware Wallet, signaling that its smart wallet and multisig security capabilities are expanding to offline signing devices.
For long-term holders, keeping private keys offline remains the most fundamental risk control. But what matters more is whether the hardware device works seamlessly with multisig accounts, permission management, and recovery processes—not simply whether it adds another hurdle to using the wallet. $SAFE ’s move from smart contract wallets to hardware is noteworthy not just for the pre-sale buzz, but for whether self-custody can truly become simpler and safer.
Before ordering, consider checking the shipping timeline, supported regions, firmware updates, and after-sales policies. There’s no need to make an impulse purchase based on claims of being “exclusive” or “limited edition.” After all, self-custody is not about owning a particular device, but about clearly understanding your signing permissions and backup plan.
#SAFE #硬件钱包 #SelfCustody
The hardware wallet space has a new development. Safe has announced that pre-orders are open for its Exclusive Hardware Wallet, signaling that its smart wallet and multisig security capabilities are expanding to offline signing devices.
For long-term holders, keeping private keys offline remains the most fundamental risk control. But what matters more is whether the hardware device works seamlessly with multisig accounts, permission management, and recovery processes—not simply whether it adds another hurdle to using the wallet. $SAFE ’s move from smart contract wallets to hardware is noteworthy not just for the pre-sale buzz, but for whether self-custody can truly become simpler and safer.
Before ordering, consider checking the shipping timeline, supported regions, firmware updates, and after-sales policies. There’s no need to make an impulse purchase based on claims of being “exclusive” or “limited edition.” After all, self-custody is not about owning a particular device, but about clearly understanding your signing permissions and backup plan.
#SAFE #硬件钱包 #SelfCustody
For long-term holders, keeping private keys offline remains the most fundamental risk control. But what matters more is whether the hardware device works seamlessly with multisig accounts, permission management, and recovery processes—not simply whether it adds another hurdle to using the wallet. $SAFE ’s move from smart contract wallets to hardware is noteworthy not just for the pre-sale buzz, but for whether self-custody can truly become simpler and safer.
Before ordering, consider checking the shipping timeline, supported regions, firmware updates, and after-sales policies. There’s no need to make an impulse purchase based on claims of being “exclusive” or “limited edition.” After all, self-custody is not about owning a particular device, but about clearly understanding your signing permissions and backup plan.
#SAFE #硬件钱包 #SelfCustody
59
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#NvidiaEarningsTonight:AIStocks’NextMove?
29,795 views
504 Discussing
2
#A Packed Week of Earnings and Data Tests Markets
109,687 views
565 Discussing
3
#AnthropicIPOTestsInvestorAppetiteForAI
230,559 views
2,289 Discussing
4
#NvidiaBoardNotConsideringHuang’sReturnasCEO
53,543 views
588 Discussing
5
#KOSPIFalls2.59%ToLowestCloseSinceFebruary
544 views
33 Discussing
6
#AnthropicClearedToListOnNasdaqAsANT
1,869 views
61 Discussing
7
#WhatInvestmentSignalsDo13FFilingsReveal?
30,699 views
446 Discussing
8
#EvernorthRecords$505MImpairmentOnPreListingXRP
708 views
14 Discussing
9
#GoldmanSachsReports$1.22BInEtherETFHoldings
551 views
8 Discussing
10
#GoldmanSachsAndMillenniumEachHeldOver$1.2BInBitcoinETFs
4,936 views
13 Discussing