
#security
security
2M views
6,334 Discussing
Hot
Latest

🚨 $NAORIS EYEING SUPPLY-CHAIN SECURITY NARRATIVES AS TRADITIONAL FINANCE FACES VENDOR BREACHES
Recent legacy banking infrastructure vulnerabilities highlight the urgent demand for decentralized cryptographic verification across third-party networks. 📊 As institutional capital reassesses systemic counterparty exposure, on-chain security protocols are stepping into the spotlight.
Assets like $YB and $LUNC are also catching structural attention as market participants re-evaluate network integrity and data handling standards. 💡 The macroeconomic shift toward robust cybersecurity solutions creates an evolving liquidity footprint for specialized decentralized layers.
How is your portfolio positioned to capture capital rotation into infrastructure security plays? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #NAORIS #Security #MarketStructure #Crypto
🔥
🚨 $NAORIS EYEING SUPPLY-CHAIN SECURITY NARRATIVES AS TRADITIONAL FINANCE FACES VENDOR BREACHES
Recent legacy banking infrastructure vulnerabilities highlight the urgent demand for decentralized cryptographic verification across third-party networks. 📊 As institutional capital reassesses systemic counterparty exposure, on-chain security protocols are stepping into the spotlight.
Assets like $YB and $LUNC are also catching structural attention as market participants re-evaluate network integrity and data handling standards. 💡 The macroeconomic shift toward robust cybersecurity solutions creates an evolving liquidity footprint for specialized decentralized layers.
How is your portfolio positioned to capture capital rotation into infrastructure security plays? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #NAORIS #Security #MarketStructure #Crypto
🔥
Recent legacy banking infrastructure vulnerabilities highlight the urgent demand for decentralized cryptographic verification across third-party networks. 📊 As institutional capital reassesses systemic counterparty exposure, on-chain security protocols are stepping into the spotlight.
Assets like $YB and $LUNC are also catching structural attention as market participants re-evaluate network integrity and data handling standards. 💡 The macroeconomic shift toward robust cybersecurity solutions creates an evolving liquidity footprint for specialized decentralized layers.
How is your portfolio positioned to capture capital rotation into infrastructure security plays? 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #NAORIS #Security #MarketStructure #Crypto
🔥
5

Security Risks Emerge as Illicit Funds Linked to Sky Ecosystem
Recent investigations have traced $518 million in illicit activity to a reserve backing stablecoins like DAI and USDS.
This activity involves funds allegedly used by North Korean hackers in high-profile events, including the 2025 Bybit hack.
The findings place the Sky stablecoin protocol under intense scrutiny regarding its institutional finance ambitions and decentralized design.
WHY IT MATTERS: Security vulnerabilities within stablecoin reserves pose a systemic risk to the stability and regulatory acceptance of decentralized finance platforms.
MARKET IMPACT: Bearish, as security breaches and links to illicit activity often cause temporary instability for affected protocols and tokens.
How important is security auditing when you choose which stablecoins to hold?
#Security #DeFi #Stablecoins
Security Risks Emerge as Illicit Funds Linked to Sky Ecosystem
Recent investigations have traced $518 million in illicit activity to a reserve backing stablecoins like DAI and USDS.
This activity involves funds allegedly used by North Korean hackers in high-profile events, including the 2025 Bybit hack.
The findings place the Sky stablecoin protocol under intense scrutiny regarding its institutional finance ambitions and decentralized design.
WHY IT MATTERS: Security vulnerabilities within stablecoin reserves pose a systemic risk to the stability and regulatory acceptance of decentralized finance platforms.
MARKET IMPACT: Bearish, as security breaches and links to illicit activity often cause temporary instability for affected protocols and tokens.
How important is security auditing when you choose which stablecoins to hold?
#Security #DeFi #Stablecoins
Recent investigations have traced $518 million in illicit activity to a reserve backing stablecoins like DAI and USDS.
This activity involves funds allegedly used by North Korean hackers in high-profile events, including the 2025 Bybit hack.
The findings place the Sky stablecoin protocol under intense scrutiny regarding its institutional finance ambitions and decentralized design.
WHY IT MATTERS: Security vulnerabilities within stablecoin reserves pose a systemic risk to the stability and regulatory acceptance of decentralized finance platforms.
MARKET IMPACT: Bearish, as security breaches and links to illicit activity often cause temporary instability for affected protocols and tokens.
How important is security auditing when you choose which stablecoins to hold?
#Security #DeFi #Stablecoins
263

·
--
Traders on X are sounding the alarm, and this one is worth your attention. 🚨
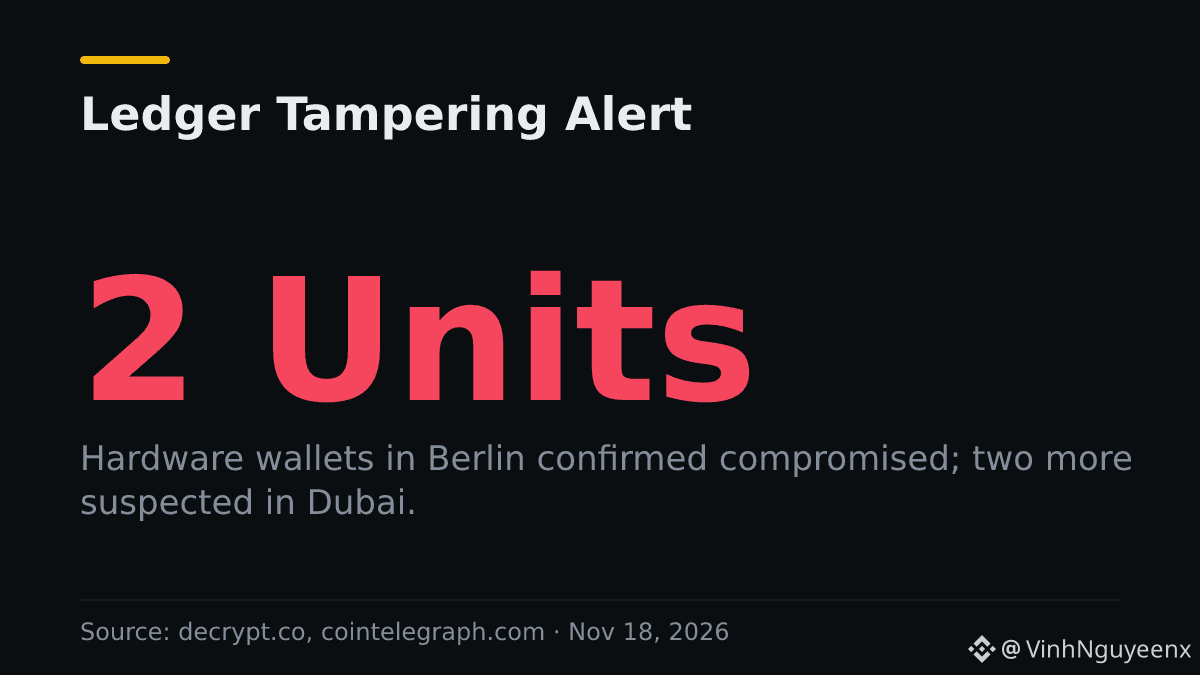
Ledger just confirmed tampered hardware wallets in Berlin, and it is investigating two more suspected units in Dubai. Every confirmed device carries the same physical modification, built to capture your 24-word recovery phrase during setup. On-chain investigators have traced a suspected ~$87M drain linked to the implants.
Ledger says there is no flaw in its chip or OS, and no confirmed case involves a device bought on ledger.com. Every tampered unit so far came through a third-party reseller.
Why it matters: this started as a Southeast Asia incident in October. Now it is in Europe, and Ledger expects more units to surface.
Action Required:
• Bought a Ledger in Berlin since Jan 2026? Contact Ledger Support
• Never set up or restore a wallet on a suspect device
• Move funds to a fresh wallet with a brand-new recovery phrase
• Free X-ray inspections at Ledger's Vierzon, France factory, for a limited time
Ledger will never ask for your 24 words. Anyone who does is a scammer.
Is your $BTC sitting on a Ledger bought from a reseller, or straight from ledger.com? 👇
Not financial advice. DYOR.
#crypto #Ledger #Security
Traders on X are sounding the alarm, and this one is worth your attention. 🚨
Ledger just confirmed tampered hardware wallets in Berlin, and it is investigating two more suspected units in Dubai. Every confirmed device carries the same physical modification, built to capture your 24-word recovery phrase during setup. On-chain investigators have traced a suspected ~$87M drain linked to the implants.
Ledger says there is no flaw in its chip or OS, and no confirmed case involves a device bought on ledger.com. Every tampered unit so far came through a third-party reseller.
Why it matters: this started as a Southeast Asia incident in October. Now it is in Europe, and Ledger expects more units to surface.
Action Required:
• Bought a Ledger in Berlin since Jan 2026? Contact Ledger Support
• Never set up or restore a wallet on a suspect device
• Move funds to a fresh wallet with a brand-new recovery phrase
• Free X-ray inspections at Ledger's Vierzon, France factory, for a limited time
Ledger will never ask for your 24 words. Anyone who does is a scammer.
Is your $BTC sitting on a Ledger bought from a reseller, or straight from ledger.com? 👇
Not financial advice. DYOR.
#crypto #Ledger #Security
Ledger just confirmed tampered hardware wallets in Berlin, and it is investigating two more suspected units in Dubai. Every confirmed device carries the same physical modification, built to capture your 24-word recovery phrase during setup. On-chain investigators have traced a suspected ~$87M drain linked to the implants.
Ledger says there is no flaw in its chip or OS, and no confirmed case involves a device bought on ledger.com. Every tampered unit so far came through a third-party reseller.
Why it matters: this started as a Southeast Asia incident in October. Now it is in Europe, and Ledger expects more units to surface.
Action Required:
• Bought a Ledger in Berlin since Jan 2026? Contact Ledger Support
• Never set up or restore a wallet on a suspect device
• Move funds to a fresh wallet with a brand-new recovery phrase
• Free X-ray inspections at Ledger's Vierzon, France factory, for a limited time
Ledger will never ask for your 24 words. Anyone who does is a scammer.
Is your $BTC sitting on a Ledger bought from a reseller, or straight from ledger.com? 👇
Not financial advice. DYOR.
#crypto #Ledger #Security
14
Article
Trezor Hit by Third Data Breach in 2023: Shipping Partners BlamedTrezor users are facing new risks after another major data breach linked to a third-party shipping partner, raising big questions about supply chain security in the crypto space.
On November 16, Trezor confirmed its third customer data breach of 2023. This time, the incident stemmed from Czech-based shipping provider Skladon, which suffered an intrusion that exposed sensitive data tied to about 27,000 orders placed between August 9 and November 7. The compromised info includes full names, phone numbers, delivery addresses, email addresses, and product details. Importantly, Trezor states that wallet PINs and recovery phrases were not affected.
This is the third such breach for Trezor in just four months:
• In August, logistics partner ShipMonk was breached, with the affected user count eventually surpassing 80,000.
• In September, marketing platform Brevo leaked the email addresses of roughly 347,149 newsletter subscribers.
• Now, the Skladon incident adds to the toll, all involving different types of customer data.
Trezor has stressed that no hardware wallets or their backups were compromised. However, some users have reported suspicious phone calls following these leaks, raising fears about phishing and even physical threats due to the exposure of home addresses. Trezor has warned users to be cautious of unsolicited communication and never to share wallet backups.
To address privacy concerns, Trezor has rolled out Anonymous Pickup in 18 European countries, letting buyers collect hardware wallets using only a nickname and email at pickup points. The company is also reducing its data retention window from 90 days to 45 days to limit exposure.
Despite these steps, more than half a million customer records have been exposed since August, and uncertainty remains about whether further fraudulent activity or physical threats will emerge from the Skladon breach.
Will these privacy efforts be enough to regain user trust, or is Trezor facing deeper reputational risks?
#Trezor #bitcoin #security #brevo
Trezor Hit by Third Data Breach in 2023: Shipping Partners Blamed
Trezor users are facing new risks after another major data breach linked to a third-party shipping partner, raising big questions about supply chain security in the crypto space.
On November 16, Trezor confirmed its third customer data breach of 2023. This time, the incident stemmed from Czech-based shipping provider Skladon, which suffered an intrusion that exposed sensitive data tied to about 27,000 orders placed between August 9 and November 7. The compromised info includes full names, phone numbers, delivery addresses, email addresses, and product details. Importantly, Trezor states that wallet PINs and recovery phrases were not affected.
This is the third such breach for Trezor in just four months:
• In August, logistics partner ShipMonk was breached, with the affected user count eventually surpassing 80,000.
• In September, marketing platform Brevo leaked the email addresses of roughly 347,149 newsletter subscribers.
• Now, the Skladon incident adds to the toll, all involving different types of customer data.
Trezor has stressed that no hardware wallets or their backups were compromised. However, some users have reported suspicious phone calls following these leaks, raising fears about phishing and even physical threats due to the exposure of home addresses. Trezor has warned users to be cautious of unsolicited communication and never to share wallet backups.
To address privacy concerns, Trezor has rolled out Anonymous Pickup in 18 European countries, letting buyers collect hardware wallets using only a nickname and email at pickup points. The company is also reducing its data retention window from 90 days to 45 days to limit exposure.
Despite these steps, more than half a million customer records have been exposed since August, and uncertainty remains about whether further fraudulent activity or physical threats will emerge from the Skladon breach.
Will these privacy efforts be enough to regain user trust, or is Trezor facing deeper reputational risks?
#Trezor #bitcoin #security #brevo
On November 16, Trezor confirmed its third customer data breach of 2023. This time, the incident stemmed from Czech-based shipping provider Skladon, which suffered an intrusion that exposed sensitive data tied to about 27,000 orders placed between August 9 and November 7. The compromised info includes full names, phone numbers, delivery addresses, email addresses, and product details. Importantly, Trezor states that wallet PINs and recovery phrases were not affected.
This is the third such breach for Trezor in just four months:
• In August, logistics partner ShipMonk was breached, with the affected user count eventually surpassing 80,000.
• In September, marketing platform Brevo leaked the email addresses of roughly 347,149 newsletter subscribers.
• Now, the Skladon incident adds to the toll, all involving different types of customer data.
Trezor has stressed that no hardware wallets or their backups were compromised. However, some users have reported suspicious phone calls following these leaks, raising fears about phishing and even physical threats due to the exposure of home addresses. Trezor has warned users to be cautious of unsolicited communication and never to share wallet backups.
To address privacy concerns, Trezor has rolled out Anonymous Pickup in 18 European countries, letting buyers collect hardware wallets using only a nickname and email at pickup points. The company is also reducing its data retention window from 90 days to 45 days to limit exposure.
Despite these steps, more than half a million customer records have been exposed since August, and uncertainty remains about whether further fraudulent activity or physical threats will emerge from the Skladon breach.
Will these privacy efforts be enough to regain user trust, or is Trezor facing deeper reputational risks?
#Trezor #bitcoin #security #brevo
90

The recent K3 Capital exploit highlights a critical vulnerability in how block builders prioritize transactions. With over half of the stolen $3.4 million in the sBOLD vault hack flowing directly to MEV-boosted builders, it underscores how automation and gas bidding wars can facilitate malicious activity on-chain. This incident serves as a stark reminder that the current block construction process remains a double-edged sword for network integrity. Security in DeFi is truly paramount. $ETH #Ethereum #DeFi #Security
The recent K3 Capital exploit highlights a critical vulnerability in how block builders prioritize transactions. With over half of the stolen $3.4 million in the sBOLD vault hack flowing directly to MEV-boosted builders, it underscores how automation and gas bidding wars can facilitate malicious activity on-chain. This incident serves as a stark reminder that the current block construction process remains a double-edged sword for network integrity. Security in DeFi is truly paramount. $ETH #Ethereum #DeFi #Security
8

·
--
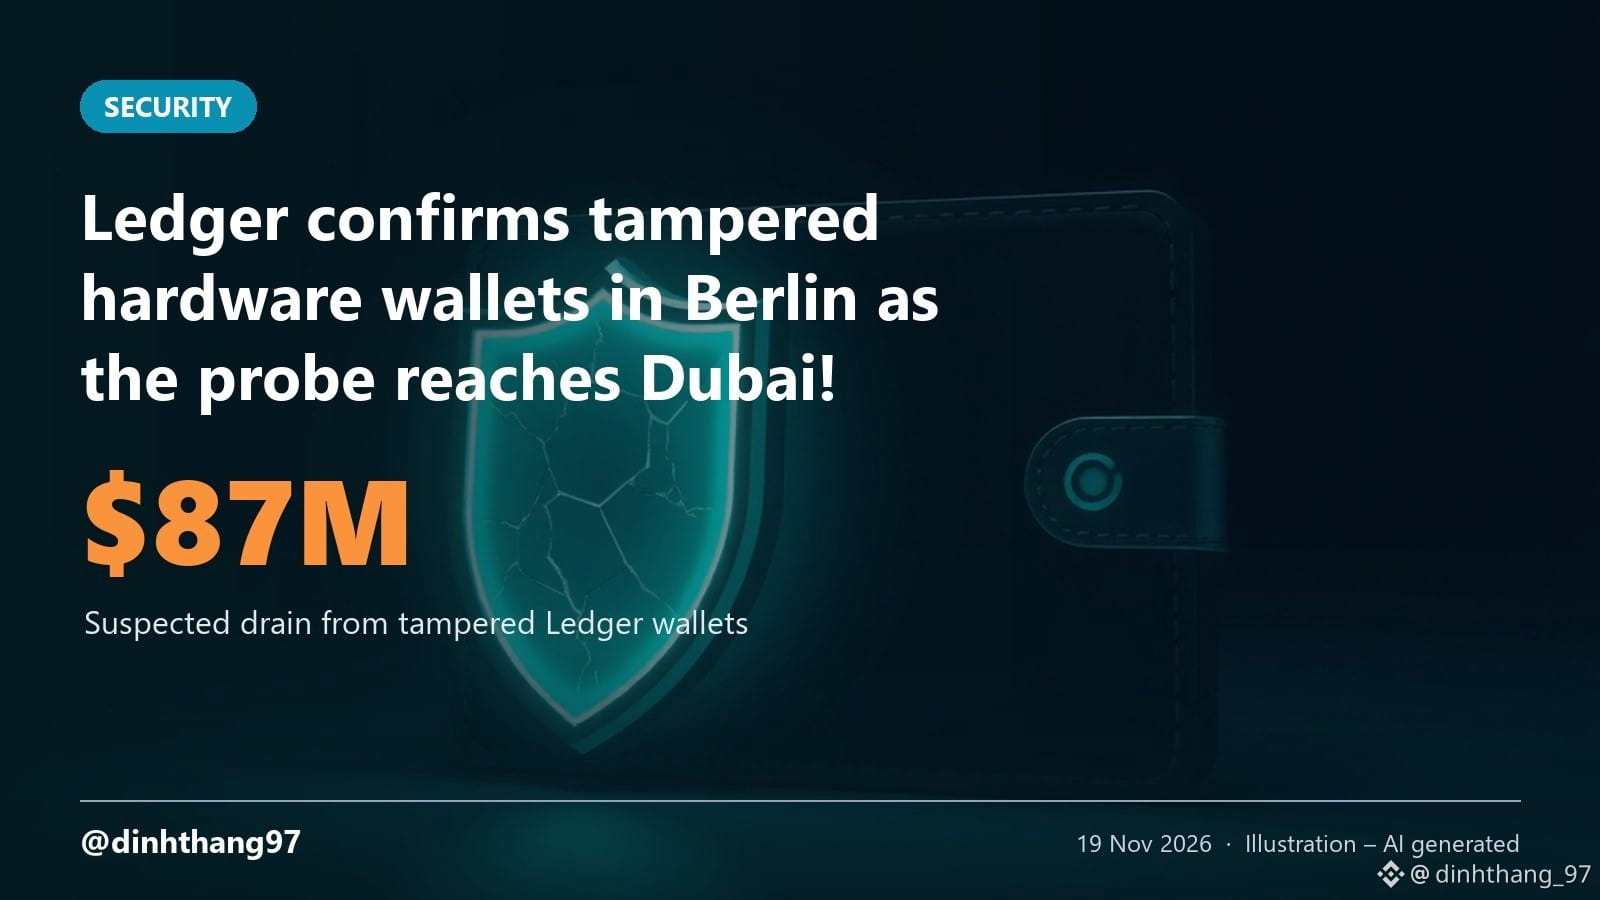
Ledger confirms tampered hardware wallets in Berlin as the probe reaches Dubai!
According to Decrypt, Cointelegraph and The Defiant, the modified devices are built to capture the recovery phrase during setup:
🔴 About $87M suspected drained from hundreds of victim wallets
🔸 Berlin: buyers since January 2026 should contact support
🔸 Dubai: two suspect units from a retail store
🔸 One user reported a $320,000 loss after a Berlin purchase
Here's what caught my attention: Ledger says its secure chip and OS are not flawed, and no confirmed case involves ledger.com purchases.
Of course, Ledger also expects more affected devices to surface.
Only buy hardware wallets direct from the maker and never share your recovery phrase.
Not financial advice, DYOR.
#Ledger #Security
Ledger confirms tampered hardware wallets in Berlin as the probe reaches Dubai!
According to Decrypt, Cointelegraph and The Defiant, the modified devices are built to capture the recovery phrase during setup:
🔴 About $87M suspected drained from hundreds of victim wallets
🔸 Berlin: buyers since January 2026 should contact support
🔸 Dubai: two suspect units from a retail store
🔸 One user reported a $320,000 loss after a Berlin purchase
Here's what caught my attention: Ledger says its secure chip and OS are not flawed, and no confirmed case involves ledger.com purchases.
Of course, Ledger also expects more affected devices to surface.
Only buy hardware wallets direct from the maker and never share your recovery phrase.
Not financial advice, DYOR.
#Ledger #Security
According to Decrypt, Cointelegraph and The Defiant, the modified devices are built to capture the recovery phrase during setup:
🔴 About $87M suspected drained from hundreds of victim wallets
🔸 Berlin: buyers since January 2026 should contact support
🔸 Dubai: two suspect units from a retail store
🔸 One user reported a $320,000 loss after a Berlin purchase
Here's what caught my attention: Ledger says its secure chip and OS are not flawed, and no confirmed case involves ledger.com purchases.
Of course, Ledger also expects more affected devices to surface.
Only buy hardware wallets direct from the maker and never share your recovery phrase.
Not financial advice, DYOR.
#Ledger #Security
132
With online fraud losses hitting staggering highs in 2025, regulatory pressure is shifting toward aggressive intervention. The new administration's dedicated center targeting scam payments could reshape compliance across the board. While this aims to protect everyday users, it also means traditional rails and digital assets alike will face heightened scrutiny. Expect stricter oversight on cross-border transactions as authorities try to cut off illicit flows at the source. #CryptoRegulation #Security #FraudPrevention
With online fraud losses hitting staggering highs in 2025, regulatory pressure is shifting toward aggressive intervention. The new administration's dedicated center targeting scam payments could reshape compliance across the board. While this aims to protect everyday users, it also means traditional rails and digital assets alike will face heightened scrutiny. Expect stricter oversight on cross-border transactions as authorities try to cut off illicit flows at the source. #CryptoRegulation #Security #FraudPrevention

·
--
🔐 Ledger warns Berlin buyers as its device-tampering probe widens
Ledger told customers who bought hardware wallets in Berlin since January 2026 to contact support after it found several suspicious devices in the city. It also acknowledged tampered devices in Dubai, where two customers recently reported losing a combined $604,000 in crypto. Ledger says all confirmed cases share physical modifications built to capture recovery phrases during setup, tied to the same distribution-channel campaign it began probing in Southeast Asia in October. The company found no flaw in its secure chip or OS and no confirmed cases from devices bought directly on its website.
⭐ Supply-chain attacks can bypass even strong hardware security, making official purchase channels more important than ever.
#Ledger #Security #HardwareWallet #CryptoNews
🔐 Ledger warns Berlin buyers as its device-tampering probe widens
Ledger told customers who bought hardware wallets in Berlin since January 2026 to contact support after it found several suspicious devices in the city. It also acknowledged tampered devices in Dubai, where two customers recently reported losing a combined $604,000 in crypto. Ledger says all confirmed cases share physical modifications built to capture recovery phrases during setup, tied to the same distribution-channel campaign it began probing in Southeast Asia in October. The company found no flaw in its secure chip or OS and no confirmed cases from devices bought directly on its website.
⭐ Supply-chain attacks can bypass even strong hardware security, making official purchase channels more important than ever.
#Ledger #Security #HardwareWallet #CryptoNews
Ledger told customers who bought hardware wallets in Berlin since January 2026 to contact support after it found several suspicious devices in the city. It also acknowledged tampered devices in Dubai, where two customers recently reported losing a combined $604,000 in crypto. Ledger says all confirmed cases share physical modifications built to capture recovery phrases during setup, tied to the same distribution-channel campaign it began probing in Southeast Asia in October. The company found no flaw in its secure chip or OS and no confirmed cases from devices bought directly on its website.
⭐ Supply-chain attacks can bypass even strong hardware security, making official purchase channels more important than ever.
#Ledger #Security #HardwareWallet #CryptoNews
836
·
--
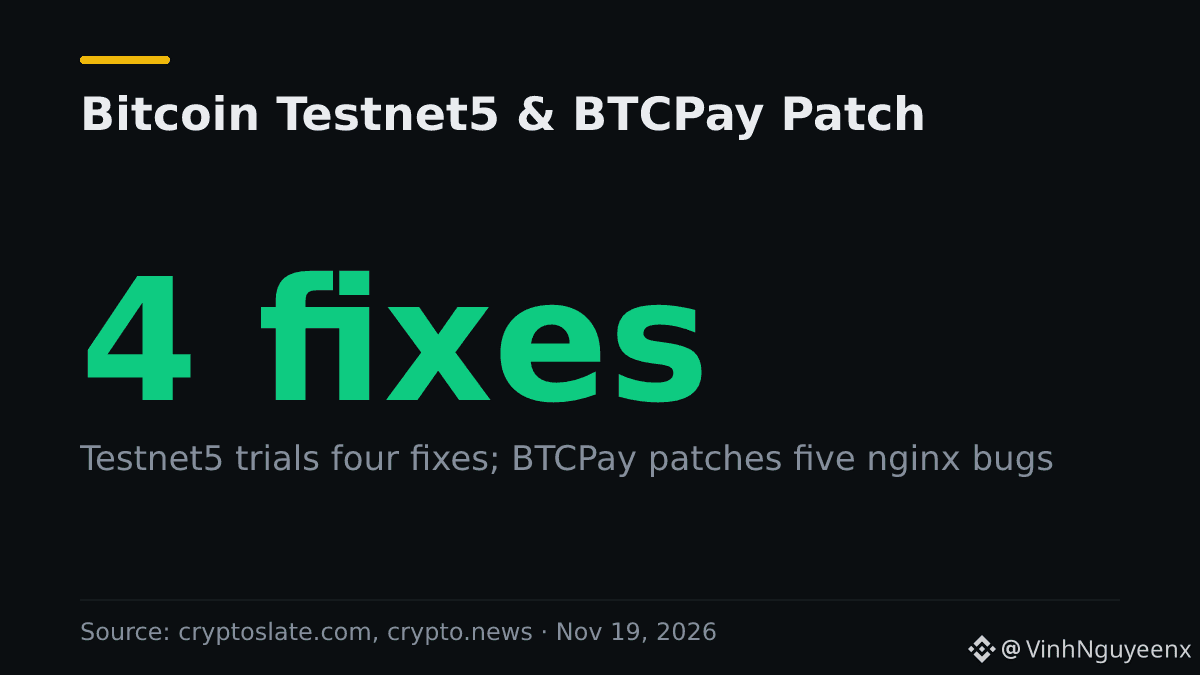
Bitcoin's latest upgrades let miners test four fixes while BTCPay patches five nginx bugs.
• Bitcoin launches Testnet5, offering miners a live trial of four proposed protocol fixes (cryptoslate.com)
• BTCPay Server releases emergency update fixing five critical nginx vulnerabilities (crypto.news)
These moves underscore the ecosystem’s push to harden core infrastructure before major network changes.
Which upgrade will shape the network most?
A) Testnet5 protocol fixes
B) BTCPay security patch
$BTC #Testnet5 #BTCPay #Security 🚀🔧
⚠️ Not financial advice. DYOR.
Bitcoin's latest upgrades let miners test four fixes while BTCPay patches five nginx bugs.
• Bitcoin launches Testnet5, offering miners a live trial of four proposed protocol fixes (cryptoslate.com)
• BTCPay Server releases emergency update fixing five critical nginx vulnerabilities (crypto.news)
These moves underscore the ecosystem’s push to harden core infrastructure before major network changes.
Which upgrade will shape the network most?
A) Testnet5 protocol fixes
B) BTCPay security patch
$BTC #Testnet5 #BTCPay #Security 🚀🔧
⚠️ Not financial advice. DYOR.
• Bitcoin launches Testnet5, offering miners a live trial of four proposed protocol fixes (cryptoslate.com)
• BTCPay Server releases emergency update fixing five critical nginx vulnerabilities (crypto.news)
These moves underscore the ecosystem’s push to harden core infrastructure before major network changes.
Which upgrade will shape the network most?
A) Testnet5 protocol fixes
B) BTCPay security patch
$BTC #Testnet5 #BTCPay #Security 🚀🔧
⚠️ Not financial advice. DYOR.
75

🚨 $ETH EXPLOIT UNVEILS $1M BRIDGE BREACH! 🦈
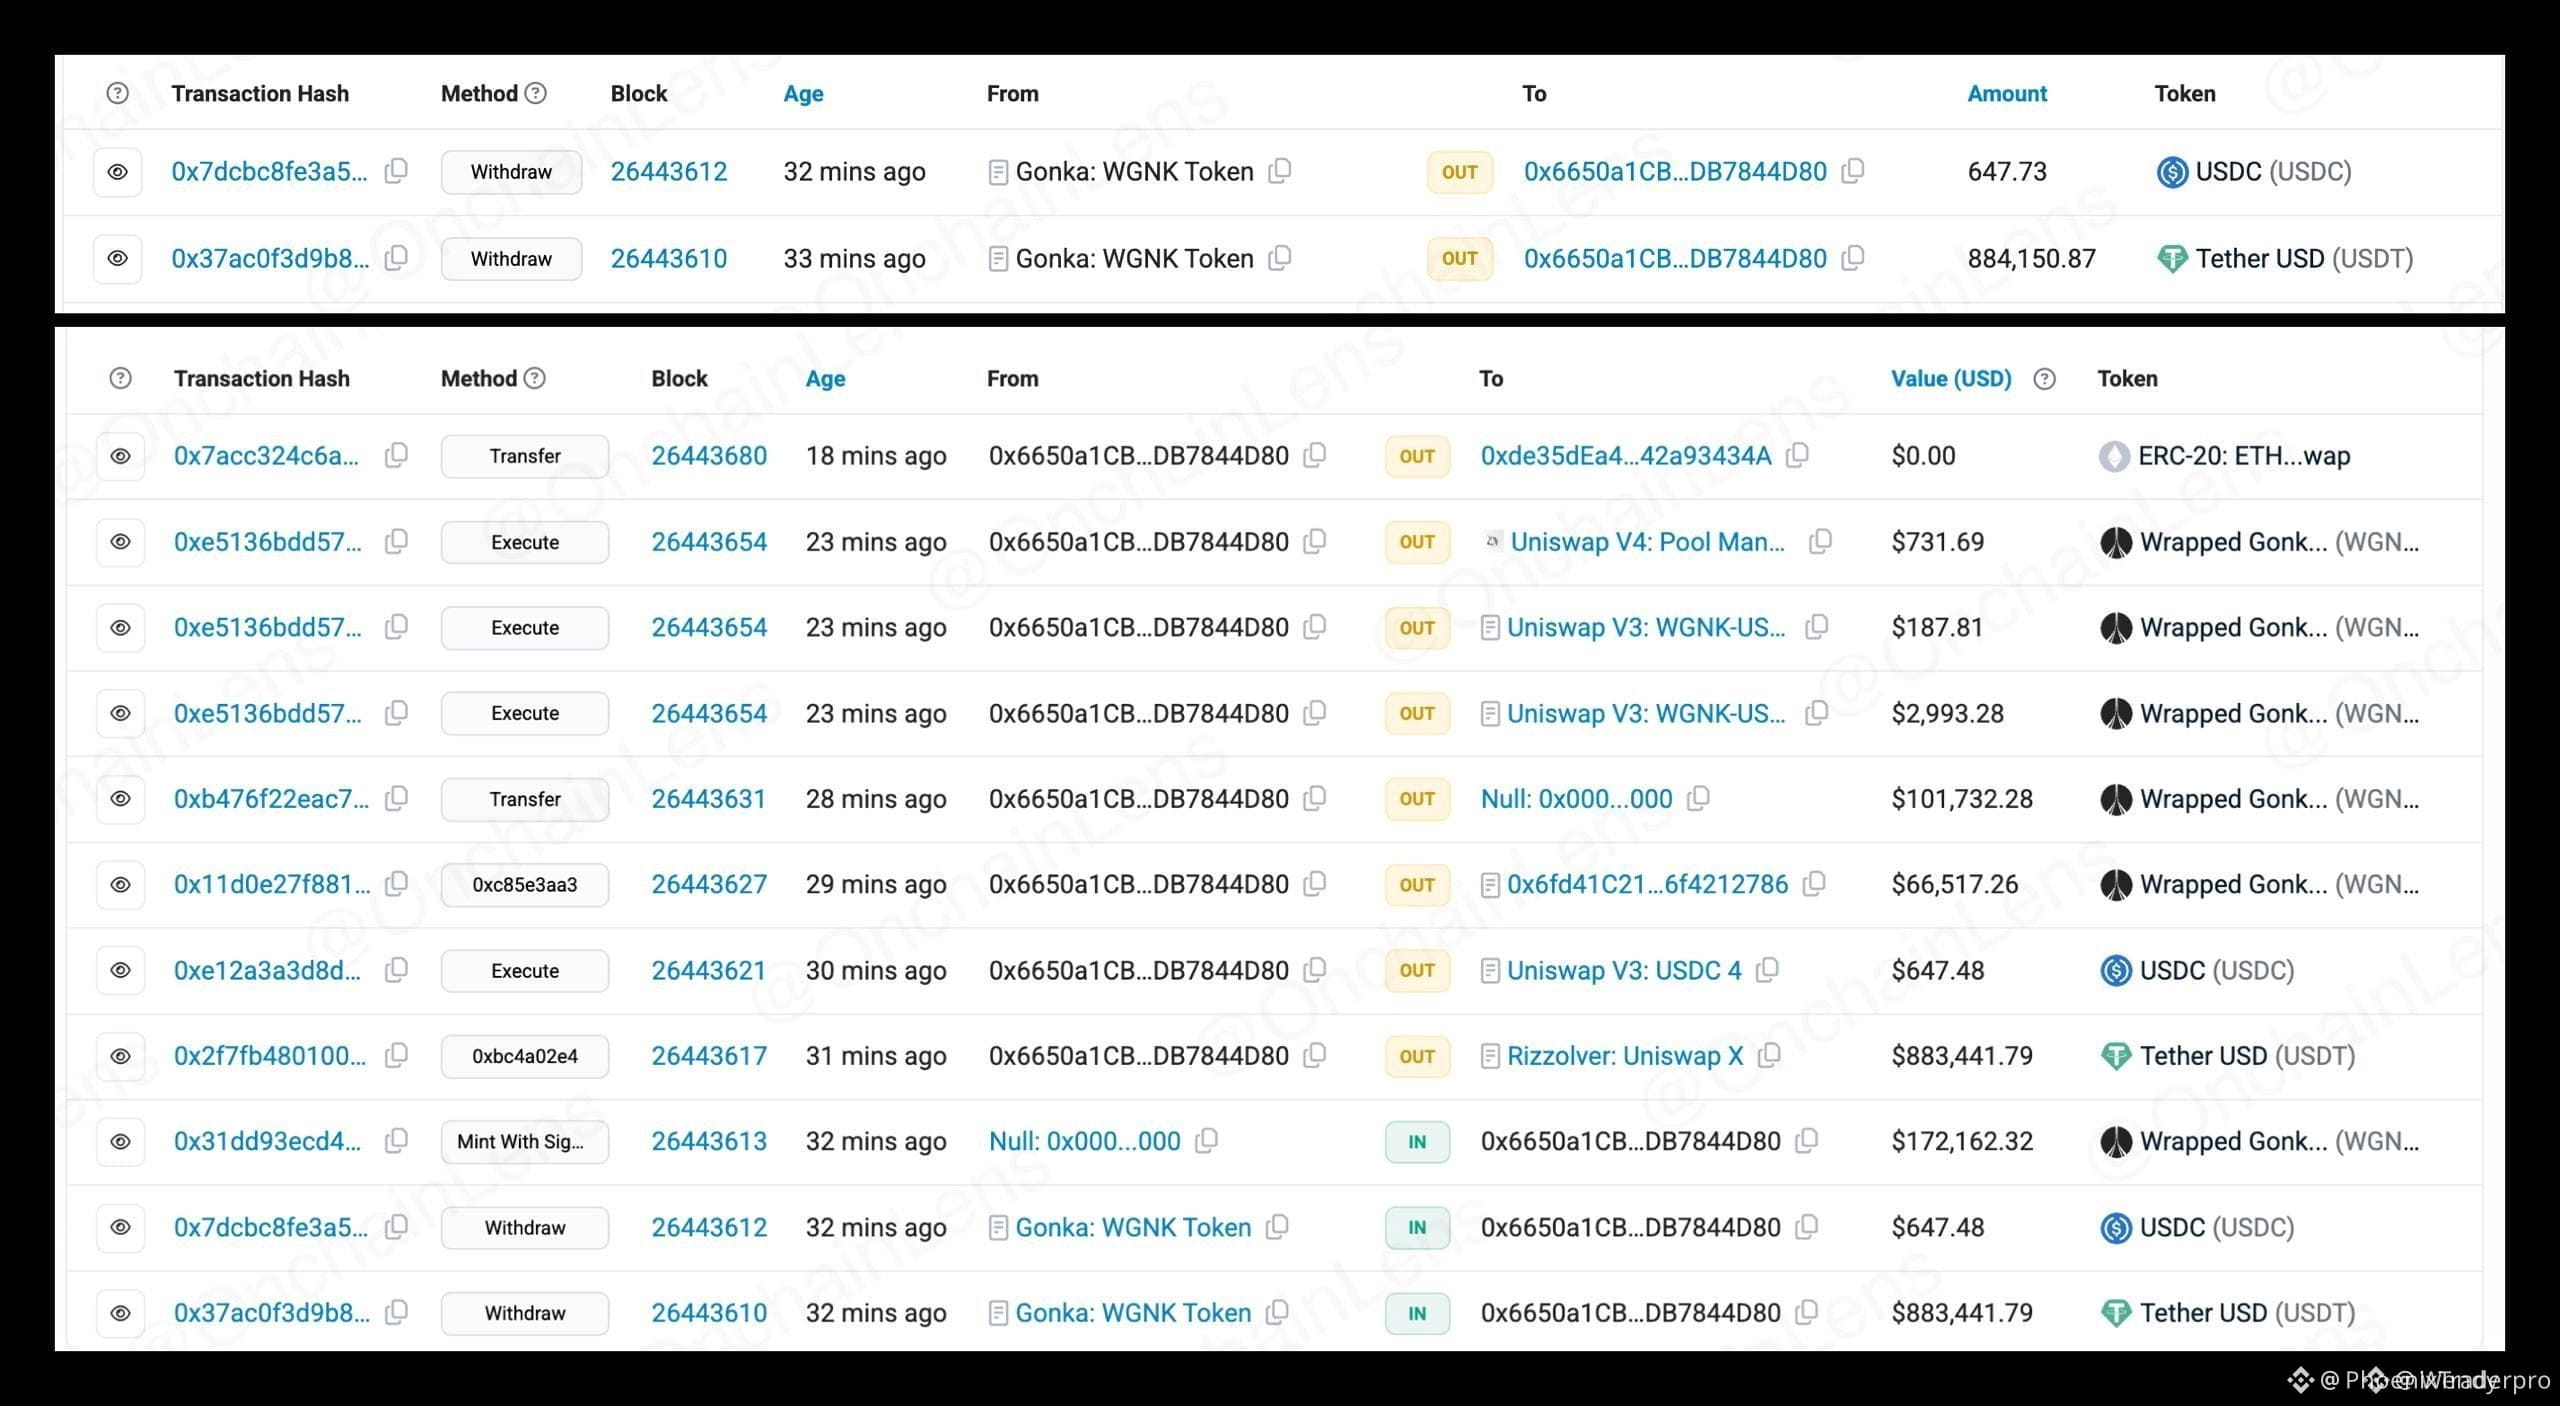
On‑chain forensics show a compromised bridge BLS group key at Gonka AI, letting an attacker siphon ~ $884.8K USDT/USDC and mint $172K unbacked WGNK. 📊
The flow hit Uniswap and bounced across multiple wallets, a classic liquidity sweep that lets whales clean the floor before the dust settles. 🦈⚡
While the breach isn’t independently verified yet, the sheer volume flags a red alert for any $ETH ‑linked exposure. 💬 What defensive moves are you taking to shield your positions?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Security #Exploit #Crypto
🚀 ⚡
🚨 $ETH EXPLOIT UNVEILS $1M BRIDGE BREACH! 🦈
On‑chain forensics show a compromised bridge BLS group key at Gonka AI, letting an attacker siphon ~ $884.8K USDT/USDC and mint $172K unbacked WGNK. 📊
The flow hit Uniswap and bounced across multiple wallets, a classic liquidity sweep that lets whales clean the floor before the dust settles. 🦈⚡
While the breach isn’t independently verified yet, the sheer volume flags a red alert for any $ETH ‑linked exposure. 💬 What defensive moves are you taking to shield your positions?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Security #Exploit #Crypto
🚀 ⚡
On‑chain forensics show a compromised bridge BLS group key at Gonka AI, letting an attacker siphon ~ $884.8K USDT/USDC and mint $172K unbacked WGNK. 📊
The flow hit Uniswap and bounced across multiple wallets, a classic liquidity sweep that lets whales clean the floor before the dust settles. 🦈⚡
While the breach isn’t independently verified yet, the sheer volume flags a red alert for any $ETH ‑linked exposure. 💬 What defensive moves are you taking to shield your positions?
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #ETH #Security #Exploit #Crypto
🚀 ⚡
9
Government tests reveal that major AI models like ChatGPT and Claude can be manipulated to assist in planning attacks. While safety guardrails are tightening, this highlights a critical vulnerability in unregulated digital infrastructure. As AI security becomes a global priority, the intersection of advanced tech and national defense will heavily impact regulatory policies moving forward. #AI #Security #TechNews
Government tests reveal that major AI models like ChatGPT and Claude can be manipulated to assist in planning attacks. While safety guardrails are tightening, this highlights a critical vulnerability in unregulated digital infrastructure. As AI security becomes a global priority, the intersection of advanced tech and national defense will heavily impact regulatory policies moving forward. #AI #Security #TechNews
63
·
--
🚨 Ledger warns of tampered wallets in Berlin – is your $BTC safe?
A recent report reveals that some Ledger hardware wallets shipped to Berlin show signs of a tampering device that could expose private keys. Users holding $BTC on Ledger should stay alert.
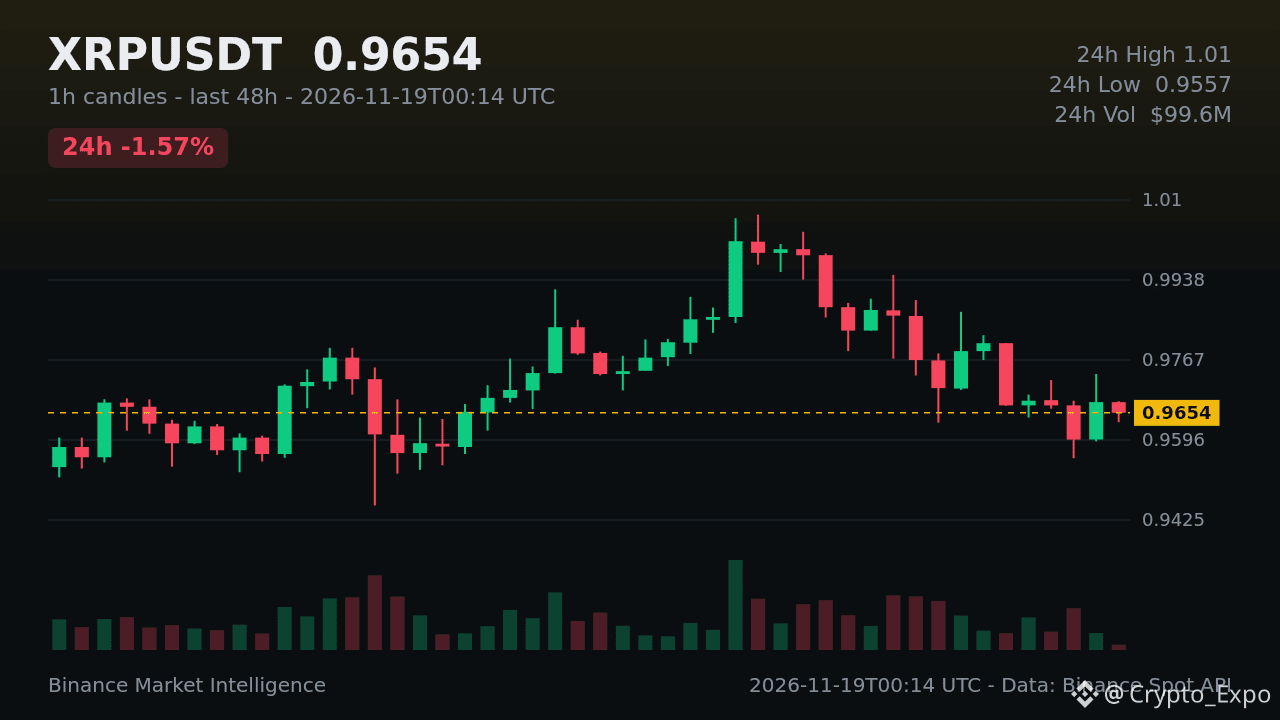
• 📉 $BTC down ~3% to $62,834 (price $62,833.87, change -3.122%)
• 📊 $ETH down ~2.7% to $1,772 (price $1,772.44, change -2.692%)
• 😨 Fear & Greed Index at 10 – "Extreme Fear"
How are you protecting your crypto after this news? Share your strategies below 👇
$BTC #Crypto #Security #Bitcoin
🚨 Ledger warns of tampered wallets in Berlin – is your $BTC safe?
A recent report reveals that some Ledger hardware wallets shipped to Berlin show signs of a tampering device that could expose private keys. Users holding $BTC on Ledger should stay alert.
• 📉 $BTC down ~3% to $62,834 (price $62,833.87, change -3.122%)
• 📊 $ETH down ~2.7% to $1,772 (price $1,772.44, change -2.692%)
• 😨 Fear & Greed Index at 10 – "Extreme Fear"
How are you protecting your crypto after this news? Share your strategies below 👇
$BTC #Crypto #Security #Bitcoin
A recent report reveals that some Ledger hardware wallets shipped to Berlin show signs of a tampering device that could expose private keys. Users holding $BTC on Ledger should stay alert.
• 📉 $BTC down ~3% to $62,834 (price $62,833.87, change -3.122%)
• 📊 $ETH down ~2.7% to $1,772 (price $1,772.44, change -2.692%)
• 😨 Fear & Greed Index at 10 – "Extreme Fear"
How are you protecting your crypto after this news? Share your strategies below 👇
$BTC #Crypto #Security #Bitcoin
90
·
--
Ledger flagged two suspected compromised wallets in Dubai while confirming tampering in Berlin.
• Ledger confirmed hardware implants in Berlin‑purchased wallets (decrypt.co)
• The investigation now includes two suspected tampered units in Dubai (cointelegraph.com)
• Affected users are urged to contact support and halt transactions (decrypt.co)
The breach underscores a physical attack vector on crypto custody, urging stricter supply‑chain audits.
What’s your next move?
A) Update firmware immediately
B) Switch to a different hardware wallet
C) Keep using but monitor support
$BTC #Ledger #HardwareWallet #Security 🔐
⚠️ Not financial advice. DYOR.
Ledger flagged two suspected compromised wallets in Dubai while confirming tampering in Berlin.
• Ledger confirmed hardware implants in Berlin‑purchased wallets (decrypt.co)
• The investigation now includes two suspected tampered units in Dubai (cointelegraph.com)
• Affected users are urged to contact support and halt transactions (decrypt.co)
The breach underscores a physical attack vector on crypto custody, urging stricter supply‑chain audits.
What’s your next move?
A) Update firmware immediately
B) Switch to a different hardware wallet
C) Keep using but monitor support
$BTC #Ledger #HardwareWallet #Security 🔐
⚠️ Not financial advice. DYOR.
• Ledger confirmed hardware implants in Berlin‑purchased wallets (decrypt.co)
• The investigation now includes two suspected tampered units in Dubai (cointelegraph.com)
• Affected users are urged to contact support and halt transactions (decrypt.co)
The breach underscores a physical attack vector on crypto custody, urging stricter supply‑chain audits.
What’s your next move?
A) Update firmware immediately
B) Switch to a different hardware wallet
C) Keep using but monitor support
$BTC #Ledger #HardwareWallet #Security 🔐
⚠️ Not financial advice. DYOR.
30
Ledger Warns Berlin Customers Amid Expanding Hardware Wallet Tampering Probe
Hardware wallet manufacturer Ledger has issued an urgent advisory to customers who purchased devices in Berlin since January 2026.
The company is urging affected buyers to contact its support team immediately.
This warning comes as Ledger expands an ongoing investigation into suspected hardware implants.
The probe currently focuses on potential physical tampering incidents across both Germany and Dubai.
WHY IT MATTERS: Physical supply-chain attacks on hardware wallets pose a serious threat to self-custody security for crypto users holding assets like $BTC and $ETH.
Ensuring the integrity of cold storage devices is critical for maintaining trust in decentralized asset management.
MARKET IMPACT: Bearish, as security concerns surrounding major hardware wallet providers can undermine investor confidence in self-custody solutions.
How do you verify the authenticity of your hardware wallet before transferring funds?
#Ledger #Security #Crypto
Ledger Warns Berlin Customers Amid Expanding Hardware Wallet Tampering Probe
Hardware wallet manufacturer Ledger has issued an urgent advisory to customers who purchased devices in Berlin since January 2026.
The company is urging affected buyers to contact its support team immediately.
This warning comes as Ledger expands an ongoing investigation into suspected hardware implants.
The probe currently focuses on potential physical tampering incidents across both Germany and Dubai.
WHY IT MATTERS: Physical supply-chain attacks on hardware wallets pose a serious threat to self-custody security for crypto users holding assets like $BTC and $ETH .
Ensuring the integrity of cold storage devices is critical for maintaining trust in decentralized asset management.
MARKET IMPACT: Bearish, as security concerns surrounding major hardware wallet providers can undermine investor confidence in self-custody solutions.
How do you verify the authenticity of your hardware wallet before transferring funds?
#Ledger #Security #Crypto
Hardware wallet manufacturer Ledger has issued an urgent advisory to customers who purchased devices in Berlin since January 2026.
The company is urging affected buyers to contact its support team immediately.
This warning comes as Ledger expands an ongoing investigation into suspected hardware implants.
The probe currently focuses on potential physical tampering incidents across both Germany and Dubai.
WHY IT MATTERS: Physical supply-chain attacks on hardware wallets pose a serious threat to self-custody security for crypto users holding assets like $BTC and $ETH .
Ensuring the integrity of cold storage devices is critical for maintaining trust in decentralized asset management.
MARKET IMPACT: Bearish, as security concerns surrounding major hardware wallet providers can undermine investor confidence in self-custody solutions.
How do you verify the authenticity of your hardware wallet before transferring funds?
#Ledger #Security #Crypto
9
Ledger confirms tampered wallets in Berlin, weighs two Dubai unitsLedger says tampered devices were confirmed in Berlin, and it is now examining two suspected units in Dubai — the implant probe has moved past Southeast Asia. The coin at the center of it is $BTC.
First, the confirmed fact: Ledger says the Berlin devices were tampered with, which turns a probe that began in Southeast Asia into a European problem.
Second, the open fact: the two Dubai units are only suspected, not confirmed, so the full list of affected devices is still unknown.
Third, the pattern: crypto has been here before with supply-chain trust — the device you buy to protect your keys becomes the thing you have to verify.
So what: if you hold $BTC in self-custody, this could mean checking your device's provenance and firmware through official channels rather than trusting a sealed box.
Which group does this hit hardest — long-term holders, active traders, newcomers, or miners? 👇
#Bitcoin #Security
For information only, not financial advice.
Tap $BTC to trade
$BTC
غيرك سبقك وتابع. ادخل بروفايلي وخلك مع اللي يقرأ قبل ما ينتشر الخبر.
Ledger confirms tampered wallets in Berlin, weighs two Dubai units
Ledger says tampered devices were confirmed in Berlin, and it is now examining two suspected units in Dubai — the implant probe has moved past Southeast Asia. The coin at the center of it is $BTC .
First, the confirmed fact: Ledger says the Berlin devices were tampered with, which turns a probe that began in Southeast Asia into a European problem.
Second, the open fact: the two Dubai units are only suspected, not confirmed, so the full list of affected devices is still unknown.
Third, the pattern: crypto has been here before with supply-chain trust — the device you buy to protect your keys becomes the thing you have to verify.
So what: if you hold $BTC in self-custody, this could mean checking your device's provenance and firmware through official channels rather than trusting a sealed box.
Which group does this hit hardest — long-term holders, active traders, newcomers, or miners? 👇
#Bitcoin #Security
For information only, not financial advice.
Tap $BTC to trade
$BTC
غيرك سبقك وتابع. ادخل بروفايلي وخلك مع اللي يقرأ قبل ما ينتشر الخبر.
First, the confirmed fact: Ledger says the Berlin devices were tampered with, which turns a probe that began in Southeast Asia into a European problem.
Second, the open fact: the two Dubai units are only suspected, not confirmed, so the full list of affected devices is still unknown.
Third, the pattern: crypto has been here before with supply-chain trust — the device you buy to protect your keys becomes the thing you have to verify.
So what: if you hold $BTC in self-custody, this could mean checking your device's provenance and firmware through official channels rather than trusting a sealed box.
Which group does this hit hardest — long-term holders, active traders, newcomers, or miners? 👇
#Bitcoin #Security
For information only, not financial advice.
Tap $BTC to trade
$BTC
غيرك سبقك وتابع. ادخل بروفايلي وخلك مع اللي يقرأ قبل ما ينتشر الخبر.
54
·
--
Article
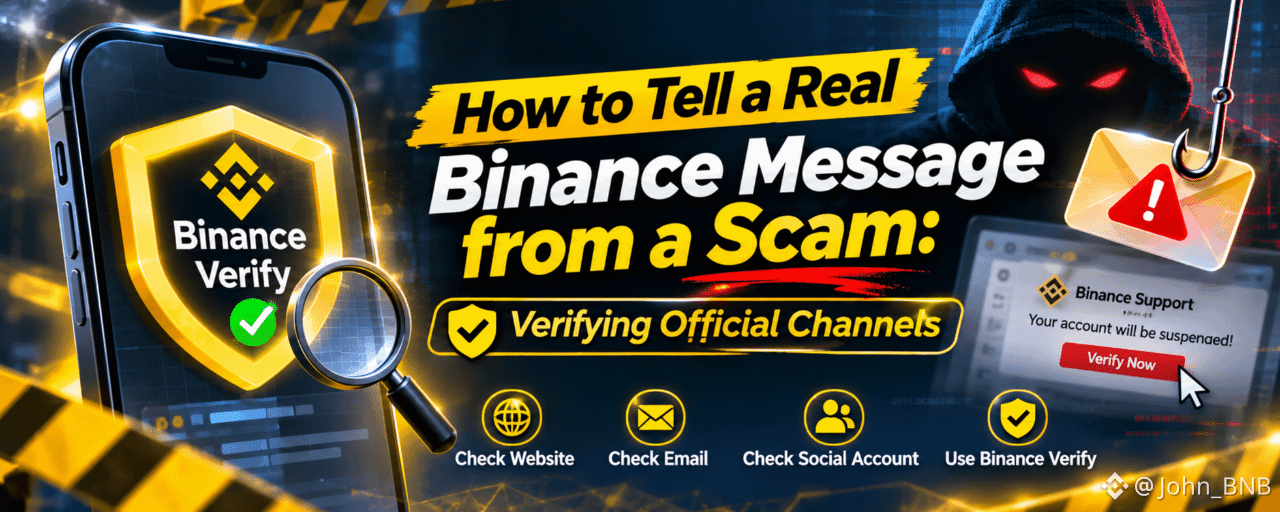
How to Tell a Real Binance Message from a Scam: Verifying Official ChannelsBinance Security Guide | Account Protection | Anti-Phishing
In the crypto world, not every message that looks official comes from the real source.
Scammers frequently impersonate trusted crypto platforms, especially after major security incidents or breaking news. They use fake emails, cloned websites, fraudulent social media accounts, and impersonated customer support agents to trick users into revealing sensitive information or transferring funds.
A message may carry the Binance logo, use professional language, and even appear to come from a familiar account. But appearances are not proof of authenticity.
The good news is that users have a way to check.
This guide explains how to verify whether a website, email, social media account, or other communication genuinely belongs to Binance, how to recognize common scam tactics, and what to do when something feels suspicious.
1. Use Binance Verify Before Trusting a Message
One of the simplest ways to check whether a communication is legitimate is Binance Verify.
Binance Verify is an official verification tool that allows users to check whether a website address, email address, phone number, or social media account is associated with Binance's official channels.
Instead of trusting a message because it looks professional, independently verify its source.
How to use it:
Visit [Binance Verify](https://www.binance.com/en/official-verification)Copy the website URL, email address, phone number, or social media account you want to check.Enter the information into the verification tool.Review the result to determine whether the source is officially recognized.If the source cannot be verified, do not interact with it until you confirm through Binance's official channels.
Important: Always access Binance Verify by typing the official Binance website address yourself or using a trusted bookmark. Avoid clicking verification links sent by suspicious accounts.
2. Check Every Channel, Not Just the Logo
Scammers can imitate almost anything. Knowing where legitimate Binance communications originate is an important part of account security.
Here are the main channels to check:
A. Websites and URLs
Always check the domain name before entering login credentials.Watch for misspellings, extra characters, unusual extensions, and misleading subdomains.Avoid shortened URLs from unknown sources.Access Binance by typing its official address directly: cf-workers-proxy-cyt.pages.dev
B. Social media accounts
Check the account handle and verification status.Be careful with accounts using similar usernames, copied profile pictures, and Binance branding.Verify the social media handle through Binance Verify.Never trust someone simply because they claim to be a Binance employee or Angel.
C. Emails
Inspect the complete sender address, not just the display name.Check your personal Anti-Phishing Code.Avoid opening unexpected attachments or clicking suspicious links.Remember that email sender addresses can be spoofed.
D. Customer Support
Start conversations through Binance's official app or website.Do not trust unsolicited messages from people claiming to be support agents.Never install remote-access software or share your screen because someone claiming to be support asks you to.
3. Recognize the Warning Signs of a Scam
Most impersonation scams follow a familiar pattern: create fear, establish false trust, and push the victim into making a quick decision.
Watch for these common warning signs:
Warning sign
What scammers might say
Urgency
"Your account will be suspended in 30 minutes!"
Security threats
"We detected suspicious activity. Verify immediately."
Fake rewards
"Claim your exclusive Binance bonus here."
Account recovery
"Send your verification code to restore access."
Fake support
"I am your assigned Binance security officer."
Fund transfers
"Move your assets to this secure wallet."
Suspicious links
"Click here to unlock your account."
One particularly important lesson:
Urgency combined with a request for credentials is one of the clearest signs of a scam.
Legitimate security notifications may inform you about account activity, but you should independently open Binance and investigate rather than following instructions from an unexpected message.
4. Understand the Power of Your Anti-Phishing Code
Binance provides an additional security feature called the Anti-Phishing Code.
It allows users to create a unique personal code that appears in genuine Binance emails.
When enabled, you can use this code to distinguish legitimate Binance emails from many phishing attempts.
How to enable it:
Log in through the official Binance app or website.Navigate to your account's Security settings.Find Anti-Phishing Code.Create a unique code that is difficult for others to guess.Save your settings.
Whenever you receive an email claiming to come from Binance, check whether your personal code is displayed.
If it is missing or incorrect, treat the email as suspicious and verify it independently.
Remember: This feature helps authenticate emails, not every SMS, phone call, or social media message. It should be used alongside Binance Verify.
5. What Binance Will Never Ask You to Do
This is perhaps the most important section for every crypto user.
Scammers often pretend to help users protect their accounts, but their real objective is to gain access to their funds.
Keep these rules in mind:
Never share your account password.Never disclose your 2FA or verification codes.Never share your wallet seed phrase or private keys.Never transfer cryptocurrency to a stranger claiming it is necessary to secure your account.Never scan an unknown QR code to log in or authorize access.Never install remote-access applications at the request of an unverified support agent.Never provide screenshots or sensitive account information to strangers.
Your credentials belong to you. No legitimate support conversation should require you to hand over your password, 2FA codes, or private keys.
6. What Should You Do If You Receive a Suspicious Message?
If you receive a suspicious message claiming to be from Binance, don't panic. Follow these steps:
Stop: Don't click links, download files, reply, or share information.Verify: Check the sender, URL, email, or social account through Binance Verify.Report: Report suspicious impersonation through official Binance Support.Secure: If you have interacted with a suspicious website or disclosed information, change your password through the official platform and review your security settings.Act immediately: If you suspect unauthorized access, contact Binance Support through the official app or website and follow its instructions to secure or disable your account.
Also review your account activity, login history, and withdrawal records for anything you don't recognize.
The sooner you respond, the better your chances of limiting potential damage.
7. Security Is a Shared Responsibility
Binance provides security tools and official verification channels, but users also play an important role in protecting their assets.
A strong password, 2FA, Anti-Phishing Code, and regular security checks can help reduce risks. However, the most valuable habit is learning to question unexpected communications before taking action.
Scammers don't necessarily need to break through a platform's security systems if they can convince users to give away their credentials.
The next time someone sends you an urgent message claiming to be from Binance, remember three simple words:
STOP. VERIFY. PROTECT.
Don't trust appearances. Verify the source before you trust the message.
Frequently Asked Questions
1. How can I verify whether a Binance employee is real?
Use Binance Verify to check their email address, phone number, or social media handle. If you cannot verify their identity, do not proceed with their requests.
2. Does Binance Verify check Telegram accounts?
Yes. You can enter Telegram usernames and other supported social media handles to check whether they are officially recognized.
3. What if Binance Verify says an account is verified, but the message still looks suspicious?
Remain cautious. Email and SMS sender information can be spoofed. Contact Binance Support independently if you have doubts.
4. Does Binance Support ever ask for my password or 2FA code?
You should never disclose your password, 2FA codes, seed phrase, or private keys to anyone claiming to be support.
5. Where can I report a fake Binance account?
Use the official Binance Support portal to report suspicious accounts, messages, and phishing websites.
Official Security Resources
[Binance Verify – Official Verification Tool](https://www.binance.com/en/official-verification)[How to Identify and Avoid Binance Imposters](https://www.binance.com/blog/security/299010416215875222?ref=CPA_0037NAK6ST)[How to Identify Phishing Emails](https://www.binance.com/en/support/faq/detail/360002070252?utm_source=new_share&ref=CPA_0037NAK6ST)[How to Prevent Phishing Attacks](https://www.binance.com/en/support/faq/detail/360020819031?utm_source=new_share&ref=CPA_0037NAK6ST)
#Binance #security #SAFE #safu
How to Tell a Real Binance Message from a Scam: Verifying Official Channels
Binance Security Guide | Account Protection | Anti-Phishing
In the crypto world, not every message that looks official comes from the real source.
Scammers frequently impersonate trusted crypto platforms, especially after major security incidents or breaking news. They use fake emails, cloned websites, fraudulent social media accounts, and impersonated customer support agents to trick users into revealing sensitive information or transferring funds.
A message may carry the Binance logo, use professional language, and even appear to come from a familiar account. But appearances are not proof of authenticity.
The good news is that users have a way to check.
This guide explains how to verify whether a website, email, social media account, or other communication genuinely belongs to Binance, how to recognize common scam tactics, and what to do when something feels suspicious.
1. Use Binance Verify Before Trusting a Message
One of the simplest ways to check whether a communication is legitimate is Binance Verify.
Binance Verify is an official verification tool that allows users to check whether a website address, email address, phone number, or social media account is associated with Binance's official channels.
Instead of trusting a message because it looks professional, independently verify its source.
How to use it:
Visit Binance VerifyCopy the website URL, email address, phone number, or social media account you want to check.Enter the information into the verification tool.Review the result to determine whether the source is officially recognized.If the source cannot be verified, do not interact with it until you confirm through Binance's official channels.
Important: Always access Binance Verify by typing the official Binance website address yourself or using a trusted bookmark. Avoid clicking verification links sent by suspicious accounts.
2. Check Every Channel, Not Just the Logo
Scammers can imitate almost anything. Knowing where legitimate Binance communications originate is an important part of account security.
Here are the main channels to check:
A. Websites and URLs
Always check the domain name before entering login credentials.Watch for misspellings, extra characters, unusual extensions, and misleading subdomains.Avoid shortened URLs from unknown sources.Access Binance by typing its official address directly: cf-workers-proxy-cyt.pages.dev
B. Social media accounts
Check the account handle and verification status.Be careful with accounts using similar usernames, copied profile pictures, and Binance branding.Verify the social media handle through Binance Verify.Never trust someone simply because they claim to be a Binance employee or Angel.
C. Emails
Inspect the complete sender address, not just the display name.Check your personal Anti-Phishing Code.Avoid opening unexpected attachments or clicking suspicious links.Remember that email sender addresses can be spoofed.
D. Customer Support
Start conversations through Binance's official app or website.Do not trust unsolicited messages from people claiming to be support agents.Never install remote-access software or share your screen because someone claiming to be support asks you to.
3. Recognize the Warning Signs of a Scam
Most impersonation scams follow a familiar pattern: create fear, establish false trust, and push the victim into making a quick decision.
Watch for these common warning signs:
Warning sign
What scammers might say
Urgency
"Your account will be suspended in 30 minutes!"
Security threats
"We detected suspicious activity. Verify immediately."
Fake rewards
"Claim your exclusive Binance bonus here."
Account recovery
"Send your verification code to restore access."
Fake support
"I am your assigned Binance security officer."
Fund transfers
"Move your assets to this secure wallet."
Suspicious links
"Click here to unlock your account."
One particularly important lesson:
Urgency combined with a request for credentials is one of the clearest signs of a scam.
Legitimate security notifications may inform you about account activity, but you should independently open Binance and investigate rather than following instructions from an unexpected message.
4. Understand the Power of Your Anti-Phishing Code
Binance provides an additional security feature called the Anti-Phishing Code.
It allows users to create a unique personal code that appears in genuine Binance emails.
When enabled, you can use this code to distinguish legitimate Binance emails from many phishing attempts.
How to enable it:
Log in through the official Binance app or website.Navigate to your account's Security settings.Find Anti-Phishing Code.Create a unique code that is difficult for others to guess.Save your settings.
Whenever you receive an email claiming to come from Binance, check whether your personal code is displayed.
If it is missing or incorrect, treat the email as suspicious and verify it independently.
Remember: This feature helps authenticate emails, not every SMS, phone call, or social media message. It should be used alongside Binance Verify.
5. What Binance Will Never Ask You to Do
This is perhaps the most important section for every crypto user.
Scammers often pretend to help users protect their accounts, but their real objective is to gain access to their funds.
Keep these rules in mind:
Never share your account password.Never disclose your 2FA or verification codes.Never share your wallet seed phrase or private keys.Never transfer cryptocurrency to a stranger claiming it is necessary to secure your account.Never scan an unknown QR code to log in or authorize access.Never install remote-access applications at the request of an unverified support agent.Never provide screenshots or sensitive account information to strangers.
Your credentials belong to you. No legitimate support conversation should require you to hand over your password, 2FA codes, or private keys.
6. What Should You Do If You Receive a Suspicious Message?
If you receive a suspicious message claiming to be from Binance, don't panic. Follow these steps:
Stop: Don't click links, download files, reply, or share information.Verify: Check the sender, URL, email, or social account through Binance Verify.Report: Report suspicious impersonation through official Binance Support.Secure: If you have interacted with a suspicious website or disclosed information, change your password through the official platform and review your security settings.Act immediately: If you suspect unauthorized access, contact Binance Support through the official app or website and follow its instructions to secure or disable your account.
Also review your account activity, login history, and withdrawal records for anything you don't recognize.
The sooner you respond, the better your chances of limiting potential damage.
7. Security Is a Shared Responsibility
Binance provides security tools and official verification channels, but users also play an important role in protecting their assets.
A strong password, 2FA, Anti-Phishing Code, and regular security checks can help reduce risks. However, the most valuable habit is learning to question unexpected communications before taking action.
Scammers don't necessarily need to break through a platform's security systems if they can convince users to give away their credentials.
The next time someone sends you an urgent message claiming to be from Binance, remember three simple words:
STOP. VERIFY. PROTECT.
Don't trust appearances. Verify the source before you trust the message.
Frequently Asked Questions
1. How can I verify whether a Binance employee is real?
Use Binance Verify to check their email address, phone number, or social media handle. If you cannot verify their identity, do not proceed with their requests.
2. Does Binance Verify check Telegram accounts?
Yes. You can enter Telegram usernames and other supported social media handles to check whether they are officially recognized.
3. What if Binance Verify says an account is verified, but the message still looks suspicious?
Remain cautious. Email and SMS sender information can be spoofed. Contact Binance Support independently if you have doubts.
4. Does Binance Support ever ask for my password or 2FA code?
You should never disclose your password, 2FA codes, seed phrase, or private keys to anyone claiming to be support.
5. Where can I report a fake Binance account?
Use the official Binance Support portal to report suspicious accounts, messages, and phishing websites.
Official Security Resources
Binance Verify – Official Verification ToolHow to Identify and Avoid Binance ImpostersHow to Identify Phishing EmailsHow to Prevent Phishing Attacks
#Binance #security #SAFE #safu
In the crypto world, not every message that looks official comes from the real source.
Scammers frequently impersonate trusted crypto platforms, especially after major security incidents or breaking news. They use fake emails, cloned websites, fraudulent social media accounts, and impersonated customer support agents to trick users into revealing sensitive information or transferring funds.
A message may carry the Binance logo, use professional language, and even appear to come from a familiar account. But appearances are not proof of authenticity.
The good news is that users have a way to check.
This guide explains how to verify whether a website, email, social media account, or other communication genuinely belongs to Binance, how to recognize common scam tactics, and what to do when something feels suspicious.
1. Use Binance Verify Before Trusting a Message
One of the simplest ways to check whether a communication is legitimate is Binance Verify.
Binance Verify is an official verification tool that allows users to check whether a website address, email address, phone number, or social media account is associated with Binance's official channels.
Instead of trusting a message because it looks professional, independently verify its source.
How to use it:
Visit Binance VerifyCopy the website URL, email address, phone number, or social media account you want to check.Enter the information into the verification tool.Review the result to determine whether the source is officially recognized.If the source cannot be verified, do not interact with it until you confirm through Binance's official channels.
Important: Always access Binance Verify by typing the official Binance website address yourself or using a trusted bookmark. Avoid clicking verification links sent by suspicious accounts.
2. Check Every Channel, Not Just the Logo
Scammers can imitate almost anything. Knowing where legitimate Binance communications originate is an important part of account security.
Here are the main channels to check:
A. Websites and URLs
Always check the domain name before entering login credentials.Watch for misspellings, extra characters, unusual extensions, and misleading subdomains.Avoid shortened URLs from unknown sources.Access Binance by typing its official address directly: cf-workers-proxy-cyt.pages.dev
B. Social media accounts
Check the account handle and verification status.Be careful with accounts using similar usernames, copied profile pictures, and Binance branding.Verify the social media handle through Binance Verify.Never trust someone simply because they claim to be a Binance employee or Angel.
C. Emails
Inspect the complete sender address, not just the display name.Check your personal Anti-Phishing Code.Avoid opening unexpected attachments or clicking suspicious links.Remember that email sender addresses can be spoofed.
D. Customer Support
Start conversations through Binance's official app or website.Do not trust unsolicited messages from people claiming to be support agents.Never install remote-access software or share your screen because someone claiming to be support asks you to.
3. Recognize the Warning Signs of a Scam
Most impersonation scams follow a familiar pattern: create fear, establish false trust, and push the victim into making a quick decision.
Watch for these common warning signs:
Warning sign
What scammers might say
Urgency
"Your account will be suspended in 30 minutes!"
Security threats
"We detected suspicious activity. Verify immediately."
Fake rewards
"Claim your exclusive Binance bonus here."
Account recovery
"Send your verification code to restore access."
Fake support
"I am your assigned Binance security officer."
Fund transfers
"Move your assets to this secure wallet."
Suspicious links
"Click here to unlock your account."
One particularly important lesson:
Urgency combined with a request for credentials is one of the clearest signs of a scam.
Legitimate security notifications may inform you about account activity, but you should independently open Binance and investigate rather than following instructions from an unexpected message.
4. Understand the Power of Your Anti-Phishing Code
Binance provides an additional security feature called the Anti-Phishing Code.
It allows users to create a unique personal code that appears in genuine Binance emails.
When enabled, you can use this code to distinguish legitimate Binance emails from many phishing attempts.
How to enable it:
Log in through the official Binance app or website.Navigate to your account's Security settings.Find Anti-Phishing Code.Create a unique code that is difficult for others to guess.Save your settings.
Whenever you receive an email claiming to come from Binance, check whether your personal code is displayed.
If it is missing or incorrect, treat the email as suspicious and verify it independently.
Remember: This feature helps authenticate emails, not every SMS, phone call, or social media message. It should be used alongside Binance Verify.
5. What Binance Will Never Ask You to Do
This is perhaps the most important section for every crypto user.
Scammers often pretend to help users protect their accounts, but their real objective is to gain access to their funds.
Keep these rules in mind:
Never share your account password.Never disclose your 2FA or verification codes.Never share your wallet seed phrase or private keys.Never transfer cryptocurrency to a stranger claiming it is necessary to secure your account.Never scan an unknown QR code to log in or authorize access.Never install remote-access applications at the request of an unverified support agent.Never provide screenshots or sensitive account information to strangers.
Your credentials belong to you. No legitimate support conversation should require you to hand over your password, 2FA codes, or private keys.
6. What Should You Do If You Receive a Suspicious Message?
If you receive a suspicious message claiming to be from Binance, don't panic. Follow these steps:
Stop: Don't click links, download files, reply, or share information.Verify: Check the sender, URL, email, or social account through Binance Verify.Report: Report suspicious impersonation through official Binance Support.Secure: If you have interacted with a suspicious website or disclosed information, change your password through the official platform and review your security settings.Act immediately: If you suspect unauthorized access, contact Binance Support through the official app or website and follow its instructions to secure or disable your account.
Also review your account activity, login history, and withdrawal records for anything you don't recognize.
The sooner you respond, the better your chances of limiting potential damage.
7. Security Is a Shared Responsibility
Binance provides security tools and official verification channels, but users also play an important role in protecting their assets.
A strong password, 2FA, Anti-Phishing Code, and regular security checks can help reduce risks. However, the most valuable habit is learning to question unexpected communications before taking action.
Scammers don't necessarily need to break through a platform's security systems if they can convince users to give away their credentials.
The next time someone sends you an urgent message claiming to be from Binance, remember three simple words:
STOP. VERIFY. PROTECT.
Don't trust appearances. Verify the source before you trust the message.
Frequently Asked Questions
1. How can I verify whether a Binance employee is real?
Use Binance Verify to check their email address, phone number, or social media handle. If you cannot verify their identity, do not proceed with their requests.
2. Does Binance Verify check Telegram accounts?
Yes. You can enter Telegram usernames and other supported social media handles to check whether they are officially recognized.
3. What if Binance Verify says an account is verified, but the message still looks suspicious?
Remain cautious. Email and SMS sender information can be spoofed. Contact Binance Support independently if you have doubts.
4. Does Binance Support ever ask for my password or 2FA code?
You should never disclose your password, 2FA codes, seed phrase, or private keys to anyone claiming to be support.
5. Where can I report a fake Binance account?
Use the official Binance Support portal to report suspicious accounts, messages, and phishing websites.
Official Security Resources
Binance Verify – Official Verification ToolHow to Identify and Avoid Binance ImpostersHow to Identify Phishing EmailsHow to Prevent Phishing Attacks
#Binance #security #SAFE #safu
Abu Fahadأ:
💛
2
3
503
·
--
A Hard Lesson: Recovering From a Severe Account Hack & Moving ForwardImportant Update:
My Binance account was recently hacked, and the hackers took everything—all my crypto balance and the rewards Binance had given me for my work. My account was completely emptied. Binance itself is aware that my account was hacked and that everything was stolen. Because the hackers locked me out and deleted everything, I couldn't reach out to anyone during that time. Thank you all for your support! ❤️
@Binance_Square_Official @Binance_Customer_Support @CZ
#Binance #crypto #security #BinanceSquare
A Hard Lesson: Recovering From a Severe Account Hack & Moving Forward
Important Update:
My Binance account was recently hacked, and the hackers took everything—all my crypto balance and the rewards Binance had given me for my work. My account was completely emptied. Binance itself is aware that my account was hacked and that everything was stolen. Because the hackers locked me out and deleted everything, I couldn't reach out to anyone during that time. Thank you all for your support! ❤️
@Binance Square Official @Binance Customer Support @CZ
#Binance #crypto #security #BinanceSquare
My Binance account was recently hacked, and the hackers took everything—all my crypto balance and the rewards Binance had given me for my work. My account was completely emptied. Binance itself is aware that my account was hacked and that everything was stolen. Because the hackers locked me out and deleted everything, I couldn't reach out to anyone during that time. Thank you all for your support! ❤️
@Binance Square Official @Binance Customer Support @CZ
#Binance #crypto #security #BinanceSquare
1
81
Anchorage exec: next 12 months a 'slaughterhouse' for crypto securityAn Anchorage exec calls the next 12 months a slaughterhouse for crypto security as North Korea steps up attacks ⚖️ $SOL
You have seen this movie before in crypto: a threat gets cheaper to run, and the industry spends a cycle catching up.
First, the warning came from security chiefs at Solana's Breakpoint, and the core claim is that AI is lowering the bar for hackers.
Second, North Korea is stepping up its attacks on crypto firms, which turns a technical problem into a sustained campaign.
Third, the window is the next 12 months — the slaughterhouse framing is about the near term, not some distant scenario.
If AI tools keep getting cheaper, teams with thin security budgets could become the easiest targets, and the volume of attempts may matter more than any single clever exploit.
What you can save from this: in the next year, defense is a budget question as much as a code question.
Which comes first — a wave of breaches, or a wave of security spending? 👇
#Solana #Security
For information only, not financial advice.
Tap $SOL to trade
$SOL
غيرك سبقك وتابع. ادخل بروفايلي وخلك مع اللي يقرأ قبل ما ينتشر الخبر.
Anchorage exec: next 12 months a 'slaughterhouse' for crypto security
An Anchorage exec calls the next 12 months a slaughterhouse for crypto security as North Korea steps up attacks ⚖️ $SOL
You have seen this movie before in crypto: a threat gets cheaper to run, and the industry spends a cycle catching up.
First, the warning came from security chiefs at Solana's Breakpoint, and the core claim is that AI is lowering the bar for hackers.
Second, North Korea is stepping up its attacks on crypto firms, which turns a technical problem into a sustained campaign.
Third, the window is the next 12 months — the slaughterhouse framing is about the near term, not some distant scenario.
If AI tools keep getting cheaper, teams with thin security budgets could become the easiest targets, and the volume of attempts may matter more than any single clever exploit.
What you can save from this: in the next year, defense is a budget question as much as a code question.
Which comes first — a wave of breaches, or a wave of security spending? 👇
#Solana #Security
For information only, not financial advice.
Tap $SOL to trade
$SOL
غيرك سبقك وتابع. ادخل بروفايلي وخلك مع اللي يقرأ قبل ما ينتشر الخبر.
You have seen this movie before in crypto: a threat gets cheaper to run, and the industry spends a cycle catching up.
First, the warning came from security chiefs at Solana's Breakpoint, and the core claim is that AI is lowering the bar for hackers.
Second, North Korea is stepping up its attacks on crypto firms, which turns a technical problem into a sustained campaign.
Third, the window is the next 12 months — the slaughterhouse framing is about the near term, not some distant scenario.
If AI tools keep getting cheaper, teams with thin security budgets could become the easiest targets, and the volume of attempts may matter more than any single clever exploit.
What you can save from this: in the next year, defense is a budget question as much as a code question.
Which comes first — a wave of breaches, or a wave of security spending? 👇
#Solana #Security
For information only, not financial advice.
Tap $SOL to trade
$SOL
غيرك سبقك وتابع. ادخل بروفايلي وخلك مع اللي يقرأ قبل ما ينتشر الخبر.
24

·
--
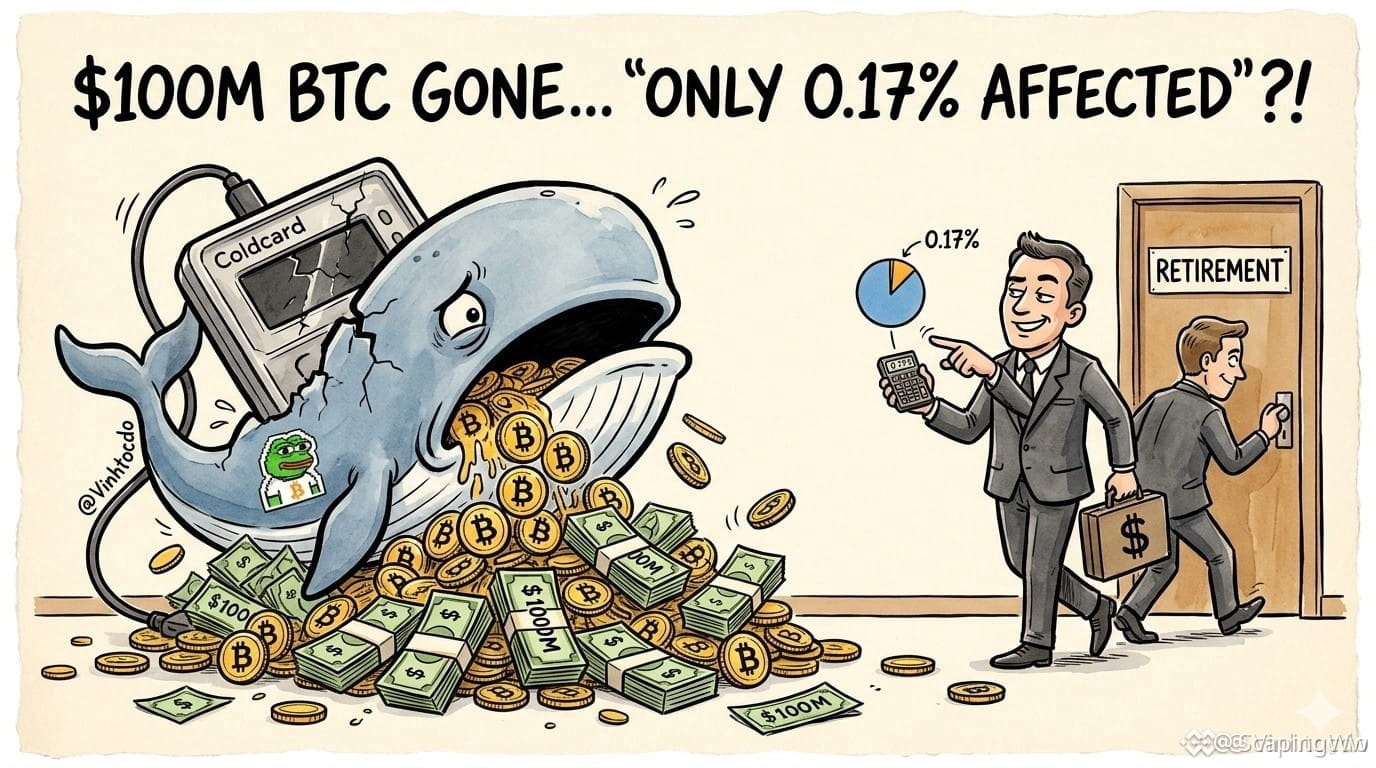
🚨 ONE HUNDRED MILLION IN $BTC SWEPT FROM HARDWARE STORAGE AS SECURITY CRACKS EXPOSED! 🛡️
When over eighteen hundred coins vanish from cold storage across thousands of addresses, dismissing it as a minor statistical anomaly is pure negligence. 🦈
Institutional-grade custody starts with elite hygiene, meaning immediate firmware upgrades and dispersing master backups across isolated physical locations rather than leaving a single point of failure. 💡
Are you auditing your hardware security protocols today or waiting for a liquidity event to test your defenses? 💬 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #HardwareWallet #Crypto
🔥 💎
🚨 ONE HUNDRED MILLION IN $BTC SWEPT FROM HARDWARE STORAGE AS SECURITY CRACKS EXPOSED! 🛡️
When over eighteen hundred coins vanish from cold storage across thousands of addresses, dismissing it as a minor statistical anomaly is pure negligence. 🦈
Institutional-grade custody starts with elite hygiene, meaning immediate firmware upgrades and dispersing master backups across isolated physical locations rather than leaving a single point of failure. 💡
Are you auditing your hardware security protocols today or waiting for a liquidity event to test your defenses? 💬 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #HardwareWallet #Crypto
🔥 💎
When over eighteen hundred coins vanish from cold storage across thousands of addresses, dismissing it as a minor statistical anomaly is pure negligence. 🦈
Institutional-grade custody starts with elite hygiene, meaning immediate firmware upgrades and dispersing master backups across isolated physical locations rather than leaving a single point of failure. 💡
Are you auditing your hardware security protocols today or waiting for a liquidity event to test your defenses? 💬 👇
⚠️ Not financial advice. Always manage your risk. 🛡️
🏷️ #BTC #Security #HardwareWallet #Crypto
🔥 💎
8
Log in to explore more content
Join global crypto users on Binance Square
⚡️ Get latest and useful information about crypto.
💬 Trusted by the world’s largest crypto exchange.
👍 Discover real insights from verified creators.
Email / Phone number
Trending Topics
1
#IsAnthropic’s$1.5TMarketCapJustified?
3,542 views
39 Discussing
2
#BTCRemainsUnderPressureAfterHawkishFOMCMinutes
175,739 views
1,838 Discussing
3
#NvidiaBoardReportedlySplitOverHuang’sReturn
84,263 views
972 Discussing
4
#StrategySTRCPreferredSlips3.65%Below$100Par
3,542 views
55 Discussing
5
#MASToUpgradeSGDTestnetToSGDigitalLedger
10,344 views
172 Discussing
6
#CanGTA6'sLaunchLiftTTWOShares?
57,596 views
727 Discussing
7
#Solana2027RoadmapTargetsDoubleComputeCapacity
2,693 views
85 Discussing
8
#InjectiveTokenizedRealEstateMortgagesTop$1.5B
789 views
27 Discussing
9
#TetherMakesStrategicInvestmentInSCRYPT
3,020 views
70 Discussing
10
#CapitalGroupAdds1264500StrategyShares
17,782 views
201 Discussing