#keplradvisessocialloginuserstotransferassets
Security Alert in Keplr Wallet:
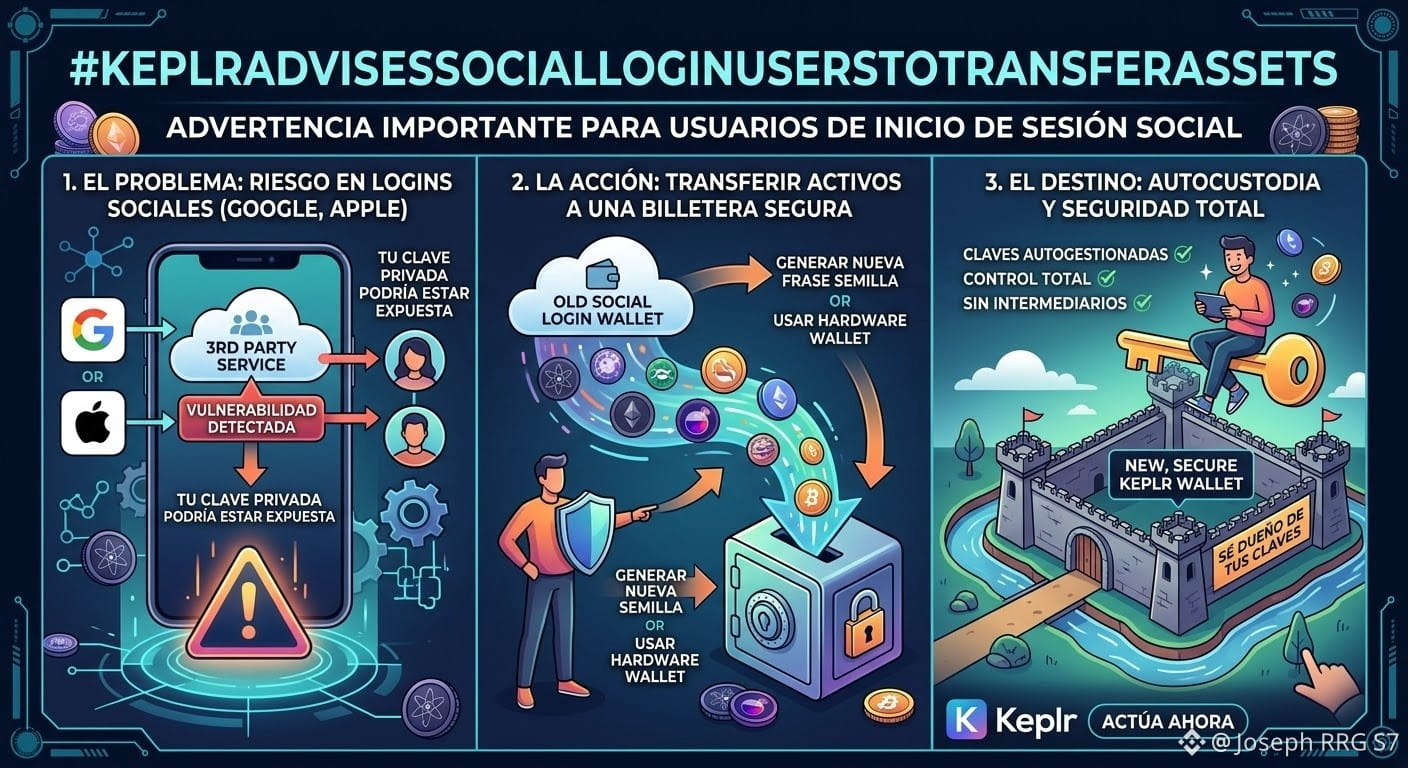
A critical vulnerability in third-party authentication infrastructure has put thousands of users in the Cosmos ecosystem at risk. Keplr Wallet, one of the most popular cryptocurrency wallets for networks such as Cosmos, Osmosis, and Injective, has issued an urgent warning urging users who created their accounts using social login (Google or Apple) to stop making deposits and immediately transfer their liquid assets to safer wallets.
The incident, initially reported after unauthorized transactions were detected between November 6 and 7, 2026, has reopened the debate about balancing convenient access with true self-custody in the Web3 world.
What exactly happened? The Web3Auth vulnerability
It is important to clarify that Keplr Wallet’s codebase was not directly compromised. The attack originated with Web3Auth, the infrastructure provider responsible for managing sign-ins through Google and Apple accounts.
When a user chooses social login instead of generating a traditional seed phrase, Web3Auth uses a distributed key generation system to create and assemble the private key in the background. According to preliminary reports, a vulnerability in Web3Auth’s infrastructure exposed these private keys, allowing attackers to drain funds without authorization.
As an immediate containment measure:
Web3Auth paused its embedded wallet services while it investigates the scope of the breach.
Keplr temporarily disabled Google and Apple sign-in options.
Rescue transfers: In some cases, Web3Auth’s security teams and its partners carried out precautionary transfers to verified safe addresses to prevent attackers from emptying vulnerable accounts.
$ARIA
$SOXLB
Security Alert in Keplr Wallet:
A critical vulnerability in third-party authentication infrastructure has put thousands of users in the Cosmos ecosystem at risk. Keplr Wallet, one of the most popular cryptocurrency wallets for networks such as Cosmos, Osmosis, and Injective, has issued an urgent warning urging users who created their accounts using social login (Google or Apple) to stop making deposits and immediately transfer their liquid assets to safer wallets.
The incident, initially reported after unauthorized transactions were detected between November 6 and 7, 2026, has reopened the debate about balancing convenient access with true self-custody in the Web3 world.
What exactly happened? The Web3Auth vulnerability
It is important to clarify that Keplr Wallet’s codebase was not directly compromised. The attack originated with Web3Auth, the infrastructure provider responsible for managing sign-ins through Google and Apple accounts.
When a user chooses social login instead of generating a traditional seed phrase, Web3Auth uses a distributed key generation system to create and assemble the private key in the background. According to preliminary reports, a vulnerability in Web3Auth’s infrastructure exposed these private keys, allowing attackers to drain funds without authorization.
As an immediate containment measure:
Web3Auth paused its embedded wallet services while it investigates the scope of the breach.
Keplr temporarily disabled Google and Apple sign-in options.
Rescue transfers: In some cases, Web3Auth’s security teams and its partners carried out precautionary transfers to verified safe addresses to prevent attackers from emptying vulnerable accounts.
$ARIA
$SOXLB