LuCa

Post

燕寶Melissa
·
--
Bullish⚠️【Safety Warning|High-Risk Vulnerability Detected】
Security agencies have detected:
GoPlus warning, OpenClaw Gateway has a high-risk vulnerability.
Attackers can remotely gain Agent administrator privileges through malicious websites.
Once exploited, it may lead to:
🔓 Privilege takeover
🔑 API key leakage
🧠 Node control being hijacked
💰 Asset security risks increasing
📌 Security recommendations (must be executed immediately):
1️⃣ Upgrade to OpenClaw 2026.2.25 or higher;
2️⃣ Audit and revoke unnecessary credentials, API Keys, and node permissions in the Agent instances;
3️⃣ Check recent access logs for abnormal calls;
4️⃣ Suspend external connections from suspicious sources.
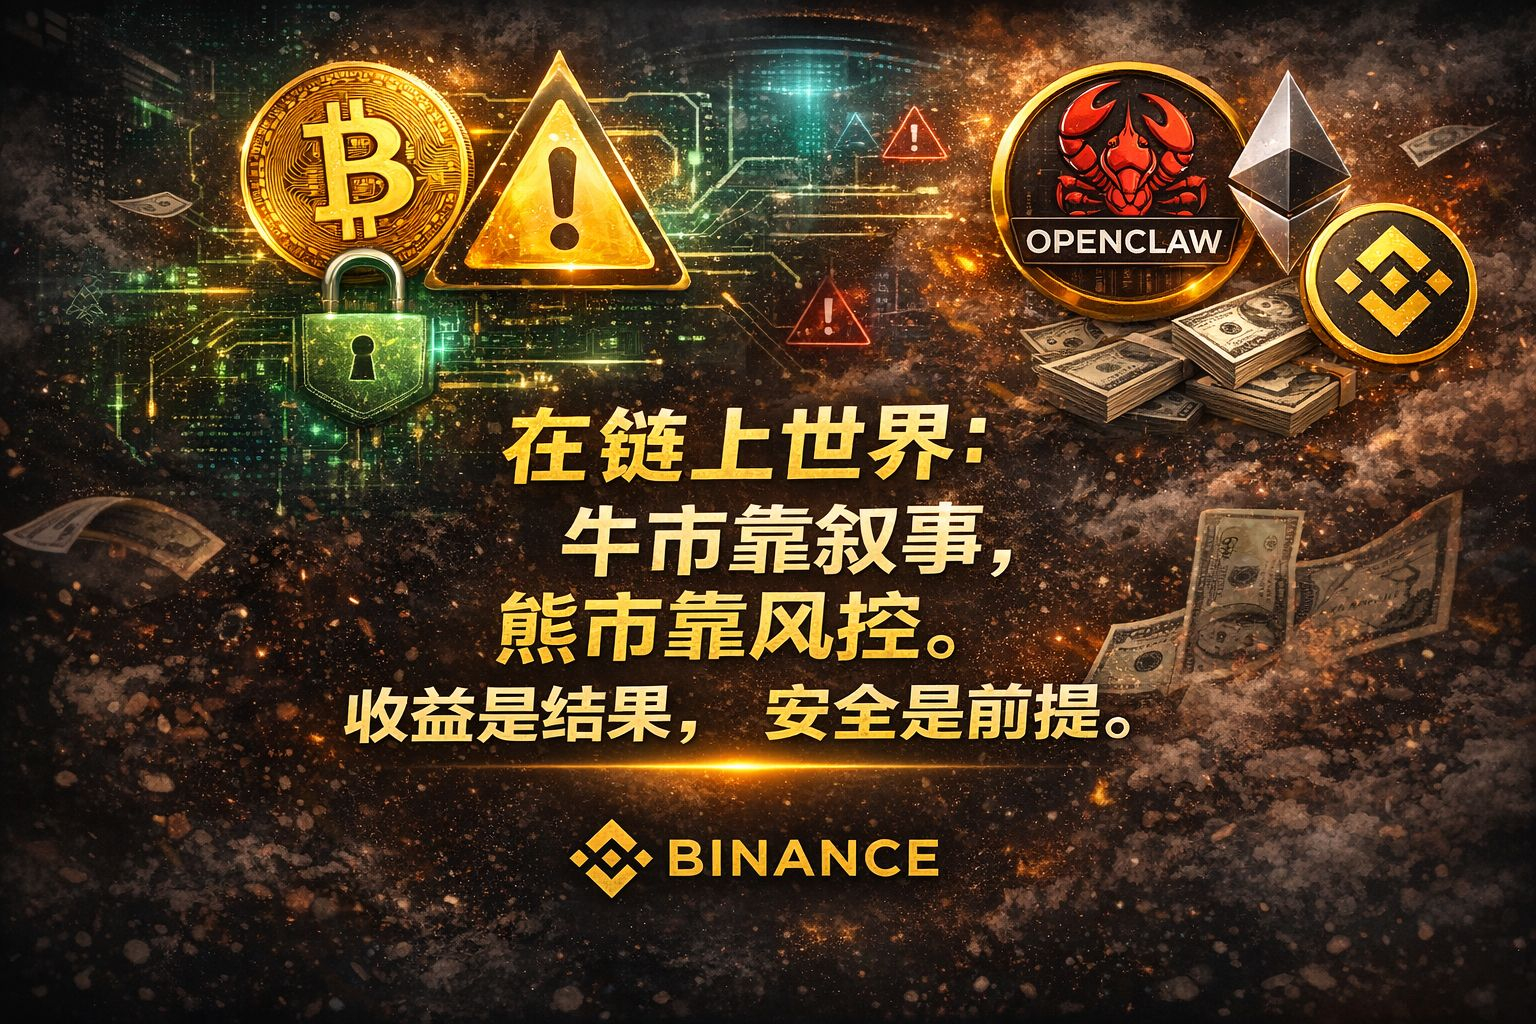
In the on-chain world:
Bull markets rely on narratives,
Bear markets rely on risk control.
Vulnerabilities do not provide advance notice,
Risks only reward those who are vigilant.
🔒 Remember:
Profits are the result,
Security is the prerequisite.
#OpenClawDevelopers
$BTC
$ETH
$BNB
Security agencies have detected:
GoPlus warning, OpenClaw Gateway has a high-risk vulnerability.
Attackers can remotely gain Agent administrator privileges through malicious websites.
Once exploited, it may lead to:
🔓 Privilege takeover
🔑 API key leakage
🧠 Node control being hijacked
💰 Asset security risks increasing
📌 Security recommendations (must be executed immediately):
1️⃣ Upgrade to OpenClaw 2026.2.25 or higher;
2️⃣ Audit and revoke unnecessary credentials, API Keys, and node permissions in the Agent instances;
3️⃣ Check recent access logs for abnormal calls;
4️⃣ Suspend external connections from suspicious sources.
In the on-chain world:
Bull markets rely on narratives,
Bear markets rely on risk control.
Vulnerabilities do not provide advance notice,
Risks only reward those who are vigilant.
🔒 Remember:
Profits are the result,
Security is the prerequisite.
#OpenClawDevelopers
$BTC
$ETH
$BNB